Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
vxlang-page — Code obfuscation, virtualization, and anti-tamper protector for x86-64 Windows binaries (EXE/DLL/SYS) and .NET modules, with beta ELF support. Features code flattening, memory encryption, and multi-VM engine. | Kitploit
Tools/GitHubGitHub/vxlang/vxlang-page
Reverse Engineering
GitHubvxlang/vxlang-page

vxlang-page

Code obfuscation, virtualization, and anti-tamper protector for x86-64 Windows binaries (EXE/DLL/SYS) and .NET modules, with beta ELF support. Features code flattening, memory encryption, and multi-VM engine.

Repository anzeigenWebseite
7665036vor 4 TagenVon Kitploit geprüft
Teilen
Inhalt in der angeforderten Sprache nicht verfügbar. Englische Version wird angezeigt.

VxLang


  • Contents
    • Docs
    • What is VxLang?
    • Supported File Formats
    • Preview
      • Virtualization Preview
      • Dual-Mode Preview
      • Obfuscation Preview
      • Code-Flattening Preview
      • Runtime Code Encryption
    • How to get the full version
      • Donate and Subscription
        • Patreon
          • Link
          • Event

Document

  • Link

What is VxLang?

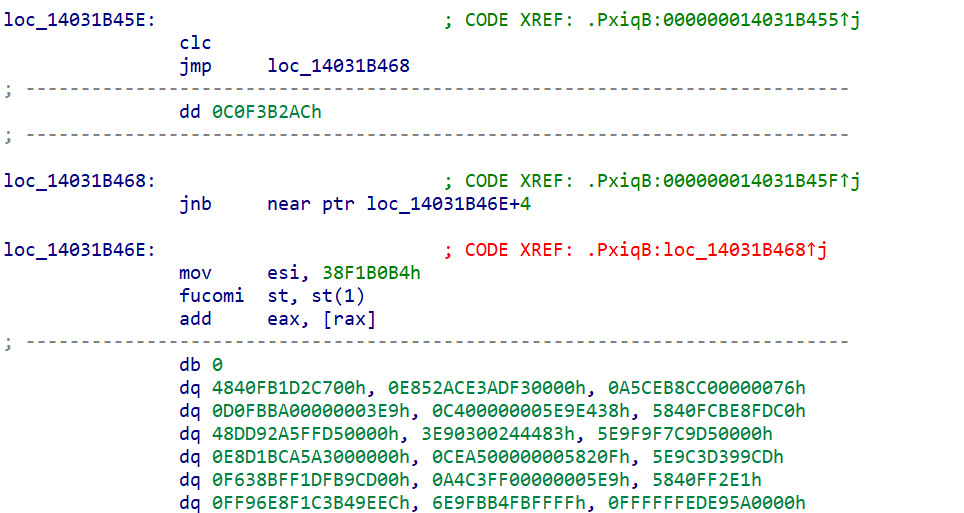
VxLang is a binary protection solution designed to make reverse engineering and tampering with Windows executables more difficult. It combines technologies such as executable packing, code obfuscation, code virtualization, control-flow flattening, and Runtime Code Encryption to protect important code and data.

The VxLang project currently targets x86-64 system and .NET binaries, native binary files for the Microsoft Windows operating system, including executables with the ".exe" extension, dynamic link library files with the ".dll" extension, and kernel driver files with the ".sys" extension. (The types of target binaries supported by vxlang will be expanded in future updates).

  • Added beta code for the ELF file format.
    • The beta version only supports general code-flattening.
    • Beta features require users to specify target code.
    • VxLang recommends using the -fno-pic option in ELF 32bit binary builds.

Supported File Formats

Windows EXE/DLL Windows Kernel Drive
Obfuscator Obfuscator
Virtualizer Virtualizer
Protector Protector
Windows UEFI Modules Windows .NET
Obfuscator Obfuscator
Virtualizer Virtualizer
Protector Protector
Linux ELF
Obfuscator
Virtualizer
Protector

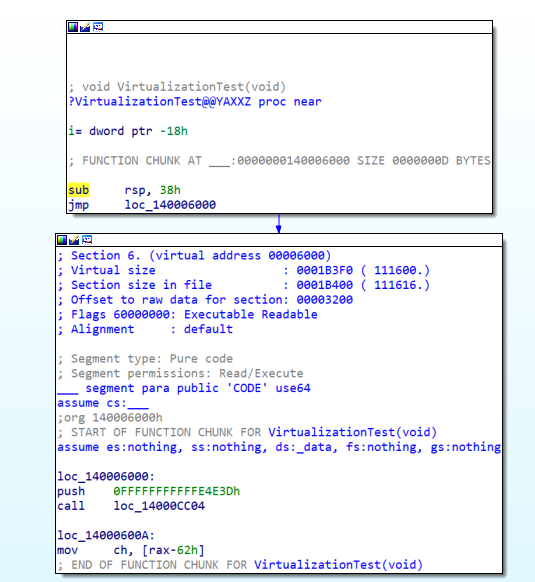
Virtualization Preview

; x86-64 asm
cmp         qword ptr [rsp + 0x20], rax
jae         0x140001bf5
mov         rax, qword ptr [rsp + 0x20]
movzx       eax, byte ptr [rsp + rax + 0x50]
; to v-asm
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
movi   exr_0, ${RANDOM}
movi   exr_1, ${RANDOM}
xorr   exr_0, exr_1
mulr   r7, exr_0
addr   r6, r7
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
addr   r6, r7
movr   r0, r6
movr   r1, rax
ldrr   r2, r0
cmpr   r2, r1
be     0x2c59
movr   r0, rax
movr   r6, rsp
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
movi   exr_0, ${RANDOM}
movi   exr_1, ${RANDOM}
xorr   exr_0, exr_1
mulr   r7, exr_0
addr   r6, r7
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
addr   r6, r7
movr   r1, r6
ldrr   r2, r1
movr   rax, r2
; compile
e7 f8 f1 e5 01 e1 a2 9a 22 87 c3 93 61 e5 06 e1
a2 9a 22 87 c3 93 61 eb 06 01 e6 01 e0 a2 9a 22 
e6 0a e1 a2 9a 22 ec 01 0a d6 06 01 da 07 06 e5 
01 e1 a2 9a 22 87 c3 93 61 e5 06 c1 a2 9a 22 87 
c3 93 61 eb 06 01 da 07 06 e7 f7 f8 e7 fc e5 c6 
00 08 a9 00 03 bb c6 01 00 00 e7 f7 e5 e7 f8 f1 
e5 01 6d 86 d3 6d 7f 86 9d a2 e5 06 6d 86 d3 6d 
7f 86 9d a2 eb 06 01 e6 01 6c 86 d3 6d e6 0a 6d 
86 d3 6d ec 01 0a d6 06 01 da 07 06 e5 01 6d 86 
d3 6d 7f 86 9d a2 e5 06 4d 86 d3 6d 7f 86 9d a2            

Before
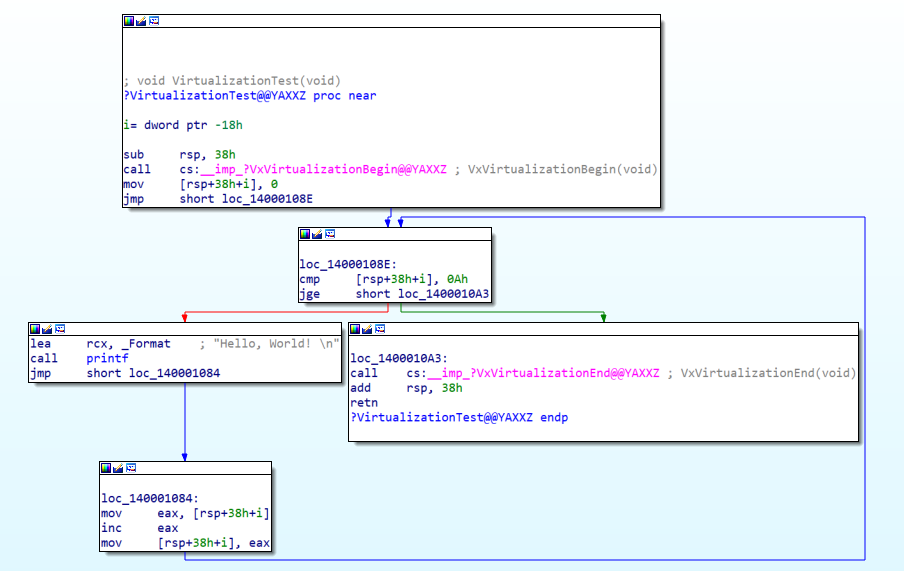
After
Dual-Mode(Obfuscation + Virtualization) Preview

Obfuscation Preview

Preview

Code-Flattening Preview

Before

After

Runtime Code Encryption

Tool herunterladen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-seitiges Red-Team-Toolkit mit 102 Offline-Tools für Recon, Payload-Generierung, Credential-Angriffe, Krypto, Encoding und Engagement-Reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT-Plattform, die Shadowserver-Berichte in MongoDB einliest und sie als interaktive Karten, Analysen, Findings, Advisories und Executive-Dashboards wiedergibt.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Das System der Handlung für KI-native Cybersicherheit – wo Absicht zu gesteuerter Ausführung wird, Beweise zu operativem Gedächtnis werden und jeder Einsatz den nächsten verbessert.

    280

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →