
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Tools/GitHubGitHub/tjt001/cve-2026-125350-poc
Vulnerability AnalysisExploitationWeb Application Exploitation
GitHubtjt001/cve-2026-125350-poc

CVE-2026-125350-PoC

Google Chrome XSLT pattern-cache Use-After-Free (CVE-2026-125350) crash PoC — affected < 157.0.8103.50

Repository anzeigen
11vor 7 TagenNoch nicht geprüft
Teilen
Inhalt in der angeforderten Sprache nicht verfügbar. Englische Version wird angezeigt.

CVE-2026-125350 — Google Chrome XSLT Pattern Cache Use-After-Free

AttributeInformation
CVECVE-2026-125350 / EUVD-2026-121390
TypeUse After Free (CWE-416)
Componentlibxslt pattern.c — xsltTestCompMatchDirect
Affected versionsGoogle Chrome < 157.0.8103.50
Fixed version157.0.8103.50
Fix CL61cab3f7 / M157 cherry-pick 049750111b1e
Bugcrbug.com/582442907

Vulnerability Principle

Before calling xmlXPathEval, libxslt's xsltTestCompMatchDirect reads the node-set pointer from the pattern match cache slot. When the count predicate of xsl:number references a lazily evaluated global variable, and that variable's value in turn executes xsl:number, the evaluation process re-enters the same cache slot and frees/replaces the cached object; after the outer call returns, it frees again using the stale pointer read before evaluation →

double free / use-after-free → renderer process memory corruption.

The fix is only 9 lines: after evaluation completes, re-read the cache slot pointer before freeing.

Repository Contents

ContentDescription
poc.pyCrash PoC: starts a local HTTP service and prints the trigger URL, which the user manually visits in the target browser
repro/Official regression test (included with the fix CL, i.e., the official trigger files): test page + 9 XML/XSLT files
chrome-vulnerable-157.0.8103.39/
crash-renderer-157.0.8103.39.dmp

PoC Usage

# Zero dependencies, pure Python standard library
python poc.py                # start service (default port 8899) and print trigger URL
python poc.py --port 9999    # custom port

Flow: start a local HTTP service → print the trigger URL http://127.0.0.1:8899/ → the user manually visits it in the target browser (vulnerable Chrome version).

  • The script does not launch a browser; any browser can access it (document() requires HTTP delivery; opening directly via file:// does not work)
  • The service runs continuously and prints HTTP access logs in real time; on Ctrl+C stop, it counts the number of times the trigger XML was delivered in this session

Determination:

SymptomConclusion
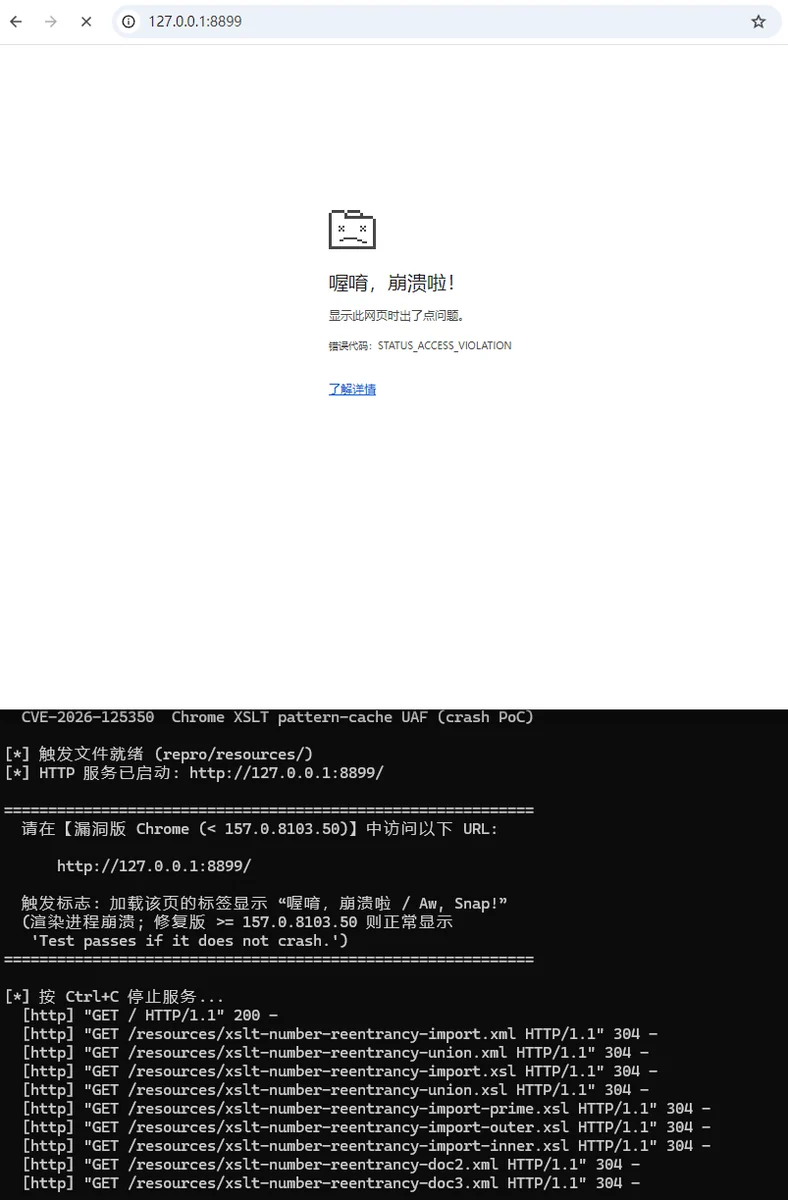
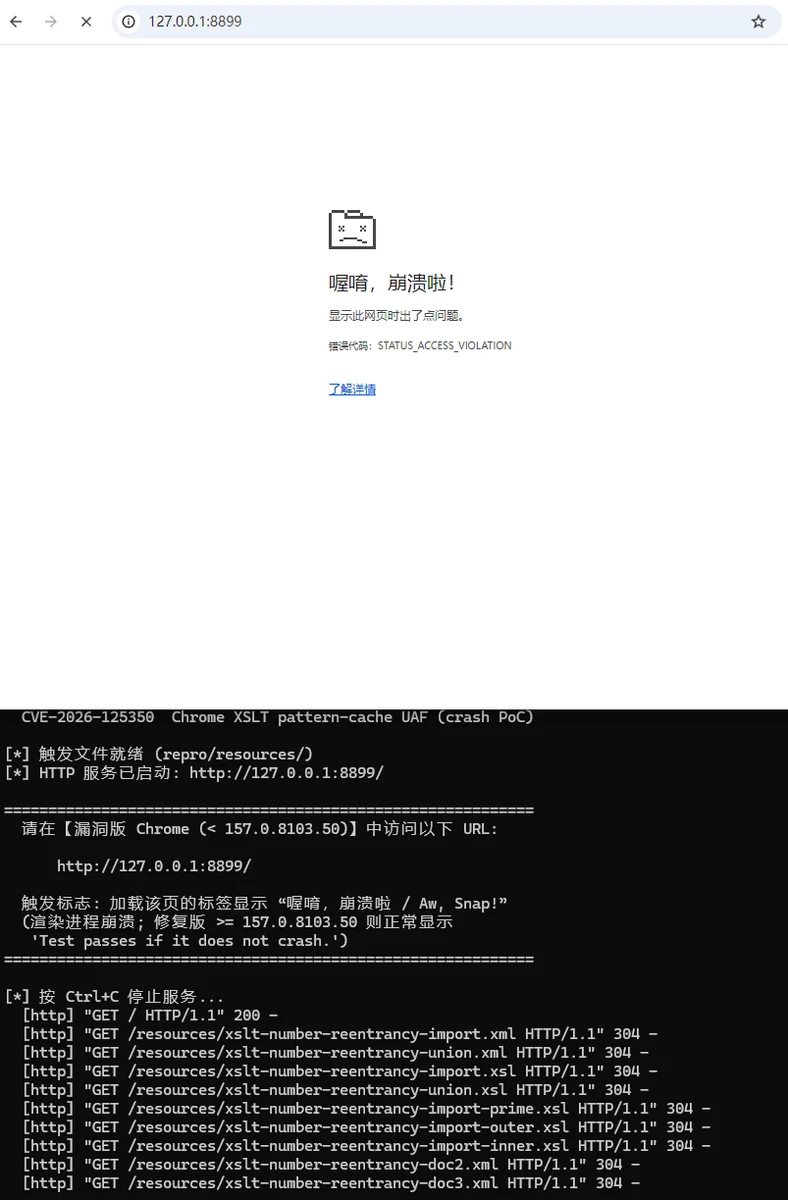
Tab shows "Aw, Snap!"Renderer process crash → Affected (< 157.0.8103.50)
Normally displays "Test passes if it does not crash."Fixed (≥ 157.0.8103.50)

Reproduction Results

VersionResult
157.0.8103.39 (vulnerable version, manually visit trigger URL)Tab crashes, renderer process Crashpad dump generated (stably reproduced multiple times)
157.0.8103.51 (fixed version)No crash, normally displays test passed

image-20261111144908770

Scope Notes

  • This PoC only triggers UAF memory corruption (renderer process crash); it does not include heap layout control, UAF object reuse, RCE, or sandbox escape.
  • The trigger file comes from the regression test included in the official Chromium fix CL.

References

  • Chrome Releases announcement
  • Chromium issue 582442907
  • Fix commit (GitHub mirror)
  • Official CVE record

For authorized security research and educational purposes only.

Tool herunterladen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    927
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-seitiges Red-Team-Toolkit mit 102 Offline-Tools für Recon, Payload-Generierung, Credential-Angriffe, Krypto, Encoding und Engagement-Reporting.

    360
  • 4

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT-Plattform, die Shadowserver-Berichte in MongoDB einliest und sie als interaktive Karten, Analysen, Findings, Advisories und Executive-Dashboards wiedergibt.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Das System der Handlung für KI-native Cybersicherheit – wo Absicht zu gesteuerter Ausführung wird, Beweise zu operativem Gedächtnis werden und jeder Einsatz den nächsten verbessert.

    289

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →