
 #1
Tools zum Sammeln, Analysieren und Operationalisieren von Bedrohungsfeeds, Indicators of Compromise (IOCs) und Angriffstrends.
Kitploit empfohlen

 lore-hex/quill-router
TrustedRouter.com Repo für sicheres LLM-Proxying
 nomi-sec/poc-in-github
📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.
 yamato-security/hayabusa
Multithreaded-Windows-Ereignisprotokoll-Forensik-Zeitleistengenerator und Bedrohungsjagd-Tool mit vollständiger Sigma-Regelunterstützung, das…
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
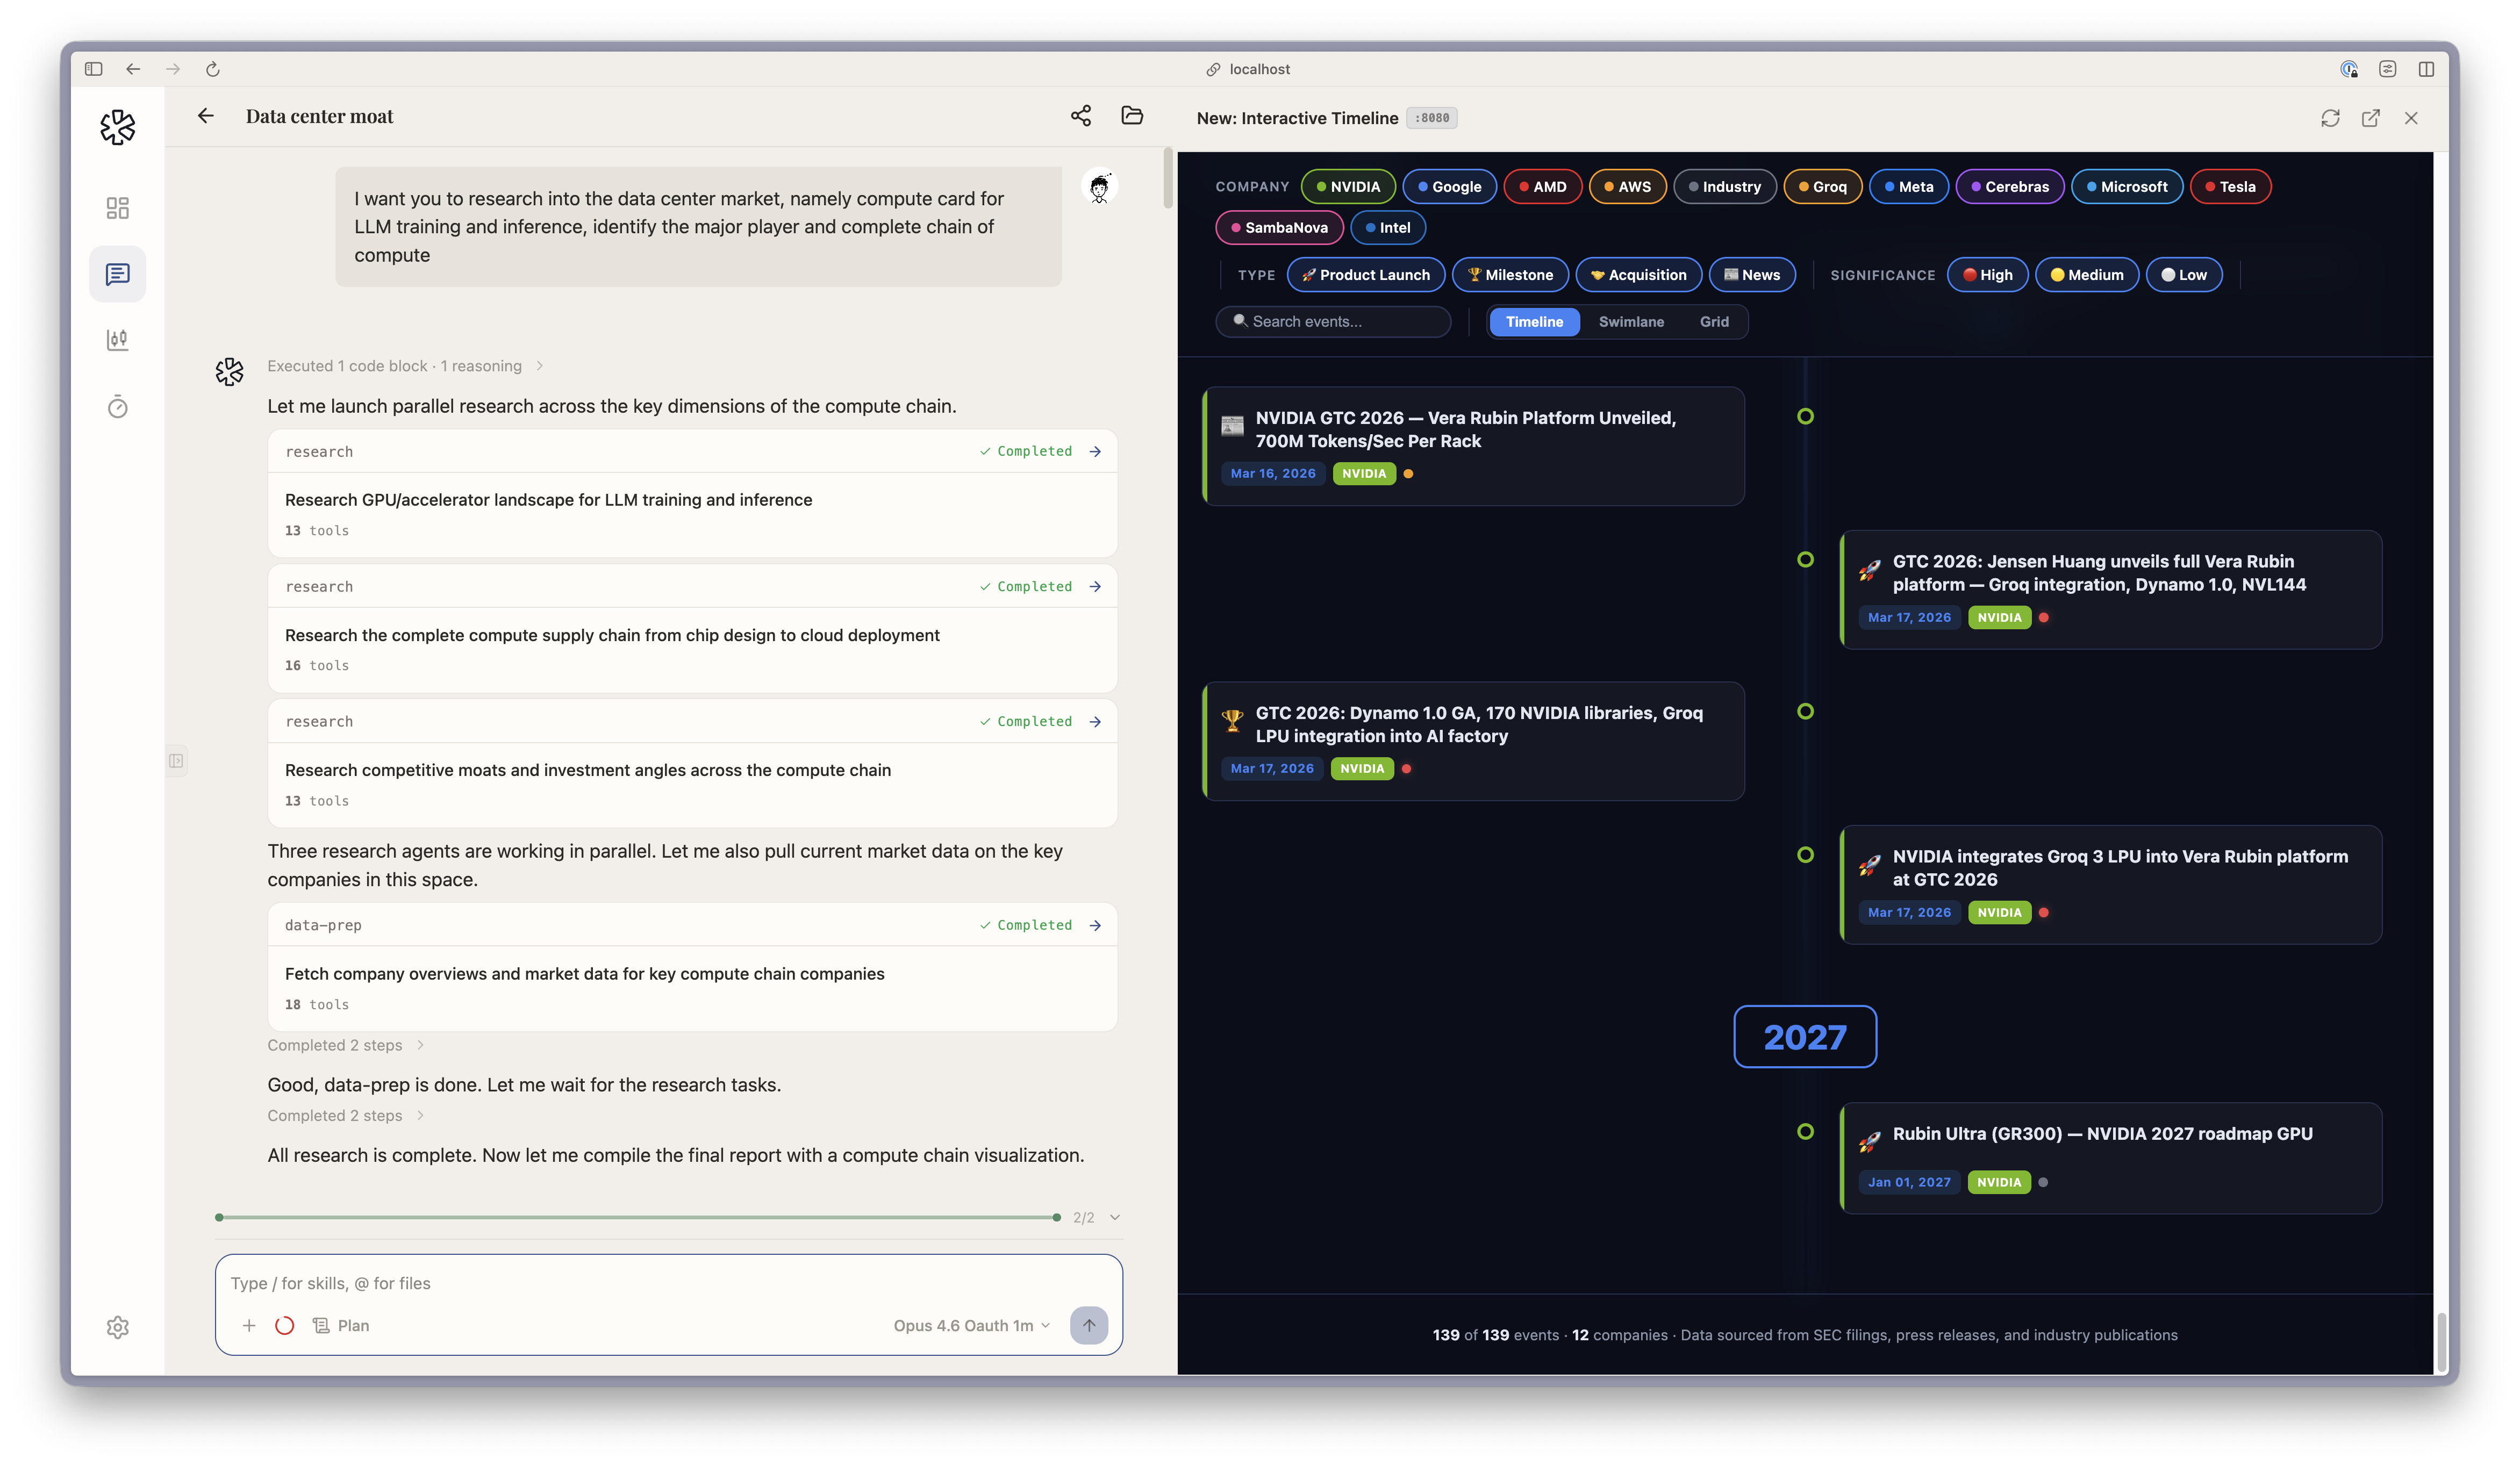 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 ossf/scorecard
OpenSSF Scorecard - Sicherheits-Gesundheitsmetriken für Open Source
 0xv1n/macnoise
Erweiterbarer Generator für MacOS-Systemtelemetrie.
 aquasecurity/vuln-list-debian
Debian Security Tracker
 aquasecurity/vuln-list-nvd
NVD
 google/osv.dev
Open-Source-Schwachstellendatenbank und Triage-Dienst.
 gautamvarmadatla/mcpsafetywarden
Proxy-Server, der MCP-Server mit Verhaltensprofilerstellung, Sicherheitsscans, Risikobewertung und sicherer Ausführung umschließt. Erkennt…
 ssc-ict-innovatie/nl-kat-coordination
Modulares Netzwerk-Scanning-Framework, das verschiedene Tools und externe Datenbanken integriert, um Schwachstellen und Konfigurationsfehler zu…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 tjnel/certgraveyard_yara
Automatisierte YARA-Regelgenerierung aus der Cert Central-Datenbank kompromittierter Zertifikate.
 kaifcodec/user-scanner
Multi-platform OSINT scanner for email and username reconnaissance across 295+ vectors. Extracts profile metadata, checks account registrations, and…
 julioliraup/antiphishing
Erweiterter Phishing-Schutz: Offene und kostenlose Suricata-Regelsätze








