

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Robber — Robber is open source tool for finding executables prone to DLL hijacking | Kitploit

Tools/GitHubGitHub/mojtabatajik/robber
Privilege EscalationVulnerability ScannersVulnerability AnalysisBinary Analysis
GitHubmojtabatajik/robber

Robber

Robber is open source tool for finding executables prone to DLL hijacking

View Repository
798153586 months agoReviewed by Kitploit
Share
Website

Robber — DLL Hijack Scanner

Free, open source tool for finding DLL hijacking opportunities in Windows executables. No third-party dependencies.


What it does

Windows loads DLLs by searching a fixed set of directories in order — the executable's own directory first, then System32, Windows, PATH entries. If a DLL isn't found in a system directory, an attacker who can write to an earlier directory in that chain can drop a malicious copy and have it loaded instead.

Robber walks a directory tree, checks each executable's import table against what's actually on disk, and tells you which ones are worth looking at and why.
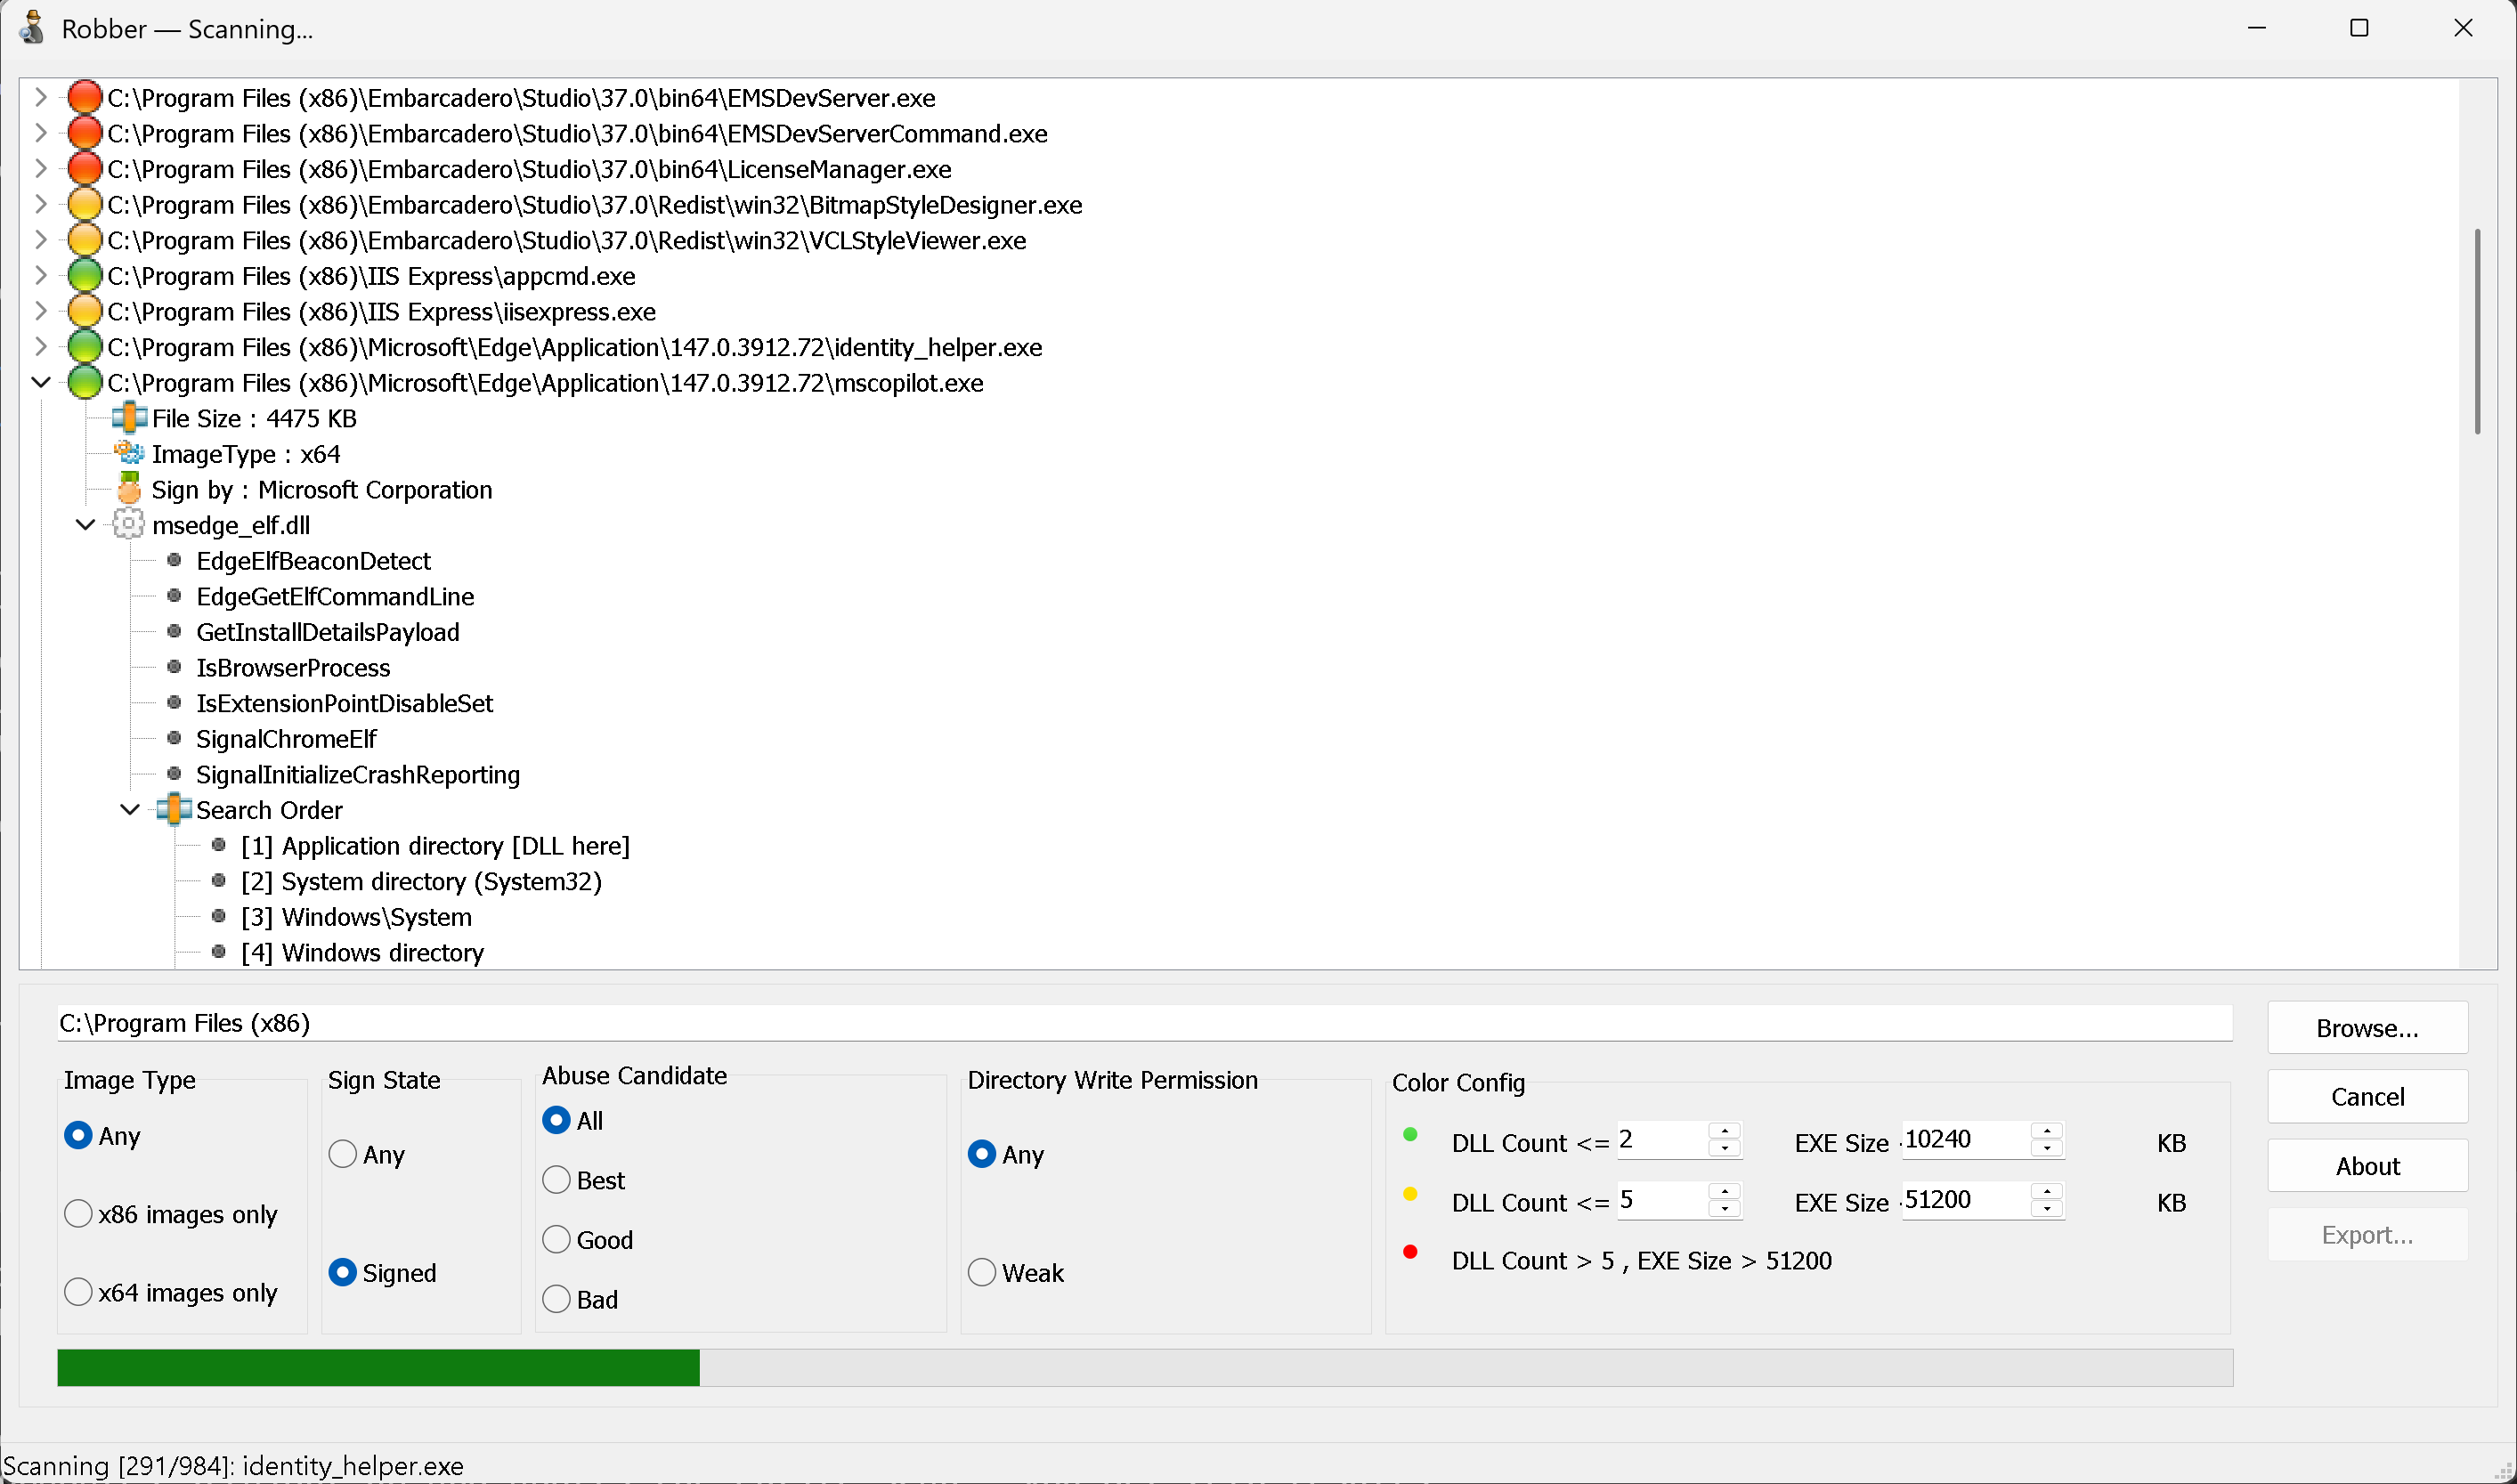

GUI usage

Robber

Point it at a directory, hit Scan. Results show up in the tree as they're found — expand any executable to see which DLLs are hijackable, what methods they export, and the full search order with writability flags for each directory.

The Color Config panel controls the thresholds for Best/Good/Bad ratings:

  • Best (green) — few imported DLLs, small binary. Easy to build a proxy DLL that stubs everything out.
  • Good (yellow) — moderate complexity
  • Bad (red) — lots of imports or large binary, harder to proxy without crashing the app

Use the filters to narrow results by architecture, signing status, severity, or whether the executable's directory is actually writable. Hit Export when done to save as JSON or CSV.

Settings and the last scan path are remembered between sessions.


CLI

Robber.exe --path <dir> [options]
--path <dir>               Directory to scan (required)
--output <file>            Write to file (.json or .csv). Default: stdout
--image-type any|x86|x64
--sign any|signed
--rate any|best|good|bad
--write-perm               Only show results in writable directories
--best-dll-count <n>       (default: 2)
--best-exe-size <n>        KB threshold (default: 10240)
--good-dll-count <n>       (default: 5)
--good-exe-size <n>        KB threshold (default: 51200)
--help

Progress goes to stderr, results to stdout — pipe-friendly.

Robber.exe --path "C:\Program Files" --rate best --output hits.json
Robber.exe --path "C:\Program Files" | jq '.[].exePath'
Robber.exe --path "C:\Tools" --sign signed --write-perm

A few things worth knowing

  • System DLLs (System32, SysWOW64, Windows\System) are excluded automatically — no false positives from redistributable runtimes like msvcr120.dll
  • Both standard and delayed imports are scanned
  • Executables requiring elevation (requireAdministrator / highestAvailable) are flagged — a hijack on an elevated process is a privilege escalation, not just code execution
  • The search order tree shows exactly which directories Windows would check and which of those you can write to

Building

Delphi XE2 or later. Open Robber\Robber.dproj, build. Nothing else needed.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →





