

Vigil
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
penetration-testing-frameworksreconnaissancestatic-code-analysis+9
29
 knostic/openant
来自 Knostic 的 OpenAnt 是领先的开源基于 LLM 的漏洞发现产品,帮助防御者主动发现已验证的安全缺陷,同时将误报和漏报降到最低。第一阶段负责检测,第二阶段负责攻击。幸存下来的才是真实漏洞。
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 blackvectorops/semantic_firewall
Generate deterministic semantic fingerprints for Go functions. Detect xz-style backdoors and verify semantic equivalence using Static Single…
 0xdea/semgrep-rules
我收集的Semgrep规则,用于促进漏洞研究。
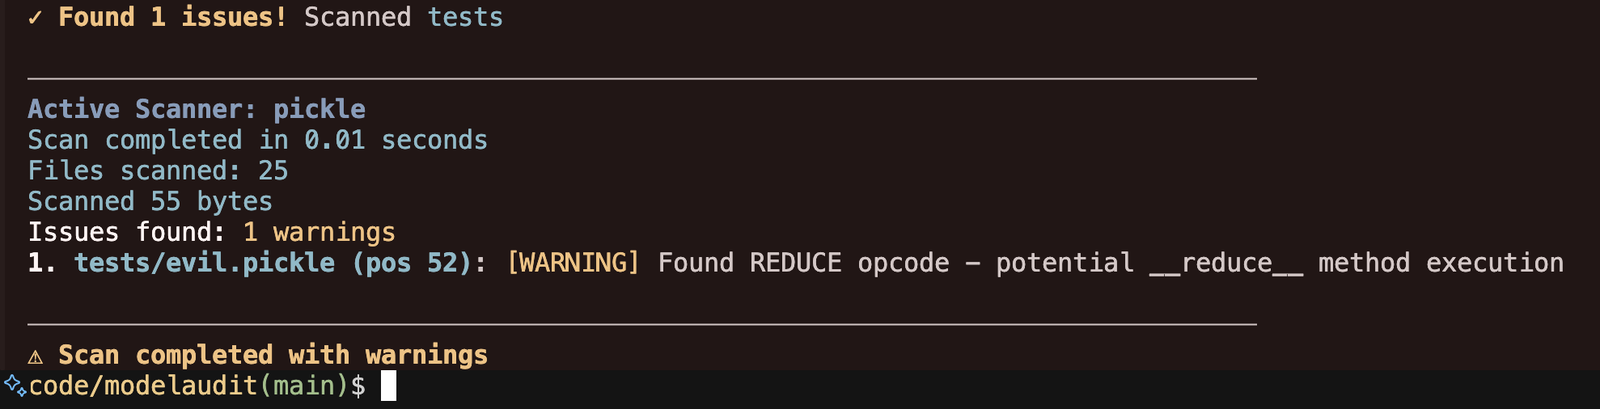 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 makenowjust-labs/recheck
用于检测JavaScript和Scala代码库中ReDoS(正则表达式拒绝服务)漏洞的静态分析工具,提供可信赖的正则表达式安全检查。
 github/codeql
CodeQL:为全球安全研究人员提供支持,以及GitHub高级安全中代码扫描功能的库和查询。
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
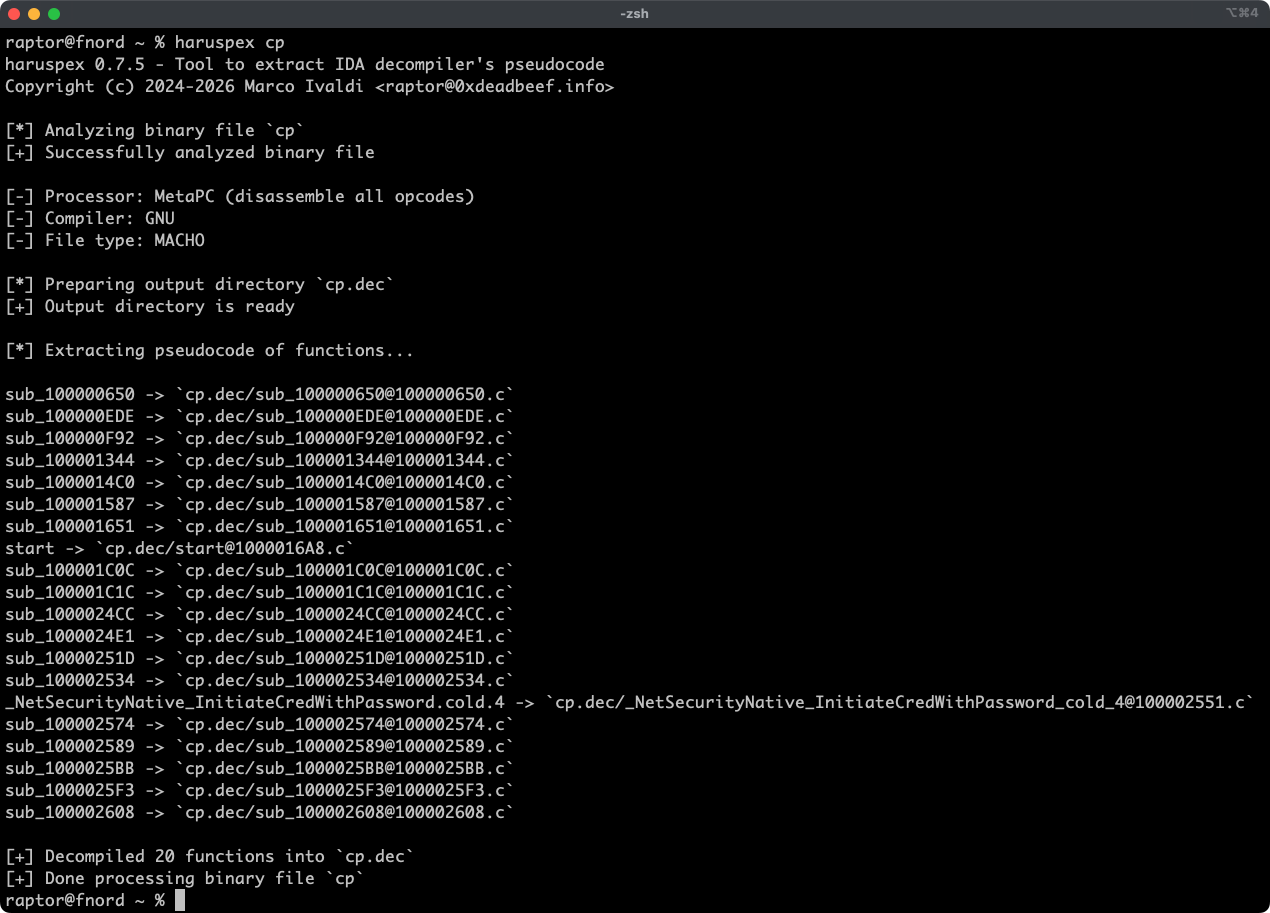 0xdea/haruspex
漏洞研究助手,可从 IDA Hex-Rays 反编译器中提取伪代码。
 sonarsource/sonarqube
代码质量与静态分析平台,具备质量门禁、多语言扫描以及以安全为核心的规则,可在CI/CD工作流中检测漏洞和可维护性问题。
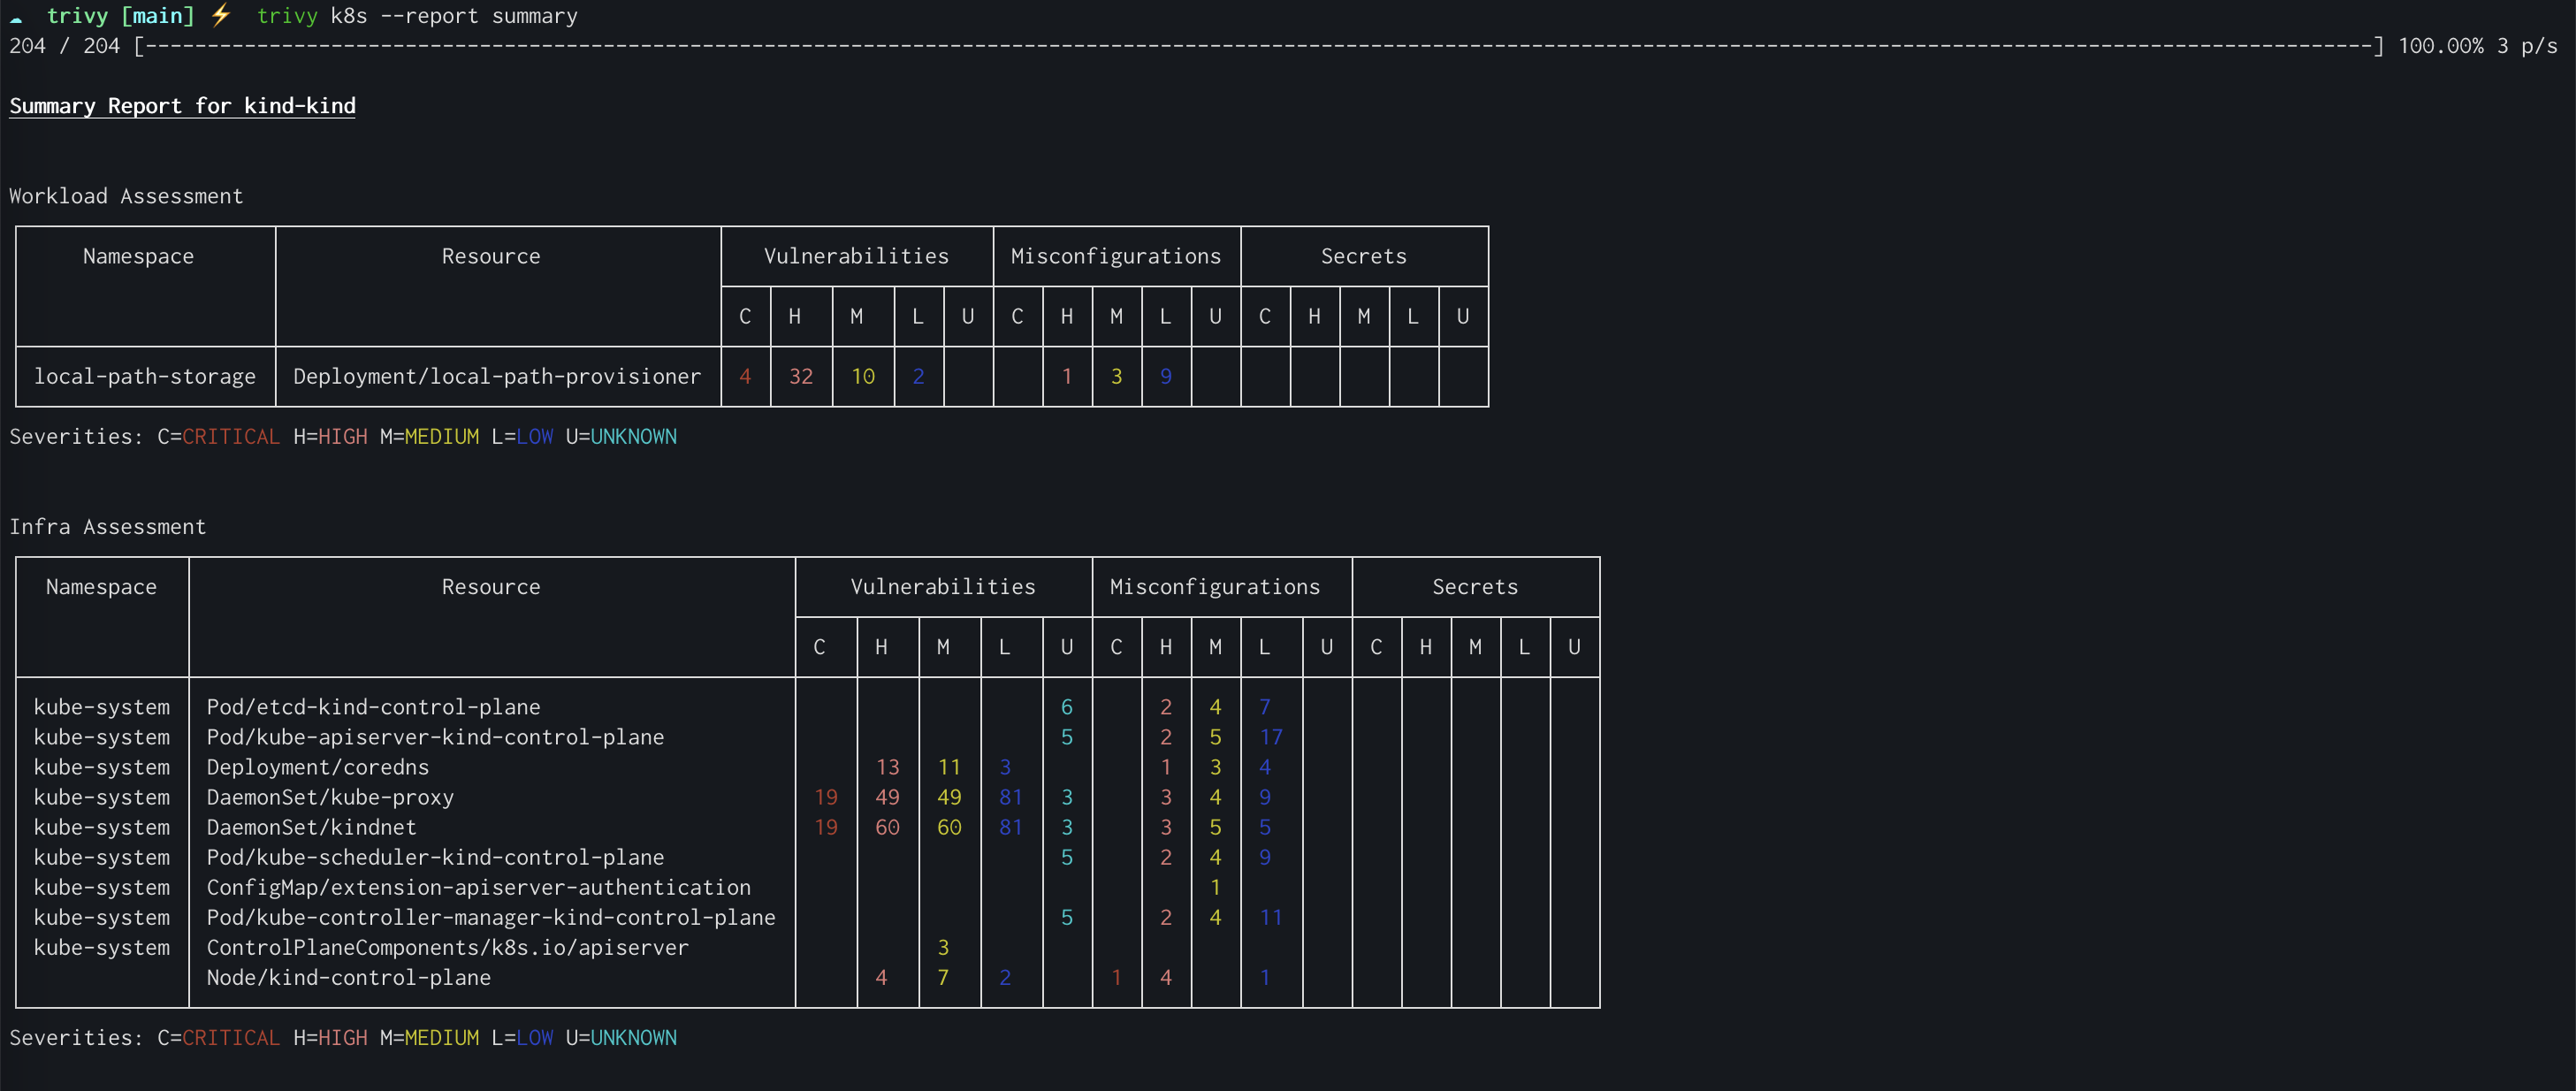 aquasecurity/trivy
在容器、Kubernetes、代码仓库、云环境等中发现漏洞、错误配置、密钥、SBOM
 facebook/infer
一个用于 Java、C、C++ 和 Objective-C 的静态分析器
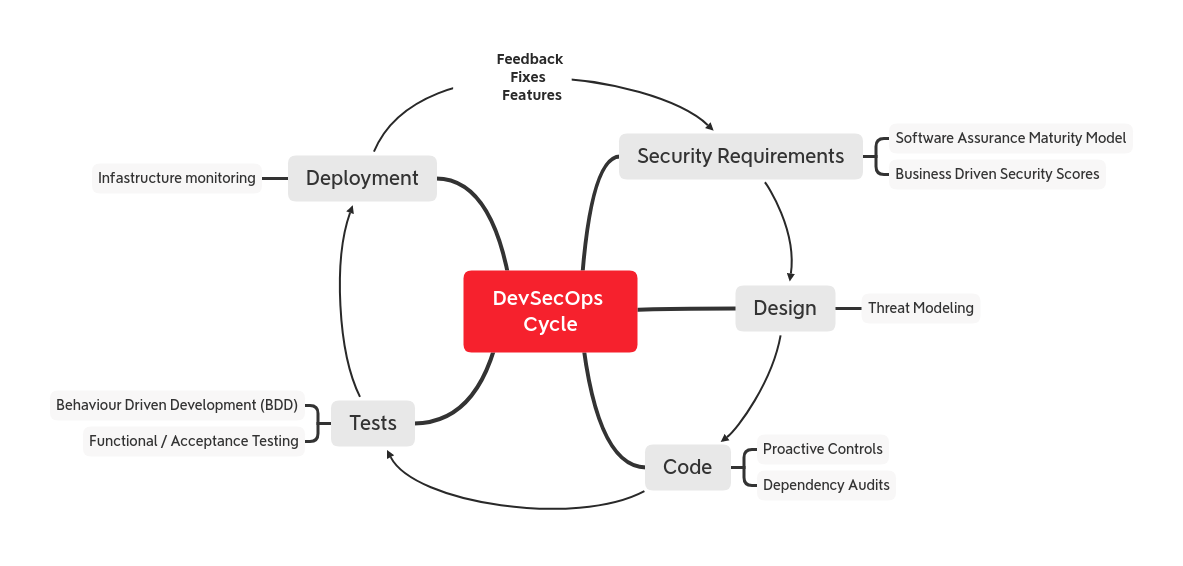 owasp/devsecopsguideline
OWASP DevSecOps 指南可以帮助我们将安全作为开发流水线的一部分嵌入其中。