
 vxlang/vxlang-page
Code obfuscation, virtualization, and anti-tamper protector for x86-64 Windows binaries (EXE/DLL/SYS) and .NET modules, with beta ELF support. Features code flattening, memory encryption, and multi-VM engine.


VxLang is a binary protection solution designed to make reverse engineering and tampering with Windows executables more difficult. It combines technologies such as executable packing, code obfuscation, code virtualization, control-flow flattening, and Runtime Code Encryption to protect important code and data.
The VxLang project currently targets x86-64 system and .NET binaries, native binary files for the Microsoft Windows operating system, including executables with the ".exe" extension, dynamic link library files with the ".dll" extension, and kernel driver files with the ".sys" extension. (The types of target binaries supported by vxlang will be expanded in future updates).
ELF file format.
code-flattening.-fno-pic option in ELF 32bit binary builds.| Windows EXE/DLL | Windows Kernel Drive | ||
| Obfuscator |  |
Obfuscator | |
| Virtualizer | |
Virtualizer | |
| Protector | |
Protector | |
| Windows UEFI Modules | Windows .NET | ||
| Obfuscator | |
Obfuscator |  |
| Virtualizer | |
Virtualizer | |
| Protector | |
Protector |  |
| Linux ELF | |
| Obfuscator |  |
| Virtualizer | |
| Protector | |
; x86-64 asm
cmp         qword ptr [rsp + 0x20], rax
jae         0x140001bf5
mov         rax, qword ptr [rsp + 0x20]
movzx       eax, byte ptr [rsp + rax + 0x50]
; to v-asm
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
movi   exr_0, ${RANDOM}
movi   exr_1, ${RANDOM}
xorr   exr_0, exr_1
mulr   r7, exr_0
addr   r6, r7
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
addr   r6, r7
movr   r0, r6
movr   r1, rax
ldrr   r2, r0
cmpr   r2, r1
be     0x2c59
movr   r0, rax
movr   r6, rsp
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
movi   exr_0, ${RANDOM}
movi   exr_1, ${RANDOM}
xorr   exr_0, exr_1
mulr   r7, exr_0
addr   r6, r7
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
addr   r6, r7
movr   r1, r6
ldrr   r2, r1
movr   rax, r2
; compile
e7 f8 f1 e5 01 e1 a2 9a 22 87 c3 93 61 e5 06 e1
a2 9a 22 87 c3 93 61 eb 06 01 e6 01 e0 a2 9a 22
e6 0a e1 a2 9a 22 ec 01 0a d6 06 01 da 07 06 e5
01 e1 a2 9a 22 87 c3 93 61 e5 06 c1 a2 9a 22 87
c3 93 61 eb 06 01 da 07 06 e7 f7 f8 e7 fc e5 c6
00 08 a9 00 03 bb c6 01 00 00 e7 f7 e5 e7 f8 f1
e5 01 6d 86 d3 6d 7f 86 9d a2 e5 06 6d 86 d3 6d
7f 86 9d a2 eb 06 01 e6 01 6c 86 d3 6d e6 0a 6d
86 d3 6d ec 01 0a d6 06 01 da 07 06 e5 01 6d 86
d3 6d 7f 86 9d a2 e5 06 4d 86 d3 6d 7f 86 9d a2
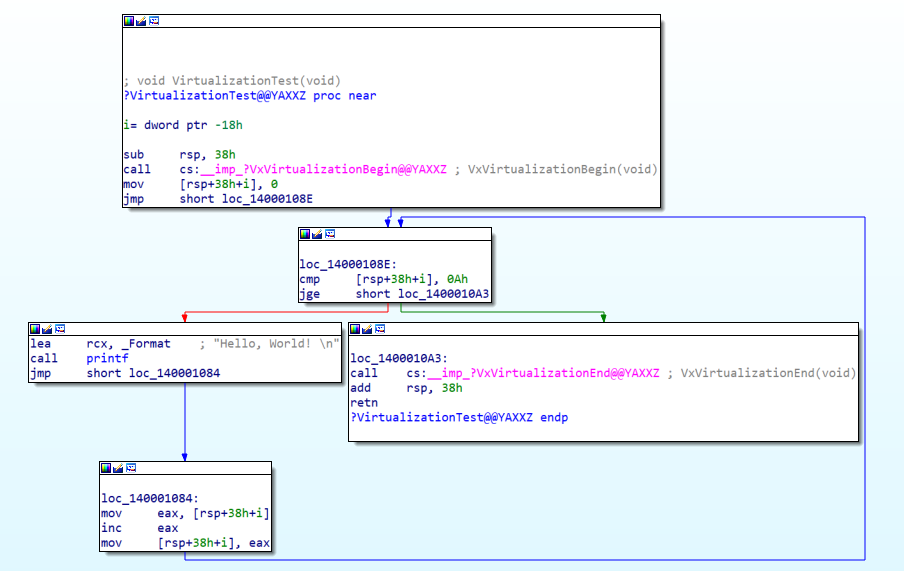
Before
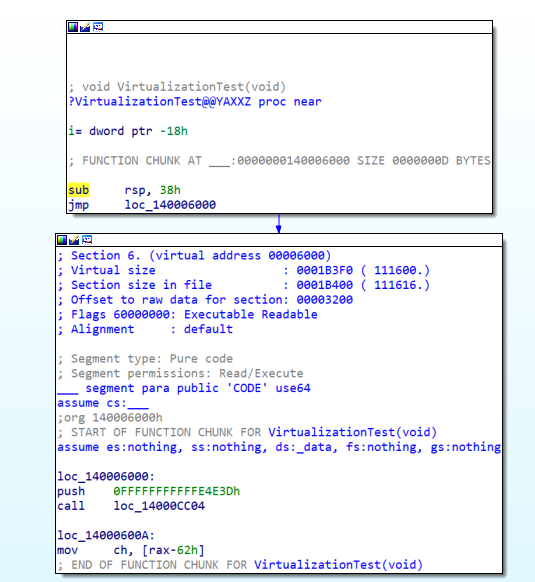
After
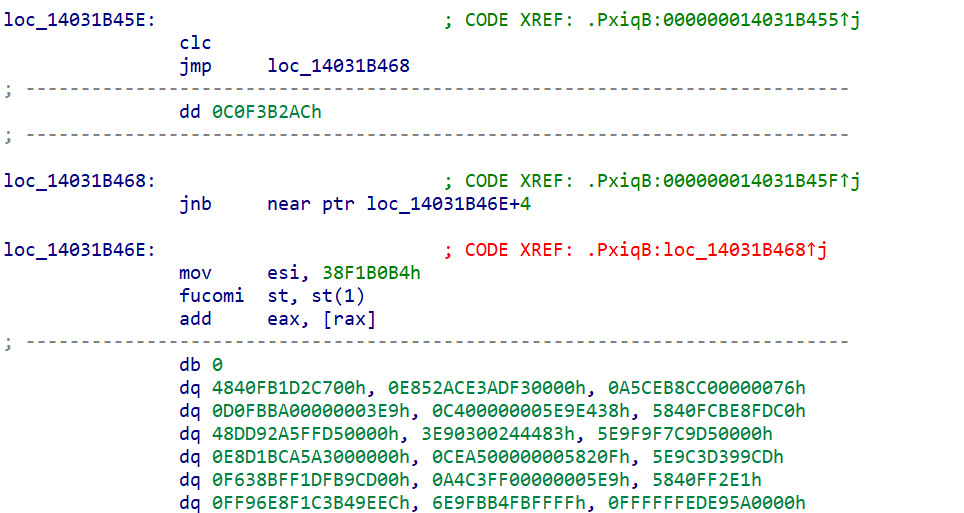
Preview
Before

After







