Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
Guardrails — Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask sensitive data. | Kitploit
工具/GitHubGitHub/nvidia-nemo/guardrails
Defensive ToolsVulnerability AnalysisPrivacyMachine LearningAI SecurityAnomaly DetectionAI Security 分类第 10 名
GitHubnvidia-nemo/guardrails

Guardrails

Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask sensitive data.

7.5k9031729小时48分前Kitploit 审核通过
分享
查看仓库
网站
内容在请求的语言中不可用。显示英文版本。

NVIDIA NeMo Guardrails Library

License PyPI Python Tests/Linux Tests/Windows Tests/macOS Lint Documentation Total downloads Monthly downloads

Documentation · Quickstart · Use cases · Integrations · Guardrail catalog · Examples · Community · Security · Releases · Changelog

NeMo Guardrails is an open-source library for applying programmable safety and security controls to LLM and agentic applications. Agents run commands, call APIs, query your data, and read the web. Conversational applications apply input and output checks; retrieval-augmented generation (RAG) systems filter retrieved content and check answers against evidence.

You use the NeMo Guardrails library to declare what each agent may do in a policy, combining low-latency local rules with model-backed checks for jailbreaks, injected instructions, and unsafe tool calls. Your application or agent harness runs these checks and uses their results to decide whether to continue.

pip install nemoguardrails

Requires Python 3.11–3.13. Refer to the installation guide for optional packages and setup.

[!NOTE] Version 0.25.0 deprecates LLMRails, with removal planned no earlier than 0.27.0. Use Guardrails for new integrations and follow the migration guide.
What You Can Build

  • AI agents and coding assistants: Check proposed tool calls and returned results with tool rails, or connect an agent through the hooks server.
  • Conversational applications: Apply input and output checks.
  • Retrieval-augmented generation (RAG): Detect or mask sensitive data in retrieved content and check whether answers are grounded in evidence.

How It Works

  • Define your policy. Configure rails, models, and prompts in YAML. Use Python actions for custom logic.
  • Run the checks. Invoke rails at the points where your application needs a policy decision.
  • Read the result. Handle blocked or modified content before executing a tool or returning a response. You can also route generation through Guardrails.

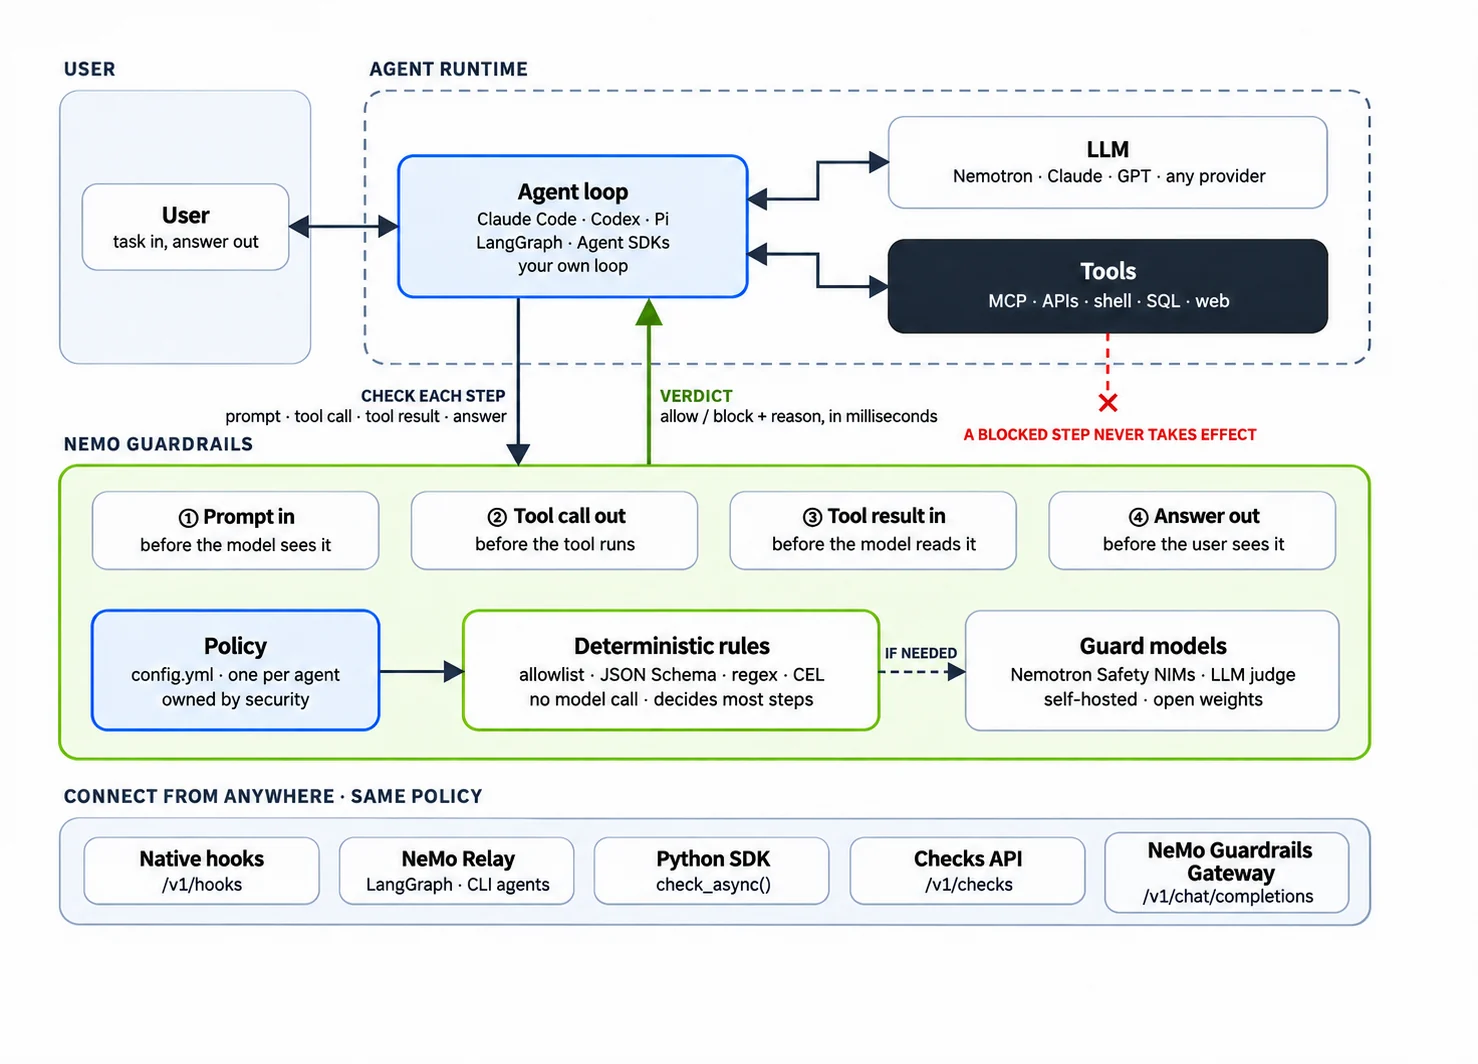
Agent runtime connected to NeMo Guardrails: configurable checks for prompts, tool calls, tool results, and answers, with policy rules, optional guard models, and integration options.

Tool-call checks run before execution, while tool-result checks run after the tool has executed. Latency depends on the configured rules, models, and services.

Integrations support different checks. Rail support varies by engine; refer to rail engine support and configuration.

Why NeMo Guardrails

  • Govern what agents do. Validate tool names and argument schemas before execution. Check tool results and apply per-tool policies before returning them to the model.
  • Keep your model and agent loop. Use checks without main-model generation to add guardrails to an existing application. Model-backed checks still call their configured model or service.
  • Compose the policy you need. Combine local regex and CEL rules with safety models and third-party checks.
  • Connect your runtime. Choose an integration for your application, shared service, or coding agent.
  • Open and yours to run. The library is Apache 2.0 licensed. Choose supported model providers and run checks with local detectors or hosted inference endpoints.

Quickstart

Check a support agent's proposed refund against a $500 limit, without a model or API key. Install the optional CEL extra for this example:

pip install "nemoguardrails[cel]"

The example validates the tool's argument schema and blocks calls over the limit. Expand it and save it as check_refund.py:

Complete Python example
import asyncio
import json

from nemoguardrails import Guardrails, RailsConfig
from nemoguardrails.rails.llm.options import RailStatus, RailType

config = RailsConfig.from_content(yaml_content="""
models: []
rails:
  tool_call:
    flows: [tool call validation]
    per_tool:
      issue_refund: [cel check tool call]
  config:
    cel:
      tool_call:
        issue_refund:
          expressions: ["args.amount > 500"]
""")

TOOLS = [{
    "type": "function",
    "function": {
        "name": "issue_refund",
        "parameters": {
            "type": "object",
            "properties": {"amount": {"type": "number", "minimum": 0}},
            "required": ["amount"],
            "additionalProperties": False,
        },
    },
}]

下载工具

最受欢迎

查看全部 →

发现我们社区最常用的工具。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 终极 OSINT 工具包:调查图谱、置信度评分、别名家族、地图、时间线和报告。49 个模块、400+ 个站点,无需 API 密钥。

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock 一键执行应用(CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    基于LLM的多智能体自主渗透测试平台,具备规划器/执行器智能体、资产与探索图谱、MITM流量记录以及漏洞复测功能。

    429
  • 4

    redforge

    cybersecurity91/redforge

    浏览器端红队工具包,包含 102 个离线工具,用于侦察、载荷生成、凭据攻击、加密、编码和交战报告。

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI原生网络安全的行动系统——在这里,意图转化为受治理的执行,证据沉淀为运营记忆,每一次操作都让下一次更出色。

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT 平台,可将 Shadowserver 报告导入 MongoDB,并将其重放为交互式地图、分析、发现、公告和高管仪表板。

    256

探索所有工具

浏览我们的工具集合

查看所有工具 →