
 ncsc-nl/php2shell
Operational advisory repository tracking CVE-2026-109618 and CVE-2026-109619 PHP RCE flaws, with detection and mitigation guidance, affected software inventories, and vendor status updates.

Operational information: 28 October 2026 16:46 CET
Software list last status update: 12 November 2026 08:56 CET
This repository contains operational information regarding the critical PHP vulnerabilities tracked by CERT-EU as CVE-2026-109618 and CVE-2026-109619.
PHP is a widely used open-source server-side scripting language, so these vulnerabilities may affect a broad range of internet-facing web applications and products that embed or depend on PHP.
This repository tracks 972 products, including 212 vulnerable and 213 fixed.
On 21 October 2026, PHP published fixed releases for CVE-2026-109618 and CVE-2026-109619: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP states that both vulnerabilities can allow unauthenticated remote code execution and that all PHP installations serving web requests are at risk, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. PHP considers the risk highest for mod_php, where an unauthenticated request can trigger exploitation before application code runs.
PHP describes CVE-2026-109618 as remote code execution via out-of-memory corruption during request cleanup, and CVE-2026-109619 as remote code execution via stale request-owned global state reused by a later request on the same worker. PHP 8.1 and older are no longer supported by the PHP project; distributions and LTS vendors may provide backported packages, and PHP has published minimal source backports for PHP 7.4, 8.0 and 8.1.
On 23 October 2026, PHP published an informational advisory suggesting session.upload_progress.enabled=0 until the next regular bugfix release to fully protect from an unlikely RCE vector (CVE-2026-115560). PHP will publish a full advisory with the next release; this repository does not track CVE-2026-115560 separately in the software list.
The impact is not limited to websites: PHP is also embedded in appliances, network devices, management interfaces and other vendor products where administrators may not be able to update PHP directly.
session.upload_progress.enabled=0 until the next regular PHP bugfix release (PHP informational advisory of 23 October 2026, CVE-2026-115560), unless your application needs the feature and never changes session.serialize_handler at runtime.session.upload_progress, restarting workers, and reviewing the official memory_limit, post_max_size and PHP 8.5 fatal_error_backtraces guidance. PHP states that these measures are not complete fixes.For additional information see:
| Directory | Purpose |
|---|---|
| detection_mitigation | Contains detection and mitigation material for the vulnerabilities. |
| software | Contains inventory lists of software products with a PHP dependency potentially affected by the vulnerabilities. |
| tools | Contains tools for using/generating files within this repo |
| Community contributions | Community tools, tips, guides, and reference resources. |
The repository is being updated as the situation develops. Check back for updates.
Statistics as of 2026-11-12 (UTC), from the current SPDX inventory.
| Products tracked | Fixed | Vulnerable | Under investigation | Runtime-dependent | Not affected | Unassessed / unknown |
|---|---|---|---|---|---|---|
| 972 | 213 | 212 | 92 | 240 | 214 | 1 |
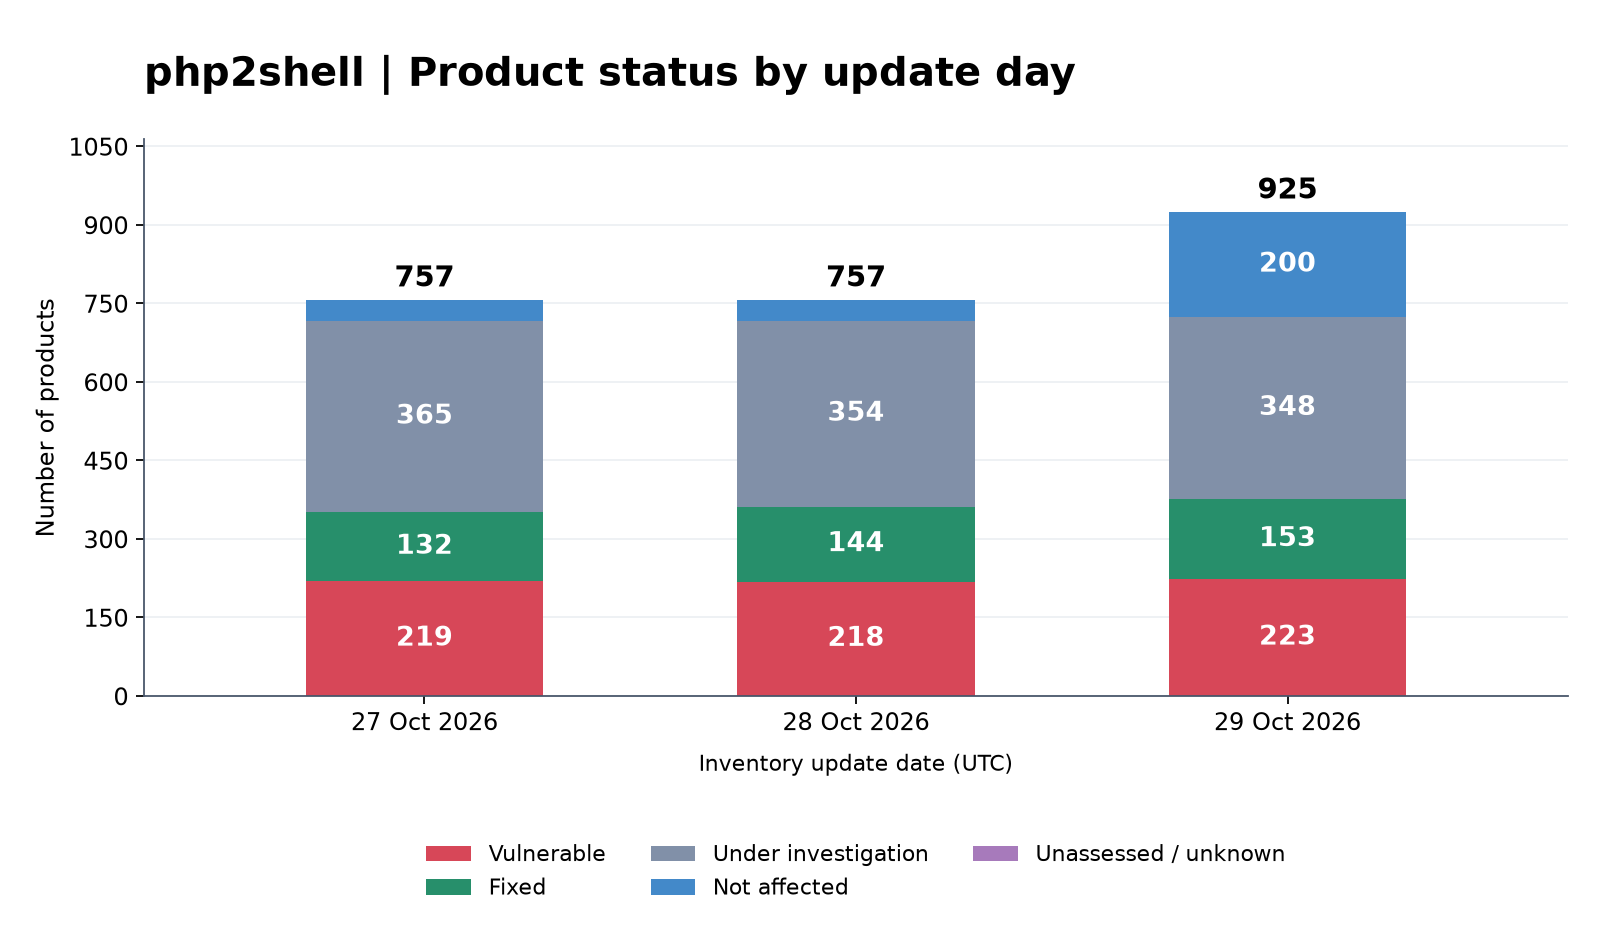
Counts by update day and per-CVE statistics (JSON) | Software list
| Date and time | Supplier | Product | Version (see Status) | Status CVE-2026-109618 / CVE-2026-109619 | Links |
|---|---|---|---|---|---|
| 2026-11-12 08:56:41 +0100 | Cisco | Cisco Ultra-Reliable Wireless Backhaul (URWB) | 26.2.1.9 | Fix | source |
| 2026-11-12 08:56:41 +0100 | Cisco | Cisco Unified Industrial Wireless Software | 26.2.1.9 | Fix | source |
| 2026-11-12 08:56:41 +0100 | Oro Inc. | OroCommerce on OroCloud managed environments | Managed environments patched 2026-10-22 | Fix | source |
| 2026-11-12 08:56:41 +0100 | QNAP | QNAP QNE (ADRA) | 1.0.7.q327 | Fix | source 1 source 2 source 3 |
| 2026-11-12 08:56:41 +0100 | Trend Micro | Apex Central 2019 (Japanese Windows release) | Critical Patch build 7351 (Japanese Windows) | Fix | source 1 source 2 source 3 source 4 |
See the full software status update history.






