mandiant/capa
基于规则的静态和动态分析工具,可识别PE、ELF、.NET和shellcode文件中的功能,并将其映射到MITRE ATT&CK技术,用于恶意软件分类。
capa 能够检测可执行文件中的能力。 你针对一个 PE、ELF、.NET 模块、shellcode 文件或沙箱报告运行它,它就会告诉你它认为该程序能够做什么。 例如,它可能会指出该文件是一个后门、能够安装服务、或依赖 HTTP 进行通信。
要交互式地在浏览器中查看 capa 结果,请使用 capa Explorer Web。
如果你想查看或编写 capa 规则,请前往 capa-rules 仓库。否则,请继续阅读。
下面你可以找到 我们关于 capa 的博客文章列表,其中包含更多细节。
$ capa.exe suspicious.exe
+--------------------+------------------------------------------------------------------------+ | ATT&CK Tactic | ATT&CK Technique | |--------------------+------------------------------------------------------------------------| | DEFENSE EVASION | Obfuscated Files or Information [T1027] | | DISCOVERY | Query Registry [T1012] | | | System Information Discovery [T1082] | | EXECUTION | Command and Scripting Interpreter::Windows Command Shell [T1059.003] | | | Shared Modules [T1129] | | EXFILTRATION | Exfiltration Over C2 Channel [T1041] | | PERSISTENCE | Create or Modify System Process::Windows Service [T1543.003] | +--------------------+------------------------------------------------------------------------+
+-------------------------------------------+-------------------------------------------------+ | CAPABILITY | NAMESPACE | |-------------------------------------------+-------------------------------------------------| | read and send data from client to server | c2/file-transfer | | execute shell command and capture output | c2/shell | | receive data (2 matches) | communication | | send data (6 matches) | communication | | connect to HTTP server (3 matches) | communication/http/client | | send HTTP request (3 matches) | communication/http/client | | create pipe | communication/named-pipe/create | | get socket status (2 matches) | communication/socket | | receive data on socket (2 matches) | communication/socket/receive | | send data on socket (3 matches) | communication/socket/send | | connect TCP socket | communication/socket/tcp | | encode data using Base64 | data-manipulation/encoding/base64 | | encode data using XOR (6 matches) | data-manipulation/encoding/xor | | run as a service | executable/pe | | get common file path (3 matches) | host-interaction/file-system | | read file | host-interaction/file-system/read | | write file (2 matches) | host-interaction/file-system/write | | print debug messages (2 matches) | host-interaction/log/debug/write-event | | resolve DNS | host-interaction/network/dns/resolve | | get hostname | host-interaction/os/hostname | | create process | host-interaction/process/create | | create registry key | host-interaction/registry/create | | create service | host-interaction/service/create | | create thread | host-interaction/thread/create | | persist via Windows service | persistence/service | +-------------------------------------------+-------------------------------------------------+
# 下载与使用
在[这里](https://github.com/mandiant/capa/releases)下载独立的capa二进制文件的稳定版本。你可以直接运行这些独立二进制文件,无需安装。capa是一个命令行工具,应从终端运行。
要将capa用作库或与其他工具集成,请参阅[doc/installation.md](https://github.com/mandiant/capa/blob/master/doc/installation.md)获取进一步的设置说明。
**文档:** [用法与技巧](https://github.com/mandiant/capa/blob/master/doc/usage.md) · [安装](https://github.com/mandiant/capa/blob/master/doc/installation.md) · [局限性](https://github.com/mandiant/capa/blob/master/doc/limitations.md) · [常见问题](https://github.com/mandiant/capa/blob/master/doc/faq.md)
# capa Explorer Web
[capa Explorer Web](https://mandiant.github.io/capa/explorer/) 使您能够在Web浏览器中交互式地探索capa结果。除了在线版本外,您还可以下载独立的HTML文件用于本地离线使用。
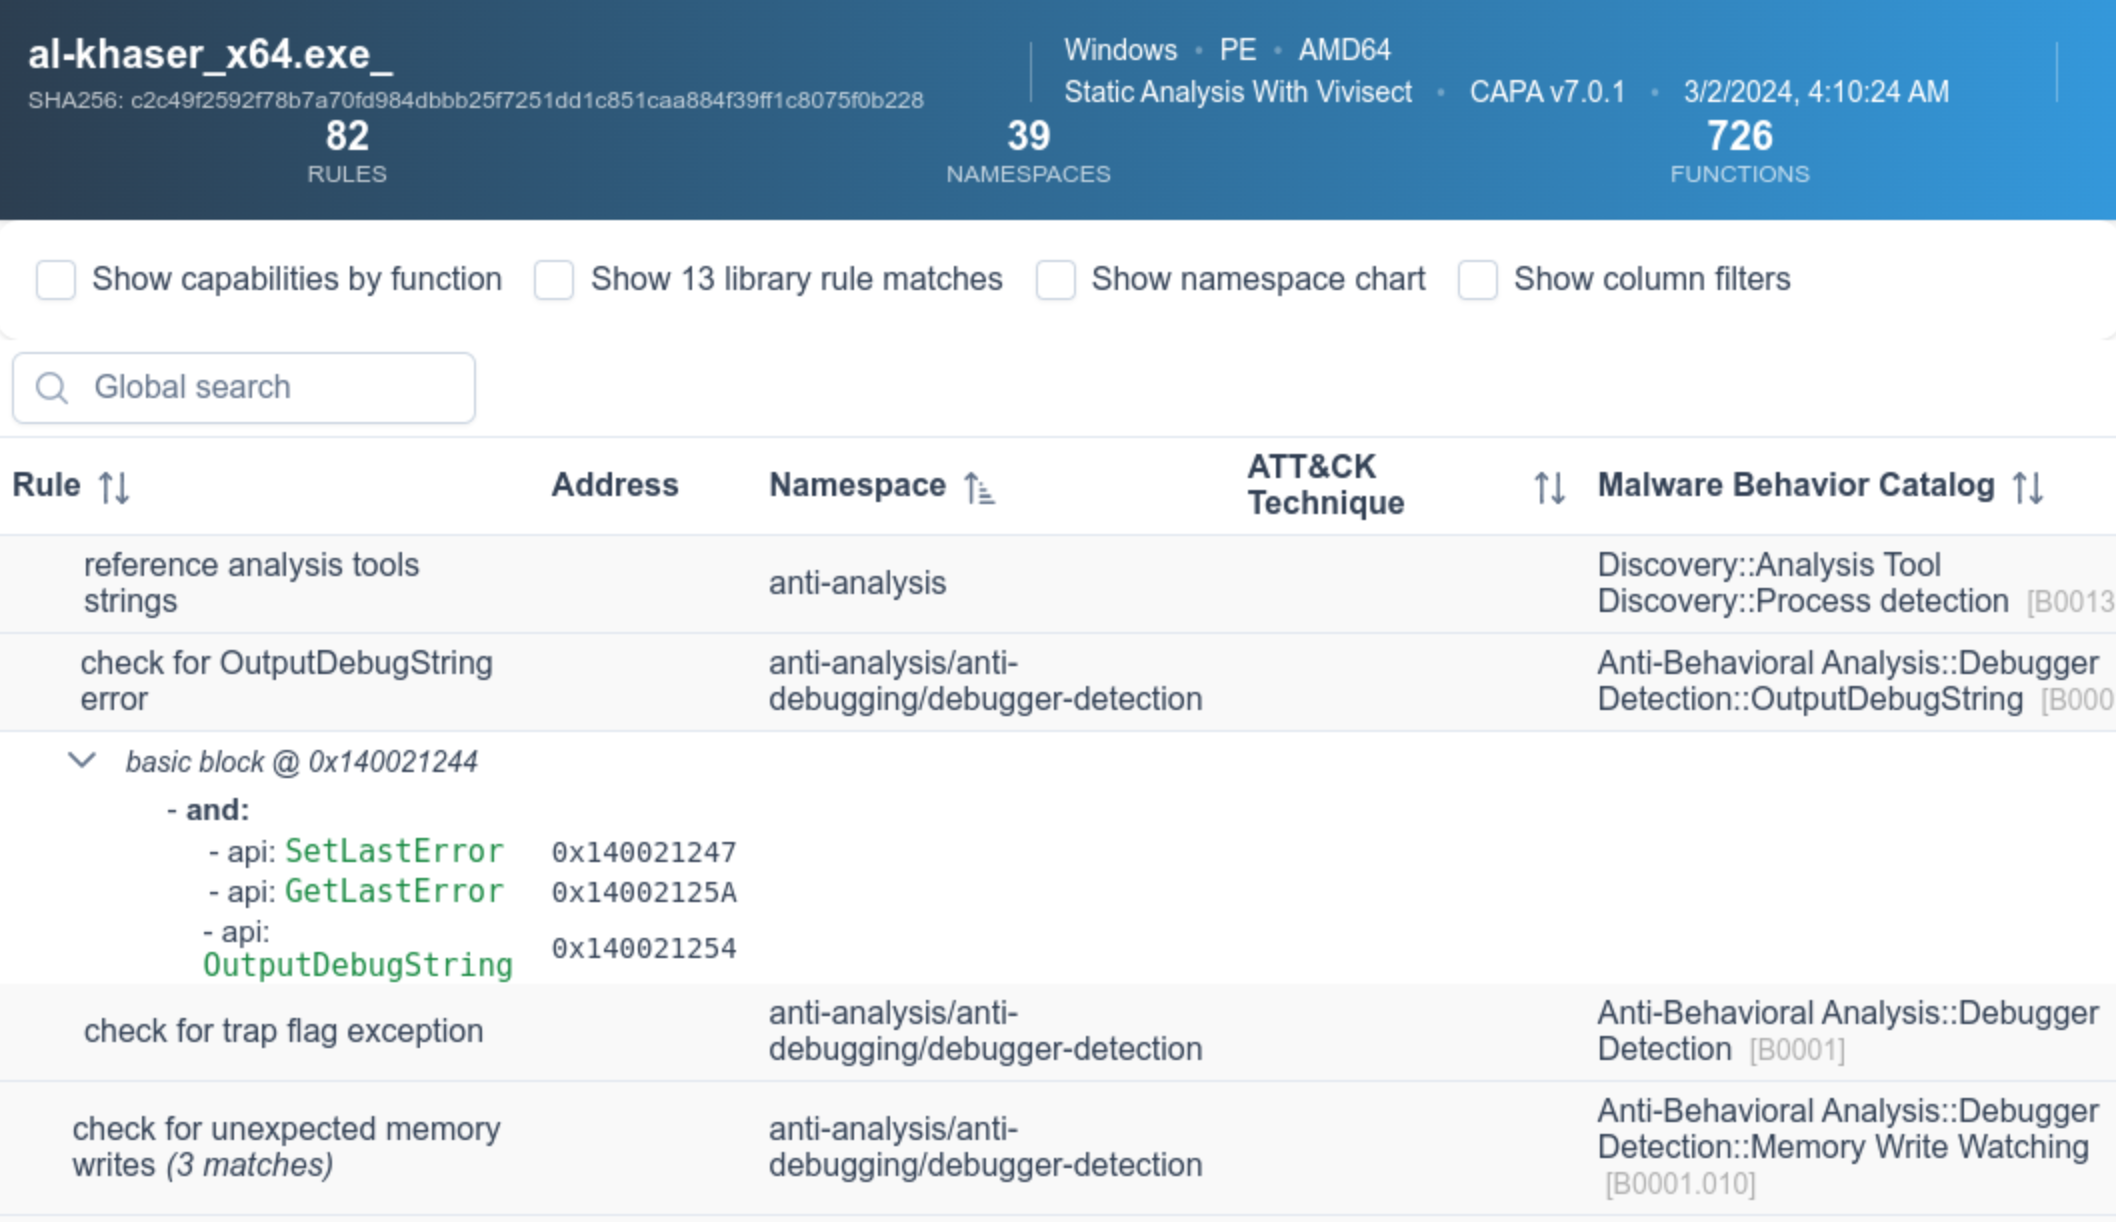
关于Web UI的更多细节,请参阅[capa Explorer Web README](https://github.com/mandiant/capa/blob/master/web/explorer/README.md)。
# 示例
在上面的示例输出中,我们对一个未知二进制文件(`suspicious.exe`)运行capa,该工具报告该程序可以发送HTTP请求、通过XOR和Base64解码数据、安装服务以及产生新进程。综合来看,这让我们认为`suspicious.exe`可能是一个持久化后门。因此,我们的下一步分析可能是将`suspicious.exe`放入沙盒中运行,并尝试恢复命令与控制服务器。
## 详细结果
通过传递`-vv`标志(用于非常详细模式),capa会精确报告它在何处发现这些能力的证据。这至少有两个好处: