 karib0u/rustinel
Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required.

Open-source endpoint detection. Three platforms. Your rules.
Run Sigma, YARA, and IOC detections on native Windows, Linux, and macOS telemetry.
Written in Rust, with local alerts and no cloud account required.


Download | Documentation | Detection packs | Website

rustinel sigma doctor explains which rules can fire, while rustinel doctor reports runtime health and events dropped under load.Install into a local rustinel folder, then start it.
Linux (kernel 5.8+):
curl -fsSL https://rustinel.io/install.sh | sh
cd rustinel && sudo ./rustinel run
Windows, in an elevated PowerShell:
irm https://rustinel.io/install.ps1 | iex
Set-Location rustinel; .\rustinel.exe run
macOS (experimental) needs Full Disk Access first, see macOS permissions:
curl -fsSL https://rustinel.io/install.sh | sh
cd rustinel && sudo ./rustinel run
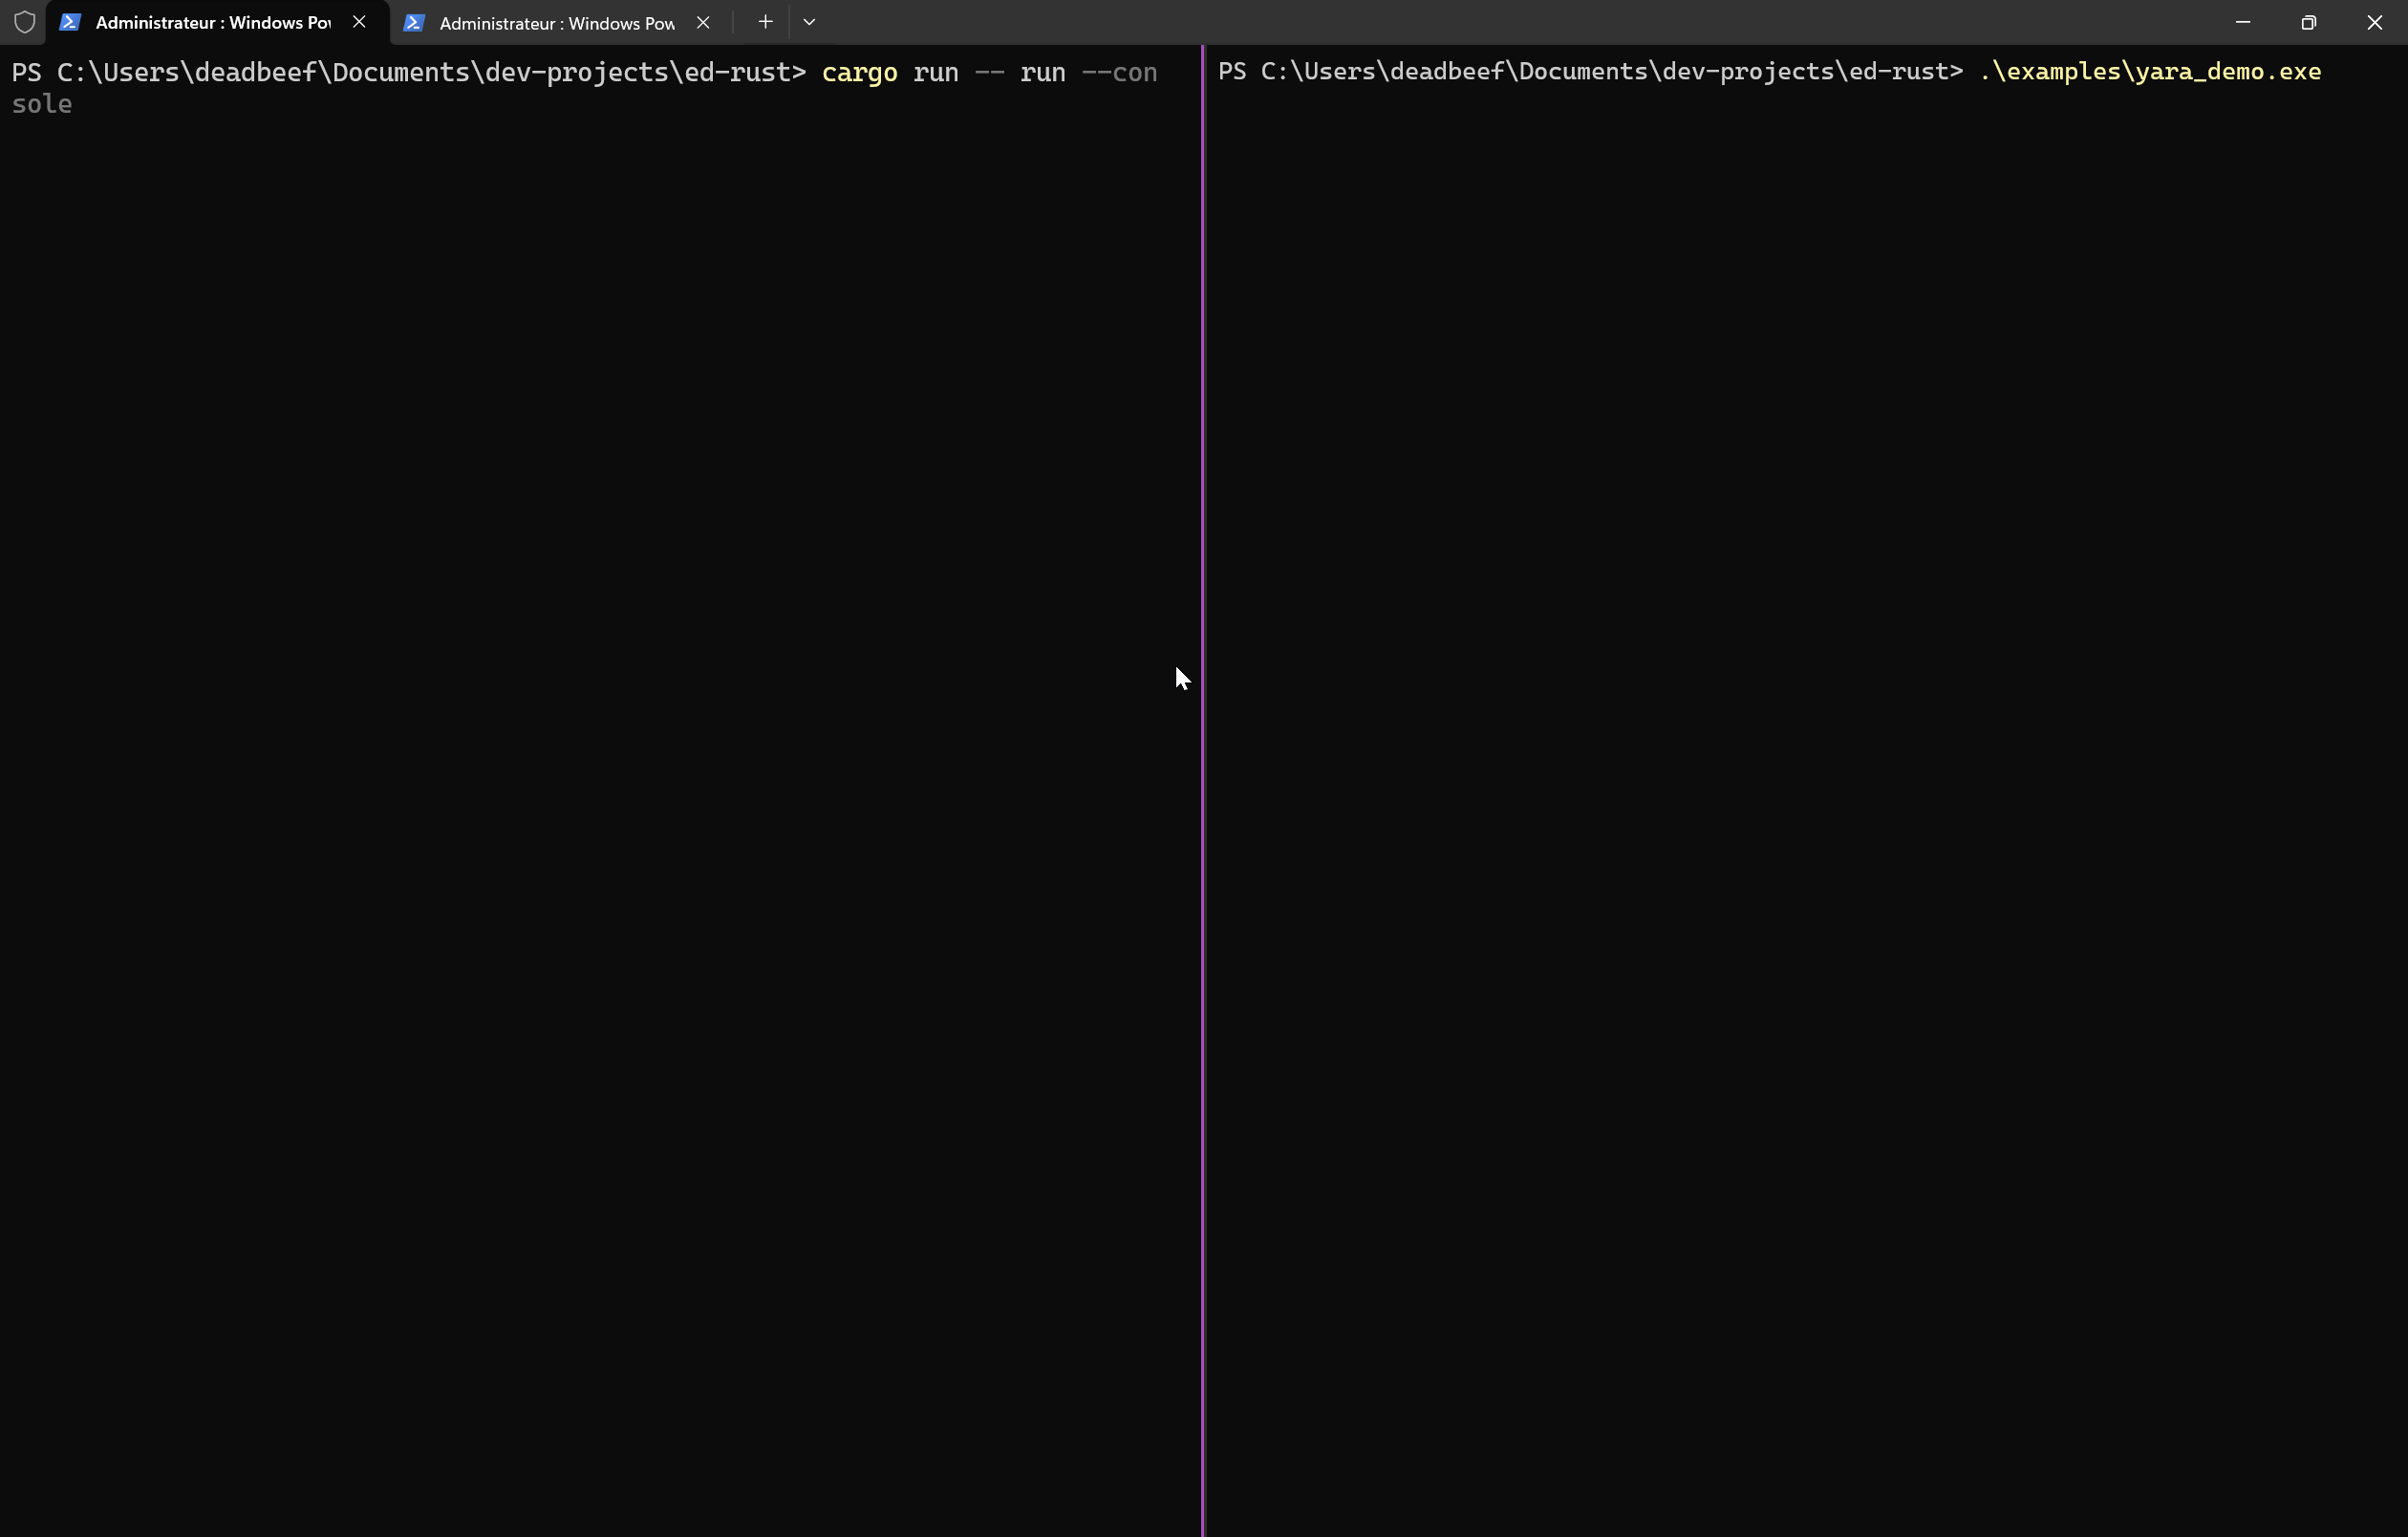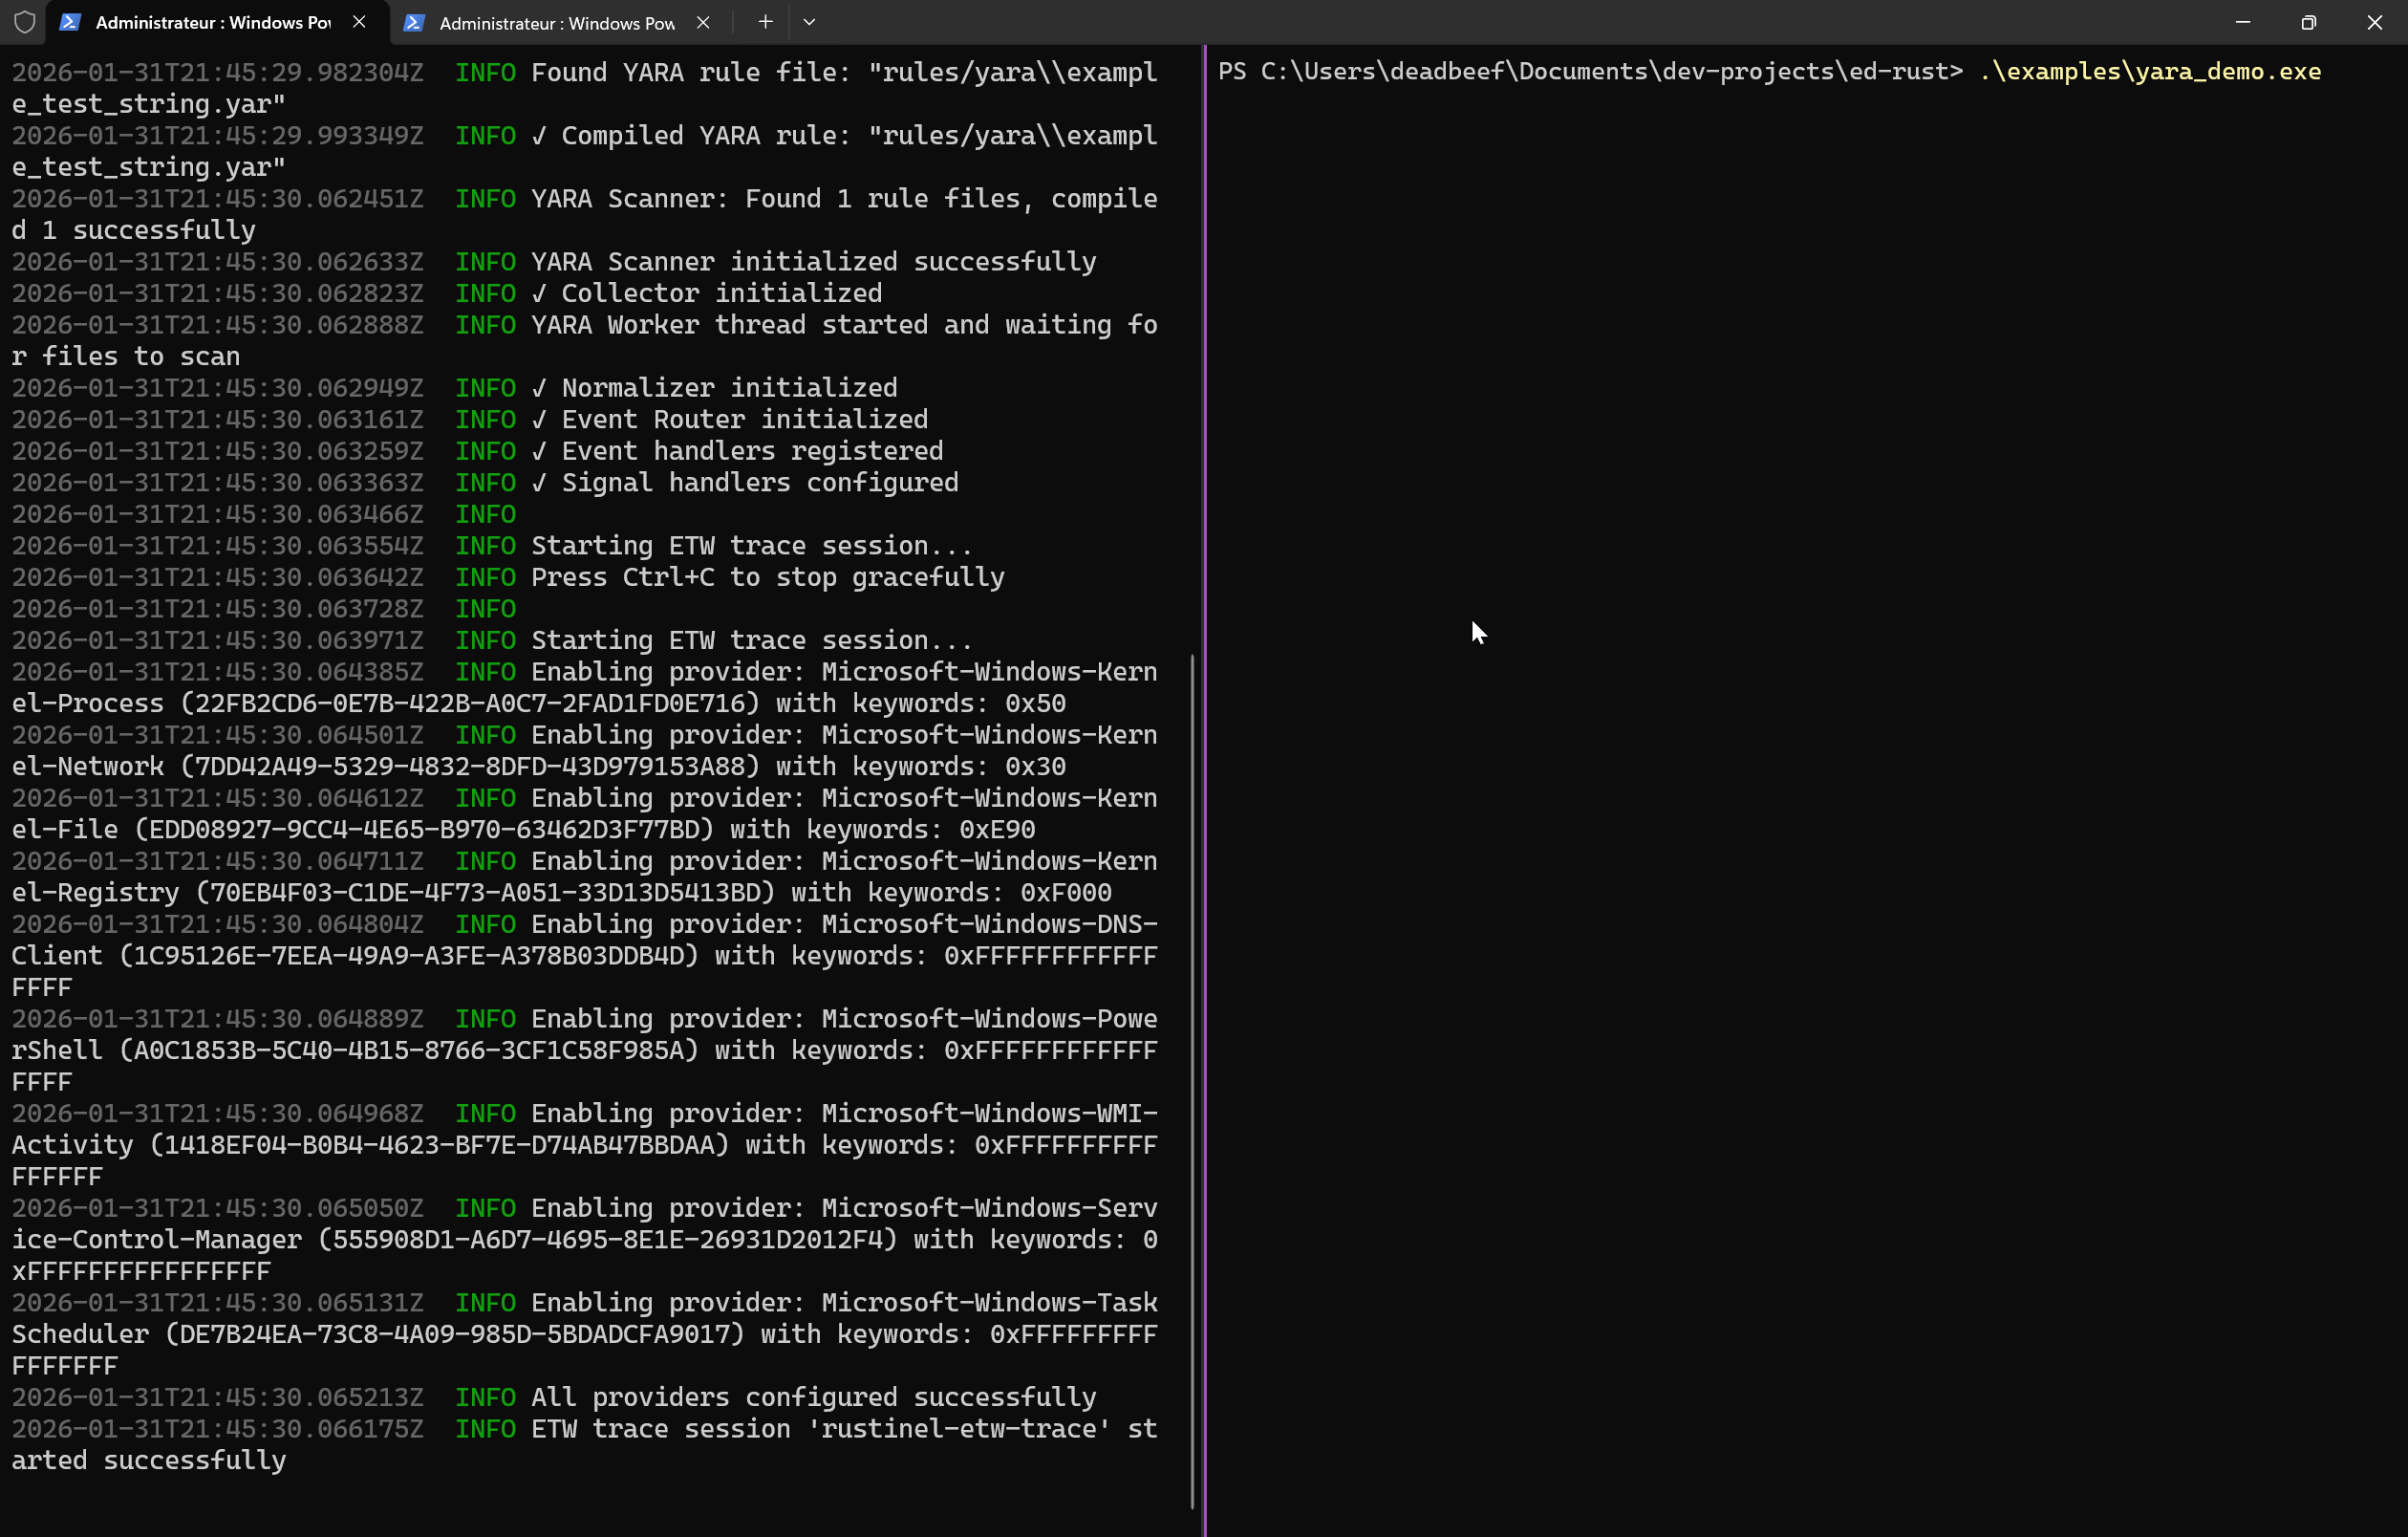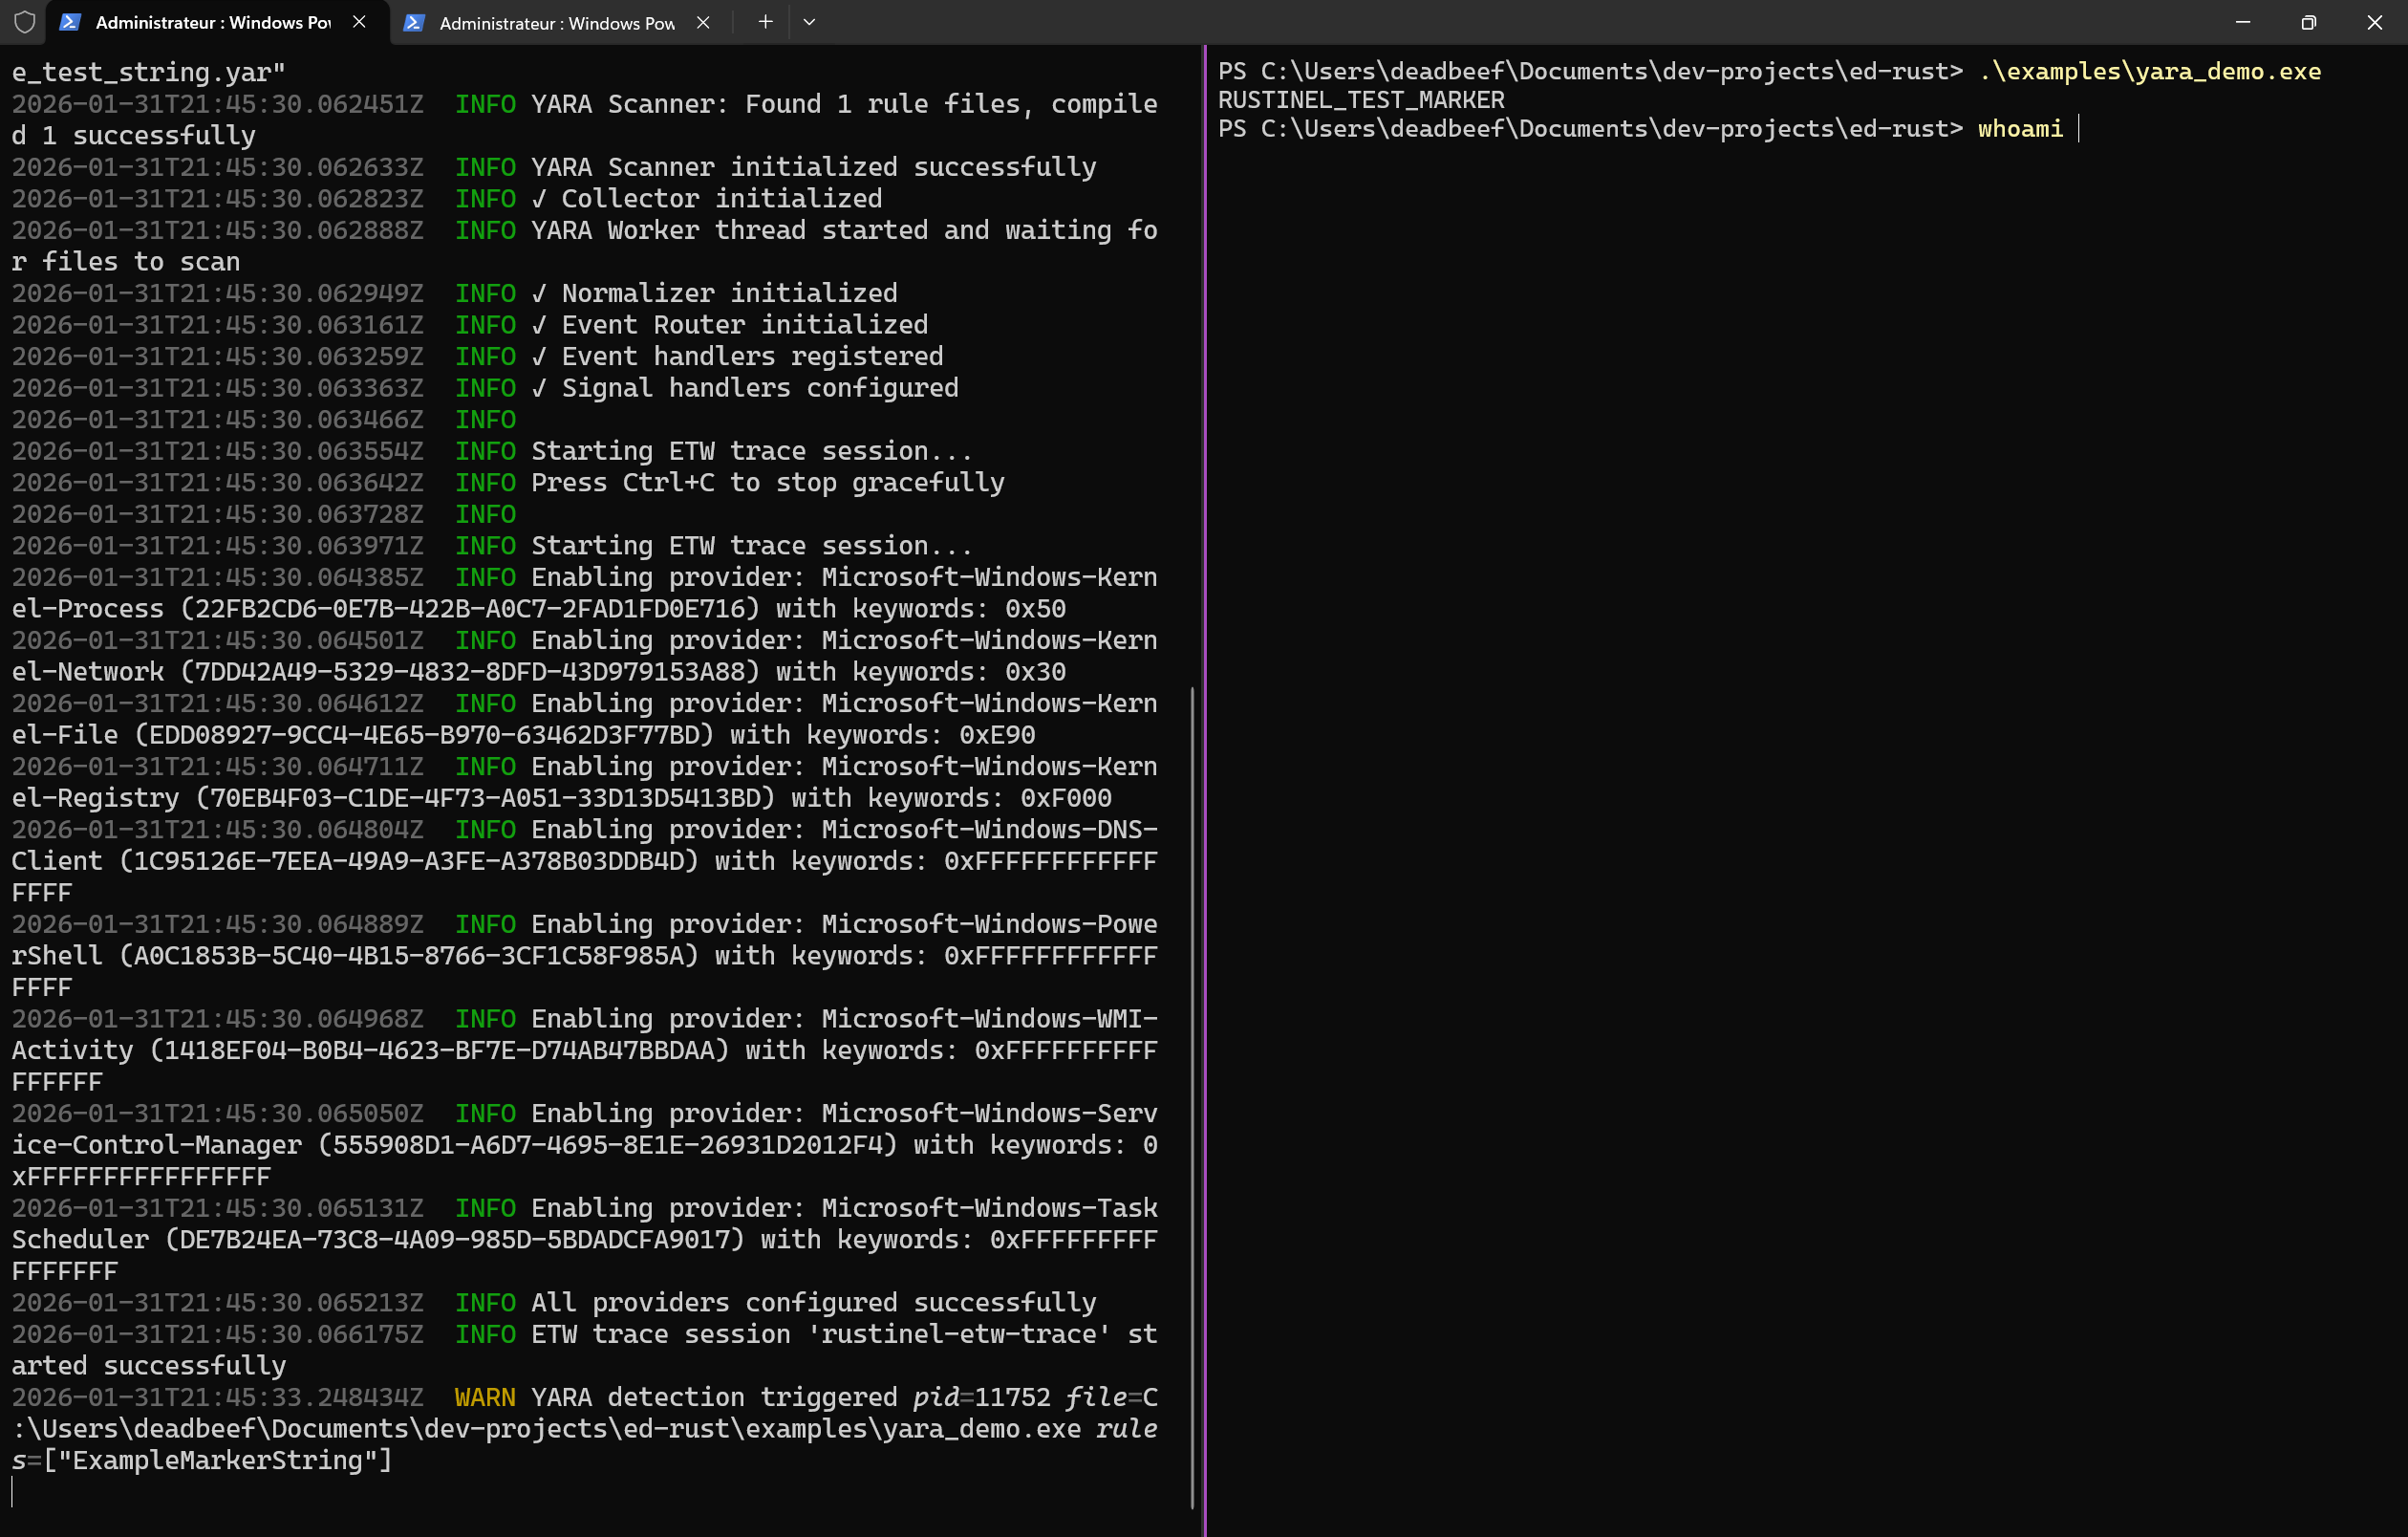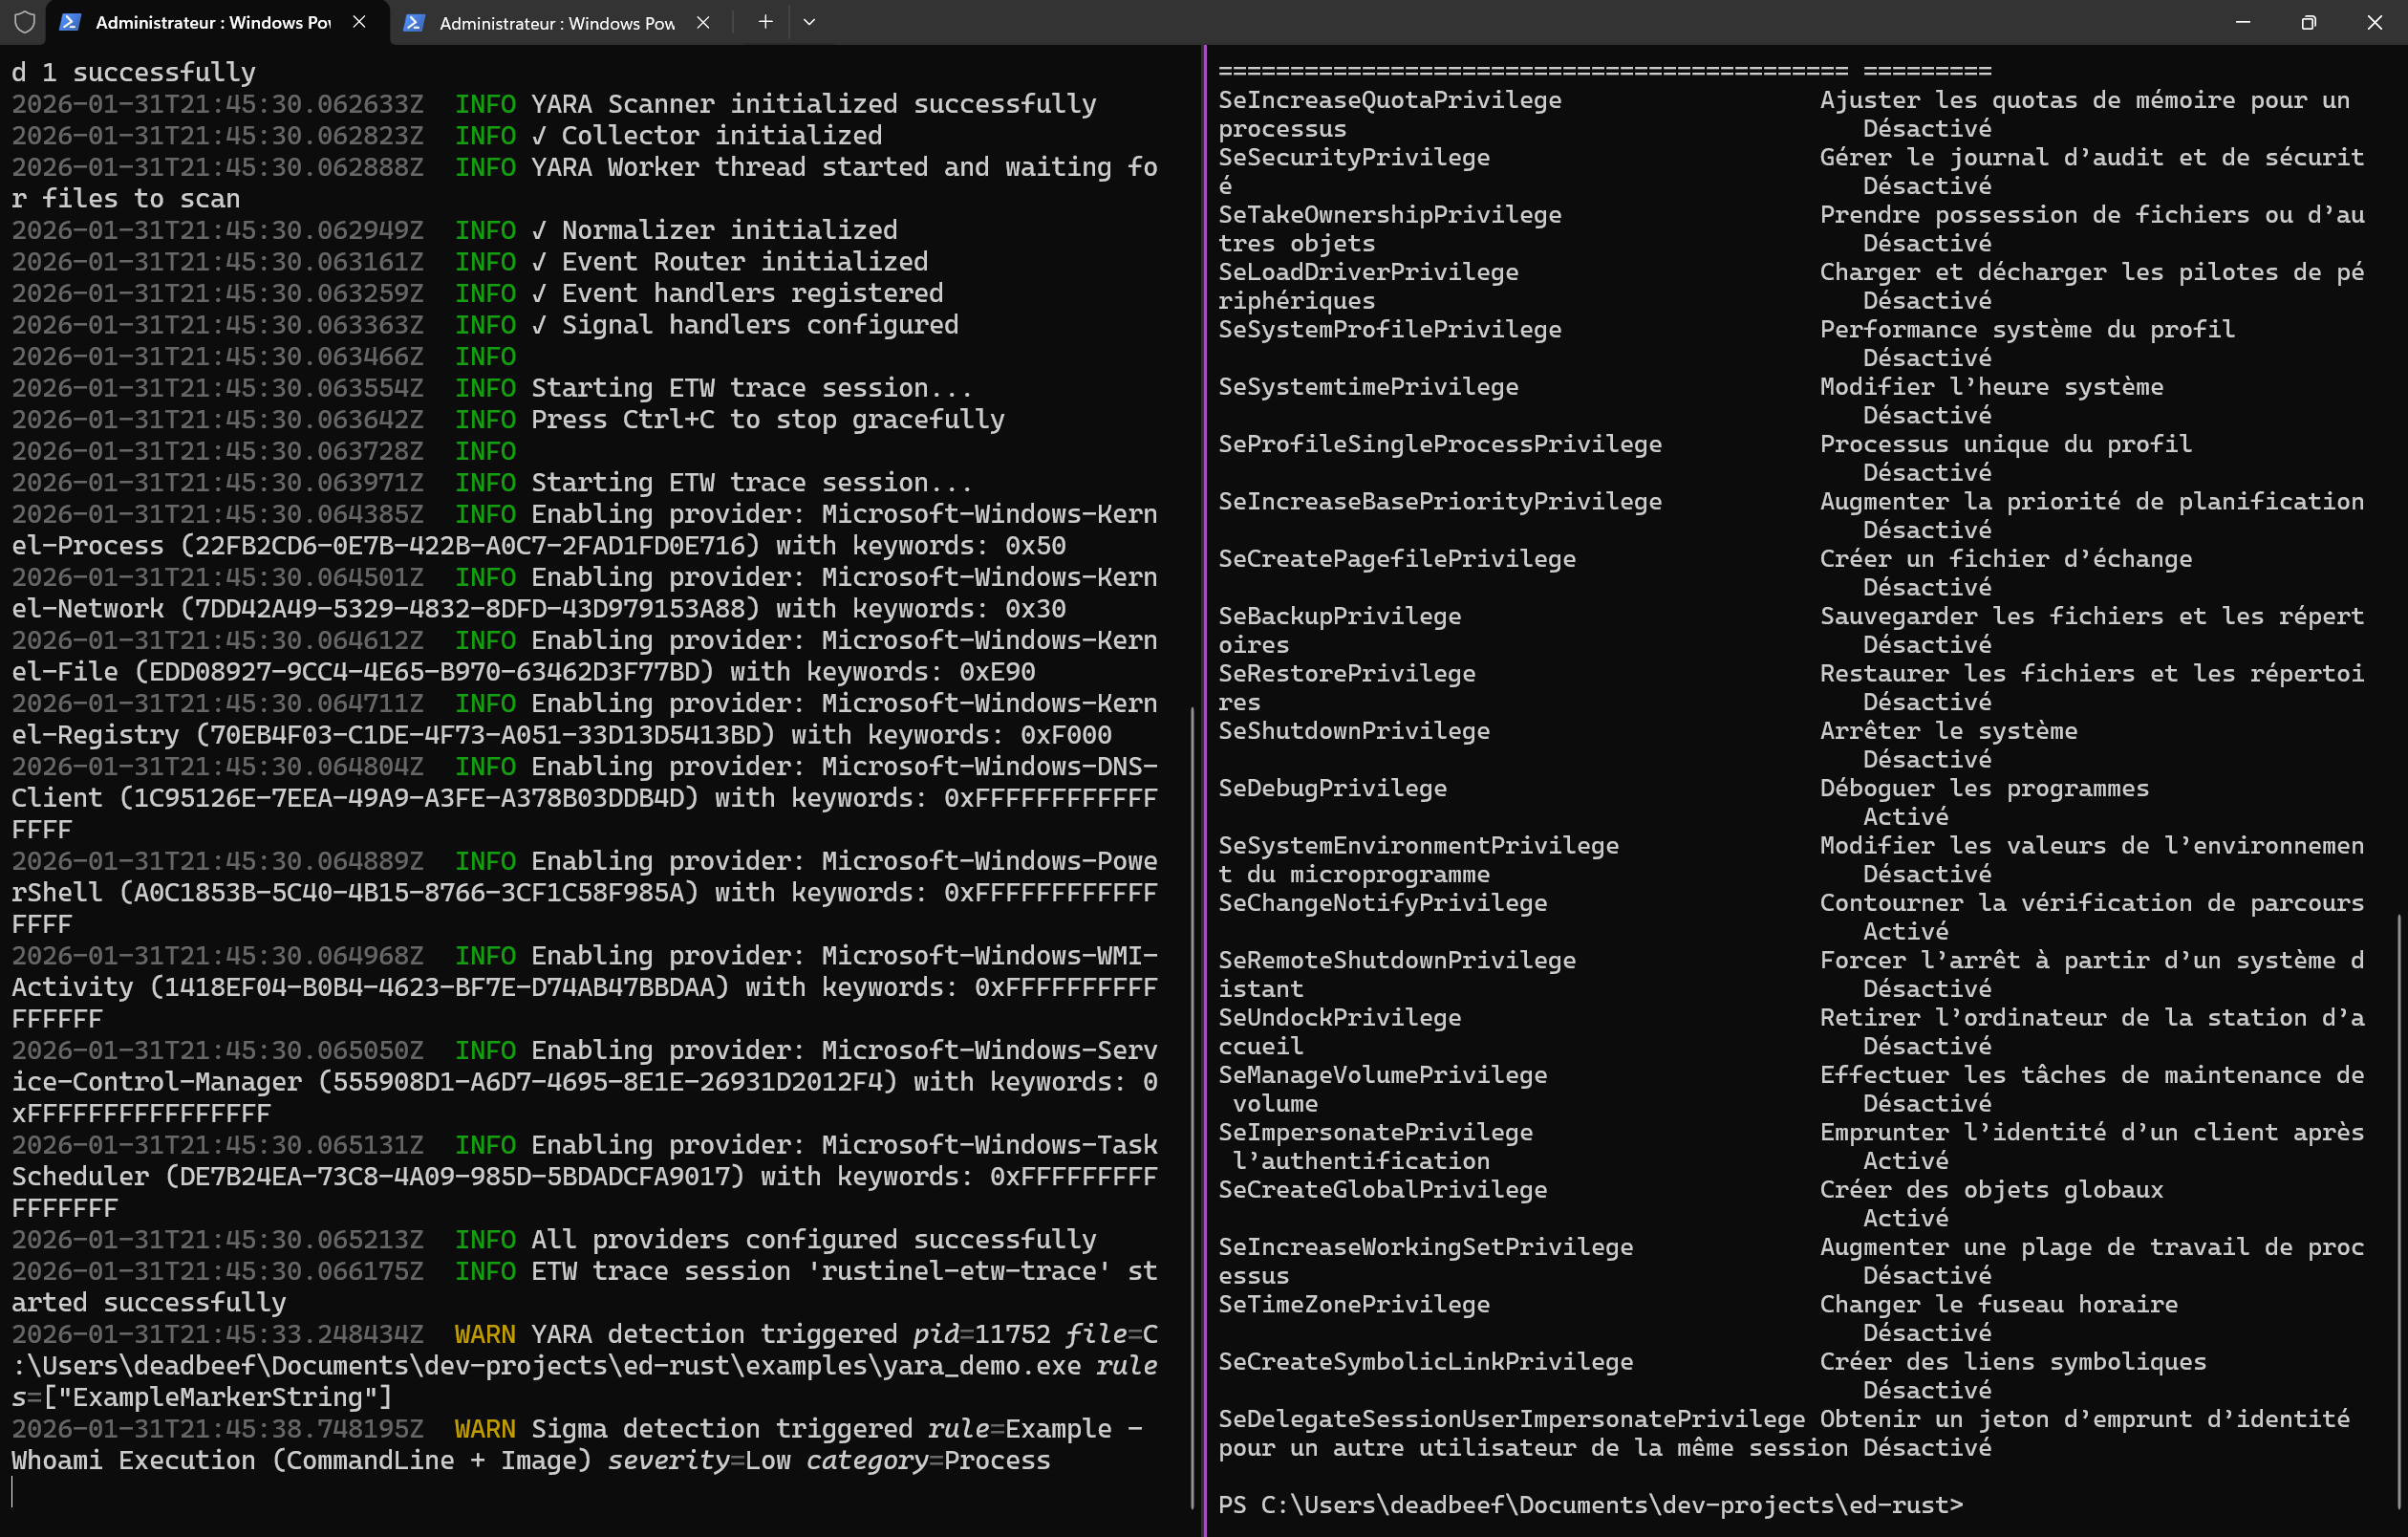
Run whoami in another terminal.
The demo rule fires and the alert lands in rustinel/logs/alerts.json.<date>.
To install it as a service with a real rules pack, stop it with Ctrl-C and run sudo ./rustinel setup --yes from the rustinel folder (.\rustinel.exe setup --yes on Windows).
See Deploy on an endpoint.
sudo ./rustinel capture --output ~/captures/session.ndjson   # Ctrl-C when done
sudo chown -R "$USER" ~/captures
./rustinel replay ~/captures/session.ndjson
./rustinel replay ~/captures/session.ndjson --config candidate.toml
Replay needs no privileges and works across platforms: a Windows recording replays on Linux. See Test rules with replay.
| Platform | Sensors | Telemetry | Status |
|---|---|---|---|
| Windows 10/11, Server 2016+ | ETW + Windows Event Log | Process, image load, network, file, registry, DNS, PowerShell, WMI, service, task, Security audit events | Stable |
| Linux 5.8+ | eBPF | Process, network, file, DNS | Stable |
| macOS 11+ | Endpoint Security + /dev/bpf | Process, file, network, DNS | Experimental |
Details: Platform coverage and Limitations.
Rustinel is built for endpoint monitoring, detection engineering, labs, and SIEM pipeline testing. It is not a replacement for a commercial EDR: it has no anti-tamper, no pre-execution blocking, and no management console. See the Security model.
Free code signing for the Windows binary is provided by SignPath.io, certificate by SignPath Foundation. See the Code signing policy for roles and privacy.
Bug reports, detection tests, and platform work are welcome. Tell us what you monitor and where you get stuck.
Contributing | Issues | Development guide | Roadmap






