

基于规则的Android恶意软件评分引擎,通过静态和动态分析APK,检测漏洞、识别恶意软件家族并生成详细威胁报告。
<p align="center">
    <a href="https://www.blackhat.com/asia-24/arsenal/schedule/index.html#quark-script---dig-vulnerabilities-in-the-blackbox-37549">
        <img alt="Black Hat Arsenal" src="https://img.shields.io/badge/Black%20Hat%20Arsenal-Asia%202024-blue">
    </a>
    <a href="https://www.blackhat.com/asia-21/arsenal/schedule/index.html#quark-engine-storyteller-of-android-malware-22458">
        <img alt="Black Hat Arsenal" src="https://img.shields.io/badge/Black%20Hat%20Arsenal-Asia%202021-blue">
    </a>
    <a href="https://conference.hitb.org/hitb-lockdown002/sessions/quark-engine-an-obfuscation-neglect-android-malware-scoring-system/">
        <img alt="HITB" src="https://img.shields.io/badge/HITB-Lockdown%20002-red">
    </a>
    <a href="https://www.youtube.com/watch?v=XK-yqHPnsvc&ab_channel=DEFCONConference">
        <img alt="defcon" src="https://img.shields.io/badge/DEFCON%2028-BTV-blue">
    </a><br>
    <a href="https://github.com/quark-engine/quark-engine/actions/workflows/pytest.yml">
        <img alt="build status" src="https://github.com/quark-engine/quark-engine/actions/workflows/pytest.yml/badge.svg">
    </a>
    <a href="https://codecov.io/gh/quark-engine/quark-engine">
        <img alt="codecov" src="https://codecov.io/gh/ev-flow/quark-engine/graph/badge.svg">
    </a>
    <a href="https://github.com/18z/quark-rules/blob/master/LICENSE">
        <img alt="license" src="https://img.shields.io/badge/License-GPLv3-blue.svg">
    </a>
    <a href="https://www.python.org/downloads/release/python-31015/">
        <img alt="python version" src="https://img.shields.io/badge/python-3.10-blue.svg">
    </a>
    <a href="https://pypi.org/project/quark-engine/">
        <img alt="PyPi Download" src="https://pepy.tech/badge/quark-engine">
    </a><br>
    <a href="https://twitter.com/quarkengine">
        <img alt="Twitter" src="https://img.shields.io/twitter/follow/quarkengine?style=social">
    </a><br>
    <img src="https://assets.kitploit.com/production/public/readmes/6741/03a197011a23cc6c340ef8243156a4a8da0cb226daf3ea012a0d007029c48fa9.png"/>
</p>

## 恶意软件家族分析报告展示

<table>

  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/e14e7970a278faef3a85a6ceee30dd7681c8d7be6f16bc8fad16ff3230600bc1.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/72948195e3960572f7c23ff84362625375890339c5f75d651fe42d02e9ed1e95.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/1705305abf7957429991bf0cf5ba0bc619edc460604806451ecd0ddc8c464a23.png" width="310"></td>
  </tr>
  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/d94cb3d285cfcc850934be26d17b38c226bc671cddb707ce6597e399f2dca1de.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/2423f24f7933d1923794763e041bdb9d99027688f5f3254e73f7b36e79e3c00a.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/0035c5f69112d8097ee4ece87a8b0f05f28bc2dec6a8f8cec645138c4d0b5080.png" width="310"></td>
  </tr>
  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/f73f15ad9490c35e70dbea6a90acbd69b480103f9fcdc87440868c3f745c1450.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/c0628a03cbd744f7cb5077d27e9cf3b31e4e6faa11a480c729e6f66f1c9f9391.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/ff076c7dc8c384297783518dcec6861ef3de193f292724589759ab38c6717032.png" width="310"></td>
  </tr>
  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/d8a967c14e5b508626a281d50f008ab3a6422008231e9e7b3b6b8bbc0822afe5.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/eea1fde985ce1cbc5097045e39ed59a92b3c1b9defa920084d64764bd582b8f6.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/4e1ef70891c707c427030190d413c66e65183608abfc96d550c203ae7b121ead.png" width="310"></td>
  </tr>
  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/64d7d5044f1b2e2219507f765302a95313f04c19e81a10f5b7c0dd04ceb13a12.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/5a4348c3ee554e08cf1509923c29152a337b9c1e7f674b5d0f187feb8884b7f0.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/cf2ac808de2437476ff2b20e8178cd906614fe5daea9c3d56c57683c45f73558.png" width="310"></td>
  </tr>
  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/00a382b46e7116952deba2411f72d1eb3addd9d94a0f43cc28419c6e7728c4c0.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/fb3f3c0f39b14940edfc6ba133a0670a333e509b19d1e4c5d259621d8875eefb.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/6bc7b397dedd9d531ff7a4add4e97001ff5bfe6f78d0506de06b0f4352f65538.png" width="310"></td>
  </tr>
  <tr>
      <td><img src="https://assets.kitploit.com/production/public/readmes/6741/946a13c57e64267f069f0bd0ca98dba98216d014092dc0f09c5eadb060854986.png" width="310"></td>
  </tr>
</table>


| 家族名称 | 总结                                            | 特征行为                    | 报告 |
|-------------|----------------------------------------------------|--------------------------|--------|
| DroidKungFu | 通过C2控制实现权限提升。              | 1. 获取设备的无限制访问权限。<br>2. 安装/卸载其他应用。<br>3. 转发机密数据。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-droidkungfu) |
| GoldDream   | 通过远程C2命令窃取短信/通话记录。 | 1. 监控短信和电话。<br>2. 将短信和电话上传到远程服务器。              | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-golddream) |
| SpyNote     | 通过RAT窃取凭证并监控设备。  | 1. 截取屏幕截图。<br>2. 模拟用户手势。<br>3. 记录用户输入。<br>4. 与C2服务器通信。      | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-spynote) |
| DawDropper  | 释放器,用于安装银行木马以窃取金融信息。 | 1. 从远程服务器下载APK。<br>2. 安装额外的APK。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-dawdropper) |
| SLocker     | 锁定/加密设备的Android勒索软件。     | 1. 使用覆盖屏幕锁定设备。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-slocker) |
| PhantomCard | 基于NFC中继的金融欺诈。                   | 1. 与C2服务器通信。<br>2. 读取NFC卡支付数据。<br>3. 通过欺骗性屏幕捕获NFC卡PIN码。  | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-phantomcard) |
| ToxicPanda  | 银行木马,可实现设备内欺诈。     | 1. 滥用无障碍服务。<br>2. 远程设备控制。<br>3. 拦截OTP。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-toxicpanda) |
| Hydra       | 使用覆盖攻击的银行木马。        | 1. 覆盖层窃取凭证。<br>2. 滥用无障碍服务。<br>3. 窃取OTP/Cookie。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-hydra) |
| SharkBot    | 针对金融凭证和交易的银行木马。 | 1. 滥用无障碍服务。<br>2. 进行覆盖攻击以窃取凭证。<br>3. 拦截短信(OTP)。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-sharkbot) |
| Antidot     | 伪装成合法更新的银行木马,用于窃取金融数据。 | 1. 拦截短信(OTP)。<br>2. 记录用户输入(键盘记录)。<br>3. 通过C2实现远程控制。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-antidot) |
| Arsink      | 专注于窃取凭证和金融数据的银行木马。 | 1. 从设备窃取敏感数据。<br>2. 拦截短信(OTP)。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-arsink) |
| TrickMo     | 使用覆盖攻击和滥用无障碍服务窃取凭证的银行木马。 | 1. 覆盖攻击窃取银行凭证。<br>2. 拦截短信绕过双因素认证。<br>3. 屏幕录制和滥用无障碍服务。<br>4. 通过反射动态加载载荷。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-trickmo) |
| Anubis      | 具有RAT功能的银行木马。              | 1. 覆盖层窃取凭证。<br>2. 键盘记录。<br>3. 拦截短信(OTP)。<br>4. 通过C2远程控制。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-anubis) |
| GodFather  | 通过覆盖攻击和滥用无障碍服务针对金融凭证的银行木马。 | 1. 进行覆盖攻击以窃取凭证。<br>2. 滥用无障碍服务。<br>3. 拦截短信(OTP)。<br>4. 窃取银行凭证和敏感数据。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-godfather) |
| TangleBot   | 通过短信传播的Android恶意软件,窃取个人和金融数据。 | 1. 通过短信钓鱼链接传播。<br>2. 控制设备交互和覆盖屏幕。<br>3. 访问短信、联系人、通话记录、摄像头和麦克风。<br>4. 窃取账户和金融信息。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-tanglebot) |
| BRATA       | 具有远程控制和反分析能力的银行木马。 | 1. 进行覆盖攻击以窃取银行凭证。<br>2. 滥用无障碍服务实现设备控制。<br>3. 拦截短信(OTP)。<br>4. 执行恢复出厂设置或擦除设备命令。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#brata-malware-family-analysis-report) |
| Cerberus    | 通过覆盖攻击和设备控制针对金融凭证的银行木马。 | 1. 进行覆盖攻击以窃取凭证。<br>2. 滥用无障碍服务。<br>3. 记录用户输入(键盘记录)。<br>4. 通过C2远程控制。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#cerberus-malware-family-analysis-report) |
| SuperCardX  | 可实现非接触式支付欺诈的NFC中继恶意软件。 | 1. 读取NFC支付卡数据。<br>2. 将NFC交易中继到攻击者控制的设备。<br>3. 与C2服务器通信。<br>4. 促进未经授权的非接触式支付。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#supercardx-malware-family-analysis-report) |
| NGate       | 可实现中继攻击和支付欺诈的NFC恶意软件。 | 1. 读取NFC支付卡数据。<br>2. 将NFC通信中继到攻击者控制的设备。<br>3. 与C2服务器通信。<br>4. 促进未经授权的非接触式支付。 | [查看](https://quark-engine.readthedocs.io/en/latest/malware_report.html#ngate-malware-family-analysis-report) |

## 快速开始

### 步骤1. 通过PyPi安装
安装Quark Engine的最新版本:
```bash
$ pip3 install -U quark-engine
```

### 步骤2. 下载最新规则
获取最新的规则数据库:
```bash
$ freshquark
```

### 步骤3. 运行摘要报告
使用下载的规则分析APK并生成摘要报告:
```bash
$ quark -a <apk文件> -s
```
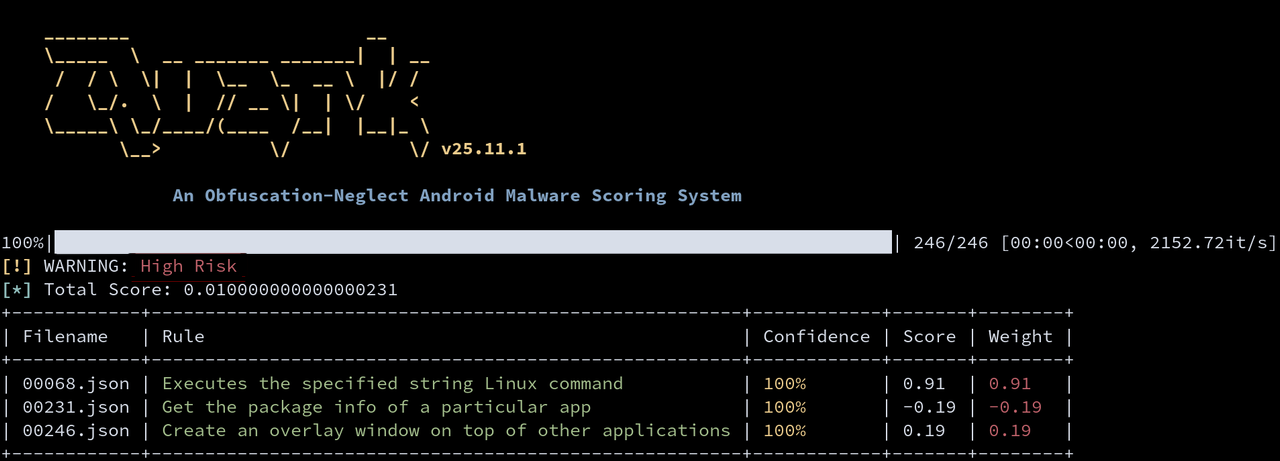
### 步骤4. 查看结果
示例输出:
<img width="1280" height="461" alt="Screenshot-2025-11-25-22-36-54" src="https://assets.kitploit.com/production/public/readmes/6741/896c831335911a2de27ffe4eaa7f501d0f1670432afde44c94df5f1a46b06bd1.png" />


## 致谢

### Honeynet项目

<a href="https://www.honeynet.org"> <img style="border: 0.2px solid black" width=115 height=150 src="https://assets.kitploit.com/production/public/readmes/6741/3434e2b0361550a5a1836ff81c009062d9e83ef7bb84cd53186cd9cd939252ed.png" alt="Honeynet.org logo"> </a>

### Google Summer Of Code

Quark-Engine已参与由Honeynet项目主持的GSoC!

*   2021:
    *   [YuShiang Dang](https://twitter.com/YushianhD): [新规则生成技术 & 让Quark遍布安全开源项目](https://github.com/ev-flow/ref/blob/main/GSoC-2021-YuShiangDang.md)
    *   [Sheng-Feng Lu](https://twitter.com/haeter525): [替换Quark-Engine的核心库](https://github.com/ev-flow/ref/blob/main/GSoC-2021-ShengFengLu.md)

敬请关注即将到来的GSoC!加入[Honeynet Slack聊天](https://gsoc-slack.honeynet.org/)获取更多信息。

## Quark Engine团队核心价值观

*   我们热爱**战场**。我们拥抱**不确定性**。我们挑战**不可能**。我们**重新思考**一切。我们改变人们的思维方式。而最重要的是,我们通过**先**利他来利己。