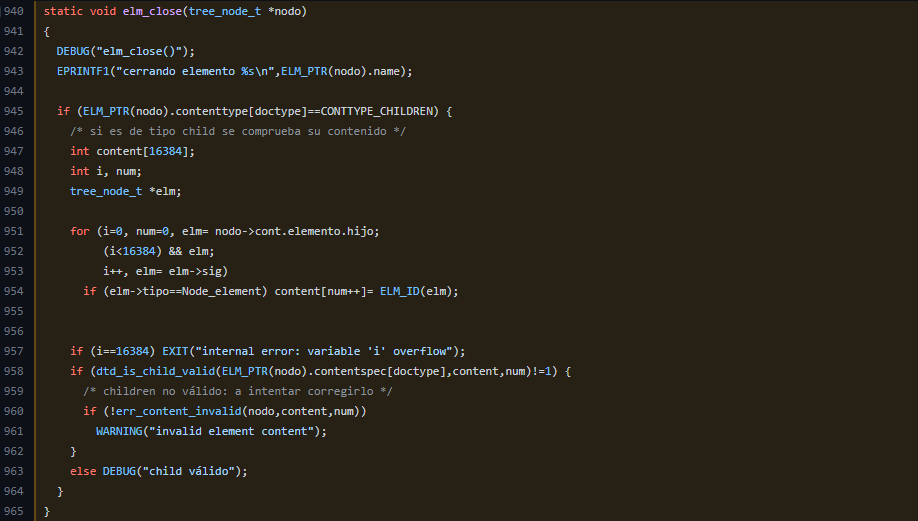
Html2xhtml v1.3 被发现存在越界读取漏洞,位于函数 static void elm_close(tree_node_t *nodo) 的 procesador.c 中。攻击者可通过构造的 HTML 文件访问敏感文件或导致拒绝服务(DoS)。
CWE-125 越界读取 是一种软件错误类型,发生在从内存中读取数据时。例如,当程序尝试读取数组末尾之后的数据时可能发生。越界读取可能导致崩溃或其他意外漏洞,并允许攻击者读取本不应访问的敏感信息。
html2xhtml/src/procesador.c 中的越界读取(GHSA-28fm-qh2h-3mch)Html2xhtml 是一个命令行工具,可将 HTML 文件转换为 XHTML 文件。Html2xhtml 可以生成符合以下文档类型之一的 XHTML 输出:XHTML 1.0(过渡型、严格型和框架集)、XHTML 1.1、XHTML Basic 和 XHTML Mobile Profile。
该漏洞是由于使用 -t frameset 选项时发生段错误而发现的。段错误或分段错误 是一种由于访问不属于自己的内存而导致的特定错误。它是一种辅助机制,防止内存损坏并引入难以调试的内存错误。
通过使用 Valgrind(一种用于查找 C 和 C++ 程序中堆内存(使用 new 或 malloc 动态分配的内存)访问错误的工具),对段错误进行调试,并在测试用例中报告了 invalid read of size 4:
==1040381== Memcheck, a memory error detector
==1040381== Copyright (C) 2002-2017, and GNU GPL'd, by Julian Seward et al.
==1040381== Using Valgrind-3.18.1 and LibVEX; rerun with -h for copyright info
==1040381== Command: ./src/html2xhtml -t frameset report/vuln/id:000000,sig:11,src:001386+001369,time:12081510,execs:2336913,op:splice,rep:16
==1040381==
==1040381== Invalid read of size 4
==1040381==    at 0x40E911: elm_close (procesador.c:944)
==1040381==    by 0x410617: err_html_struct (procesador.c:1889)
==1040381==    by 0x40F20A: err_content_invalid (procesador.c:0)
==1040381==    by 0x40F20A: elm_close (procesador.c:959)
==1040381==    by 0x40E7C4: saxEndDocument (procesador.c:233)
==1040381==    by 0x40DF7A: main (html2xhtml.c:117)
==1040381==  Address 0x6f20d4 is not stack'd, malloc'd or (recently) free'd
==1040381==
==1040381==
==1040381== Process terminating with default action of signal 11 (SIGSEGV)
==1040381==  Access not within mapped region at address 0x6F20D4
==1040381==    at 0x40E911: elm_close (procesador.c:944)
==1040381==    by 0x410617: err_html_struct (procesador.c:1889)
==1040381==    by 0x40F20A: err_content_invalid (procesador.c:0)
==1040381==    by 0x40F20A: elm_close (procesador.c:959)
==1040381==    by 0x40E7C4: saxEndDocument (procesador.c:233)
==1040381==    by 0x40DF7A: main (html2xhtml.c:117)
==1040381==  If you believe this happened as a result of a stack
==1040381==  overflow in your program's main thread (unlikely but
==1040381==  possible), you can try to increase the size of the
==1040381==  main thread stack using the --main-stacksize= flag.
==1040381==  The main thread stack size used in this run was 8388608.
==1040381==
==1040381== HEAP SUMMARY:
==1040381==     in use at exit: 88,190 bytes in 13 blocks
==1040381==   total heap usage: 22 allocs, 9 frees, 2,218,413 bytes allocated
==1040381==
==1040381== LEAK SUMMARY:
==1040381==    definitely lost: 0 bytes in 0 blocks
==1040381==    indirectly lost: 0 bytes in 0 blocks
==1040381==      possibly lost: 0 bytes in 0 blocks
==1040381==    still reachable: 88,190 bytes in 13 blocks
==1040381==         suppressed: 0 bytes in 0 blocks
==1040381== Rerun with --leak-check=full to see details of leaked memory
==1040381==
==1040381== For lists of detected and suppressed errors, rerun with: -s
==1040381== ERROR SUMMARY: 1 errors from 1 contexts (suppressed: 0 from 0)
==1040419== Memcheck, a memory error detector
来自 Valgrind 的错误日志将我们引向以下发生段错误的函数:
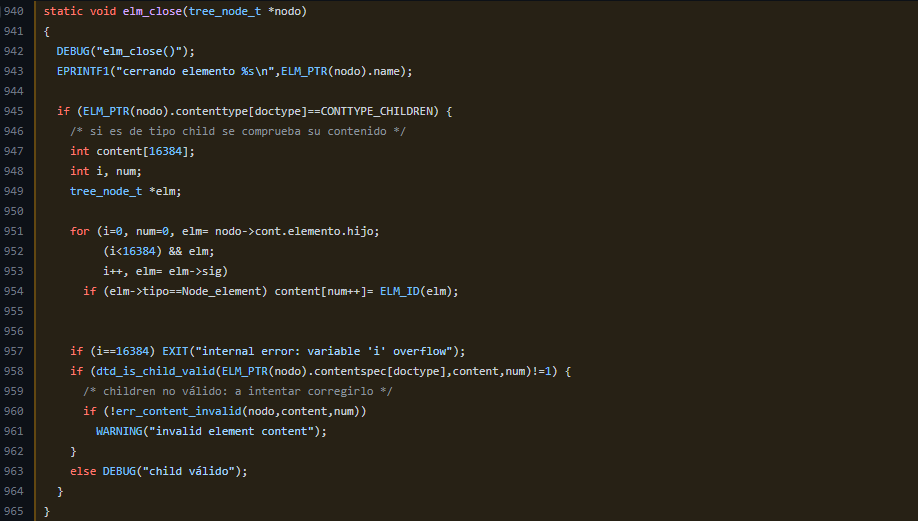
发现该函数中缺少类型检查。用户向函数传递了一个类型为 comment 的节点,而非 element,这导致了越界读取错误。攻击者可以提供畸形的文档,其中包含无效的 ELM_PTR(nodo).contenttype[doctype],从而产生以下汇编比较:
cmp dword ptr [rbp + rax*4 + 0xc], 4
攻击者可以利用此漏洞,通过构造的文件读取敏感文件、内存或位置。
| 严重性 | 高 8.1 / 10 |
|---|---|
| 攻击复杂度 | 低 |
| 所需权限 | 无 |
| 用户交互 | 需要 |
| 影响范围 | 不变 |
| 机密性 | 高 |
| 完整性 | 无 |
| 可用性 | 高 |