

新发布Aug 27, 2026
cottage v0.7.0
一款面向团队的、基于 git 的现代化 age 加密机密管理器。


cottage 是一款面向团队的 GitOps 工具,用于在 git 仓库中管理 age 加密的机密信息。
它提供了一套简单的工作流,用于加密/解密机密、管理接收者,并将机密排除在仓库之外,同时仍可通过 VCS 轻松共享。cottage 还会生成加密机密的脱敏预览,以便更好地查看,并支持持久化和临时解密工作流,同时确保机密绝不会以明文形式提交。

功能特性
- 暴露安全:利用 Rust 的类型系统确保缺陷绝不会意外泄露机密。
- 团队友好:在仓库中共享公钥(接收者),将私钥(身份)保留在本地。
- 访问控制:简单的允许/拒绝规则,用于控制哪些机密为哪些接收者加密。
- 管理 .gitignore:自动更新
.gitignore,将未加密的机密排除在仓库之外。 - 预览:生成带时间戳的加密机密脱敏预览,提升可见性。
- 丰富的差异对比:保持 git diff 干净且易于审查,同时
ctg diff可显示本地修改的机密与已跟踪的加密对应文件之间的差异。 - 校验和验证:通过验证加密机密和接收者列表与元数据是否匹配来防止篡改。
- Git 钩子:轻松设置 git 钩子,在提交前自动检查/加密机密,并在检出后自动解密。
- 路径前缀:可选择将加密机密和元数据存储在专用目录下,而非解密文件旁边。
- 持久化机密工作流:
ctg decrypt/sync将解密后的机密保留在磁盘上。 - 智能清理生命周期:
ctg run(快捷方式ctgx)和ctg edit在操作前解密机密,若事先已存在于磁盘上则保留,否则在操作后自动清理。 - 完成后清理:
ctg encrypt --clean、ctg run --clean和ctg edit --clean确保即使解密文件事先已存在,也会从磁盘上清理掉。 - 环境变量注入工作流:
ctg env将解密后的机密作为环境变量注入以运行命令,完全不写入磁盘。 - 安全的机密管道传输:
ctg cat在内存中解密并打印到 stdout,以便直接通过 stdin 管道传输给其他工具。ctg tee将 stdin 加密写入 PATH,而不将明文写入磁盘。ctg rotate为当前接收者重新加密现有机密,同样不将明文写入磁盘。 - 清理:
ctg clean从本地仓库删除所有解密后的机密,让你运行 AI 代理时少一分担忧。 - 支持 jj 和非 git 目录:
ctg init可将任意目录变为机密存储库。 - 与任意提供商同步:允许你将任何具有 API 的提供商配置为上游,并像
git pull/diff/push一样开始使用ctg pull/diff/push。 - 与任意设备同步:使用 cottage 加密并在 git 仓库中管理的机密,可通过 Cottage Sync 在设备间同步。
安装
或从包注册表安装:
# rust: cargo-binstall/cargo
cargo binstall --locked cottage
cargo install --locked cottage

# python: pip/uv/uvx
pip install cottage
uv pip install cottage
uvx --from cottage ctg --version

# node: yarn/pnpm/npx
yarn global add @sayanarijit/cottage
pnpm add -g @sayanarijit/cottage
npx -p @sayanarijit/cottage ctg --version
也可作为 Docker 镜像获取:
# Docker
docker run --rm -v $PWD:/app sayanarijit/cottage --version

# Podman
podman run --rm -v $PWD:/app quay.io/sayanarijit/cottage --version
或从 GitHub 下载最新版本。
编辑器集成
VS Code 扩展
使用 Cottage VS Code 扩展 安装 ctg、添加 Copilot 安全钩子、从资源管理器加密文件,并通过编辑器工作流打开 .cott.age 文件。
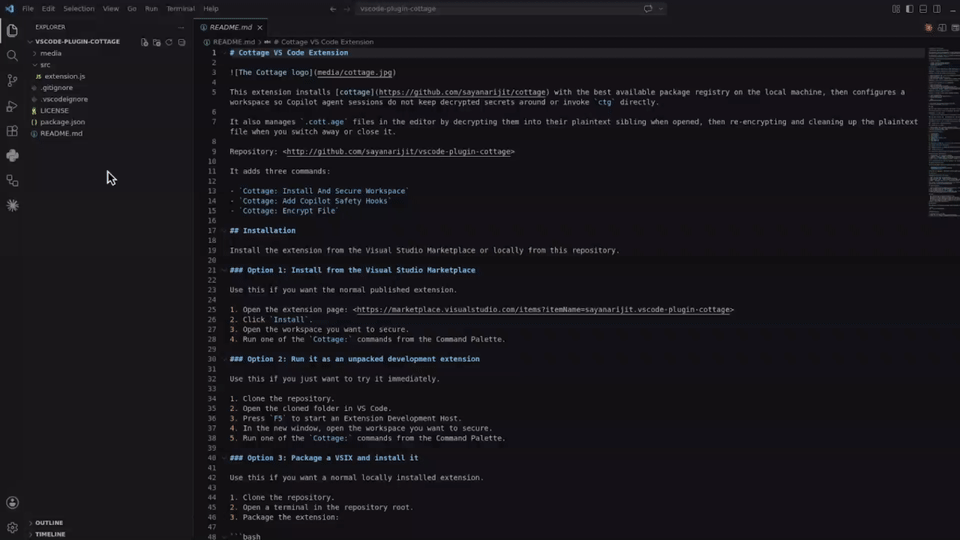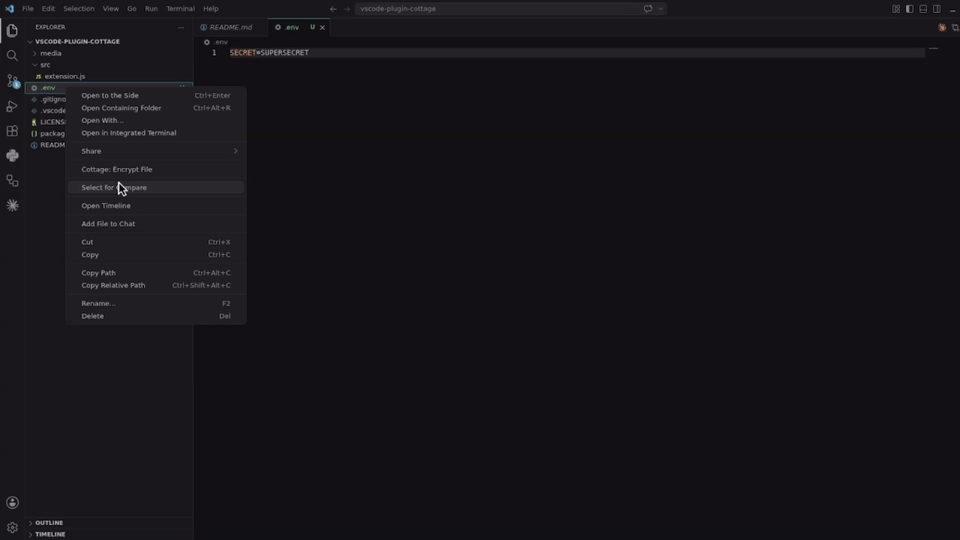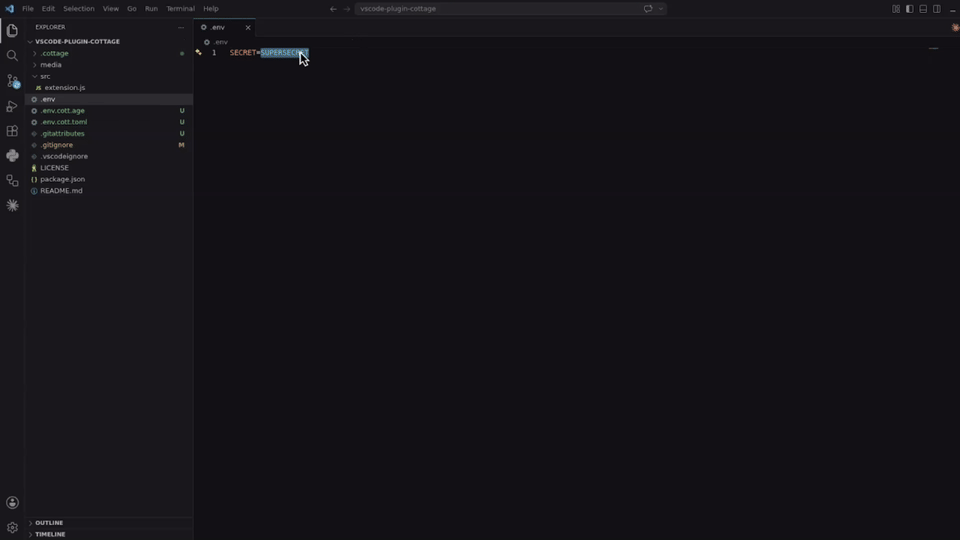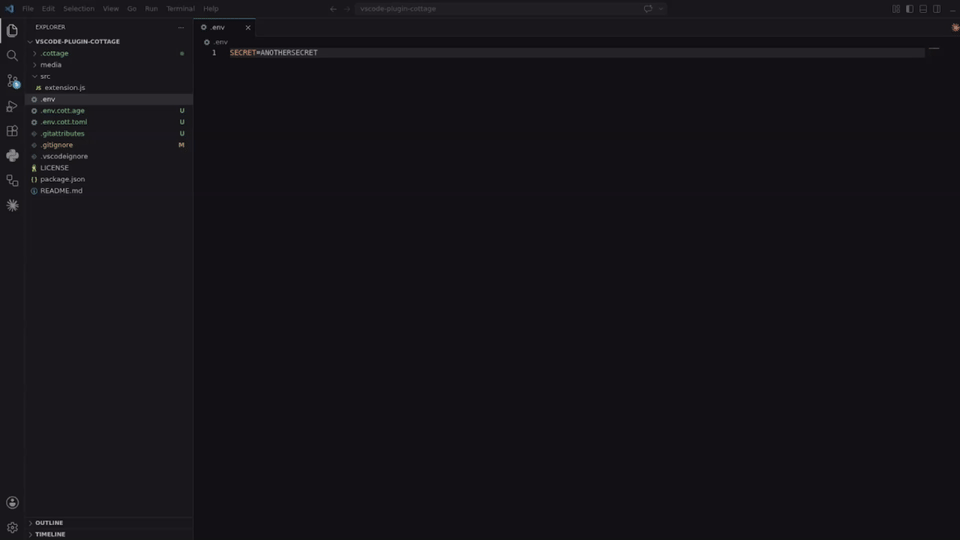
从 Visual Studio Marketplace 安装,或从 vscode-plugin-cottage 本地构建并安装。
Cursor 和 Eclipse 扩展
下载 VSX 文件 并在你的 Cursor 或 Eclipse IDE 中安装。它的工作方式与 VS Code 扩展类似。
Vim 插件
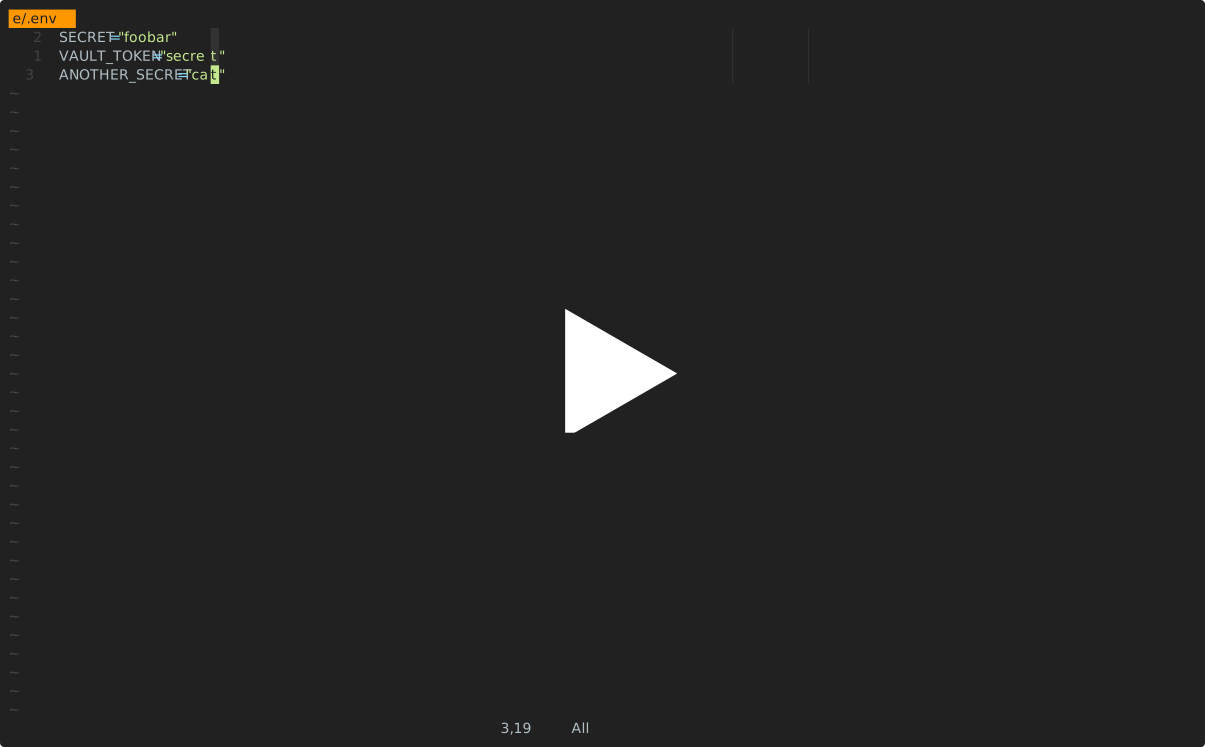
使用 cottage.vim 插件在 Vim 或 Neovim 中加密/解密机密信息。
AI 代理集成
以下所有集成都会阻止 AI 代理直接运行 ctg/ctgx,并阻止其查看或编辑机密文件:.cottage/ 内的任何内容、任何 *.cott.* 文件(加密的 *.cott.age 二进制文件和脱敏的 *.cott.toml 预览文件),以及磁盘上仍存在对应 *.cott.age 文件的任何已解密文件。
- .agents 用于 Antigravity(
agy) - .claude 用于 Claude Code
- .codex 用于 Codex
- .cursor 用于 Cursor
- .github 用于 GitHub Copilot
快速开始
初始化项目:
mkdir project && cd project

git init  # Optional, cottage works better with git but it's not required
ctg init  # Sets up the .cottage directory and necessary files

tree -a
# .
# ├ .cottage/         <- Auto-generated by `ctg init`
# │ └ recipients/     <- This is where your team keeps the public keys of all the recipients.
# │     └ sayanarijit <- Your public key. Commit it. To use an existing public key, just copy that key here.
# ├ .git/...
# └ .gitattributes    <- Added `*.cott.age binary linguist-generated filter=cottage-encrypted -diff` to avoid polluting git diff

# Your private key is stored safely in `~/.config/cottage/identity/<dirname>/<timestamp>.key`.
# You can run `ctg clean --all` anytime to clean up everything cottage ever did.
创建或编辑密钥:
# `ctg edit` decrypts the file before opening in $EDITOR and re-encrypts upon save.
# If the decrypted file was not present on disk before running `ctg edit`, it is cleaned up afterwards.
# If it was already present, it is kept on disk.
ctg edit secret.yml

# Use `--clean` with `ctg edit` or `ctg encrypt` to ensure decrypted files are deleted even if present before
ctg edit secret.yml --clean    # Opens in $EDITOR, encrypts on save, and cleans up
ctg encrypt secret.yml --clean # Encrypts secret.yml and cleans up
# encrypt secret.yml
#    into secret.yml.cott.age
#    edit secret.yml.cott.toml
#    edit .gitignore
# delete secret.yml
使用解密后的密钥运行命令:
cat secret.yml
# cat: secret.yml: No such file or directory