
Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
逆向工程 — 第 81 页 | Kitploit
分类

逆向工程

用于反编译、反汇编和理解恶意软件内部结构和复杂二进制文件的工具。

Kitploit 推荐
精选工具

10 已选择
ghidra preview#1

ghidra

GitHubnationalsecurityagency/ghidra
71.1k16小时52分前
radare2 preview#2

radare2

GitHubradareorg/radare2
24.5k0天前
cutter preview#3

cutter

GitHubrizinorg/cutter
19.4k1个月前
rizin preview#4

rizin

GitHubrizinorg/rizin
4.1k1天前
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1k1天前
ImHex preview#6

ImHex

GitHubwerwolv/imhex
54.4k21天前
angr preview#7

angr

GitHubangr/angr
9.0k1天前
unicorn preview#8

unicorn

GitHubunicorn-engine/unicorn
9.2k8个月前
capstone preview#9

capstone

GitHubcapstone-engine/capstone
8.9k5天前
keystone preview#10

keystone

GitHubkeystone-engine/keystone
2.7k3个月前
最新相关性最受欢迎最近更新
1828 结果
Vidar-Stealer-Reverse-Engineering preview

Vidar-Stealer-Reverse-Engineering

GitHubkaandemir993/vidar-stealer-reverse-engineering

深度逆向工程分析:Vidar Stealer 2.0,涵盖任务计划程序篡改(1999时间戳)、Explorer.exe进程空洞以及Microsoft Copilot注入。
memory-forensicspersistence-mechanismsreverse-engineering+7
23个月前
cve-2025-5915 preview

cve-2025-5915

GitHubr3n3r0/cve-2025-5915

针对 libarchive RAR v4 过滤器堆越界读取漏洞(CVE-2025-5915)的概念验证漏洞利用,包含 ASan 复现、编码器以及 iOS 18.5 真机演示。
ios-securityvulnerability-analysisexploitation+3
3个月前
Cisco-ASA-vulnerability-research preview

Cisco-ASA-vulnerability-research

GitHubcobbbex/cisco-asa-vulnerability-research

对 Cisco ASA 的 lina 二进制进行系统性逆向工程,以发现并分析内存破坏漏洞,包括 CVE-2025-20333 和 CVE-2025-20362,重点聚焦于寻找远程代码执行原语。

vulnerability-analysisexploitationreverse-engineering+4
2个月前
the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss preview

the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss

GitHubhunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss

CVE-2026-78997 的 PoC,这是 UC Browser for Android 中的一个通用 XSS 漏洞。包含一个精心构造的 URL 生成器、一个回调分发预言机,以及用于观察存在漏洞的桥接的 Frida hook。
android-securitydynamic-analysis-sandboxingvulnerability-analysis+6
1个月前
CVE-2025-4275 preview

CVE-2025-4275

GitHubthemalwareguardian/cve-2025-4275

分析并利用 CVE-2025-4275(Hydr0ph0bia),这是一个 Secure Boot 信任链弱点,其中固件变量被用来引入攻击者控制的证书,而这些证书会被后续启动组件所信任。

persistence-mechanismsvulnerability-analysisexploitation+5
2个月前
CVE-2022-34303 preview

CVE-2022-34303

GitHubthemalwareguardian/cve-2022-34303

演示了 CVE-2022-34303 Secure Boot 绕过,通过 CryptoPro 签名的 UEFI Shell,使用 mm 命令将 gSecurity2 置空并加载未签名的 UEFI 应用程序。
persistence-mechanismsvulnerability-analysisexploitation+7
1个月前
Analysis-for-stage1-shellcode-loader-from-hacking- preview

Analysis-for-stage1-shellcode-loader-from-hacking-

GitHubspiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-

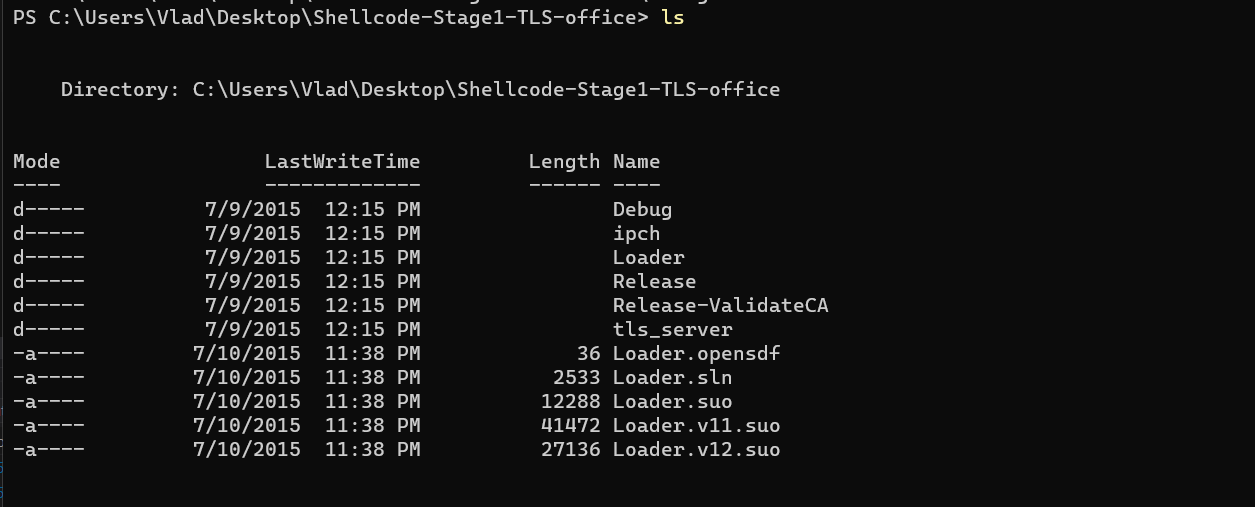
来自黑客攻击的阶段1 shellcode加载器分析
reverse-engineeringshellcodemalware-analysis+2
31年前
CVE-2022-26711 preview

CVE-2022-26711

GitHubxpcmdshell/cve-2022-26711

Apple ImageIO WebP 解析中的整数溢出 (macOS/iOS)

memory-forensicsvulnerability-analysisexploitation+3
310个月前
CVE-2022-34302 preview

CVE-2022-34302

GitHubthemalwareguardian/cve-2022-34302

演示 CVE-2022-34302,一种通过 New Horizon Datasys 签名的引导加载程序实现的 Secure Boot 绕过,该引导加载程序内置的自定义 PE/COFF 加载器可执行未签名的 UEFI 应用程序。
embedded-systems-securitypersistence-mechanismsvulnerability-analysis+7
1个月前
vankyo-s30-bootloader-unlock preview

vankyo-s30-bootloader-unlock

GitHubgadorach/vankyo-s30-bootloader-unlock

Vankyo MatrixPad S30(Unisoc SC9863A)— 通过 CVE-2022-38694 FDL1 方法解锁 Bootloader
embedded-systems-securityexploitationreverse-engineering+3
1个月前
CVE-2025-3052 preview

CVE-2025-3052

GitHubthemalwareguardian/cve-2025-3052

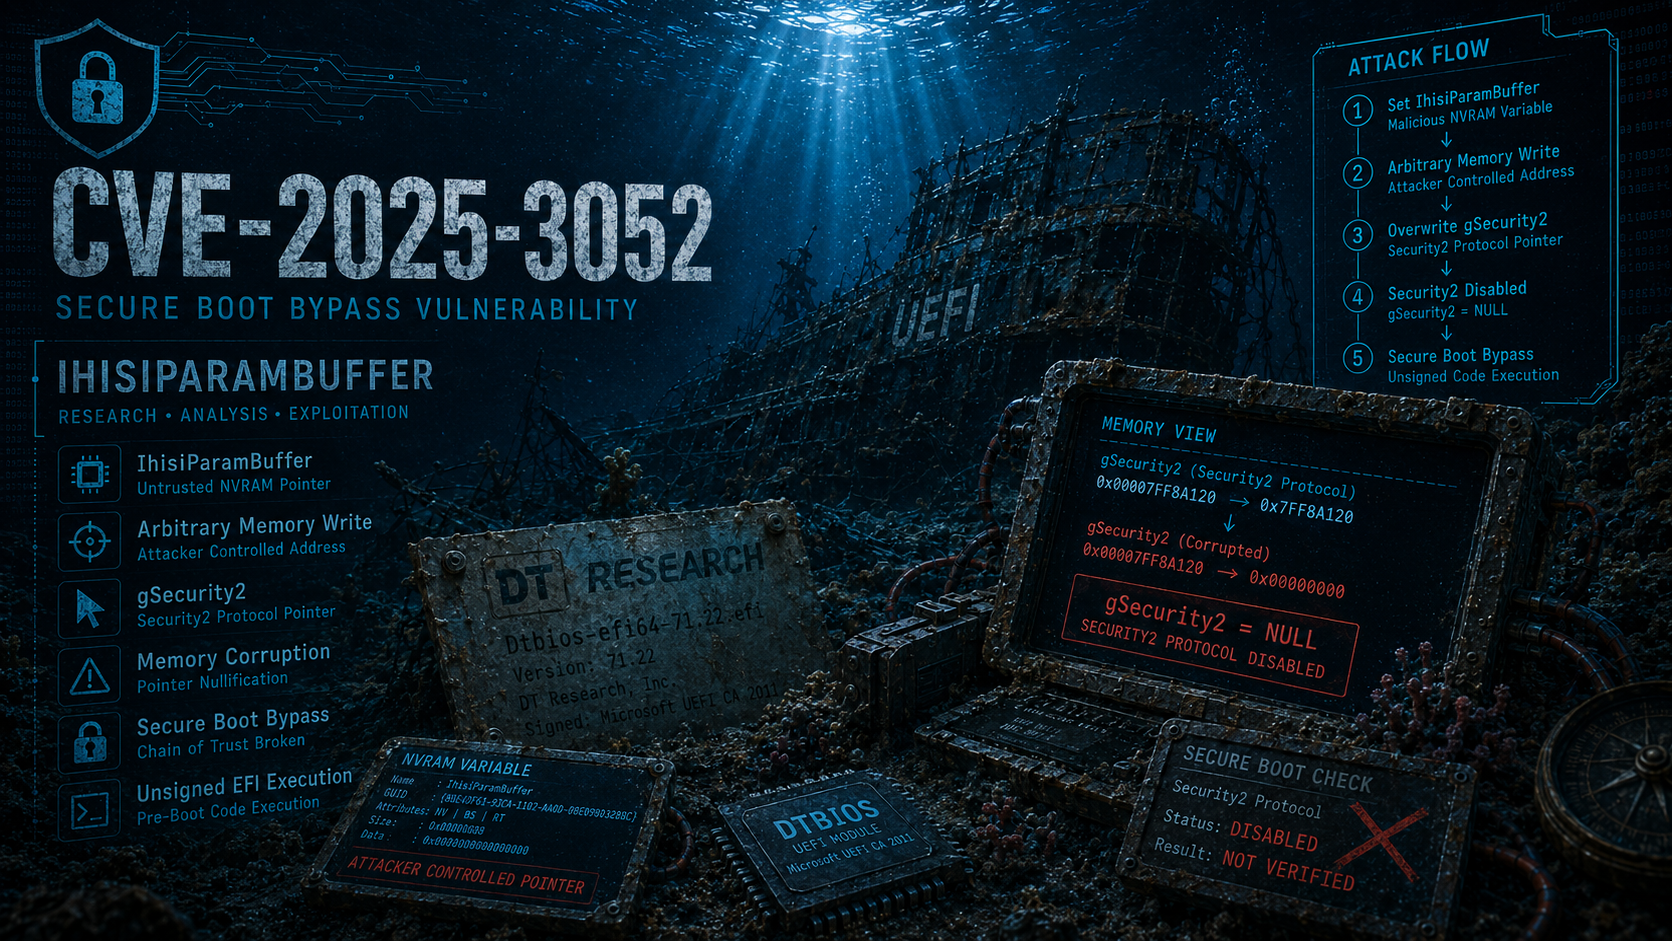
关于 CVE-2025-3052 的研究,这是一个 Insyde 固件漏洞,暴露了一个能够修改安全关键指针的任意写入原语。
embedded-systems-securityvulnerability-analysisexploitation+5
2个月前
cve-2010-4221-lab preview

cve-2010-4221-lab

GitHubdiegslva/cve-2010-4221-lab

从补丁到RCE:针对CVE-2010-4221(ProFTPD TELNET IAC栈溢出)手工构建的漏洞利用,并完整记录了由失败驱动的全过程
exploit-frameworksvulnerability-analysisexploitation+5
1个月前
accfly preview

accfly

GitHubtezeb/accfly

Accfly 摄像头漏洞披露:CVE-2020-25782、CVE-2020-25783、CVE-2020-25784、CVE-2020-25785。
embedded-systems-securityiot-securityvulnerability-analysis+6
35年前
zte-smartlife-app-pwned preview

zte-smartlife-app-pwned

GitHubminanagehsalalma/zte-smartlife-app-pwned

ZTE SmartLife 安全发现导致账户接管:Google Play 下载量超过 10 万次,以及 CVE-2026-86552 至 CVE-2026-86555。
android-securityvulnerability-analysisexploitation+7
1个月前
rmgp-complete-handoff preview

rmgp-complete-handoff

GitHubabdgalaxy36-code/rmgp-complete-handoff

完整的 RMGP(CVE-2026-43499)工作区 + 实验状态交接,适用于 SM-A376B/A376BXXU1AZB7
android-securityexploit-frameworksvulnerability-analysis+5
2个月前
cve-2025-9951-ffmpeg-jp2-poc preview

cve-2025-9951-ffmpeg-jp2-poc

GitHubfm0ss/cve-2025-9951-ffmpeg-jp2-poc

针对CVE-2025-9951的概念验证,演示了通过JPEG 2000组件映射不匹配在FFmpeg中实现受控回调执行。包含技术分析文档、payload生成器以及用于确定性布局利用研究的GDB启动脚本。
vulnerability-analysisexploitationreverse-engineering+3
3个月前
CVE-2025-70962 preview

CVE-2025-70962

GitHubnamaek2/cve-2025-70962

CVE-2025-70962 PoC
iot-securityvulnerability-analysisexploitation+3
2个月前
cfgrip preview

cfgrip

GitLabbinaryhardening/cfgrip

反汇编 PE/ELF x86/x64 二进制文件,通过 GOT、跳转表和寄存器追踪解析间接分支,并将完整控制流图导出为结构化 JSON,用于静态分析和补丁。

static-analysisreverse-engineeringdebuggers+1
23个月前
上一页1…808182…100下一页









