


Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
分类

权限提升

用于在受损系统上获取更高级别权限或未经授权访问的工具。

Kitploit 推荐

精选工具

10 已选择
PEASS-ng preview#1

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k4小时52分前
PrivescCheck preview#2

PrivescCheck

GitHubitm4n/privesccheck
3.9k24天前
LinEnum preview#3

LinEnum

GitHubrebootuser/linenum
8.0k6年前
linux-smart-enumeration preview#4

linux-smart-enumeration

GitHubdiego-treitos/linux-smart-enumeration
4.0k6个月前
WinPwn preview#5

WinPwn

GitHubs3cur3th1ssh1t/winpwn
3.7k1年前
wesng preview#6

wesng

GitHubbitsadmin/wesng
4.9k7小时43分前
BeRoot preview#7

BeRoot

GitHubalessandroz/beroot
2.6k2年前
PowerUpSQL preview#9

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1年前
Seatbelt preview#10

Seatbelt

GitHubghostpack/seatbelt
4.7k1年前
SharpUp preview#11

SharpUp

GitHubghostpack/sharpup
1.5k3年前
最新相关性最受欢迎最近更新
4622 结果
CVE preview

CVE

GitHubtomerpeled92/cve

精选的 CVE 存储库,包含 PoC、文章及详细描述,用于漏洞研究与利用。

privilege-escalationvulnerability-analysisexploitation+3
112个月前
Termix-research preview

Termix-research

GitHubgabrielha12/termix-research

CVE-2026-45746, CVE-2026-45750, CVE-2026-53547 — Termix 中的三个严重漏洞:跨租户会话劫持、OS 命令注入和账户接管
privilege-escalationvulnerability-analysisexploitation+2
23个月前
CVE-2020-24028 preview

CVE-2020-24028

GitHubredteambrasil/cve-2020-24028

CVE-2020-24028 的 PoC:通过 ForLogic Qualiex 中经过身份验证的权限绕过实现权限提升,允许创建用户和更改密码。

privilege-escalationvulnerability-analysisexploitation+2
3个月前
CVE-2020-24029 preview

CVE-2020-24029

GitHubredteambrasil/cve-2020-24029

关于 ForLogic Qualiex v1 和 v3 中一个未经验证的密码更改漏洞的详细披露,该漏洞可实现远程权限提升和信息泄露。

privilege-escalationvulnerability-analysisexploitation+4
3个月前
CVE-2020-24030 preview

CVE-2020-24030

GitHubredteambrasil/cve-2020-24030

CVE-2020-24030 披露:ForLogic Qualiex 存在弱令牌过期机制,可通过令牌重用实现远程权限提升并访问敏感数据。

authentication-authorizationprivilege-escalationvulnerability-analysis+2
3个月前
CVE-2026-43499-root-KernelSU preview

CVE-2026-43499-root-KernelSU

GitHubwoshimaniubi8/cve-2026-43499-root-kernelsu

基于内核漏洞CVE-2026-43499的本地提权适配,集成嵌入式 KernelSU.CVE-2026-43499+KernelSU越狱模式

android-securityprivilege-escalationexploitation+2
183个月前
UnPlus preview

UnPlus

GitHubno-22-github/unplus

CVE-2026-43499 每次启动的 root 提权漏洞 — 核心逻辑(arm64 Android GKI 6.6)
android-securityprivilege-escalationexploitation+2
24个月前
CVE-2023-28252- preview

CVE-2023-28252-

GitHubdanasuley/cve-2023-28252-

检测 CVE-2023-28252 漏洞利用
privilege-escalationvulnerability-analysisexploitation+1
3年前
CVE-2020-1472 preview

CVE-2020-1472

GitHubstriveben/cve-2020-1472

针对CVE-2020-1472的利用工具,这是一个Windows NetLogon权限提升漏洞,使用Impacket实现域管理员权限获取。
privilege-escalationvulnerability-analysisexploitation+1
56年前
CVE-2020-1472 preview

CVE-2020-1472

GitHubsv3nbeast/cve-2020-1472

CVE-2020-1472复现时使用的py文件整理打包

privilege-escalationvulnerability-analysisexploitation+1
103年前
CVE-2022-0847 preview

CVE-2022-0847

GitHubr1is/cve-2022-0847

CVE-2022-0847-DirtyPipe-Exploit CVE-2022-0847 是存在于 Linux内核 5.8 及之后版本中的本地提权漏洞。攻击者通过利用此漏洞,可覆盖重写任意可读文件中的数据,从而可将普通权限的用户提升到特权 root。 CVE-2022-0847…

privilege-escalationvulnerability-analysisexploitation+2
2823年前
CVE-2017-16995 preview

CVE-2017-16995

GitHubph4ntonn/cve-2017-16995

👻CVE-2017-16995
privilege-escalationvulnerability-analysisexploitation+2
25年前
CVE-2017-8890 preview

CVE-2017-8890

GitHubthinkycx/cve-2017-8890

CVE-2017-8890 漏洞利用实现,附带详细分析文档,用于在 Ubuntu 16.04 和 Nexus 6P 内核上进行权限提升。

privilege-escalationvulnerability-analysisexploitation+3
367年前
CVE-2026-40000 preview

CVE-2026-40000

GitHubskorpion96/cve-2026-40000

ZTE 文件管理器(zte.com.cn.filer)中一个漏洞的 PoC,该漏洞允许以该文件管理器的权限读取其他应用中的任意文件。
android-securityprivilege-escalationvulnerability-analysis+3
13个月前
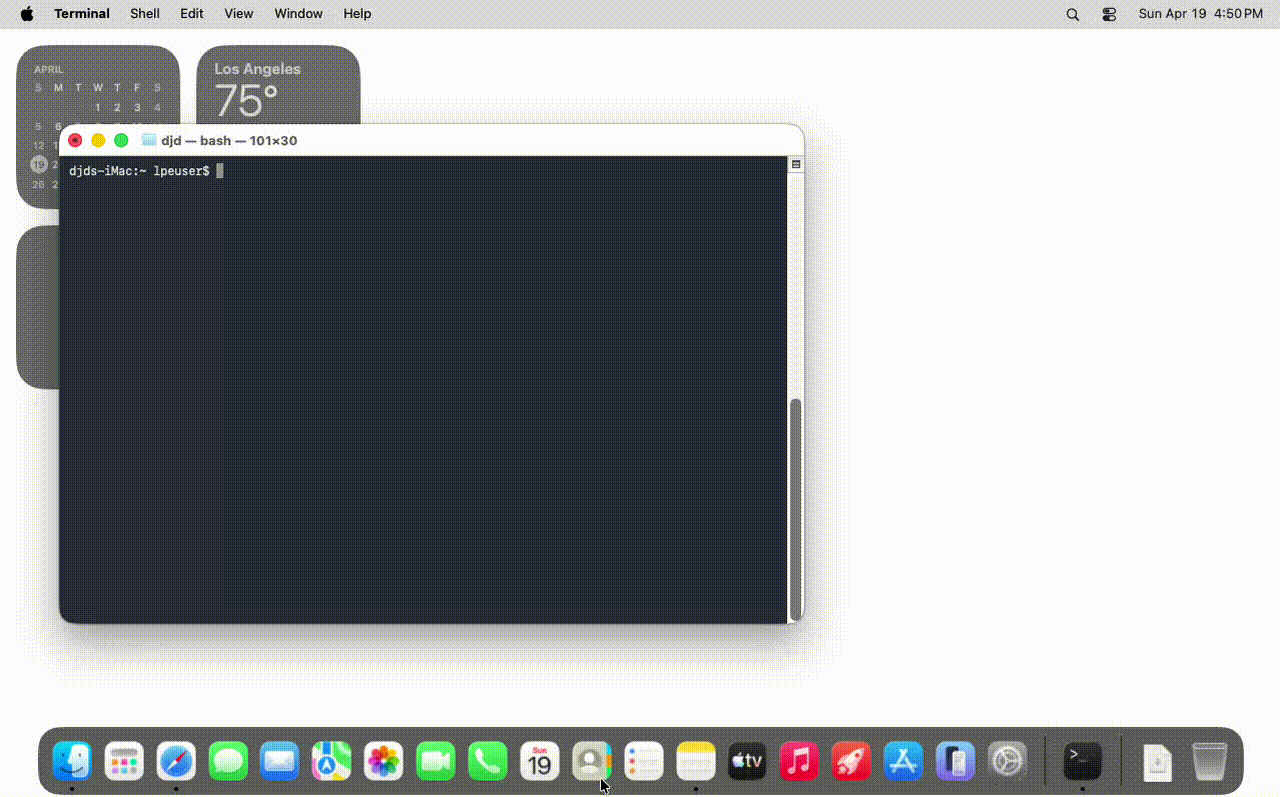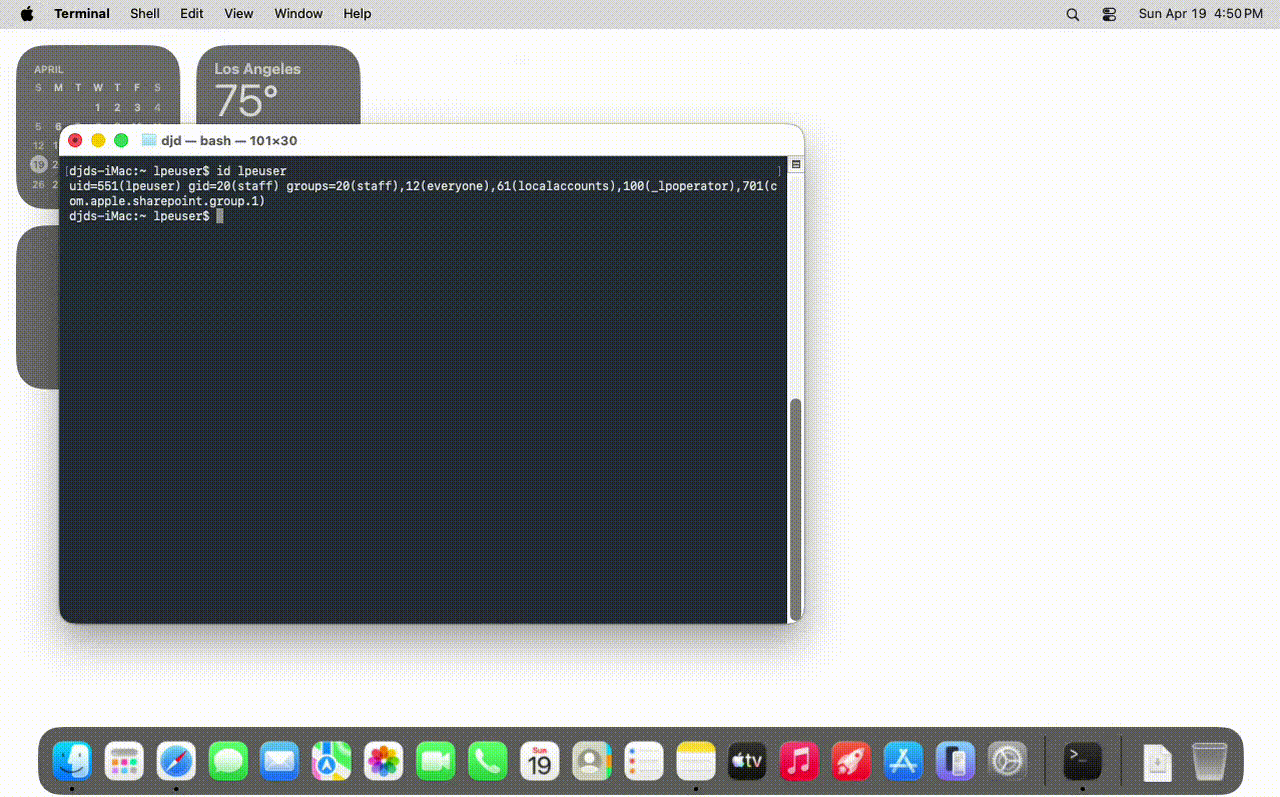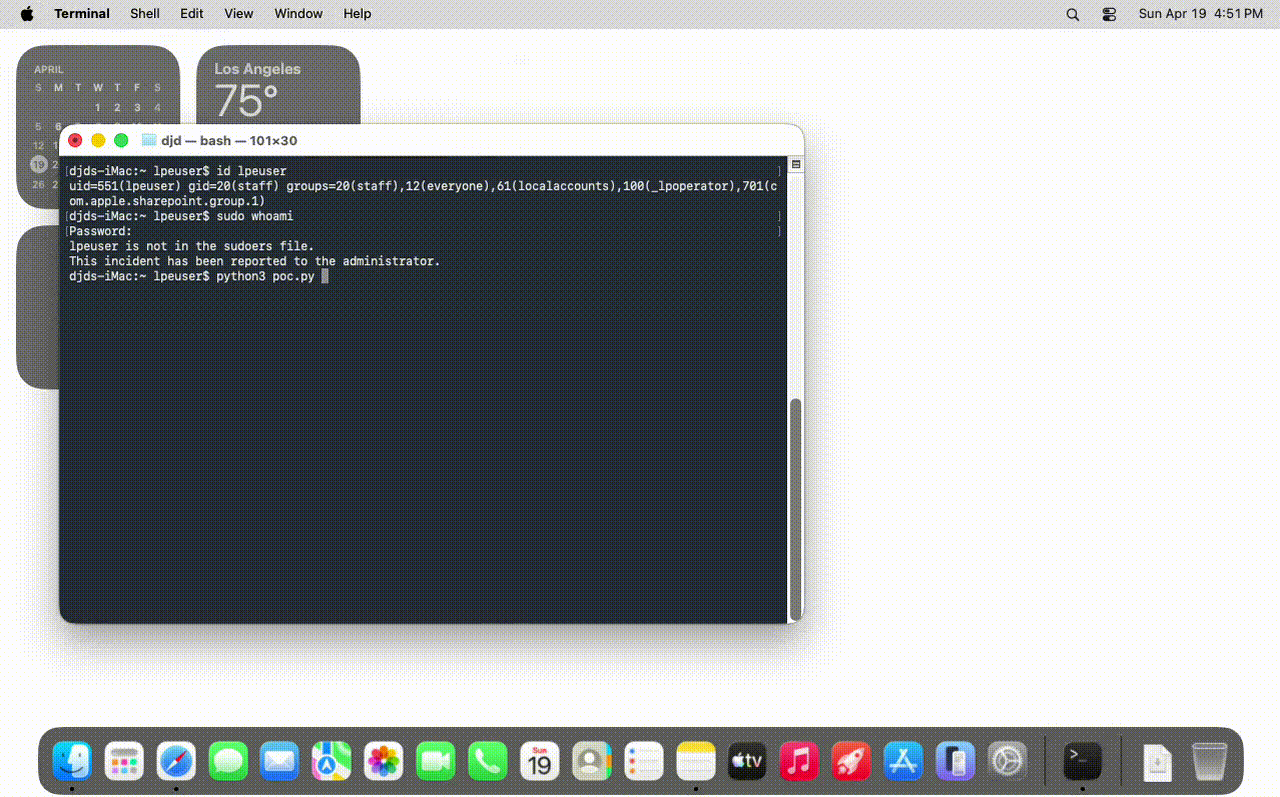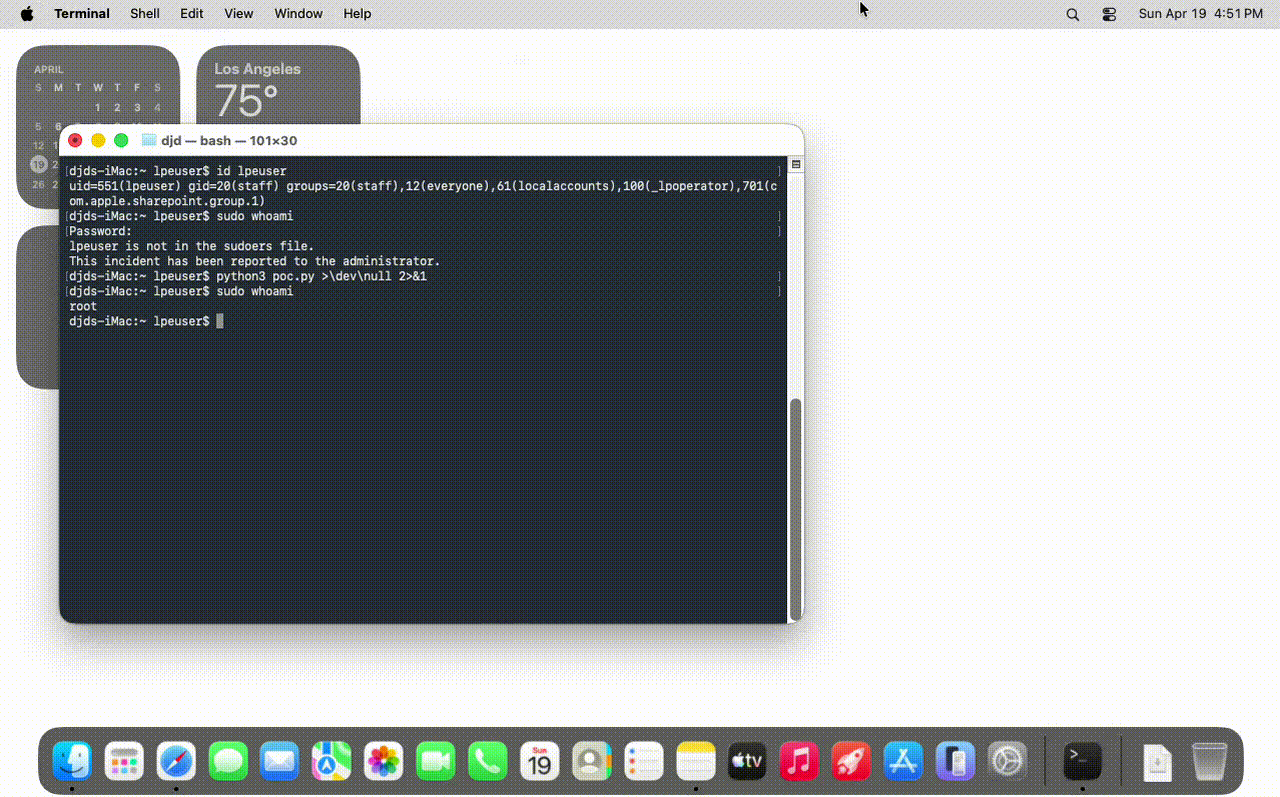
CVE-2026-39875-macOS-CUPS-LPE preview

CVE-2026-39875-macOS-CUPS-LPE

GitHubmac-123456789-lab/cve-2026-39875-macos-cups-lpe

macOS Sonoma、Sequoia 和 Tahoe 上从非特权用户提升至 root。已在 macOS 26.6 / 15.7.8 / 14.8.8 中修复。

privilege-escalationexploitationbinary-exploitation
103个月前
SELinux-Permissive-Only-CVE-2025-21479 preview

SELinux-Permissive-Only-CVE-2025-21479

GitHubcamsshaft/selinux-permissive-only-cve-2025-21479

这是一个 SELinux 宽容模式版本的 Cheese 漏洞利用程序,也被称为 CVE-2025-21479,该漏洞影响了许多设备(包括三星骁龙设备)上的 adreno kgsl。

android-securityprivilege-escalationexploitation+2
63个月前
Root-My-Device preview

Root-My-Device

GitHubwitaqua-tools/root-my-device

适用于受支持固件的 KSU 安装程序,针对 CVE-2026-43499
android-securityprivilege-escalationvulnerability-analysis+6
91个月前
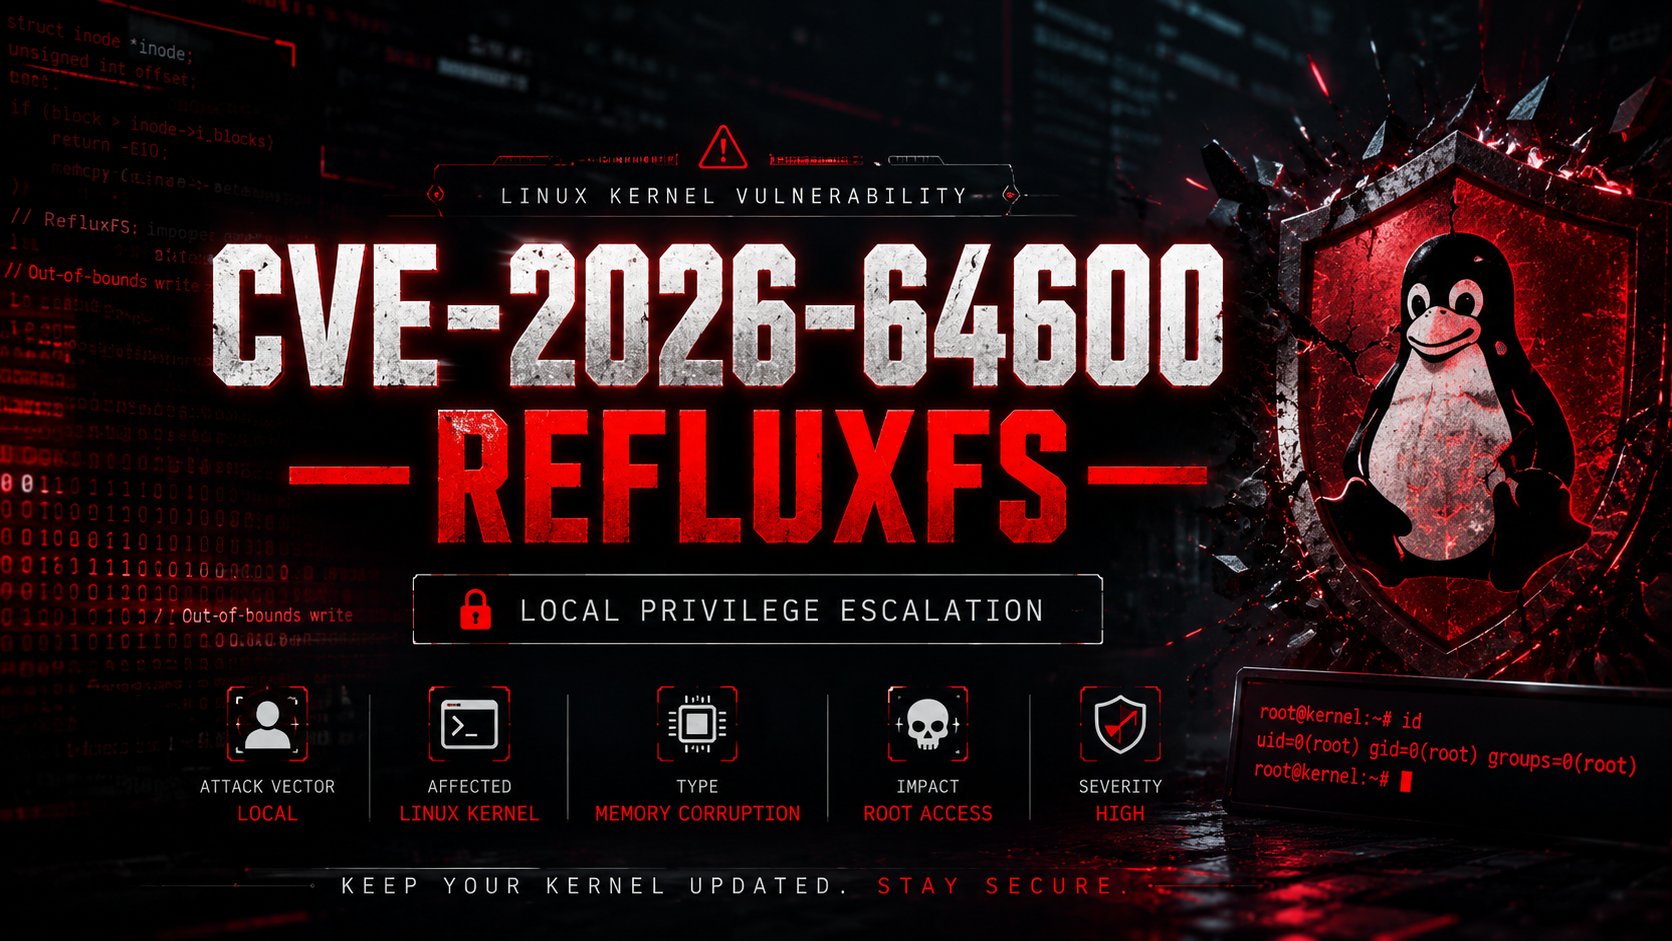
RefluxFS_CVE-2026-64600 preview

RefluxFS_CVE-2026-64600

GitHubletsr00t/refluxfs_cve-2026-64600

针对 CVE-2026-64600 的技术分析,该漏洞为 RefluxFS 中因内存损坏导致的 Linux 内核本地权限提升漏洞,附有缓解措施及面向防御研究与教育的参考资料。

privilege-escalationvulnerability-analysispapers-research+2
3个月前
上一页1…747576…100下一页




