
 #1
 owasp/owasp-hunting
Curated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
 lumoslab-innovation/openhunterai
面向 Web、API 和 LLM 应用安全的本地优先 AI 红队。攻击者式推理、有证据支撑的发现,以及面向 AI 编码代理的技能。
 garrytan/gstack
Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA
 blacklanternsecurity/trevorproxy
一个用Python编写的SOCKS代理,可随机化你的源IP地址。通过SSH隧道轮询你的恶意数据包,或者为它们提供数十亿个唯一源地址!
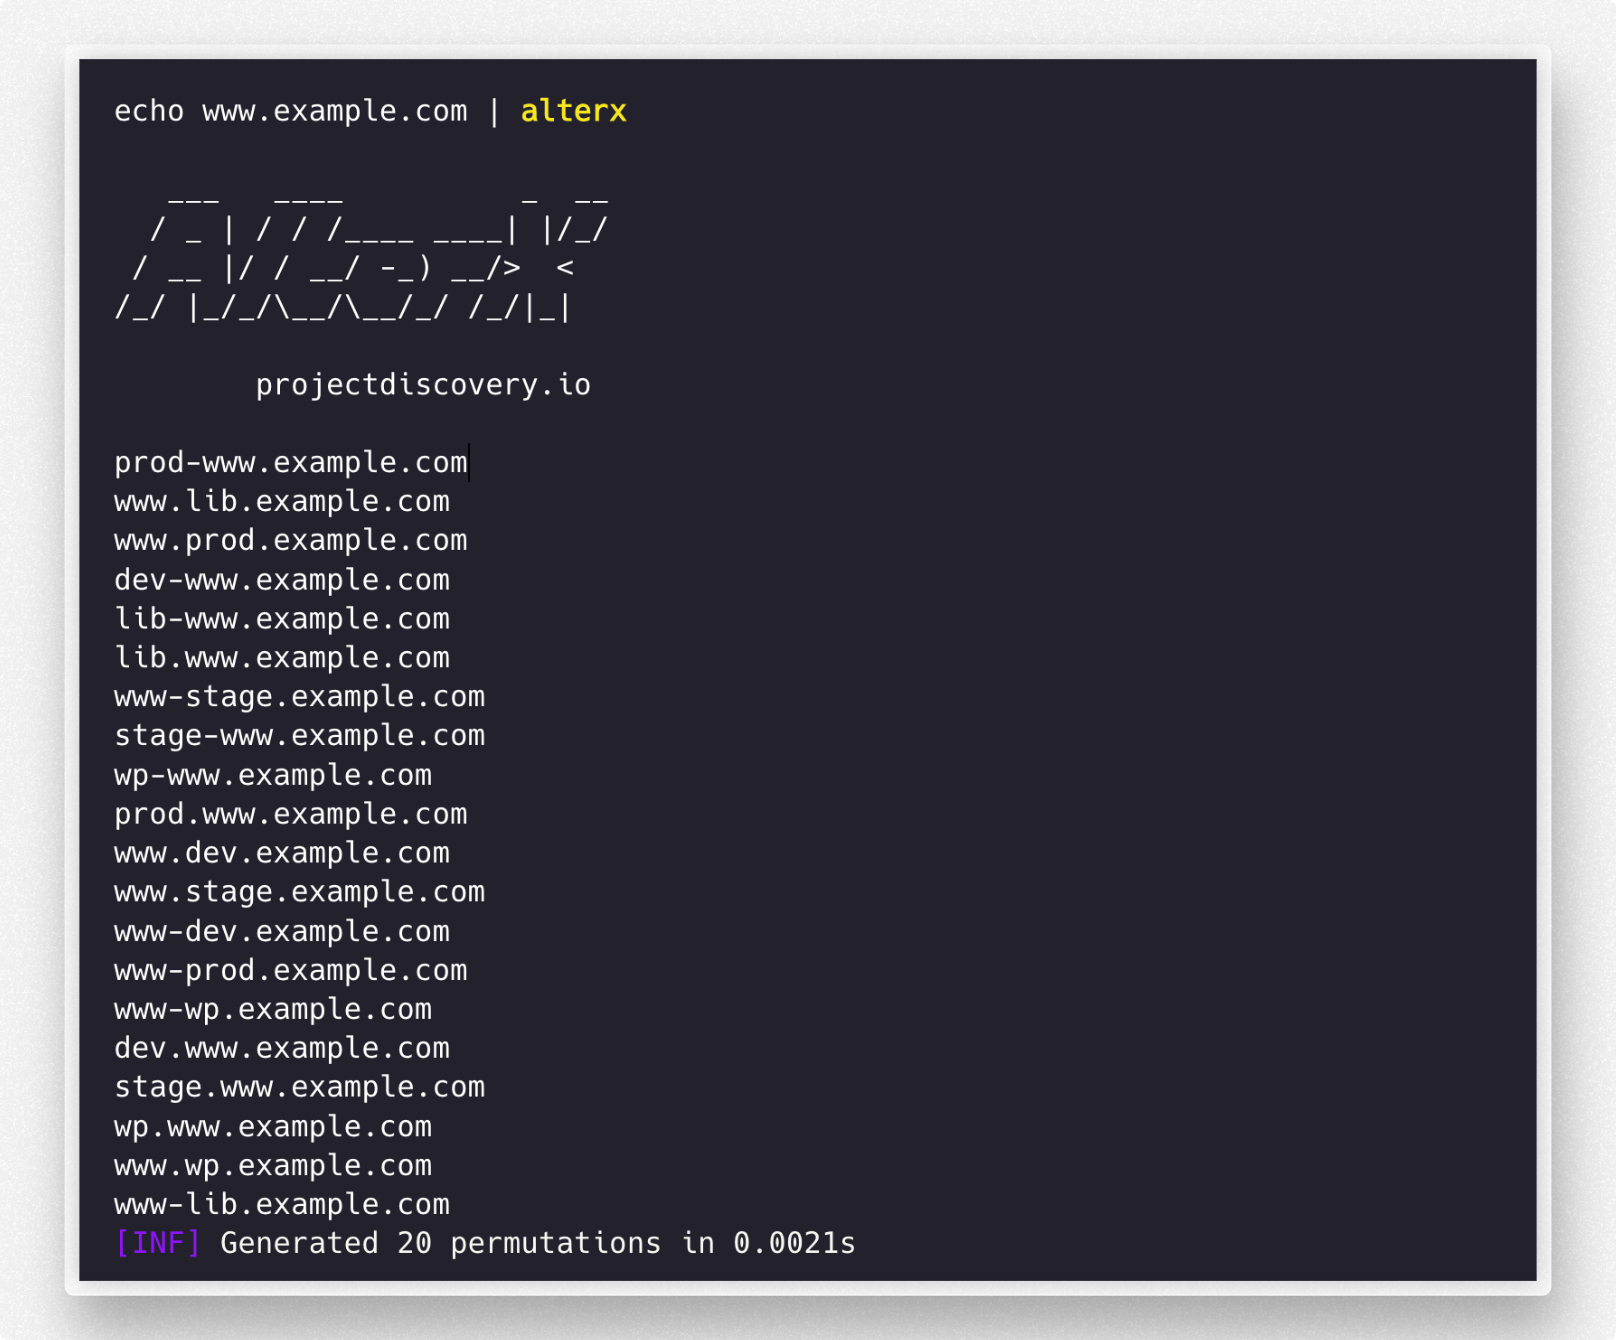 projectdiscovery/alterx
基于DSL的快速可定制子域名字典生成器
 mr-xn/penetration_testing_poc
渗透测试有关的POC、EXP、脚本、提权、小工具等---About penetration-testing python-script poc getshell csrf xss cms php-getshell domainmod-xss csrf-webshell cobub-razor…
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
rapid7/metasploit-framework开源漏洞利用框架,具备模块化载荷、编码器和辅助系统,用于跨网络和应用的渗透测试、漏洞验证及安全研究。
 danielmiessler/seclists
精心策划的用于安全评估的字典集合,包括用户名、密码、URL、模糊测试载荷以及用于渗透测试和情报收集的敏感数据模式。
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
 projectdiscovery/katana
下一代爬取与爬虫框架。
 pensarai/apex
使用自主智能体,直接在您的终端中进行AI驱动的进攻性安全测试。
 promptfoo/promptfoo
测试你的提示词、代理和RAG。对AI进行红队测试/渗透测试/漏洞扫描。比较GPT、Claude、Gemini、DeepSeek等的性能。简单的声明式配置,支持命令行和CI/CD集成。被OpenAI和Anthropic使用。
 cliffe/breakescape
可挂载的Rails引擎,提供24+个网络安全密室逃脱场景,包含随机密码、即时编译的NPC对话以及用于游戏状态管理的RESTful API。专为实践性安全培训设计。










