
 #1
 funcan/sshole
A simple reproducer for CVE-2026-123158
 devzero-security/redstackpro
在画布上编排红队基础设施和 Active Directory 靶场,然后编译为完整的 Terraform 和 Ansible 工作目录,由你自己运行。在生产运维级别验证 TTP 和工具。支持 GCP、AWS 和 Azure。
 lpizziniacofortinet/cve-2026-123158-openssh-musl-lab
Automated Terraform lab environment for OpenSSH on Linux with musl libc without PAM (CVE-2026-123158 research)
 halilkirazkaya/cve-2026-123158
Proof-of-concept scanner and Docker lab for the OpenSSH password authentication bypass (CVE-2026-123158) on musl libc Alpine builds without PAM.
 mfthomps/labtainers
Labtainers:一个基于Docker的网络实验室框架
 thiscitze/cve-2026-98432-root-shell
CVE-2026-98432 - Linux IPv4/TCP lab root-shell kit (by thiscitze)
 thiscitze/cve-2026-86596-poc
CVE-2026-86596 - s2Member <= 260927 template injection (lab PoC by thiscitze)
 criticalwombat/sshole_scanner-cve-2026-123158
Scans SSH hosts for the musl libc crypt() authentication bypass (CVE-2026-123158) with single-host checks, CIDR sweeps, and a Docker test lab.
 laremontada12/cve-2026-39987-marimo-preauth-rce
使用 Docker、Nginx、Linux 进程监控、Splunk SIEM 和 SPL 检测规则对 CVE-2026-39987 进行安全研究与 SOC 调查。
 secprbench/secprbench
针对九个 C、C++ 和 Rust 项目中 265 个真实引入漏洞的代码变更的基准测试,包含配对的审查任务、Docker 沙箱、评判器和评估框架。
 h1z3-br0/cve-2026-98432
CVE-2026-98432 Linux TCP ireq_opt 释放后使用(use-after-free)实验室工具包:带堆复用预言机的竞态触发、泄漏解析器、KASLR 解析器、pcap 分析、IDS 规则与加固。
 tharsh2003/inf2005-acw3-pythonssl
针对 CVE-2026-19553 的概念验证与修复实验环境,演示 Python 的 SSLContext.wrap_bio() 中 TLS 主机名验证绕过,并包含本地 CA、服务器以及修补版本对比。
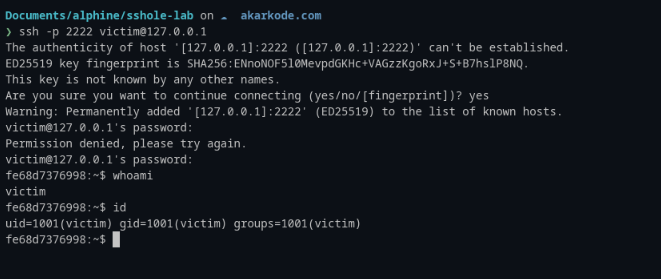 akarkode/alpine-openssh-sshole-auth-bypass
Vulnerability research, PoC reproduction lab, and technical analysis for Alpine Linux OpenSSH authentication bypass (CVE-2026-123158 / sshole)
 capivara-research/cve-2026-122158
Analysis and loopback-restricted PoC for CVE-2026-122158, a cross-tenant privilege escalation in InvoiceShelf allowing an owner to assign arbitrary…
 xairy/linux-kernel-exploitation
与Linux内核安全与利用相关的链接集合

 rdelasierra-uy/rag-seguridad
CyberRAG — 基于网络安全笔记和书籍的 100% 本地 RAG(Ollama):混合检索、带引用的回答、分阶段渗透测试助手和重建索引监控器。无重型框架。
 rothoma2/cve-2026-123158-sshole
Lab-only scanner and reproducible Alpine Docker test case for the SSHole OpenSSH password-authentication bypass (CVE-2026-123158) using overlong…









