

Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
数字取证 — 第 71 页 | Kitploit
分类

数字取证

用于为法律或调查目的获取、保存和分析数字证据的工具。

Kitploit 推荐

精选工具

10 已选择
autopsy preview#1

autopsy

GitHubsleuthkit/autopsy
3.3k6个月前
sleuthkit preview#2

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k7天前
volatility3 preview#3

volatility3

GitHubvolatilityfoundation/volatility3
4.3k1个月前
plaso preview#4

plaso

GitHublog2timeline/plaso
2.2k3天前
bulk_extractor preview#5

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k1个月前
velociraptor preview#6

velociraptor

GitHubvelocidex/velociraptor
4.2k21小时29分前
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.5k8天前
mvt preview#8

mvt

GitHubmvt-project/mvt
16.1k2天前
androidqf preview#9

androidqf

GitHubmvt-project/androidqf
23013天前
avml preview#10

avml

GitHubmicrosoft/avml
1.1k8天前
最新相关性最受欢迎最近更新
1458 结果
CVE-2021-36934-DLL-Hijacking-DFIR-Investigation preview

CVE-2021-36934-DLL-Hijacking-DFIR-Investigation

GitHubduyduongduyduong/cve-2021-36934-dll-hijacking-dfir-investigation

适用于 CVE-2021-36934 的 DFIR 调查资源,涵盖 DLL 劫持、权限提升检测,以及对受影响 Windows 系统的取证分析。

privilege-escalationvulnerability-analysisexploitation+2
3个月前
LsassReflectDumping preview

LsassReflectDumping

GitHuboffensive-panda/lsassreflectdumping

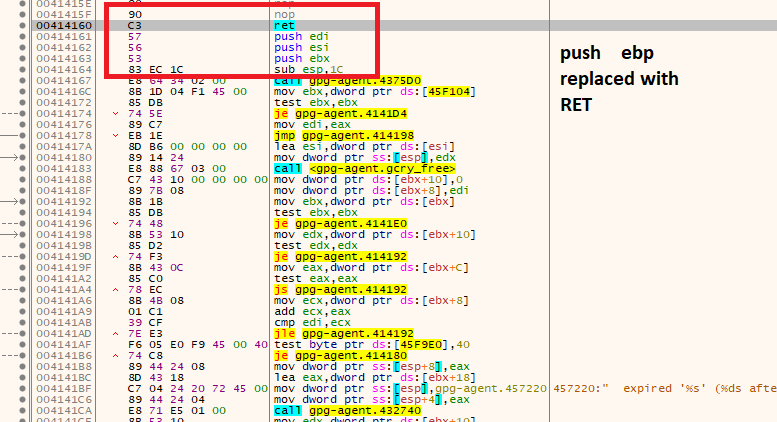
该工具利用进程分叉技术,通过 RtlCreateProcessReflection API 克隆 lsass.exe 进程。创建克隆后,它使用 MINIDUMP_CALLBACK_INFORMATION 回调来生成克隆进程的内存转储。
memory-forensicspassword-attackspost-exploitation+1
2202年前
gpg_reaper preview

gpg_reaper

GitHubkacperszurek/gpg_reaper

GPG Reaper - 从 gpg-agent 缓存/内存中获取/窃取/恢复 GPG 私钥

memory-forensicsexploitationpost-exploitation+1
968年前
windbg-mcp preview

windbg-mcp

GitHubgengstah/windbg-mcp

一个 MCP(模型上下文协议)服务器,可将所有 pybag Windows 调试器功能转换为原生 MCP 工具。它允许兼容 MCP 的客户端(Claude Desktop、Claude Code、Cowork、OpenAI Codex CLI、Cursor 以及自定义代理)通过结构化 JSON…
dynamic-analysis-sandboxingmemory-forensicsvulnerability-analysis+7
866个月前
fingerprint preview

fingerprint

GitHubbitranox/fingerprint

监控 Windows 注册表和文件变化

forensicsdigital-forensicsincident-response
707个月前
Ticketbleed preview

Ticketbleed

GitHubegebalci/ticketbleed

这是一个用于利用 Ticketbleed(CVE-2016-9244)漏洞的工具。

memory-forensicsvulnerability-analysisexploitation+2
309年前
cve-2018-8174_analysis preview

cve-2018-8174_analysis

GitHubpiotrflorczyk/cve-2018-8174_analysis

VBS 漏洞利用 CVE-2018-8174 分析
memory-forensicsvulnerability-analysisexploitation+3
308年前
CVE-2026-46331 preview

CVE-2026-46331

GitHub0xblackash/cve-2026-46331

CVE-2026-46331

privilege-escalationmemory-forensicsvulnerability-analysis+3
294个月前
CVE-2023-30367-mRemoteNG-password-dumper preview

CVE-2023-30367-mRemoteNG-password-dumper

GitHubs1lkys/cve-2023-30367-mremoteng-password-dumper

CVE-2023-30367 的原始 PoC

password-crackingmemory-forensicsvulnerability-analysis+2
162年前
xz-backdoor-github preview

xz-backdoor-github

GitHubemirkmo/xz-backdoor-github

与 xz 后门相关的提交历史,发现于 2024 年 3 月 29 日:CVE-2024-3094。

malware-analysisdigital-forensicsthreat-intelligence+3
112年前
BiBi-Windows-Wiper-Analysis preview

BiBi-Windows-Wiper-Analysis

GitHubknight0x07/bibi-windows-wiper-analysis

针对以色列组织的 Bibi-Windows Wiper 技术分析
reverse-engineeringmalware-analysisdigital-forensics+3
83年前
cve-2011-3026-firefox preview

cve-2011-3026-firefox

GitHubargp/cve-2011-3026-firefox

在 Firefox (Linux/x86) 上利用 CVE-2011-3026 的示例

memory-forensicsvulnerability-analysisexploitation+3
614年前
CVE-2014-4481 preview

CVE-2014-4481

GitHubfeliam/cve-2014-4481

Apple CoreGraphics框架在解析CCITT group 3编码数据时未能验证输入,导致堆溢出条件。一个较小的堆内存分配可能被来自输入的受控数据溢出,从而在Mobile Safari上下文中实现任意代码执行。
ios-securitymemory-forensicsvulnerability-analysis+3
511年前
CVE-2021-33624 preview

CVE-2021-33624

GitHubbenschlueter/cve-2021-33624

针对 CVE-2021-33624 的概念验证
memory-forensicsvulnerability-analysisexploitation+1
35年前
CVE-2021-44852 preview

CVE-2021-44852

GitHubcrackercat/cve-2021-44852

在 Biostar RACING GT Evo 2.1.1905.1700 的 BS_RCIO64.sys 中发现了一个问题。低完整性进程可以打开该驱动的设备对象并发送 IOCTL,以读取或写入任意物理内存位置(或调用任意地址),从而导致任意代码执行。这与 0x226040、0x226044 和…

privilege-escalationmemory-forensicsvulnerability-analysis+3
23年前
CVE-2025-65320 preview

CVE-2025-65320

GitHubyonathanpy/cve-2025-65320

CVE-2025-65320 概念验证,演示通过调试器附加从进程内存中提取明文许可证密钥,从而在 Abacre Restaurant POS 上实现软件激活绕过。

memory-forensicsvulnerability-analysisexploitation+3
28个月前
watcher preview

watcher

GitHubthemoonsir/watcher

检测反向 shell 并在尝试 shell 之前将其终止。
defensive-toolsmemory-forensicsreverse-engineering+5
29个月前
CVE-2017-8641_chakra_Js_GlobalObject preview

CVE-2017-8641_chakra_Js_GlobalObject

GitHubhomjxi0e/cve-2017-8641_chakra_js_globalobject

在Chakra中,当eval一个足够大的字符串时,存在一个经典的堆溢出问题!该问题可以在Win10 WIP的最新版Edge中稳定复现。打开POC.html时,Edge会立即发生异常。

memory-forensicsvulnerability-analysisexploitation+3
19年前
上一页1…707172…81下一页








