Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
蓝牙安全 — 第 9 页 | Kitploit
分类

蓝牙安全

用于评估和利用蓝牙设备安全性和通信漏洞的工具。

Kitploit 推荐

精选工具

10 已选择
ubertooth preview#1

ubertooth

GitHubgreatscottgadgets/ubertooth
2.2k7个月前
btlejack preview#2

btlejack

GitHubvirtualabs/btlejack
2.1k3年前
internalblue preview#3

internalblue

GitHubseemoo-lab/internalblue
7822年前
Sniffle preview#4

Sniffle

GitHubnccgroup/sniffle
1.2k1年前
BLESuite preview#5

BLESuite

GitHubnccgroup/blesuite
1917年前
BTLE preview#6

BTLE

GitHubjiaoxianjun/btle
9494个月前
BlueToolkit preview#7

BlueToolkit

GitHubsgxgsx/bluetoolkit
7431个月前
bettercap preview#8

bettercap

GitHubbettercap/bettercap
19.8k2个月前
toothpicker preview#9

toothpicker

GitHubseemoo-lab/toothpicker
2455年前
bluffs preview#10

bluffs

GitHubfrancozappa/bluffs
5242年前
最新相关性最受欢迎最近更新
250 结果
ble-cve2025-attack-new-version preview

ble-cve2025-attack-new-version

GitHubbloodcode-spasov/ble-cve2025-attack-new-version

# android-ble-cve-2025-4866 🔐 **PoC 针对 CVE-2025-4866 — Android BLE 漏洞(公开版本)** 📡 利用 Android 设备上的 BLE 授权漏洞(仅公开 PoC)。 👨💻 由 BloodCode Labs 开发 —…
android-securitybluetooth-securityvulnerability-analysis+3
51年前
DevicePairedTool preview

DevicePairedTool

GitHubelevenpaths/devicepairedtool

用于测试和审计蓝牙设备配对安全性的工具,能够识别无线配对协议和硬件物联网实现中的漏洞。
embedded-systems-securitybluetooth-securitywireless-security+3
58年前
CVE-2023-52709-PoC preview

CVE-2023-52709-PoC

GitHubkevinmitchell-oswp-cissp/cve-2023-52709-poc

PoC for 2023-52709 - TI 蓝牙协议栈可能无法生成可解析的随机私有地址 (RPA),导致已配对的设备遭受拒绝服务 (DoS) 攻击。
bluetooth-securityvulnerability-analysisexploitation+2
52年前
ShiningAppMask-ReverseEngineering preview

ShiningAppMask-ReverseEngineering

GitHubadrihd/shiningappmask-reverseengineering

Shining App Mask 的逆向工程
embedded-systems-securitybluetooth-securityiot-security+5
69个月前
trackem preview

trackem

GitHubveteranop/trackem

被动设备追踪器 (Android)TrackEm Mobile 是一款实时、被动的 Wi-Fi + 蓝牙 LE 探测请求扫描器,专为 OSINT、红队行动和无线研究而设计。它监听主动广播 Wi-Fi 网络名称的客户端设备(手机、笔记本电脑、物联网设备)。
osintreconnaissancewi-fi-auditing+6
410个月前
packages_apps_Bluetooth_AOSP10_r33_CVE-2022-20126 preview

packages_apps_Bluetooth_AOSP10_r33_CVE-2022-20126

GitHubtrinadh465/packages_apps_bluetooth_aosp10_r33_cve-2022-20126

带有 CVE-2022-20126 补丁的 Android 蓝牙包,修复了 AOSP 10 中的一个安全漏洞。
android-securitybluetooth-securityvulnerability-analysis+2
34年前
cve-2024-0230-blue preview

cve-2024-0230-blue

GitHubkeldnorman/cve-2024-0230-blue

CVE-2024-0230 蓝牙 POC 的辅助脚本
bluetooth-securityvulnerability-analysisexploitation+2
42年前
CVE-2026-77812 preview

CVE-2026-77812

GitHubwh02m1/cve-2026-77812

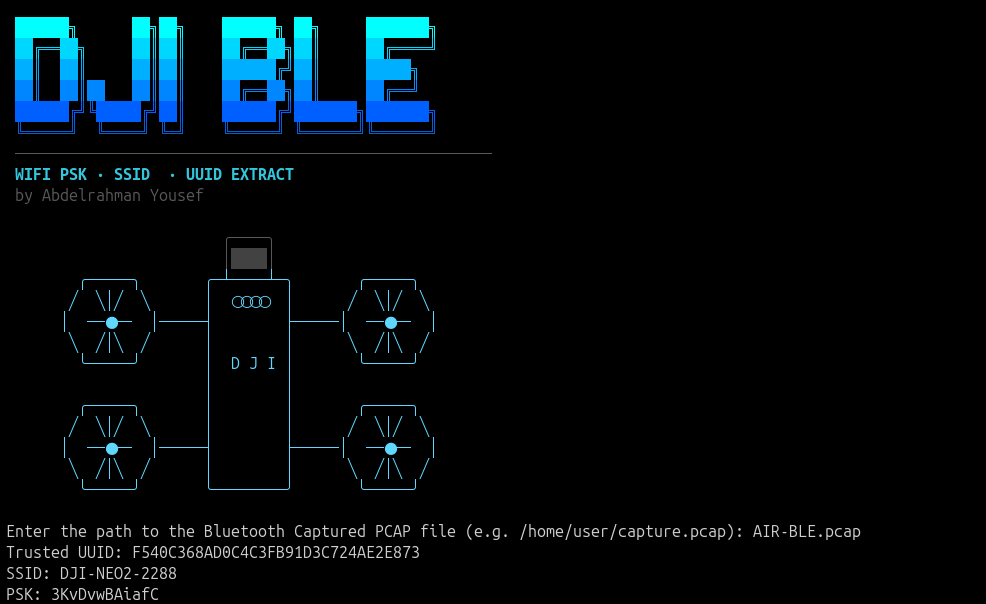
被动嗅探 DJI 无人机明文 BLE DUML 流量以恢复 Wi-Fi PSK 和受信任会话 UUID 的概念验证,演示 CVE-2026-77812。
packet-sniffing-analysisbluetooth-securityvulnerability-analysis+4
127天前
fwbt preview

fwbt

GitHubxen0bit/fwbt

用于通过 Bluetooth Low-Energy 与 Firewalla 交互以及利用 CVE-2024-40892 / CVE-2024-40893 的概念验证代码
bluetooth-securityiot-securityvulnerability-analysis+3
52年前
CVE-2026-22017-Firmware-Update-via-BLE-Without-Authentication preview

CVE-2026-22017-Firmware-Update-via-BLE-Without-Authentication

GitHubgeorge0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication

模拟 BLE 外设,暴露未认证的 GATT 固件更新特征;演示关键的 CVE-2026-22017 设备接管漏洞。
embedded-systems-securitybluetooth-securityiot-security+4
2个月前
CVE-2025-15474 preview

CVE-2025-15474

GitHubnsm-barii/cve-2025-15474

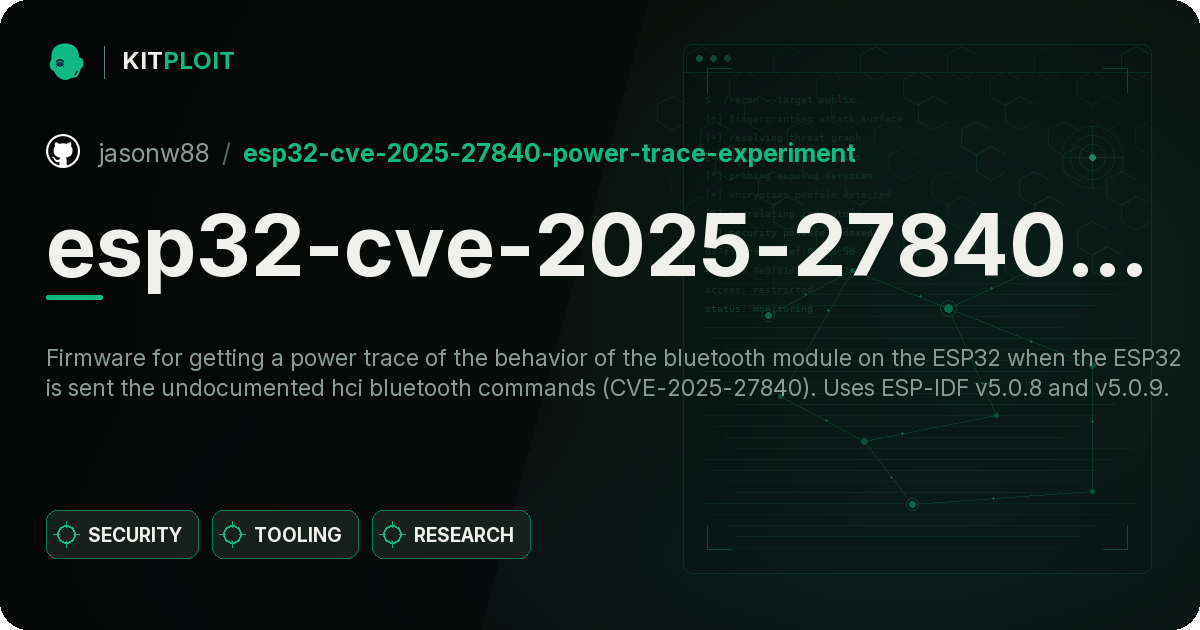
AuntyFey BLE 智能挂锁中的拒绝服务漏洞允许未经认证的连接洪泛将合法用户锁定在外。CVE-2025-15474
bluetooth-securityiot-securityvulnerability-analysis+4
410个月前
esp32-cve-2025-27840-power-trace-experiment preview

esp32-cve-2025-27840-power-trace-experiment

GitHubjasonw88/esp32-cve-2025-27840-power-trace-experiment

用于在向 ESP32 发送未记录的 hci 蓝牙命令(CVE-2025-27840)时获取 ESP32 上蓝牙模块行为的功耗迹线的固件。使用 ESP-IDF v5.0.8 和 v5.0.9。
embedded-systems-securitybluetooth-securityiot-security+2
2个月前
CVE-2026-11109-Bluetooth-Classic-KNOB-Attack-Key-Negotiation-of-Bluetooth- preview

CVE-2026-11109-Bluetooth-Classic-KNOB-Attack-Key-Negotiation-of-Bluetooth-

GitHubgeorge0papasotiriou/cve-2026-11109-bluetooth-classic-knob-attack-key-negotiation-of-bluetooth-

蓝牙经典 KNOB 攻击的 Python 模拟,展示加密密钥长度降级以及对拦截到的蓝牙流量进行暴力破解解密。
bluetooth-securityvulnerability-analysisexploitation+3
2个月前
CVE-2026-0101-BLE-Address-Spoofing-via-Weak-Resolvable-Private-Address preview

CVE-2026-0101-BLE-Address-Spoofing-via-Weak-Resolvable-Private-Address

GitHubgeorge0papasotiriou/cve-2026-0101-ble-address-spoofing-via-weak-resolvable-private-address

CVE-2026-0101 的 Python PoC,演示如何通过重放捕获的可解析私有地址(Resolvable Private Address)进行 BLE 地址欺骗,从而冒充受信任的外设。
bluetooth-securityiot-securityexploitation+3
2个月前
rinhit preview

rinhit

GitLabtoxy4ny/rinhit

收集 macOS 和 iOS 痕迹,构建网络活动、跨设备身份与物理位置关联的时间线,用于侦察和红队行动。
osintreconnaissancebluetooth-security+6
1个月前
bandexploit preview

bandexploit

GitHubcoleshelly/bandexploit

M1 Band 智能手表蓝牙低功耗漏洞利用 Python 脚本 (CVE-2018-11631)
bluetooth-securityiot-securityvulnerability-analysis+3
26年前
CVE-2023-45866_EXPLOITS preview

CVE-2023-45866_EXPLOITS

GitHubavishekdhakal/cve-2023-45866_exploits

已在 Mi A2 Lite 和 Realme 2 pro 中测试的漏洞利用
android-securitybluetooth-securityvulnerability-analysis+3
22年前
smart-sketcher-upload preview

smart-sketcher-upload

GitHubdavidrxchester/smart-sketcher-upload

利用 smART Sketcher 2.0 玩具投影仪上的蓝牙认证绕过漏洞,允许通过 Python 脚本进行未经认证的连接和图像上传。

bluetooth-securityiot-securityvulnerability-analysis+4
39个月前
上一页1…8910…14下一页