 antropos17/aegis
Windows-first desktop oversight for AI agents: live monitoring, local security reviews, token usage, audit reports and opt-in action policies/MCP gateways. Experimental Hyper-V guest execution; macOS/Linux experimental.

Local AI-agent monitoring, security reviews and explicitly configured action controls.
Install · Use AEGIS · Current development · Documentation · Contribute
Windows beta: 0.19.2-beta, published 6 October 2026. Verify the installer · Beta readiness
Current source version: 0.19.2-beta Later source work is described below. Installed builds contain the features at their release tag.
| Area | Coverage |
|---|---|
| Processes | 112 agents (265 process-name signatures), process trees, IDE-host and extension detection; Windows primary, macOS/Linux experimental |
| Files | Changes in configured sensitive directories and agent config paths; Windows open-handle and Restart Manager observations |
| Network | TCP endpoints for detected agent PIDs, endpoint names and allowlisted / unknown / flagged verdicts |
| Behavior | 73 sensitive-path detection rules across 8 categories, rolling 10-session baselines, anomaly scoring and sequence evidence |
| Resources and usage | CPU/RAM charts, local LLM probes, Claude Code token subtotals and estimated costs |
| Runtime inventory | Running WSL distribution names and local Docker/Linux-native Podman candidates; explicit freshness, no guest process inspection |
| Local review | Project, skill and profile inventory; static findings, saved snapshot comparison and offline report import |
| Investigation | Agent instances, file/network views, alerts, audit history, statistics and JSON/CSV/HTML/ZIP exports |
Monitoring requires no agent plugin or subscription. Default monitoring observes and logs; it does not automatically block commands or contain agents. Kill, suspend and resume are manual actions. See the full capability guide.
Download the installer, manifest.json and manifest.json.sig from the same
GitHub release, then follow
offline verification. Release notes describe that
installer's features.
Install the first beta manually after verification: the published 0.17.0-alpha updater cannot discover beta releases. When upgrading from 0.14.1-alpha or older, install 0.15.0-alpha or newer manually before using signed in-app updates.
Requires Node.js 24.16.0 or later in the 24.x line. Source uses Electron 44 and 64-bit platforms; macOS requires version 13 or later. Windows 10/11 is primary; macOS/Linux remain experimental.
git clone https://github.com/antropos17/Aegis.git
cd Aegis
npm ci
npm start
On Windows, run npm run build:sidecar after npm ci for native Job/MCP routes
and native-helper tests. Linux process actions additionally require Python 3.9+
at /usr/bin/python3 and kernel pidfd support; see Linux process control.
The development workflow covers helper builds and checks.
npm run dev
# open http://127.0.0.1:8770
The preview shares desktop components and uses simulated data with an isolated
host. It disables native exports and provider requests. npm run frontend:build:preview
builds that preview; npm run build:renderer builds the desktop renderer.
Source opens Advanced navigation by default. Simple interface in Settings offers investigation, file checks and settings; a saved Simple choice is retained.
| Task | Start here |
|---|---|
| See agents and their activity | Monitoring, then an agent's processes, files or connections |
| Review a sensitive-file alert | Alerts, then inspect the captured evidence |
| Inspect a Windows file read | Events → Folder to monitor → Start file read monitoring; setup and limits |
| Review a project, skill or profile | Local security |
| Check a selected action against a policy | Action control |
| Configure selected-action MCP tools | Terminal setup |
| Find other tools | Start here or Commands (Ctrl K); workspace guide |
| Monitoring | Local security |
|---|---|
 |  |
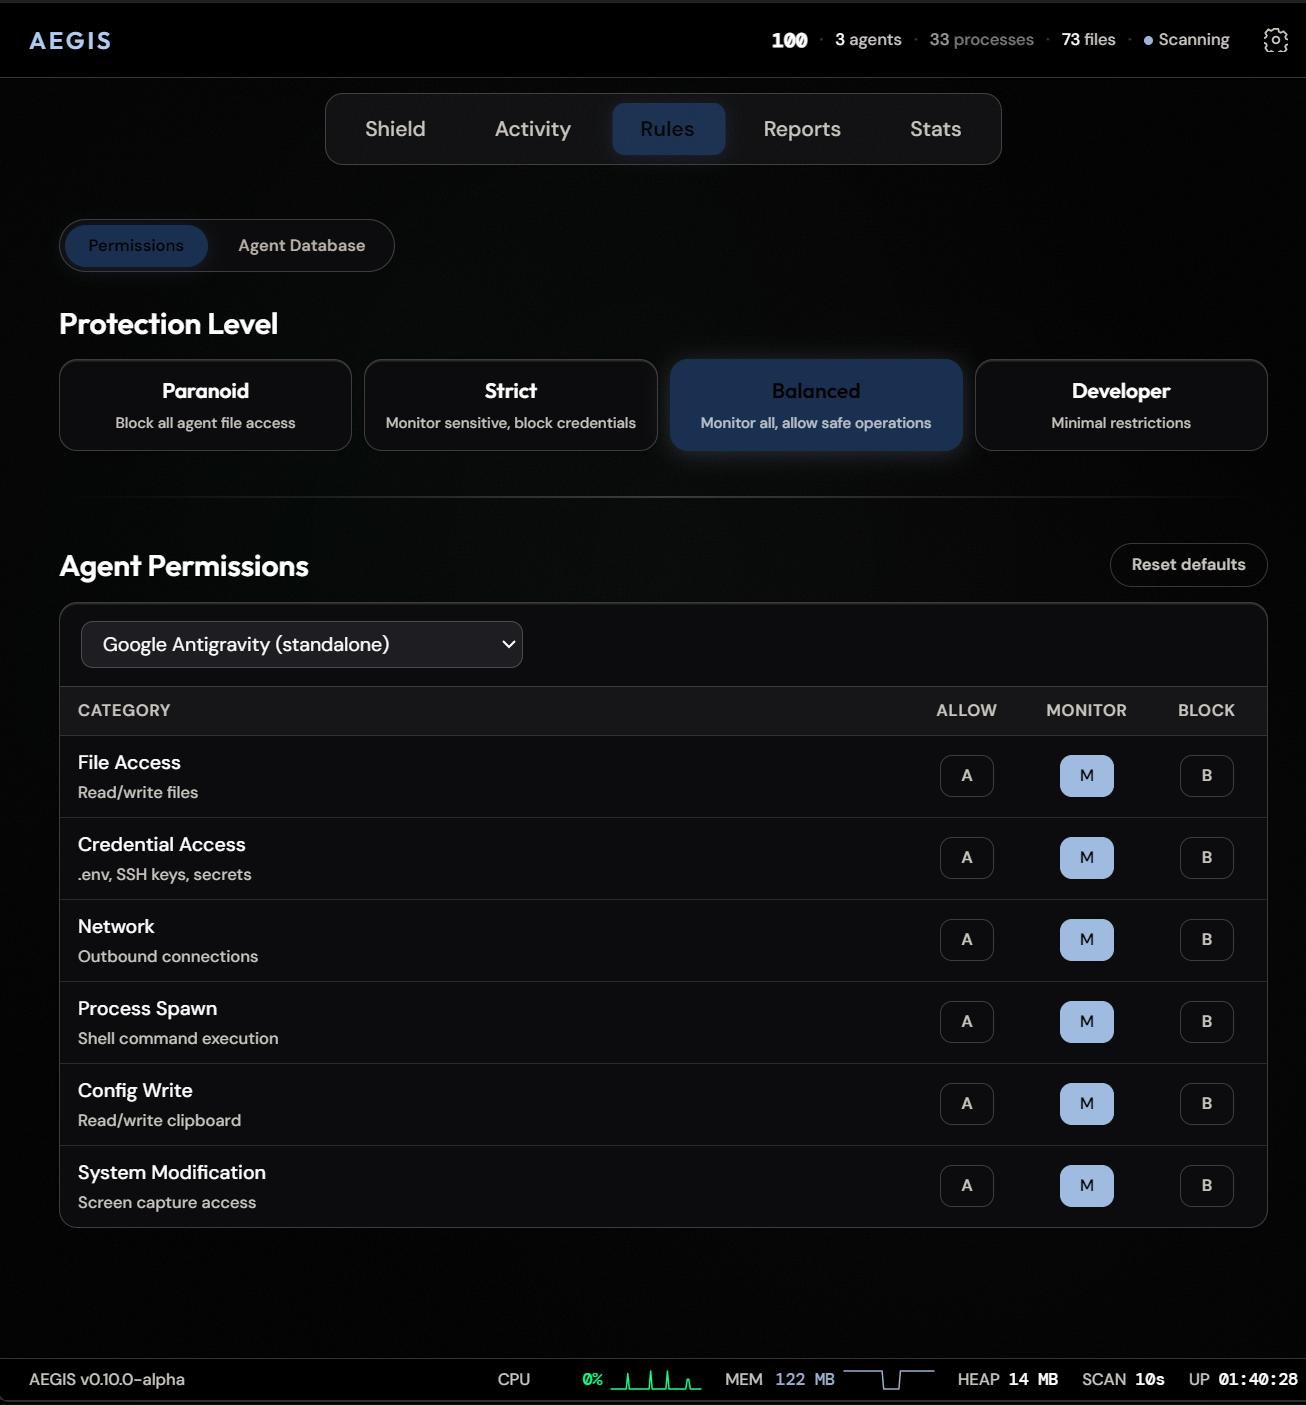
These are simulated source UI captures from 11 October 2026. All screenshots and provenance.
Windows x64 packages include experimental Kernel-File reads. In Events, choose a local folder and explicitly start capture with manual UAC consent. It stays off on startup and stops on Stop, monitoring pause, suspend or quit. Events can display a read, its verified issuing agent and Potential sensitive read from path rules. Paths remain candidates, and the label does not establish malicious intent or change risk scores.
Monitoring data stays local, with no usage telemetry or cloud sync. Endpoint naming uses DNS; update checks contact GitHub. Optional Anthropic analysis sends activity metadata on request using your own API key and incurs that service's charges. See privacy and key handling.
These routes require explicit setup and cover selected actions only. They do not intercept other agent tools, arbitrary MCP traffic or activity outside the route.
