
 #1
Инструменты для поддержания доступа, исследования и расширения контроля в скомпрометированных системах и сетях.
Рекомендация Kitploit

 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
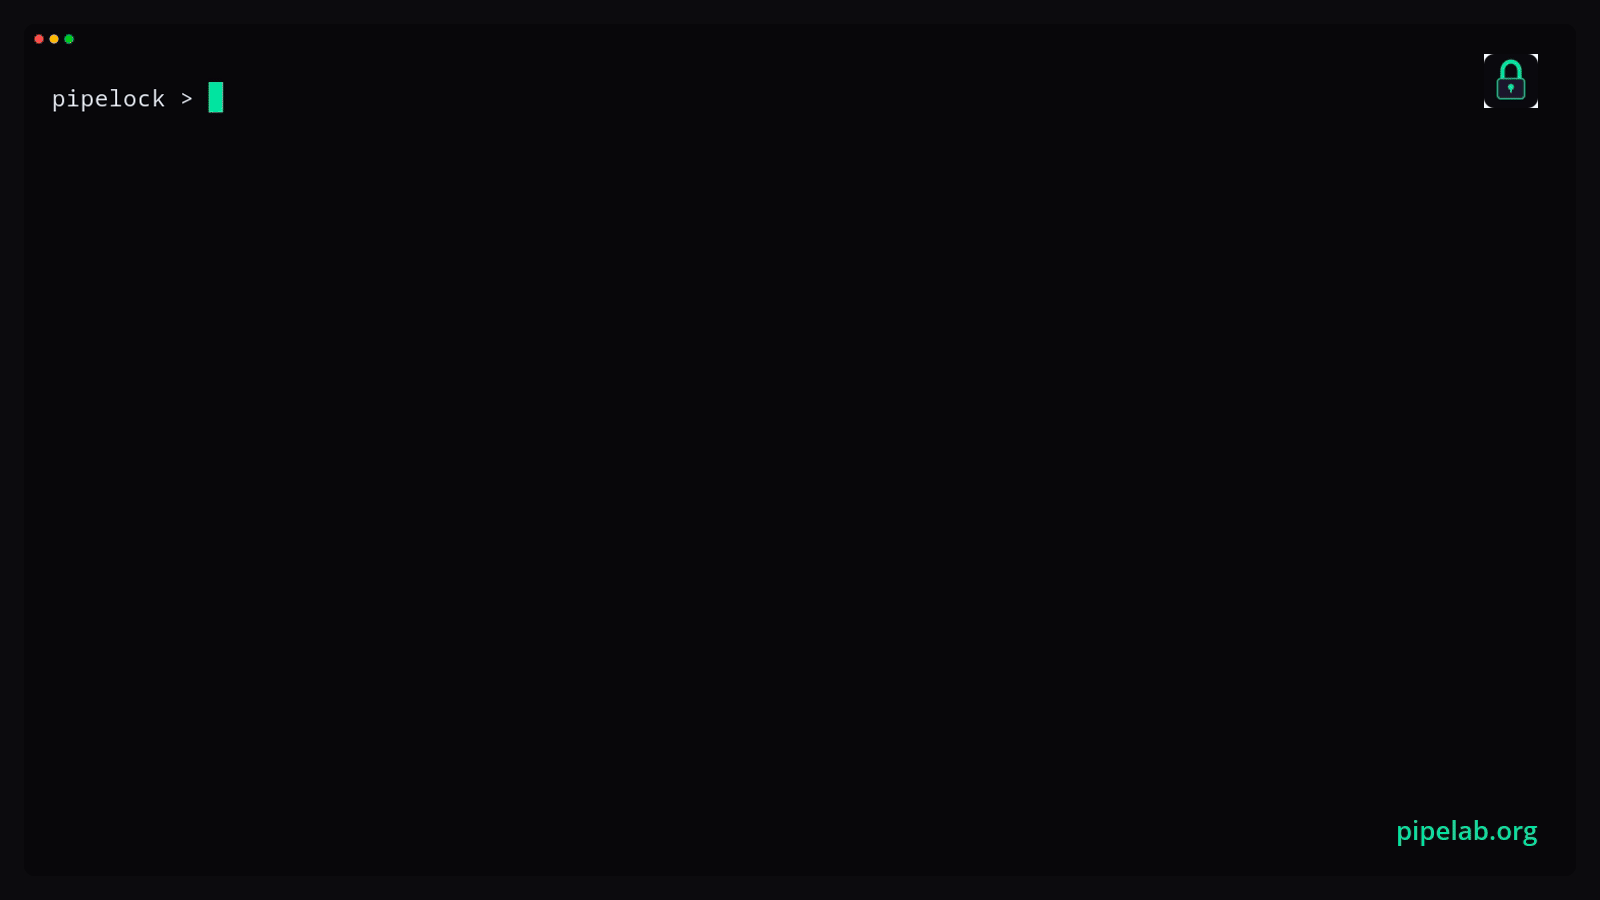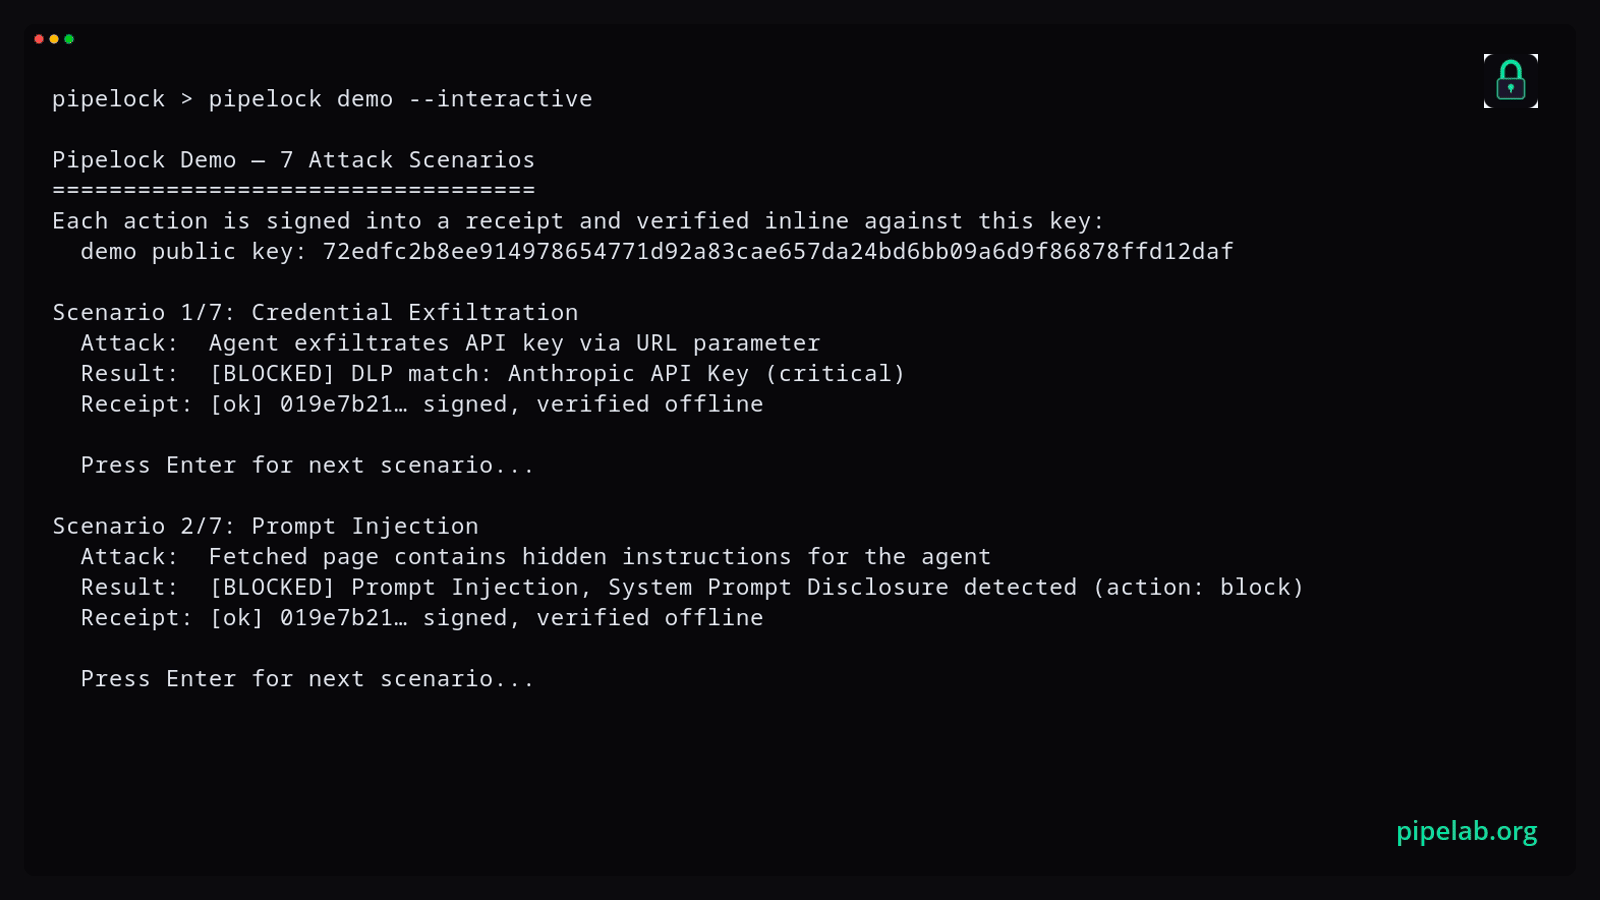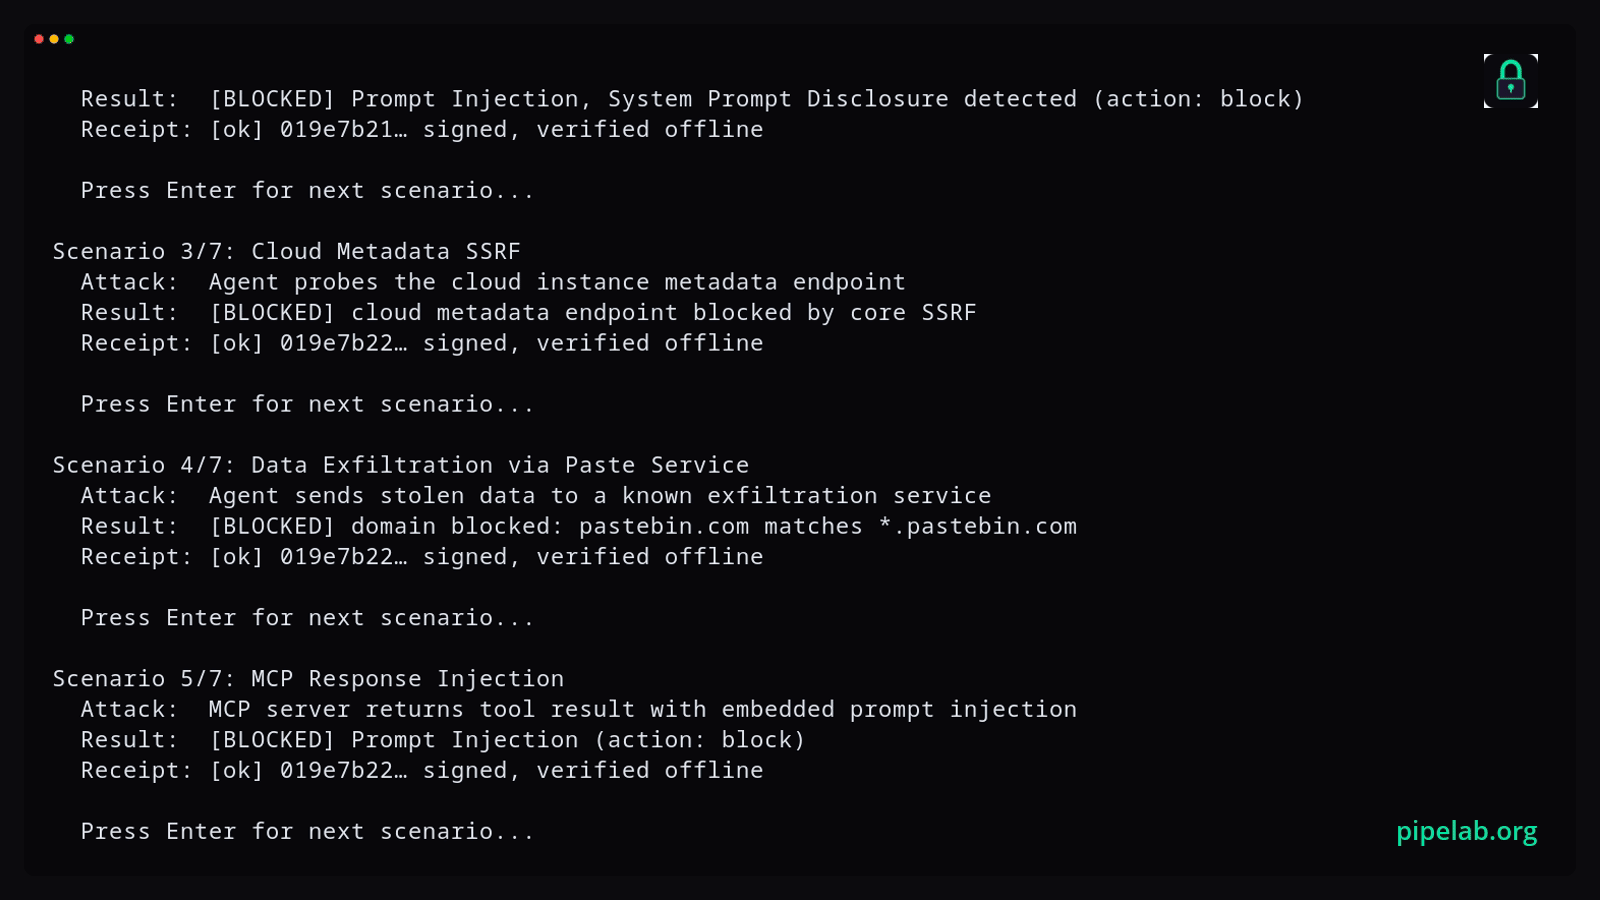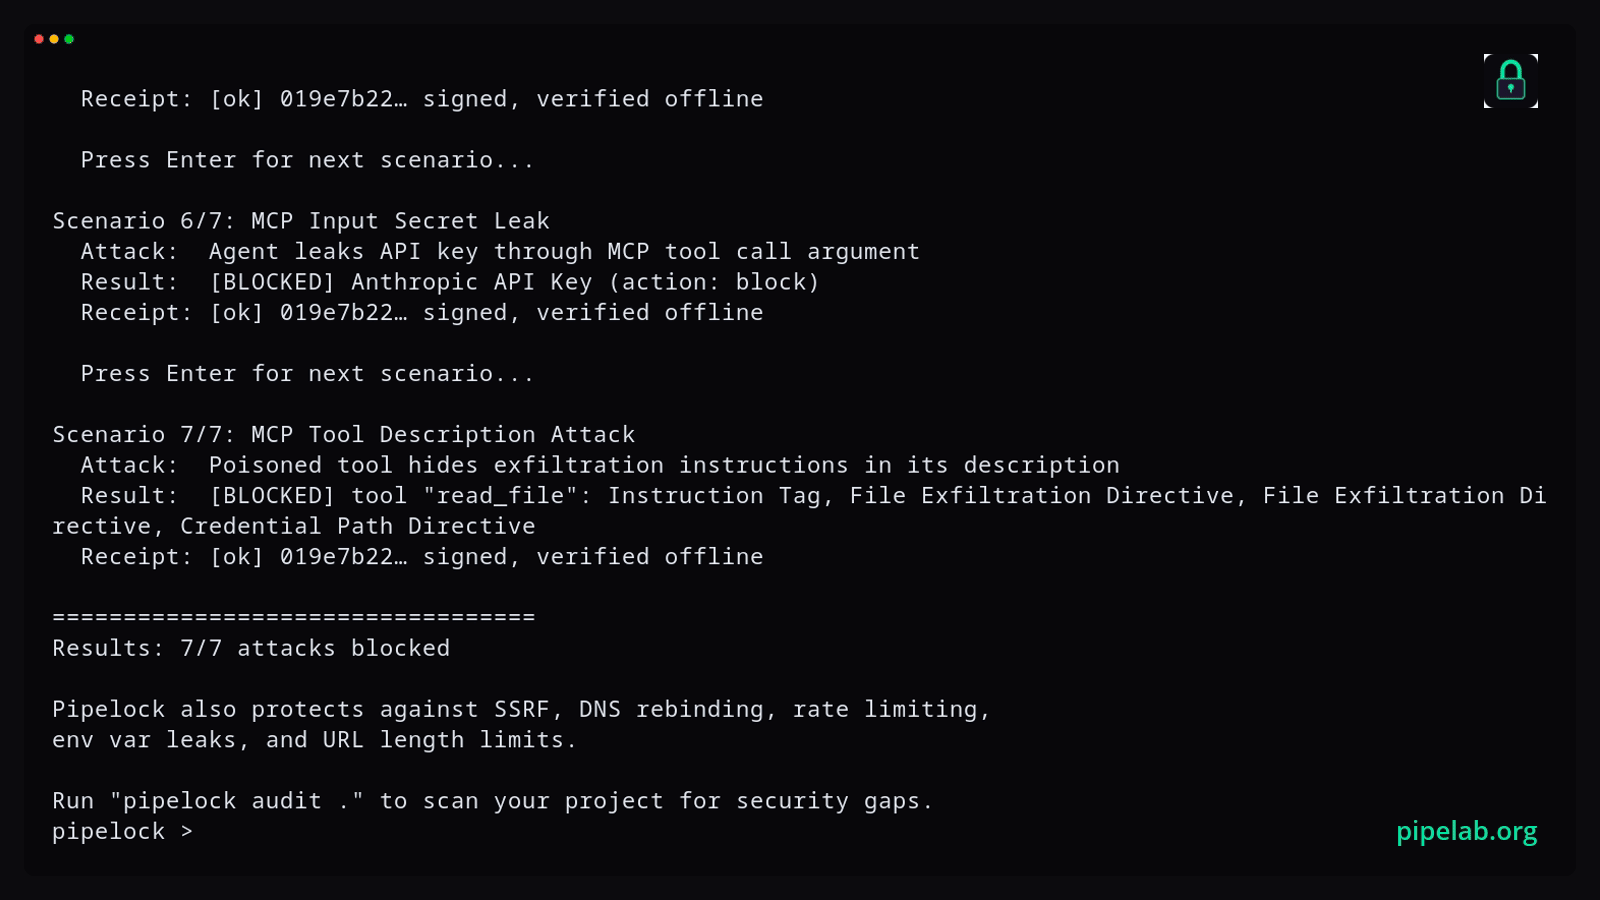 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 yaklang/yakit
Универсальная платформа для тестирования на проникновение с MITM-прокси, веб-фаззером, обработчиком обратных соединений и системой плагинов для…
 rapid7/metasploit-framework
Фреймворк для эксплуатации с открытым исходным кодом, включающий модульные полезные нагрузки, кодировщик и вспомогательную систему для тестирования…
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 hacktricks-wiki/hacktricks
Добро пожаловать на страницу, где вы найдёте каждый трюк/технику/что угодно, чему я научился в CTF, реальных приложениях, а также читая исследования…
 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
 purpleailab/decepticon
Автономный хакерский агент для Red Team
 sheeki03/tirith
Терминальная безопасность для разработчиков и агентов ИИ. Перехватывает гомографные URL, конвейер к оболочке, ANSI-инъекции, обфусцированные полезные…
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
 securewithumer/cve-2026-pocs
Exploit-Index : The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 infostealers-stats/data-breach
A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…
 deathshotxd/0xm0ncrush
Убийца процессов в режиме ядра с использованием подписанного драйвера BYOVD. Работает на всех Windows 10/11. Без смещений, без PDB. Rust.








