 shadowy-pycoder/go-http-proxy-to-socks
Proxy CLI MITM que converte SOCKS4/SOCKS5 em proxy HTTP/HTTPS/HTTP2/HTTP3 com redirecionamento transparente de TCP/UDP, spoofing ARP/NDP/DNS, sniffing de tráfego e captura de pacotes. Puramente em Go, sem libpcap.

# GoHPTS - Proxy transparente HTTP(S) e TCP/UDP para proxy SOCKS4/SOCKS5 (cadeia) escrito em Go
[](https://www.gnu.org/licenses/gpl-3.0)
[](https://pkg.go.dev/github.com/shadowy-pycoder/go-http-proxy-to-socks)



## Índice
- [Introdução](#introdução)
- [Funcionalidades](#funcionalidades)
- [Instalação](#instalação)
- [Utilização](#utilização)
- [Configuração via flags da CLI](#configuração-via-flags-da-cli)
- [Configuração via ficheiro YAML](#configuração-via-ficheiro-yaml)
- [Proxy transparente](#proxy-transparente)
- [redirect (via NAT e SO_ORIGINAL_DST)](#redirect-via-nat-e-so_original_dst)
- [Configuração automática para o modo redirect](#configuração-automática-para-o-modo-redirect)
- [tproxy (via MANGLE e IP_TRANSPARENT)](#tproxy-via-mangle-e-ip_transparent)
- [Configuração automática para o modo tproxy](#configuração-automática-para-o-modo-tproxy)
- [Suporte UDP](#suporte-udp)
- [Suporte Android](#suporte-android)
- [Configuração YAML](#configuração-yaml)
- [Sniffing de tráfego](#sniffing-de-tráfego)
- [Formato JSON](#formato-json)
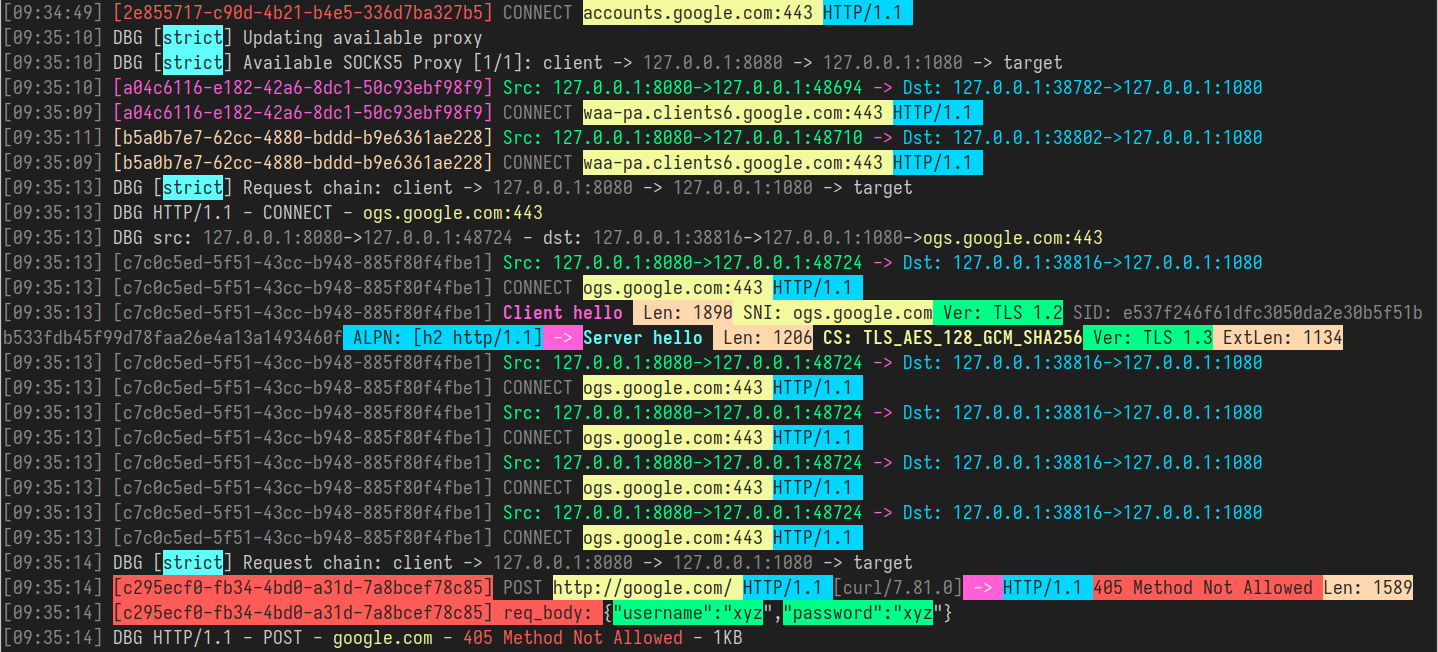
- [Formato colorido](#formato-colorido)
- [Suporte HTTP2 e HTTP3](#suporte-http2-e-http3)
- [Exemplo de configuração usando certificado autoassinado](#exemplo-de-configuração-usando-certificado-autoassinado)
- [Testar ligação](#testar-ligação)
- [Testar ligação num navegador](#testar-ligação-num-navegador)
- [Suporte IPv4 e IPv6](#suporte-ipv4-e-ipv6)
- [ARP spoofing](#arp-spoofing)
- [NDP spoofing](#ndp-spoofing)
- [DNS spoofing](#dns-spoofing)
- [Captura de pacotes](#captura-de-pacotes)
- [Network Namespaces](#network-namespaces)
- [Configuração do playground](#configuração-do-playground)
- [Exemplos de utilização](#exemplos-de-utilização)
- [Mixed Server](#mixed-server)
- [Ligações](#ligações)
- [Contribuir](#contribuir)
- [Licença](#licença)
## Introdução
[[Voltar]](#índice)
A ferramenta CLI `GoHPTS` é uma ponte entre clientes HTTP e um servidor proxy SOCKS5 ou múltiplos servidores (cadeia). Escuta localmente como um proxy HTTP, aceita pedidos HTTP
ou HTTPS padrão (via CONNECT) e encaminha a ligação através de um proxy SOCKS5. Inspirado em [http-proxy-to-socks](https://github.com/oyyd/http-proxy-to-socks) e [Proxychains](https://github.com/rofl0r/proxychains-ng)
Caso de uso possível: precisa de se ligar a uma API externa via Postman, mas essa API só está disponível a partir de algum servidor remoto.
Os seguintes comandos irão ajudá-lo a realizar essa tarefa:
Criar um servidor proxy SOCKS5 via `ssh`:```shell
ssh <remote server> -D 1080 -Nf
```
Crie uma conexão HTTP-para-SOCKS5 com `gohpts````shell
gohpts -s :1080 -l :8080
```
Especifique o servidor http na configuração de proxy do Postman
## Recursos
[[Voltar]](#table-of-contents)
- **Funcionalidade de Cadeia de Proxy**\
Suporta cadeias `strict`, `dynamic`, `random`, `round_robin` de proxy SOCKS4/SOCKS5
- **Proxy transparente**\
Suporta modos `redirect` (SO_ORIGINAL_DST) e `tproxy` (IP_TRANSPARENT)
- **Suporte a IPv4 e IPv6**\
Opera em modos `IPv4-only`, `IPv6-only` ou `dual stack`
- **Proxy transparente TCP e UDP**\
`tproxy` e `tlocal` (IP_TRANSPARENT) lidam com tráfego TCP e UDP
- **Sniffing de tráfego**\
O proxy é capaz de analisar cabeçalhos HTTP, handshake TLS, mensagens DNS e mais
- **ARP spoofing**\
Faça proxy de sub-redes inteiras com a abordagem de ARP spoofing
- **NDP spoofing**\
Faça proxy de conexões IPv6 usando Router/Neighbor Advertisement e injeções RDNSS.
- **DNS spoofing**\
Redirecione clientes para domínios arbitrários usando manipulação de registros DNS
- **Captura de Pacotes**\
Capture tráfego em arquivos txt/pcap/pcapng e analise com o Wireshark
- **Proteção contra Vazamento de DNS**\
A resolução DNS ocorre no lado do servidor SOCKS5.
- **Suporte ao Método CONNECT**\
Suporta tunelamento HTTP CONNECT, permitindo HTTPS e outros protocolos baseados em TCP.
- **Suporte a HTTP2/HTTP3**\
Suporta transporte moderno HTTP/2 e HTTP/3, permitindo conexões multiplexadas eficientes sobre TLS 1.3
- **Suporte a Network Namespaces**\
Suporta network namespaces personalizados do Linux para sockets de escuta e conexões de saída
- **Suporte a Trailer Headers**\
Lida com cabeçalhos trailer HTTP
- **Chunked Transfer Encoding**\
Lida com respostas chunked e streaming
- **Suporte a Autenticação SOCKS5**\
Suporta autenticação por nome de usuário/senha para proxies SOCKS5.
- **Suporte a Autenticação HTTP**\
Suporta autenticação por nome de usuário/senha para servidor proxy HTTP.
- **Leve e Rápido**\
Projetado com sobrecarga mínima e manipulação eficiente de requisições.
- **Multiplataforma**\
Compatível com todos os principais sistemas operacionais.
## Instalação
[[Voltar]](#table-of-contents)
- Arch Linux/CachyOS/EndeavourOS ```shell
yay -S gohpts
```
Ou usando `paru`: ```shell
paru -S gohpts
```
- Baixe o binário para a sua plataforma na página de [Releases](https://github.com/shadowy-pycoder/go-http-proxy-to-socks/releases): ```shell
GOHPTS_RELEASE=v1.15.6; wget -v https://github.com/shadowy-pycoder/go-http-proxy-to-socks/releases/download/$GOHPTS_RELEASE/gohpts-$GOHPTS_RELEASE-linux-amd64.tar.gz -O gohpts && tar xvzf gohpts && mv -f gohpts-$GOHPTS_RELEASE-linux-amd64 gohpts && ./gohpts -h
```
- Instale usando o comando `go install` (requer Go [1.26](https://go.dev/doc/install) ou posterior): ```shell
CGO_ENABLED=0 go install -ldflags "-s -w" -trimpath github.com/shadowy-pycoder/go-http-proxy-to-socks/cmd/gohpts@latest
```
Isso instalará o binário `gohpts` no seu diretório `$GOPATH/bin`.
- Compilar a partir do código-fonte: ```shell
git clone https://github.com/shadowy-pycoder/go-http-proxy-to-socks.git
cd go-http-proxy-to-socks
make build
./bin/gohpts
```
- Executar no docker: ```shell
docker run -it --privileged --network host -v "$PWD/gohpts.yaml:/config.yaml" shadowypycoder/gohpts:latest -f config.yaml
```
## Uso
[[Voltar]](#table-of-contents)```shell
gohpts -h
_____ _ _ _____ _______ _____
/ ____| | | | | __ \__ __/ ____|
| | __ ___ | |__| | |__) | | | | (___
| | |_ |/ _ \| __ | ___/ | | \___ \
| |__| | (_) | | | | | | | ____) |
\_____|\___/|_| |_|_| |_| |_____/
GoHPTS: HTTP(S) Proxy to SOCKS4/SOCKS5 proxy by shadowy-pycoder
GitHub: https://github.com/shadowy-pycoder/go-http-proxy-to-socks
Codeberg: https://codeberg.org/shadowy-pycoder/go-http-proxy-to-socks
Usage: gohpts [OPTIONS]
OPTIONS:
General:
-h Show this help message and exit
-v Show version and build information
-D Run as a daemon (provide -logfile to see logs)
-I Display list of network interfaces and exit
-f Path to proxy configuration file in YAML format
Proxy:
-l Address of HTTP proxy server (Default: "127.0.0.1:8080" for IPv4, "[::1]:8080" for IPv6)
-s Address of SOCKS proxy server (Default: "127.0.0.1:1080" for IPv4 "[::1]:1080" for IPv6)
-c Path to certificate PEM encoded file
-k Path to private key PEM encoded file
-U User for HTTP proxy (basic auth). This flag invokes prompt for password (not echoed to terminal)
-u User for SOCKS proxy authentication. This flag invokes prompt for password (not echoed to terminal)
-i Bind proxy to specific network interface (either by interface name or index)
-4 Force IPv4 stack for TCP and UDP (Default: dual stack)
-6 Force IPv6 stack for TCP and UDP (Default: dual stack)
-socks4 Use SOCKS4/SOCKS4a protocol for upstream proxy and mixed server (default: SOCKS5/SOCKS5h)
-nohttp Disable HTTP proxy server
-nosocks Disable SOCKS upstream proxy
-dns Use custom DNS server (Example: "8.8.8.8" or "2001:4860:4860::8888")
-mixed Accept SOCKS connections on HTTP proxy server address
Logs:
-d Show logs in DEBUG mode
-j Show logs in JSON format
-logfile Log file path (Default: stdout)
-nocolor Disable colored output for logs (no effect if -j flag specified)
-pprof Address of pprof server with profiling data
Sniffing:
-sniff Enable traffic sniffing for HTTP and TLS
-snifflog Sniffed traffic log file path (Default: the same as -logfile)
-body Collect request and response body for HTTP traffic (credentials, tokens, etc)
TProxy:
-T Address of transparent proxy server
-Tu Address of transparent UDP proxy server
-M Transparent proxy mode: (redirect, tproxy, tlocal)
-w Number of instances of transparent proxy server (Default: number of CPU cores)
-wu Number of instances of transparent UDP proxy server (Default: number of CPU cores)
-auto Automatically setup iptables and kernel parameters for transparent proxy (requires elevated privileges)
-mark Set mark for each packet sent through transparent proxy (Default: redirect 0, tproxy 100, tlocal 100)
-A Comma separated list of allowed ip addresses for proxying (Example: "8.8.8.8,2001:4860:4860::8888,192.168.1.0/24")
-P Comma separated list of ports to ignore when proxying traffic (Example: "22,80,443,9092")
-dump Dump iptables rules and other system settings generated by -auto flag
Spoofing:
-arpspoof Enable ARP spoof proxy for selected targets (Example: "targets 10.0.0.1,10.0.0.5-10,192.168.1.*,192.168.10.0/24;fullduplex false;debug true;interval 10s")
-ndpspoof Enable NDP spoof proxy for selected targets (Example: "ra true;na true;targets fe80::3a1c:7bff:fe22:91a4;fullduplex false;debug true;interval 10s")
Packet Capture:
-pcap Enable packet capture (Example: "promisc true;expr ip proto tcp;snaplen 65535;timeout 10s;packet_count 100;packet_buffer 8192;exts txt,pcap,pcapng")
Namespaces:
-in-netns Name or path of network namespace for inbound listeners (Default: default namespace)
-out-netns Name or path of network namespace for outbound connections (Default: default namespace)
```
### Configuração via flags da CLI
[[Voltar]](#table-of-contents)```shell
gohpts -s 1080 -l 8080 -d -j
```
Saída:```shell
{"level":"info","time":"2025-05-28T06:15:18+00:00","message":"SOCKS5 Proxy: :1080"}
{"level":"info","time":"2025-05-28T06:15:18+00:00","message":"HTTP Proxy: :8080"}
{"level":"debug","time":"2025-05-28T06:15:22+00:00","message":"HTTP/1.1 - CONNECT - www.google.com:443"}
```
Especifique o nome de usuário e a senha para o servidor proxy SOCKS5:```shell
gohpts -s 1080 -l 8080 -d -j -u user
SOCKS5 Password: #you will be prompted for password input here
```
Especifique o nome de usuário e a senha para o servidor proxy HTTP:```shell
gohpts -s 1080 -l 8080 -d -j -U user
HTTP Password: #you will be prompted for password input here
```
Quando ambos `-u` e `-U` estão presentes, você será solicitado duas vezes
Executar proxy http sobre conexão TLS```shell
gohpts -s 1080 -l 8080 -c "path/to/certificate" -k "path/to/private/key"
```
Execute o proxy como um daemon (o arquivo de log é necessário para a saída de log, caso contrário você não verá nada)```shell
gohpts -D -logfile /tmp/gohpts.log
```
Please provide the Markdown content to translate.```shell
# output
gohpts pid: <pid>
```
| | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | | |```shell
# kill the process
kill <pid>
#or
kill $(pidof gohpts)
```
`-u` e `-U` não funcionam em modo daemon (e, portanto, na autenticação), mas você pode fornecer um arquivo de configuração (veja abaixo)
### Configuração via arquivo YAML
[[Voltar]](#table-of-contents)
Arquivos de configuração são úteis quando você quer pré-configurar seu proxy sem mexer muito na CLI ou apenas quer múltiplos perfis para necessidades diferentes.
Executar proxy http em modo de cadeia de proxy SOCKS5 (especifique as configurações do servidor via arquivo de configuração YAML)```shell
gohpts -f "~/gohtps.yaml" -d -j
```
Exemplo de configuração:```yaml
# bind proxy to specific network interface (either by interface name or index)
interface: "eth0" # if specified, overrides http server IP address
disable_http: false # disable http proxy (default: false)
disable_socks: false # disable upstream socks proxy (default: false)
# if ipv4 and ipv6 are both false or both true, dual stack is assumed
ipv4: false # this must be enabled for arpspoof (default: false)
ipv6: false # this must be enabled for ndpspoof (default: false)
socks4: false # use SOCKS4/SOCKS4a protocol (tcp only protocol, no udp tproxy or http3 possible) (default: false)
dns: 8.8.8.8 # custom DNS server (used in direct dialer, namespaces, spoofing)
http_server:
address: 127.0.0.1:8080
# username and password for adding basic authentication (comment out to disable auth)
username: username
password: password
# list of socks5 proxy
# if proxy_chain is disabled, uses first server in a list as upstream
proxy_list:
- address: 127.0.0.1:1080
- address: 127.0.0.1:1081
- address: :1082 # empty host means localhost
proxy_chain:
enabled: false
# Explanations for chains taken from /etc/proxychains4.conf
# strict - Each connection will be done via chained proxies
# all proxies chained in the order as they appear in the list
# all proxies must be online to play in chain
# dynamic - Each connection will be done via chained proxies
# all proxies chained in the order as they appear in the list
# at least one proxy must be online to play in chain
# (dead proxies are skipped)
# random - Each connection will be done via random proxy
# (or proxy chain, see chain_len) from the list.
# this option is good to test your IDS :)
# round_robin - Each connection will be done via chained proxies
# of chain_len length
# all proxies chained in the order as they appear in the list
# at least one proxy must be online to play in chain
# (dead proxies are skipped).
# the start of the current proxy chain is the proxy after the last
# proxy in the previously invoked proxy chain.
# if the end of the proxy chain is reached while looking for proxies
# start at the beginning again.
# These semantics are not guaranteed in a multithreaded environment.
type: strict # dynamic, strict, random, round_robin
length: 2 # maximum number of proxy in a chain (works only for random chain and round_robin chain)
logging:
debug: true
json: false
# defaults to standard output
#logfile: /tmp/gohpts.log
# use colored output in logs (no effect if json enabled)
nocolor: false
# profiling data
pprof: 127.0.0.1:8081
```
Você pode substituir quase todas as configurações especificadas no arquivo de configuração fornecendo os sinalizadores CLI correspondentes:```shell
gohpts -l :6969 -f "~/gohtps.yaml" -nocolor
```
O Proxy usa todas as configurações especificadas em `~/gohpts.yaml`, mas inicia o servidor http em `127.0.0.1:6969` em vez de `127.0.0.1:8080` e também desativa a saída colorida nos logs.
Algumas configurações (por exemplo, proxy_chain e filtros dns) só podem ser configuradas via arquivo.
---
[Read more](https://github.com/shadowy-pycoder/go-http-proxy-to-socks)







