

Skip to content
KitploitKITPLOIT
FerramentasExploitsBlog
Log in
Enviar
FerramentasExploitsBlog
Enviar

Ferramentas de Hacking, PenTest e Cibersegurança para o seu Arsenal de Segurança!

Kitploit é um diretório de ferramentas de hacking, cibersegurança e pentesting. Descubra as últimas atualizações de projetos para encontrar vulnerabilidades, analisar sistemas, automatizar testes e fortalecer sua segurança.

FeedsContatoPrivacidade© 2026 Kitploit

Diretório de Ferramentas

Categorias

Ver todas as categorias
Loading categories
rhabdomancer — Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file. | Kitploit
Ferramentas/GitHubGitHub/0xdea/rhabdomancer
Static AnalysisVulnerability AnalysisReverse EngineeringBinary Analysis
GitHub0xdea/rhabdomancer

rhabdomancer

Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.

Ver Repositório
1311553há 16 horasRevisado pelo Kitploit
Site
Compartilhar
Conteúdo não disponível no idioma solicitado. Mostrando versão em inglês.

rhabdomancer

build doc

"The road to exploitable bugs is paved with unexploitable bugs."

-- Mark Dowd

Rhabdomancer is a blazing-fast IDA headless plugin that locates calls to potentially insecure API functions in a binary file. Auditors can backtrace from these candidate points to find pathways allowing access to untrusted input.
Features

  • Blazing-fast, headless user experience courtesy of IDA 9.x and idalib-rs Rust bindings.
  • Support for C/C++ binary targets compiled for any architecture implemented by IDA.
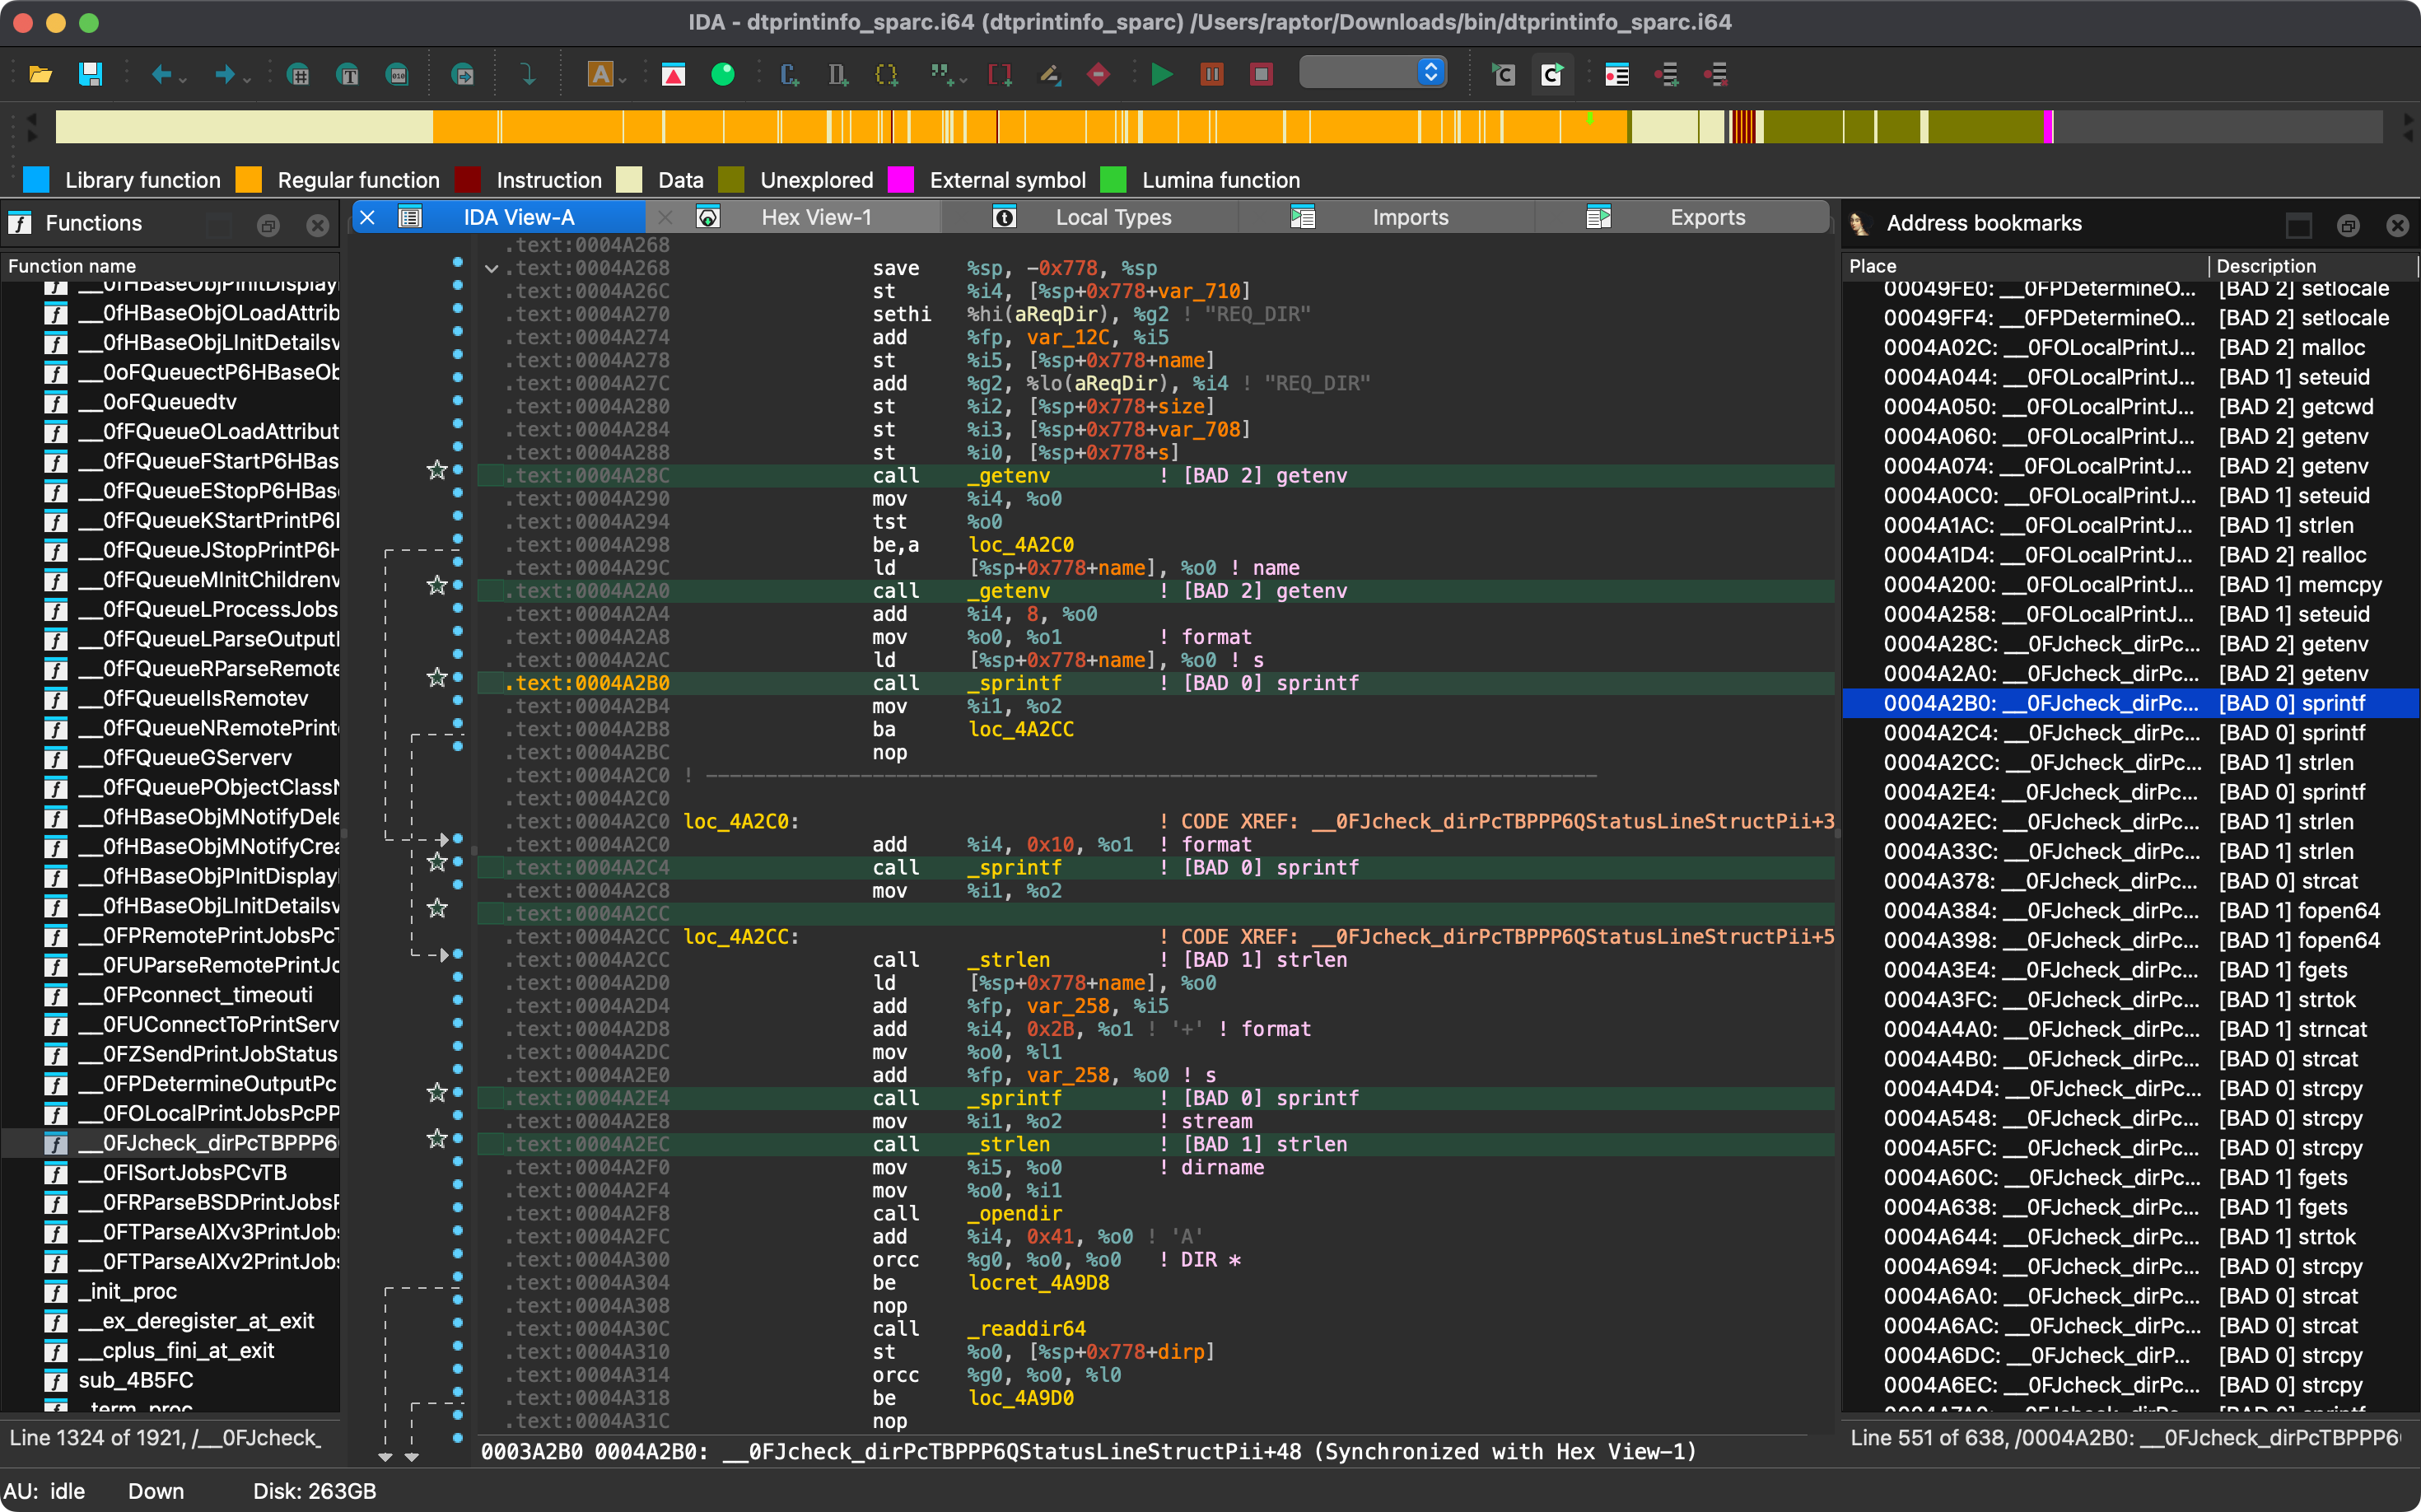
  • Bad API function call locations are printed to stdout and marked in the IDB.
    • Call locations in library code recognized by IDA (e.g., a statically linked runtime matched by FLIRT signatures) are labeled (lib).
    • Calls through stubs (e.g., the .plt entries of ELF binaries or the import stubs of PE and Mach-O binaries, listed as thunks) are traced back to their callers.
    • In ELF binaries, a function is deliberately listed twice with the same call locations: once as its .plt stub (marked as thunk) and once as its import. Each call location is marked only once in the IDB.
  • Known bad API functions are grouped in tiers of badness to help prioritize the audit work.
    • [BAD 0] High priority - Functions that are generally considered insecure.
    • [BAD 1] Medium priority - Interesting functions that should be checked for insecure use cases.
    • [BAD 2] Low priority - Code paths involving these functions should be carefully checked.
  • The list of known bad API functions is built in and can be easily customized with a configuration file based on conf/rhabdomancer.toml.
  • Function names are matched without these decorations: the # marking native ARM64EC functions (e.g., #memcpy), the variant suffixes of Apple's SDK (e.g., realpath$DARWIN_EXTSN, stat$INODE64), the size of the arguments that 32-bit x86 calling conventions append (e.g., _WinExec@8), leading dots and underscores (e.g., _strcpy), the prefixes of library aliases and redirects (e.g., __o_malloc in the Universal CRT, __libc_system, __GI___snprintf, _IO_fwrite, and __isoc23_sscanf in glibc, also in ELF .plt stubs such as .__isoc23_sscanf), and, for stubs and such aliases only, the numeric suffix that IDA appends to names already in use (e.g., memset_0). In custom configurations, a leading #, Apple's variant suffixes, the size of the arguments, dots, and underscores are ignored as well, and each name may be listed under one priority only.

[!NOTE] Fortified functions (e.g., __strcpy_chk, used instead of strcpy when building with _FORTIFY_SOURCE) are deliberately not matched, since they are the checked variants of the listed functions. To also mark their calls, add them explicitly to a custom configuration (e.g., "__strcpy_chk" with the same priority as strcpy). The same works for other redirected names that rhabdomancer doesn't map to their base function yet (e.g., "__xstat" for stat): they are matched by name, and labeled with it once normalized (e.g., [BAD 2] xstat).

Articles

  • https://hex-rays.com/blog/divining-vulnerabilities-contributor-program
  • https://hex-rays.com/blog/streamlining-vulnerability-research-idalib-rust-bindings
  • https://hnsecurity.it/blog/streamlining-vulnerability-research-with-ida-pro-and-rust

See also

  • https://github.com/0xdea/ghidra-scripts/blob/main/Rhabdomancer.java
  • https://docs.hex-rays.com/release-notes/9_0#headless-processing-with-idalib
  • https://github.com/idalib-rs/idalib
  • https://books.google.it/books/about/The_Art_of_Software_Security_Assessment.html

Installing

The easiest way to get the latest release is via crates.io:

  1. Download, install, and configure IDA (see https://hex-rays.com/ida-pro).
  2. Install LLVM/Clang (see https://rust-lang.github.io/rust-bindgen/requirements.html).
  3. On Linux/macOS, install as follows:
    export IDADIR=/path/to/ida # if not set, the build script will check common locations
    cargo install rhabdomancer --locked
    
    On Windows, instead, use the following commands:
    $env:LIBCLANG_PATH="\path\to\clang+llvm\bin"
    $env:PATH="\path\to\ida;$env:PATH"
    $env:IDADIR="\path\to\ida" # if not set, the build script will check common locations
    cargo install rhabdomancer --locked
    

Compiling

Alternatively, you can build from source:

  1. Download, install, and configure IDA (see https://hex-rays.com/ida-pro).
  2. Install LLVM/Clang (see https://rust-lang.github.io/rust-bindgen/requirements.html).
  3. On Linux/macOS, compile as follows:
    git clone --depth 1 https://github.com/0xdea/rhabdomancer
    cd rhabdomancer
    export IDADIR=/path/to/ida # if not set, the build script will check common locations
    cargo build --release --locked
    
    On Windows, instead, use the following commands:
    git clone --depth 1 https://github.com/0xdea/rhabdomancer
    cd rhabdomancer
    $env:LIBCLANG_PATH="\path\to\clang+llvm\bin"
    $env:PATH="\path\to\ida;$env:PATH"
    $env:IDADIR="\path\to\ida" # if not set, the build script will check common locations
    cargo build --release --locked
    

Usage

  1. Make sure IDA is properly configured with a valid license.
  2. Optionally customize the list of known bad API functions: copy conf/rhabdomancer.toml (pick the tag that matches your installed version for its exact built-in list), edit the copy, and set the RHABDOMANCER_CONFIG environment variable to its path. The file must define the high, medium, and low arrays, and no other keys. Otherwise, the built-in list is used, which is embedded in the binary at build time from conf/rhabdomancer.toml (editing that file requires a rebuild).
  3. Make sure the IDADIR environment variable is set if your IDA installation is in a non-standard location.
  4. Run as follows:
    rhabdomancer <binary_file>
    
    Any existing .i64 IDB file will be updated; otherwise, a new IDB file will be created.
  5. Open the resulting .i64 IDB file with IDA.
  6. Select View > Open subviews > Bookmarks
  7. Enjoy your results conveniently collected into an IDA window.

[!NOTE] Rhabdomancer also adds comments at marked call locations. Both bookmarks and comments are tagged as [BAD n] <function_name>, where n is the priority tier (0 = high, 1 = medium, 2 = low), so that scripts can search IDBs for them. This format is stable across releases.

Compatibility

Only the latest IDA release is officially supported, but older versions may work as well. The following table summarizes the latest compatible release for each IDA version:

Baixar ferramenta

Mais Populares

Ver todos →

Descubra as ferramentas mais usadas pela nossa comunidade.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 O kit definitivo de OSINT: grafo de investigação, pontuação de confiança, famílias de alias, mapa, linha do tempo e relatórios. 49 módulos, mais de 400 sites, sem necessidade de chaves de API.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicativo de Execução em Um Toque GhostLock (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    Plataforma autônoma de testes de penetração multiagente com LLM, com agentes planejador/executor, grafos de ativos e de exploração, registro de tráfego MITM e reteste de vulnerabilidades.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Kit de ferramentas de red team do lado do navegador com 102 ferramentas offline para reconhecimento, geração de payloads, ataques a credenciais, criptografia, codificação e relatórios de engajamento.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    Plataforma CSIRT que ingere relatórios do Shadowserver no MongoDB e os reproduz como mapas interativos, análises, descobertas, avisos e painéis executivos.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    O sistema de ação para cibersegurança nativa em IA—onde a intenção se torna execução governada, a evidência se torna memória operacional, e cada operação melhora a próxima.

    264

Explore todas as ferramentas

Navegue pela nossa coleção de ferramentas

Ver todas as ferramentas →






