
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
AperiSolve — Automated steganalysis platform that detects hidden data in images using 16 parallel analyzers, bit-layer visualization, and an in-app wiki for CTF and forensic investigations. | Kitploit
도구/GitHubGitHub/zeecka/aperisolve
ForensicsSteganographyCryptographyCTFLearning & Education
GitHubzeecka/aperisolve

AperiSolve

Automated steganalysis platform that detects hidden data in images using 16 parallel analyzers, bit-layer visualization, and an in-app wiki for CTF and forensic investigations.

저장소 보기
83410120414시간 14분 전Kitploit 검토 완료
공유
웹사이트
요청한 언어로 콘텐츠를 사용할 수 없습니다. 영어 버전을 표시합니다.

Aperi'Solve

Website CI Lint Docker Python Version Ruff uv ty License GitHub Issues GitHub Pull Requests Last Commit Contributors Rawsec's CyberSecurity Inventory

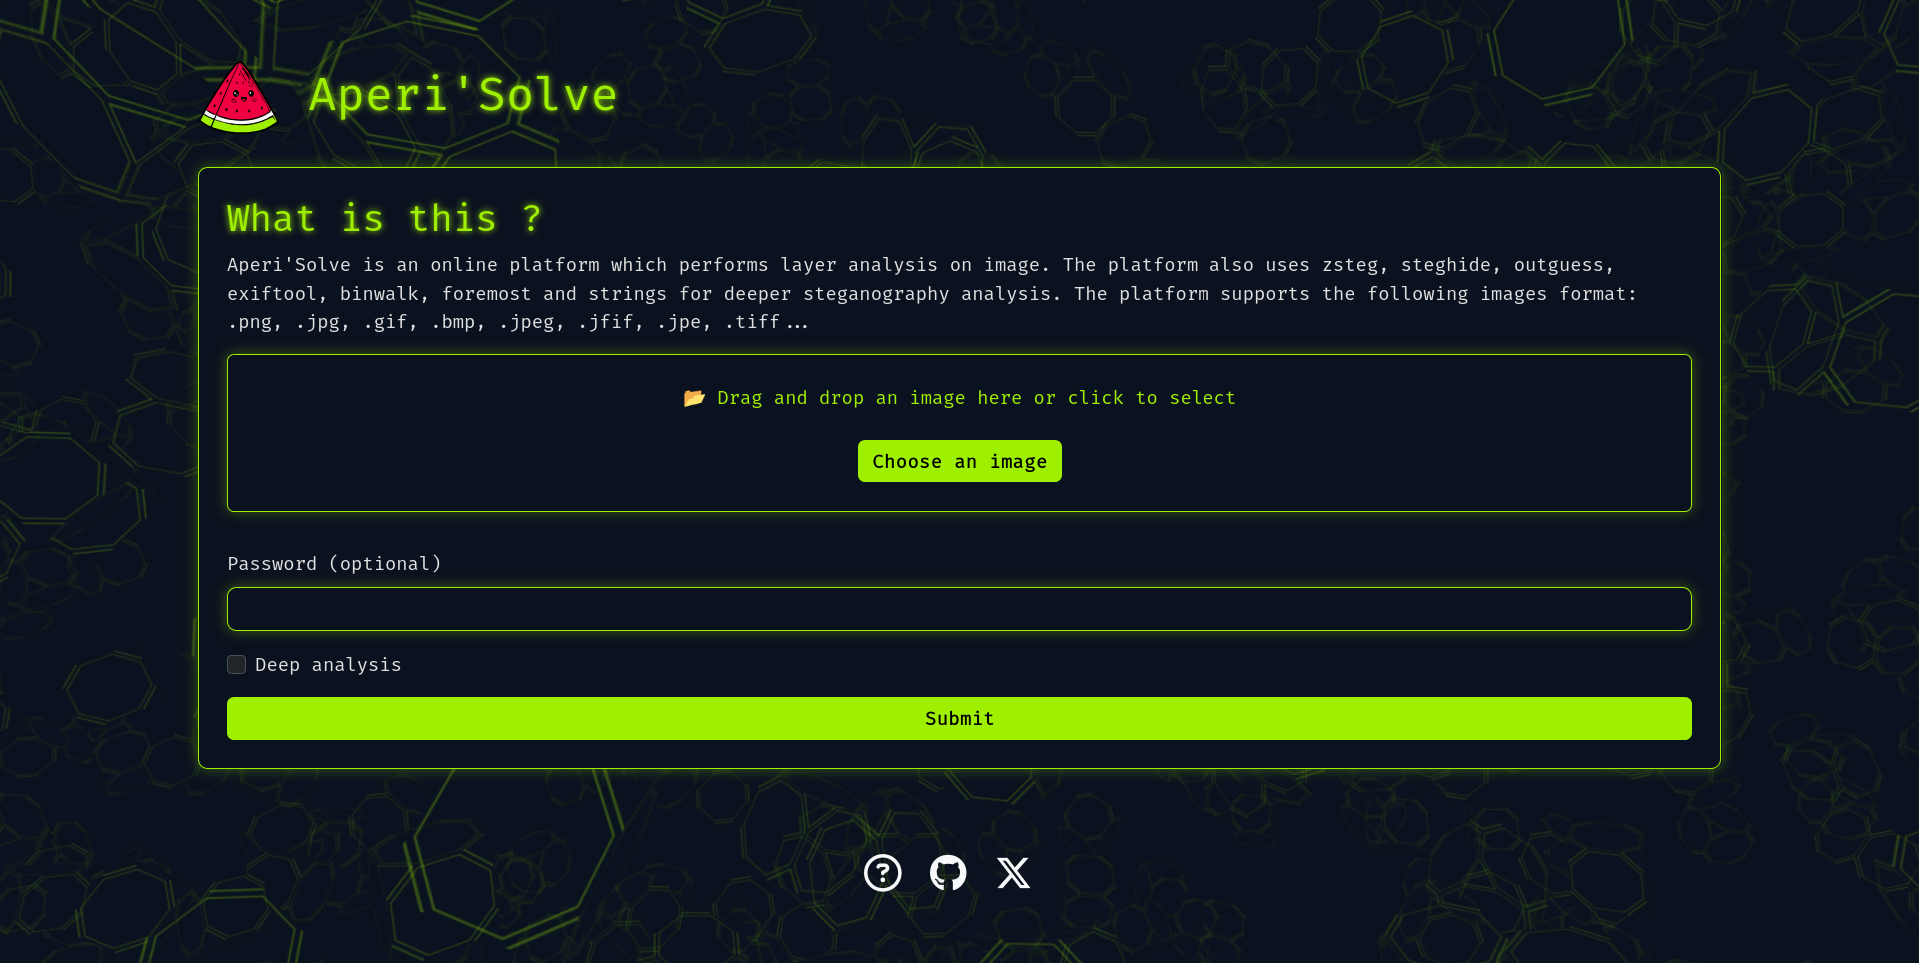
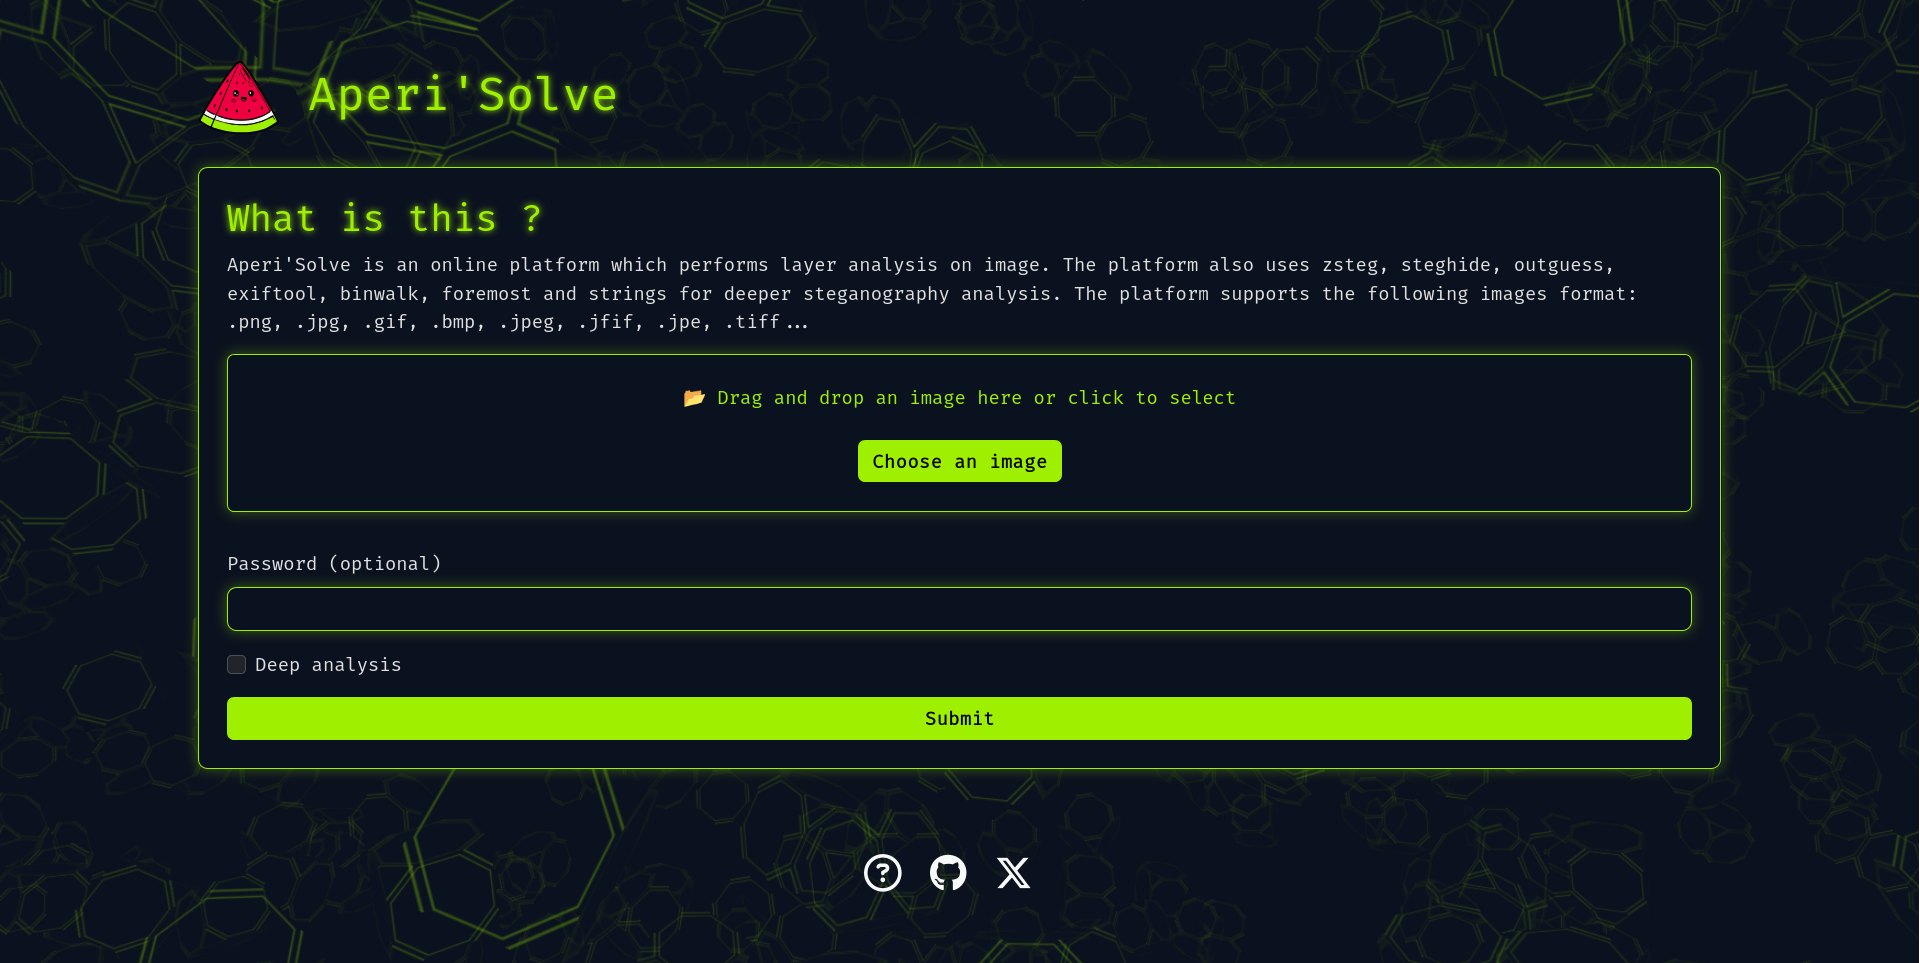
Aperi'Solve screenshot

Try it now: https://www.aperisolve.com

Support Aperi'Solve:

Sponsor Aperi'Solve on GitHub

Aperi'Solve is an open-source steganalysis web platform that performs automated analysis on images to detect and extract hidden data using common steganography tools and techniques.

Key features

  • Visualize each bit layer (LSB and other layers) per image channel (R/G/B/Alpha).
  • Color remapping (random palette remaps with 8 generated variants)
  • Runs 16 analyzers in parallel and displays their output, with per-tool success/no-result badges and one-click download of extracted files:
    • binwalk (embedded archives)
    • exiftool (metadata and geolocation)
    • file (MIME type and format detection)
    • GraphicsMagick identify (image info & properties)
    • foremost (carved files)
    • jsteg (JPEG LSB extraction)
    • jpseek / jphide (JPEG steganography extraction, with password)
    • openstego (extraction with password)
    • outguess (extraction with password, deep analysis)
    • pcrt (PNG check & repair)
    • pngcheck
    • steghide (extraction with password)
    • stegoveritas (image transforms on deep analysis, frames of animated GIF/APNG)
    • strings
    • zsteg (LSB text/data extraction)
  • In-app wiki (/wiki): a HackTricks-style steganography handbook — a triage methodology, a decision-tree cheatsheet, technique pages per medium (image, audio, text, files), and a guide per analyzer, all authored as Markdown.
  • Internationalization: UI available in English, French, Spanish, German, Russian, Chinese and Portuguese under language-prefixed URLs (/fr/, /es/, …).
  • "Ask AI" panel on the result page: send the analysis results and images straight from your browser to your own LLM provider (bring your own key) for a verdict on what is hidden and what to try next. Two checkboxes pick what the model gets: the images (on by default) and a text matrix of every image's pixel values (off by default; native resolution, so text-only models can read LSB data too). The matrix comes from the browser's image decoder: it is exact for opaque pixels of a PNG/BMP/GIF, but a semi-transparent pixel can be off by one in a colour channel (the canvas stores premultiplied alpha), the RGB under a fully transparent pixel reads 0, and JPEG depends on the decoder.
  • MCP server at https://www.aperisolve.com/mcp (docs/mcp.md): lets Claude, Cursor or any MCP client upload a file and read its analysis.
  • Worker queue architecture for offloading heavy/slow analyzers (Redis + background workers).
  • Content-addressed result cache, HTTP caching, and per-endpoint rate limiting.
  • Results stored temporarily for later browsing and download, then cleaned up automatically by a scheduled job.

Adding an analyzer

Adding an analyzer is a single file: subclass SubprocessAnalyzer, set a few class attributes (name, has_archive, needs_password, deep_only, display_order), and install the tool in the Dockerfile. The worker run list, download allow-list, and frontend order are all derived automatically. See docs/adding-analyzer.md.

Quick start (Docker)

In case you want to host your own version of https://www.aperisolve.com/.

Required: Docker + Docker Compose.

git clone https://github.com/Zeecka/AperiSolve.git
cd AperiSolve
cp .env.example .env
docker compose up -d

Then browse url: http://localhost:5000/

Ads and analytics are disabled by default; every integration (CUSTOM_EXTERNAL_SCRIPT, GOOGLE_ADS_TXT, SITE_BASE_URL, Sentry) is opt-in via environment variables documented in .env.example. The app never injects ad markup itself: CUSTOM_EXTERNAL_SCRIPT loads the AdSense script and placement is left to Auto ads.

Architecture

The stack runs as Docker Compose services:

  • web — Flask app served by gunicorn (Jinja templates + vanilla JS frontend).
  • worker — an RQ worker that runs the analyzers for each submission, fanning out to one thread per tool.
  • cron — an RQ cron scheduler that runs the retention cleanup off the request path.
  • initdb — a one-shot service that creates the tables and pre-fills the IHDR CRC recovery database.
  • postgres — stores image metadata and submission status.
  • redis — RQ broker (DB 0) and rate-limiter storage (DB 1).
  • rqdashboard — queue monitoring, bound to localhost:9181.

This separation keeps heavy tools (binwalk, foremost, zsteg, etc.) isolated and avoids blocking the web worker. Identical submissions are deduplicated by a content hash, and derived images are cached with long-lived immutable HTTP headers, so repeat traffic is cheap.

Documentation

  • docs/adding-analyzer.md — add a new analyzer.
  • docs/deploy.md — the tag-driven production deploy flow.
  • docs/mcp.md — the MCP endpoint: client setup, tool reference, quotas.
  • CONTRIBUTING.md — dev setup, tests, wiki pages, and translations.

Testing

uv sync --extra dev
uv run pytest -q            # unit tests (no services needed)

# end-to-end analyzer tests through the running app:
docker compose -f compose.dev.yml up -d
uv run pytest tests/test_webapp_analyzers.py -v

Roadmap

See Issues.

Contributing

See CONTRIBUTING.md.

Security

도구 다운로드

인기

모두 보기 →

커뮤니티에서 가장 많이 사용되는 도구를 찾아보세요.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 궁극의 OSINT 툴킷: 조사 그래프, 신뢰도 점수 산정, 별칭 패밀리, 지도, 타임라인 및 보고서. 49개 모듈, 400개 이상 사이트, API 키 불필요.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # GhostLock 원탭 실행 앱 (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM 멀티 에이전트 자율 침투 테스트 플랫폼으로, 플래너/워커 에이전트, 자산 및 탐색 그래프, MITM 트래픽 기록, 취약점 재테스트 기능을 제공합니다.

    405
  • 4

    redforge

    cybersecurity91/redforge

    브라우저 측 레드 팀 툴킷으로, 정찰, 페이로드 생성, 자격 증명 공격, 암호화, 인코딩 및 참여 보고를 위한 102개의 오프라인 도구를 제공합니다.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI 네이티브 사이버보안을 위한 행동 체계—의도가 통제된 실행이 되고, 증거가 운영 메모리가 되며, 모든 운영이 다음 운영을 개선하는 곳.

    261
  • 6

    antifox

    antifox-ai/antifox

    정찰, 공격 표면 탐색, 익스플로잇 검증, 증거 기반 보고서 전달을 수행하는 AI 멀티 에이전트 자율 침투 테스트 플랫폼입니다.

    259

모든 도구 탐색

도구 컬렉션을 둘러보세요

모든 도구 보기 →