
 eskatos/creadur-rat-gradle
Apache RAT (릴리스 감사 도구) Gradle 플러그인



이 플러그인은 라이선스에 초점을 맞춘 Apache RAT 릴리스 감사 도구를 실행할 수 있게 해줍니다.
build.gradle(.kts) 파일에 다음을 추가하세요:
plugins {
    id("org.nosphere.apache.rat") version "0.8.1"
}
이 플러그인은 rat이라는 태스크를 등록하며, build.gradle(.kts) 파일에서 다음과 같이 구성할 수 있습니다:
tasks.rat {

    // Use the default RAT license header matchers, defaults to `true`
    addDefaultMatchers.set(false)

    // Add custom substring license header matchers
    substringMatcher("family", "category", "pattern-1", "pattern-2")

    // Declare approved license families, if used, any non-declared family won't be approved
    approvedLicense("MIT")

    // Input directory, defaults to '.'
    inputDir.set("some/path")

    // List of Gradle exclude directives, defaults to ['**/.gradle/**']
    excludes.add("**/build/**")

    // RatTask 0.5.0+ implements PatternFilterable
    exclude { it.file in configurations.someConf.files }

    // Rat excludes file, one directive per line
    excludeFile.set(layout.projectDirectory.file(".rat-excludes.txt"))

    // XML, TXT and HTML reports directory, defaults to 'build/reports/rat'
    reportDir.set(file("some/other/path"))

    // Custom XSL stylesheet for the HTML report
    stylesheet.set(file("custom/rat-html-stylesheet.xsl"))

    // Fail the build on rat errors, defaults to true
    failOnError.set(false)
}
rat {

    // Input directory, defaults to '.'
    inputDir.set(file("some/path"))

    // List of Gradle exclude directives, defaults to ['**/.gradle/**']
    excludes.add("**/build/**")

    // Rat excludes file, one directive per line
    excludeFile.set(layout.projectDirectory.file(".rat-excludes.txt"))

    // XML, TXT and HTML reports directory, defaults to 'build/reports/rat'
    reportDir.set(file("some/other/path"))

    // Custom XSL stylesheet for the HTML report
    stylesheet.set(file("custom/rat-html-stylesheet.xsl"))

    // Fail the build on rat errors, defaults to true
    failOnError.set(false)

    // Prints the list of files with unapproved licences to the console, defaults to false
    verbose.set(true)
}
Gradle을 호출하여 rat 태스크를 실행할 수 있습니다:
gradle rat
프로젝트에 check 태스크가 있으면 rat 태스크가 해당 태스크에 의존하도록 자동으로 등록됩니다.
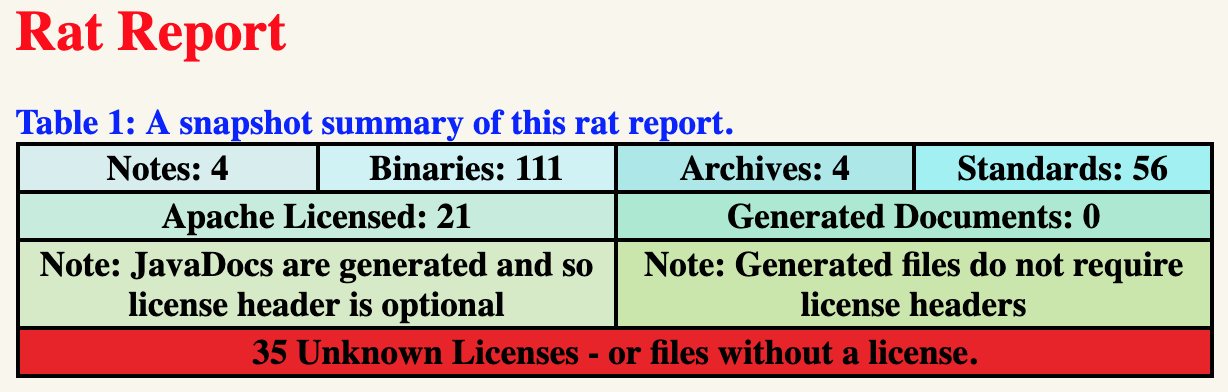
Rat 감사가 실패하면 HTML 보고서의 클릭 가능한 URL이 출력됩니다:
FAILURE: Build failed with an exception.

* What went wrong:
Execution failed for task ':rat'.
> Apache Rat audit failure - 35 unapproved licenses
    See file:///path/to/build/reports/rat/index.html
| 플러그인 | 최소 Java | 최소 Gradle | 최대 Gradle | 구성 캐시 | 빌드 캐시 |
|---|---|---|---|---|---|
0.8.1 | 1.8 | 6.0 | 8.x | 🟢 | 🟢 |
0.8.0 | 1.8 | 6.0 | 8.x | 🟡 | 🟢 |
0.7.1 | 1.8 | 6.0 | 7.x | 🟡 | 🟢 |
0.7.0 | 1.8 | 6.0 | 7.x | 🟡 | 🟢 |
0.6.0 | 1.6 | 4.7 | 6.x | 🟡 | 🟢 |
0.5.3 | 1.6 | 4.7 | 6.x | 🔴 | 🟢 |
0.5.2 | 1.6 | 4.7 | 6.x | 🔴 | 🟢 |
0.5.1 | 1.6 | 4.7 | 5.x | 🔴 | 🟢 |
0.5.0 | 1.6 | 4.7 | 5.x | 🔴 | 🟢 |
0.4.0 | 1.6 | 4.7 | 5.x | 🔴 | 🟢 |
0.3.1 | 1.6 | 2.14 | 4.x | 🔴 | 🟢 |
0.3.0 | 1.6 | 2.14 | 4.x | 🔴 | 🟢 |
0.2.0 | 1.6 | 2.14 | 4.x | 🔴 | 🟢 |
0.1.0 | 1.6 | 2.14 | 4.x | 🔴 | 🟢 |






