

chisel v1.12.0-rc3
SSH 암호화를 사용하는 HTTP 기반의 빠른 TCP/UDP 터널로, 역방향 포트 포워딩, SOCKS5 프록시, 클라이언트 인증을 지원하여 안전한 네트워크 통과 및 방화벽 우회를 가능하게 합니다.
Chisel


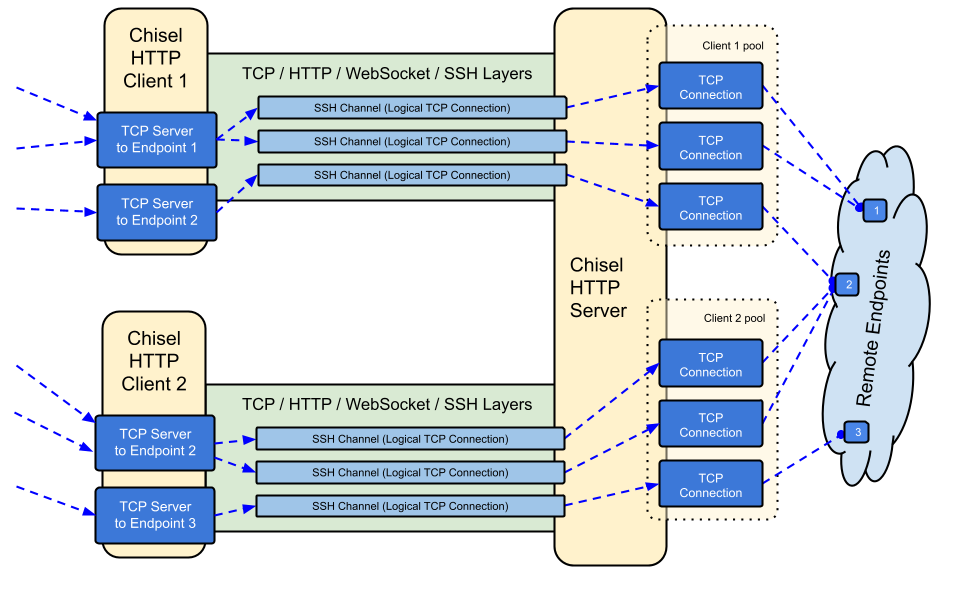
Chisel은 HTTP를 통해 전송되고 SSH로 보호되는 빠른 TCP/UDP 터널입니다. 클라이언트와 서버를 모두 포함하는 단일 실행 파일로, Go(golang)로 작성되었습니다. Chisel은 주로 방화벽을 우회하는 데 유용하며, 네트워크에 대한 보안 엔드포인트를 제공하는 데에도 사용할 수 있습니다.
목차
기능
- 사용하기 쉬움
- 고성능*
- SSH 프로토콜(
crypto/ssh경유)을 사용한 암호화된 연결 - 인증된 연결; 사용자 구성 파일로 인증된 클라이언트 연결, 지문 매칭으로 인증된 서버 연결.
- 클라이언트는 지수 백오프로 자동 재연결(
--min/max-retry-interval로 조정 가능); keepalive 핑이 타임아웃되므로, 조용히 끊어진 연결(절전/재개, NAT 타임아웃, 서버 재시작)이 감지되어 다시 설정됩니다. - 클라이언트는 단일 TCP 연결을 통해 여러 터널 엔드포인트를 생성할 수 있습니다.
- 클라이언트는 선택적으로 SOCKS 또는 HTTP CONNECT 프록시를 통과할 수 있습니다.
- 역방향 포트 포워딩(연결이 서버를 통과하여 클라이언트 밖으로 나감)
- 서버는 선택적으로 리버스 프록시 역할을 합니다.
- 서버는 선택적으로 SOCKS5 연결을 허용합니다(아래 가이드 참조).
- 클라이언트는 선택적으로 역방향 포트 포워딩에서 SOCKS5 연결을 허용합니다.
ssh -o ProxyCommand를 지원하는 stdio를 통한 클라이언트 연결로 HTTP를 통한 SSH를 제공합니다.
설치
바이너리


최신 릴리스를 확인하거나 curl https://i.jpillora.com/chisel! | bash로 지금 바로 다운로드하여 설치하세요.
바이너리는 최신 Go 릴리스로 빌드되며, 최소 OS 버전은 다음과 같습니다: Windows 10 / Server 2016, macOS 12, Linux 커널 3.2, FreeBSD 12.2. 이전 시스템(예: Windows 7)의 경우 릴리스 v1.8.1 이하를 사용하세요.
Docker

이미지는 멀티 아키텍처로 제작되어 Docker Hub(`jpillora/chisel`)와 GitHub Container Registry(`ghcr.io/jpillora/chisel`) 양쪽에 게시됩니다.

### Fedora

이 패키지는 Fedora 커뮤니티에서 유지 관리합니다. RPM 사용과 관련된 문제가 발생하면 이 [이슈 트래커](https://bugzilla.redhat.com/buglist.cgi?bug_status=NEW&bug_status=ASSIGNED&classification=Fedora&component=chisel&list_id=11614537&product=Fedora&product=Fedora%20EPEL)를 이용해 주세요.```sh
sudo dnf -y install chisel
Source
소스```sh
$ go install github.com/jpillora/chisel@latest
## 데모

몇 분 안에 나만의 데모 서버를 실행할 수 있습니다(기존 Heroku 데모는 Heroku의 무료 티어와 함께 사라졌습니다). [`example/fly.toml`](https://github.com/jpillora/chisel/blob/master/example/fly.toml)은 이 `chisel server`를 [fly.io](https://fly.io)의 무료 할당량에 배포합니다:```sh
$ chisel server --port $PORT --backend http://example.com
# listens on $PORT, proxies normal web requests to http://example.com
fly launch --copy-config 명령을 example/ 디렉토리에서 실행하여 배포한 다음, 서버 옆에서 실행 중인 서비스에 터널링합니다. 예:```sh
$ chisel client https://.fly.dev 3000
connects to your chisel server,
tunnels your localhost:3000 to the server's localhost:3000
브라우저에서 앱의 URL을 방문하면 서버의 기본 백엔드 프록시에 도달하여 [example.com](http://example.com)의 복사본이 표시됩니다.

## 사용법

<!-- render these help texts by hand,
  or use https://github.com/jpillora/md-tmpl
    with $ md-tmpl -w README.md -->

<!--tmpl,code=plain:echo "$ chisel --help" && go run main.go --help | sed 's#0.0.0-src (go1\..*)#X.Y.Z#' -->``` plain
$ chisel --help

  Usage: chisel [command] [--help]

  Version: X.Y.Z

  Commands:
    server - runs chisel in server mode
    client - runs chisel in client mode

  Read more:
    https://github.com/jpillora/chisel
$ chisel server --help
Usage: chisel server [options]
Options:
--host, Defines the HTTP listening host – the network interface
(defaults the environment variable HOST and falls back to 0.0.0.0).

--port, -p, Defines the HTTP listening port (defaults to the environment
variable PORT and falls back to port 8080).

--key, (deprecated use --keygen and --keyfile instead)
An optional string to seed the generation of a ECDSA public
and private key pair. All communications will be secured using this
key pair. Share the subsequent fingerprint with clients to enable detection
of man-in-the-middle attacks (defaults to the CHISEL_KEY environment
variable, otherwise a new key is generate each run).

--keygen, A path to write a newly generated PEM-encoded SSH private key file.
If users depend on your --key fingerprint, you may also include your --key to
output your existing key. Use - (dash) to output the generated key to stdout.

--keyfile, An optional path to a PEM-encoded SSH private key. When
this flag is set, the --key option is ignored, and the provided private key
is used to secure all communications. (defaults to the CHISEL_KEY_FILE
environment variable). Since ECDSA keys are short, you may also set keyfile
to the inline key string itself, exactly as printed by --keygen (a base64
string with a "ck-" prefix); no extra base64 encoding is needed.

--authfile, An optional path to a users.json file. This file should
be an object with users defined like:
  {
    "<user:pass>": ["<addr-regex>","<addr-regex>"]
  }
when <user> connects, their <pass> will be verified and then
each of the remote addresses will be compared against the list
of address regular expressions for a match. Patterns are NOT
anchored by default: "10.0.0.1:80" also matches
"210.0.0.1:8080", and "." matches any character. Anchor your
patterns, e.g. "^10\.0\.0\.1:80$". The empty string ""
matches every address. Addresses will
always come in the form "<remote-host>:<remote-port>" for normal remotes,
"R:<local-interface>:<local-port>" for reverse port forwarding
remotes, and "socks" for SOCKS5 proxy access. Note that SOCKS5
access previously bypassed this list; existing authfiles which
should allow SOCKS5 must add an entry matching "socks" (the
empty wildcard "" matches everything, including "socks"). This
file will be automatically reloaded on change. Reloads apply
to new connections and to new tunnels of connected clients;
established tunnels are not interrupted.

--auth, An optional string representing a single user with full
access, in the form of <user:pass>. It is equivalent to creating an
authfile with {"<user:pass>": [""]}. If unset, it will use the
environment variable AUTH.

--keepalive, An optional keepalive interval. Since the underlying
transport is HTTP, in many instances we'll be traversing through
proxies, often these proxies will close idle connections. You must
specify a time with a unit, for example '5s' or '2m'. Defaults
to '25s' (set to 0s to disable).

--backend, Specifies another HTTP server to proxy requests to when
chisel receives a normal HTTP request. Useful for hiding chisel in
plain sight. --proxy is accepted as an alias for this flag.

--socks5, Allow clients to access the internal SOCKS5 proxy. See
chisel client --help for more information.

--reverse, Allow clients to specify reverse port forwarding remotes
in addition to normal remotes.