
 #1
Tools and libraries for automating security tasks, workflows, and custom tool development.
Kitploit 추천
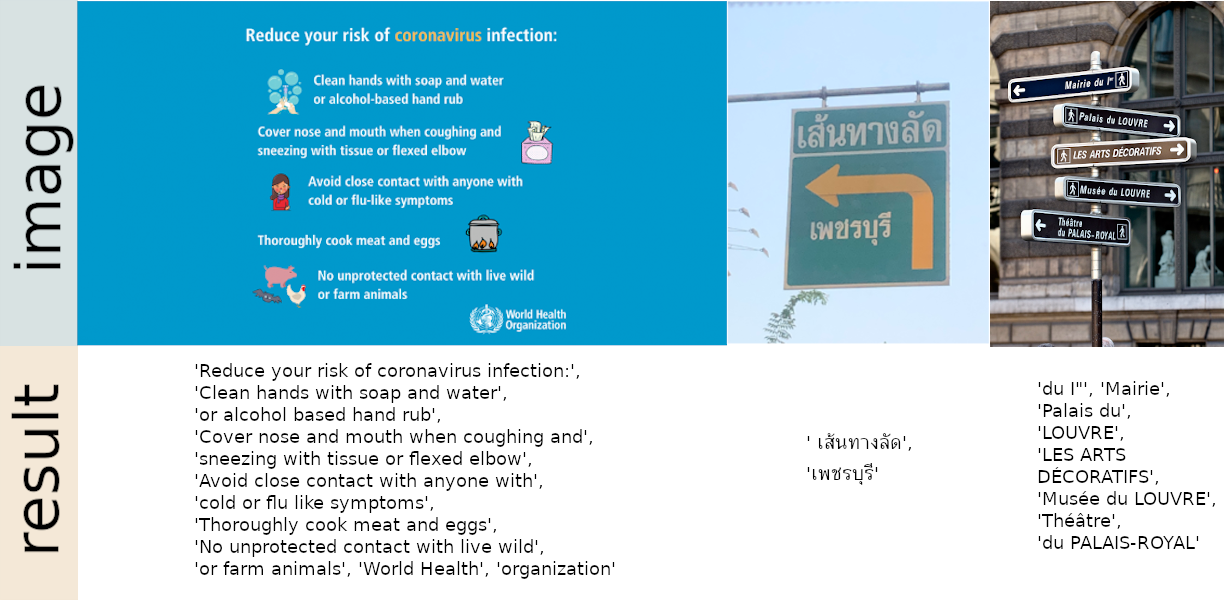
 jaidedai/easyocr
즉시 사용 가능한 OCR로, 80개 이상의 언어와 라틴 문자, 중국어, 아랍어, 데바나가리, 키릴 문자 등 모든 주요 문자 체계를 지원합니다.

 nearai/ironclaw
로컬 암호화 스토리지, OAuth/SSO 인증, 정책 기반 접근 제어, 개인 및 프로덕션 배포를 위한 확장 가능한 도구 구축 프레임워크를 갖춘 안전하고 프라이빗한 AI 에이전트 운영 체제.
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 ultrafunkamsterdam/nodriver
Undetected-Chromedriver의 후속작입니다. Captcha / CloudFlare / Imperva / hCaptcha와 같은 성가신 안티 봇 시스템에 의해 일반적으로 방해받는 웹 자동화, 웹스크래핑, 봇 및 기타 창의적인 아이디어를 위한 초고속…
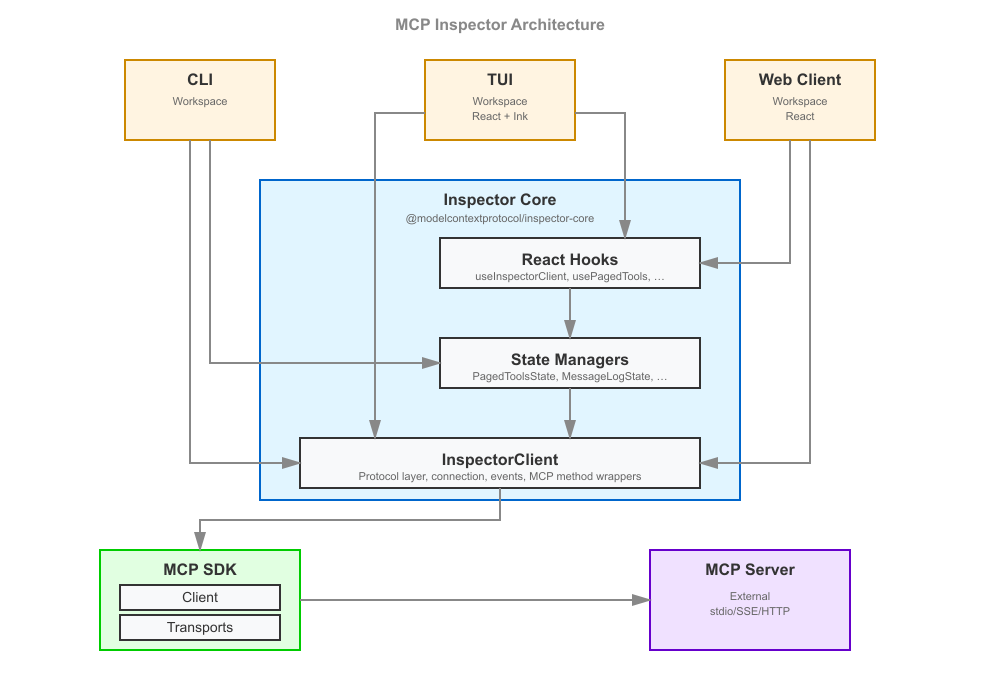 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 mkdocs/mkdocs
Markdown 형식의 프로젝트 문서.
 fabric/fabric
간단하고 Pythonic한 원격 실행 및 배포.
 pydantic/monty
AI가 작성한 코드를 위한 Rust로 작성된 안전한 Python 샌드박스입니다.
 didierstevens/didierstevenssuite
악성코드 분석, 파일 형식 파싱, 해싱, 포렌식 트리아지를 위한 Python 스크립트 모음으로, PDF, OLE, XOR 분석 유틸리티를 포함합니다.
six2dez/reconftwreconFTW는 대상 도메인에 대해 자동화된 정찰을 수행하기 위해 설계된 도구로, 최적의 도구 세트를 실행하여 스캐닝을 수행하고 취약점을 찾아냅니다.
 projectdiscovery/naabu
Go로 작성된 빠른 포트 스캐너로, 신뢰성과 단순성에 중점을 둡니다. 버그 바운티 및 침투 테스트에서 공격 표면 발견을 위해 다른 도구와 함께 사용하도록 설계되었습니다.
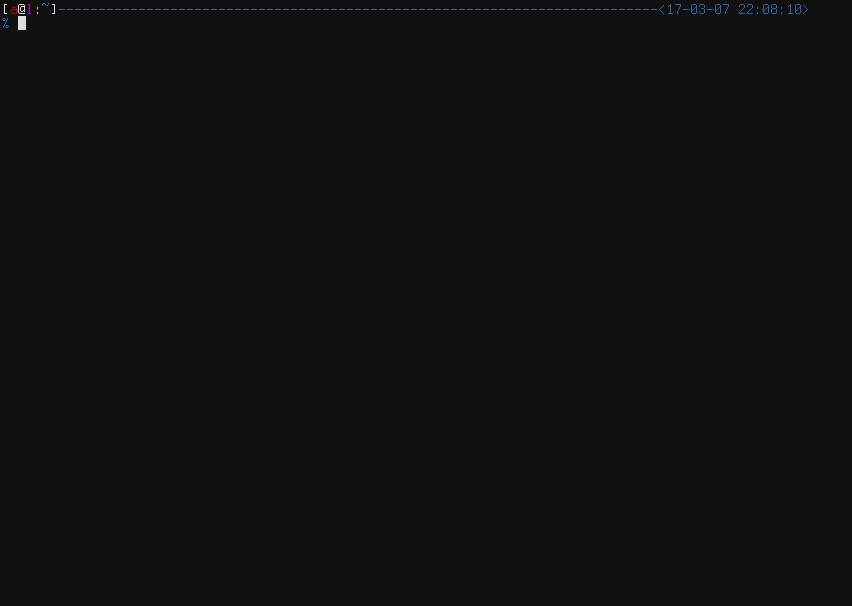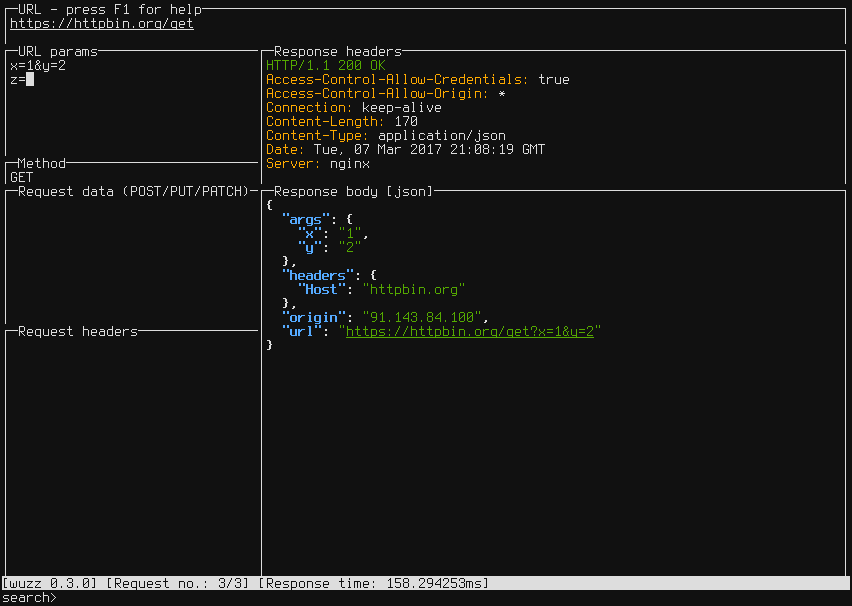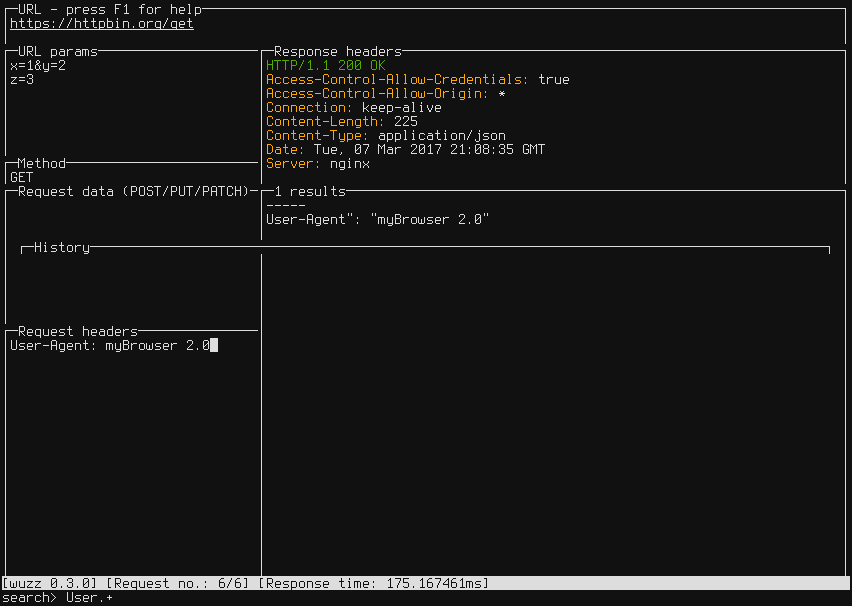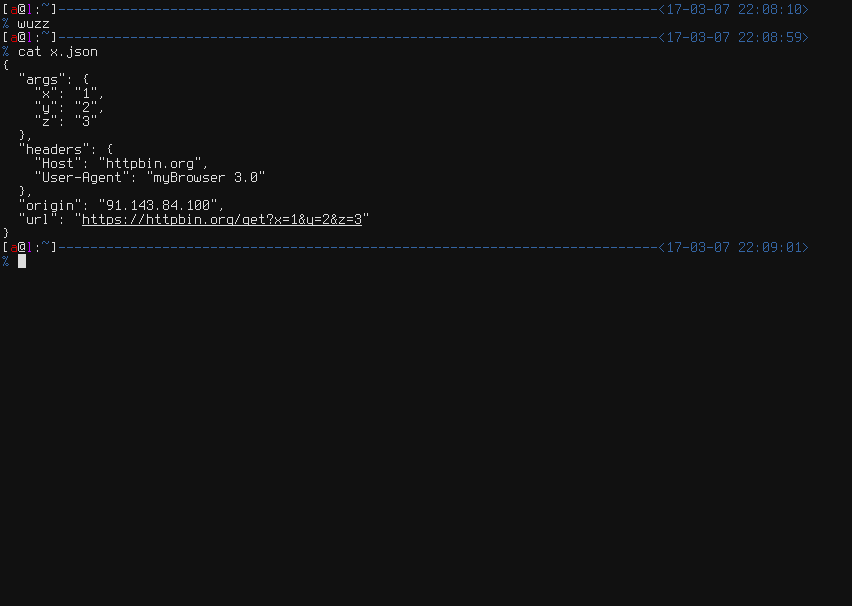 asciimoo/wuzz
HTTP 검사를 위한 대화형 CLI 도구
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 bc-security/empire
Empire는 Red Team과 침투 테스터를 지원하는 데 사용되는 사후 침투 및 적성 모의(adversary emulation) 프레임워크입니다.
 arxhr007/aliens_eye
AI powered OSINT engine to discover and map 840+ social media identities across the web




