
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Papers & Research — 56페이지 | Kitploit
카테고리

Papers & Research

Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.

Kitploit 추천

추천 도구

10 선택됨
security-research preview#1

security-research

GitHubgoogle/security-research
4.6k4일 전
0days-in-the-wild preview#2

0days-in-the-wild

GitHubgoogleprojectzero/0days-in-the-wild
1.0k3개월 전
MSRC-Security-Research preview#3

MSRC-Security-Research

GitHubmicrosoft/msrc-security-research
1.4k2년 전
publications preview#4

publications

GitHubtrailofbits/publications
1.9k8일 전
papers-we-love preview#5

papers-we-love

GitHubpapers-we-love/papers-we-love
111.7k24일 전
criticality_score preview#6

criticality_score

GitHubossf/criticality_score
1.5k2개월 전
attack-stix-data preview#7

attack-stix-data

GitHubmitre-attack/attack-stix-data
72716일 전
Security-101 preview#8

Security-101

GitHubmicrosoft/security-101
6.8k2개월 전
h4cker preview#9

h4cker

GitHubthe-art-of-hacking/h4cker
28.9k4일 전
offensive-ai-compilation preview#10

offensive-ai-compilation

GitHubjiep/offensive-ai-compilation
1.4k20일 전
최신관련성인기최근 업데이트
2394 결과
CVE-2026-54107 preview

CVE-2026-54107

GitHubpravin761/cve-2026-54107

CVE-2026-54107의 근본 원인 분석: Windows win32kfull.sys에서 발생하는 use-after-free 취약점에 대한 레이스 컨디션 디버깅, 정적 분석, MSRC 트리아지 인사이트, 그리고 실용적인 커널 익스플로잇 연구.

static-analysisvulnerability-analysisexploitation+5
13개월 전
cryptography-research-demo preview

cryptography-research-demo

GitHubanthropics/cryptography-research-demo

축소 라운드 AES에 대한 단일 키 복구 공격을 위한 재현 가능한 암호분석 산출물로, 블랙박스 키 복구, DDT-Gray 탐색, S-box 캐시, Lean 형식 증명을 포함합니다.

vulnerability-analysiscryptographypapers-research+1
603개월 전
UnConfuserEx preview

UnConfuserEx

GitHubzypherion-technologies/unconfuserex

안티 태머, 압축기, 상수, 제어 흐름 및 리소스 복구를 지원하는 ConfuserEx2 디난독화 도구입니다.

static-analysisdynamic-analysis-sandboxingcode-analysis+6
403개월 전
public-research preview

public-research

GitHubdeepfield/public-research

Nokia Deepfield ERT의 DDoS 봇넷 연구 및 침해 지표

ioc-managementosintnetwork-security+3
643개월 전
HiTMS_steganography preview

HiTMS_steganography

GitHubryehr/hitms_steganography

산술/Discop 스테가노그래픽 코더를 사용하여 LLM 채팅 토큰 선택에 여러 개의 비밀 메시지를 임베드하고, 비트 정확한 디코딩 및 스테가날리시스 평가를 제공합니다.

defensive-toolsdata-exfiltrationsteganography+4
33개월 전
objdump-Out-Of-Bounds-write preview

objdump-Out-Of-Bounds-write

GitHub4d4j/objdump-out-of-bounds-write

CVE-2026-18220을 시연하는 개념 증명(PoC)으로, GNU binutils의 DLX ELF 백엔드에 존재하는 범위를 벗어난(OOB) 쓰기 취약점입니다(`objdump -g`를 통해 트리거됨).
vulnerability-analysisexploitationbinary-analysis+3
793개월 전
CVE-2026-66748-Camaleon-CMS---Authenticated-RCE-via-select_eval-Custom-Field preview

CVE-2026-66748-Camaleon-CMS---Authenticated-RCE-via-select_eval-Custom-Field

GitHubtheopaid/cve-2026-66748-camaleon-cms---authenticated-rce-via-select_eval-custom-field

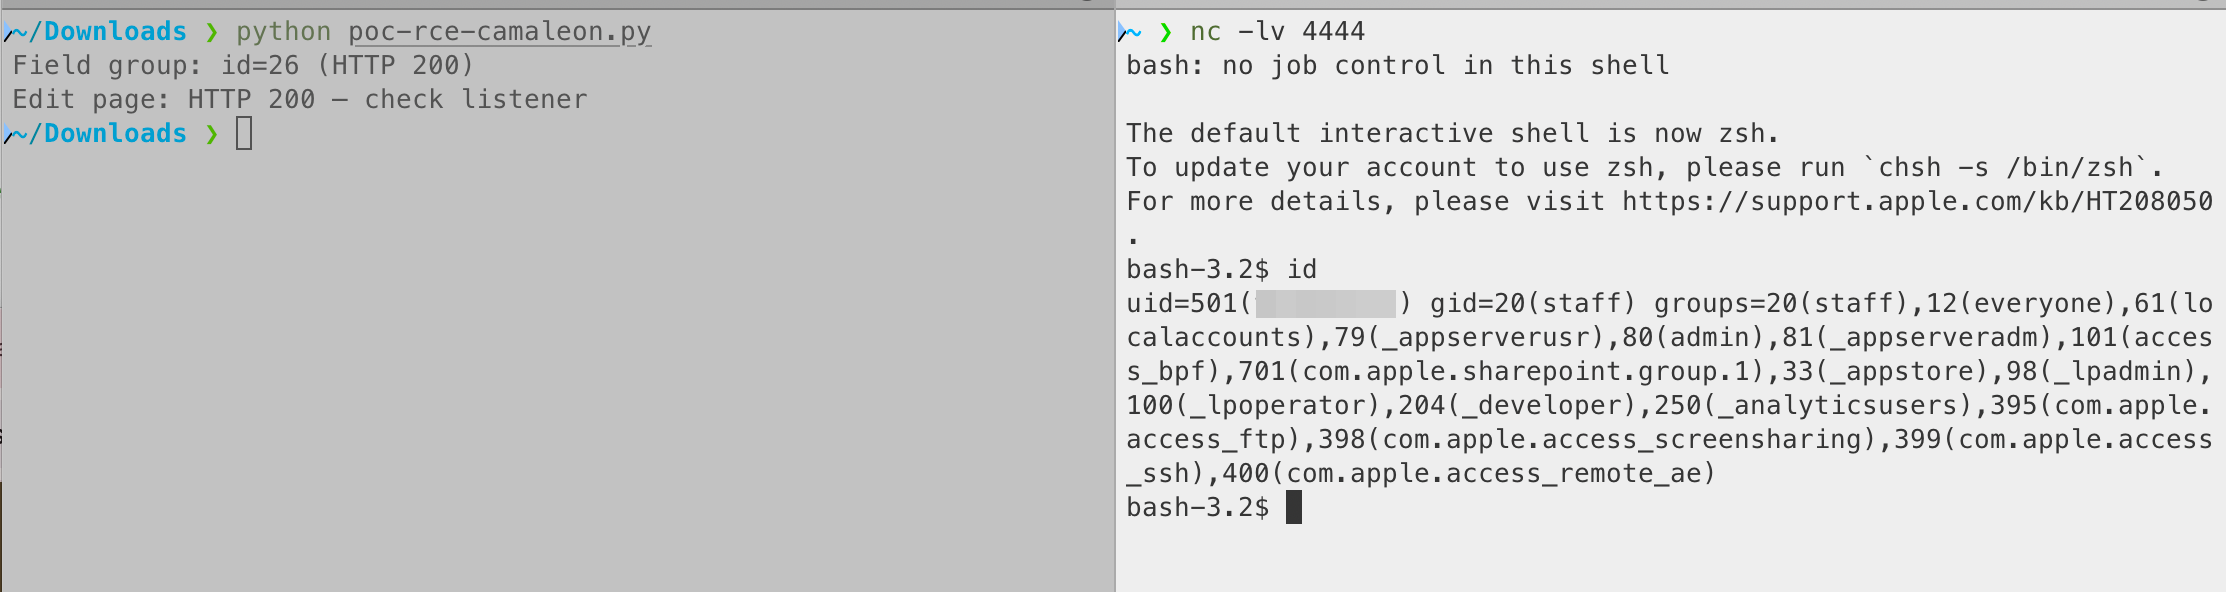
보안 권고: Camaleon CMS - `select_eval` 사용자 정의 필드를 통한 인증된 RCE
vulnerability-analysiscode-analysisexploitation+4
13개월 전
CVE-2026-67183-Unauthenticated-Memory-Leak-Leads-To-Memory-Exhaustion-TinyWeb- preview

CVE-2026-67183-Unauthenticated-Memory-Leak-Leads-To-Memory-Exhaustion-TinyWeb-

GitHubtheopaid/cve-2026-67183-unauthenticated-memory-leak-leads-to-memory-exhaustion-tinyweb-

보안 권고: 인증되지 않은 메모리 누수로 인한 메모리 고갈 (TinyWeb)
vulnerability-analysisweb-securitypapers-research+1
3개월 전
CVE-2026-67184-Unauthenticated-NULL-Pointer-Dereference-Crashes-the-Server-TinyWeb- preview

CVE-2026-67184-Unauthenticated-NULL-Pointer-Dereference-Crashes-the-Server-TinyWeb-

GitHubtheopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-

보안 권고: 인증되지 않은 NULL 포인터 역참조로 서버 충돌 발생 (TinyWeb)

vulnerability-analysisexploitationweb-application-exploitation+2
13개월 전
CVE-2026-66752-HTTP-Request-Smuggling-via-Unparsed-Transfer-Encoding-Values-tiny_http- preview

CVE-2026-66752-HTTP-Request-Smuggling-via-Unparsed-Transfer-Encoding-Values-tiny_http-

GitHubtheopaid/cve-2026-66752-http-request-smuggling-via-unparsed-transfer-encoding-values-tiny_http-

보안 권고: 구문 분석되지 않은 Transfer-Encoding 값을 통한 HTTP 요청 스머글링 (tiny_http)
vulnerability-analysisweb-application-exploitationweb-security+1
3개월 전
CVE-2026-67182-HTTP-Request-Smuggling-Enables-Front-End-Access-Control-Bypass-rouille- preview

CVE-2026-67182-HTTP-Request-Smuggling-Enables-Front-End-Access-Control-Bypass-rouille-

GitHubtheopaid/cve-2026-67182-http-request-smuggling-enables-front-end-access-control-bypass-rouille-

보안 권고: HTTP 요청 스머글링으로 프런트 엔드 접근 제어 우회 가능 (rouille)

vulnerability-analysisweb-application-exploitationweb-security+2
3개월 전
CVE-2026-66754-Remote-Denial-of-Service-via-Reachable-Assertion-in-URL-Prefix-Handling-rouille- preview

CVE-2026-66754-Remote-Denial-of-Service-via-Reachable-Assertion-in-URL-Prefix-Handling-rouille-

GitHubtheopaid/cve-2026-66754-remote-denial-of-service-via-reachable-assertion-in-url-prefix-handling-rouille-

보안 권고: URL 접두사 처리에서 도달 가능한 어서션을 통한 원격 서비스 거부 (rouille)

vulnerability-analysisweb-securitypapers-research+1
3개월 전
CVE-2026-53921 preview

CVE-2026-53921

GitHub0xblackash/cve-2026-53921

CVE-2026-53921

iot-securityvulnerability-analysispapers-research+1
23개월 전
CP-PLUS-EZ-P21-CVE-2026-65893-65894 preview

CP-PLUS-EZ-P21-CVE-2026-65893-65894

GitHubcybervinner/cp-plus-ez-p21-cve-2026-65893-65894

CP PLUS EZ-P21 IP 카메라 CVE 문서화: 디버그 기능을 통한 임의 코드 실행 및 HTTP 엔드포인트의 부적절한 인증, 책임 있는 공개 포함.
embedded-systems-securityiot-securityvulnerability-analysis+5
3개월 전
CVE-2025-47812-Research preview

CVE-2025-47812-Research

GitHubmajdae/cve-2025-47812-research

CVE-2025-47812를 분석하는 학술 연구 저장소로, Wing FTP Server의 Lua 삽입을 통한 심각한 RCE 취약점에 대한 정적/동적 분석 및 개념 증명(PoC)을 포함합니다.

vulnerability-analysisexploitationreverse-engineering+3
13개월 전
liferay-ga4-rce-research preview

liferay-ga4-rce-research

GitHubdinosn/liferay-ga4-rce-research

Liferay CE 7.0.3 GA4 보안 연구: 사전 인증 RCE as root(CVE-2020-7961 계열)를 엔드투엔드로 재현했으며, 추가로 16건의 발견 사항 포함 — 그중 8건 이상은 알려진 CVE가 없음. 에이전트 기반 루프 헌팅: Docker에서 25개…

dynamic-analysis-sandboxingvulnerability-analysisexploitation+6
63개월 전
CVE-2023-3350 preview

CVE-2023-3350

GitHubitres-labs/cve-2023-3350

IBERMATICA RPS의 암호화 관련 취약점에 대한 익스플로잇 [CVE-2023-3350]
vulnerability-analysisexploitationweb-application-exploitation+6
3개월 전
CVE-2026-66729-Out-of-Bounds-Read-in-facil.io-MIME-Parser-leads-to-Server-Crash preview

CVE-2026-66729-Out-of-Bounds-Read-in-facil.io-MIME-Parser-leads-to-Server-Crash

GitHubtheopaid/cve-2026-66729-out-of-bounds-read-in-facil.io-mime-parser-leads-to-server-crash

보안 권고: facil.io MIME 파서의 경계를 벗어난 읽기(Out-of-Bounds Read)로 인해 서버가 충돌할 수 있음

vulnerability-analysisweb-securitypapers-research+2
13개월 전
이전1…555657…100다음








